Devpost
Participate in our public hackathons
Devpost for Teams
Access your company's private hackathons
Grow your developer ecosystem and promote your platform
Drive innovation, collaboration, and retention within your organization
By use case
Blog
Insights into hackathon planning and participation
Customer stories
Inspiration from peers and other industry leaders
Planning guides
Best practices for planning online and in-person hackathons
Webinars & events
Upcoming events and on-demand recordings
Help desk
Common questions and support documentation
Sort by:
An AI-driven health monitoring platform using Splunk observability to detect risks, analyze medical data, automate alerts, and improve patient safety.
An autonomous SOC triage agent that investigates incidents against live Splunk data, writes its own SPL, and returns MITRE ATT&CK-mapped verdicts with a sealed audit trail.
AllBlue alerts trigger autonomous AI forensic triage. Findings pushed back to AllBlue as structured IOC events. 100% precision, 0 hallucinations. Claude + Go MCP + SIFT
NEXUS is an AI Incident Commander that automates outage triage, investigation, and recovery. Using LangGraph and Splunk, it pinpoints root causes and generates recovery playbooks in seconds.
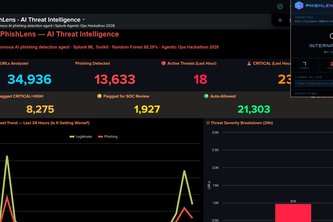
Autonomous AI phishing detection agent
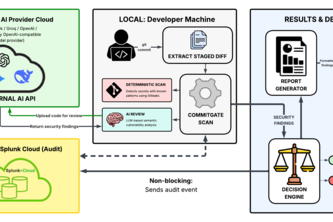
AI-powered Git pre-commit security gate
The self-correcting forensic agent that finds evil at machine speed — and proves it isn't hallucinating.
An AI agent that autonomously investigates Splunk alerts — running targeted SPL queries, pinpointing root causes, and posting a full incident report to Slack in under 30 seconds.
"Your firewall forgets. ThreatGraph never does."
GreenOps: AI‑powered Real-time monitoring of cloud workload cost, utilization, waste detection, and AI-powered insights with cloud cost and waste intelligence on Splunk .
An agentic SOC assistant for Splunk that investigates alerts with REST evidence, builds attack timelines, scores risk, keeps analysts in control, and exports reports.
NeuroScale Ops Agent: Splunk-powered AI that detects, diagnoses, and self-heals Kubernetes ML infrastructure - no human in the loop.
An AI agent that connects to any Splunk instance via MCP, maps the environment, flags what's broken, and builds you a starter kit. A week of tribal knowledge transfer in ten minutes.
Every alert your Splunk fires means to open a search, write SPL, correlate across hosts, decide if it's real, write up what're found. 80% toil and 20% actual decision-making. Symphunk flips that.
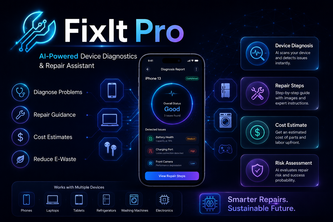
FixIt Pro uses intelligent diagnostics and repair guidance to help users troubleshoot phones, laptops, and appliances, reducing repair costs and electronic waste.
AI agents autonomously investigate security incidents in 60 seconds - from alert triage to Splunk SPL queries to MITRE ATT&CK mapping - replacing 45 minutes of manual SOC analyst work.
Four specialized AI agents autonomously detect, investigate and respond to security threats using Splunk Machine Learning, reducing analyst investigation time from 60 minutes to 12 seconds.
AI-Powered Sports Platform Observability with Nebius Medical Monitoring for diabetes, heart rate, and athlete recovery.
A calm incident queue that turns noisy service logs into runbook steps an operator can actually use.
Prisme is an autonomous AI agent that analyzes raw logs and application code to instantaneously generate and deploy props.conf, SPL queries and live dashboards through the Splunk REST API.
The digital twin of your best engineer. OpsTwin AI preserves expertise, reconstructs incident-response reasoning, and empowers every engineer to act like an expert.
Splunk is not just a log sink - it's the AI brain for enterprise grade network and environmental observability, anomaly detection, notification and forecasting.
Transform 847 SIEM alerts into a complete APT kill chain in under 90 seconds — automatically.
By 2033, quantum computers will break today's encryption — and attackers are already hoarding your data. ZeroQ's AI scans everything, spots the risks, and walks you through the fix.