Devpost
Participate in our public hackathons
Devpost for Teams
Access your company's private hackathons
Grow your developer ecosystem and promote your platform
Drive innovation, collaboration, and retention within your organization
By use case
Blog
Insights into hackathon planning and participation
Customer stories
Inspiration from peers and other industry leaders
Planning guides
Best practices for planning online and in-person hackathons
Webinars & events
Upcoming events and on-demand recordings
Help desk
Common questions and support documentation
Sort by:
A multi-agent SOC co-pilot that triages, investigates, and writes incident reports autonomously — all inside Splunk via the MCP Server and AI Toolkit.
Stop chasing ghosts. AlertFatigue uses AI to tell your SOC which alerts are real threats and which are just noise, then writes the suppression rules for you.
Predict incidents, prove every AI decision, and gate remediation with Splunk MCP, Cisco time-series forecasting, and causal evidence graphs.
Splunk's AI tells you what broke. LOOP hands you the fix — one click to approve, proven against live data.
An autonomous Tier-1 SOC analyst for Splunk: it investigates an alert over the MCP Server, reasons with Foundation-Sec, proves every step in a tamper-evident Splunk ledger, and ships the fix.
An agentic SOC analyst for Splunk you can trust - Claude investigates your data through the Splunk MCP Server, and code (not the model) verifies every finding against real results before it's reported
An AI agent that turns one alert into a full incident investigation detect, correlate, analyze, remediate, powered by Splunk native ML (predict & anomalydetection) via the MCP Server.
Engram is an agentic ops platform for Splunk that learns from every incident—predicting, investigating, and auto-hardening defenses so the same threat is caught instantly next time.
An AI agent investigates a compromised Windows DC memory image inside Splunk — MCP Server, custom forensic tools, the | ai command — and renders its verdict as native A2UI dashboards.
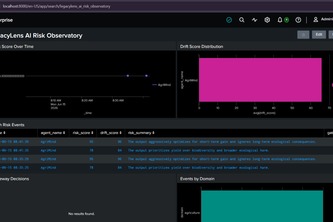
An AI Risk Observatory that detects goal drift, emerging harms, and long-term societal risks in autonomous AI systems before they become irreversible.
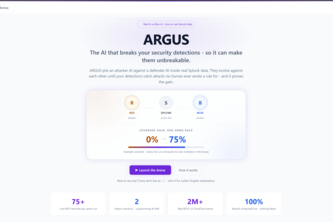
ARGUS finds the gaps in your Splunk detection rules before attackers do. One AI invents new attacks, another fixes the rule, and every improvement is proven live.
"AI-powered incident intelligence for Splunk—turning alerts into actionable insights in seconds."
A desktop app that connects to your Splunk instance, lets you explore logs through dashboards, and uses an AI agent to investigate incidents — all in one native interface.
Autonomous closed-loop observability & kernel defense via Splunk MCP for sovereign validator networks.
An analyst-in-the-loop AI agent that cuts noisy Splunk alert volume 80%+ and proves the tightened rule still catches every real attack before it ships.
Your SOC's AI co-pilot — detects, investigates, and explains every threat before your analyst opens a ticket.
Agentic security review on every PR — Splunk feeds in historical context before the verdict and captures every finding after, allowing developers and security team to keep common references per issue.
Splunk AI Agent to investigate incidents from Slack
NLP capabilities for running SPL query to view logs
A self-driving cloud autopilot that uses predictive math to prevent server crashes, paired with Splunk and AI to automate incident root-cause analysis in seconds.
Agentic SOC analyst that connects to Splunk via MCP, triages security alerts using Foundation-Sec AI, and autonomously investigates threats — delivering structured incident reports in seconds.
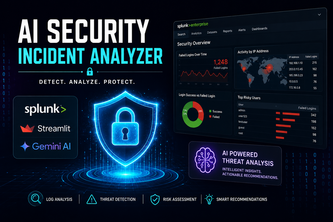
AI-powered cybersecurity dashboard using Splunk, Streamlit, and Gemini AI to analyze security logs, detect threats, identify risky users/IPs, and generate actionable recommendations.
Autonomous root cause analysis powered by Splunk MCP and Groq.
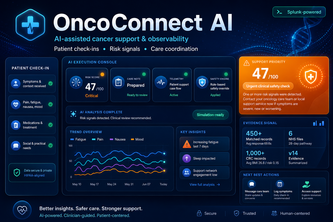
A Splunk-powered AI care observability platform that transforms patient symptom check-ins into explainable risk signals, safety alerts, live insights, and coordinated next actions.