Devpost
Participate in our public hackathons
Devpost for Teams
Access your company's private hackathons
Grow your developer ecosystem and promote your platform
Drive innovation, collaboration, and retention within your organization
By use case
Blog
Insights into hackathon planning and participation
Customer stories
Inspiration from peers and other industry leaders
Planning guides
Best practices for planning online and in-person hackathons
Webinars & events
Upcoming events and on-demand recordings
Help desk
Common questions and support documentation
Sort by:
Dashboards show symptoms. Chronoscope walks backward through Splunk via MCP, building a cited causal chain—and surfaces the highest-leverage intervention point in under 2 minutes.
Provable correctness turns noise into signal: agentic observability on Splunk, starting with oversell-proof flash drops.
AI-powered autonomous security agent that monitors Splunk logs 24/7, detects threats using GPT-4/Claude, and automatically blocks attacks in seconds—before damage occurs.
Ten AI agents that autonomously engineer, red-team, and deploy Splunk detections — cutting alert noise 99% while proving MITRE coverage, ROI and compliance.
Every other submission teaches the agent what to do. SPLUNK-MIND teaches it what it doesn't know.
Autonomous AI Security Triage Agent — Splunk + SANS SIFT MCP · Gemini 2.5 Flash.
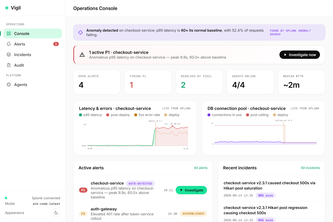
On-call as a team of AI agents: Vigil auto-detects an incident in Splunk, finds the root cause, verifies it, and applies a human-gated fix — cutting MTTR from ~45 min to ~2.
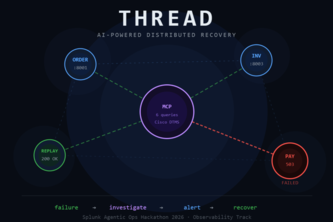
AI-powered distributed transaction tracing. 6 MCP calls. One-click recovery. Under 30 seconds.
Contract-based behavioral observability for AI agents, built natively on Splunk. Know not just that your agent ran but whether it was allowed to do what it did.
Who is watching your AI agents? AgentWatch turns Splunk into a real time governance layer that catches data theft, privilege escalation, and rogue tool calls before damage is done.
41% of breaches start with a service account, not a human. Golem monitors your Non-human Identities in Splunk using MCP Server and hosted AI models.
Autonomous Enterprise Digital Twin & Crisis Commander
5 AI agents that act as an autonomous SOC analyst — turning thousands of raw Splunk alerts into prioritized, investigated, and actionable threat intelligence in seconds, not hours
A 4-agent autonomous security operations system built specifically for hospital IT infrastructure.
CoverageForge maps your Splunk data against MITRE ATT&CK, identifies detection gaps, and auto-generates deployment-ready SPL rules - turning days of manual detection engineering into minutes.
Pin "healthy" once, diff every incident against it forever.
Autonomous AI agent that investigates security incidents through Splunk MCP — from alert to response in 60 seconds, with zero hallucinations.
OpsPilot AI is an adaptive AIOps platform that uses Splunk MCP and AI agents to detect anomalies, investigate incidents, identify root causes, and recommend remediation in real time.
AI-powered SOC triage dashboard that auto-investigates Splunk security alerts using a multi-agent system, so analysts focus only on what matters.
AI agent that detects intruders with a provable error bound, tells human attackers from AI agents, and adapts its honeypot deception to waste each one's time keeping a real breach near zero
Kernel threat detection on Splunk: eBPF detects, AI decides, three safety gates verify every action before it runs.
An autonomous vulnerability management agent inside Splunk that ingests live CVE threats, scores business risk with AI, and self-remediates critical exposures—from detection to containment in seconds.