Devpost
Participate in our public hackathons
Devpost for Teams
Access your company's private hackathons
Grow your developer ecosystem and promote your platform
Drive innovation, collaboration, and retention within your organization
By use case
Blog
Insights into hackathon planning and participation
Customer stories
Inspiration from peers and other industry leaders
Planning guides
Best practices for planning online and in-person hackathons
Webinars & events
Upcoming events and on-demand recordings
Help desk
Common questions and support documentation
Sort by:
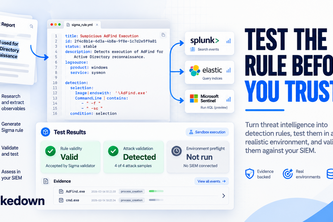
Generated Sigma rules are only candidates. Shakedown tests each one on a real attack log and benign logs in a Nebius Sandbox, repairs misses, and shows the evidence, failures included.
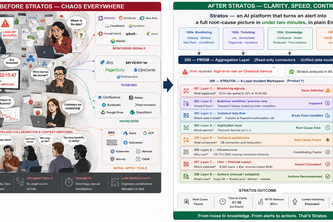
Agentic incident response that collapses the L1→L2→L3→SRE handoff into one shared, business-aware view — turning alerts into root cause and recommendations in plain English, under 5 minutes.
AI compliance copilot that cuts suspicious transaction reviews from 10 minutes to 10 seconds. LangChain ReAct agent + banking-grade security (RBAC, SHA256, PBKDF2, LLM Guard).
AI compliance copilot that cuts suspicious transaction reviews from 10 minutes to 10 seconds. LangChain ReAct agent + banking-grade security
Autonomous Banking Security for Privileged Access and Insider Threat Protection.
Agentic SOC Platform helps security teams control alert floods by turning noisy signals into organized cases, evidence-backed investigations, threat-intelligence context,
Agentic Chaos Monkey uses Google ADK to inject safe failures, diagnose issues from logs and metrics, trigger approved recovery, and verify that systems truly heal before production incidents strike.
From Alerts to Resolution—Inside Slack.
An AI agent that checks DataHub before it touches your data — ownership, deprecation, quality — and writes every DLP violation and remediation back to the context graph as the audit trail.
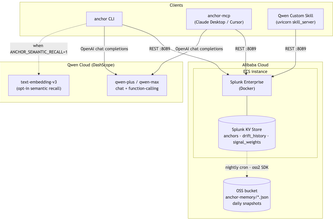
Your infra forgets. Anchor doesn't.
AI-powered system for real-time data breach detection using Explainable AI and threat intelligence for accurate, transparent security alerts.
Most AI tutors guess their way through math and science. AXIOM computes first with a deterministic combinatorial engine (exact Punnett squares, permutations, electron configurations, harmonic analysis
New data lands every week and waits months for a dashboard. Hatch turns a raw Splunk index into a working app in ~2 minutes, and proves every field it extracts on events instead of a stock template.
Splunk multi-agent war room: a fired detection becomes an auditable incident brief plus a backtested SPL fix that cuts false alarms 75%, in under 3 minutes.
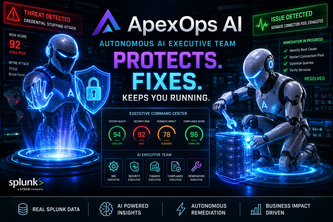
The Autonomous Executive Operations Center that autonomously monitors, investigates, analyzes, explains, predicts, and remediates operational and security incidents using Splunk data.
AI agent that triages Splunk security alerts end-to-end — writing its own SPL through the Splunk MCP Server and returning a MITRE-mapped verdict in seconds.
Your alert fired because the data changed shape while the system stayed healthy. Driftwood tells noise from news.
Splunk-native AI agent observability platform — real-time anomaly detection, two-stage detection pipeline, and plain-English root cause analysis powered by Foundation-Sec-1.1-8B
An autonomous SOC analyst on Splunk: it forms hypotheses, queries via the MCP Server, reasons with hosted models, and hands you a MITRE-mapped case file with a one-click response.
Splunk-grounded AI agents that catch risky deployments before they become incidents, scoring deploy risk, finding root cause, and writing human-approved fixes back to Splunk.
AegisOps: Modern infrastructure, intelligently defended.