-
-
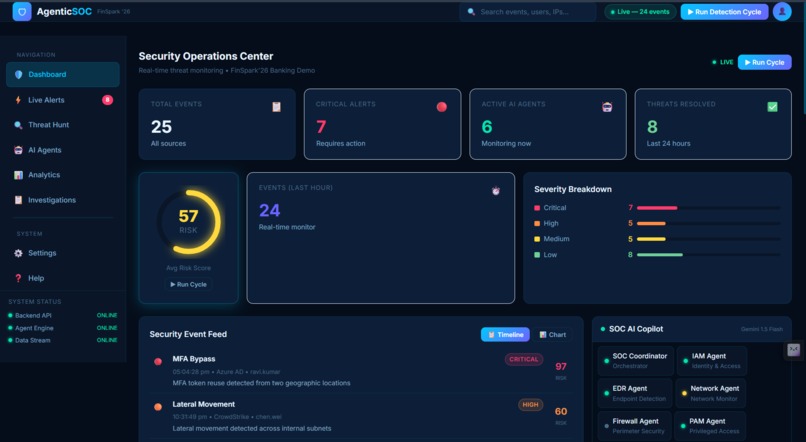
Dashboard - Real-time overview of threats, alerts, incidents, and security posture.
-
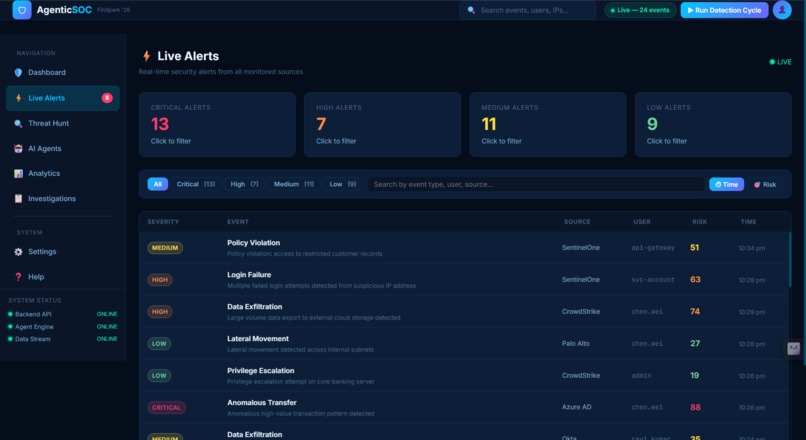
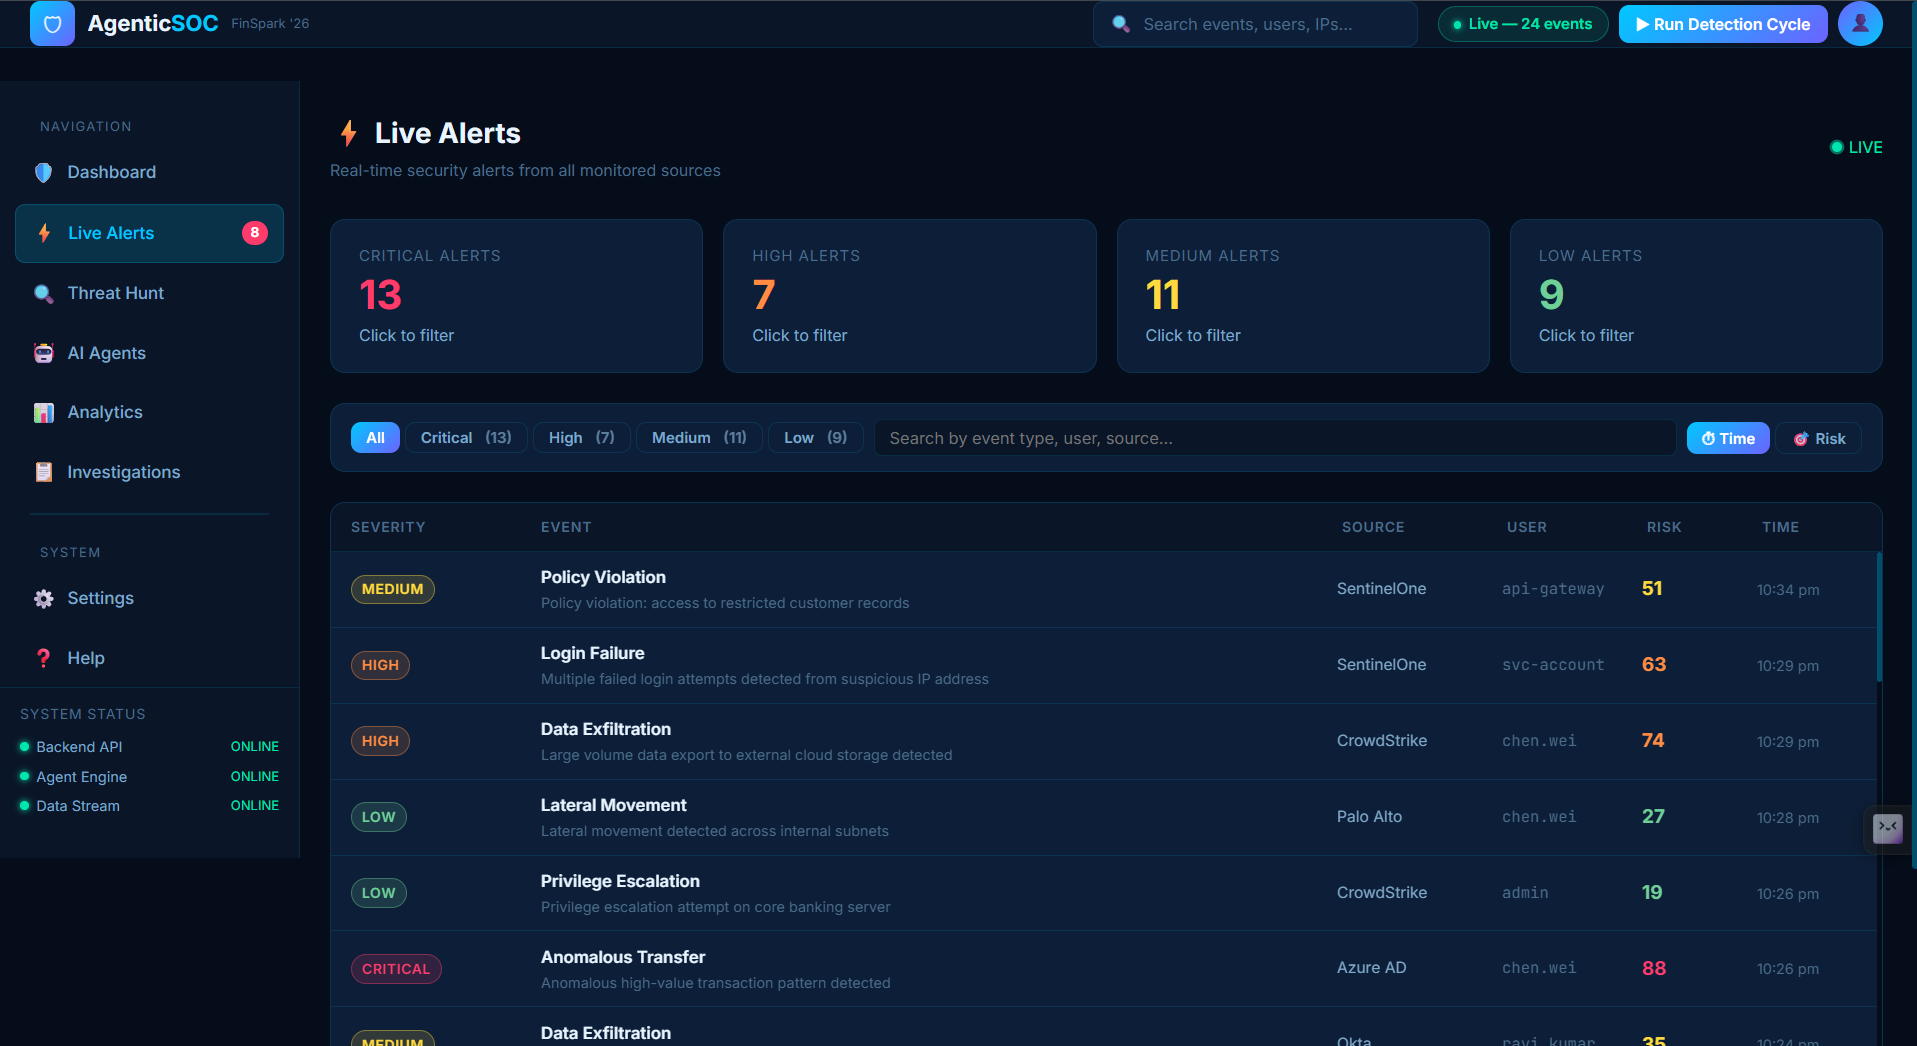
Live Alerts - Monitor and prioritize real-time security alerts and threats.
-
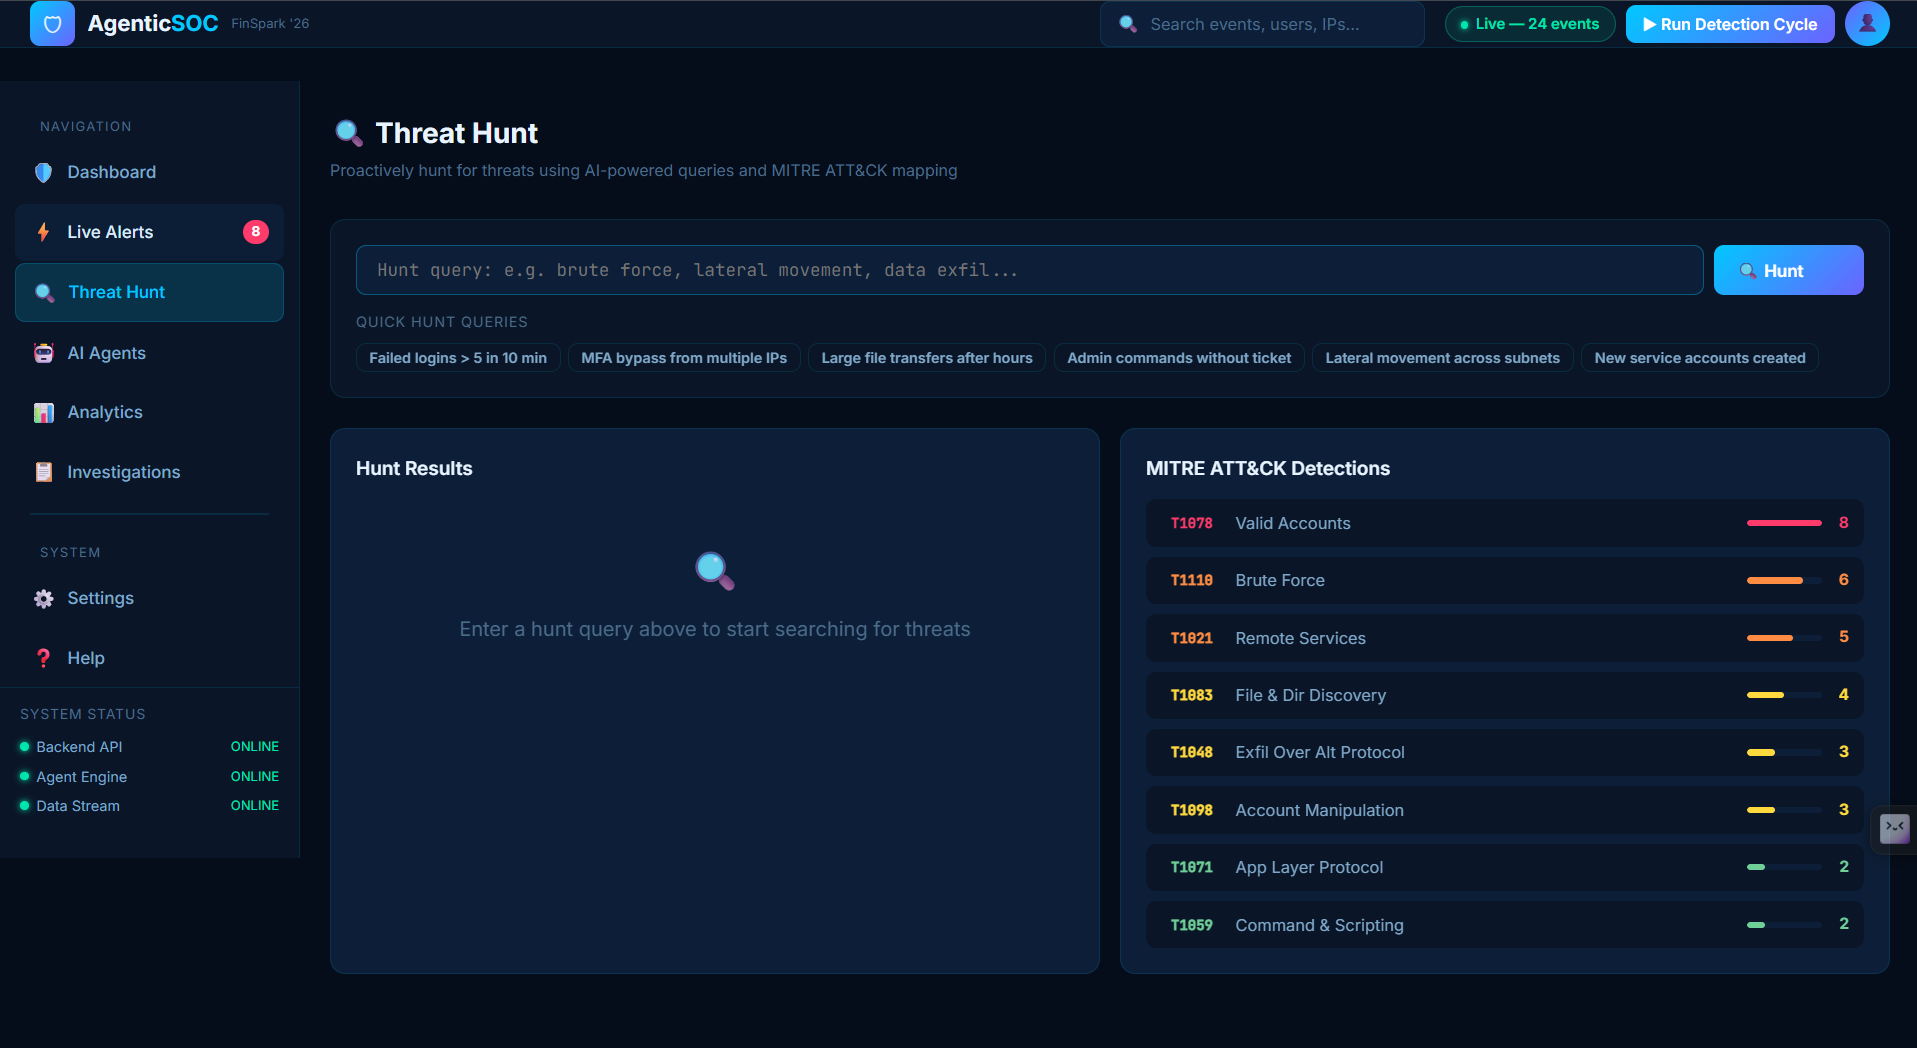
Threat Hunt - Search, analyze, and investigate suspicious security activities.
-
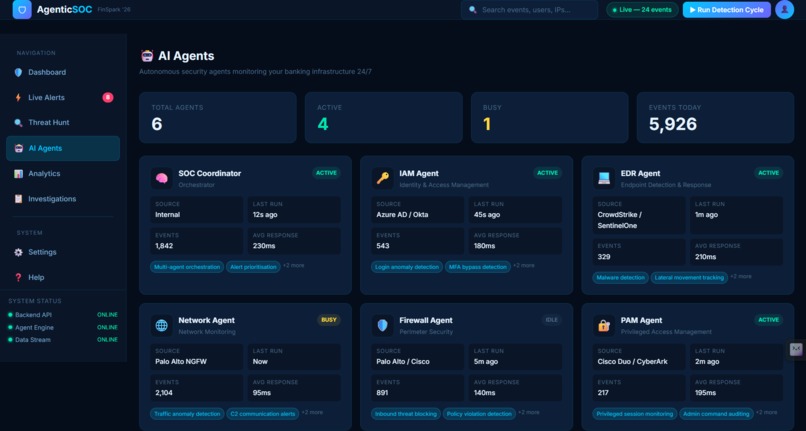
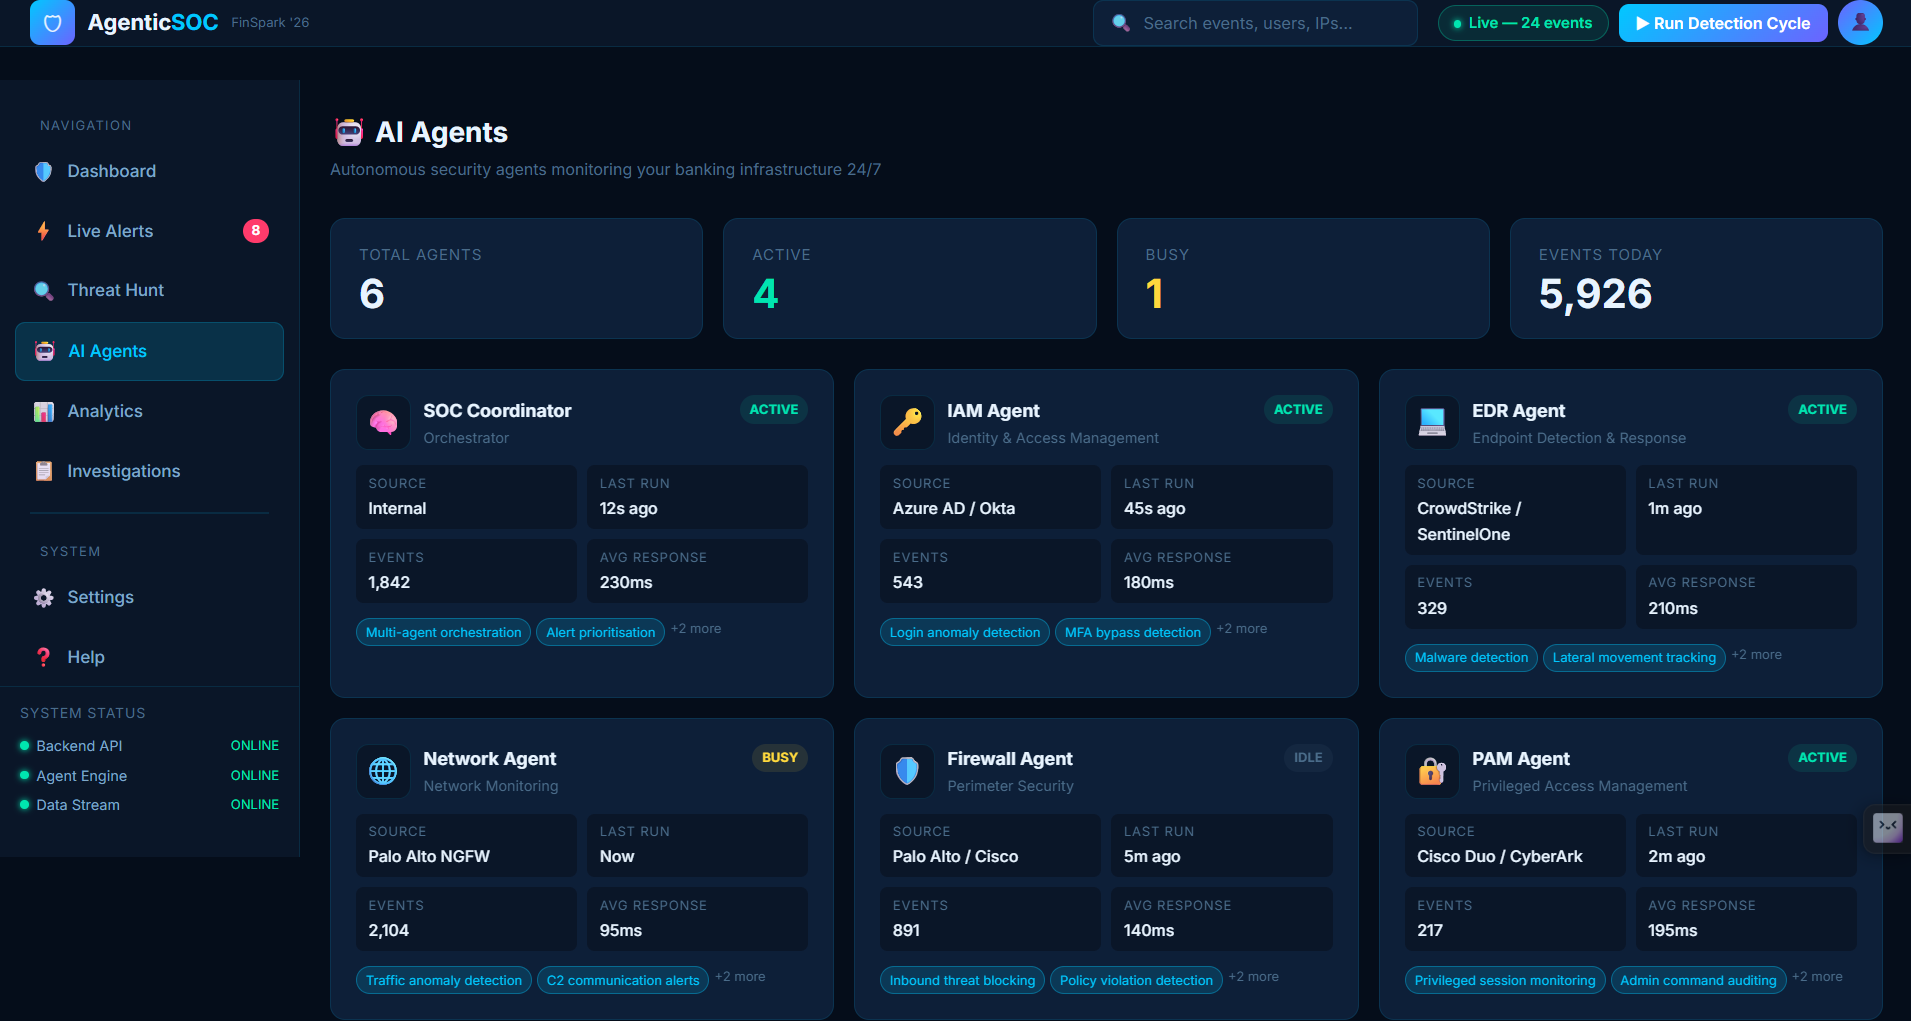
AI Agents - Autonomous agents detect, investigate, and respond to cyber threats.
-
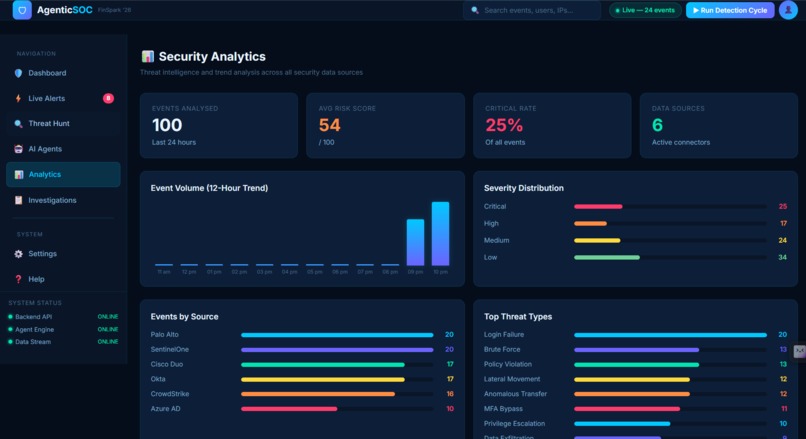
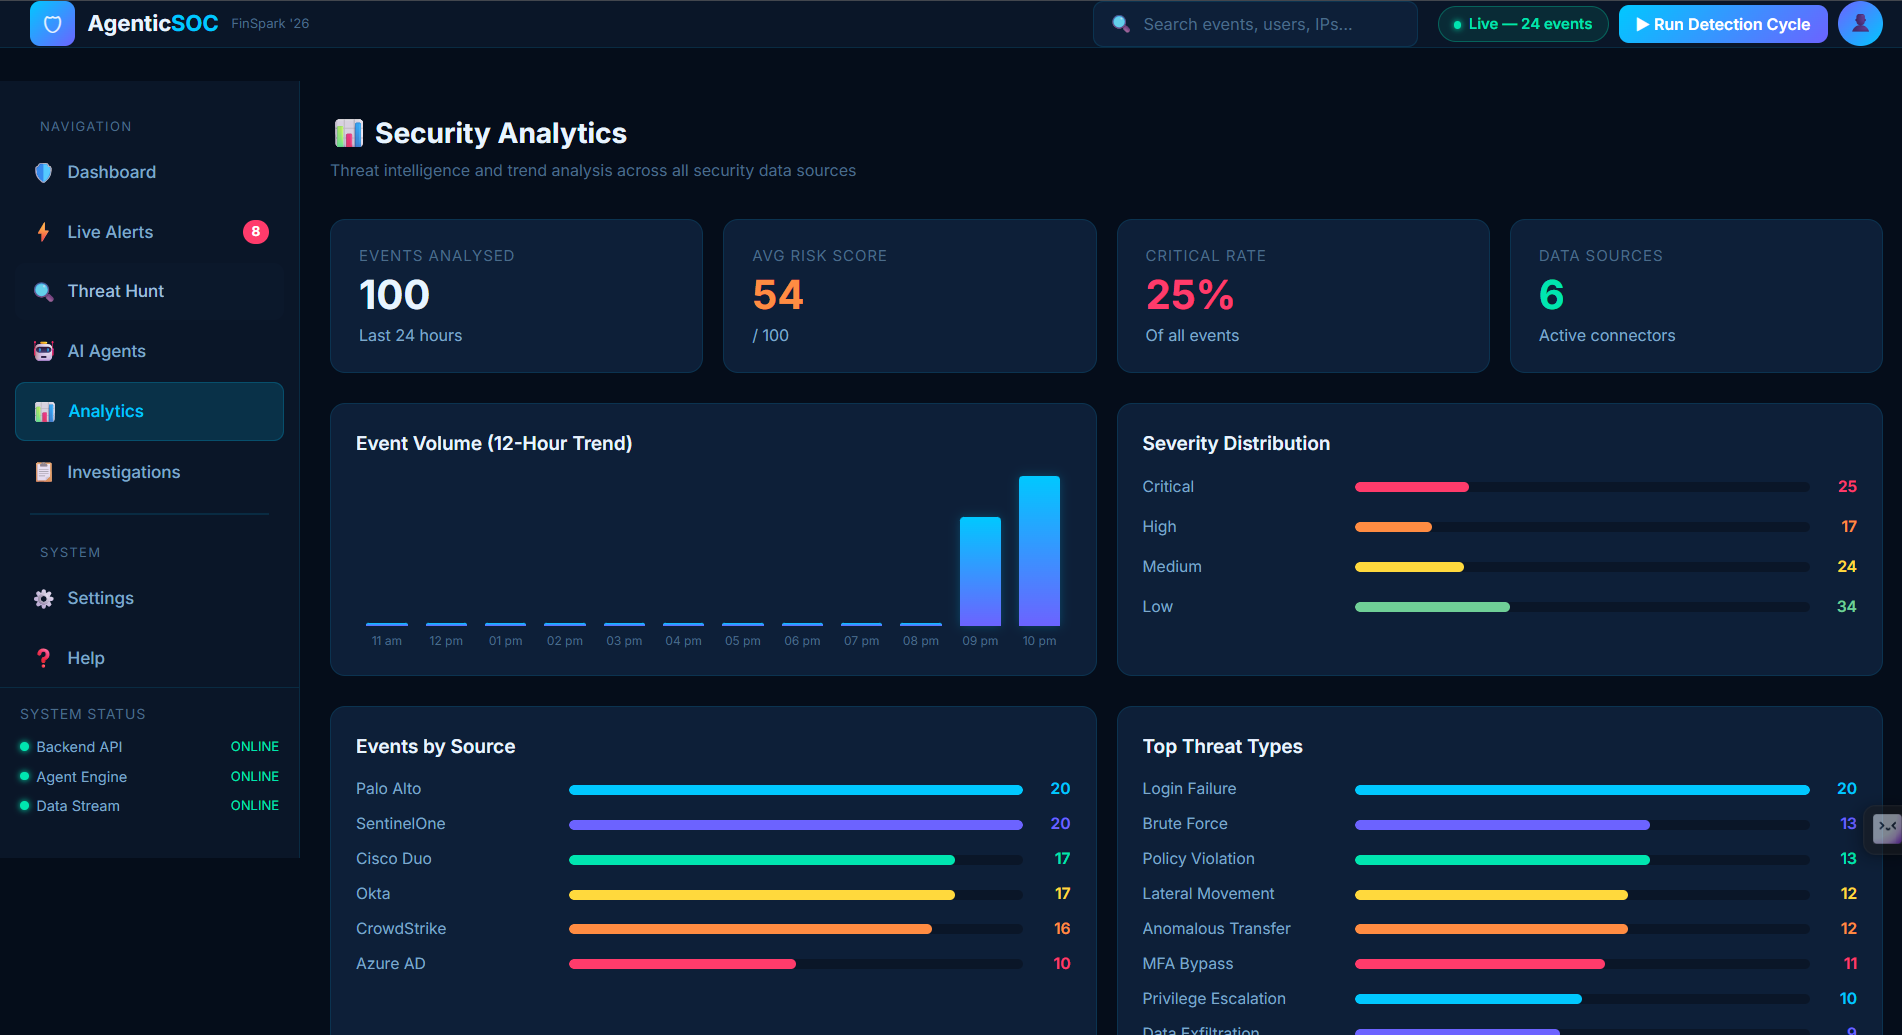
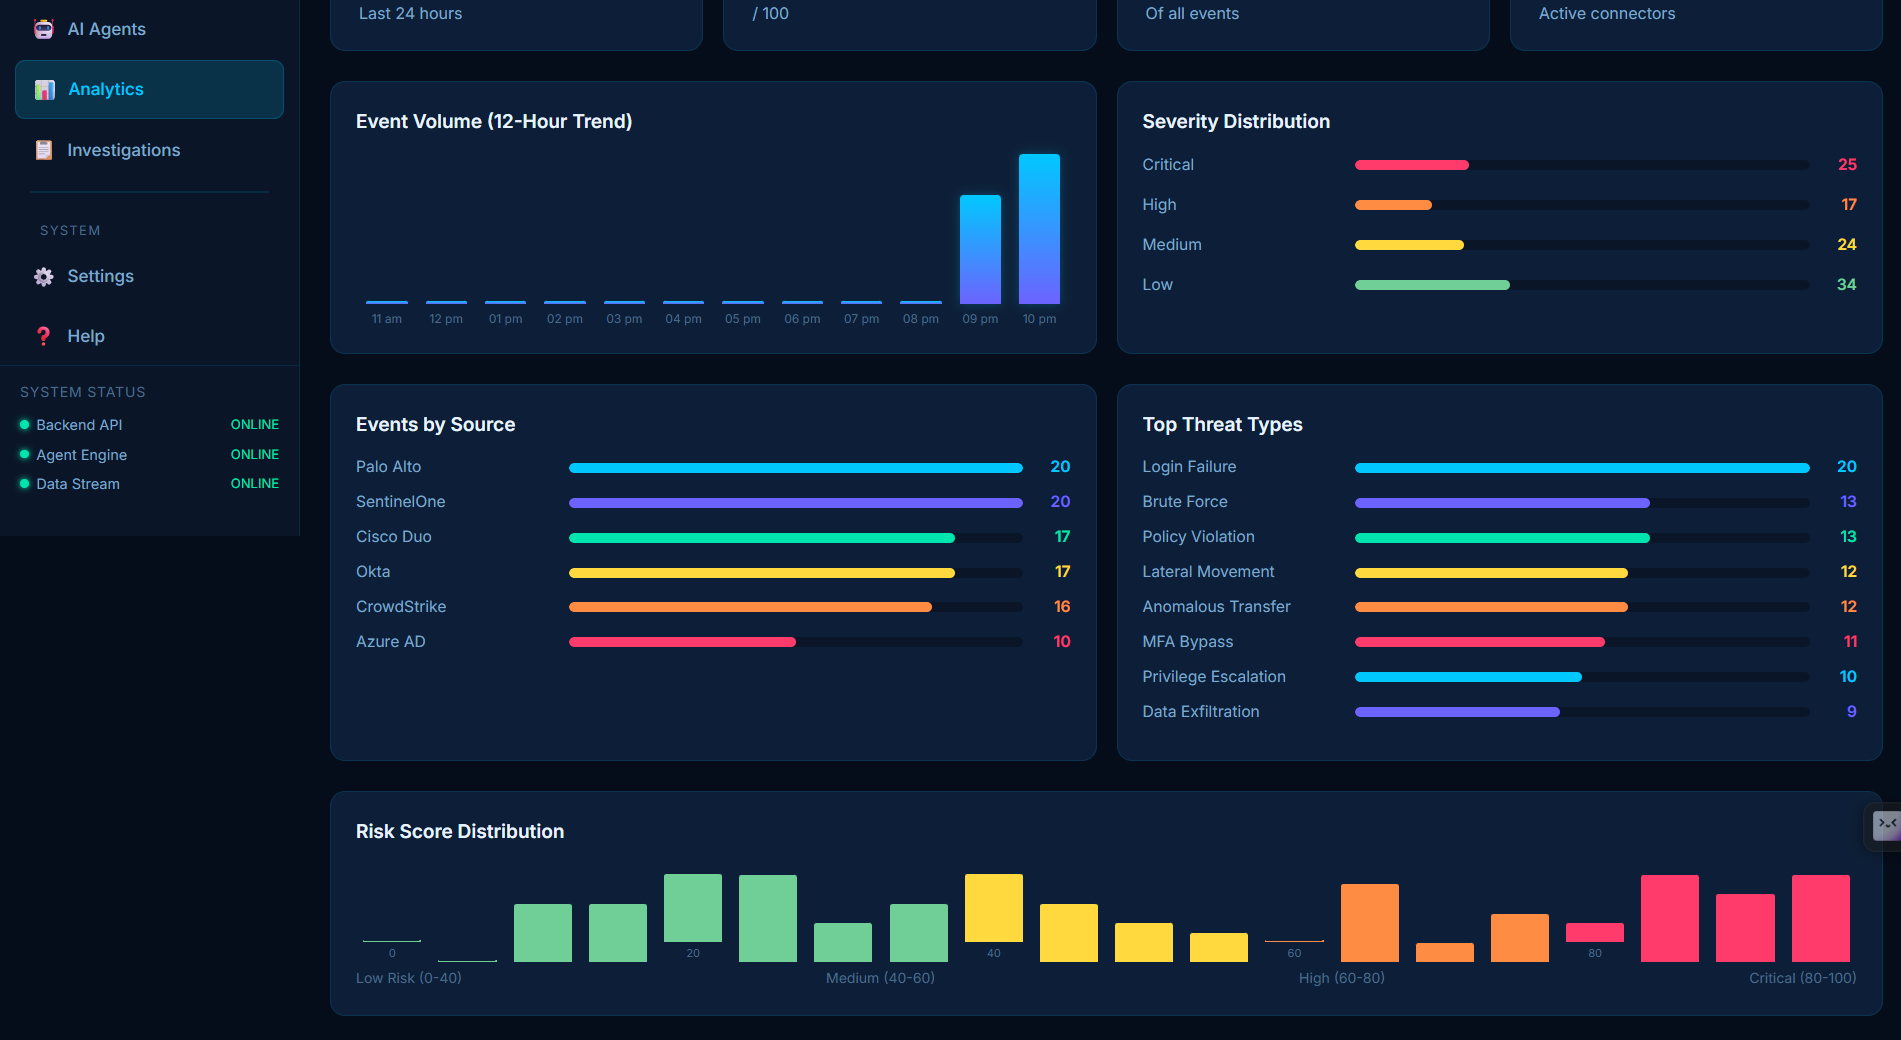
Analytics - Visualize threat trends, user behavior, and security insights.
-
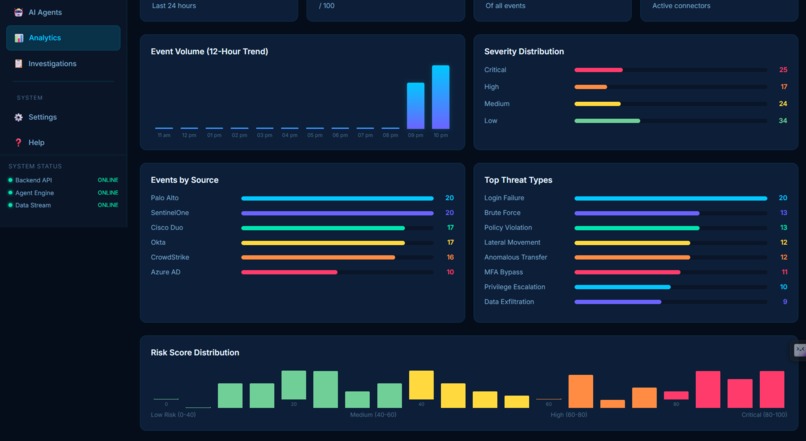
Analytics
-
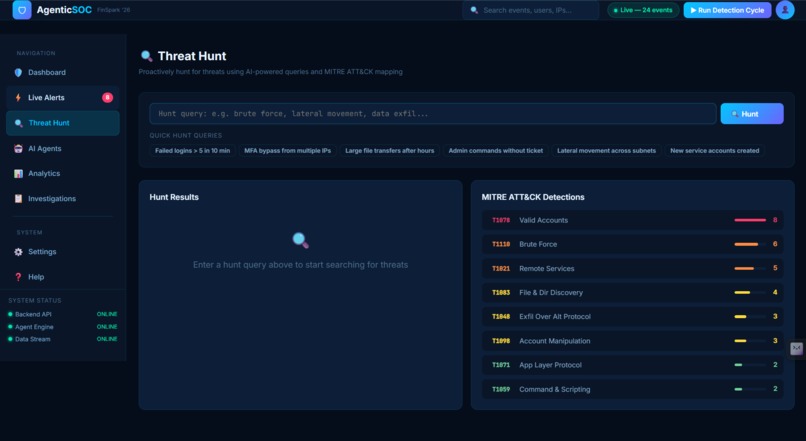
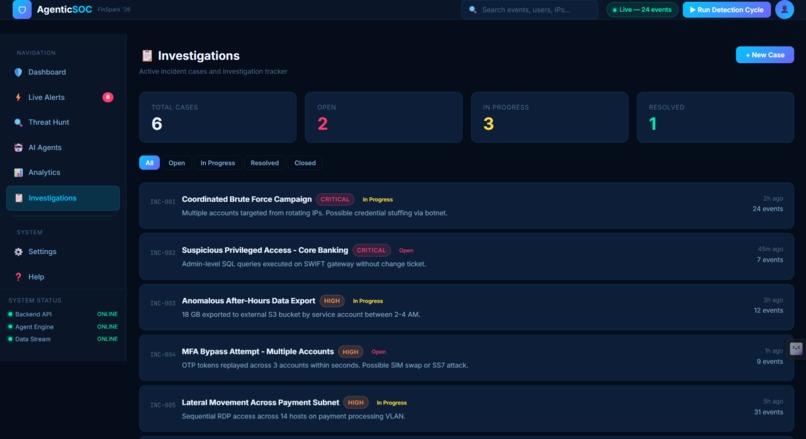
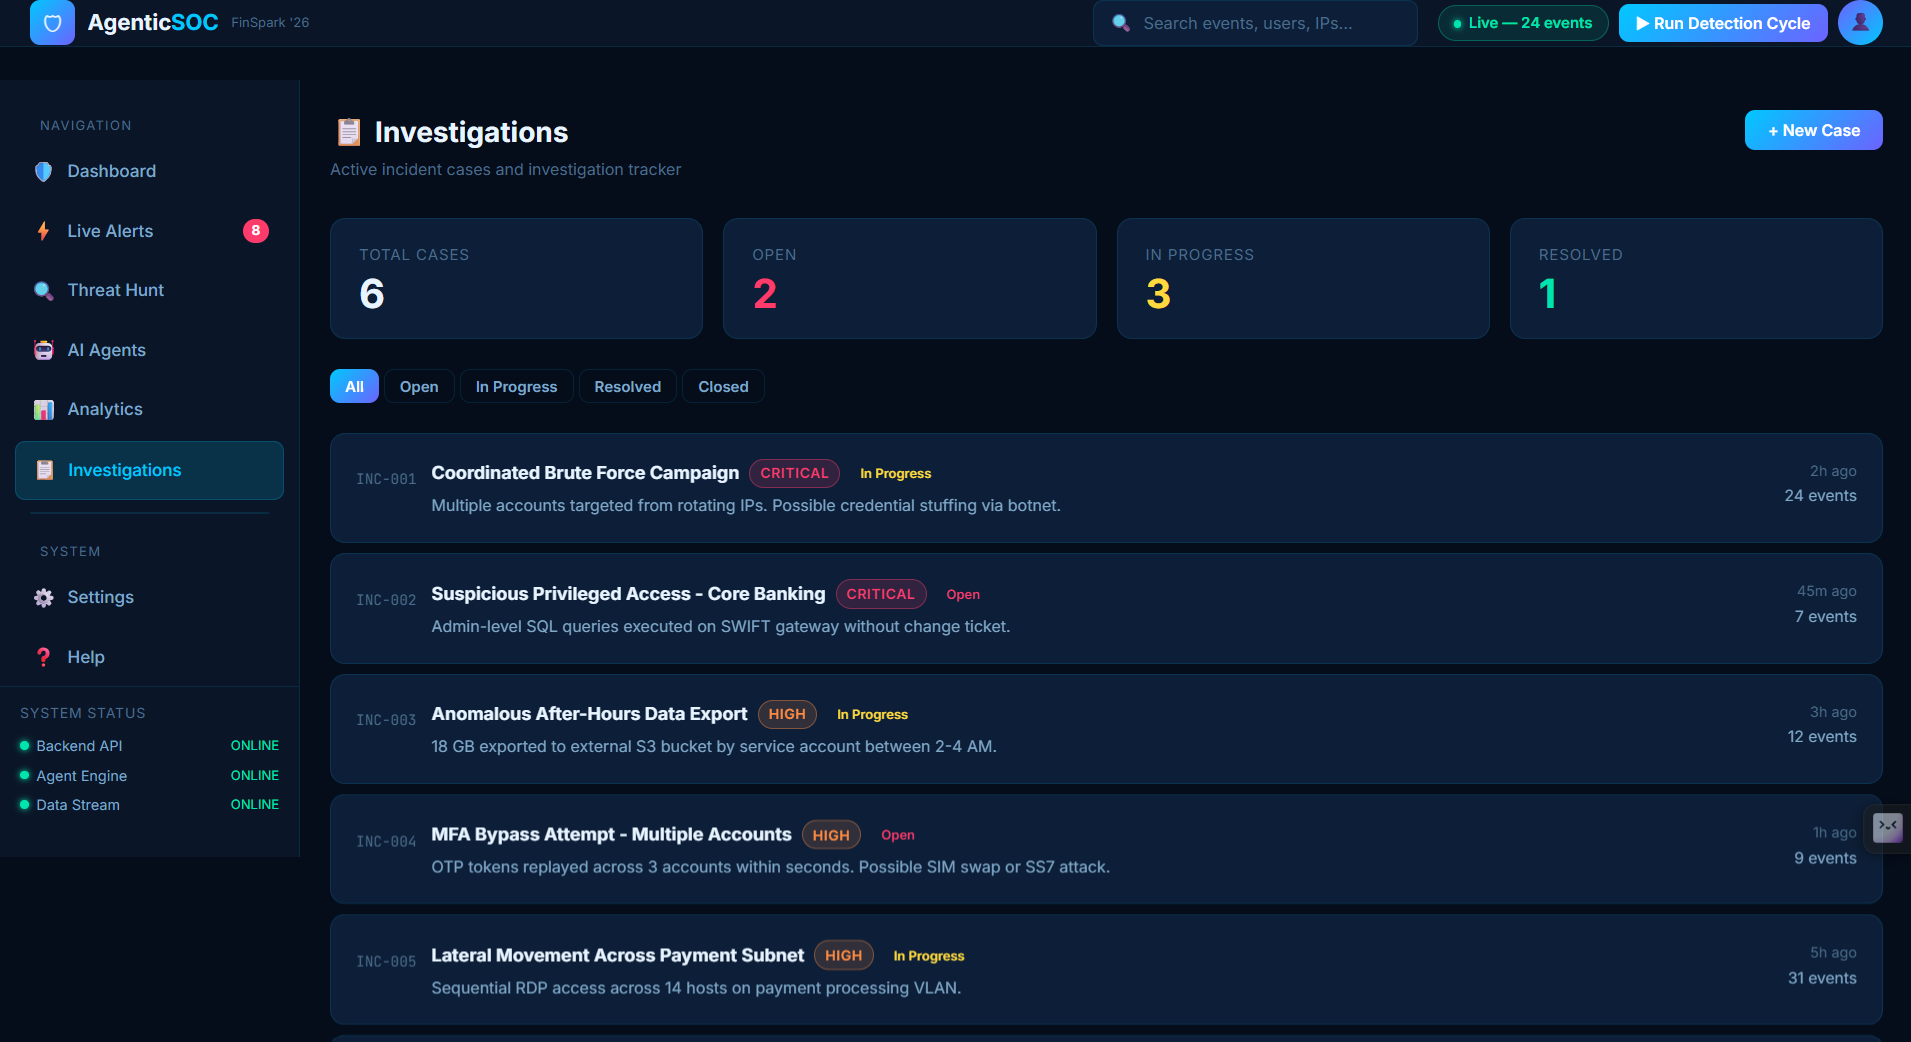
Investigations - Manage incidents with timelines, evidence, and response actions.
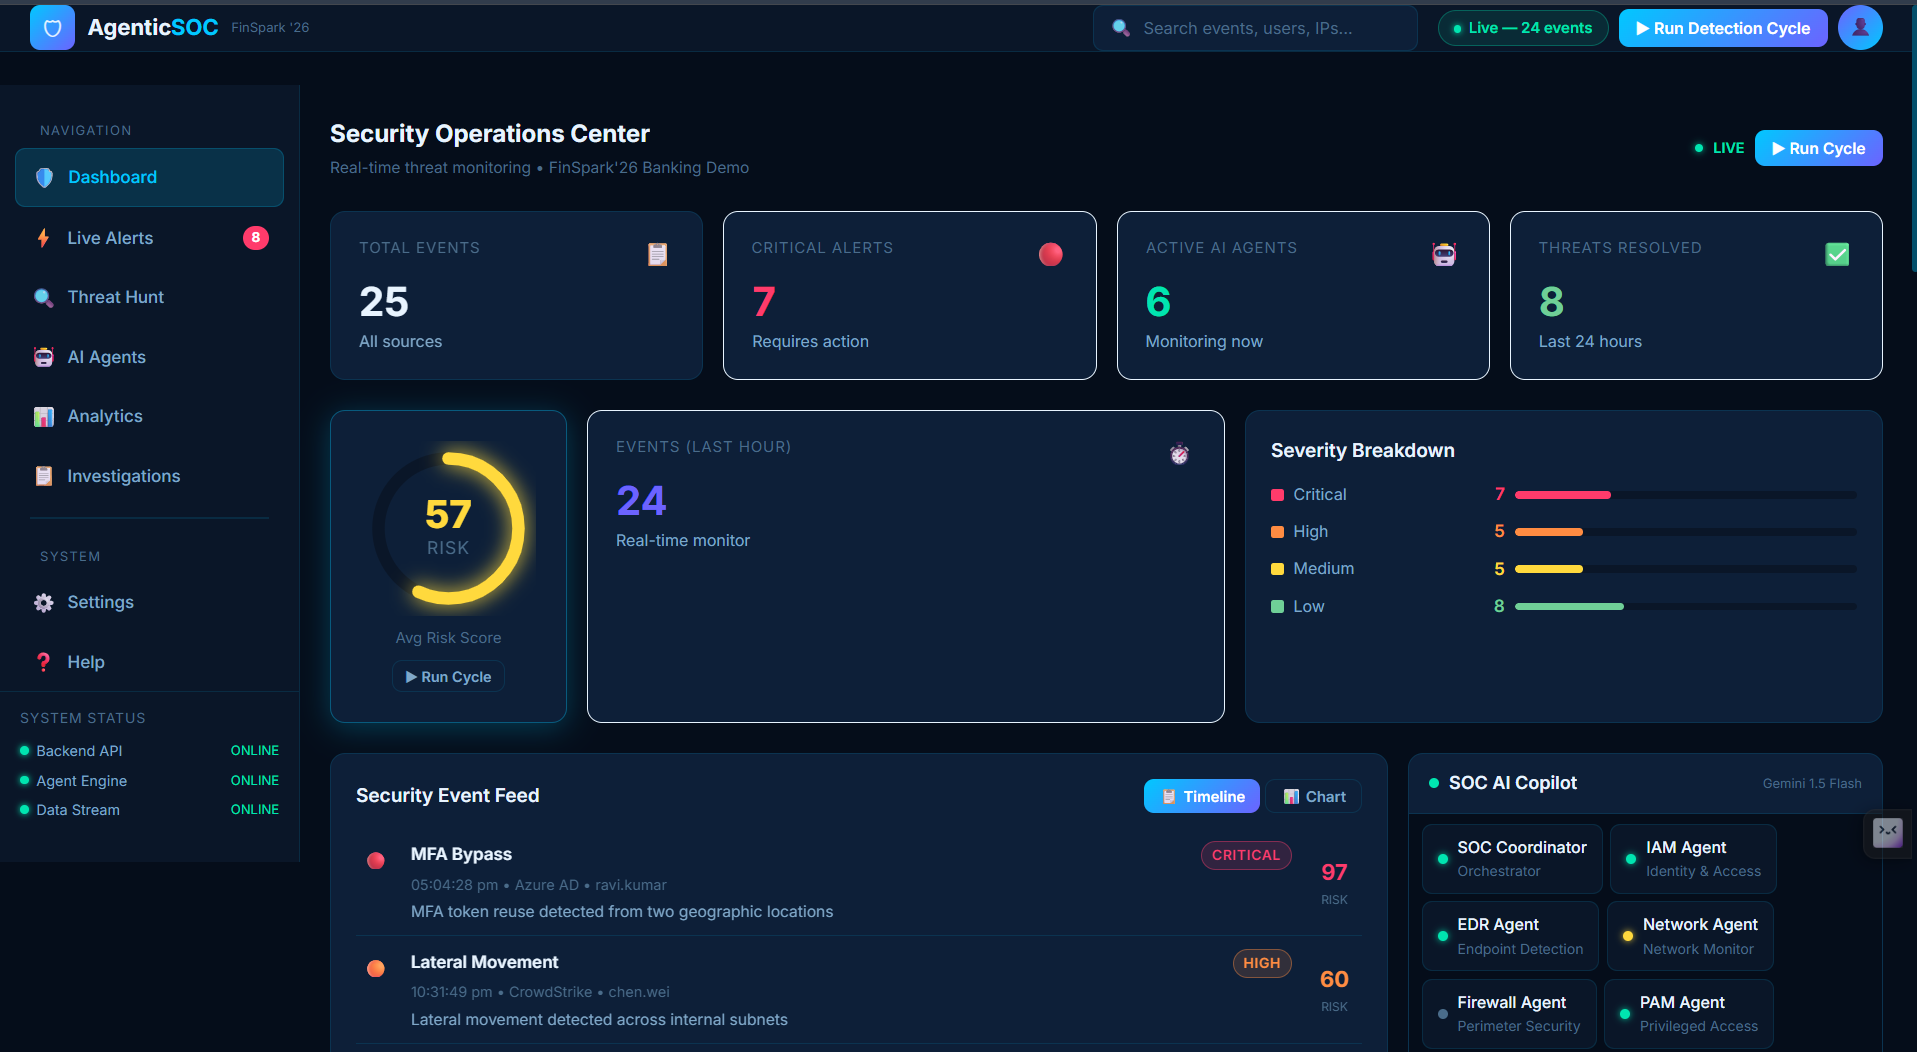
SOCShield
Inspiration
Modern banks rely on privileged accounts such as administrators, database administrators, and security administrators to manage critical systems. While these accounts are essential, they also represent one of the biggest cybersecurity risks. A compromised or malicious privileged user can bypass traditional security controls, access sensitive customer data, modify financial records, or disrupt banking operations.
Current Security Operations Centers (SOCs) generate thousands of alerts every day, making it difficult for analysts to identify genuine insider threats. This often leads to alert fatigue, delayed investigations, and increased response times.
SOCShield was inspired by the need to transform traditional SOC workflows into an intelligent, agent-driven security platform capable of detecting privileged access misuse and insider threats before they become major security incidents.
The Problem
Banking organizations continuously generate massive volumes of security logs from multiple systems, including:
- Active Directory
- Database Servers
- Endpoint Detection & Response (EDR)
- Network Infrastructure
- Banking Applications
- Authentication Services
Security analysts must manually correlate these logs to determine whether unusual activities indicate legitimate administrative work or malicious insider behavior.
The key challenges include:
- Detecting privileged account misuse
- Identifying insider threats
- Correlating security events across multiple systems
- Prioritizing critical incidents
- Reducing alert fatigue
- Accelerating incident investigation and response
Our Solution
SOCShield is an Agentic Security Operations Center designed specifically for banking environments.
Instead of relying solely on static rules, SOCShield combines intelligent automation with collaborative security agents to continuously monitor privileged accounts, analyze user behavior, correlate events from multiple security sources, calculate risk scores, and assist analysts with real-time investigations.
The platform transforms raw security logs into meaningful security intelligence, allowing banking SOC teams to detect, investigate, and respond to threats faster and more efficiently.
Key Features
- Privileged Access Monitoring
- Insider Threat Detection
- User & Entity Behavior Analytics (UEBA)
- Security Log Correlation
- Risk-Based Threat Prioritization
- Intelligent Incident Investigation
- Automated Alert Generation
- Interactive SOC Dashboard
- Real-Time Threat Monitoring
- Banking Security Analytics
System Workflow
- Security logs are collected from banking systems.
- Logs are normalized and correlated.
- User activities are analyzed for behavioral anomalies.
- Privileged account actions are continuously monitored.
- Risk scores are generated based on suspicious behavior.
- Security incidents are prioritized.
- Analysts receive actionable alerts.
- Investigation timelines are automatically generated.
- SOC teams can respond rapidly to security incidents.
How We Built It
SOCShield follows a modular architecture consisting of multiple intelligent components responsible for different stages of the security lifecycle.
The system integrates banking security logs, behavioral analytics, threat correlation, incident investigation, and security visualization into a unified platform.
A modern web dashboard provides security analysts with complete visibility into ongoing incidents while intelligent automation reduces manual effort during investigations.
Challenges We Faced
Building a banking-focused SOC platform required understanding how enterprise security infrastructures operate.
Some of the major challenges included:
- Simulating realistic banking security events
- Designing meaningful insider threat scenarios
- Correlating heterogeneous security logs
- Prioritizing alerts without excessive false positives
- Creating a dashboard that remains informative without overwhelming analysts
Balancing usability with enterprise-level security workflows was one of the biggest design challenges.
What We Learned
Throughout this project, we gained practical knowledge in:
- Banking cybersecurity architecture
- Security Operations Center (SOC) workflows
- Privileged Access Management (PAM)
- User & Entity Behavior Analytics (UEBA)
- Threat detection pipelines
- Incident response processes
- Security dashboard design
- Enterprise cybersecurity best practices
More importantly, we learned that effective cybersecurity is not only about detecting attacks—it is about providing analysts with the right information at the right time to make informed decisions.
What's Next for SOCShield
Future enhancements include:
- Live SIEM integration
- Active Directory integration
- MITRE ATT&CK mapping
- AI-powered incident summarization
- Automated remediation playbooks
- Threat intelligence integration
- Compliance reporting
- Multi-bank deployment support
- Predictive insider risk analytics
Our vision is to evolve SOCShield into a production-ready Agentic Security Operations Center capable of supporting financial institutions with intelligent, scalable, and proactive cyber defense.
Built With
- chart.js
- docker
- fastapi
- flow
- github
- jwtoauth
- leaflet.js
- pandas
- postgresql
- python
- react
- render
- restapi
- scikit-learn
- siem
- splunk
- supabase
- tailwind
- typescript
- vercel


Log in or sign up for Devpost to join the conversation.