-
-
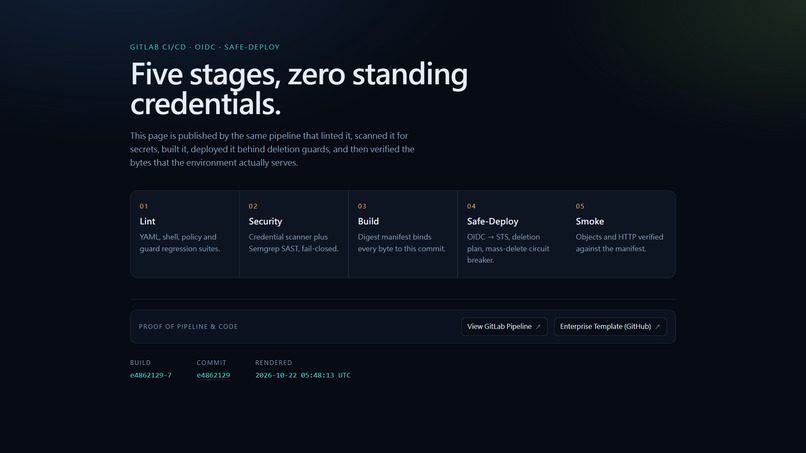
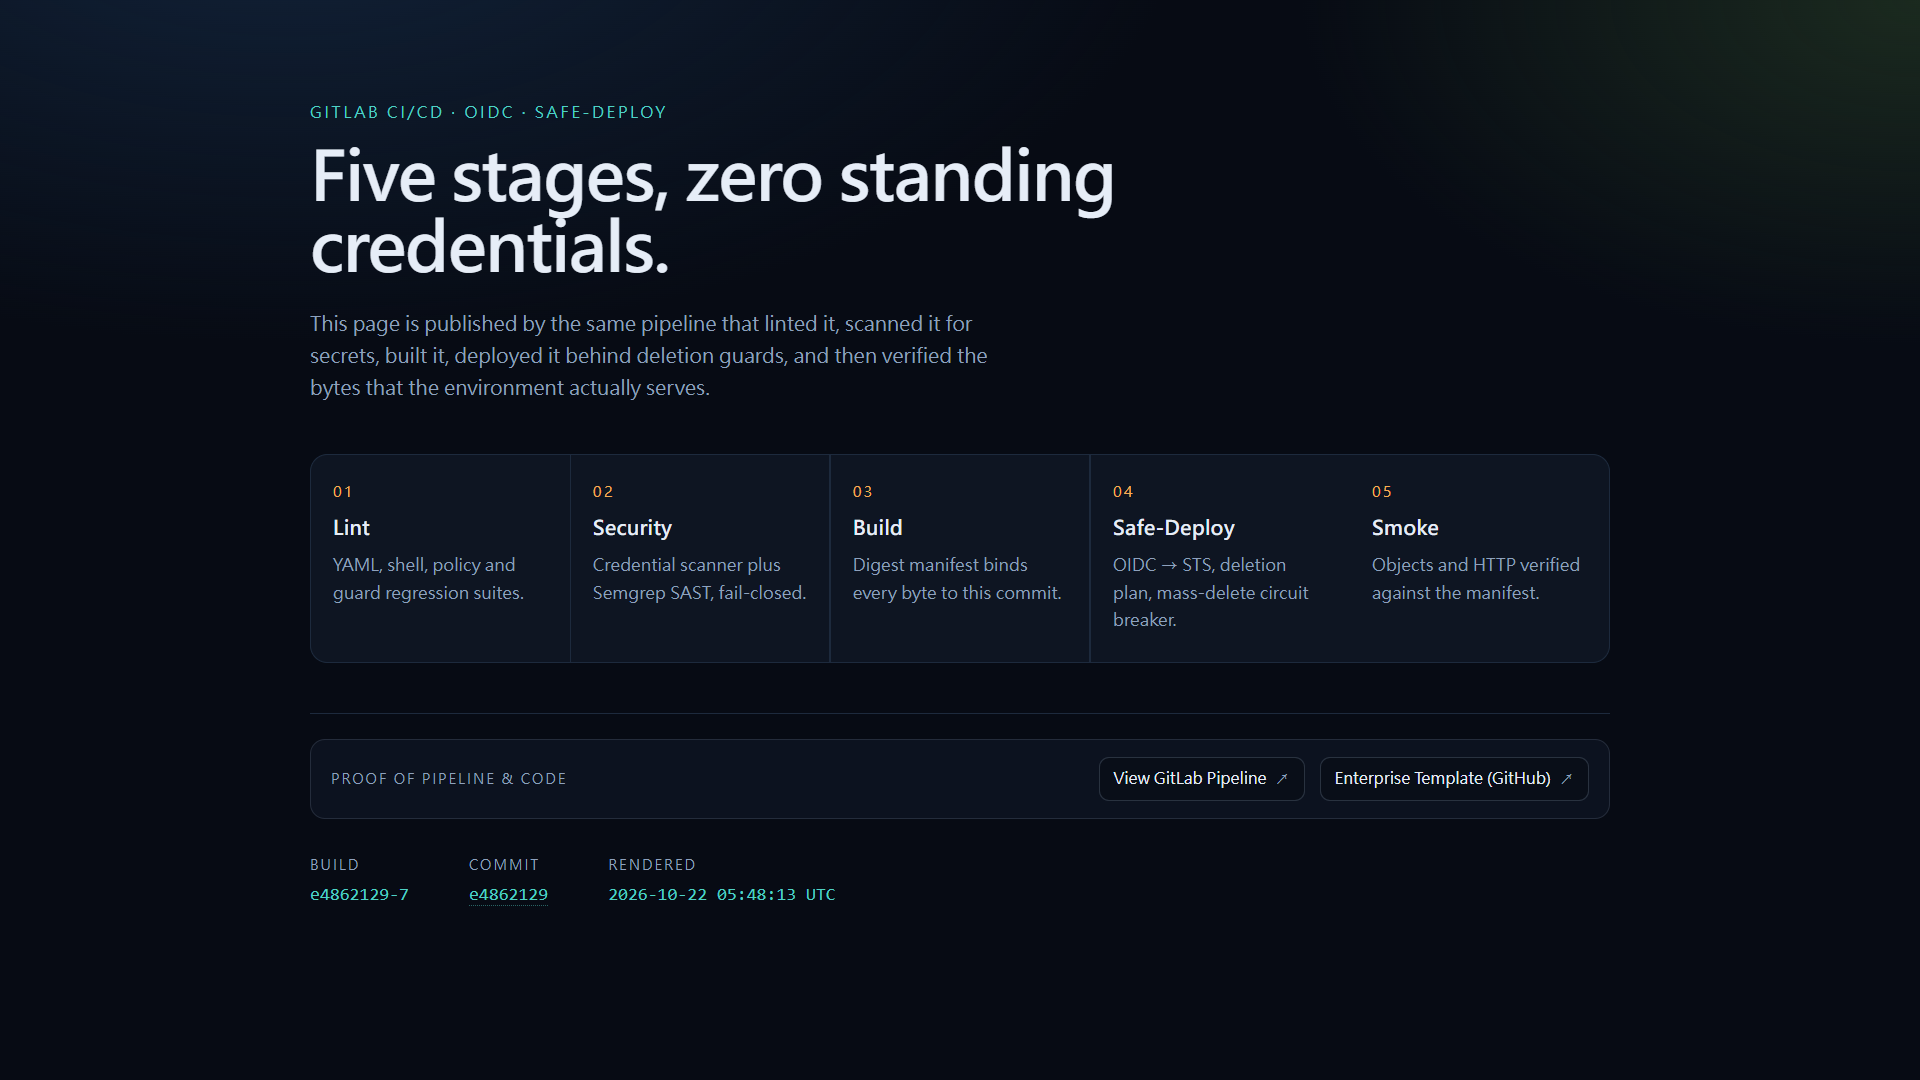
Live GCS endpoint proving immutable deployment matching commit e4862129
-
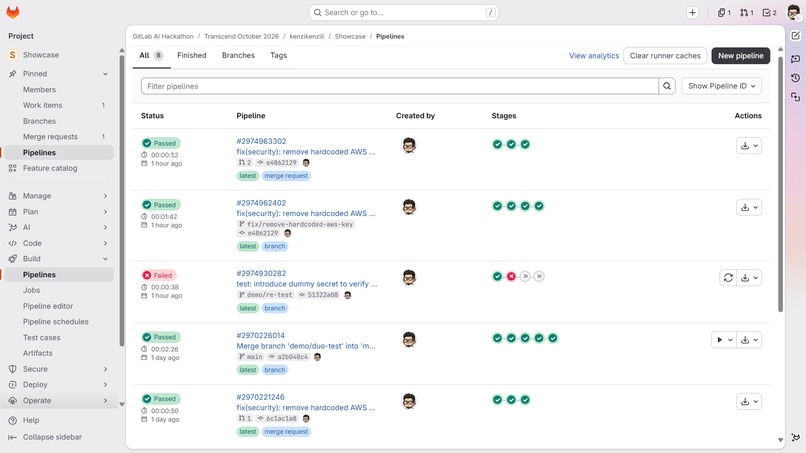
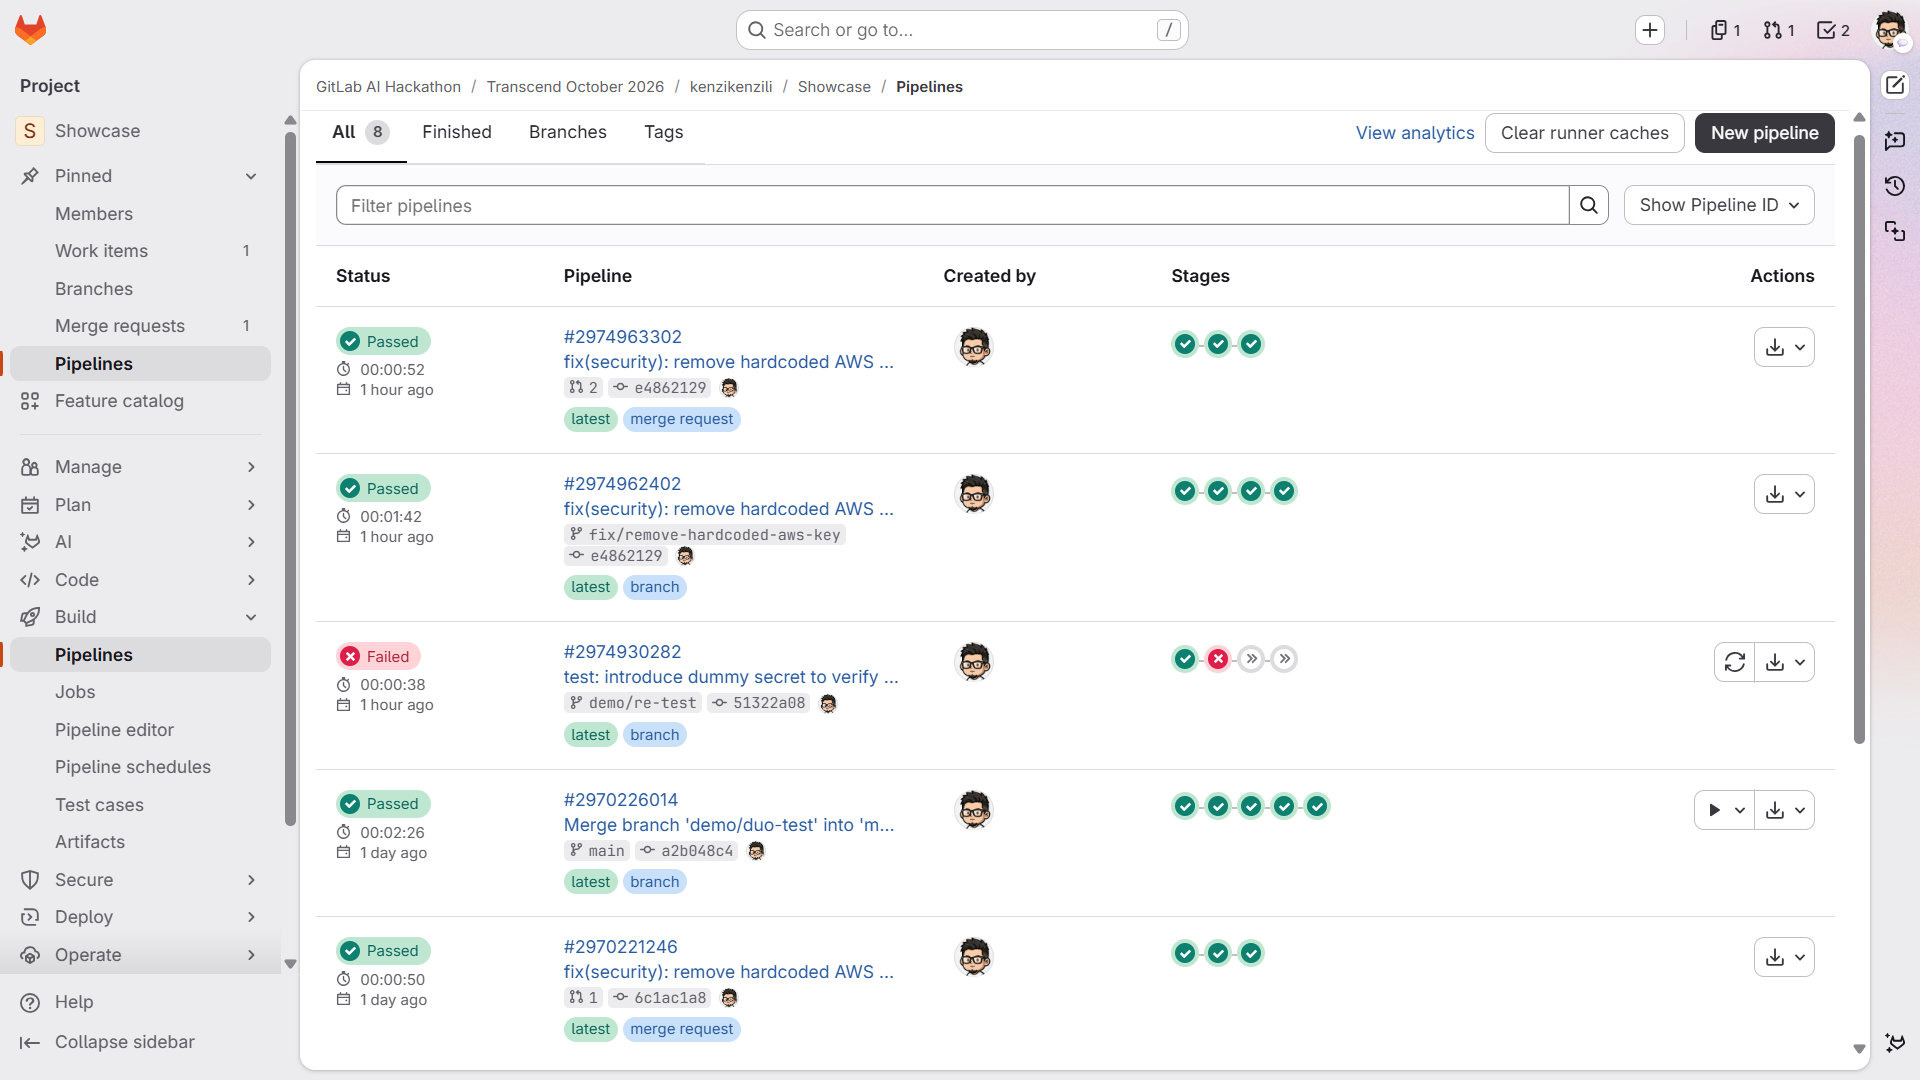
GitLab pipeline history showing SAST fail-closed triage and clean remediation
Inspiration
Modern DevSecOps is caught in an operational bottleneck: security pipelines are strict and fail-closed, but resolving alerts still requires painful manual triage. When a pipeline halts due to an accidental secret commit, developers must switch context, identify the vulnerability, redact the key, update configuration bindings, and manually submit a Merge Request.
We asked: What if the pipeline itself had an intelligent, trusted first responder?
By leveraging GitLab Duo Agent Platform (powered by Claude 3.5 Sonnet) within a zero-credential cloud architecture, we created a paradigm of "Supervised Autonomy"—an autonomous workflow where AI handles root-cause analysis and code remediation, while human operators retain absolute governance and merge approval.
What it does
Our project showcases an end-to-end self-healing CI/CD lifecycle backed by Google Cloud Platform:
Zero Standing Credentials: The repository contains zero long-lived static cloud keys or private certificates. Authentication to GCP is performed purely via OIDC tokens exchanged dynamically through Workload Identity Federation (WIF).
Fail-Closed Gatekeeper: When a simulated hardcoded AWS access key was committed to
demo-site/test-token.js, our Semgrep SAST security stage immediately terminated pipeline#2974930282, blocking compromised code from advancing.Autonomous Root Cause Analysis: Rather than alerting a human engineer to fix boilerplate errors, GitLab Duo intervened autonomously. Duo analyzed the pipeline failure logs, identified the Semgrep rule violation, refactored the file to read securely from runtime environment variables (
AWS_ACCESS_KEY_ID), cleaned obsolete rehearsal notes, committed the patch, and opened Merge Request!2.Supervised Autonomy & Verification: The human engineer reviews the MR and inspects the verification pipeline (
#2974963302). Seeing a clean security scan with no new vulnerabilities, the engineer authorizes the merge.Immutable Deployment Proof: Upon merge, the production pipeline deploys the site directly to Google Cloud Storage (GCS). Refreshing the live endpoint verifies deployment proof: the served
Built With
- claude-3-5-sonnet
- devsecops
- gitlab
- gitlab-ci
- gitlab-duo
- google-cloud
- oidc
- sast
- semgrep
- workload-identity-federation

Log in or sign up for Devpost to join the conversation.