-
-
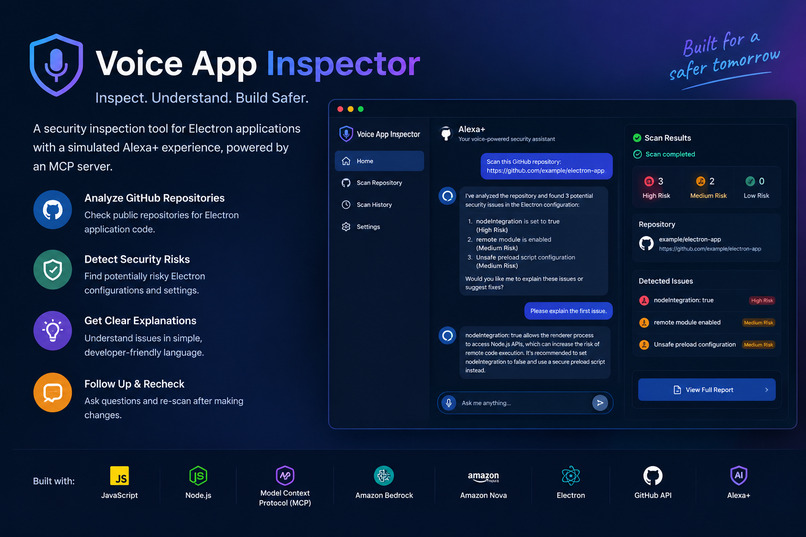
Alexa+-inspired security scanner for Electron apps, powered by MCP.
Developers often build Electron applications without realizing that certain configurations can introduce security risks. I wanted to create a simple, conversational tool that helps developers inspect their applications and understand potential security issues without needing to be security experts.
What It Does
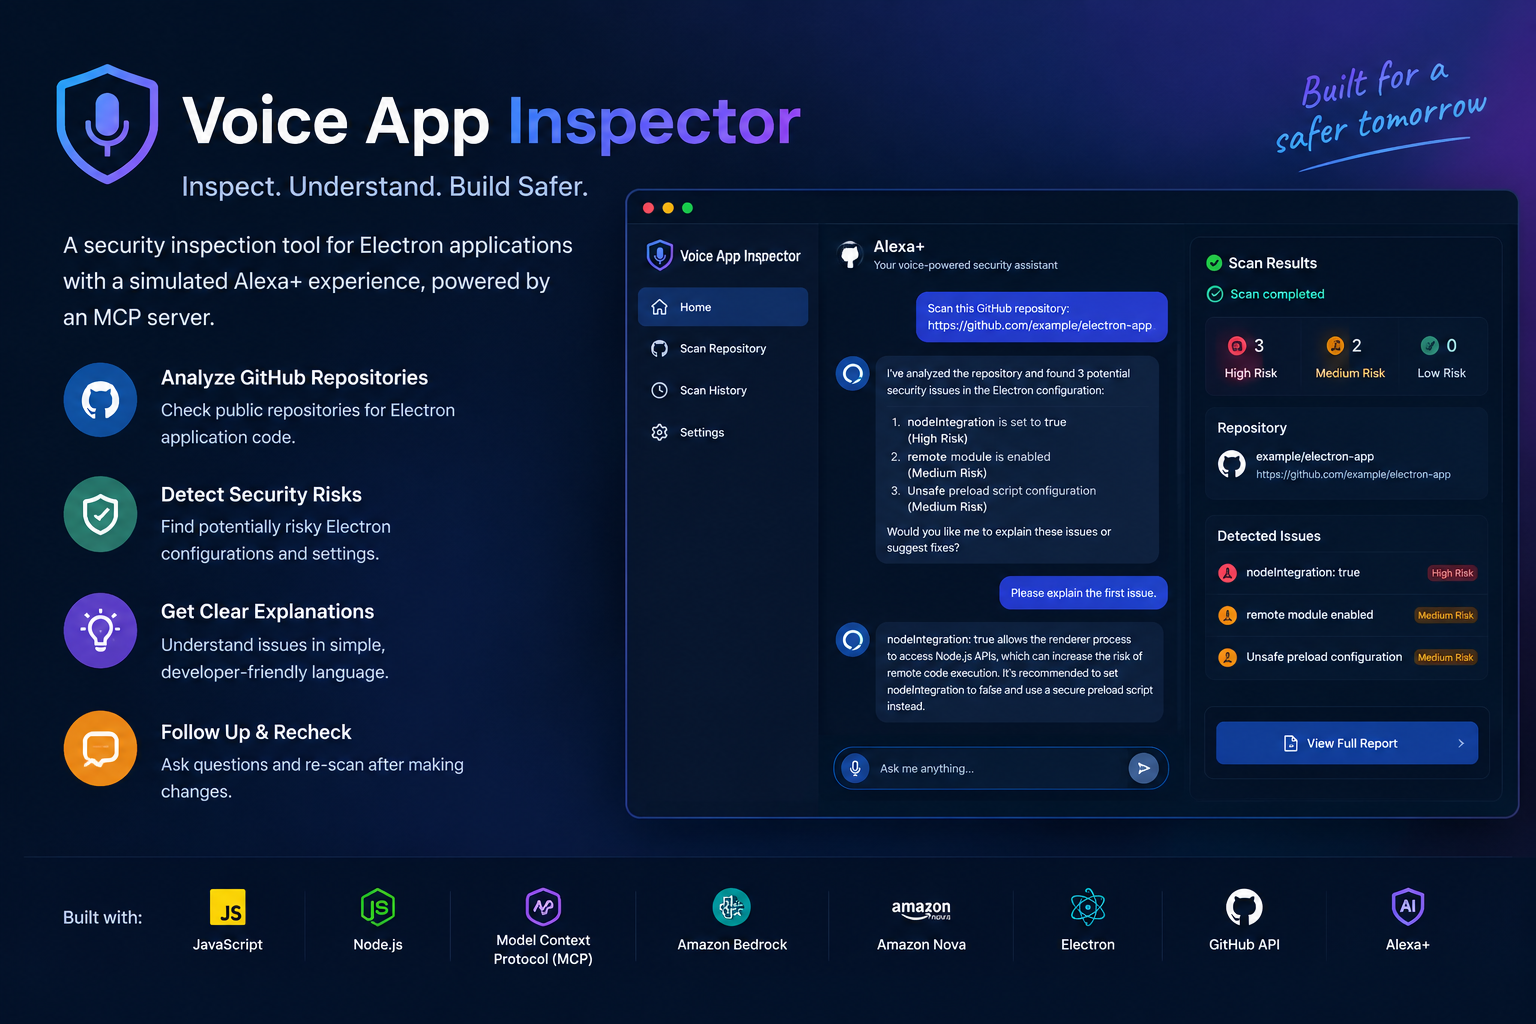
Voice App Inspector is a security inspection prototype with a simulated Alexa+ conversational interface backed by an MCP server. Users can provide a public GitHub repository link to inspect supported application source files for potentially risky Electron settings.
The project can:
- Analyze supported files from public GitHub repositories.
- Identify potential security risks in Electron configurations.
- Explain findings in simple, developer-friendly language.
- Suggest possible improvements and help users understand what to check next.
- Support follow-up questions about an inspected project.
Static analysis has limitations, so a clean scan does not guarantee that an application is completely secure.
How I Built It
I built the project using JavaScript and an MCP server that exposes tools for application inspection. I added a simulated Alexa+ conversational experience to make security checks easier to understand and interact with.
I also tested Amazon Bedrock Nova Micro using the AWS CLI. The model responded successfully to a test prompt. This verified model connectivity, while the application's runtime integration must be evaluated separately.
Challenges
One major challenge was handling public GitHub repository URLs and extracting project files correctly. Another was making scan results understandable to developers who may not have a security background. I also worked on validating the MCP server workflow and testing the AWS Bedrock Nova Micro connection.
What I Learned
This project helped me learn more about MCP-based tool workflows, repository inspection, Electron security considerations, and testing Amazon Bedrock models. It also taught me that security tools should communicate their findings clearly and avoid claiming that an application is completely safe based on a limited scan.
What's Next
Future improvements include broader security rules, deeper dependency analysis, more comprehensive repository support, and verified integration of AI-generated explanations into the application.


Log in or sign up for Devpost to join the conversation.