1. Project Name - VELORA
2. Challenge Category - Software & Technology
3. The Problem
- Wireshark is a tool used by computer network professionals and students to analyse network packets.
- It maintains protocol information, IP address information, sequence numbers, etc., regarding the packets.
- However, it is extremely difficult for beginners and even professionals to analyse due to the overwhelming number of packets present and the simultaneous information overload.
- It is extremely excruciating to traverse packet by packet to figure out the actions happening in packets.
- It does not give the larger picture of the session activity, and it is incredibly difficult to analyse the relationship between various packets.
- Even with filters, it is required to have elaborate domain and syntax knowledge in order to navigate through the packets.
- This is a cause for concern for network analysts, and it hinders incident response and digital forensics.
- There are very few tools that analyse Wireshark outputs, and the existing tools do not attempt to understand the overall session activity and explain the activity.
4. The Solution
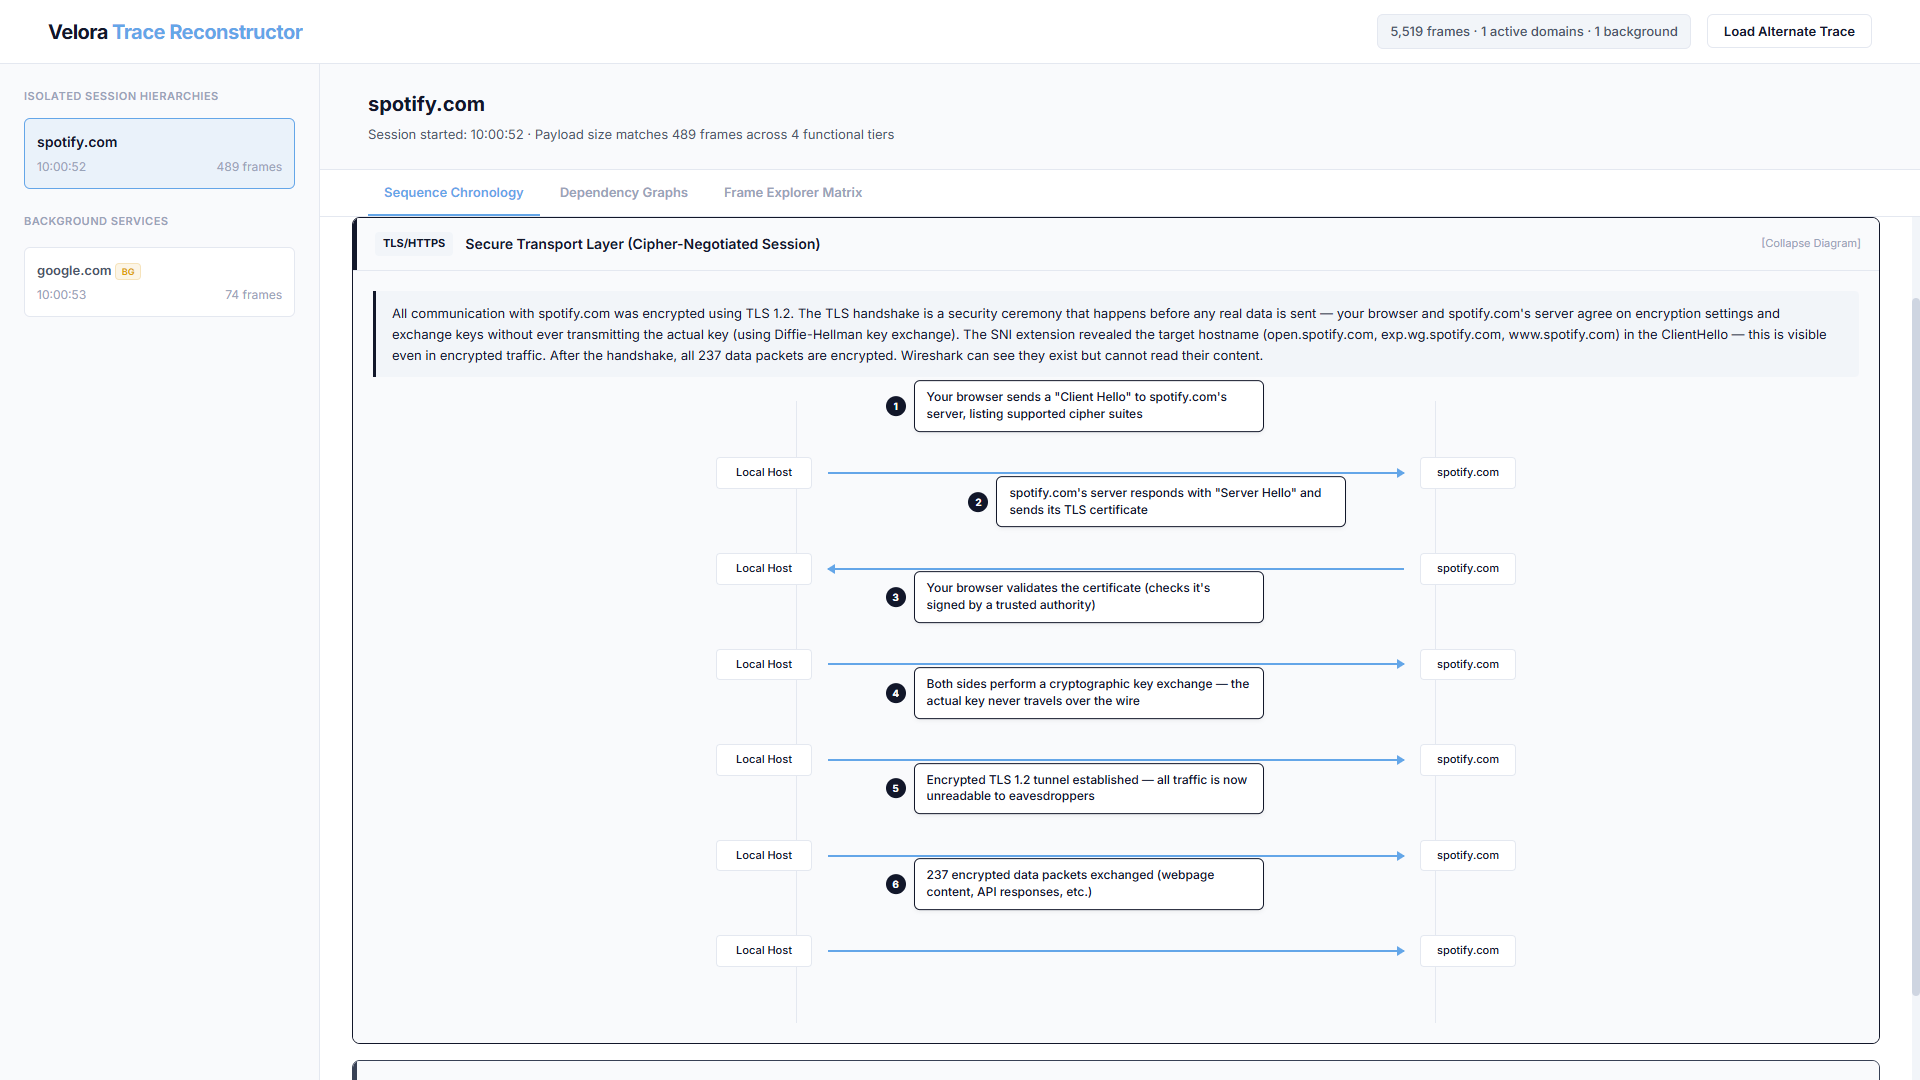
- This solution - Velora, is a PCAP intelligence and visualisation platform.
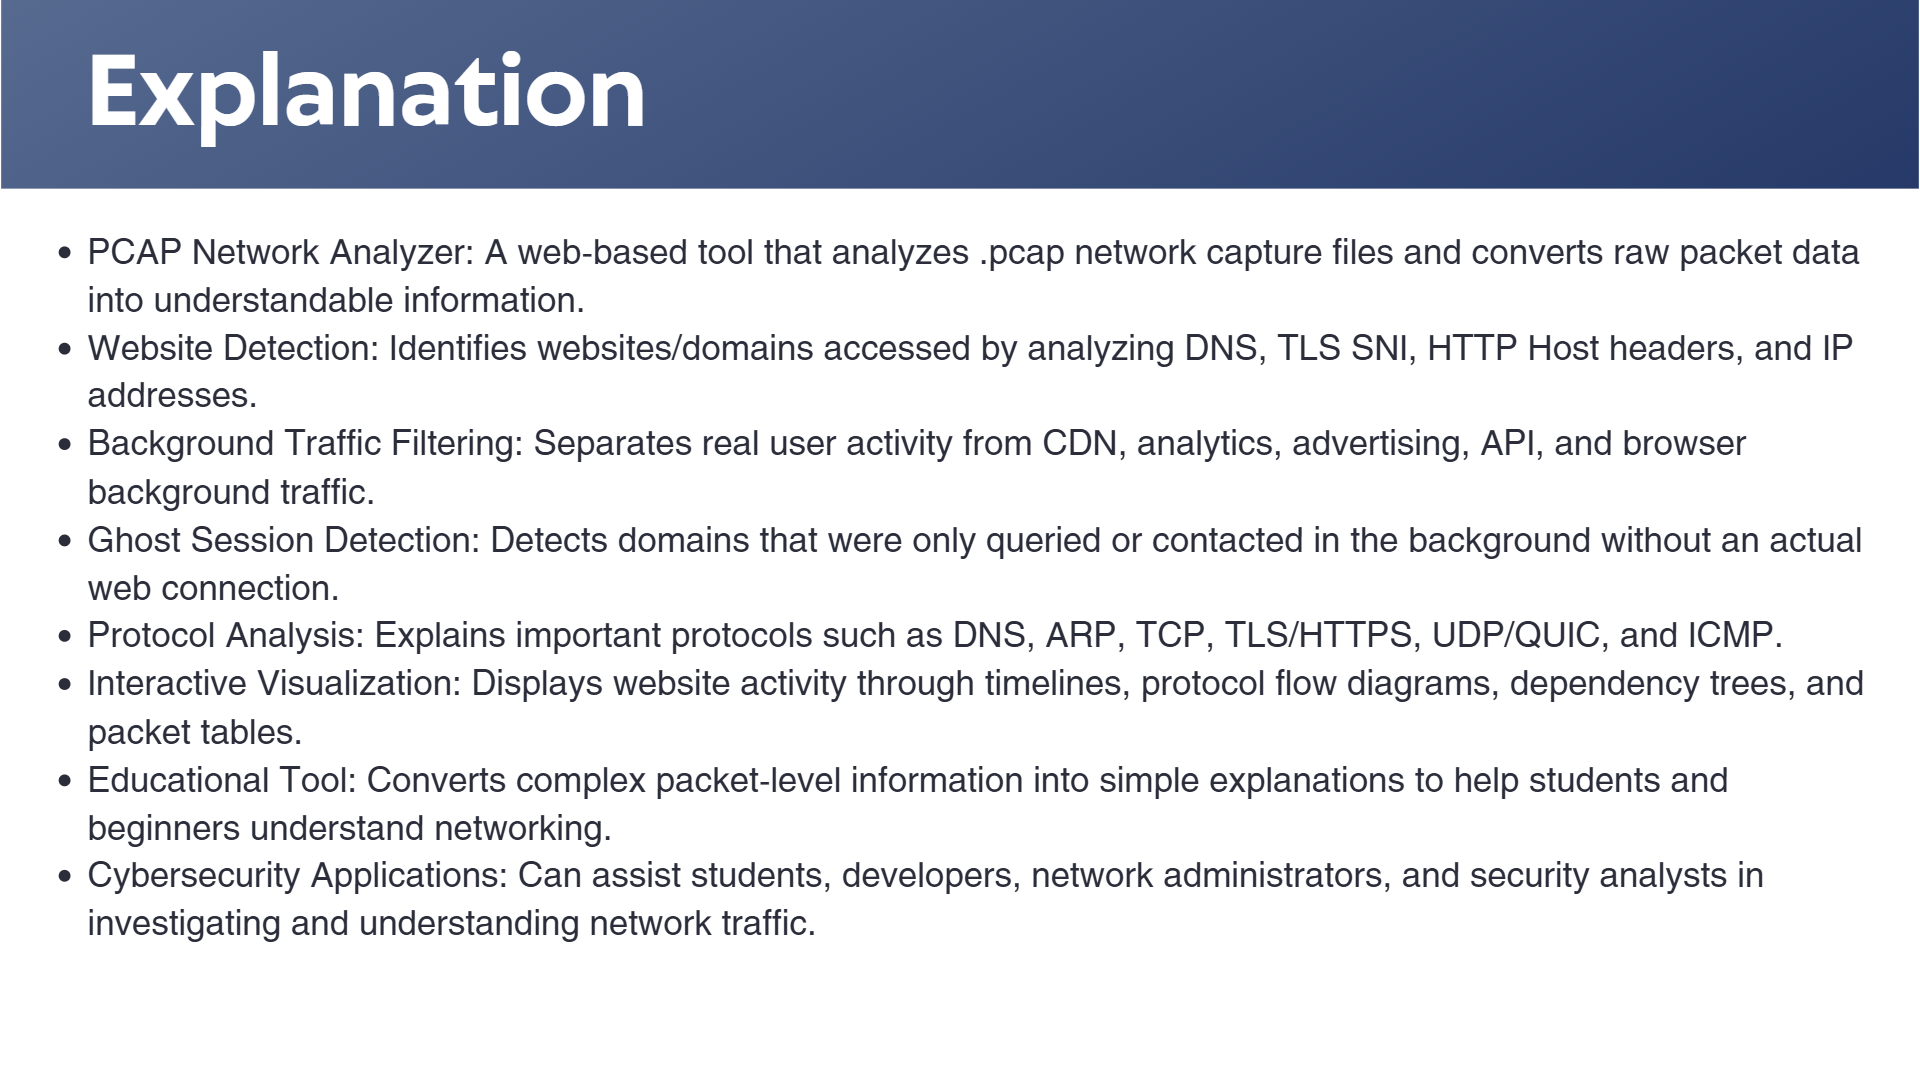
- It aims at improving packet analysis by converting the complex raw packet data obtained from Wireshark into a structured, human-readable representation of network activity, and provides packet evidence for the same.
- For each browsing session performed by the user, thousands of packets are sent, involving multiple protocols, which are incomprehensible without detailed domain knowledge and take a lot of time to analyse.
- To prevent this, browsing sessions are categorised by the website visited, and all the packets related to the particular website are grouped together.
- The background activity (Background activity refers to any network packet exchange that does not stem from direct, user-initiated navigation in an active browser tab or terminal window.) is classified separately and not included with the intended browsing activity.
- The project creates a layered interpretation of the network event - Packet, Protocol, Connection, Domain, Session, Background/Intent Classification, and Client/Application Attribution.
- That makes the system more useful for investigation and education and is a new approach to bringing browser history-based categorisation into Wireshark analysis.
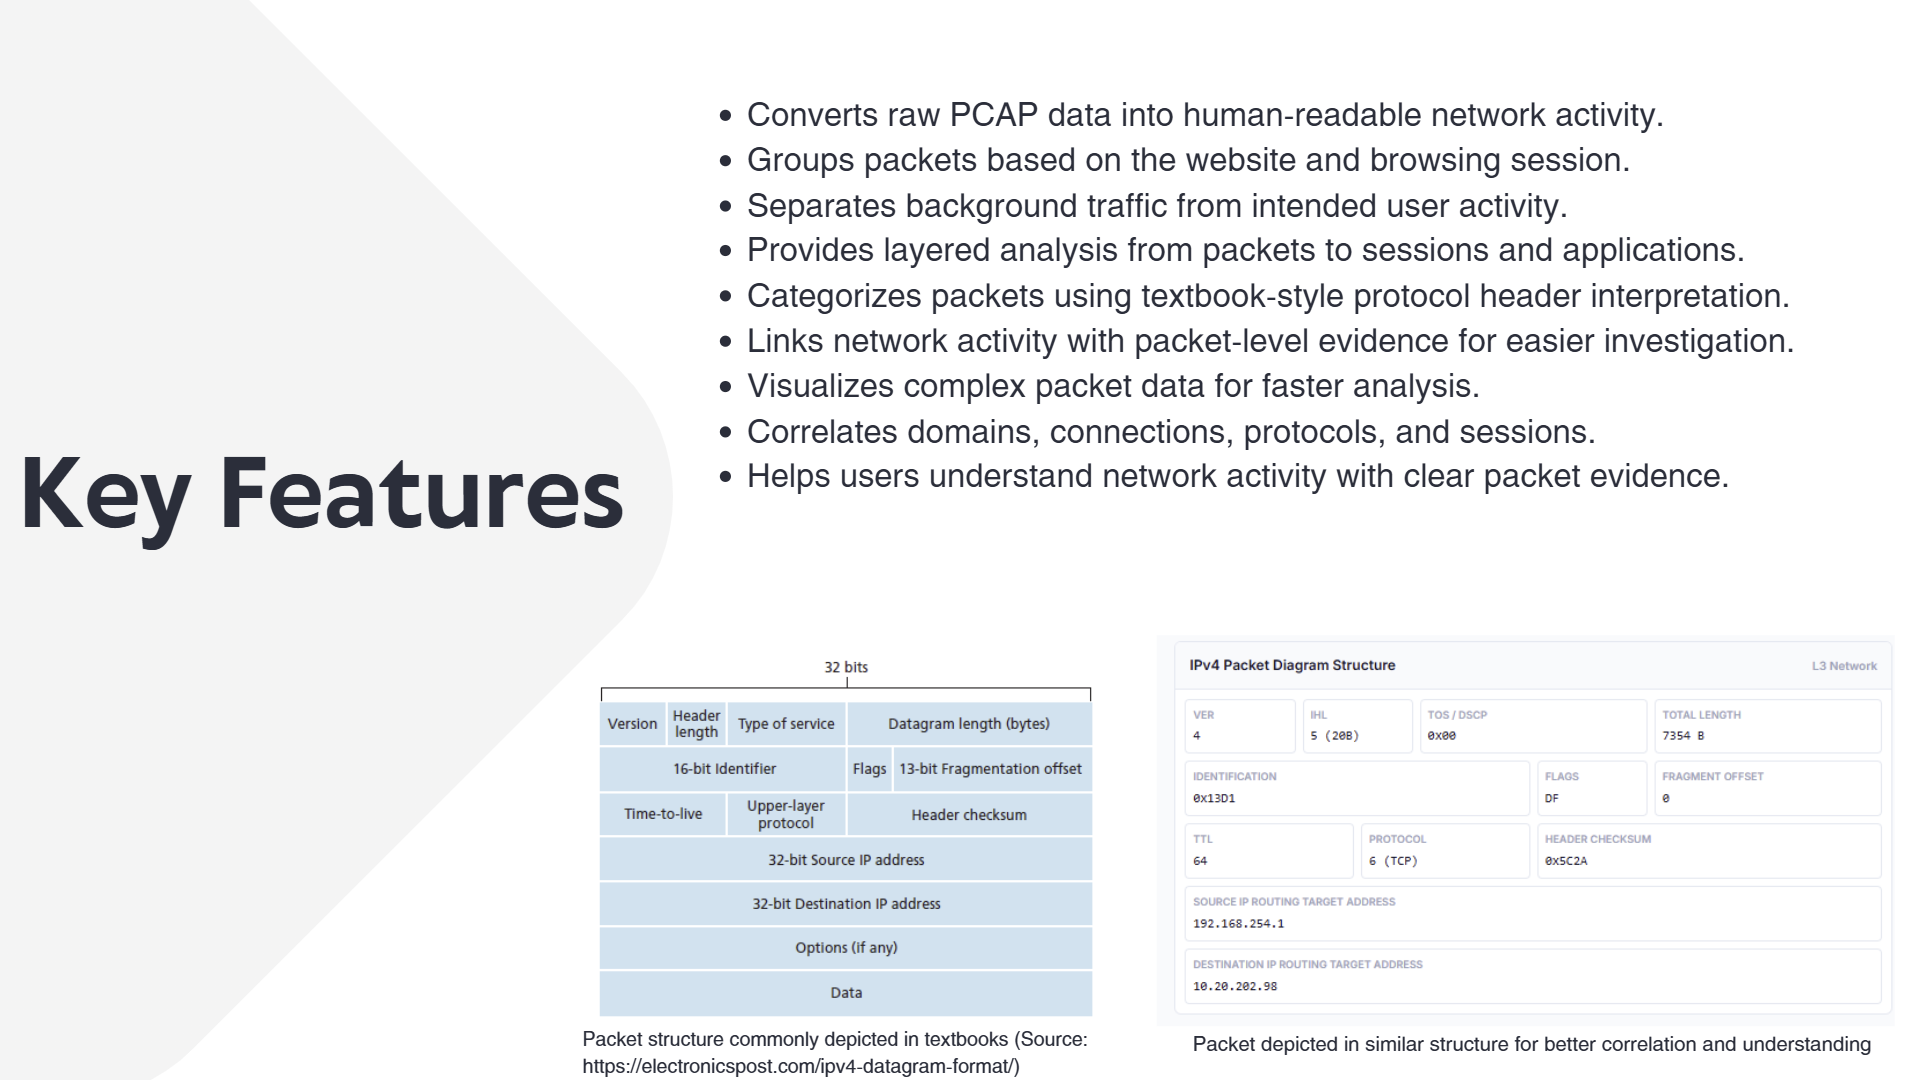
- The individual packets themselves are categorised according to the textbook images of the packet headers, which makes understanding and correlation easier.
5. Development & Process
- First, the PCAP packets are collected, and their contents are extracted.
- Then, the DNS responses are used for domain reconstruction, following which infrastructure filtering is performed in order to reduce the noise in domain detection.
- Next, ghost-session analysis is performed, which checks whether a domain merely appeared in DNS/background traffic or whether there was evidence of an actual web connection.
- Then, protocol analysis is performed, and it generates explanations for various protocols instead of merely presenting packet numbers.
- All the aggregated results are presented in a very convenient and understandable manner.
6. Demonstration
This is the deployed version of the project - https://velora-pcap-intelligence.vercel.app/ This is the GitHub repository link - https://github.com/SharGIT-prog/Velora_PCAP_Intelligence
7. Project Presentation
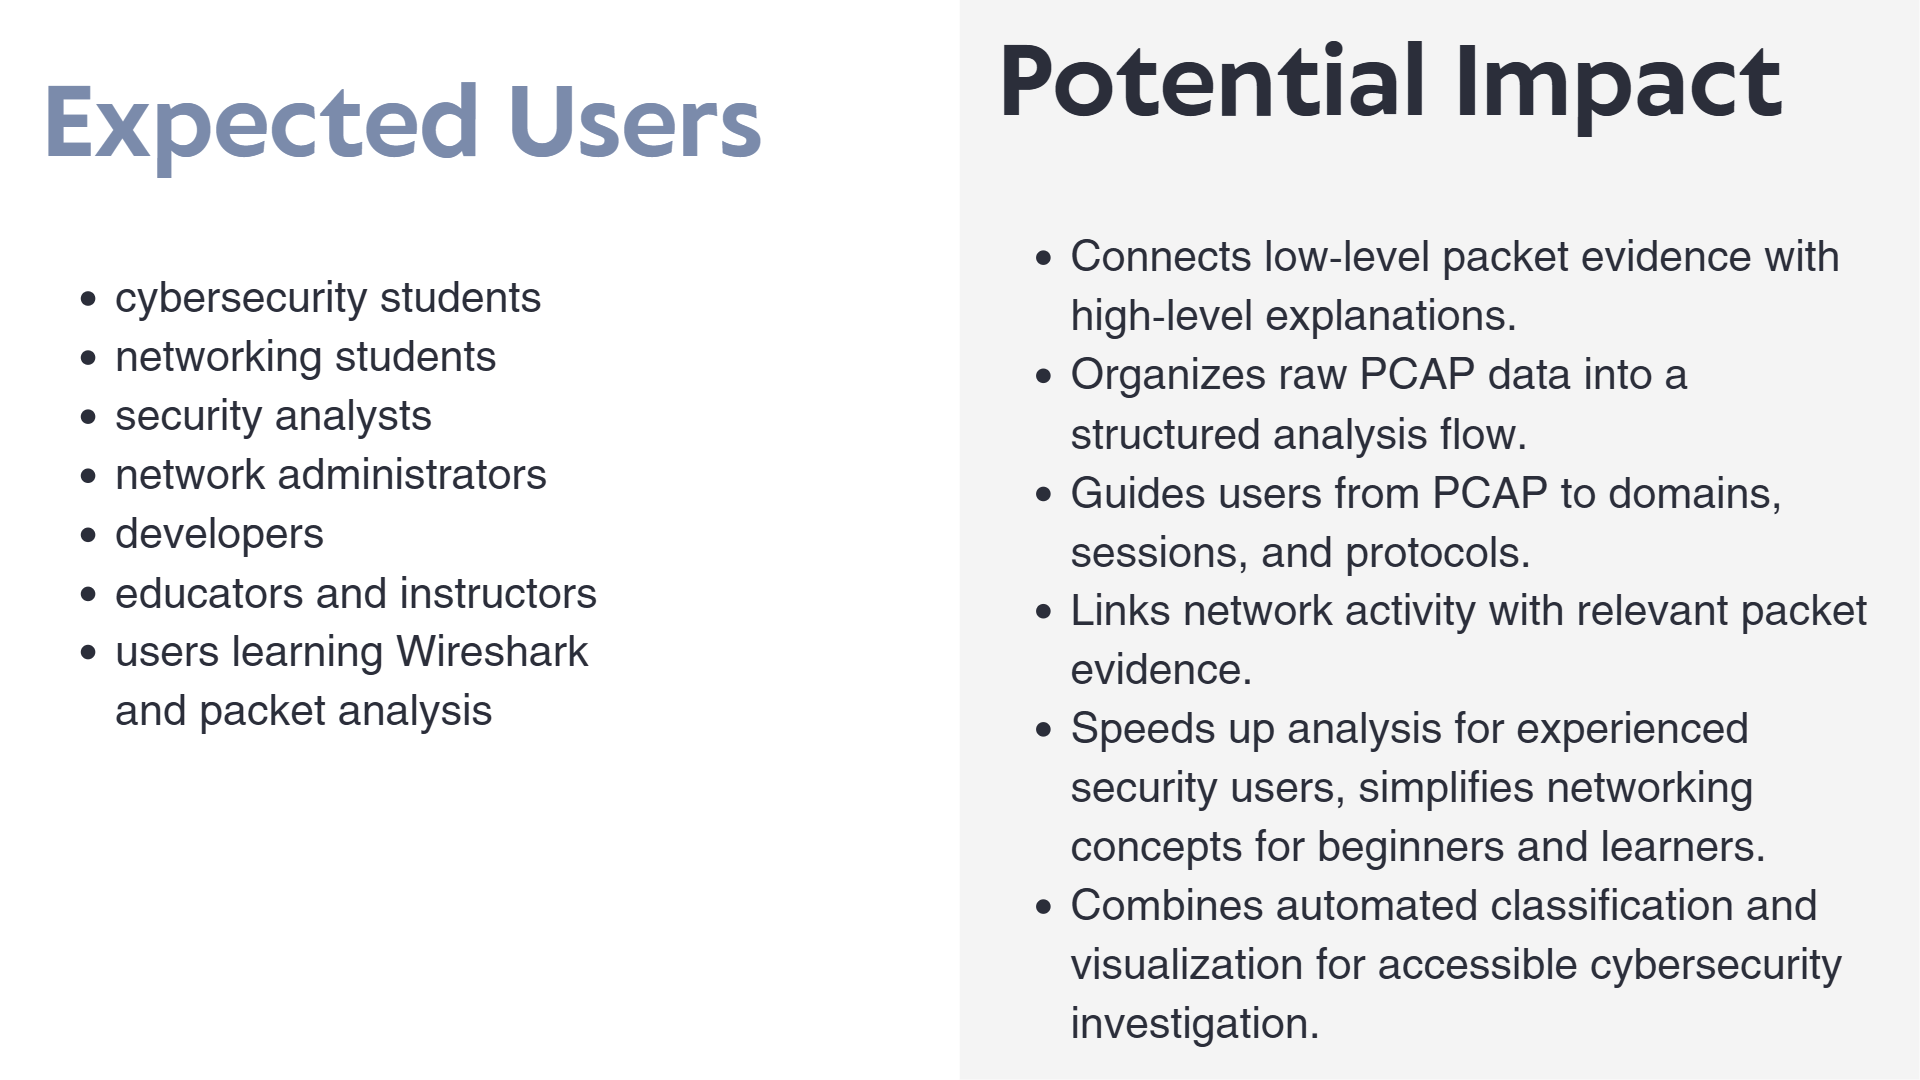
Has been attached in the images

Log in or sign up for Devpost to join the conversation.