Inspiration
Students regularly receive scholarship, internship, delivery, and campus-account messages that look convincing but create pressure to act quickly. A familiar organization name or university-looking URL can make a message feel trustworthy even when the actual destination is different.
We built TrustLens around one simple habit: pause before you click, inspect the evidence, and verify independently.
What it does
TrustLens is a browser-based scam and phishing inspection tool for messages, URLs, screenshots, and QR codes.
A user can:
- Paste a suspicious message or URL.
- Upload a PNG or JPEG screenshot.
- Decode a QR code locally.
- Review and correct extracted text before analysis.
- See an evidence-linked receipt with highlighted excerpts.
- Inspect actual hostname, registrable domain, subdomain, and URL structure.
- Receive a practical recommendation for independent verification.
TrustLens does not claim that a message is safe. It explains what it found, how reliable the declared checks are, and what the result cannot prove.
Try the live app: https://trustlens-lyart.vercel.app/
How we built it
TrustLens uses Next.js, React, TypeScript, CSS, native WebGL/GLSL, Tesseract.js for English OCR, jsQR for QR decoding, tldts for public-suffix and domain facts, Zod for typed evidence validation, and the browser’s standard URL parser.
The analyzer runs locally in the browser. It does not require an API key, database, account, message upload, URL crawling, or runtime generative AI model. Image extraction is bounded and requires user review before analysis.
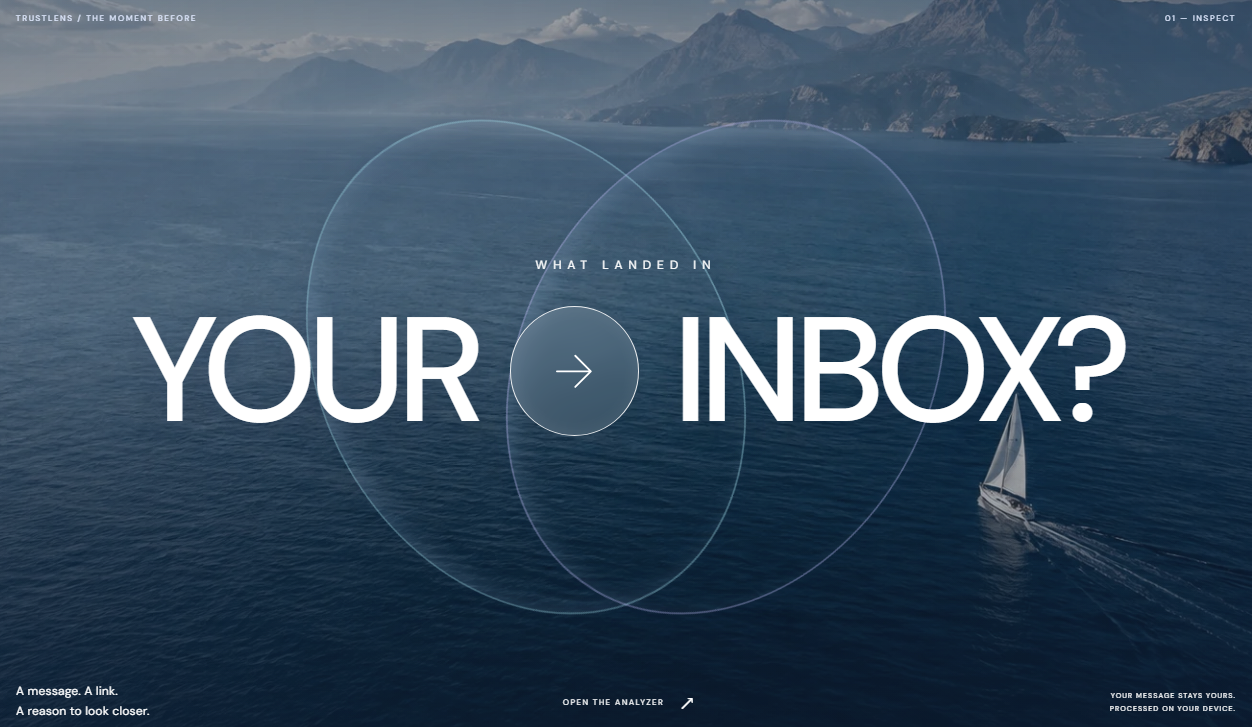
The interface includes a scroll-driven mountain-to-sea journey, an illustrated inbox reel, a 3D lens, responsive layouts, reduced-motion support, an evidence receipt, and a final TrustLens brand reveal.
Challenges we ran into
The most difficult challenge was balancing useful detection with honest uncertainty. Urgency is common in legitimate reminders, so it cannot automatically be treated as fraud. Similarly, a familiar-looking domain is not enough to establish authenticity.
We also had to handle OCR errors, QR decoding failures, malformed URLs, internationalized domains, exact source highlighting, keyboard access, mobile layouts, and animation without blocking the real analyzer.
Accomplishments we’re proud of
- Built a working end-to-end prototype in one hackathon project.
- Added message, URL, screenshot OCR, and QR workflows.
- Created evidence-linked findings that point back to exact source text.
- Made domain structure visible without opening submitted links.
- Added honest partial and undetermined results.
- Implemented privacy-preserving browser-local processing.
- Passed 48 functional and security tests and 25 Chromium browser scenarios.
- Published the live app and public source repository.
Source code: https://github.com/scribesimeon-ux/trustlens
What we learned
A security tool should explain its uncertainty rather than present a confident but unsupported verdict. The best result is not simply “scam” or “safe”; it is a clear explanation of what deserves attention and a safer next action.
We also learned that accessibility, reduced motion, mobile layout, readable evidence, and privacy boundaries are part of security design—not finishing touches.
What’s next for TrustLens
Next, we want to expand language coverage, evaluate against independently collected examples, improve OCR and QR workflows, and add carefully sourced reputation or redirect checks without sending private message content to a server.
We also want to make the evidence receipt easier to share with a trusted teacher, parent, campus office, or security team.
AI and external tools disclosure
OpenAI Codex substantially assisted with product design, architecture, implementation, testing, synthetic fixtures, and documentation. OpenAI image generation produced the original scenic background assets. The deployed TrustLens analyzer does not use a generative AI model to judge messages.
Built With
- css
- git
- github
- glsl
- jsqr
- next.js
- playwright
- react
- tesseract.js
- tldts
- typescript
- vercel
- visual-studio
- webgl
- zod

Log in or sign up for Devpost to join the conversation.