Inspiration
Building software has never been easier. Platforms like Lovable let people go from an idea to a deployed application in minutes.
But while building got easier, security became an afterthought.
see it here https://synk-web-6sgz.onrender.com/
Researchers analyzing 5,600 publicly available vibe-coded apps found more than 2,000 high-impact vulnerabilities, 400+ exposed secrets, and 175 cases of exposed personal data.
A single vulnerability can expose private user data, compromise accounts, or leak API keys that lead to massive unexpected bills.
We built Synk to make securing a vibe-coded app as easy as building one.
What it does
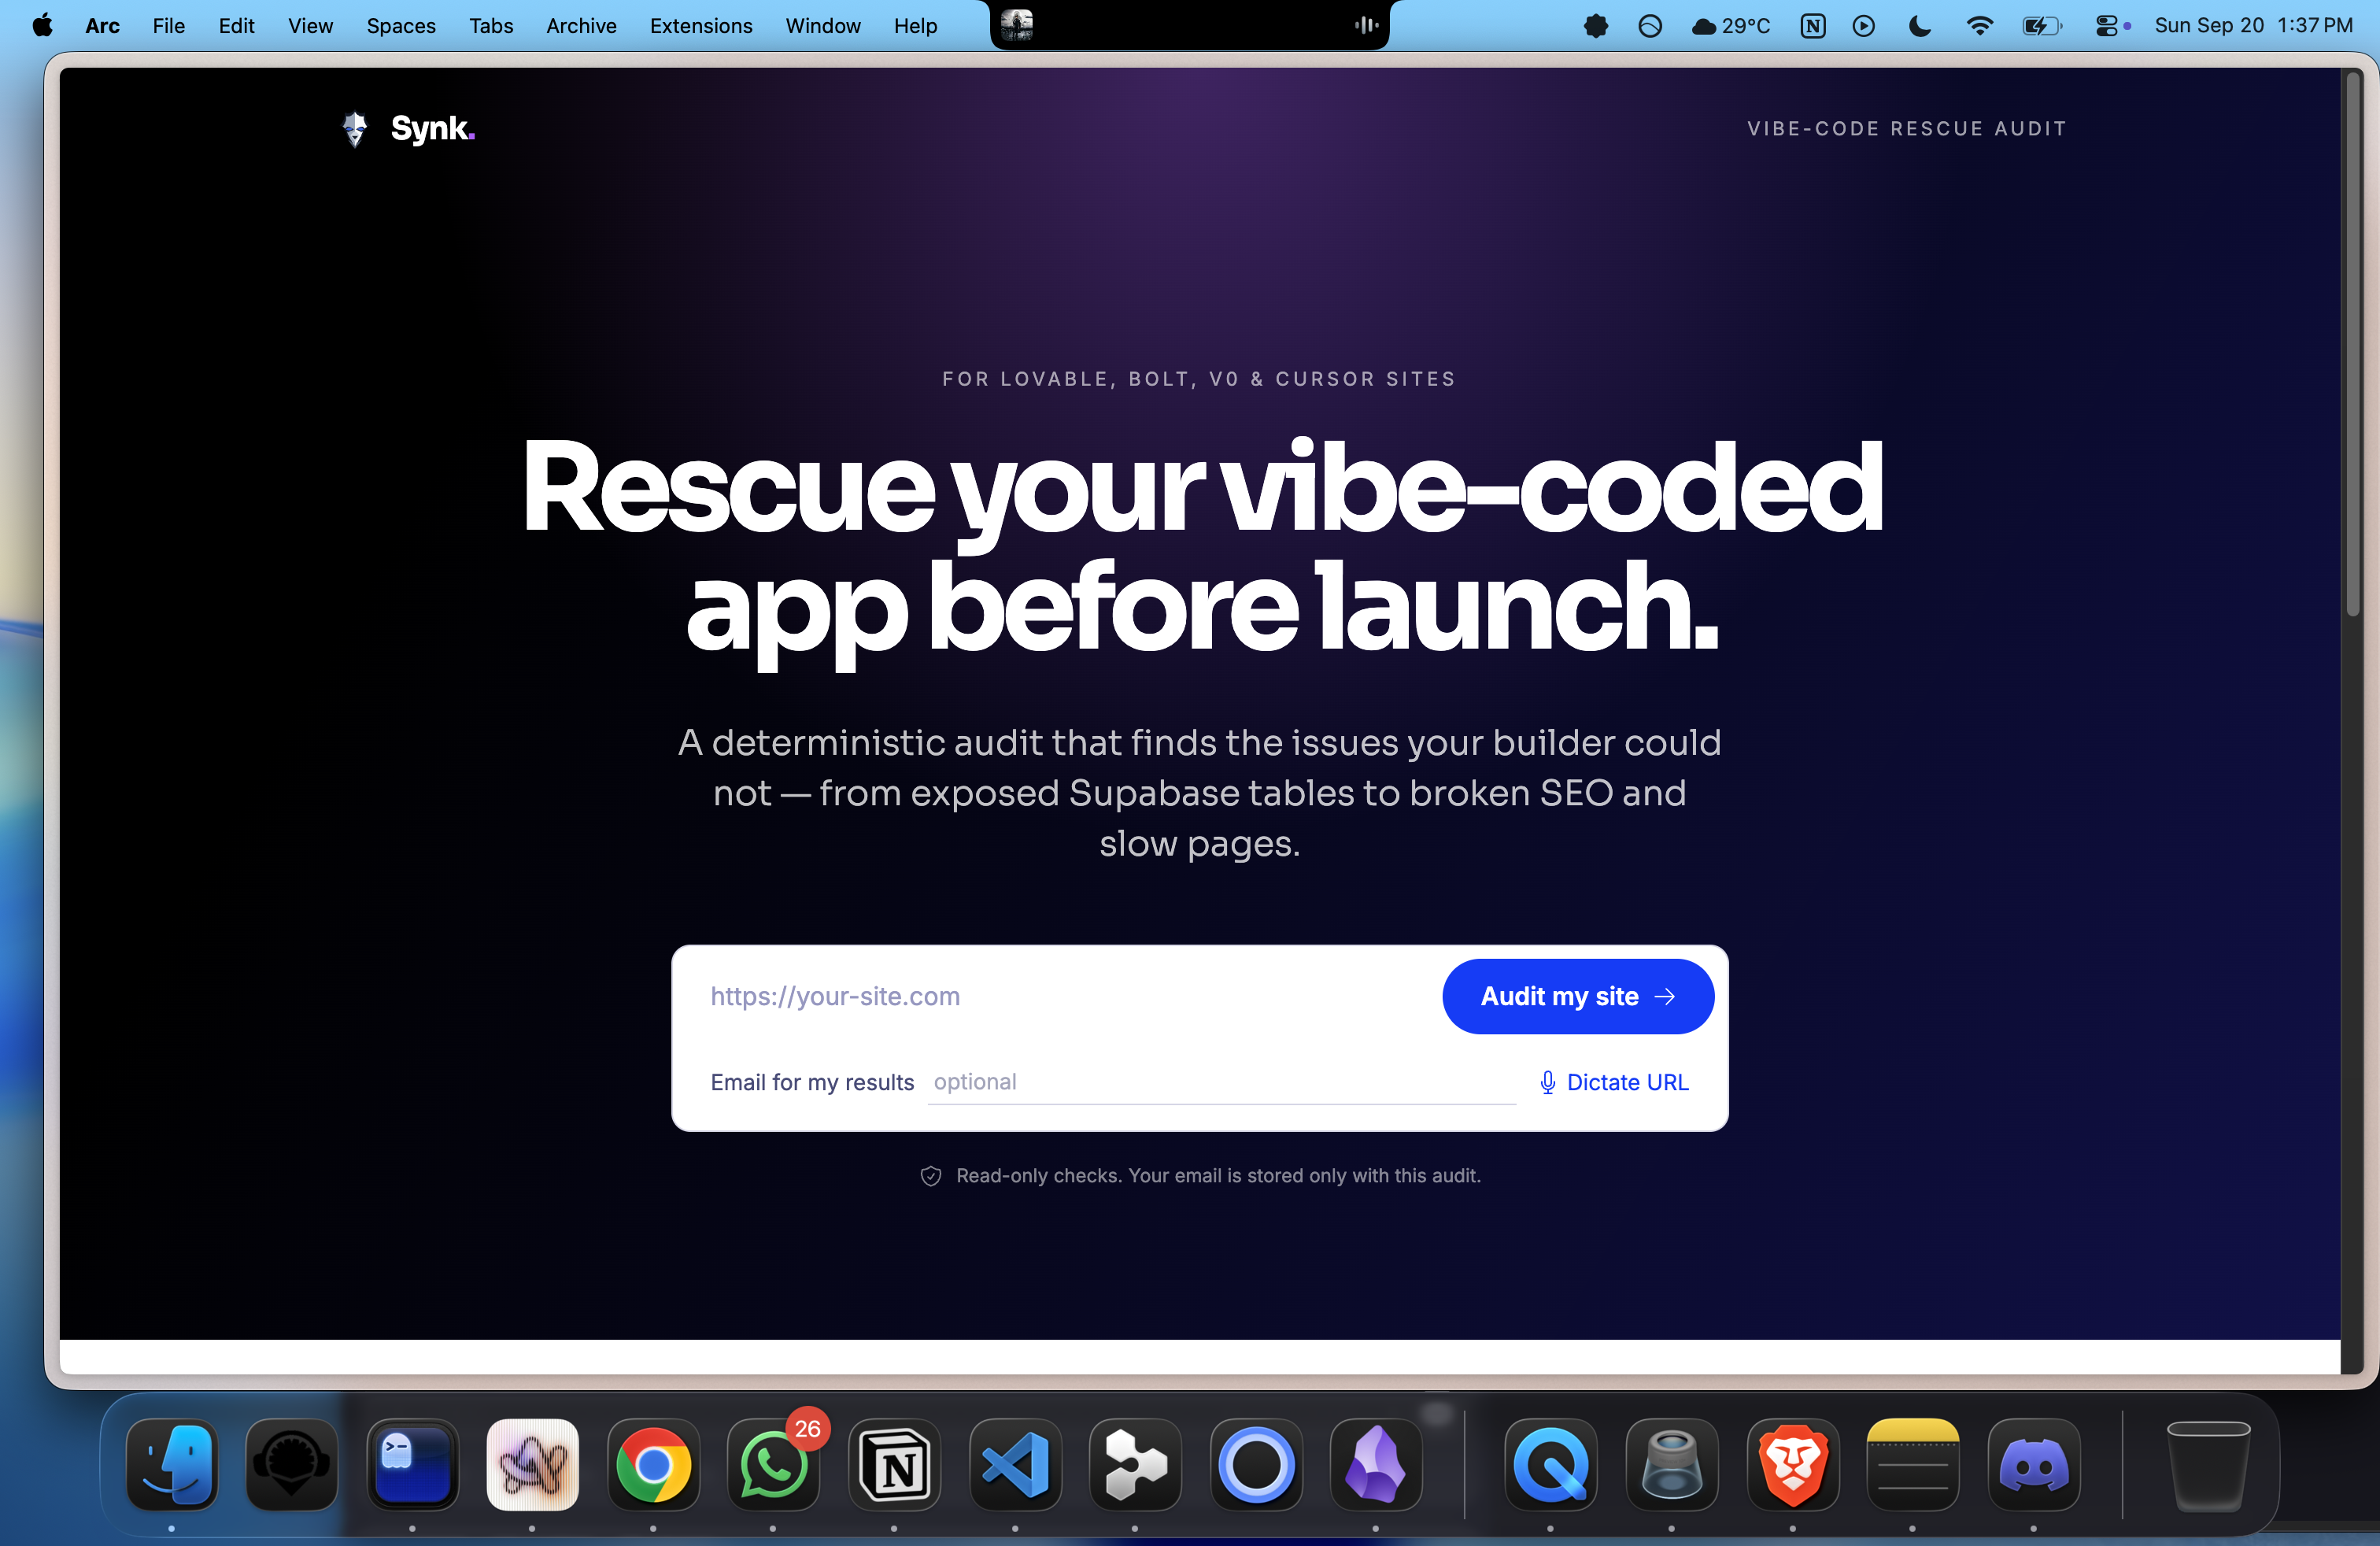
Synk takes one thing: your app's URL.
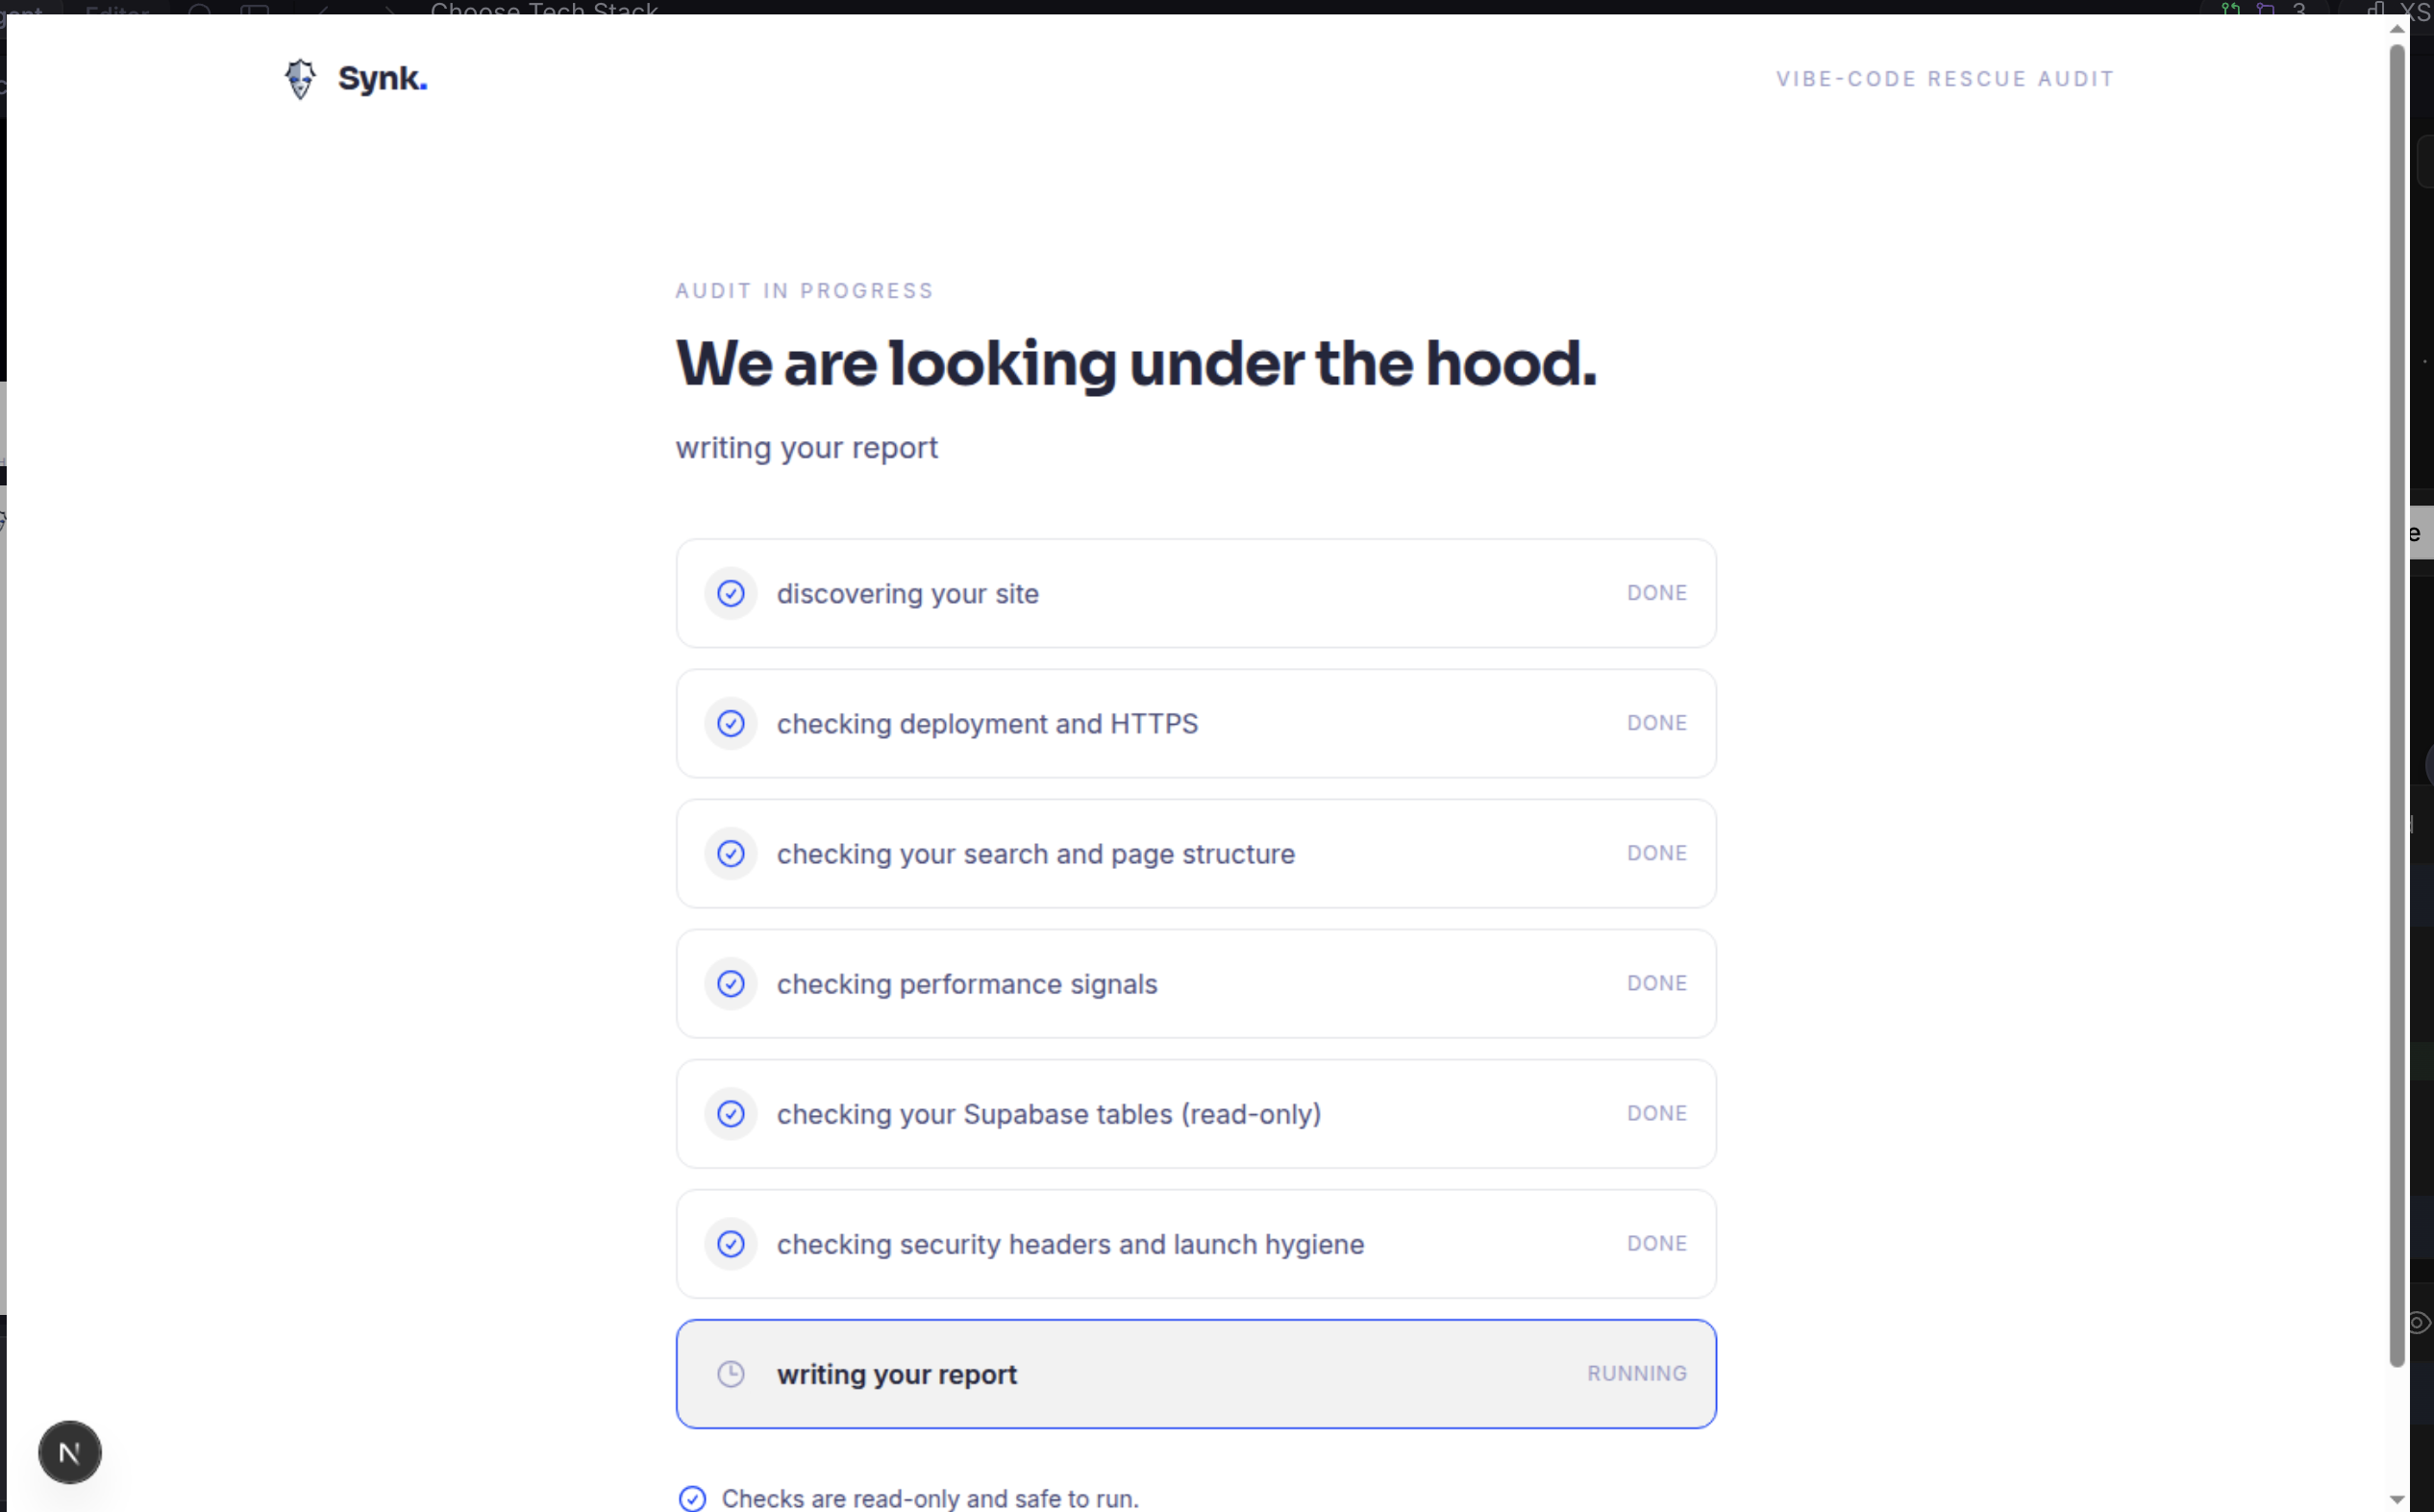
It scans the live application for security vulnerabilities, exposed secrets, performance problems, and overall application health.
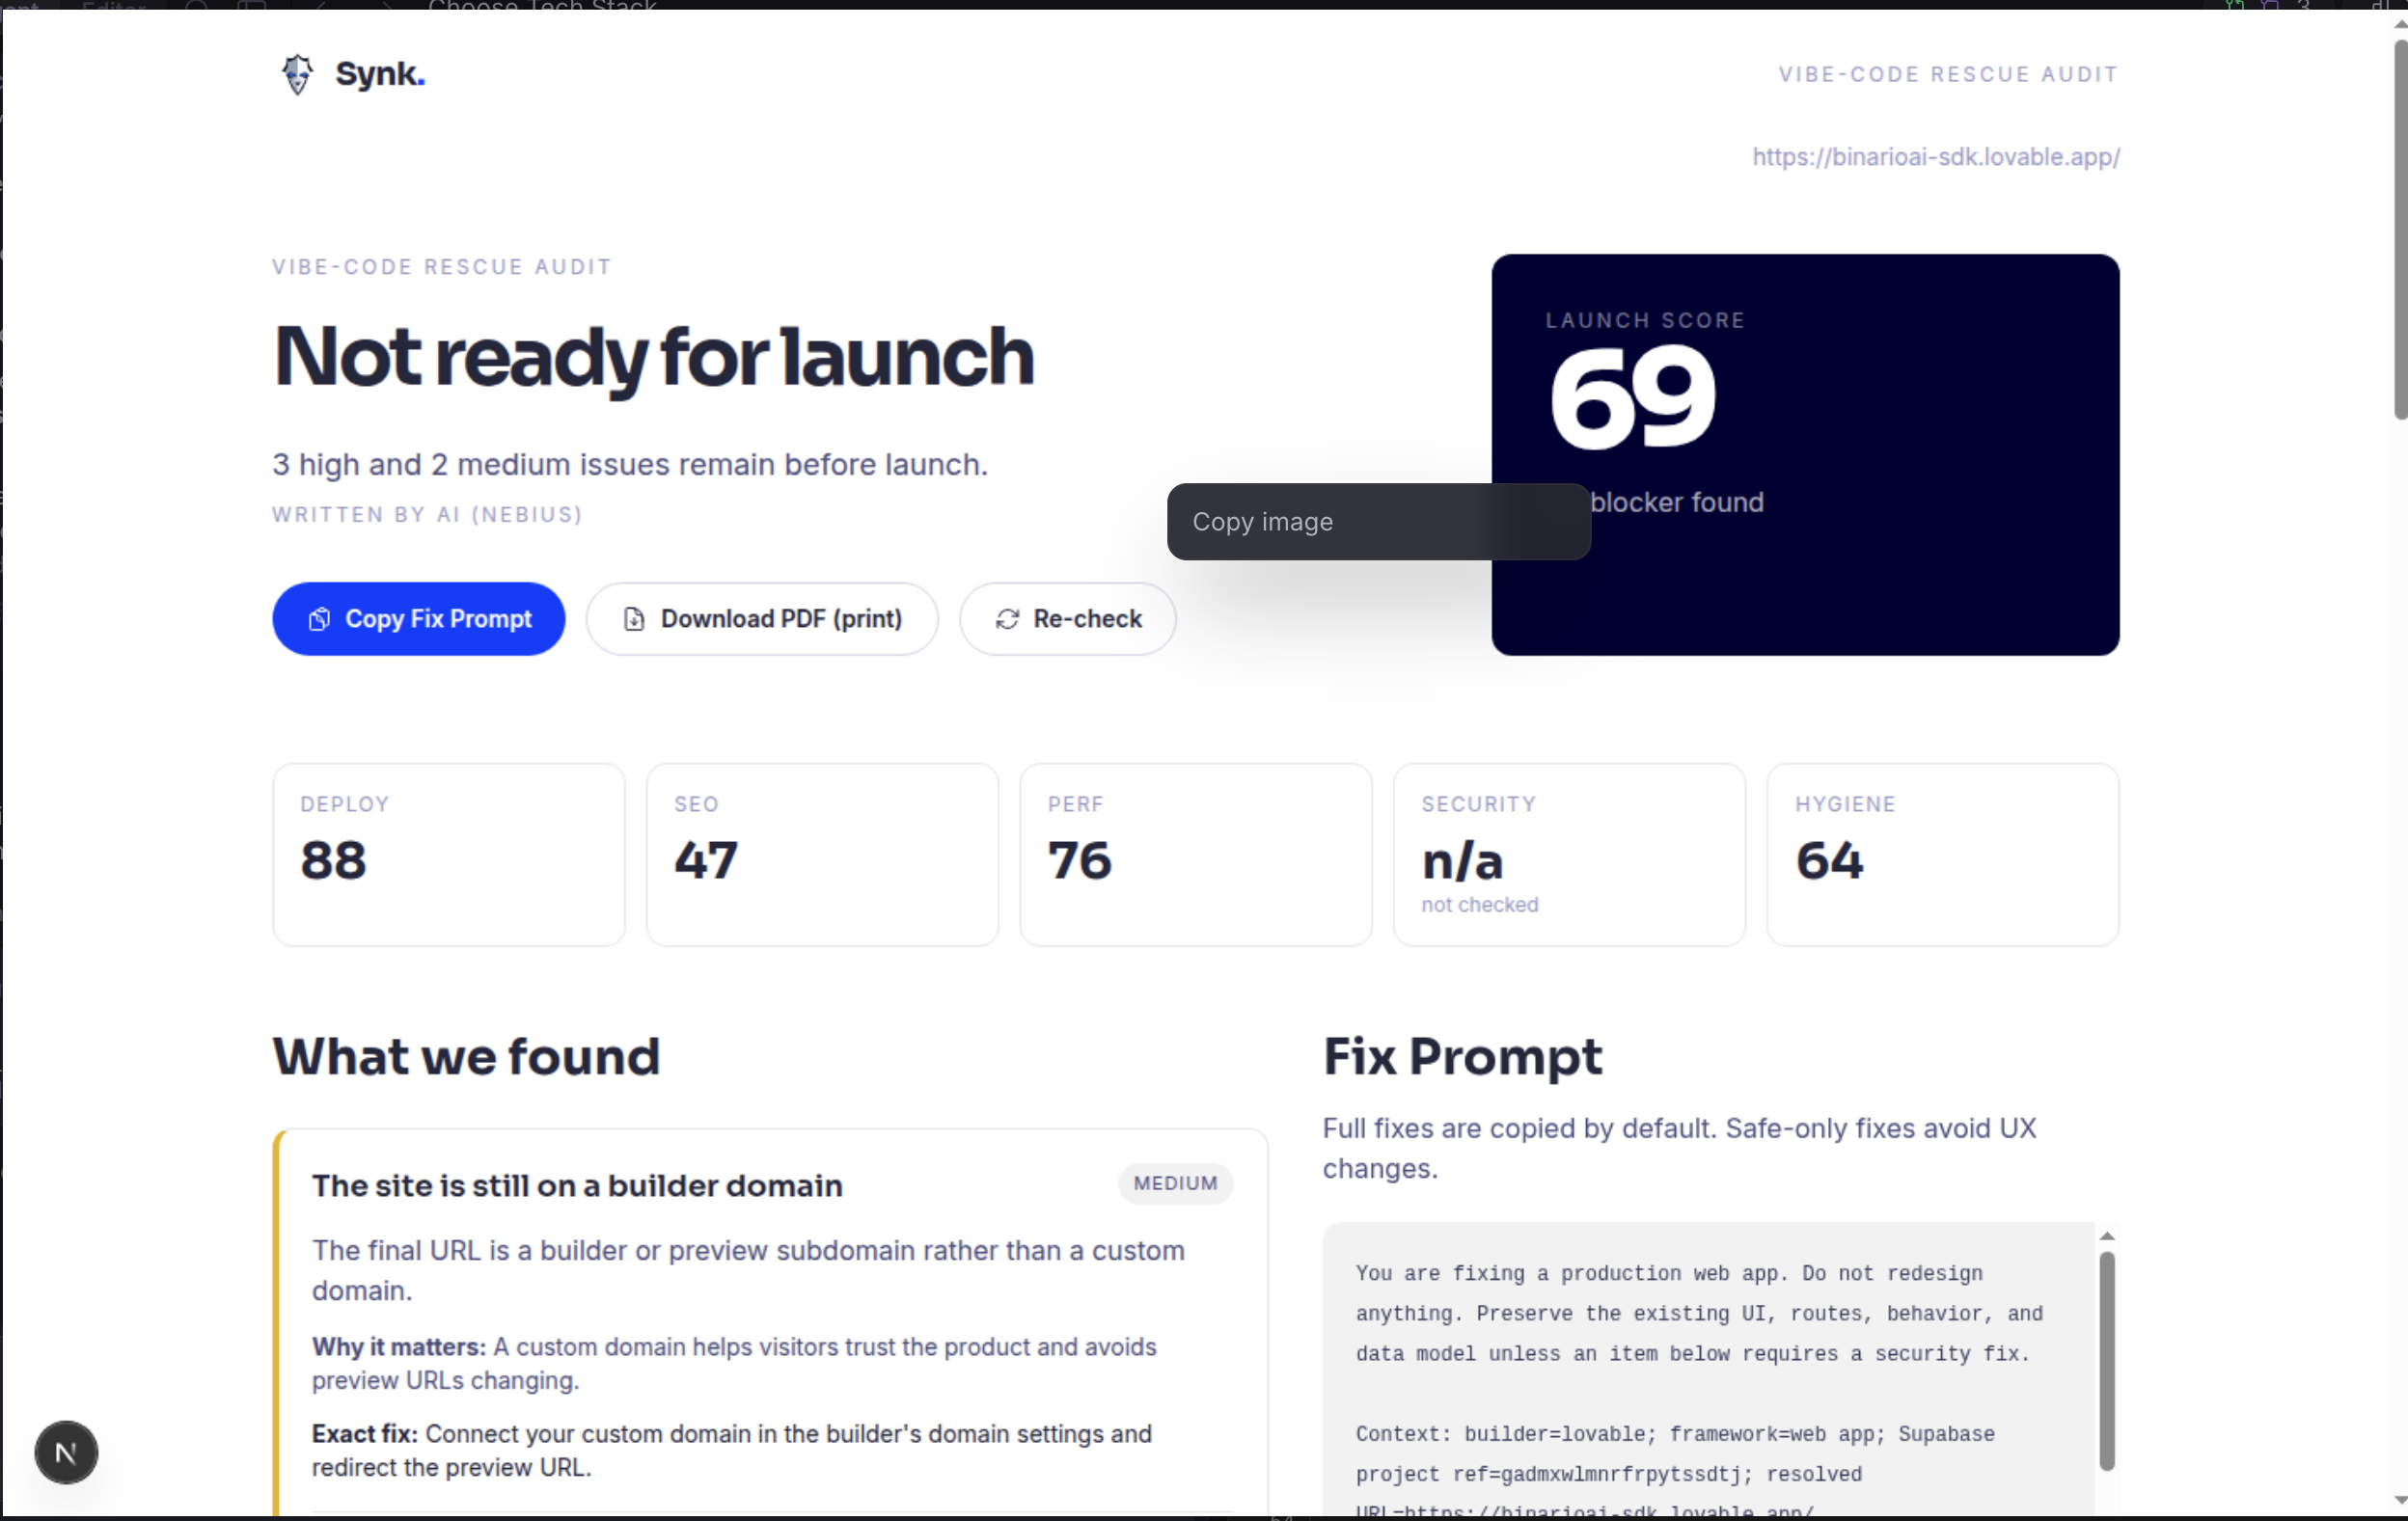
Synk then turns those findings into a simple report explaining what is wrong, why it matters, and what needs to be fixed.
And instead of leaving developers with a list of problems, Synk generates a ready-to-use fix prompt that can be pasted directly back into Lovable.
Scan. Understand. Fix. Rescan.
How we built it
We built Synk around a simple URL-first scanning workflow.
A user submits their deployed application URL, Synk analyzes the publicly accessible application surface, runs security and application-health checks, and organizes the findings by severity.
We then translate those technical findings into understandable explanations and generate an AI-ready remediation prompt designed to help the user's coding agent fix the identified issues.
The goal was to remove as much security complexity as possible from the developer's workflow.
Challenges we ran into
One of the biggest challenges was turning security findings into something actually useful.
Simply telling a developer that their application has a vulnerability isn't enough. We needed to explain the risk without overwhelming them and then give them a clear path toward fixing it.
Another challenge was balancing depth and speed. Synk needs to find meaningful problems while still fitting into the fast development loop that makes vibe coding attractive in the first place.
Accomplishments that we're proud of
We're proud that Synk doesn't stop at detection.
We created a workflow that connects finding a vulnerability directly to fixing it.
Instead of requiring developers to understand security tooling, CVEs, configuration rules, or long technical reports, Synk turns its findings into actionable instructions that can go straight back into the AI development environment they already use.
That closes the loop between building, scanning, fixing, and shipping.
What we learned
We learned that the real problem isn't just finding vulnerabilities.
It's making security actionable for people who aren't security experts.
AI has dramatically reduced the barrier to building software, but security tools still assume the person using them has deep technical knowledge.
We believe the next generation of security tooling has to meet developers where they already work.
What's next for Synk
Next, we want Synk to become the security layer for vibe-coded applications.
We're working toward deeper vulnerability detection, smarter remediation prompts, continuous monitoring, automatic rescanning after fixes, and tighter integration with platforms like Lovable.
Eventually, we want the workflow to be simple:
Build your app. Ship it. Synk scans it. Your AI fixes it. Synk verifies the fix.
Vibe coding made building software easier.
Synk is making securing it just as easy.
Built With
- firecrawl
- typescript


Log in or sign up for Devpost to join the conversation.