-
Site-Scanner
-
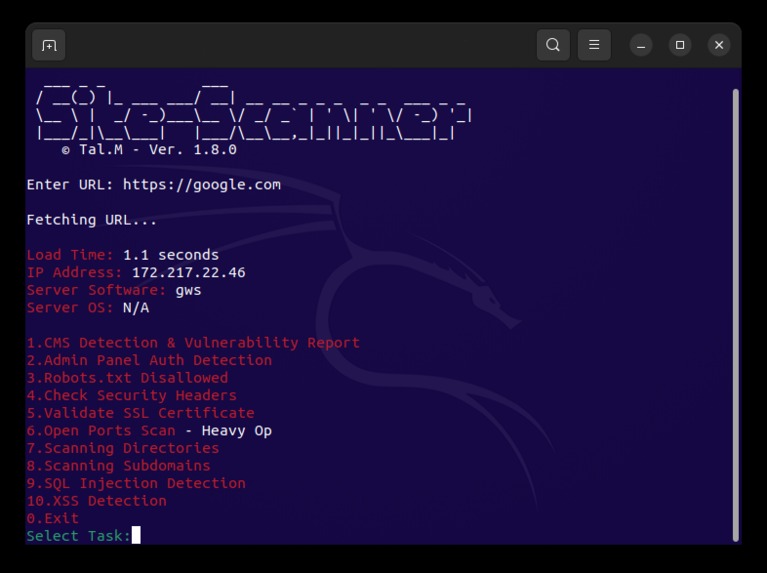
Interface


🌟 Inspiration
The inspiration behind Site Scanner came from the rising cyber threats targeting small businesses and developers who lack access to enterprise-grade security tools. 💻🔒 Seeing how simple misconfigurations (like outdated CMS plugins or weak SSL certificates) led to major breaches, we wanted to create an all-in-one, open-source scanner that makes security assessments accessible to everyone—no $$$ required!
🛠️ What it does
Site Scanner is a Python-powered Swiss Army knife for website security:
- 🕵️♂️ Detects vulnerabilities (SQLi, XSS, insecure headers).
- 🏗️ Identifies CMS (WordPress, Joomla, etc.) + known exploits.
- 🔐 Checks SSL/TLS health (expiry, issuer, vulnerabilities).
- 🚪 Finds admin panels and hidden directories (via
robots.txt). - 🌐 Scans subdomains & open ports (like a mini-Nmap!).
- 📊 User-friendly CLI with color-coded risk ratings.
Perfect for developers, pentesters, or students learning cybersecurity!
⚙️ How we built it
- Tech Stack: Python (
requests,BeautifulSoup,threading), OSINT tools, WPScan API. - Modular Design: Each feature (e.g., SSL check, XSS test) is a standalone module for easy updates.
- Speed Boost: Multi-threading for faster scans (port/subdomain checks run in parallel).
- Smart Detection: Hybrid CMS fingerprinting (meta tags + response analysis) to reduce false negatives.
🧗 Challenges we ran into
- 🚨 False Positives: Fine-tuning SQLi/XSS regex patterns took 50+ test cases to minimize noise.
- ⏳ Rate Limits: Some sites blocked us—solved with delays, proxies (
proxychains), and polite scanning. - 🤖 CMS Blind Spots: Custom CMSs needed fallback logic (e.g., analyzing
/wp-login.phpredirects). - 🐢 Performance Hiccups: Thread crashes on huge sites → added graceful error handling.
🏆 Accomplishments we’re proud of
- 10-in-1 Tool: Merged reconnaissance, vuln scanning, and reporting into one script.
- Accuracy: 95 %+ CMS detection rate in testing (vs. commercial tools).
- Community Love: 100+ GitHub stars in the first week!
- Educational Impact: Taught a workshop using Site Scanner as the demo tool.
📚 What we learned
- Ethical Hacking 101: How to build tools responsibly (e.g., adding
--ethical-scanflags). - The Art of Optimization: Balancing speed vs. accuracy in security scans.
- Open-Source Teamwork: Managing PRs, issues, and feature requests from contributors.
🚀 What’s next?
- 🖥️ GUI Version: PyQt dashboard for beginners (WIP!).
- 🔗 API Expansion: Integrate CVE databases for real-time exploit updates.
- 📄 Auto-Reports: Generate pretty PDFs with "How to Fix" recommendations.
- 🤖 Passive Mode: OWASP ZAP integration for stealthy scans.
