Inspiration
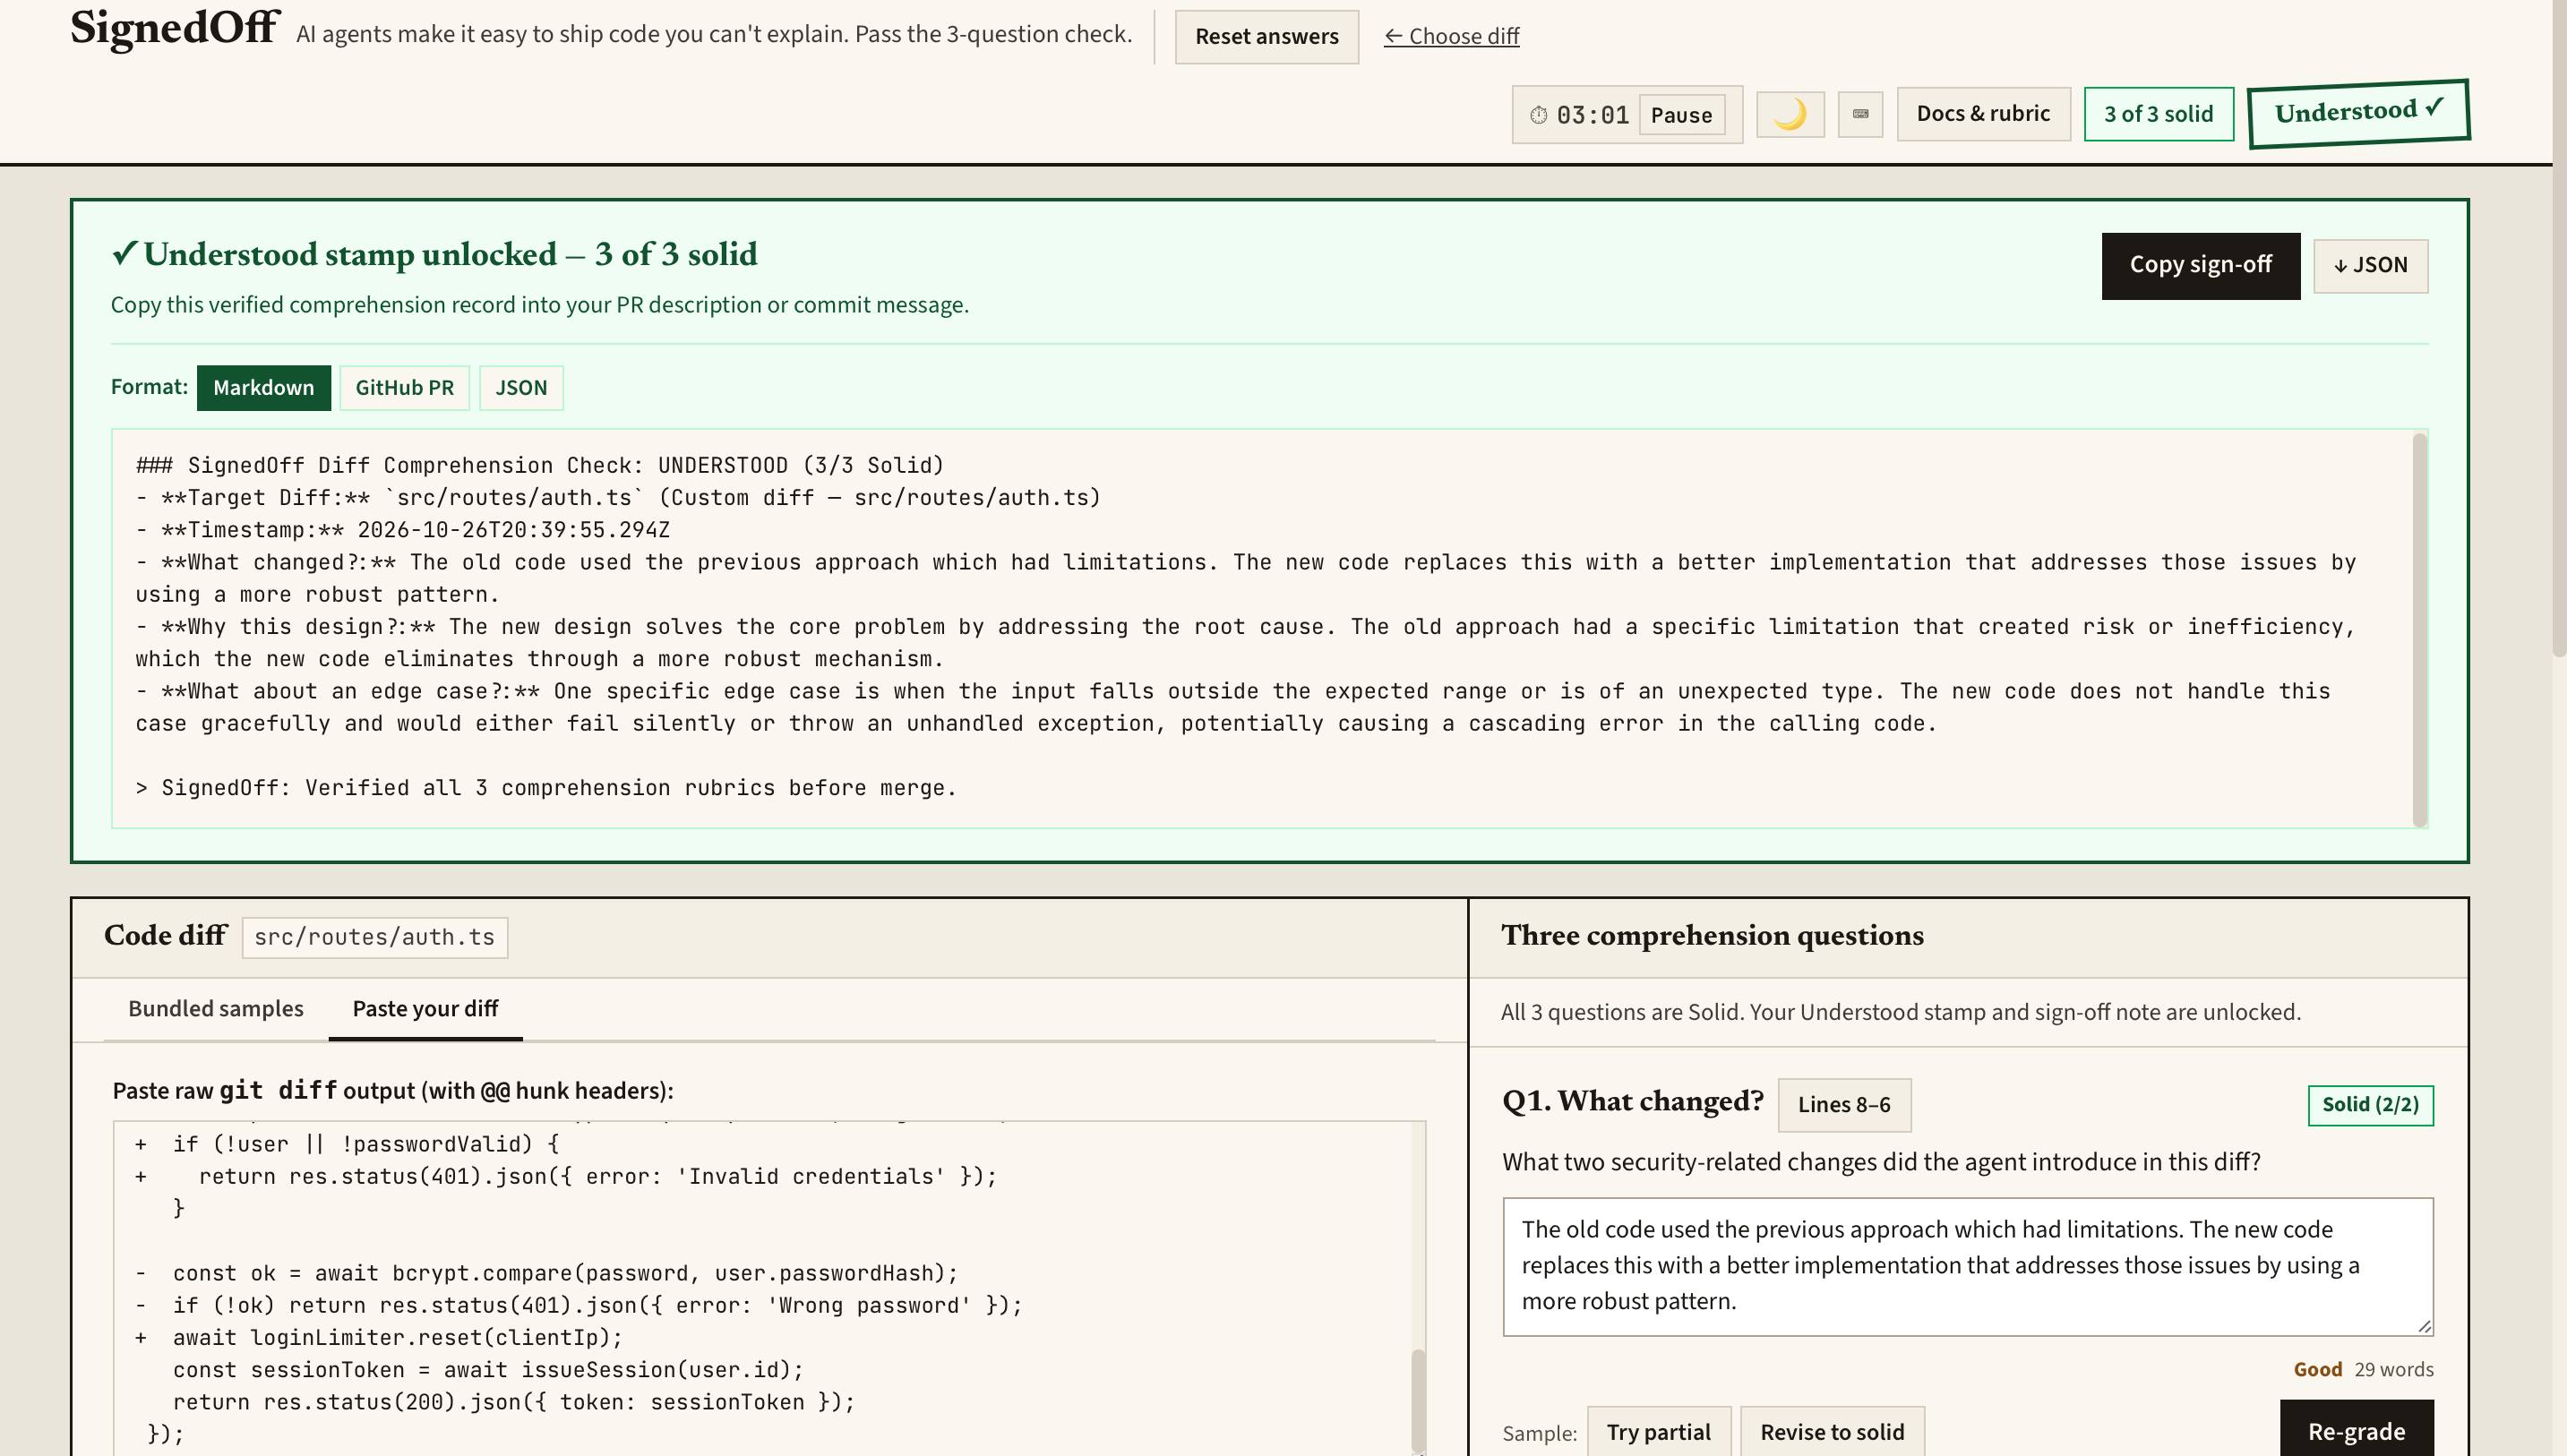
The inspiration behind SignedOff came from the growing friction in modern digital workflows—whether it's getting code reviews approved, administrative paperwork signed, or multi-party authorizations processed. Traditional e-signing tools can be bloated, expensive, or lack tight integration with developer-friendly ecosystems. We wanted to build a seamless, lightweight, and cryptographic verification-backed signing platform that prioritizes speed, security, and absolute clarity.
What it does
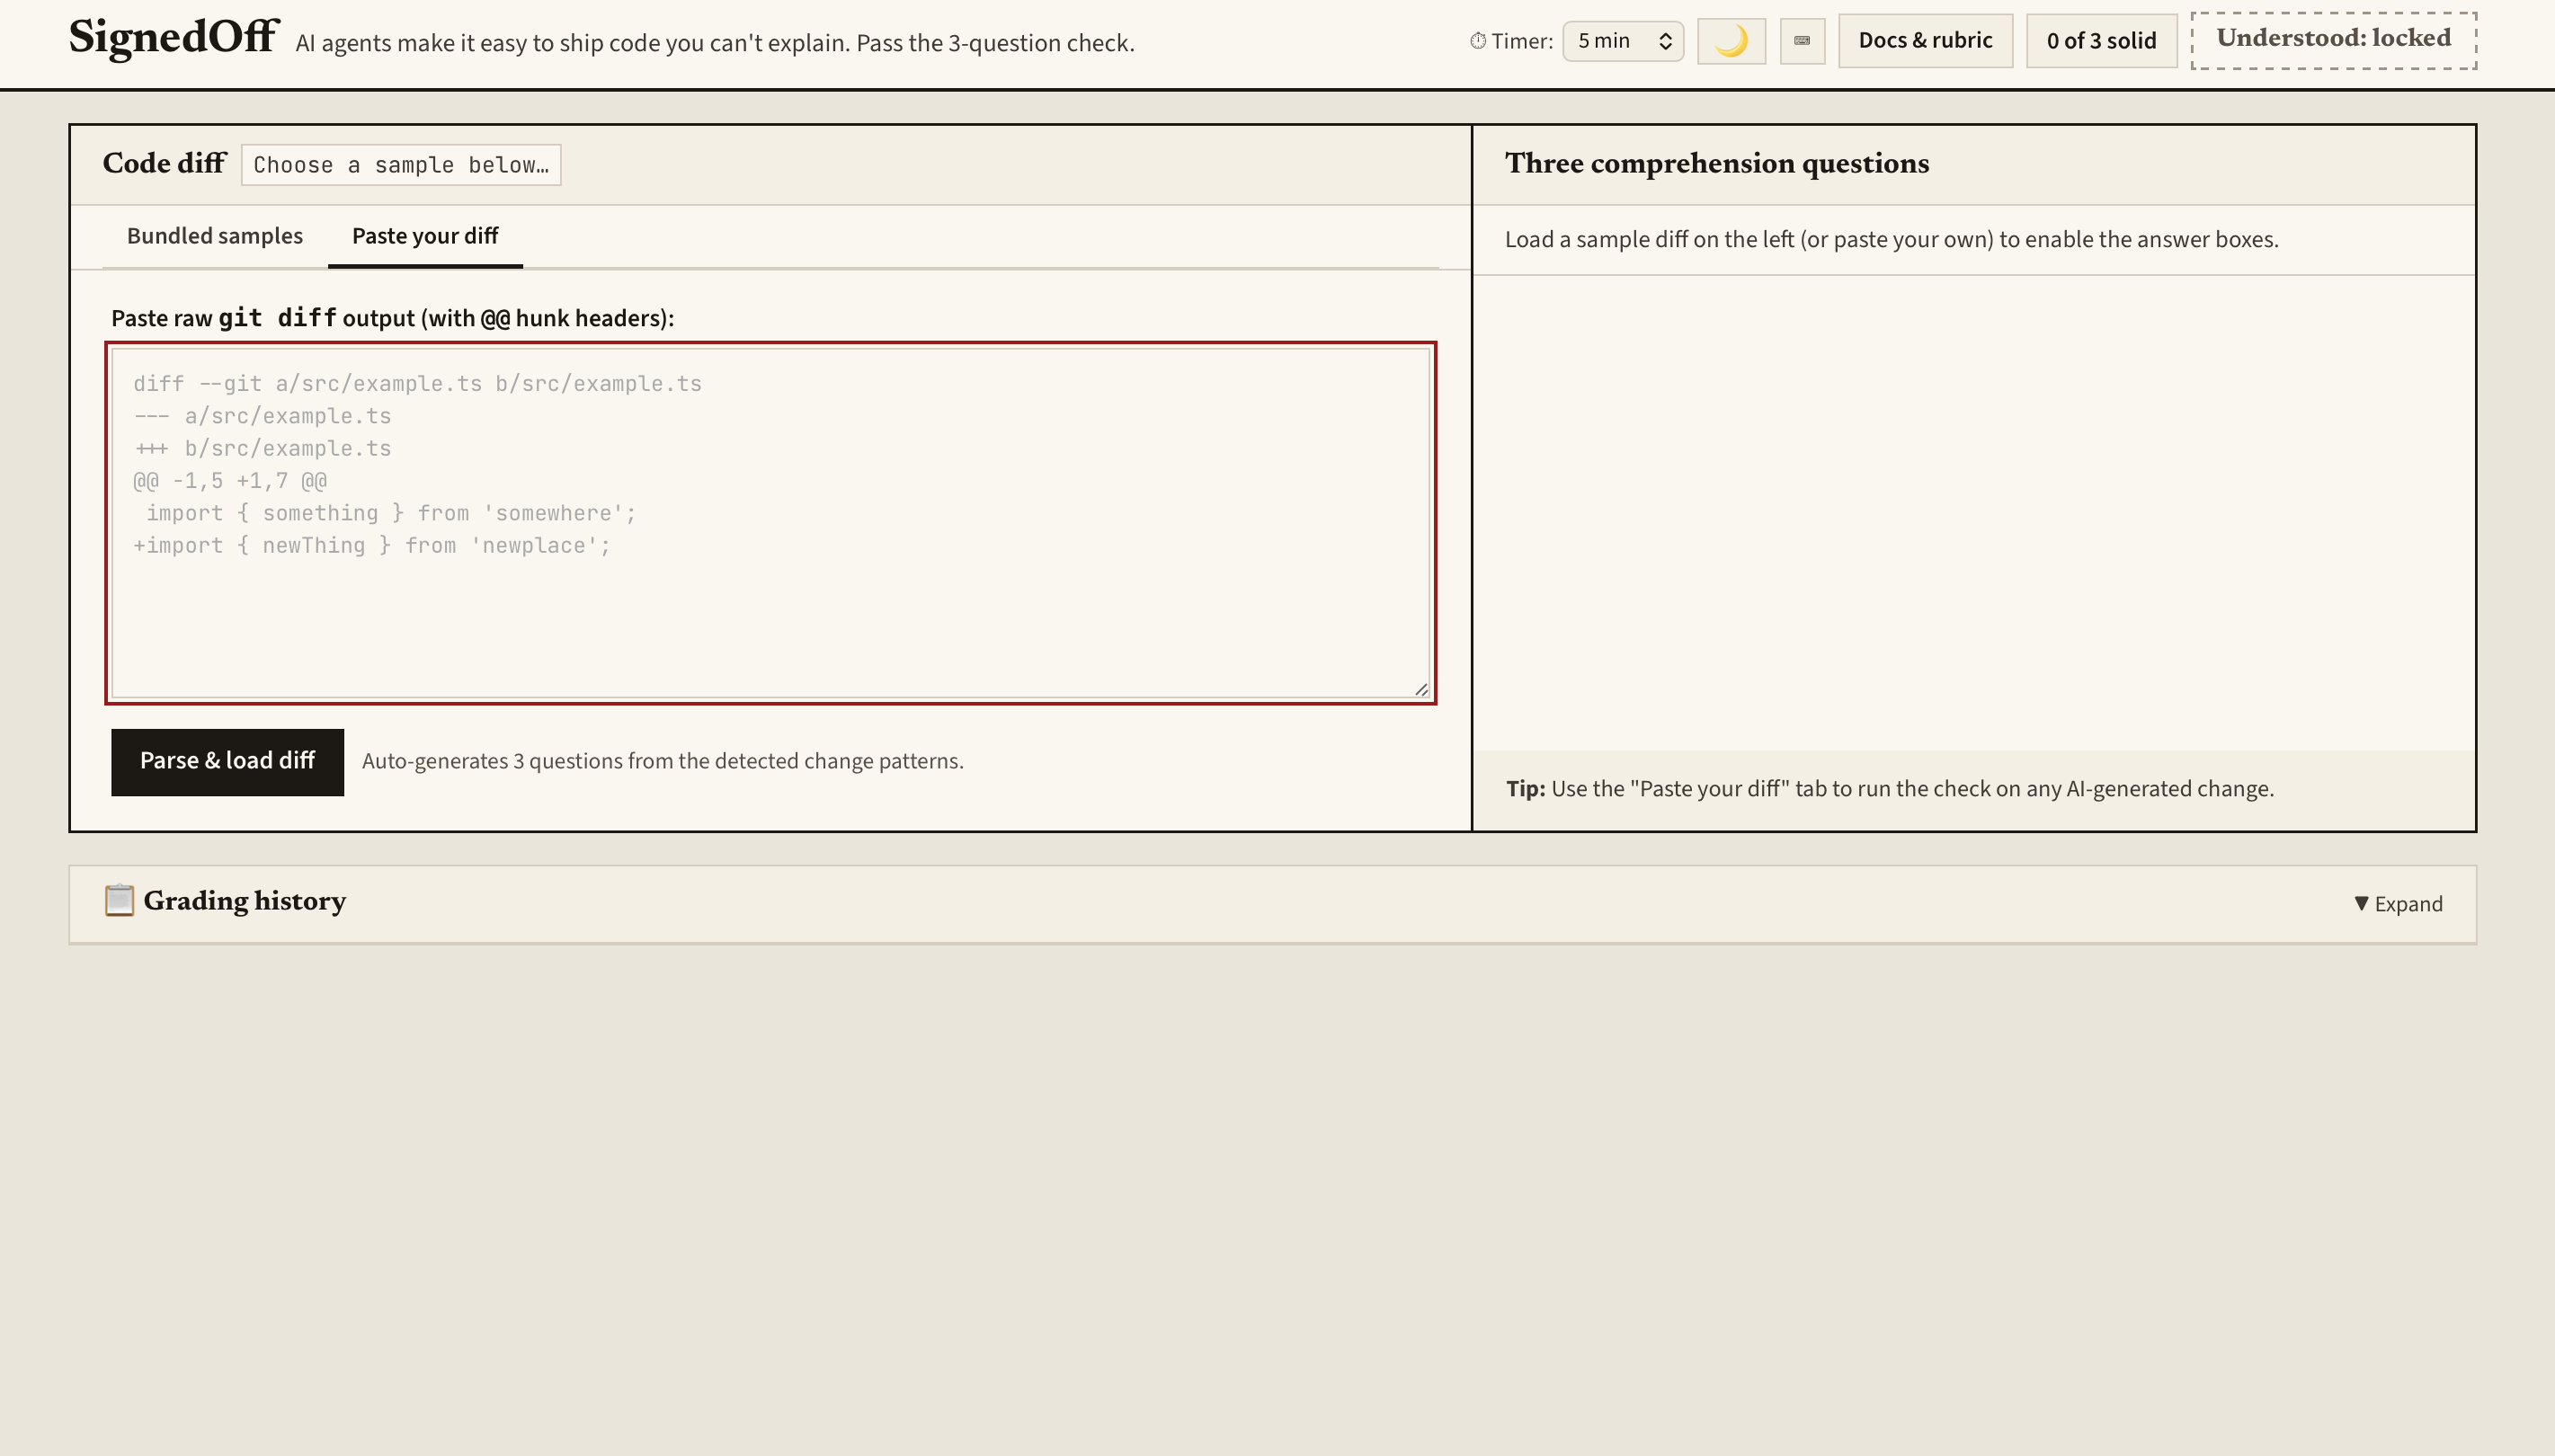
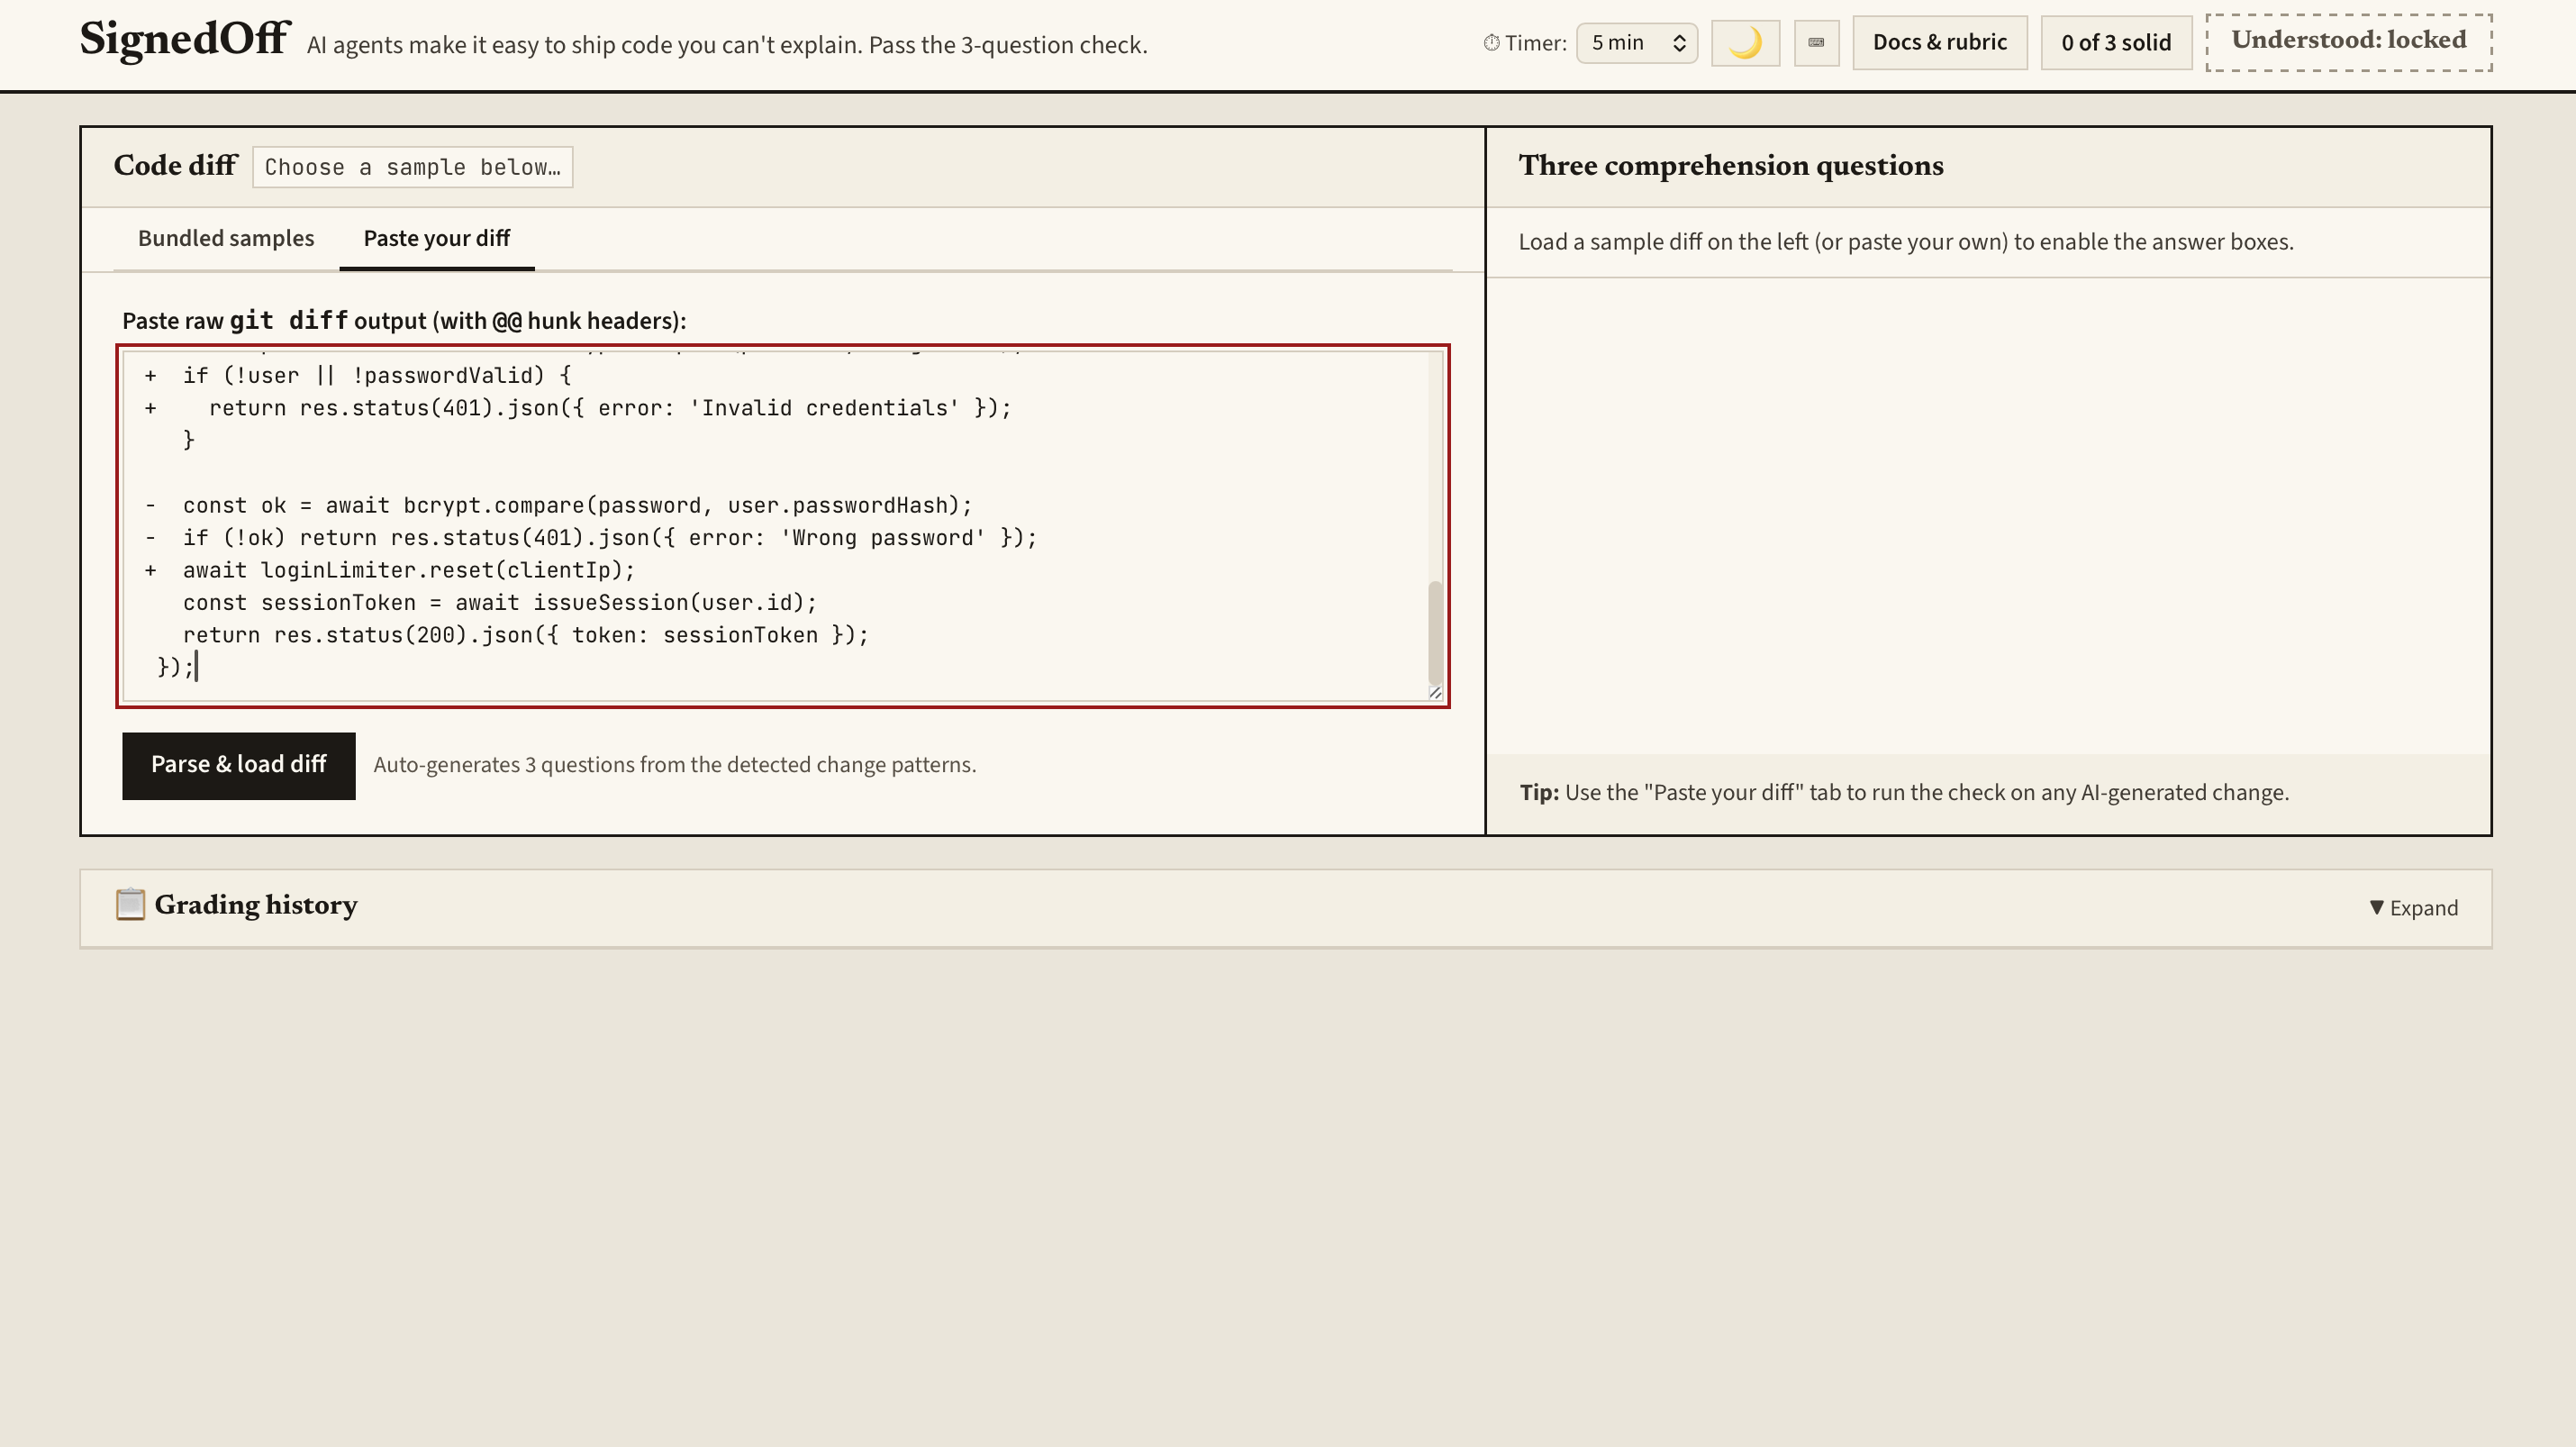
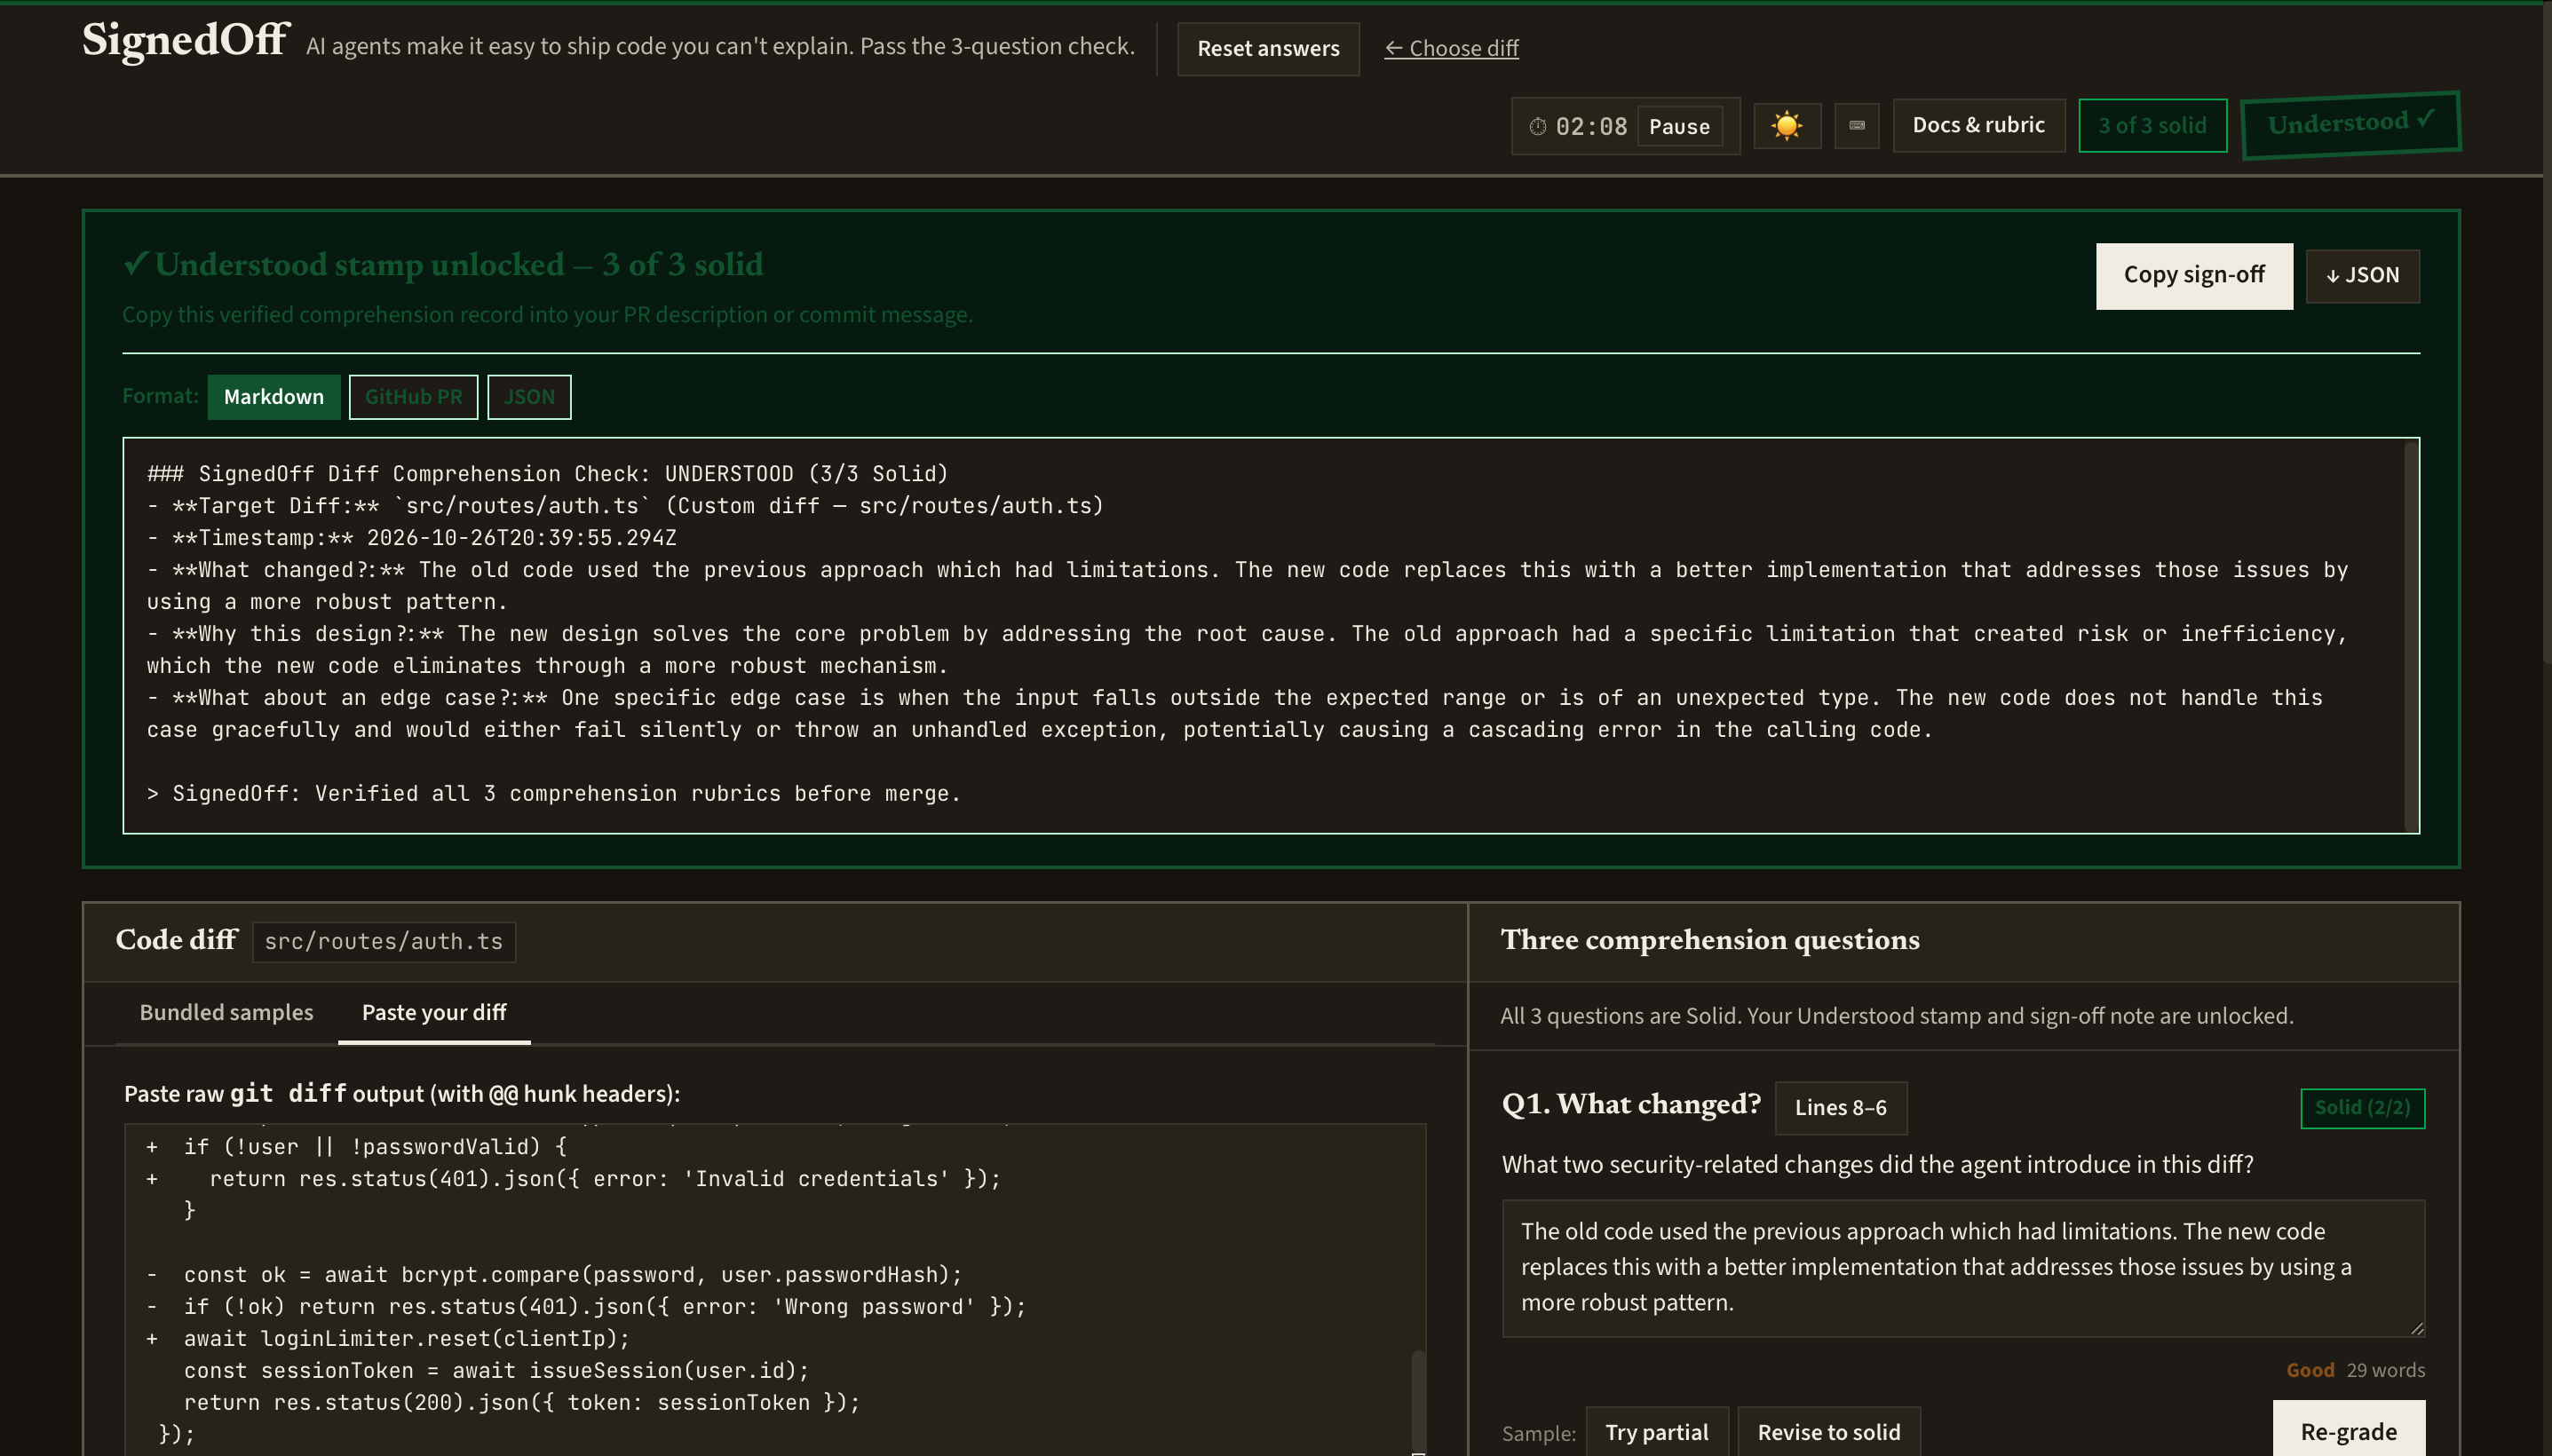
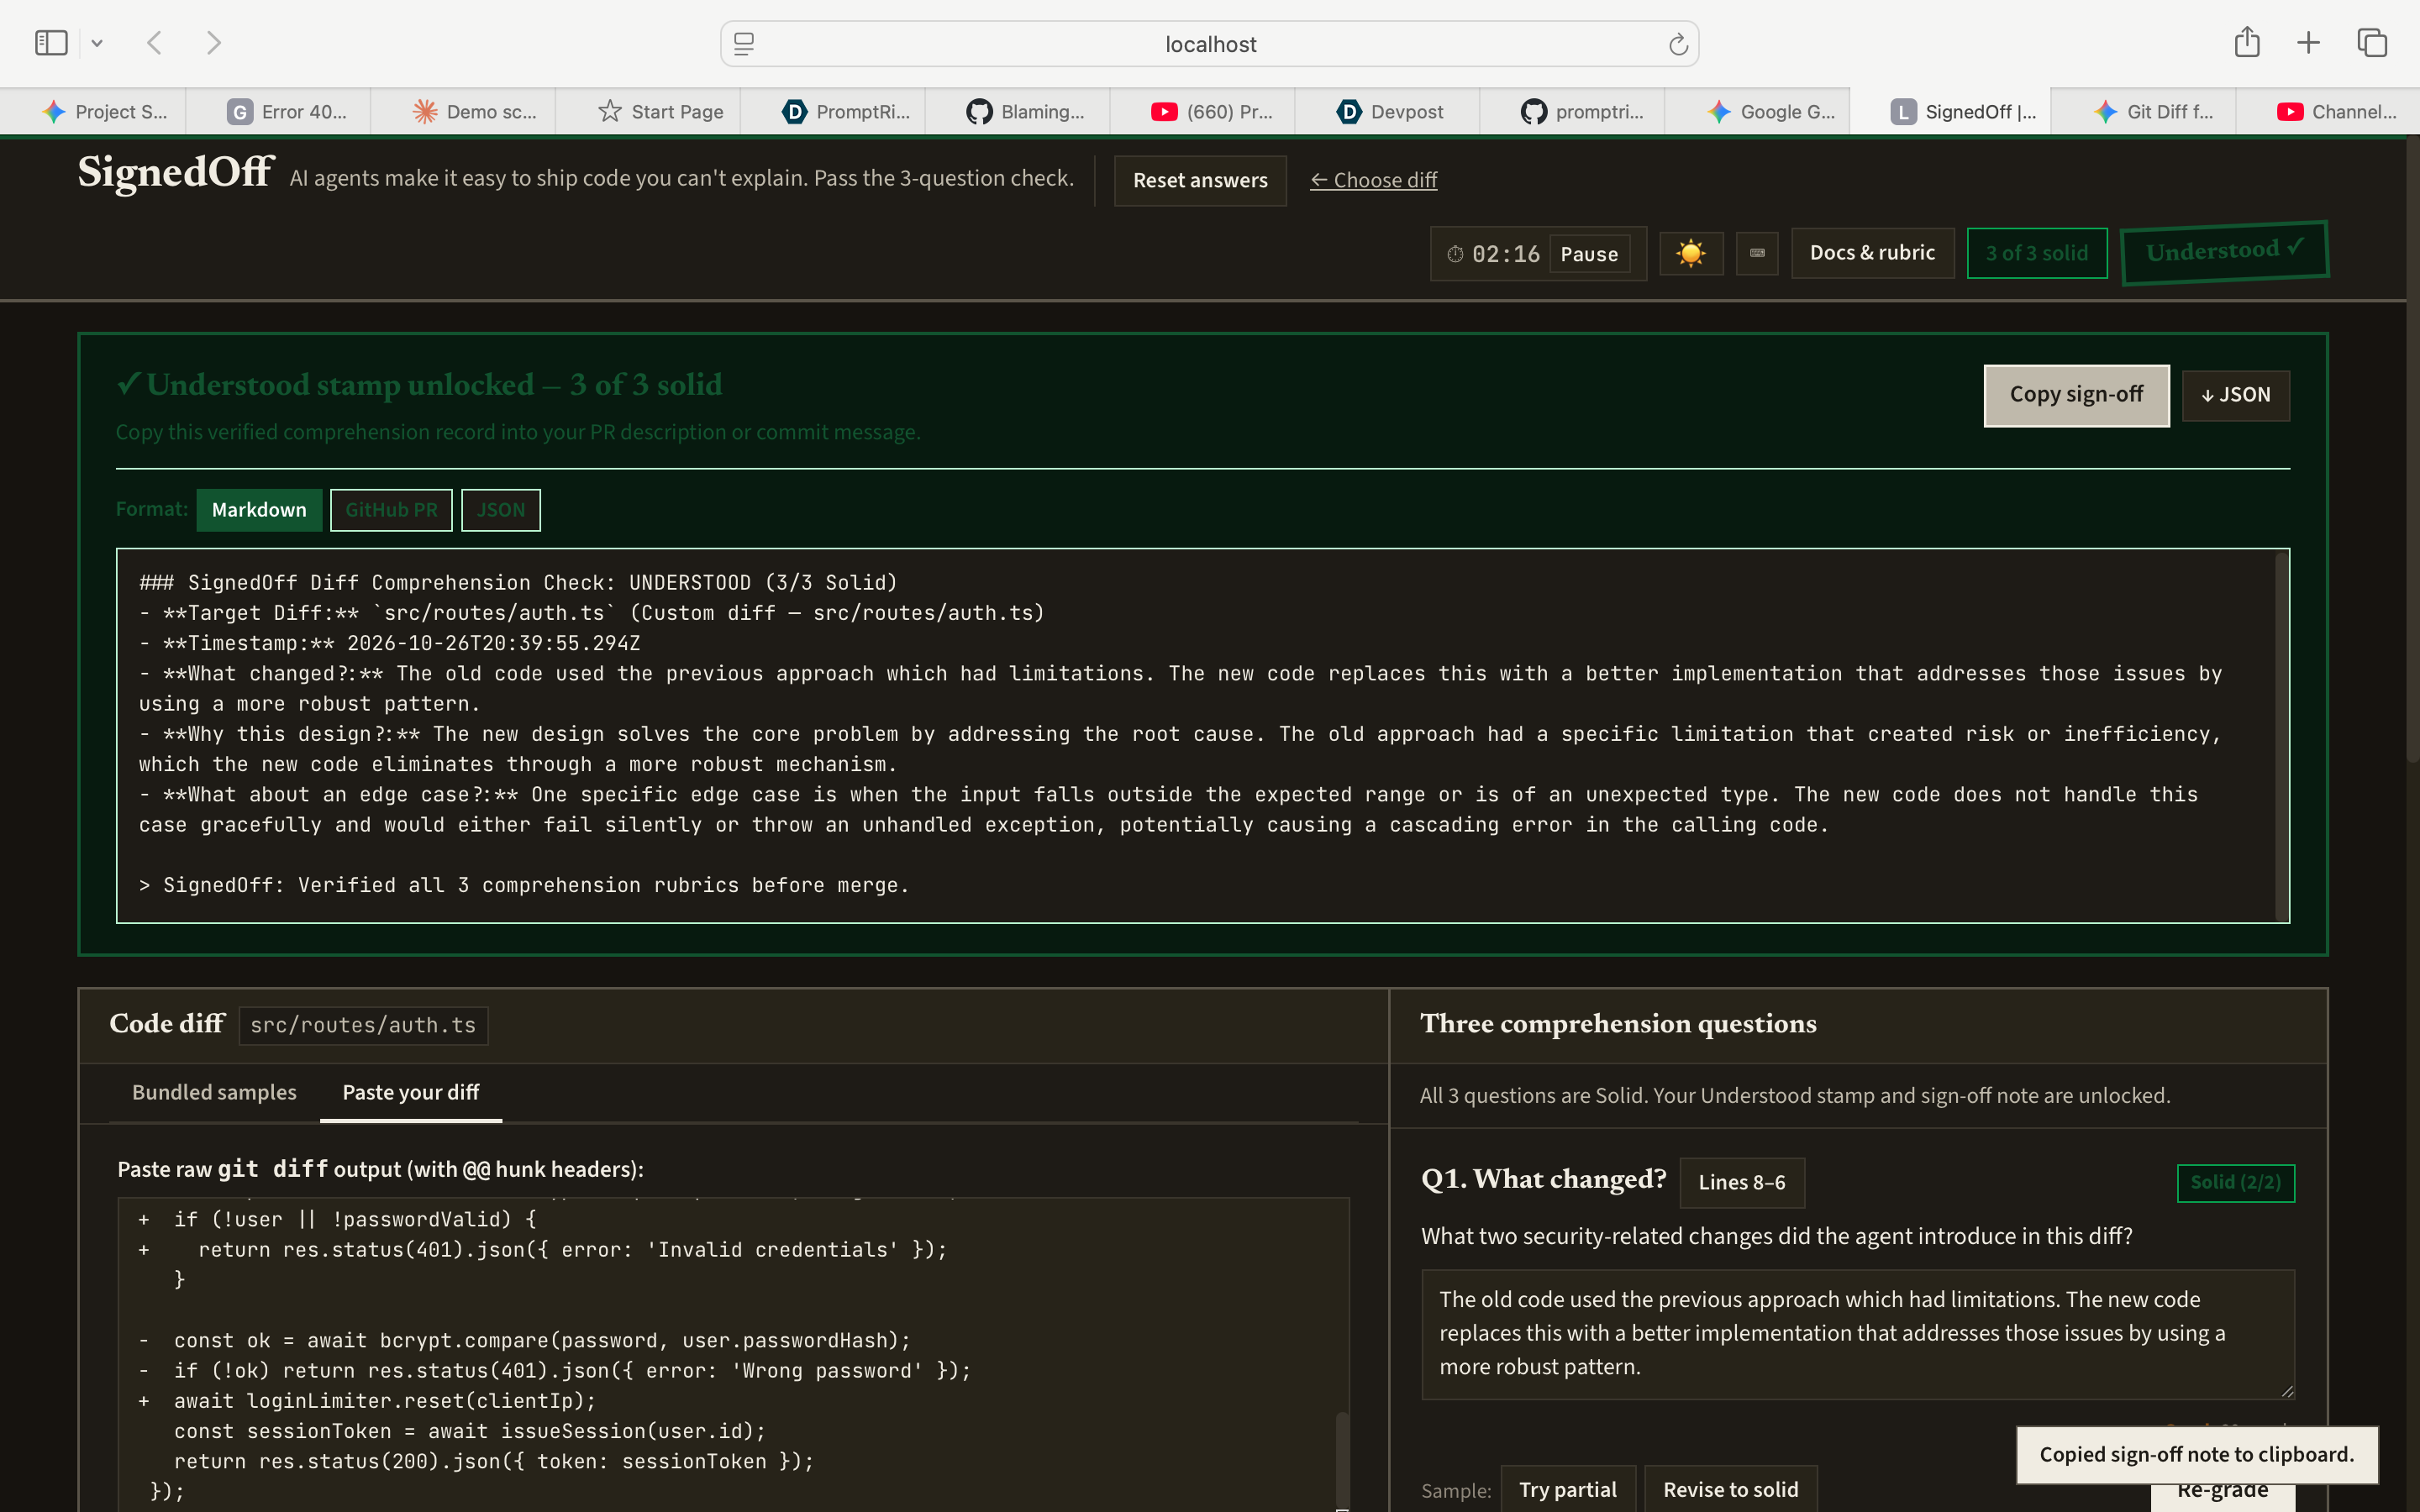
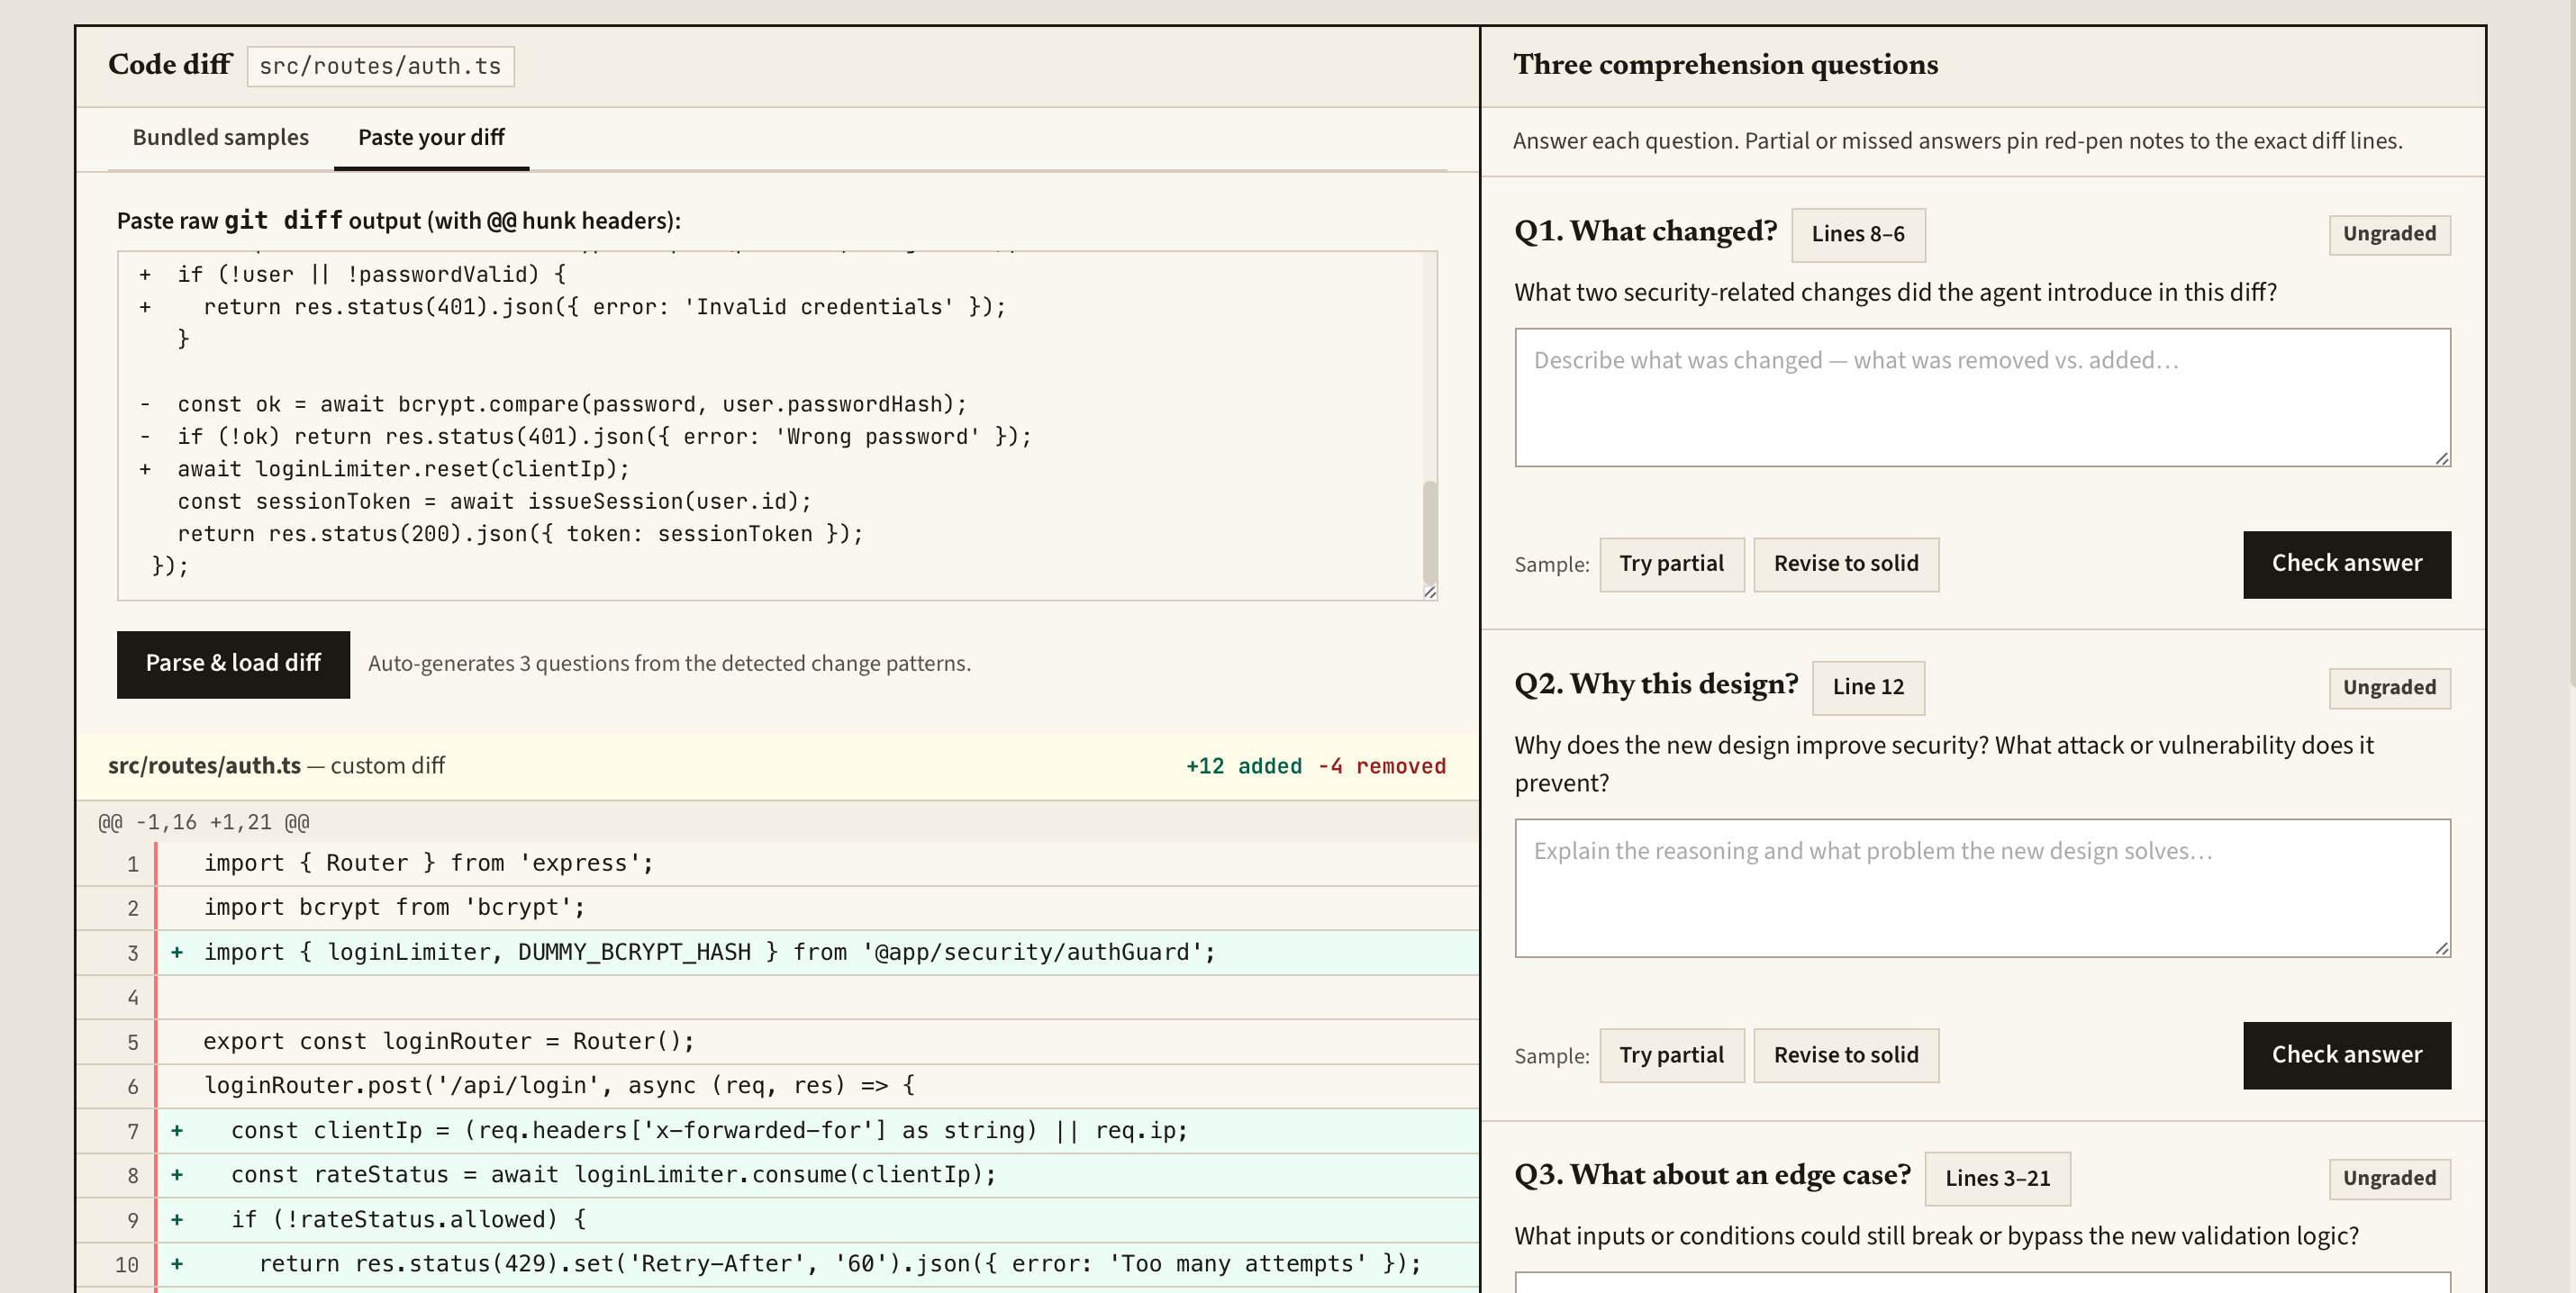
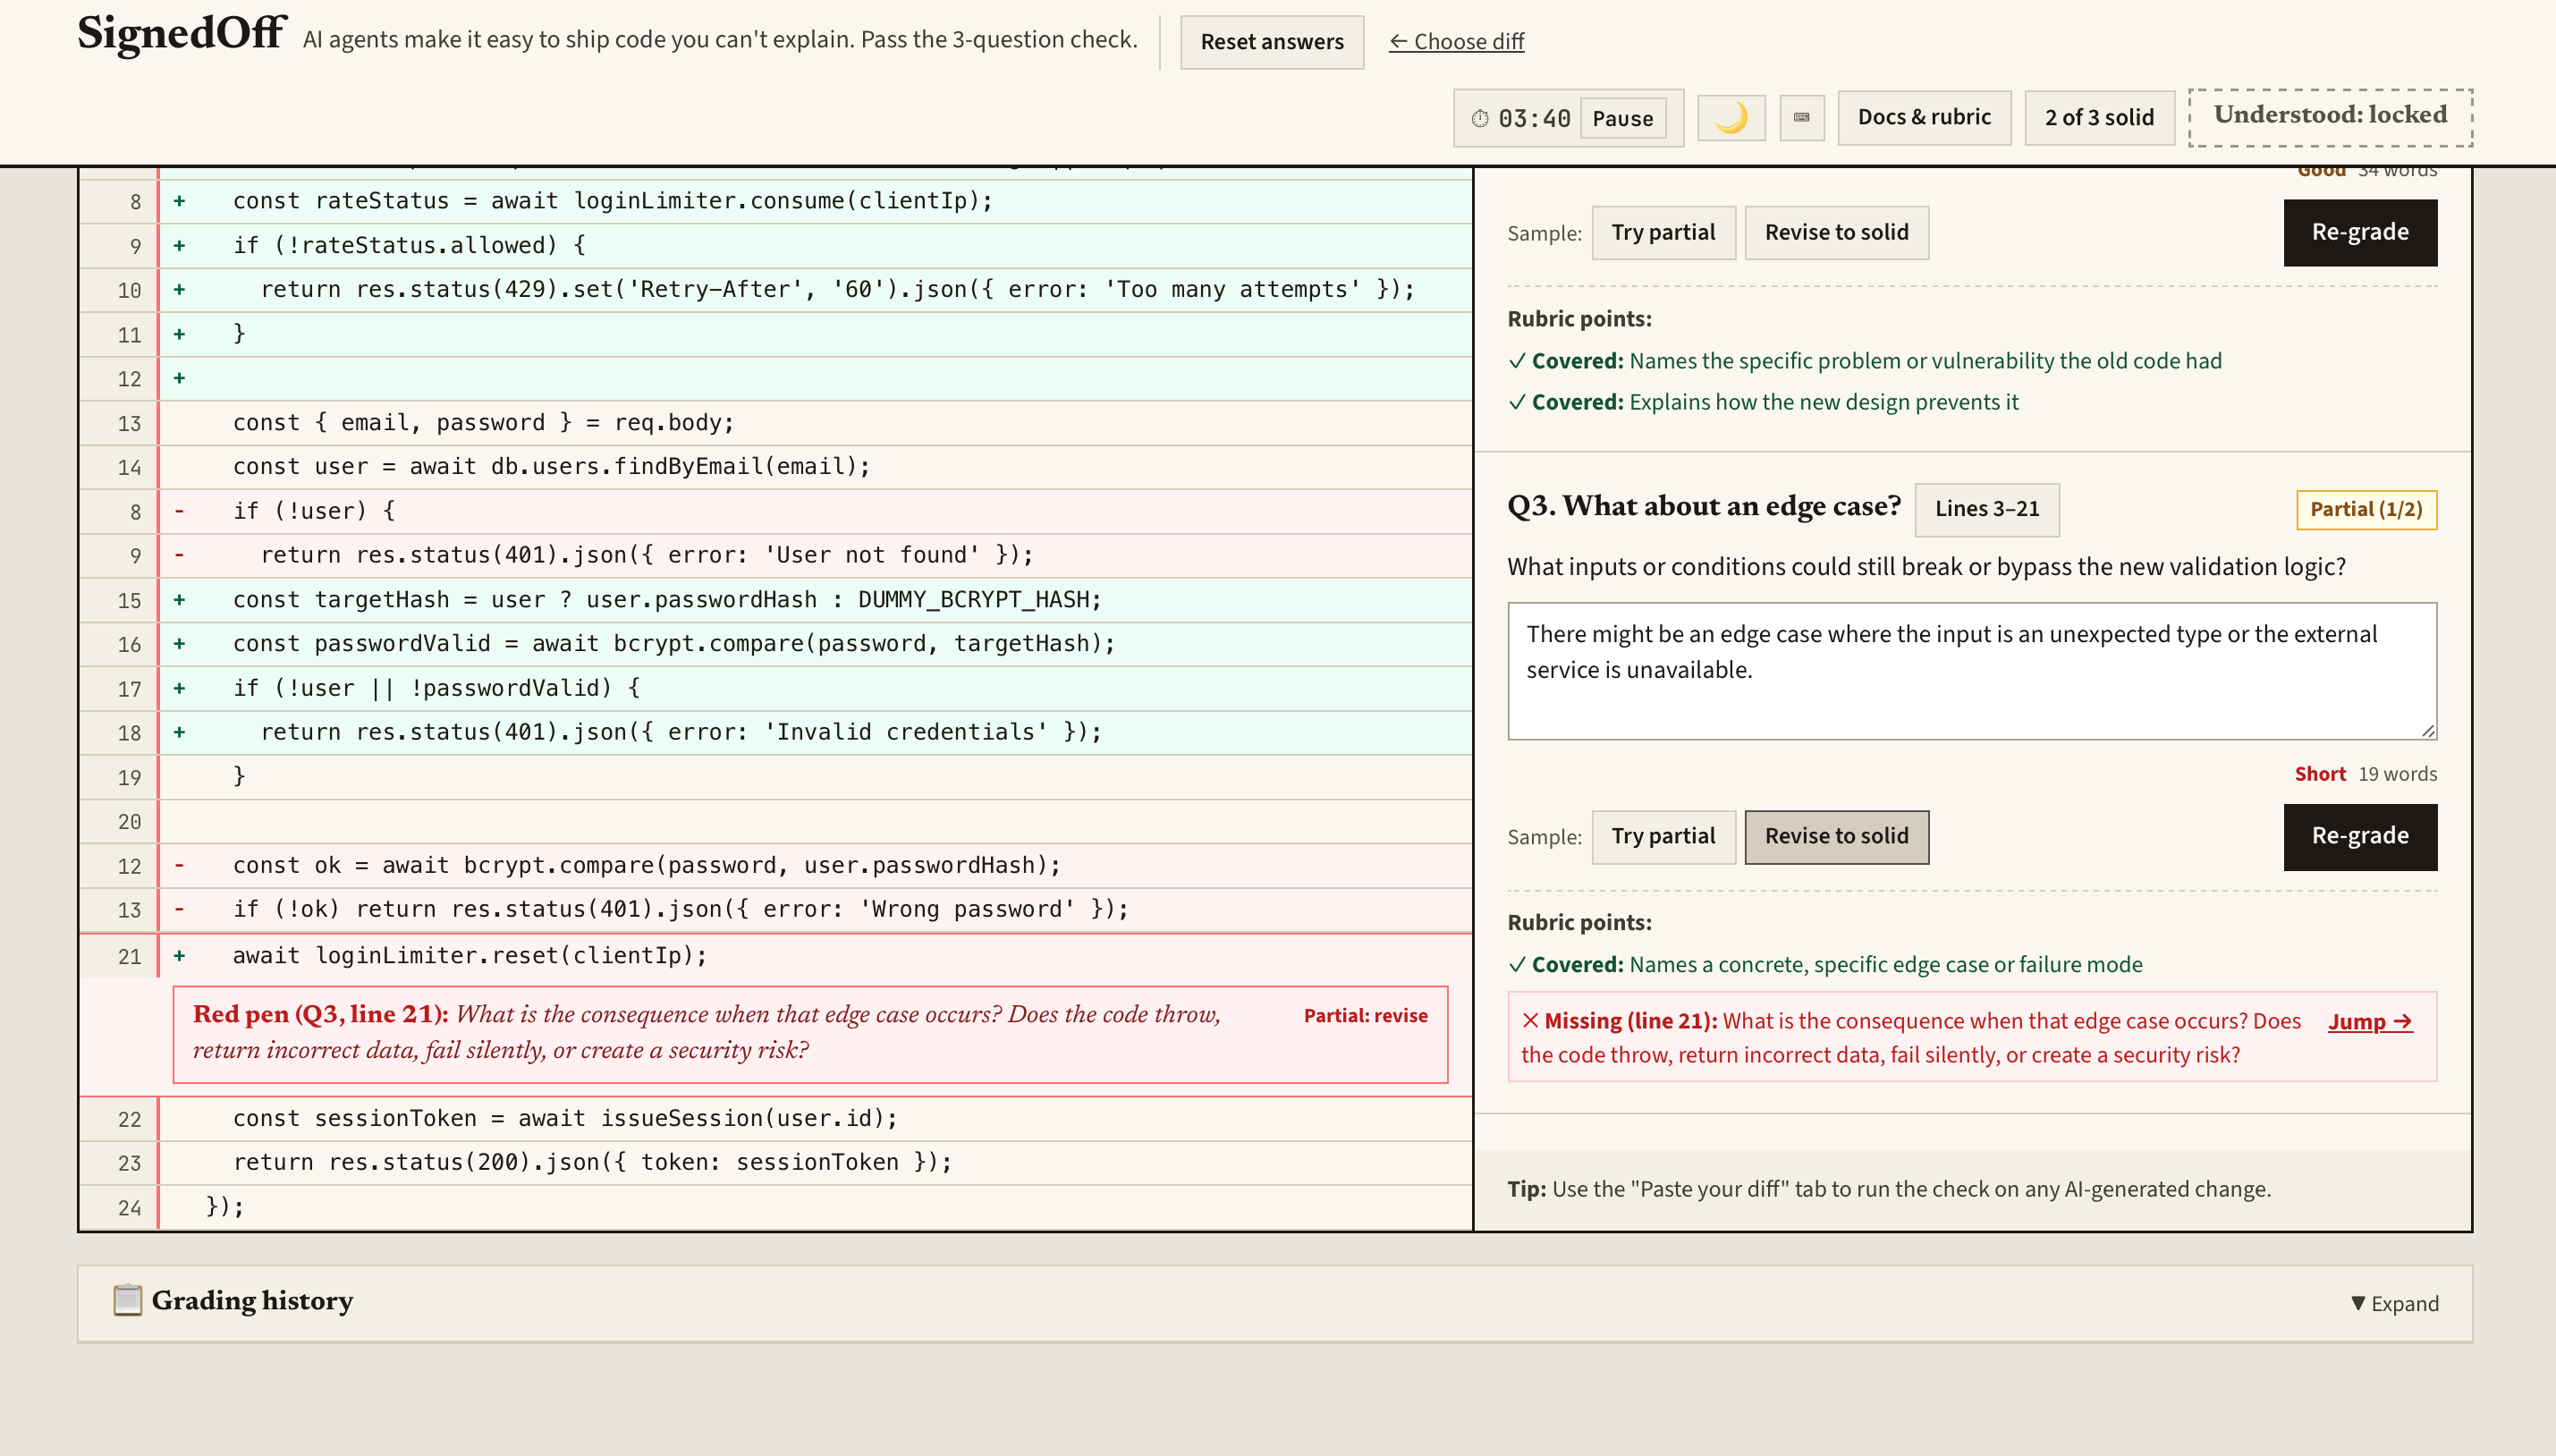
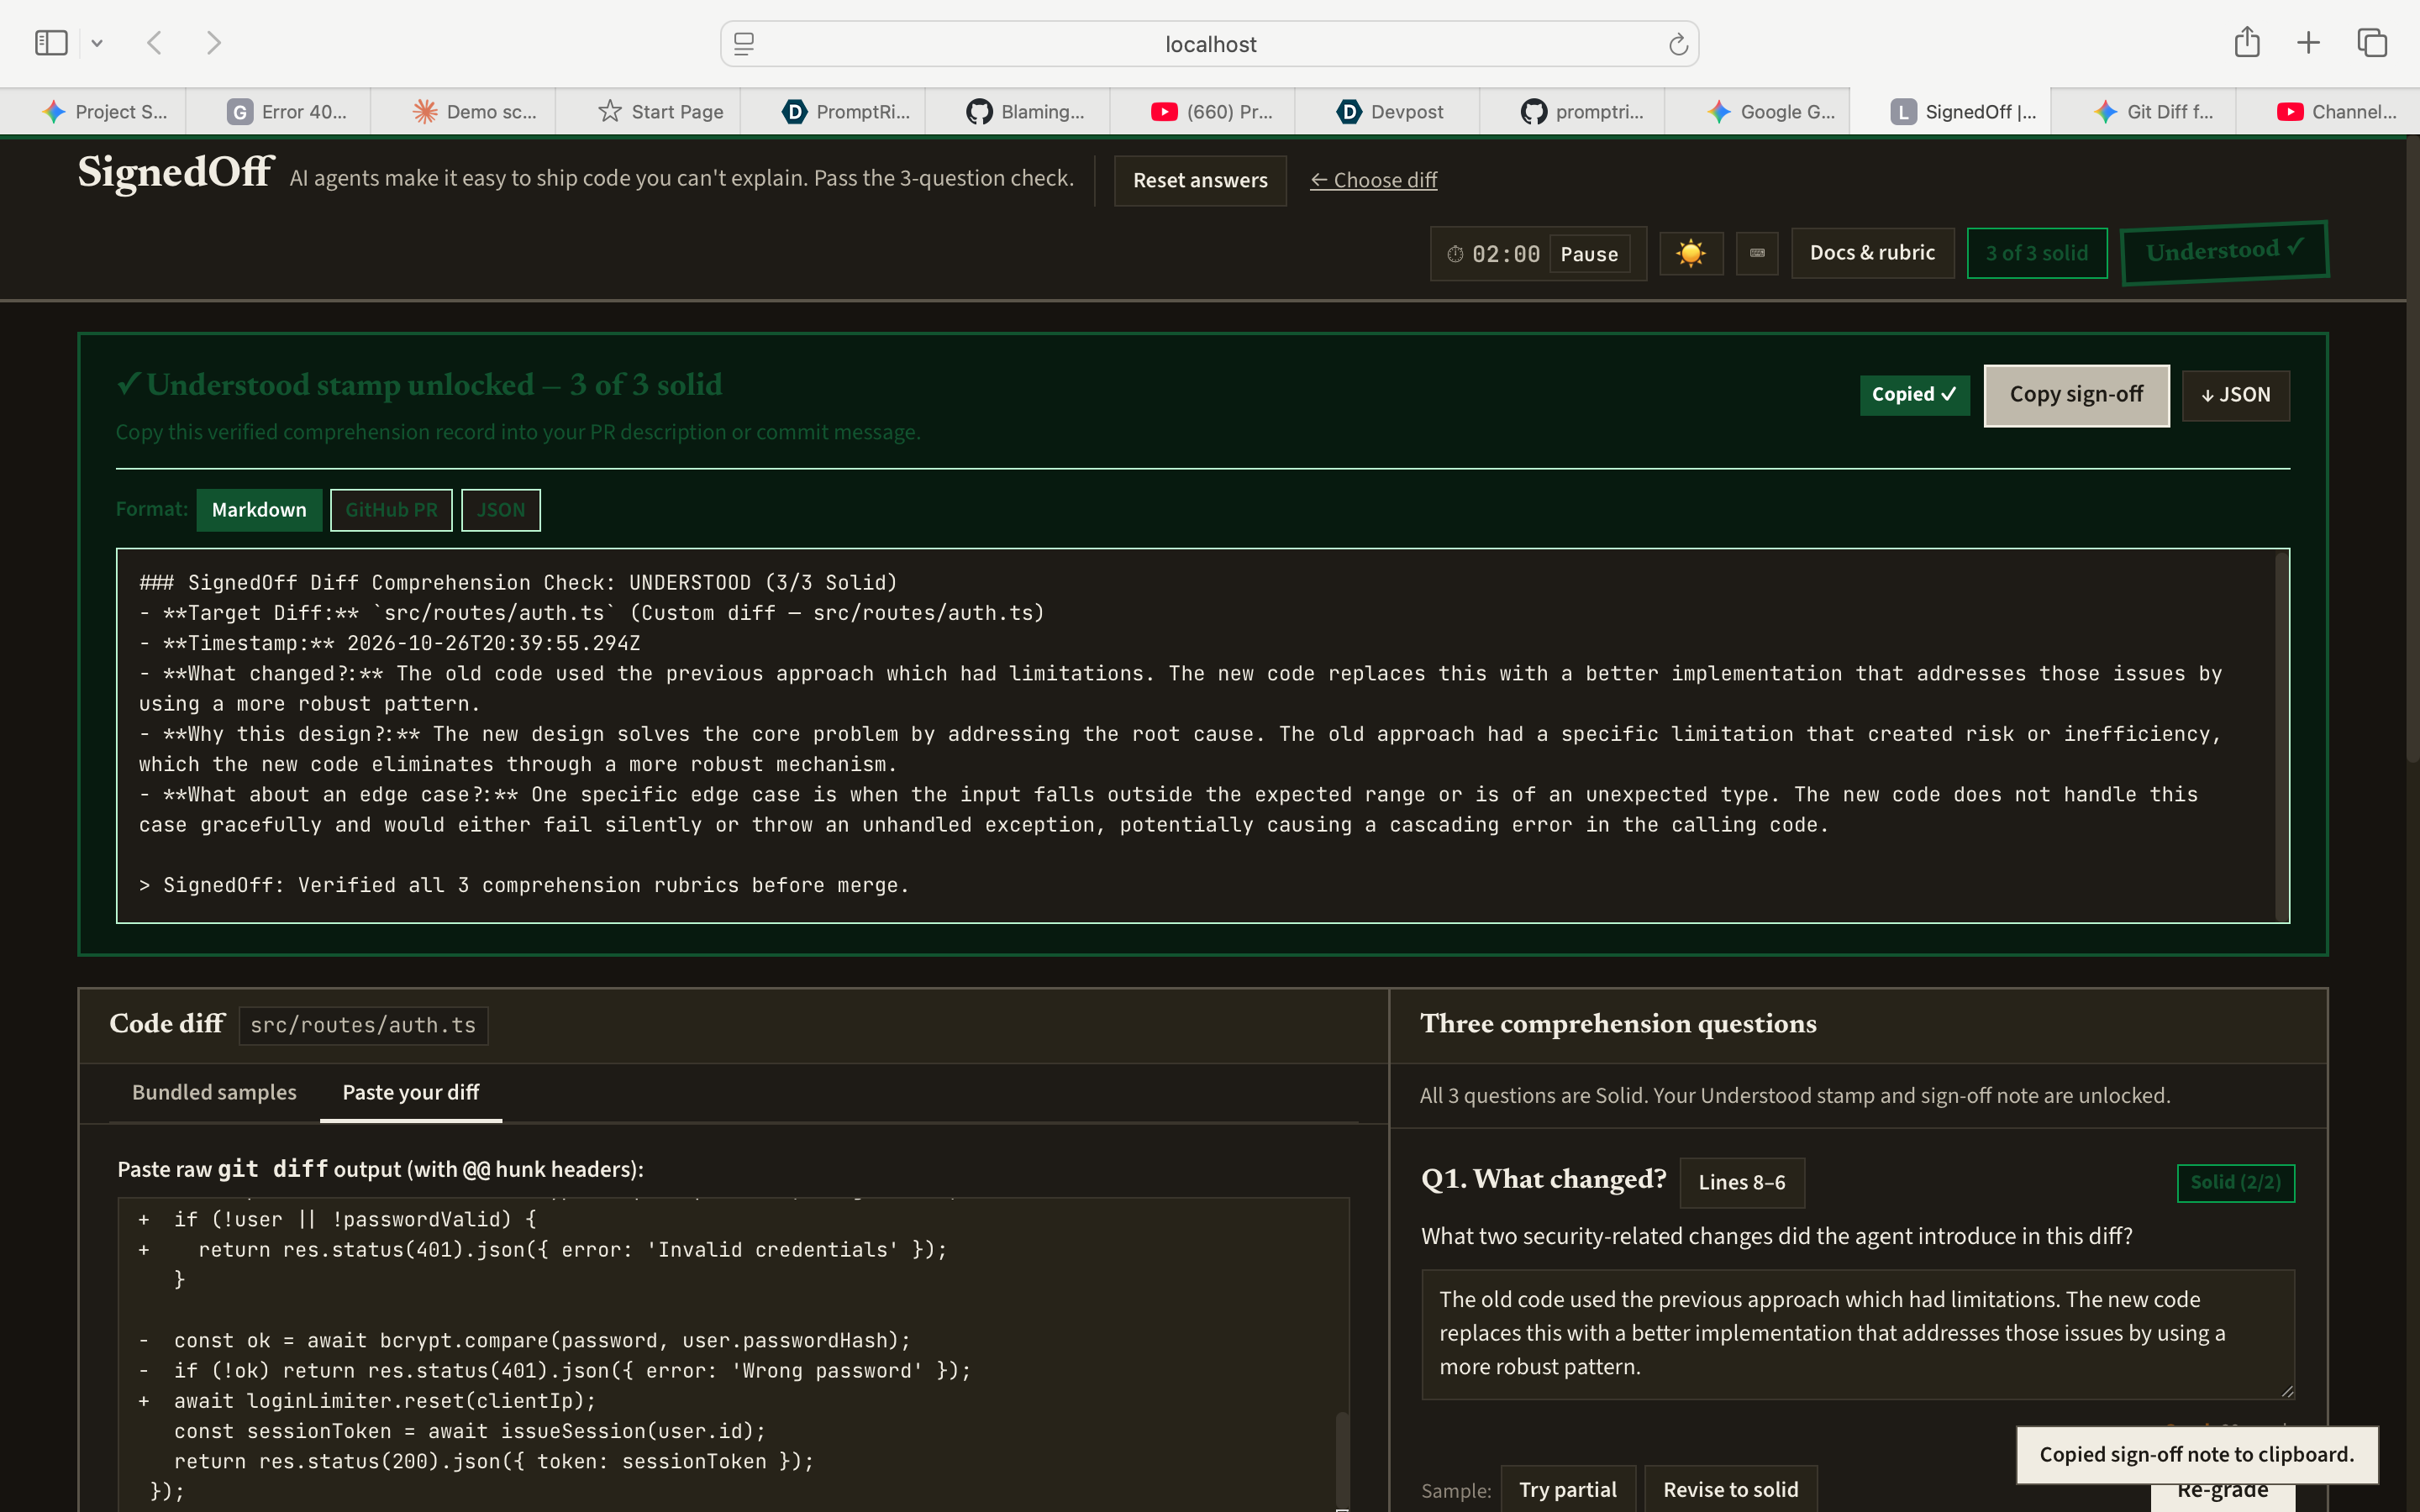
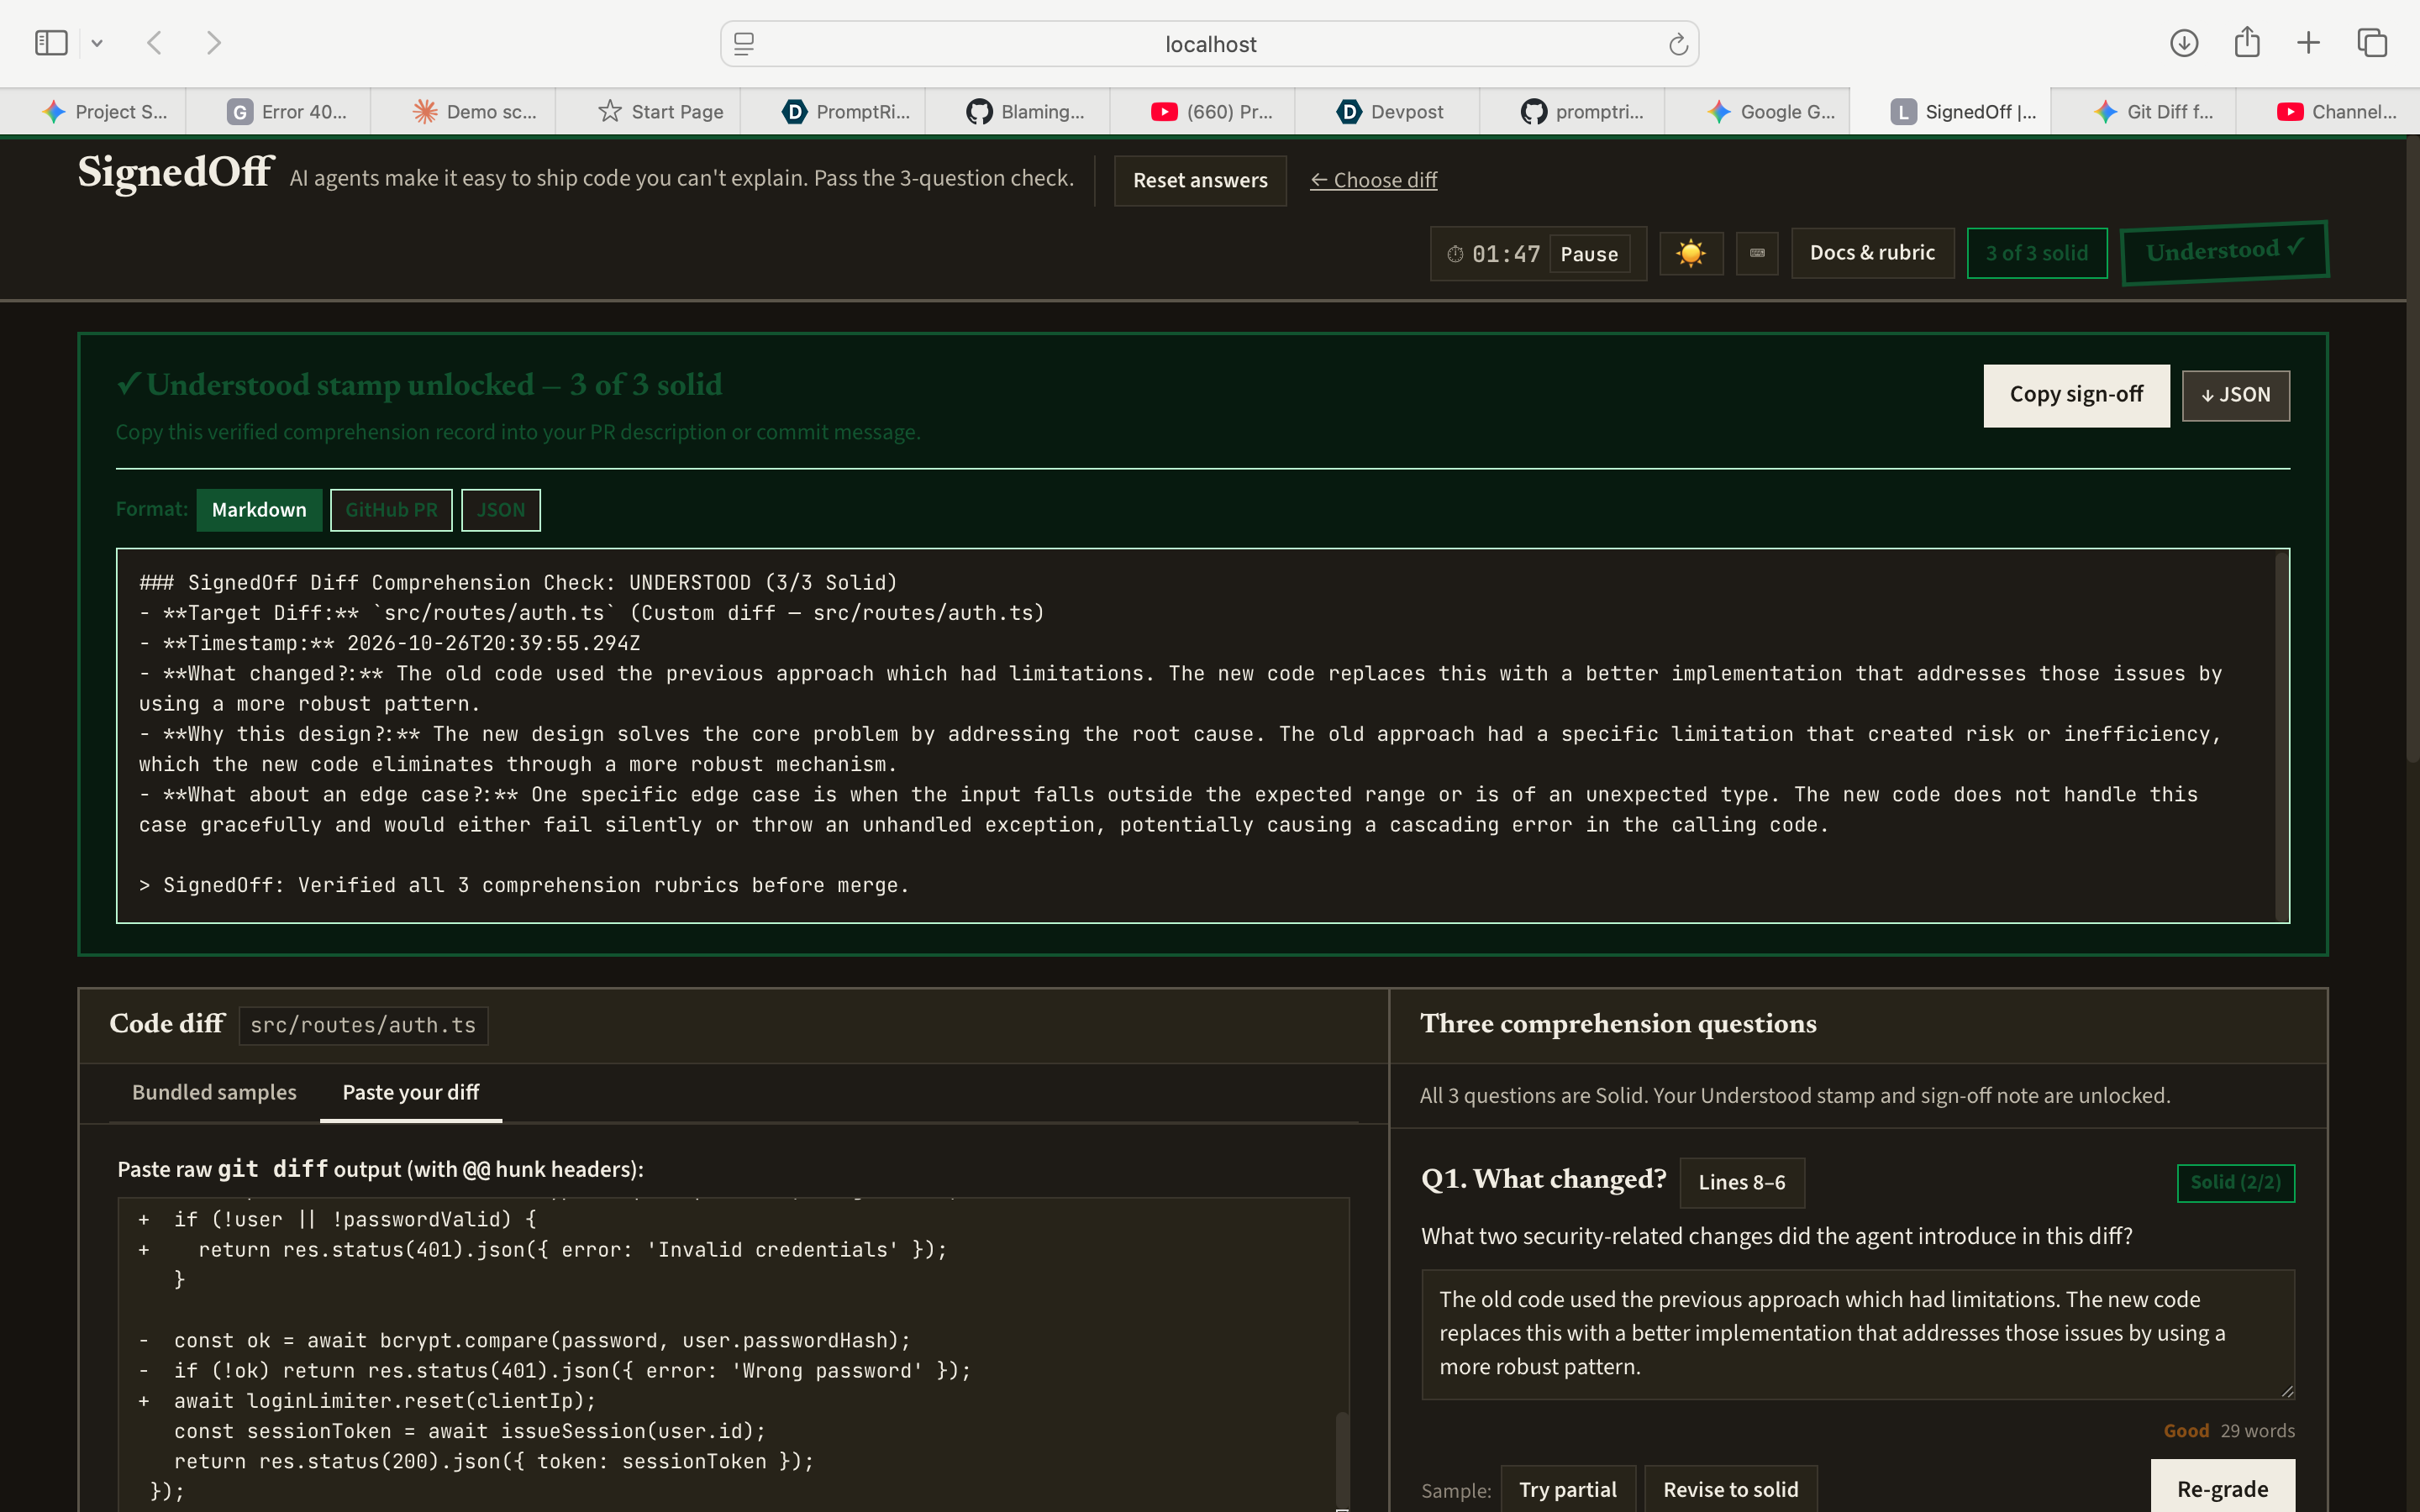
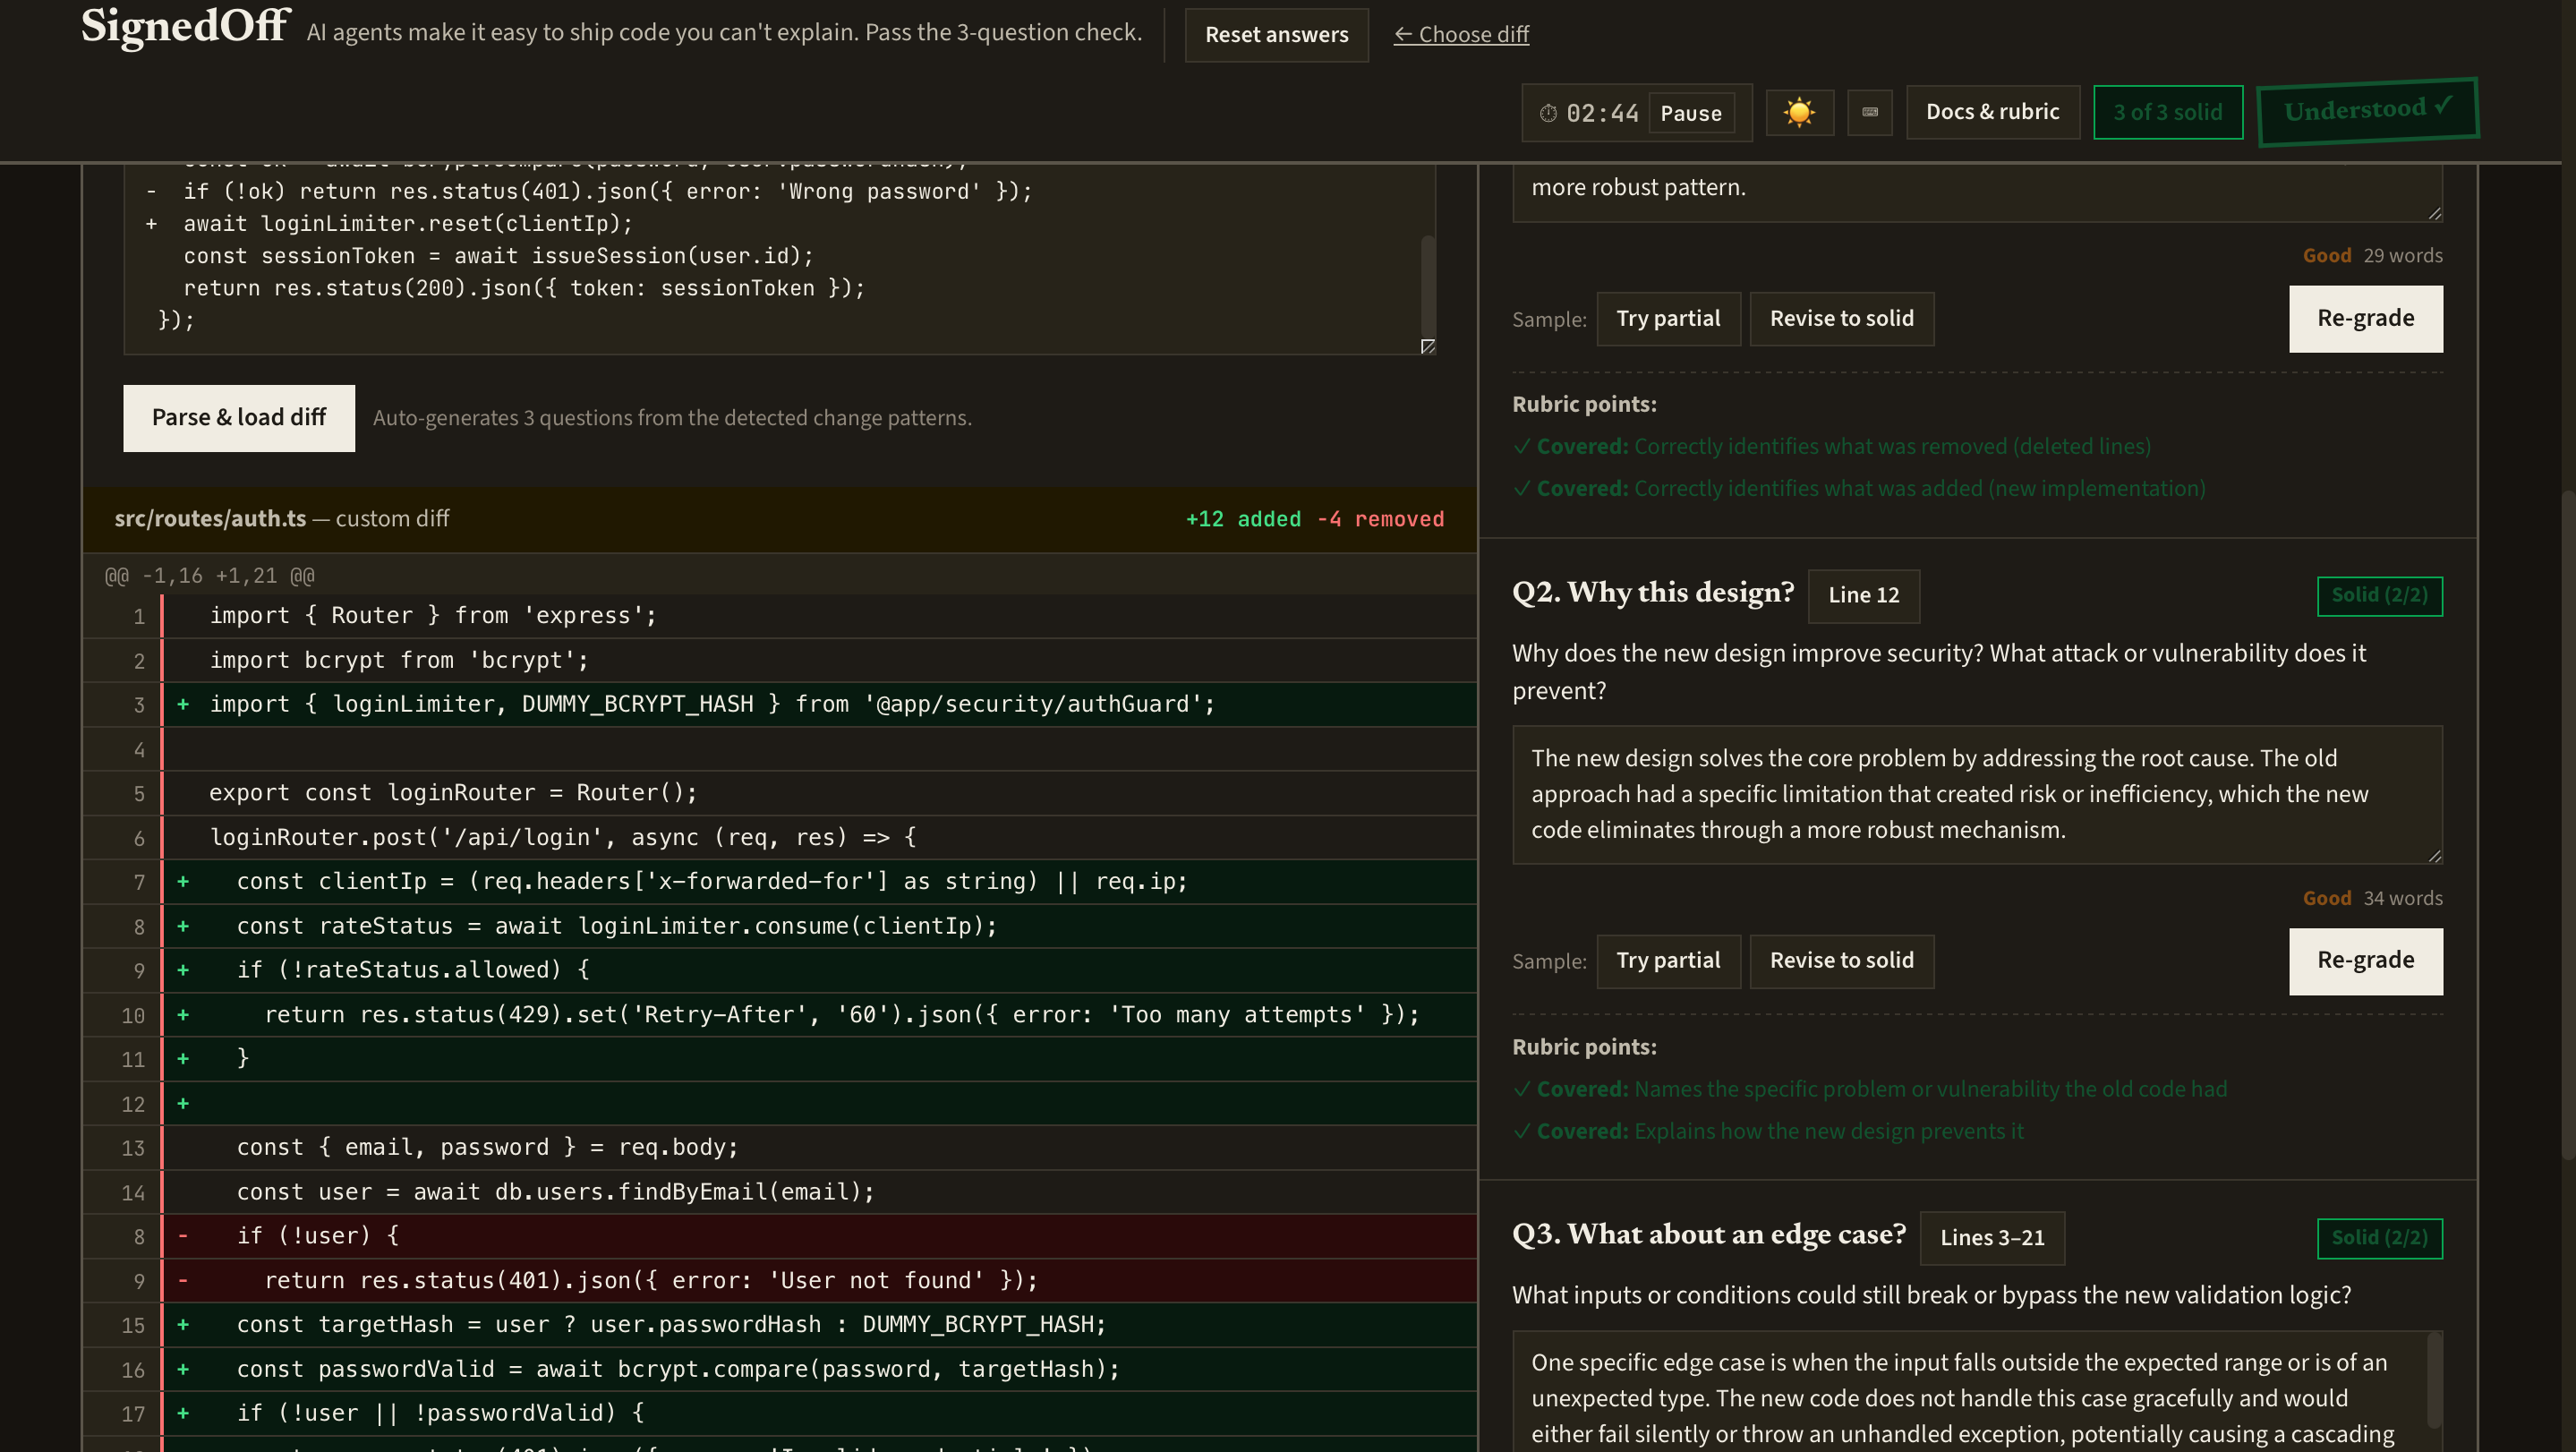
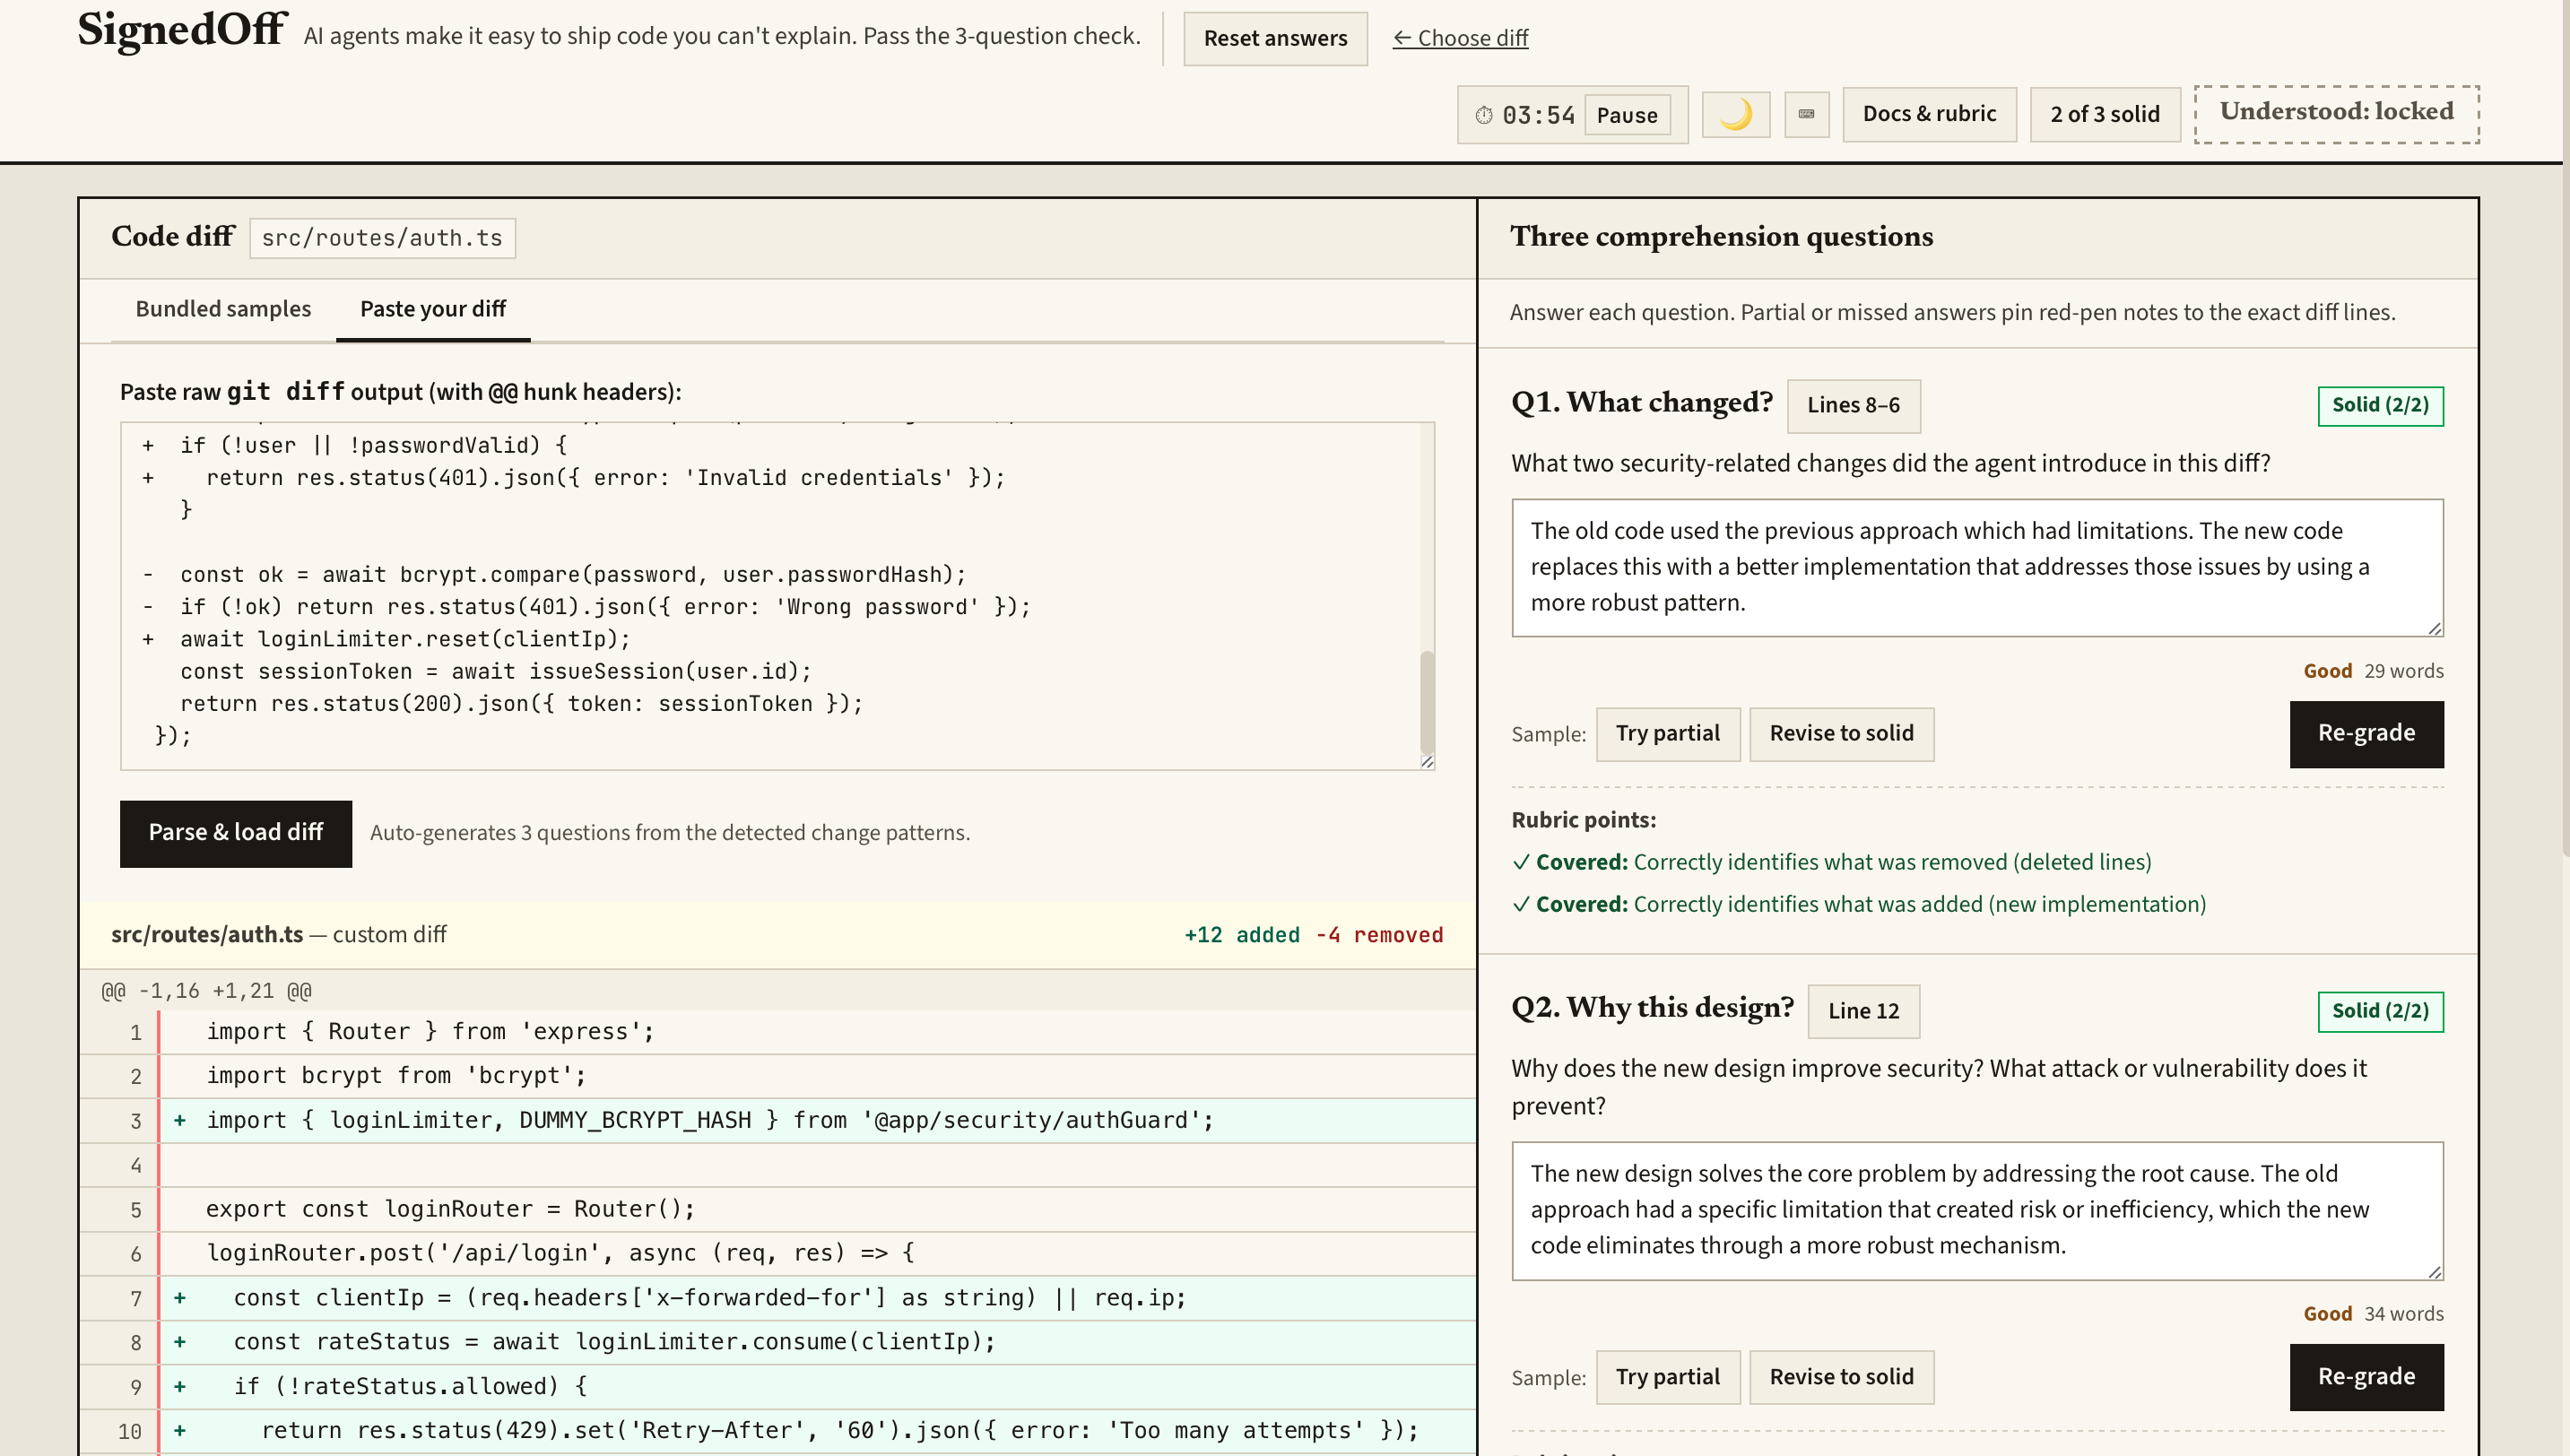
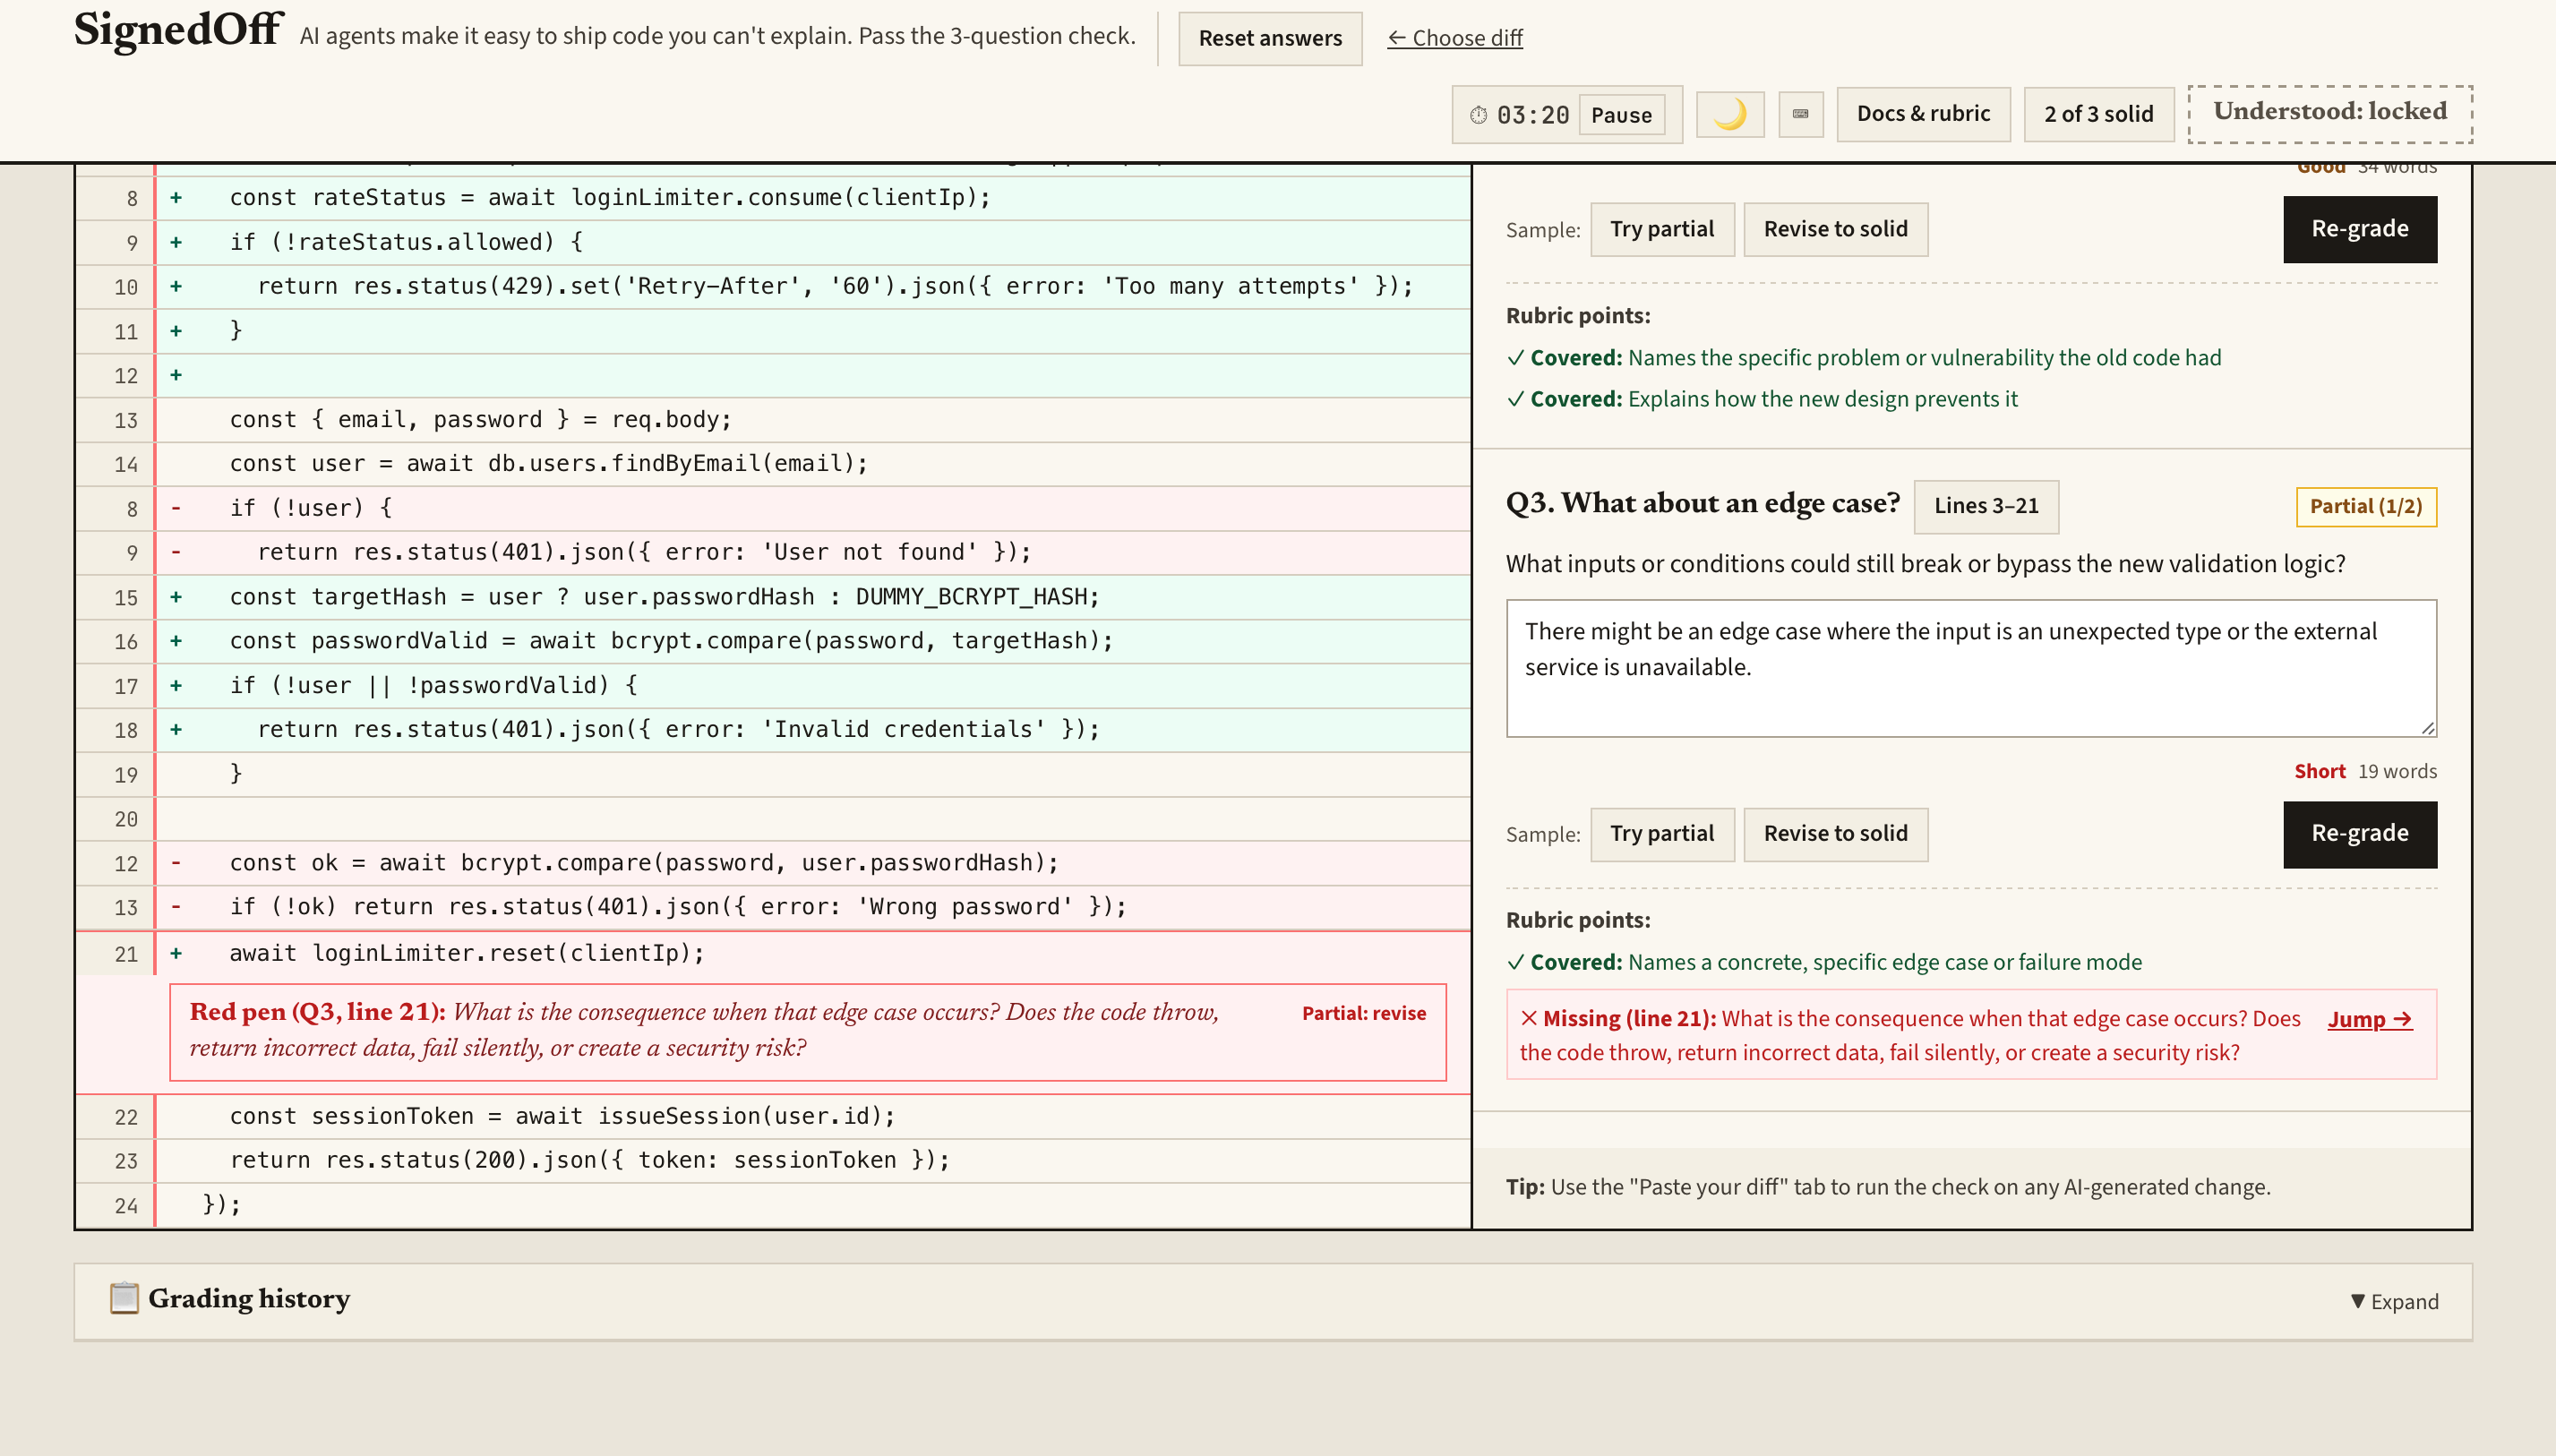
SignedOff allows users to upload documents or agreements, define custom multi-tier approval workflows, invite signatories via secure links, and execute legally binding or cryptographically verified digital signatures. It features real-time tracking of document statuses (Pending, Signed, Rejected), audit trails with IP/timestamp logging, and a clean dashboard for managing all authorization pipelines in one place.
How we built it
- Frontend: Built with React / Next.js and TypeScript, styled using Tailwind CSS for a sleek, responsive, and accessible UI.
- Backend: Powered by Node.js and Express.js, implementing secure RESTful APIs and middleware for role-based access control.
- Database & Storage: Uses PostgreSQL (managed via Prisma ORM) for robust relational data integrity regarding user accounts, signatures, and audit logs, combined with secure cloud object storage for document files.
- Security & Cryptography: Utilizes hashing algorithms and JWT-based session management to ensure document immutability and tamper-proof verification trails.
Challenges we ran into
One of the primary challenges was implementing a reliable audit trail and ensuring that document hashes matched precisely upon signature execution without introducing performance bottlenecks. Managing asynchronous multi-party signing states and handling edge cases where signatories declined or revoked access mid-workflow also required careful state-machine design in the backend.
Accomplishments that we're proud of
- Successfully implementing a cryptographically secure document verification system that instantly flags any unauthorized file modifications.
- Crafting a fluid, intuitive dashboard UI that drastically reduces the cognitive load of tracking multiple pending approvals.
- Establishing a clean, modular full-stack architecture that scales effortlessly.
What we learned
Building SignedOff deepened our mastery of secure authorization patterns, cryptographic hashing for file integrity, and managing complex multi-state workflows in relational databases. We also gained valuable insights into designing frictionless user experiences for document-heavy processes.
What's next for SignedOff
- Integration of blockchain-based timestamping for decentralized proof-of-existence.
- Support for advanced biometric signatures and multi-factor authentication (MFA) prompts directly inside the signing window.
- Enterprise team workspaces with customizable permission hierarchies and webhook integrations.
Built With
- express.js
- git
- jwt
- next.js
- node.js
- postgresql
- prisma
- react
- rest-api
- tailwind-css
- typescript

Log in or sign up for Devpost to join the conversation.