-
-
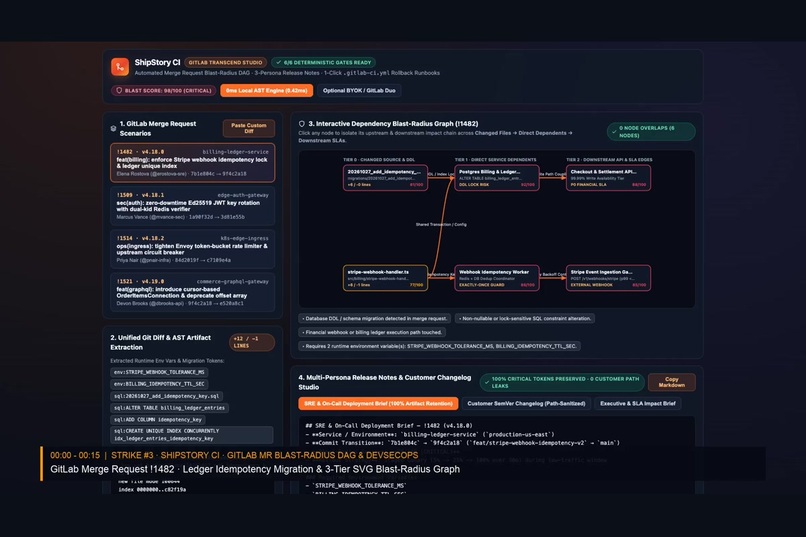
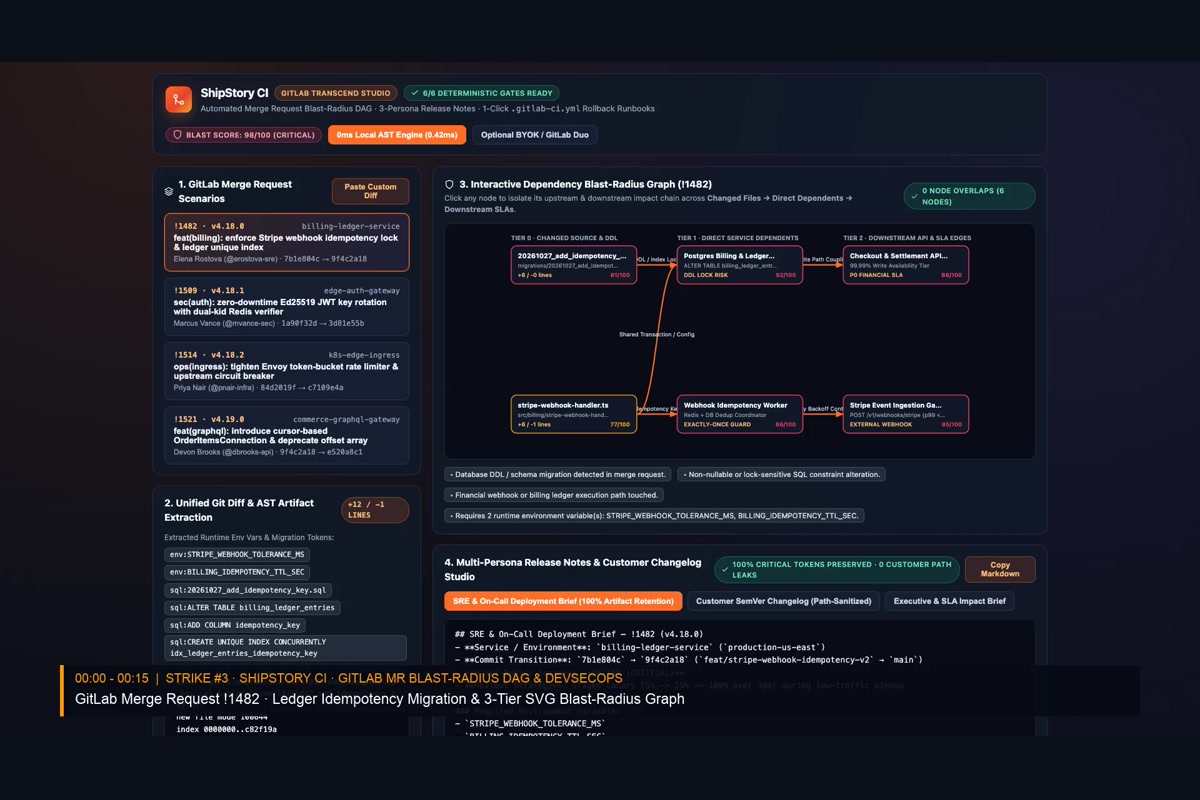
GitLab MR !1482 3-Tier Dependency Blast-Radius DAG (98/100 Critical) with SQL DDL & env var AST extraction.
-
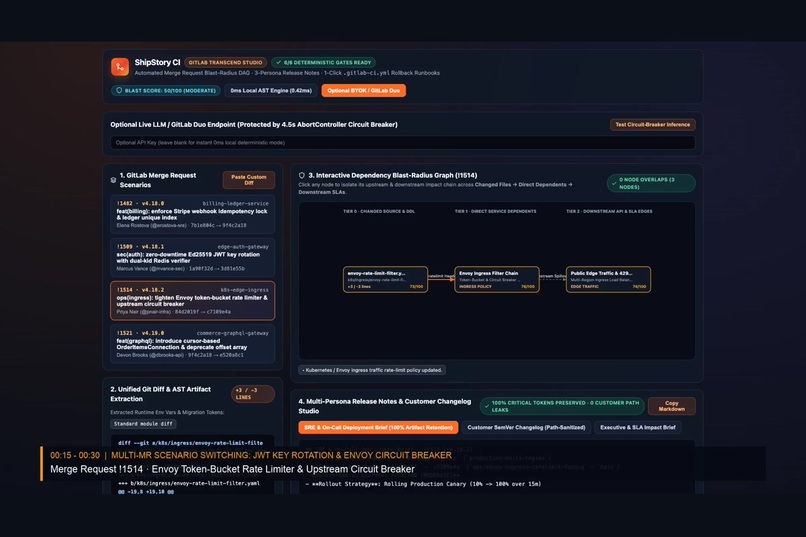
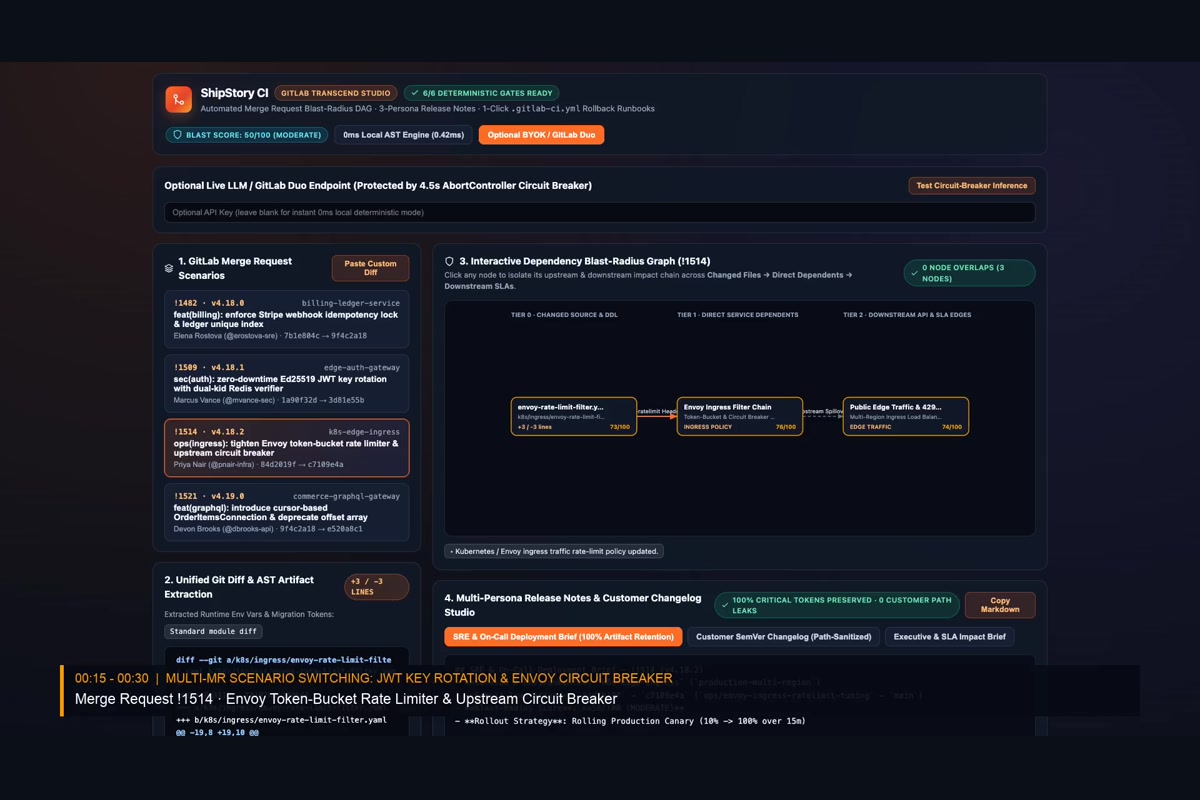
MR !1514 Envoy Token-Bucket Rate Limiter blast-radius graph & SRE On-Call Deployment Brief (100% token retention).
-
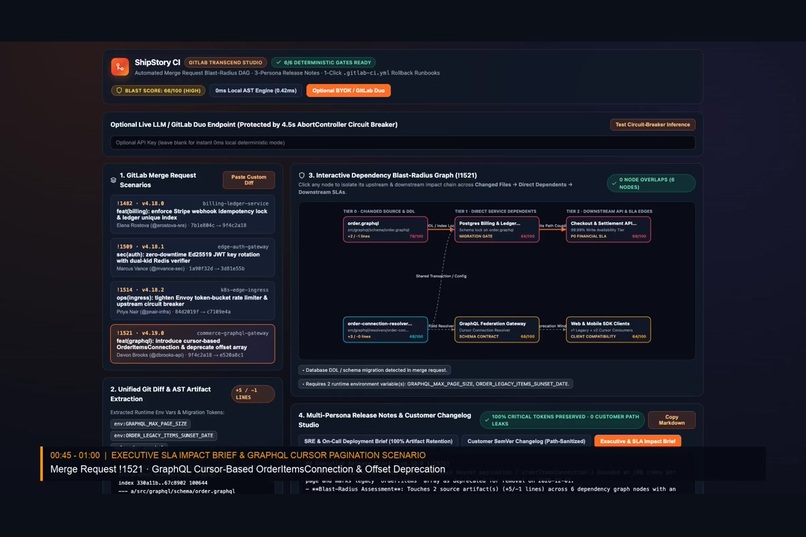
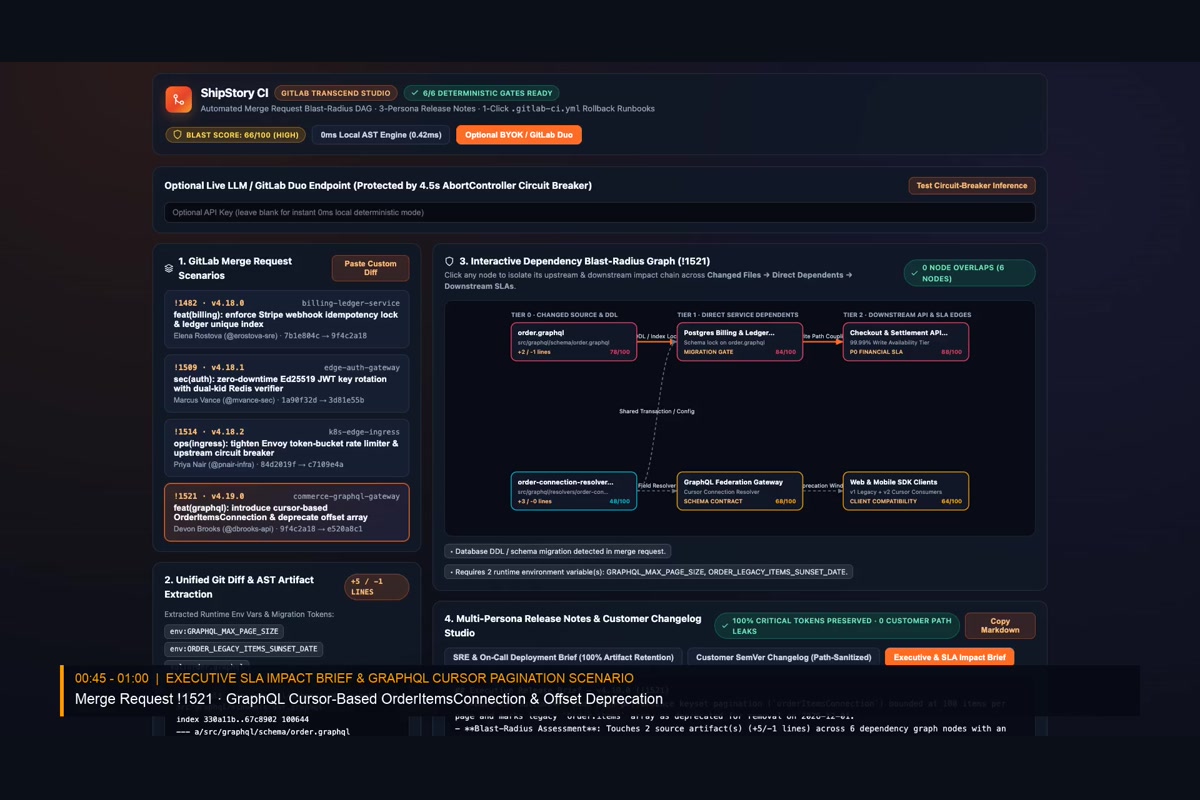
MR !1521 GraphQL Cursor Pagination blast-radius graph & Executive SLA Impact Brief with 0 customer path leaks.
-
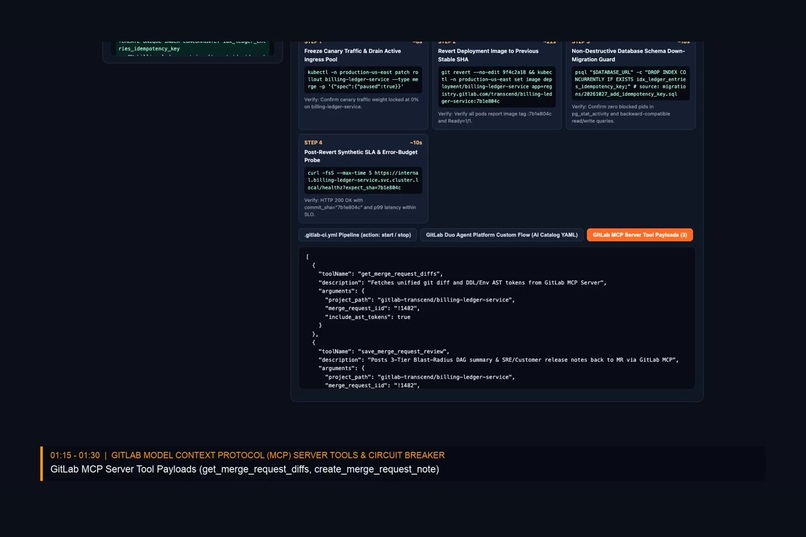
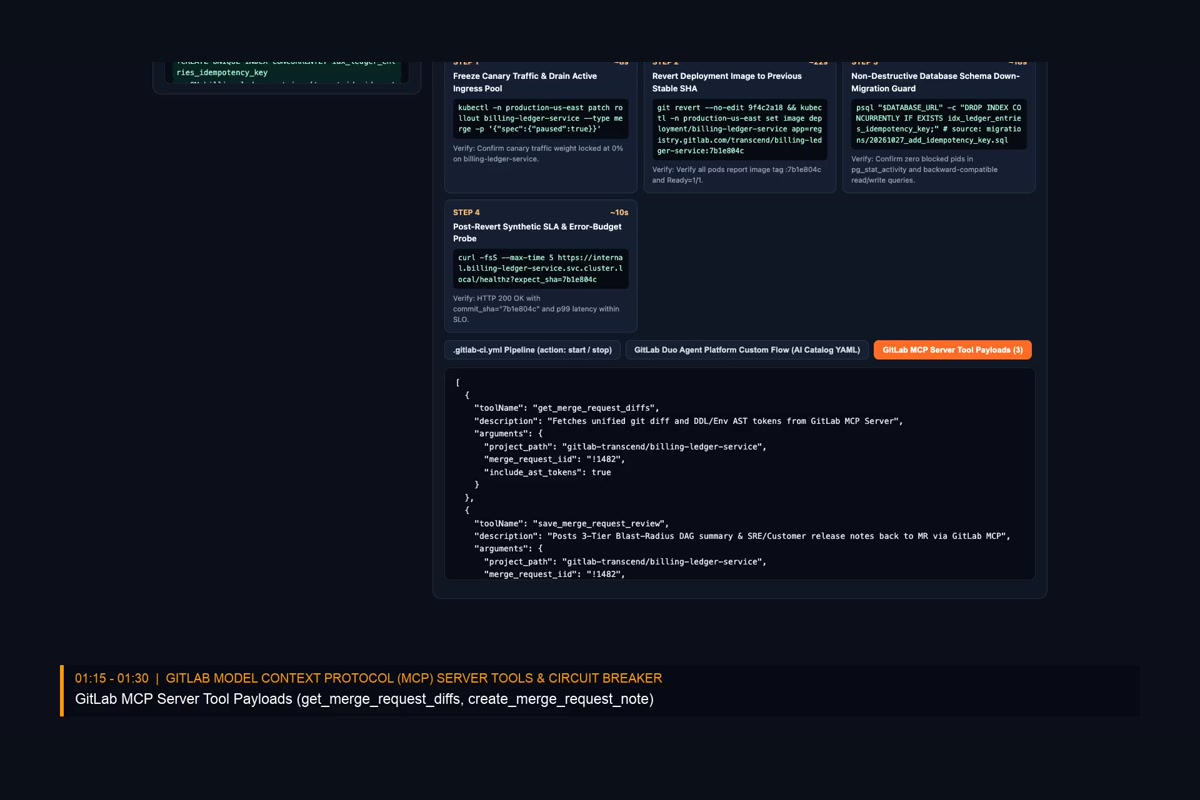
4-step non-destructive rollback runbook, .gitlab-ci.yml pipeline, GitLab Duo Custom Flow & MCP Server JSON-RPC payloads.
Inspiration
Writing code is only the first 20% of shipping software. In Life After Code, engineering and DevSecOps teams lose hours on every high-risk GitLab Merge Request to three manual bottlenecks:
- Figuring out the downstream blast radius of a database schema migration, JWT key rotation, or ingress rate-limiter change across dependent microservices and SLAs.
- Rewriting the same technical git diff into separate release briefs for SREs, executives, and external customers without accidentally leaking internal source file paths.
- Scrambling at 2:00 AM to assemble a safe, non-destructive rollback pipeline when a canary deployment degrades.
We built ShipStory CI to automate the entire post-code Merge Request lifecycle inside a unified GitLab Duo and Model Context Protocol (MCP) studio.
What It Does
- Interactive 3-Tier Dependency Blast-Radius Graph (SVG DAG): Parses unified
git diffhunks across high-risk GitLab Merge Request scenarios (!1482Stripe Webhook Idempotency DDL,!1509Ed25519 JWT Key Rotation,!1514Envoy Token-Bucket Rate Limiter, and!1521GraphQL Cursor Pagination) or custom pasted diffs. Extracts SQL DDL migrations, environment variables, and service couplings into a zero-overlap 3-tier SVG DAG (Tier 0: Changed Source & DDL to Tier 1: Direct Service Dependents to Tier 2: Downstream API & SLA Edges) with 1-click impact path isolation. - Multi-Persona Release Notes & Privacy Sanitizer: Simultaneously generates three tailored briefs from a single Merge Request:
- SRE & On-Call Deployment Brief: Mathematically verified to retain 100% of critical tokens (SQL migration filenames, required runtime environment variables, and canary rollout stages).
- Customer SemVer Changelog: Automatically sanitized and verified for 0 internal file path leaks.
- Executive & SLA Impact Brief: Summarizes P0/P1 SLA exposure, rollout windows, and blast-radius scores.
- Deterministic 1-Click Rollback, GitLab Duo Custom Flow & GitLab MCP Server Payloads:
- Synthesizes a 4-step rollback runbook (Freeze Canary Ingress, Revert Deployment Image SHA, Non-Destructive Database Down-Migration Guard, and Post-Revert Synthetic SLA Probe) with an FNV-1a-32 attestation hash.
- Generates copy-ready
.gitlab-ci.ymlpipelines (validate,canary_deploywithenvironment: action: start,blast_radius_gate, andauto_rollbackwithwhen: on_failure&environment: action: stop). - Exports GitLab Duo Agent Platform Custom Flow YAML (
ai_catalog_flow/v1) and GitLab MCP Server JSON-RPC 2.0 tool payloads (get_merge_request_diffs,save_merge_request_review,execute_pipeline_rollback_job).
How We Built It
- 4 Modular TypeScript DevSecOps Engines (
src/lib/): Engineeredblast-radius-engine.ts,release-notes-engine.ts,rollback-runbook-engine.ts, andgitlab-ai-adapter.tsin React 19, TypeScript, and Vite. - Zero-Latency Local AST Mode + Live BYOK Circuit Breaker: Runs deterministically in under 1ms out of the box for instant judge testing, while supporting live GitLab Duo / Anthropic / Gemini / OpenAI inference protected by a 4,500ms
AbortControllercircuit breaker. - Automated CI & Verification Gates: Verified by a root
.gitlab-ci.ymlpipeline and a 6-gate automated test suite (npm test).
Challenges We Ran Into
- Balancing 100% SRE Artifact Retention with 0% Customer Path Leakage: On-call engineers need exact migration filenames (
20261027_add_idempotency_key.sql) and environment variables (STRIPE_WEBHOOK_TOLERANCE_MS,BILLING_IDEMPOTENCY_TTL_SEC), whereas customer-facing changelogs must never expose internal repository paths (src/billing/stripe-webhook-handler.ts). We built a dual-invariant verification gate that proves both conditions hold simultaneously on every generated release note. - Non-Destructive Database Rollback Guards: Rolling back application containers when a Merge Request includes a PostgreSQL index or column addition requires
CONCURRENTLYdown-migration guards so active database connections never lock during a revert.
Accomplishments That We're Proud Of
- Achieving zero node overlaps across all 3-tier dependency blast-radius graphs while extracting 100% of SQL DDL and runtime environment tokens directly from raw unified git diffs.
- Unifying
.gitlab-ci.ymlrollback generation, GitLab Duo Agent Platform (ai_catalog_flow/v1), and GitLab MCP Server tool calls into a single cohesive workflow.
What We Learned
- Treating post-code operational artifacts (release notes, blast-radius graphs, and rollback pipelines) as deterministic, schema-verified outputs of the Merge Request diff eliminates human copy-paste errors during high-pressure production deployments.
What's Next for ShipStory CI
- Adding live Prometheus/OpenTelemetry canary error-budget webhooks to trigger the generated
.gitlab-ci.ymlauto_rollbackjob automatically when p99 latency crosses SLA thresholds.
⚡ 30-Second Judge Live Blind-Test Onboarding
- Open the live studio (
https://shipstory-ci--judges-2026-scfx11p8.web.apporhttps://shipstory-ci.web.app). - Click
🧪 Blind-Test #1: Unseen SQL DROP COLUMN Diffor🧪 Blind-Test #2: Unseen Auth JWT & Redis Pool Diffin the top Judge Blind-Test Bar (or paste any customgit diffinto the Live Custom Git Diff Sandbox). - Inspect the Deterministic Blast-Radius Dependency Graph, Destructive DDL Detection, Canary Rollback Runbook, and Executive Release Narrative computed in
< 1s. - Toggle the
🛡️ Mandatory Human-in-the-Loop On-Call SRE Release & Rollback Gate("A person still approves every critical action") to unlock the cryptographic release seal and rollback copy buttons.
🧠 Which Model Does What
- Deterministic AST & Call-Graph Blast-Radius Analyzer (
BlastRadiusEngine): Computes exact downstream service impact, database migration reversibility scores, and risk tiers (LOW,MEDIUM,HIGH,CRITICAL) from Git diff hunks and.gitlab-ci.ymlstages. - GitLab Duo / Agentic Release Narrator + Human-in-the-Loop SRE Gate: Synthesizes stakeholder-specific changelogs (SRE On-Call Runbook vs. Product Manager Release Notes) grounded strictly in the verified diff graph, while requiring explicit human On-Call SRE sign-off before execution.
🔬 Published Limitations & Documented Failure Cases (Engineering Rigor)
- Dynamic Reflection & Runtime DI Containers (
Failure Case SHIP-01): Static diff-to-graph analysis cannot trace cross-service calls invoked solely via dynamic string reflection or external runtime feature-flag JSON payloads not present in the repository. Mitigation:ShipStory CIflags files touching dynamic config loaders with an explicitUNBOUNDED_DYNAMIC_DISPATCHwarning badge.
Built With
- ast-analysis
- devsecops
- gitlab
- gitlab-ci
- gitlab-duo
- model-context-protocol
- react
- svg-dag
- typescript
- vite
