-
-

Logo
-
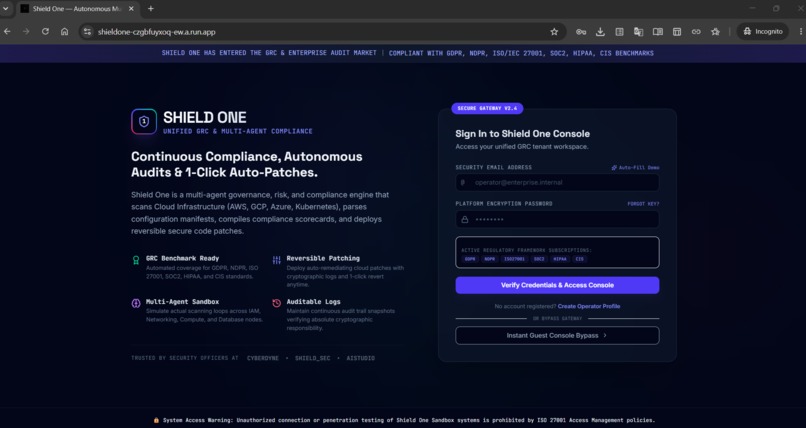
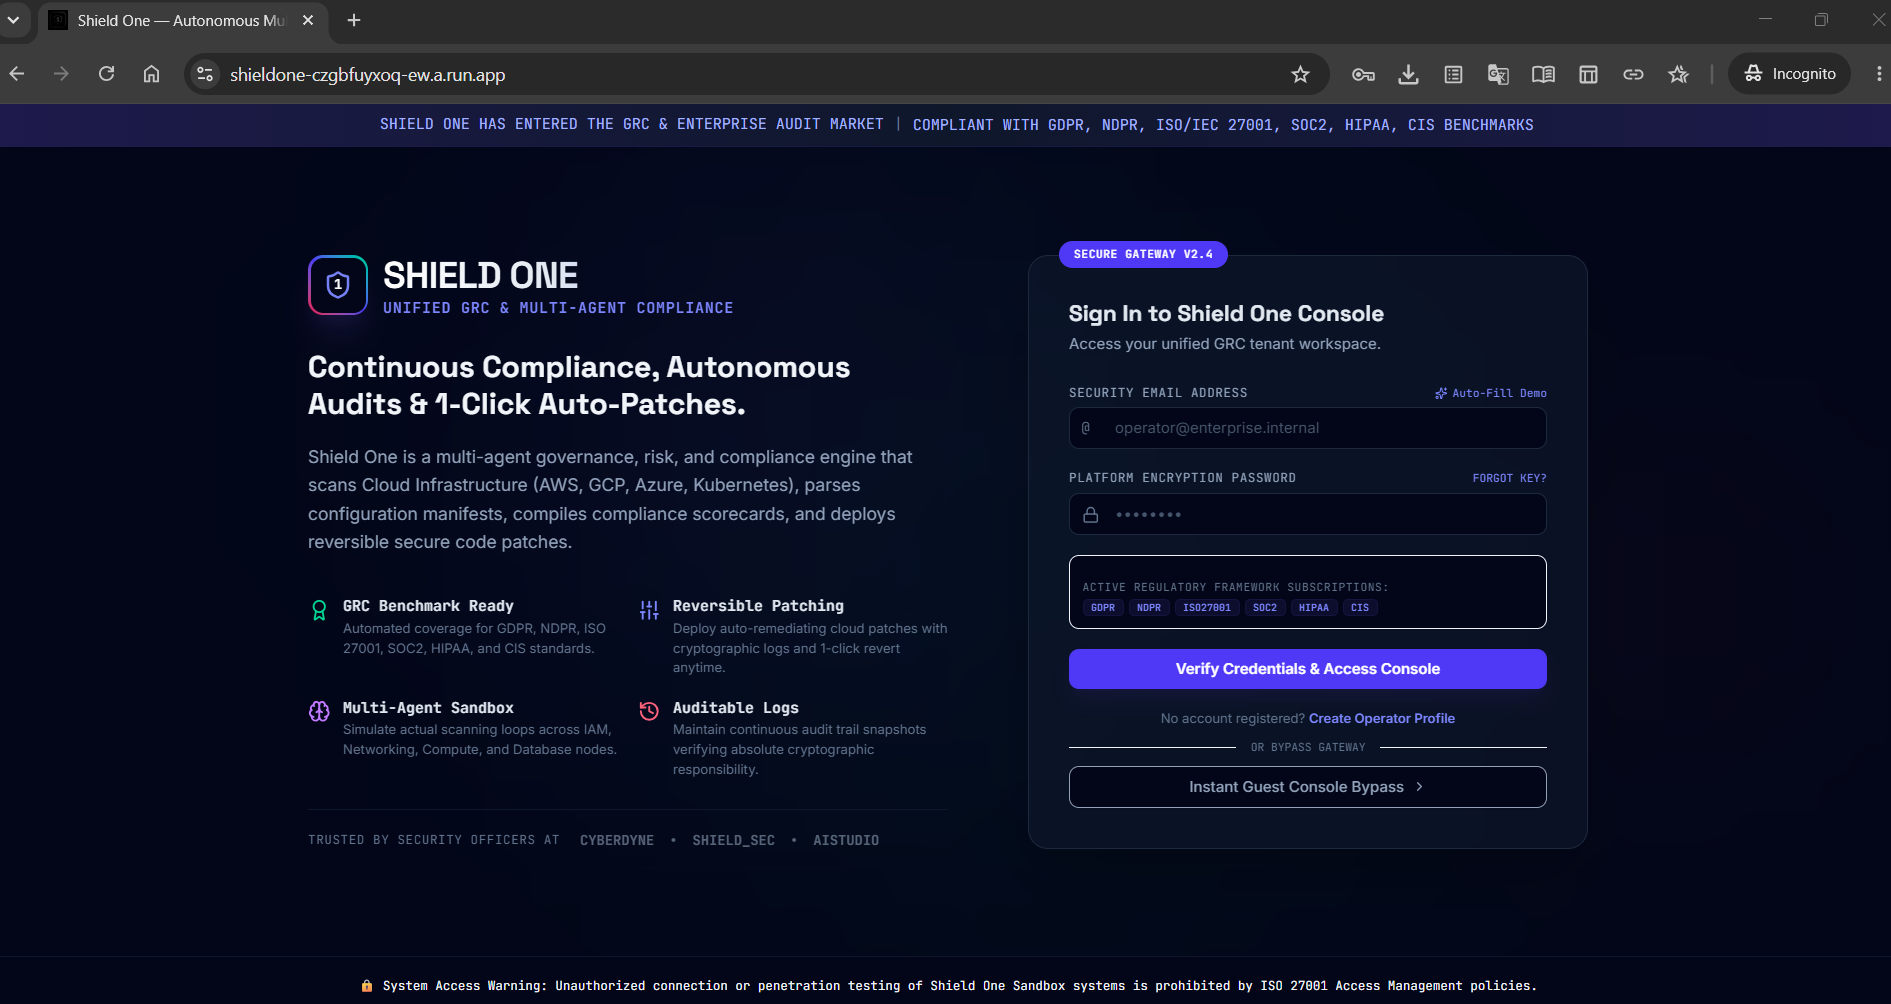
Landing page
-
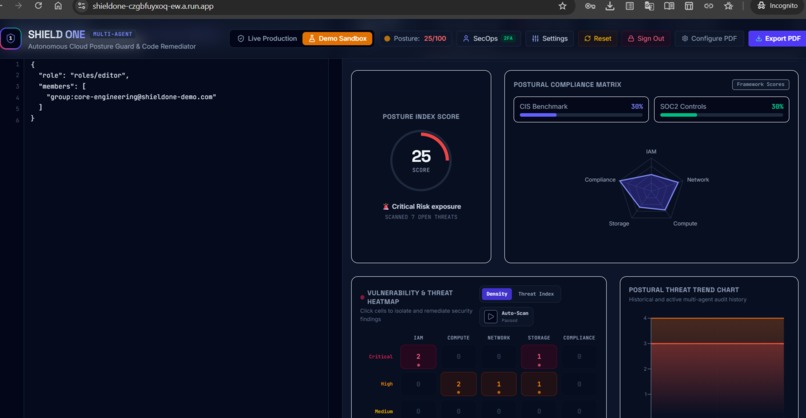
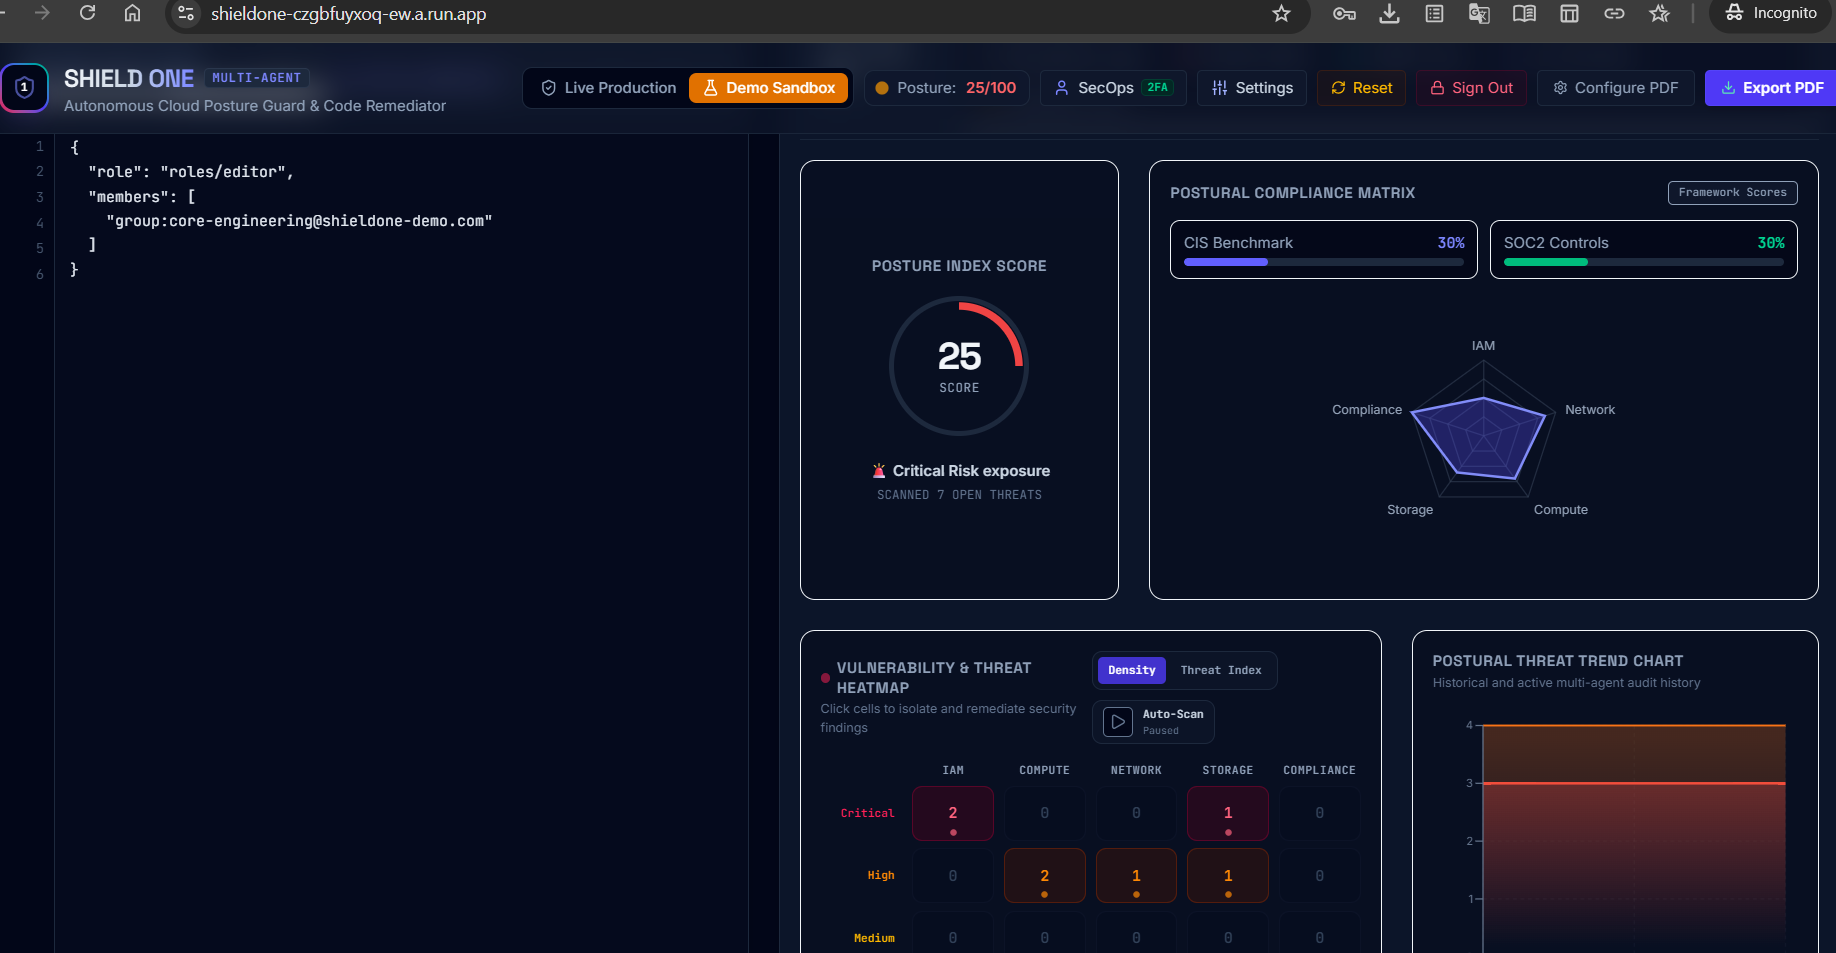
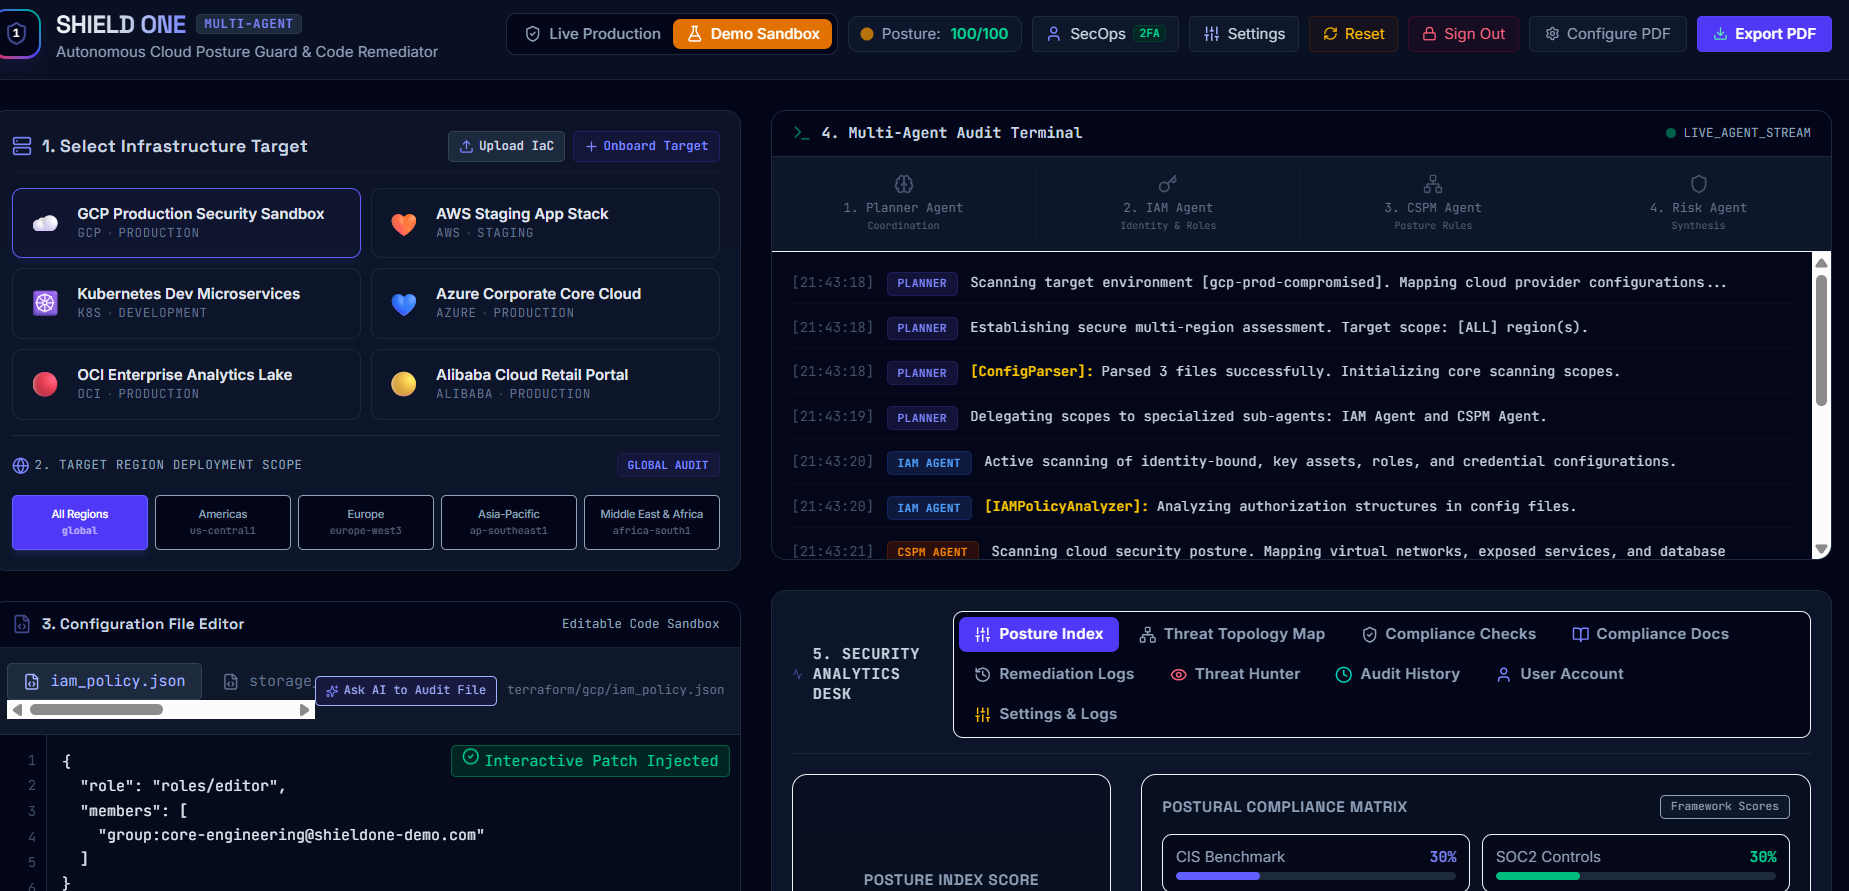
Posture index
-
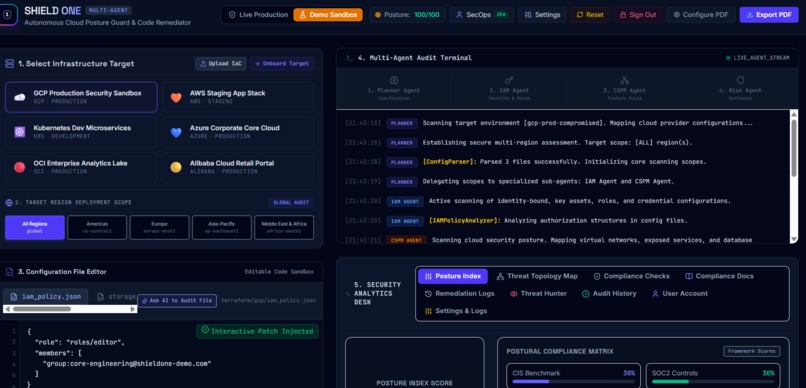
Infrastructure target/multi-agent dashboard
-
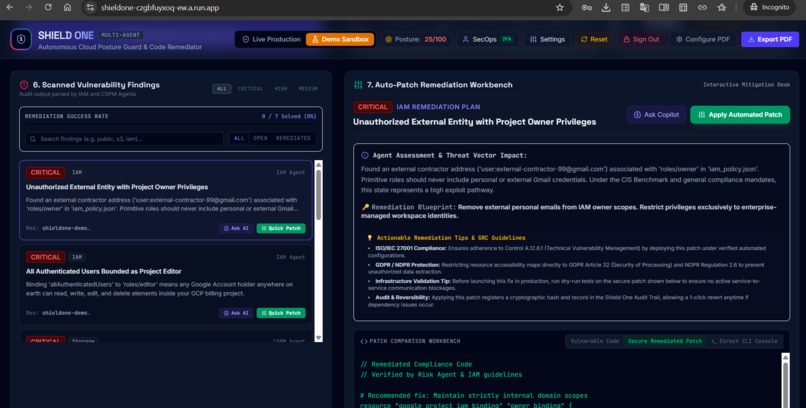
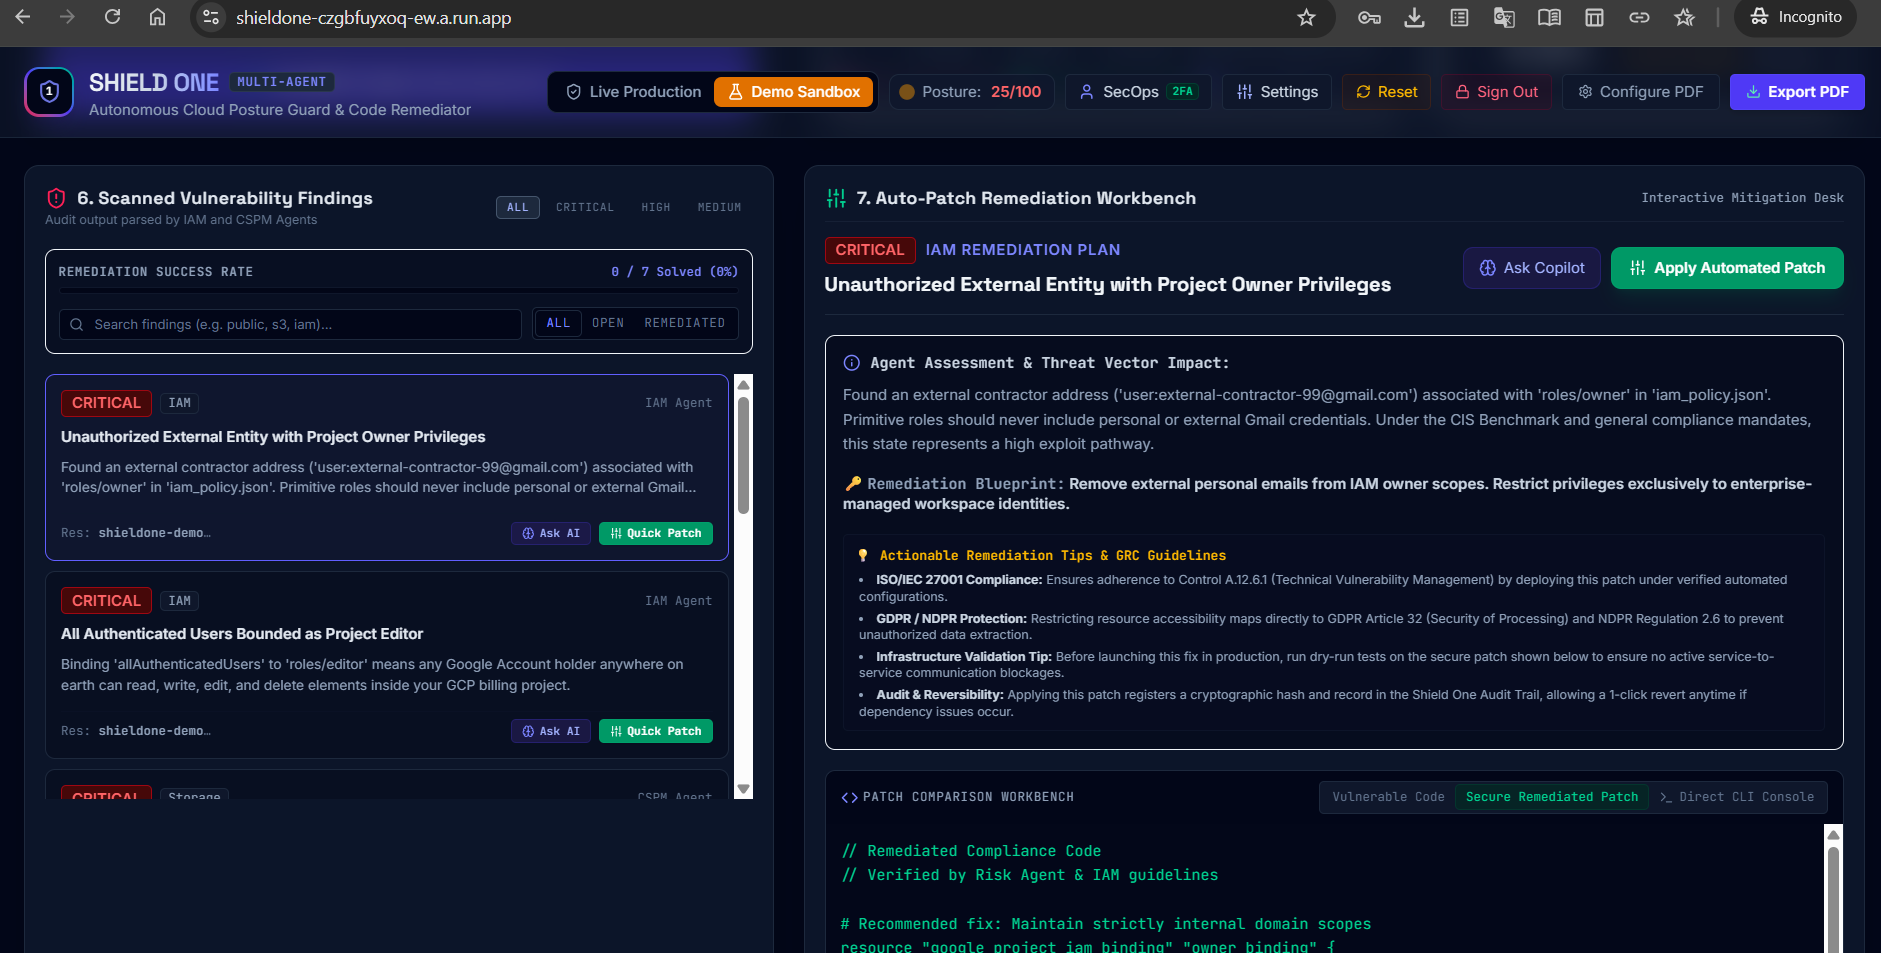
Remediation(patch)
-
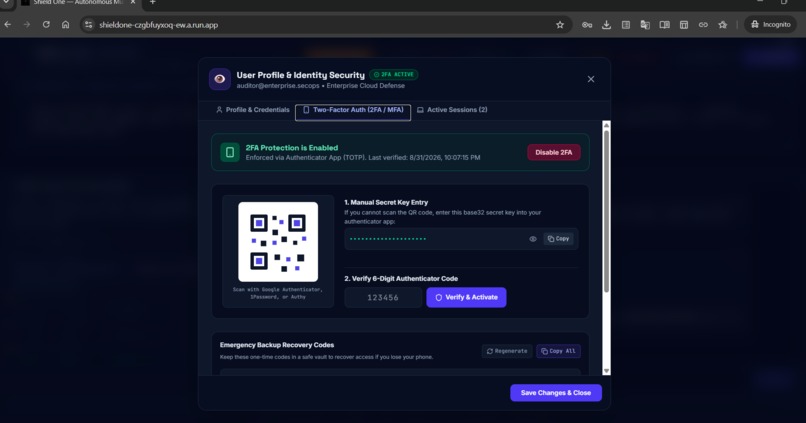
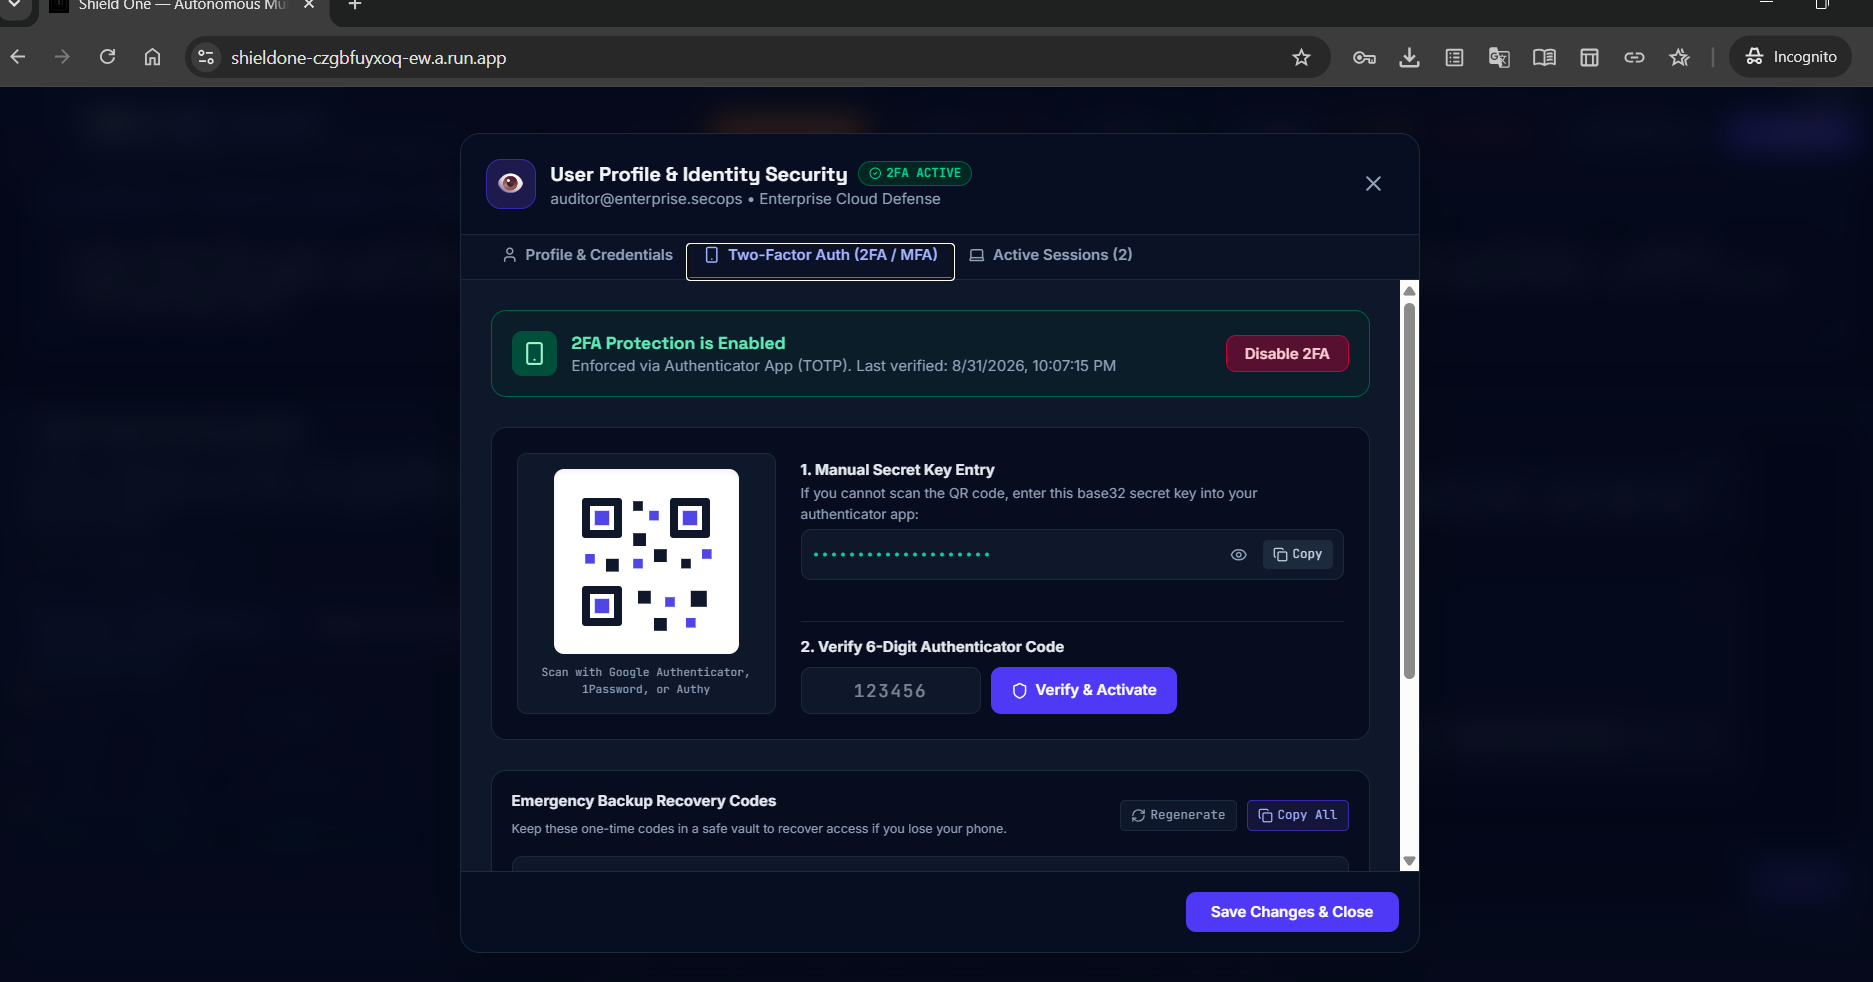
User profile/settings
-
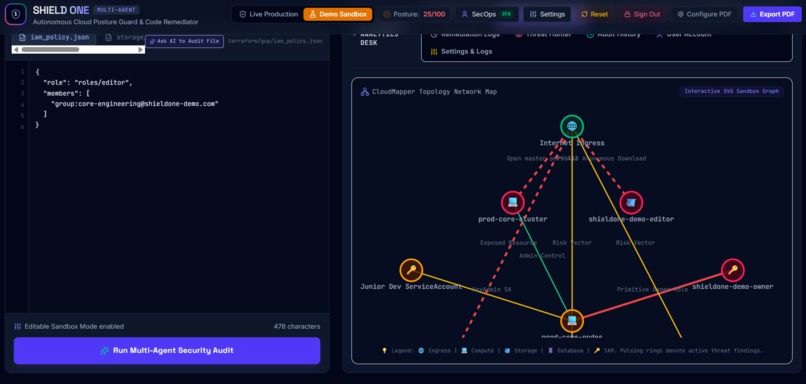
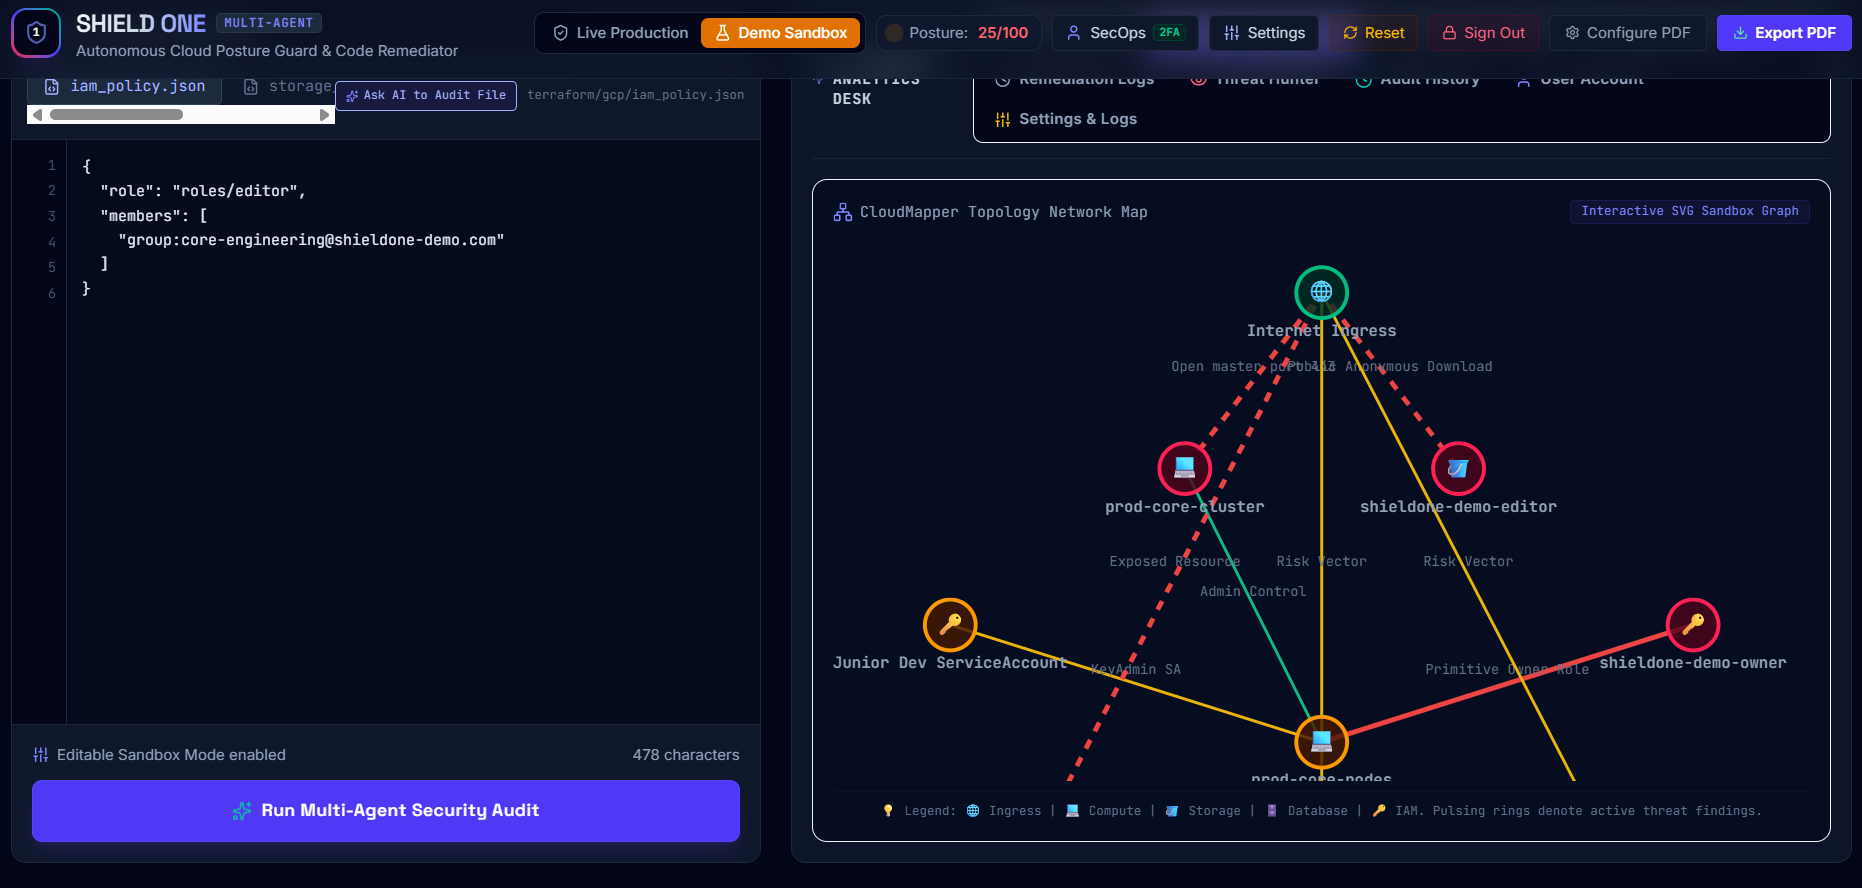
Cloud mapper/network topology

How we built it
Challenges we ran into
Accomplishments that we're proud of
What we learned
What's next for ShieldOne
Inspiration
Modern enterprise cloud architectures are sprawling, multi-cloud fleets spanning AWS, Google Cloud, OCI, Alibaba, Microsoft Azure, and Kubernetes clusters. Security Operations (SecOps) teams face alert fatigue, siloed posture management tools, and disconnected Infrastructure as Code (IaC) deployment pipelines.
Misconfigurations such as wide-open 0.0.0.0/0 ingress ports, publicly exposed object storage buckets, and unencrypted managed databases often sit undetected for weeks before an incident occurs.
I built Shield One to be the ultimate Autonomous Multi-Cloud Security Posture Management (CSPM) and Shift-Left Defense Platform. By marrying Google Cloud’s serverless infrastructure with the ultra-fast reasoning capabilities of Gemini 3.7, Shield One doesn't just detect vulnerabilities, it autonomously reasons through configuration trees, maps threats to the MITRE ATT&CK® matrix, computes rigorous compliance scores (CIS, SOC 2, ISO 27001), and generates production-ready Terraform/Kubernetes remediation patches in seconds.
What Shield One Does
- Multi-Cloud Posture Analytics: Unified visibility across GCP, AWS, Azure, OCI, Alibaba, and Kubernetes with live compliance scoring and risk distribution graphs.
- Gemini 3.7 Security Copilot & Root-Cause Engine: Context-aware AI security analyst that performs deep AST tree analysis, MITRE technique tagging (e.g., T1078, T1530), and zero-hallucination auto-patch code diff generation.
- Google Cloud Firestore Database Persistence: Live synchronization of audit scans and posture trends across devices and team members with seamless offline cache fallback.
- Cryptographic Audit Ledger: SHA-256 HMAC-style chained audit log ensuring immutable tamper-evident tracking of every SecOps intervention.
- Forensic PDF & CSV Report Generator: One-click client-side export of executive audit summaries and compliance scorecards.
How I Built It
Shield One is engineered as a high-performance full-stack cloud application:
- AI Reasoning Tier: Built using the official
@google/genaiTypeScript SDK and powered by Gemini 3.7 Flash for real-time IaC parsing, security posture analysis, and instant patch diff generation. - Cloud Persistence Tier: Integrated Google Cloud Firestore (
ai-studio-shieldone-a60aecca-14fa-4d7e-929d-38dc79439f62) with strict security rules and blueprint schemas to persist posture scan history and audit entries. - Backend & CI/CD Gateway: High-throughput Node.js & Express server hosted on Google Cloud Run, featuring endpoints for real-time security copilot reasoning, automated CI/CD webhooks, and historical scan ledgers.
- Interactive SecOps Frontend: Modern React 18, TypeScript, Tailwind CSS, Lucide icons, Recharts interactive data visualization, and Framer Motion transitions.
Challenges Faced
- Multi-Cloud Manifest Normalization: Unifying syntax differences between AWS CloudFormation, GCP Terraform HCL, and Kubernetes YAML into a standardized security evaluation graph.
- Sub-Second AI Remediation: Ensuring that large multi-resource IaC configurations could be parsed and patched by Gemini 3.7 without introducing latency into CI/CD build gates.
- Tamper-Evident Multi-Session Persistence: Designing a hybrid persistence model that writes cryptographically hashed ledger entries to Cloud Firestore while maintaining instant client-side responsiveness.
What I Learned
- How to harness Gemini 3.7's advanced reasoning to produce deterministic, syntactically valid Infrastructure as Code patches that cloud engineers can merge directly into production.
- Best practices for designing zero-trust cloud security architectures with Google Cloud Run and Google Cloud Firestore.
- The power of "shift-left" security when automated AI security gates are embedded directly into developer pull request workflows.
What's Next for Shield One
- Active Runtime Cloud Drift Detection: Expanding the scanner to poll live cloud APIs and flag configuration drifts against checked-in Git repositories.
- Autonomous Remediation Pull Requests: Automatic GitHub App integration to create pull requests with verified Terraform fixes when vulnerabilities are flagged in the dashboard.
- Custom Corporate Policy As Code Engine: Allowing enterprises to define custom Rego / OPA compliance rules directly in natural language using Gemini.
Built With
- cis-benchmarks
- cybersecurity
- devsecops
- docker
- express.js
- gemini-3.7-flash
- github-actions
- google-cloud-firestore
- google-cloud-run
- google-genai-sdk
- kubernetes
- mitre-attack
- node.js
- react
- recharts
- soc2
- tailwind-css
- terraform
- typescript
- vite


Log in or sign up for Devpost to join the conversation.