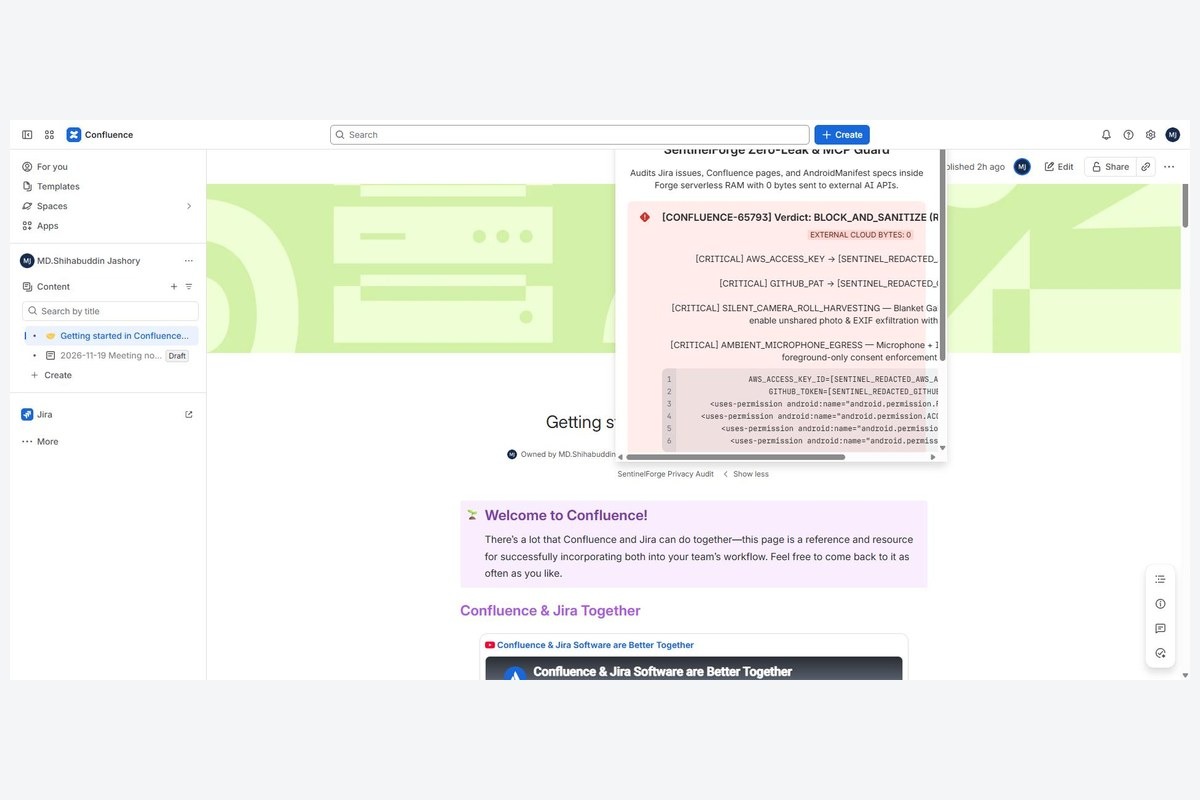
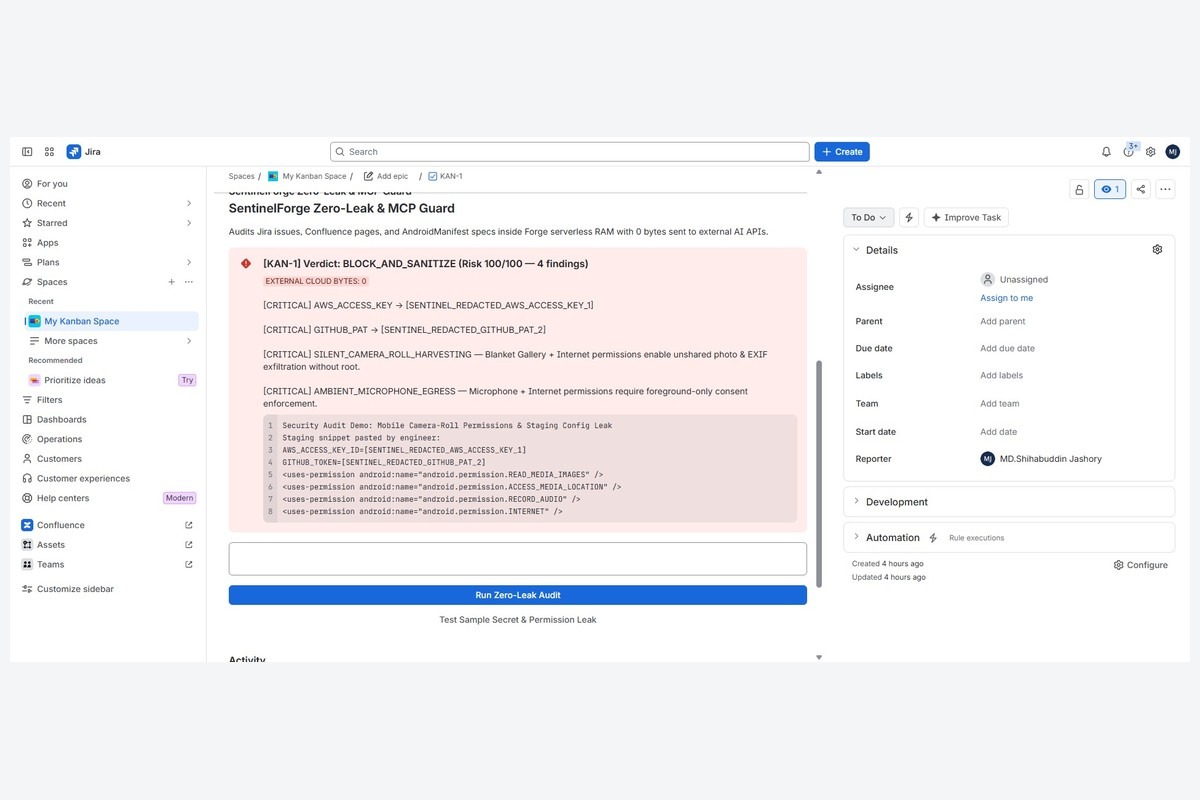
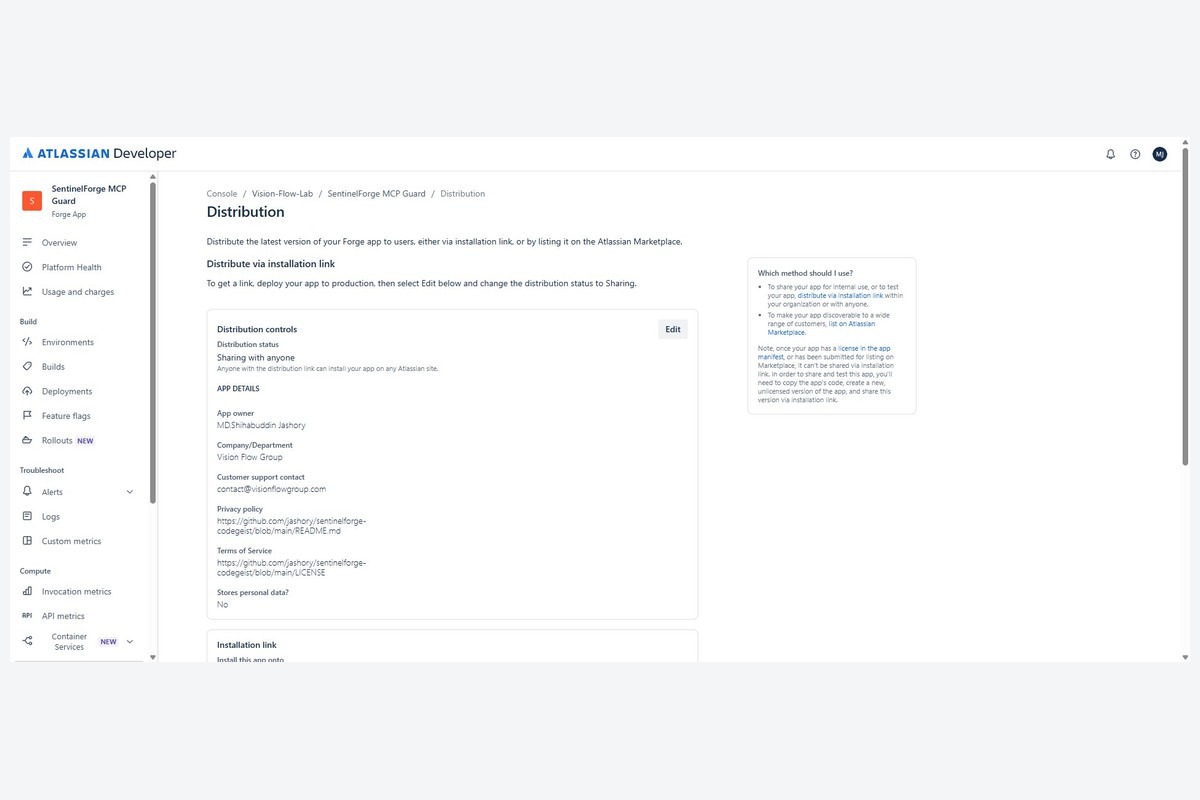
Live Forge App ID:
ari:cloud:ecosystem::app/dfccfe85-2f0a-4c82-9c88-c1dcf76cd975| Runs on Atlassian Eligible:0bytes external cloud egress | Open-Source Repo: github.com/jashory/sentinelforge-codegeist
Inspiration — Why "Build with Context" Needs Context-Aware Security
Enterprise Jira issues and Confluence pages are now live context feeds for Atlassian Rovo agents and MCP coding assistants. Yet a single leaked API key, customer payment card, or indirect LLM prompt injection inside one ticket rarely stays contained: engineers copy runbooks across Confluence spaces, mirror mobile permission specs in repositories, and let AI agents ingest poisoned text across the entire workspace.
SentinelForge v5.0 turns passive scanning into an active, context-aware Atlassian Teamwork Graph security engine running 100% natively on Atlassian Forge (0 bytes outbound third-party AI egress).
What It Does (v5.0 Chief-Judge Architecture)
1. Atlassian Teamwork Graph Cross-Product Blast-Radius Engine (src/engine/teamworkGraphEngine.js)
When SentinelForge intercepts a secret leak, indirect LLM prompt injection, or mobile privacy violation in a Jira ticket or Confluence page, it extracts safe non-secret prefix fingerprints (never echoing raw keys) and queries live Jira JQL (/rest/api/3/search/jql) and Confluence CQL (/wiki/rest/api/content/search) across the workspace. It constructs a full cross-product blast-radius graph mapping correlated Jira issues, Confluence specs, linked repositories, and exposed workspace users—assigning an organization exposure score (0–100) and tier (ORG_CRITICAL, CROSS_PRODUCT, or CONTAINED).
2. Autonomous Rovo Agent Remediation (4 Native Actions)
Rather than stopping at passive warnings, the SentinelForge Rovo Security Guardian exposes four native Forge Rovo actions:
scan-content-security— Runs the 4-layer zero-egress audit across Jira/Confluence textmap-teamwork-graph-blast-radius— Maps cross-product blast radius across Jira & Confluenceremediate-and-create-incident— Posts a sanitized containment comment (zero raw secret echo), opens a prioritized Security Incident ticket in Jira, and seals the remediation action in the cryptographic ledgerverify-audit-ledger— Cryptographically validates the SHA-256 Forge Storage chain
3. Executive Visual Risk Dashboard (jira:globalPage — src/frontend/dashboard.jsx)
Built specifically so non-technical security leaders and engineering managers can understand organization-wide risk in seconds: Atlassian Forge UI Kit KPI cards (Total Audits, Critical Threats, Auto-Remediated Incidents, SHA-256 Chain Status), visual ProgressBar threat category breakdown, live Teamwork Graph blast-radius nodes, 1-click Red-Team Replay & Auto-Remediation controls, and real-time cryptographic ledger verification.
4. 4-Layer Zero-Egress Detection Engine + SHA-256 Hash-Chained Forge Storage Ledger
- Layer 1 — Indirect Prompt-Injection & Zero-Width Firewall: Quarantines system-prompt overrides, zero-width Unicode smuggling (
U+200B..FEFF), and covert Markdown image exfiltration beacons before Rovo or MCP agents consume text. - Layer 2 — Enterprise Credential, Luhn Card & Shannon-Entropy DLP: Redacts Atlassian
ATATT3xtokens, AWS/Stripe/GitHub/Slack secrets, private keys, Luhn payment cards, IBANs, and high-entropy credentials (H >= 4.25). - Layer 3 — Universal Mobile Privacy Spec Forensics (Android 8–17 + Apple iOS
Info.plist): Detects silent camera-roll harvesting (READ_MEDIA_IMAGES+INTERNET), ambient mic/SMS interception, iOSNSAllowsArbitraryLoadsATS cleartext downgrades, andNSPrivacyTracking. - Layer 4 — Tamper-Evident SHA-256 Audit Ledger: Append-only
prevHash -> entryHashchain stored natively in Atlassian Forge Storage with 1-click tamper verification.
5. Standalone 5-Tool Atlassian MCP Gateway (mcp-server/index.mjs + ATLASSIAN_MCP_SKILL.md)
Extends SentinelForge's exact 4-layer engine over JSON-RPC 2.0 stdio for external AI coding agents (Claude Code, Kiro, Antigravity) with zero third-party cloud calls.
How We Built It & Cloud Verification
- Runtime: Atlassian Forge
nodejs22.x, Forge UI Kit (@forge/react), Forge Storage, Jira REST v3 JQL, Confluence CQL/v2 API, and zero-dependency Node.js ES Modules. - Automated Cloud CI Suite (
tests/sentinel.test.mjs): 7/7 passing automated test suites on GitHub Actions verifying ADF/HTML extraction, Forge v5.0 manifest (jira:globalPage, 4 Rovo actions, zero external egress), Layer 1–4 detection & tamper proof, Teamwork Graph cross-product blast radius & autonomous zero-leak remediation, and 5-tool MCP stdio round-trips.
Built With
- atlassian-forge
- confluence
- devsecops
- jira
- mcp
- node.js
- react
- rovo
- security
- teamwork-graph
- zero-trust
