Inspiration
We wanted to understand how malicious insiders operate and how organizations can detect early signs of data exfiltration. Protecting sensitive information is critical, and simulating real-world insider threats helps prepare security teams proactively.
What it does
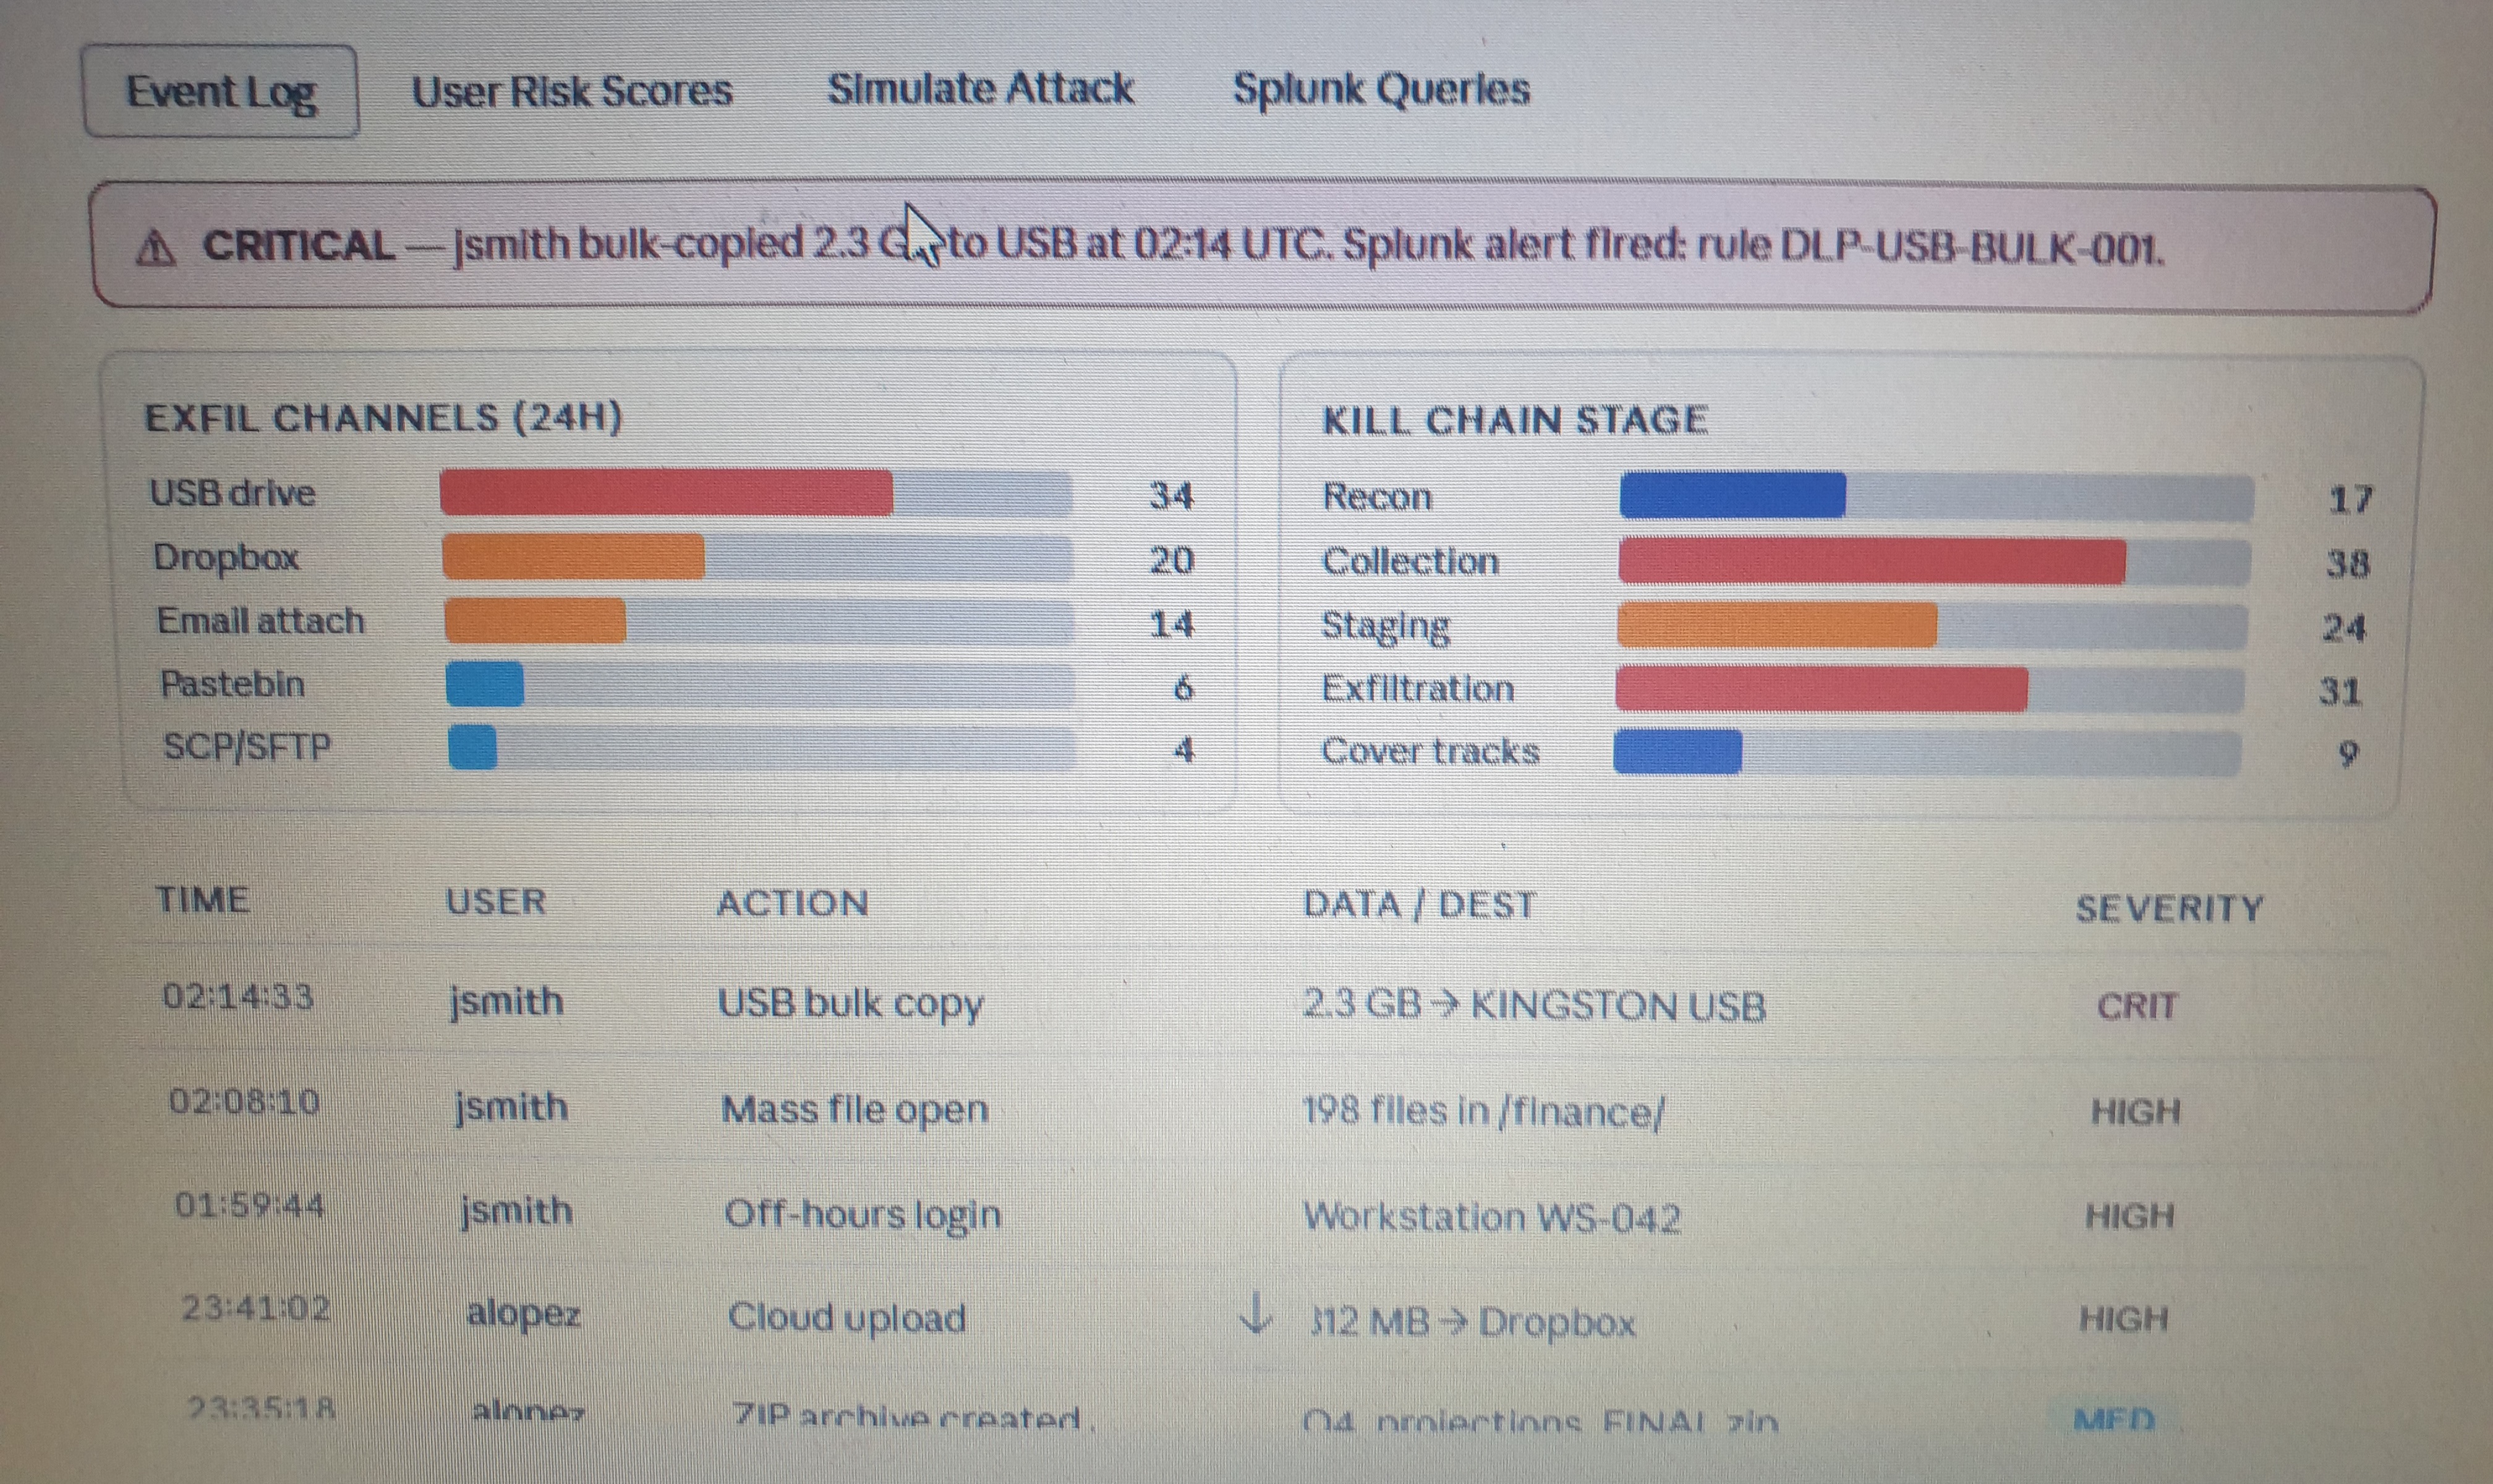
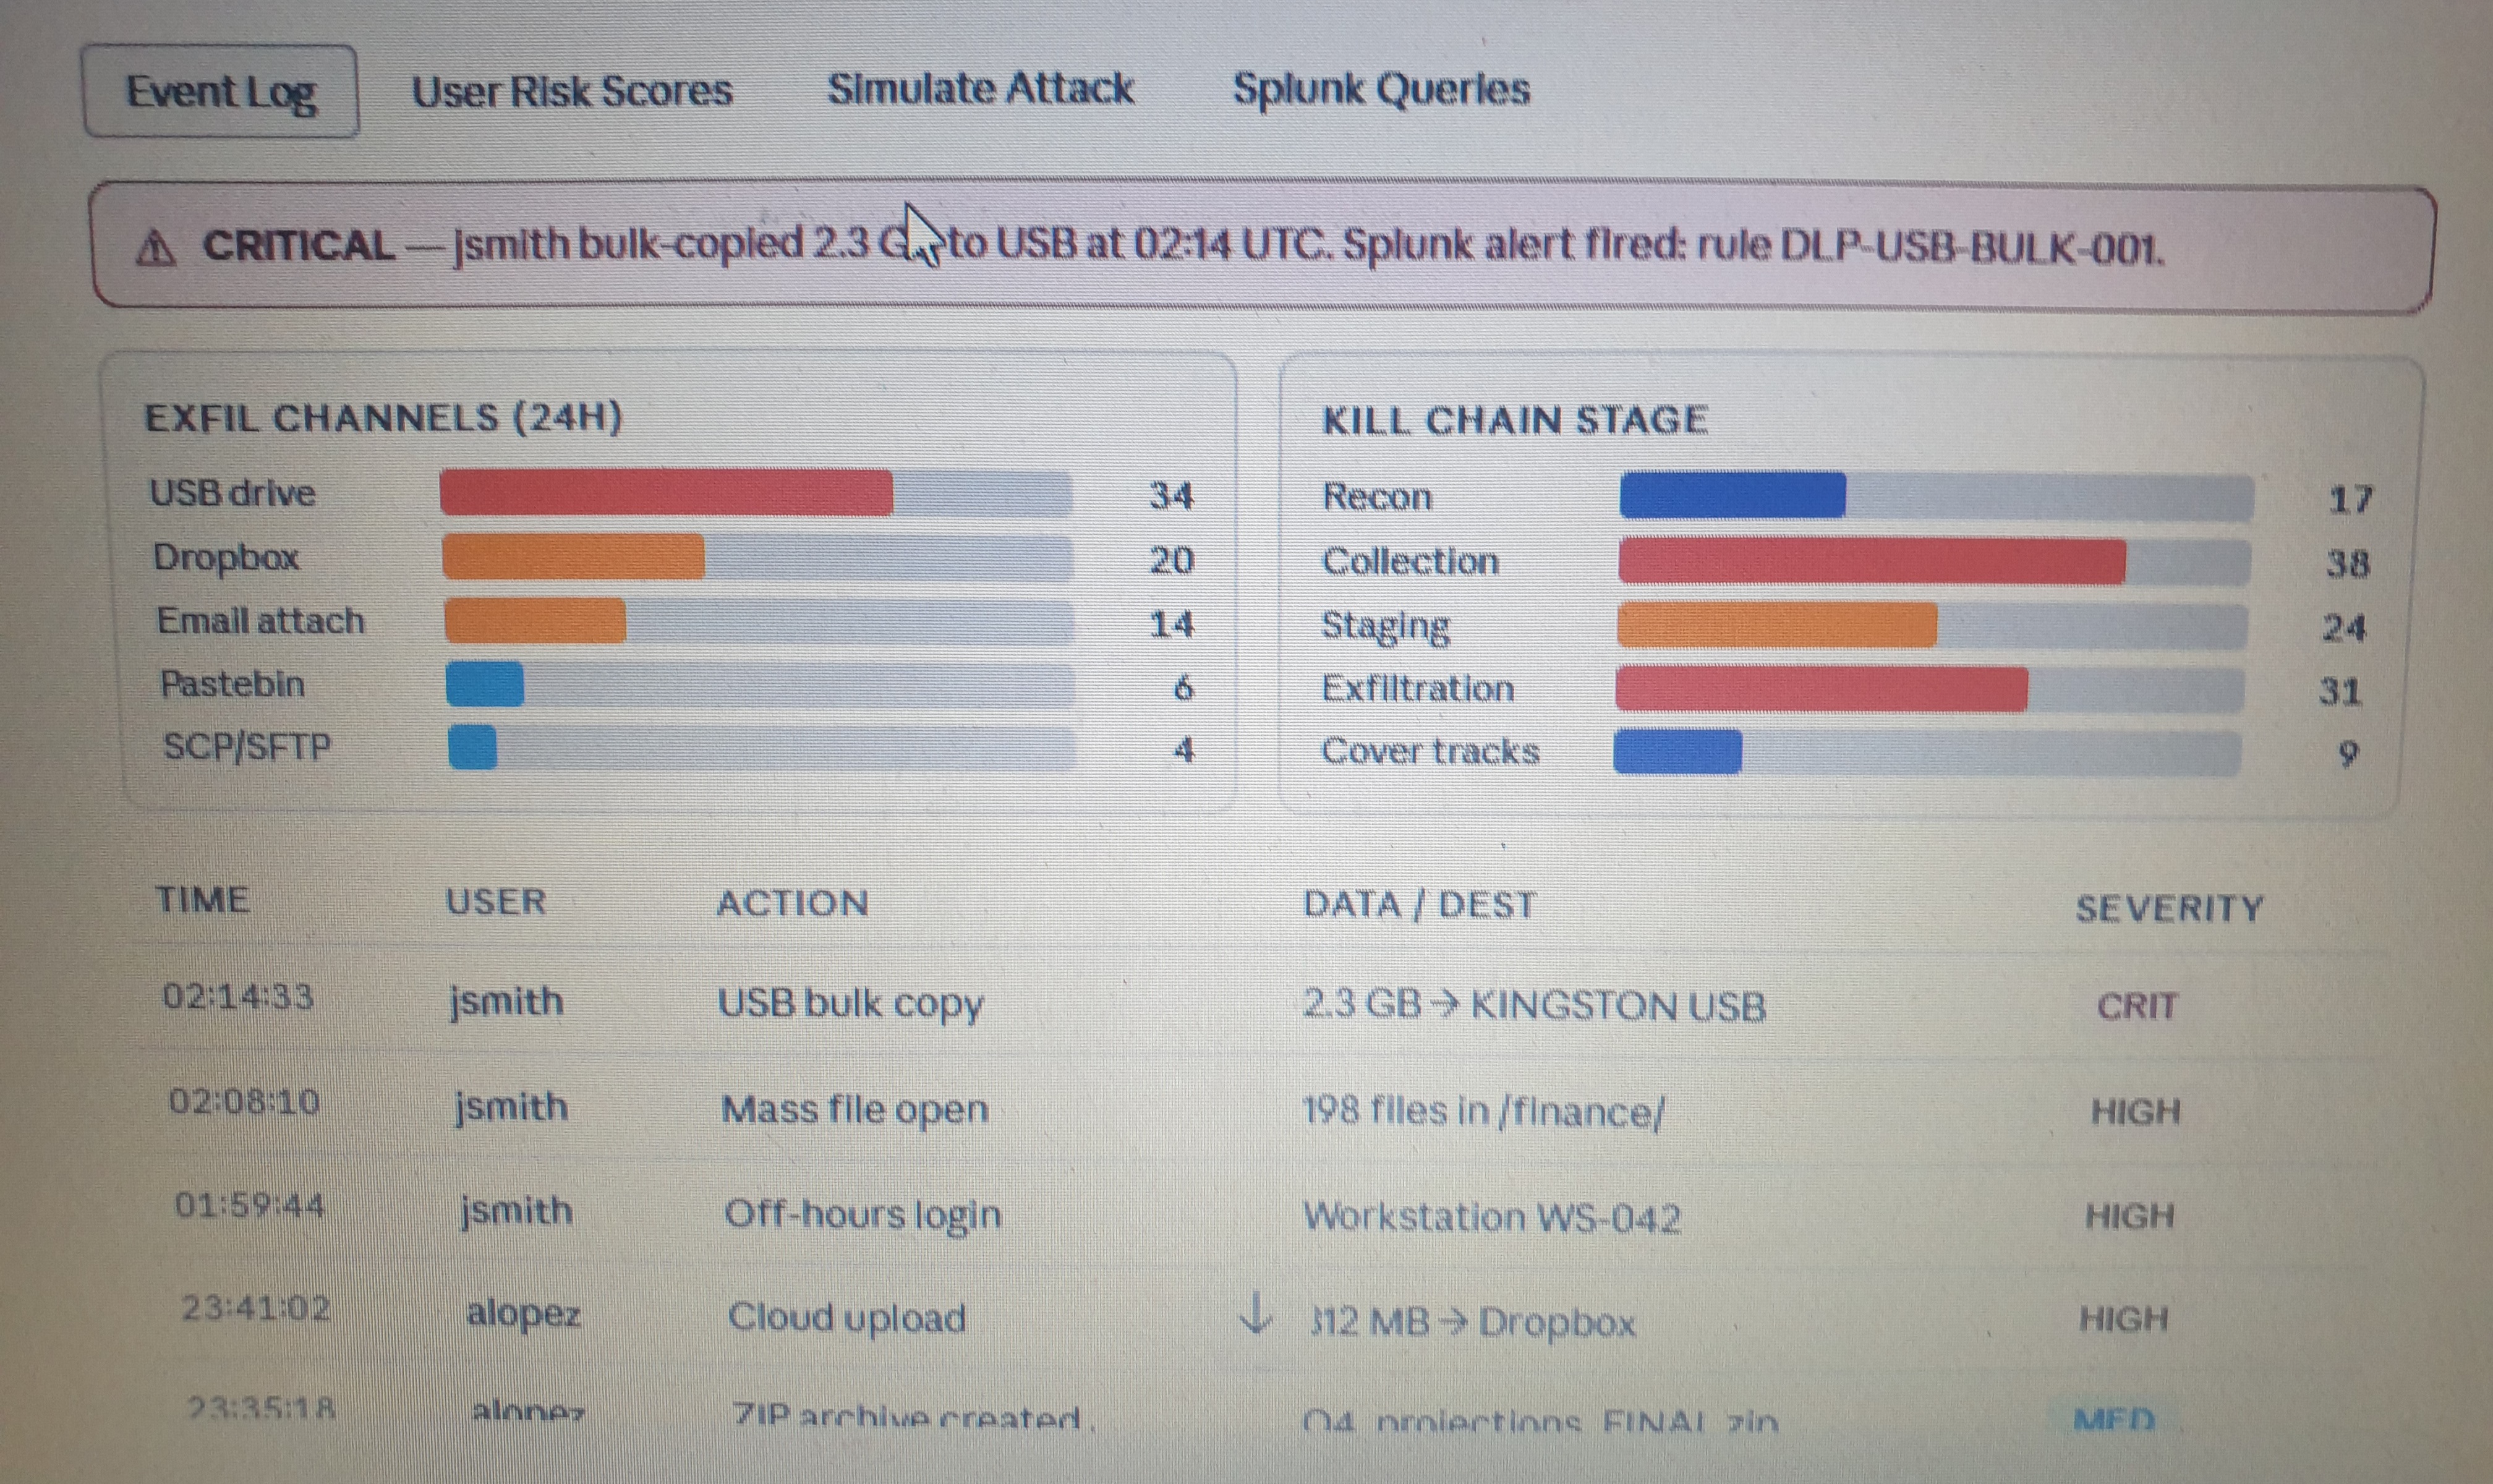
This simulation replicates a malicious insider attempting to exfiltrate data via USB, email, or cloud services. Splunk monitors file access logs, email gateway logs, and endpoint telemetry, producing a risk-scoring dashboard that highlights unusual behavior, like bulk file transfers or off-hours activity.
How we built it
We integrated Splunk with multiple data sources, created correlation searches for suspicious activity, and developed a risk-scoring system. Dashboards and alerts were configured to give actionable insights, helping detect and mitigate insider threats quickly.
Challenges we ran into
Generating realistic insider activity data without compromising real systems. Fine-tuning alerts to reduce false positives while catching genuine threats. Correlating data from multiple sources efficiently for accurate risk scoring.
Accomplishments that we're proud of
Successfully built a working simulation that identifies risky insider behavior. Developed a clear, interactive dashboard that makes monitoring easy. Improved understanding of insider threat patterns and DLP monitoring in Splunk
What we learned
Insider threat detection requires balancing sensitivity and noise in alerts. Correlating data across endpoints, logs, and email gateways improves detection accuracy. Splunk’s dashboards and risk scoring are powerful tools for proactive security.
What's next for Insider Threats and Data Exfiltration Simulation
Expand the simulation to include more sophisticated attack patterns. Integrate machine learning for predictive insider threat detection. Share best practices and dashboards for organizations aiming to improve their DLP strategies.
Built With
- bash/powershell-platforms/tools:-splunk-enterprise
- cloud-storage-apis-libraries:-pandas
- google-drive
- html
- onedrive-apis:-splunk-rest-api
- windows/linux-endpoints-cloud:-aws-s3


Log in or sign up for Devpost to join the conversation.