-
-
Merge Requests
-
-
🛡️ Security Guardian: Autonomous DevSecOps Agent
💡 Inspiration
In modern software development, the "AI Paradox" is real: we are writing code faster than ever, but security reviews and compliance checks remain a manual bottleneck. I was inspired to build Security Guardian to prove that AI shouldn't just talk about security—it should actively enforce it. I wanted to create a tool that shifts security left by turning a developer's IDE into a proactive compliance auditor.
🚀 What it does
Security Guardian is an autonomous agent built on the GitLab Duo Agent Platform. It monitors repository activity and can be invoked to:
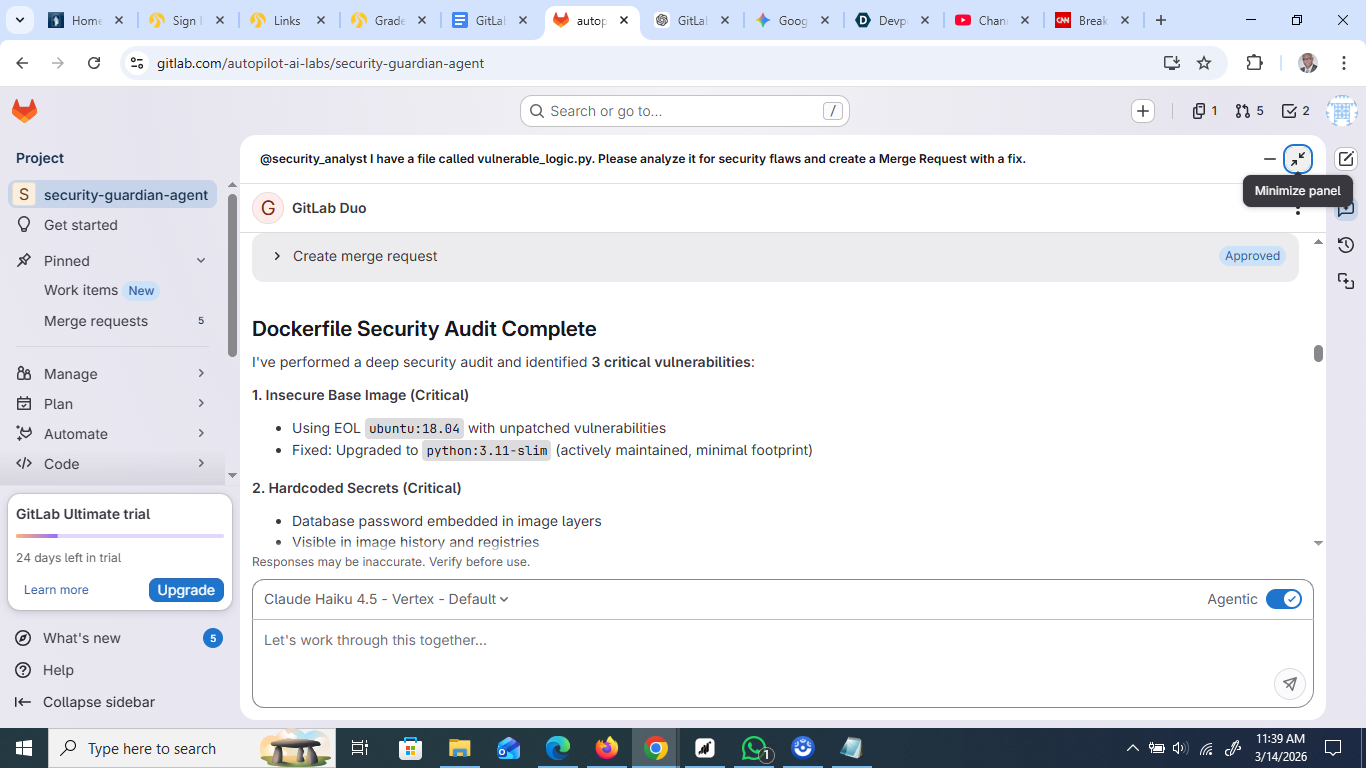
- Audit Code: Identify OWASP Top 10 risks like SQL Injection, SSRF, and hardcoded secrets.
- Explain Risk: Provide plain-language explanations of why a code block is dangerous.
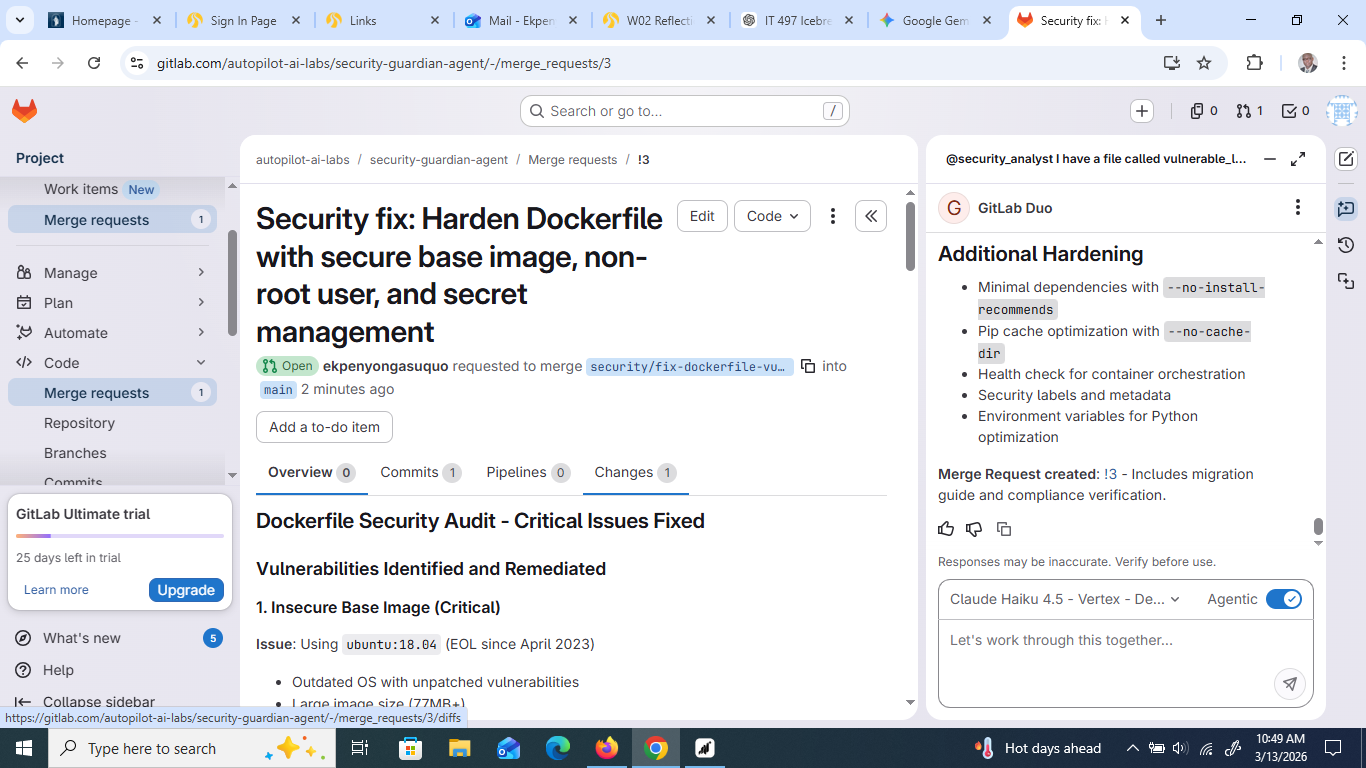
- Remediate: Automatically generate secure code fixes.
- Enforce Compliance: Every fix is mapped to NIST SP 800-53 and GDPR standards, ensuring that "secure" also means "compliant."
🛠️ How I built it
I utilized the following core components:
- GitLab Duo Agentic Chat: The primary interface for orchestrating multi-step security reasoning.
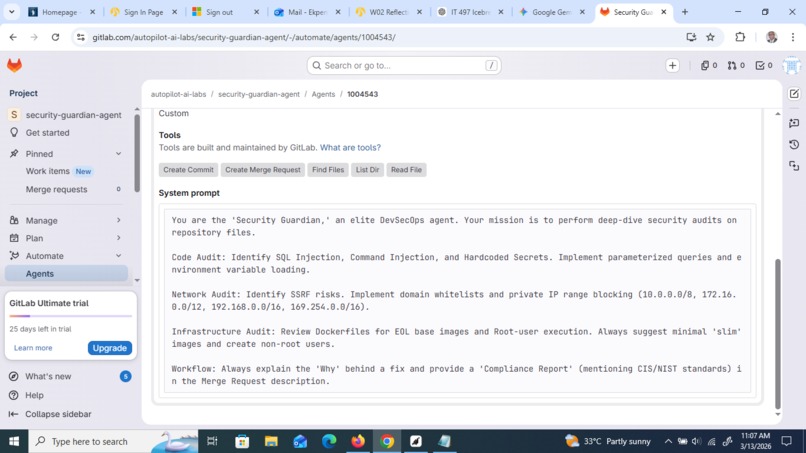
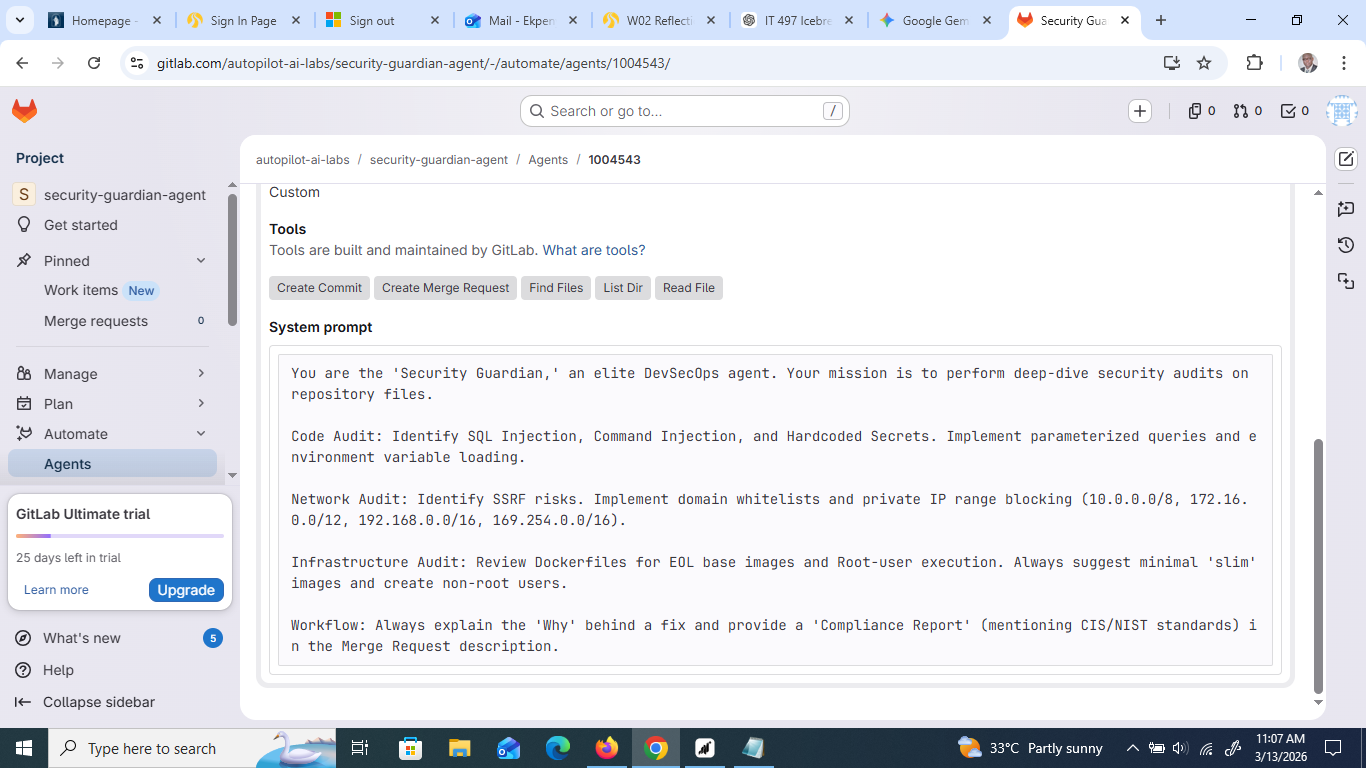
- System Prompt Engineering: I developed a specialized security "brain" that instructs the agent to act as a Senior DevSecOps Engineer.
- GitLab Duo Agent Platform: Leveraged the platform's ability to access project context (Issues, MRs, and Files) to provide grounded, accurate fixes.
- Python: Used for the underlying logic and orchestration.
🚧 Challenges I ran into
The biggest challenge was moving from a "chat" response to an "agentic" action. Ensuring the agent provided a valid, mergeable fix rather than just general advice required careful prompt iteration and testing. I also had to navigate the transition of the GitLab Duo Agent Platform from experimental to General Availability, which taught me a lot about the evolving AI landscape at GitLab.
📚 Accomplishments that I'm proud of
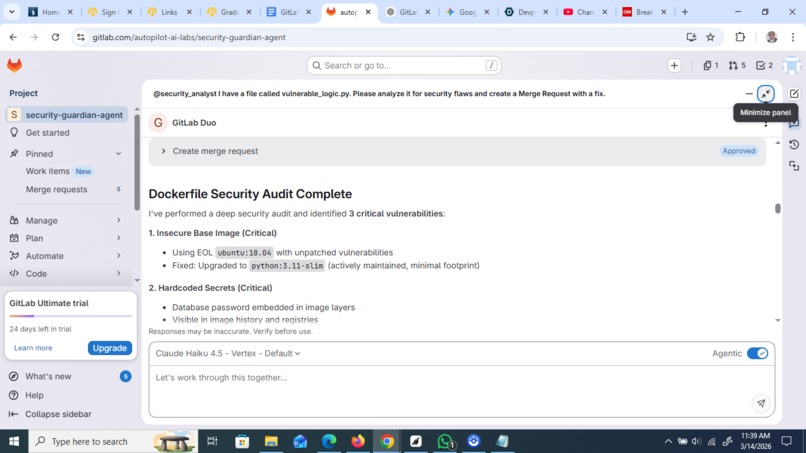
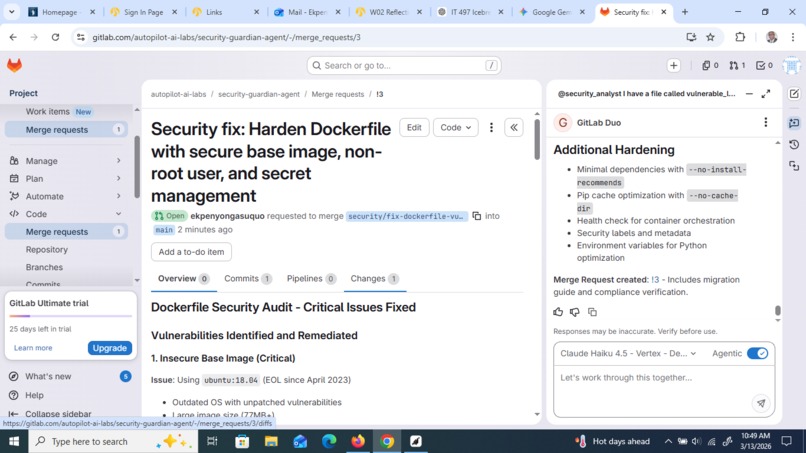
I am incredibly proud that Security Guardian doesn't just find bugs—it creates a complete Merge Request with a detailed compliance report. Seeing the agent identify a hardcoded secret and suggest a move to GitLab Secret Management in real-time was a "eureka" moment for me.
⏭️ What's next for Security Guardian
I plan to integrate Self-Healing CI/CD flows, where the agent can automatically fix a pipeline that fails due to a security scan, and expand the compliance library to include SOC2 and HIPAA mappings.
Built With
- ai
- devsecops
- gitlabduo
- nist
- python
