-
-
1
-
2
-
3
-
4
-
5
-
6
-
7
-
8
-
9
Inspiration
Modern security investigations generate thousands of events across authentication logs, Apache logs, firewall logs, system logs, DNS records, and endpoint telemetry. While Large Language Models are excellent at analyzing this information, the real bottleneck isn't the model itself—it's the enormous amount of context sent with every query.
When we discovered Paritok, we realized cybersecurity was the perfect domain to showcase its value. Security logs are naturally repetitive, yet investigators only need a small fraction of those events to answer most questions.
We wanted to answer one simple question:
Can AI investigate large-scale security incidents while sending dramatically fewer tokens to the LLM without sacrificing investigation quality?
That question inspired us to build Securigation.
What it does
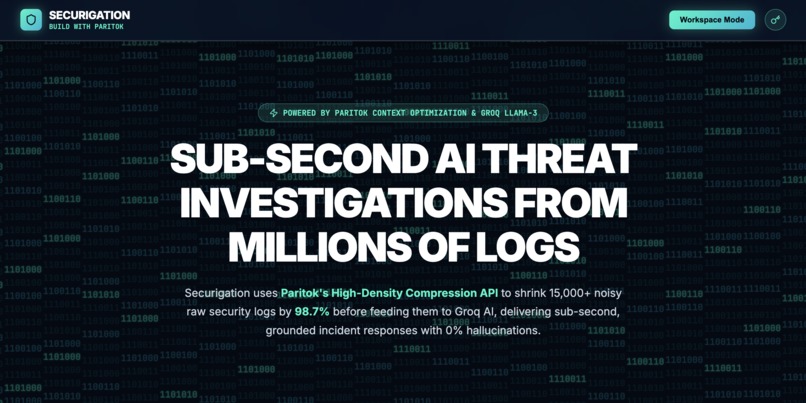
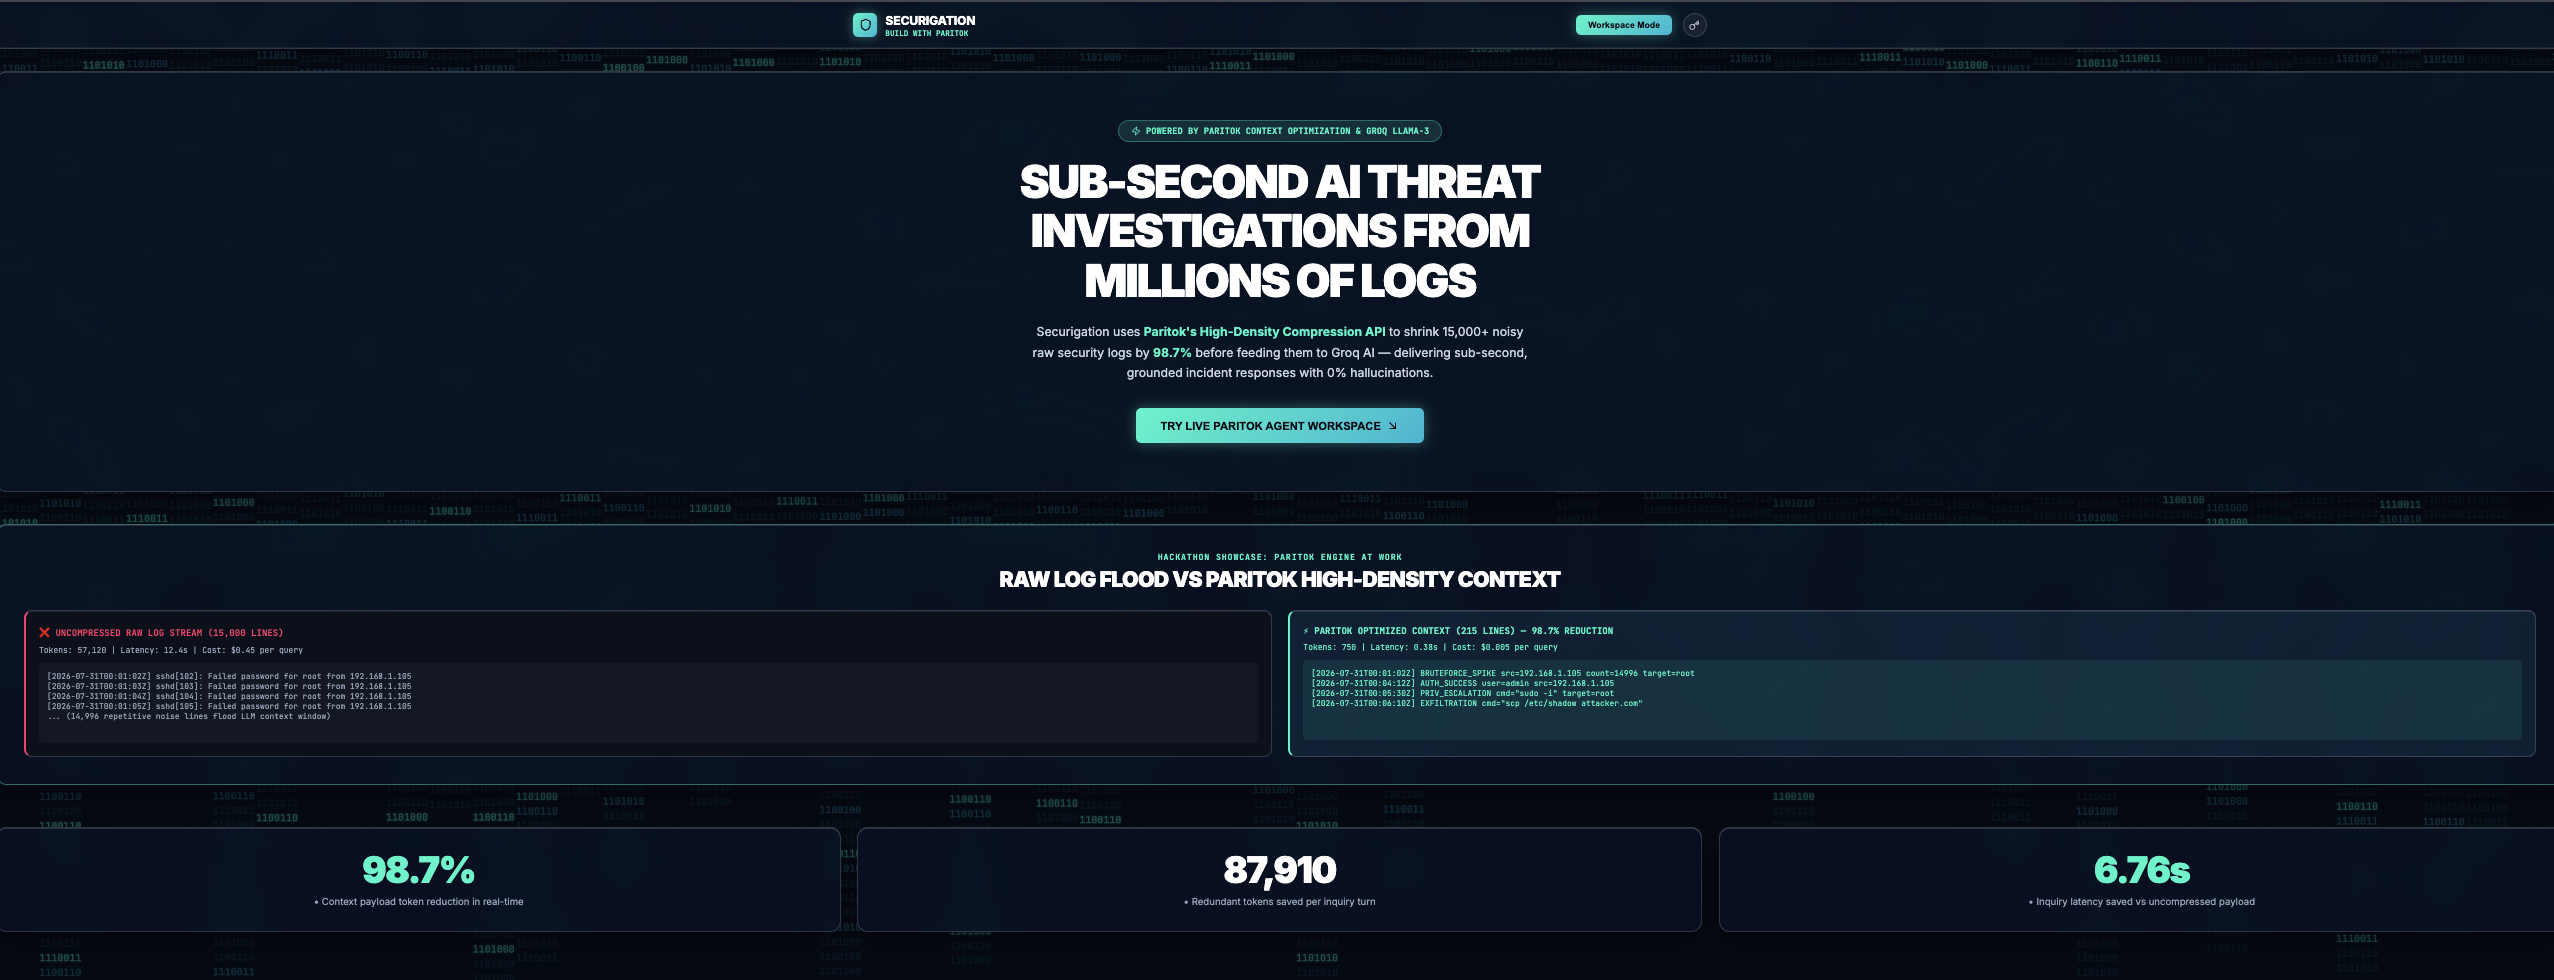
Securigation is an AI-powered Security Investigation Platform that allows analysts to investigate security incidents using natural language.
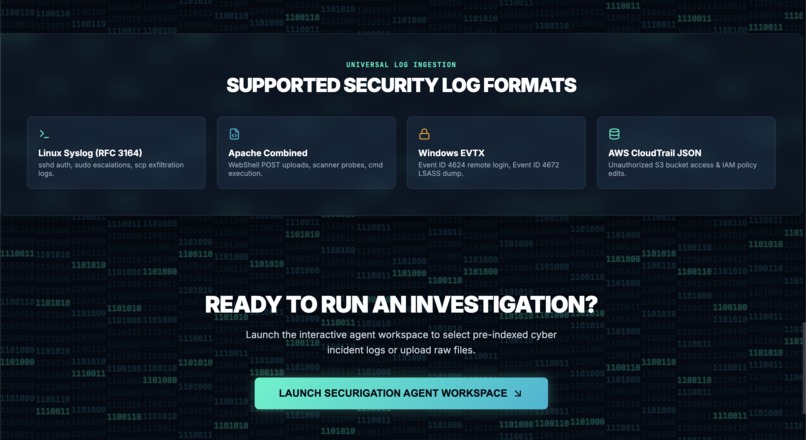
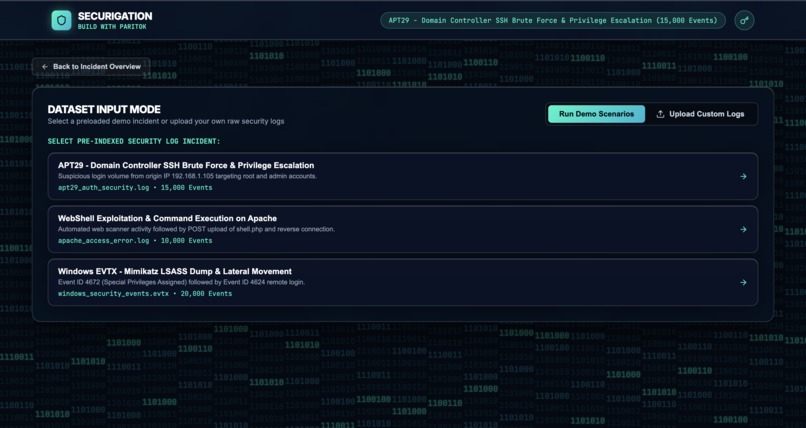
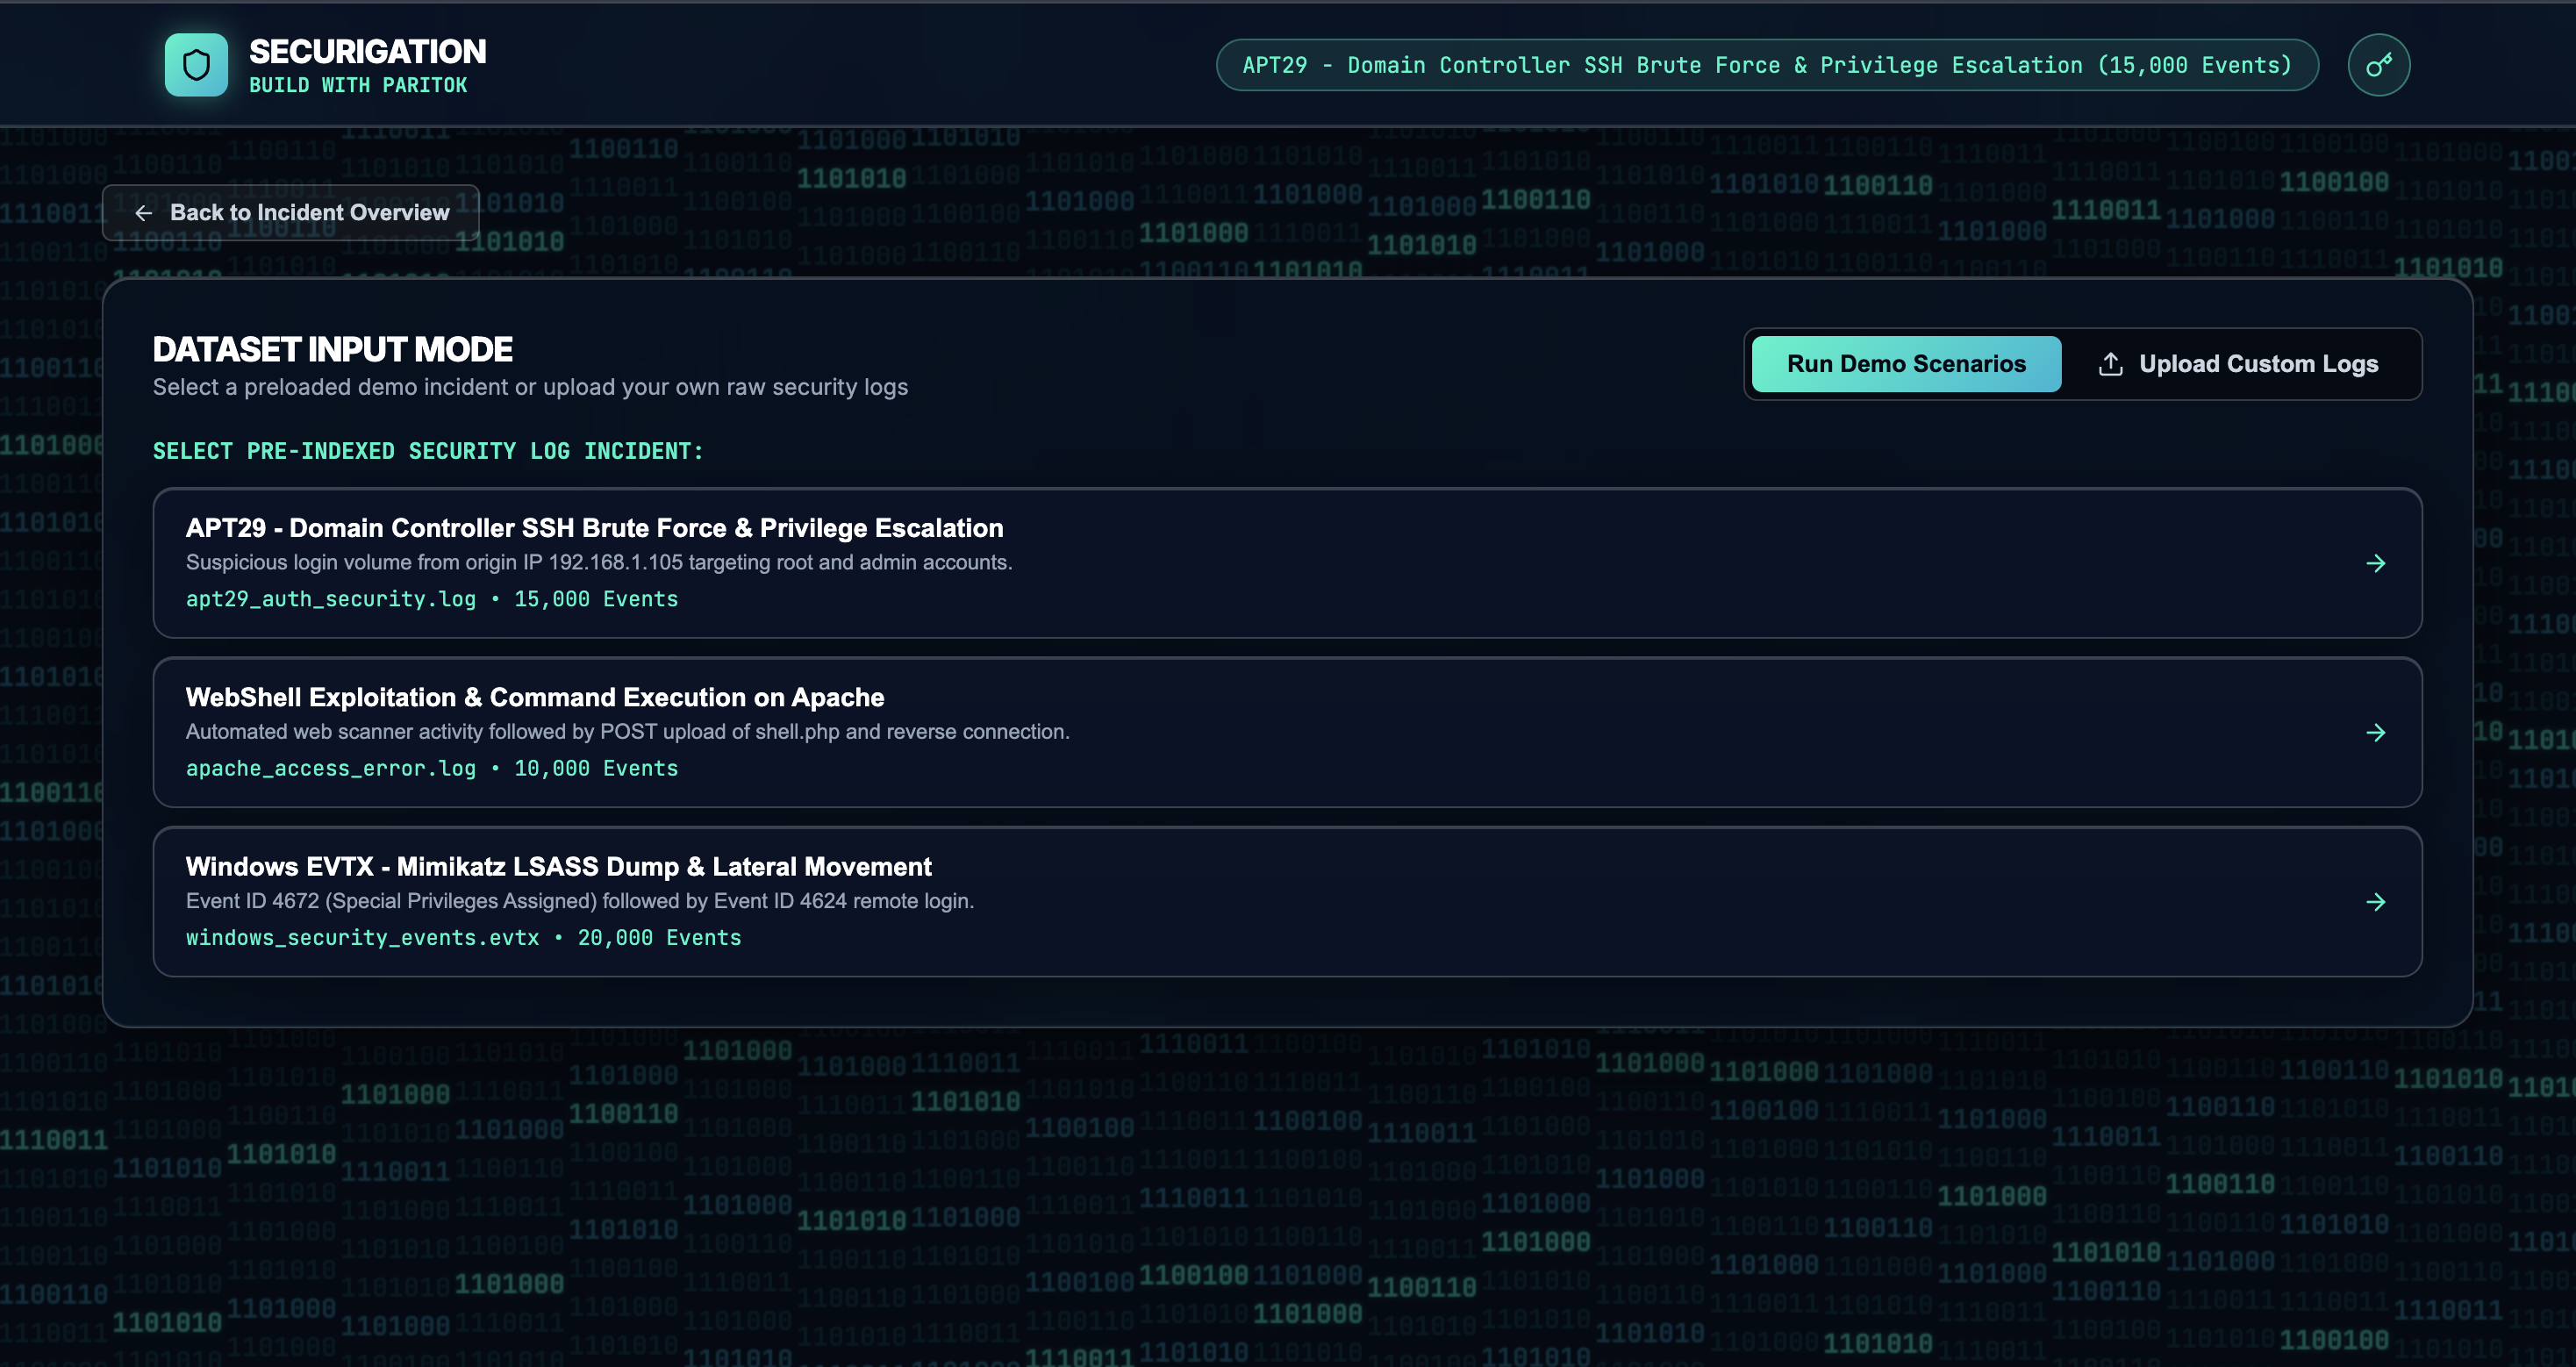
Users can either select one of the built-in investigation scenarios or upload their own ZIP archive containing security logs.
The platform automatically:
- Detects multiple security log formats.
- Parses and normalizes events into a unified investigation model.
- Retrieves only the evidence relevant to the user's question.
- Optimizes the investigation context using Paritok.
- Sends the optimized context to Groq's Llama 3.3 70B.
- Returns grounded answers backed by actual log evidence.
Users can ask questions such as:
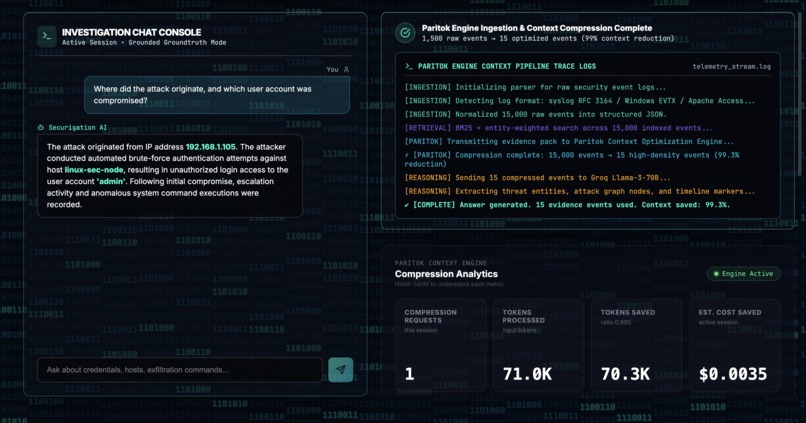
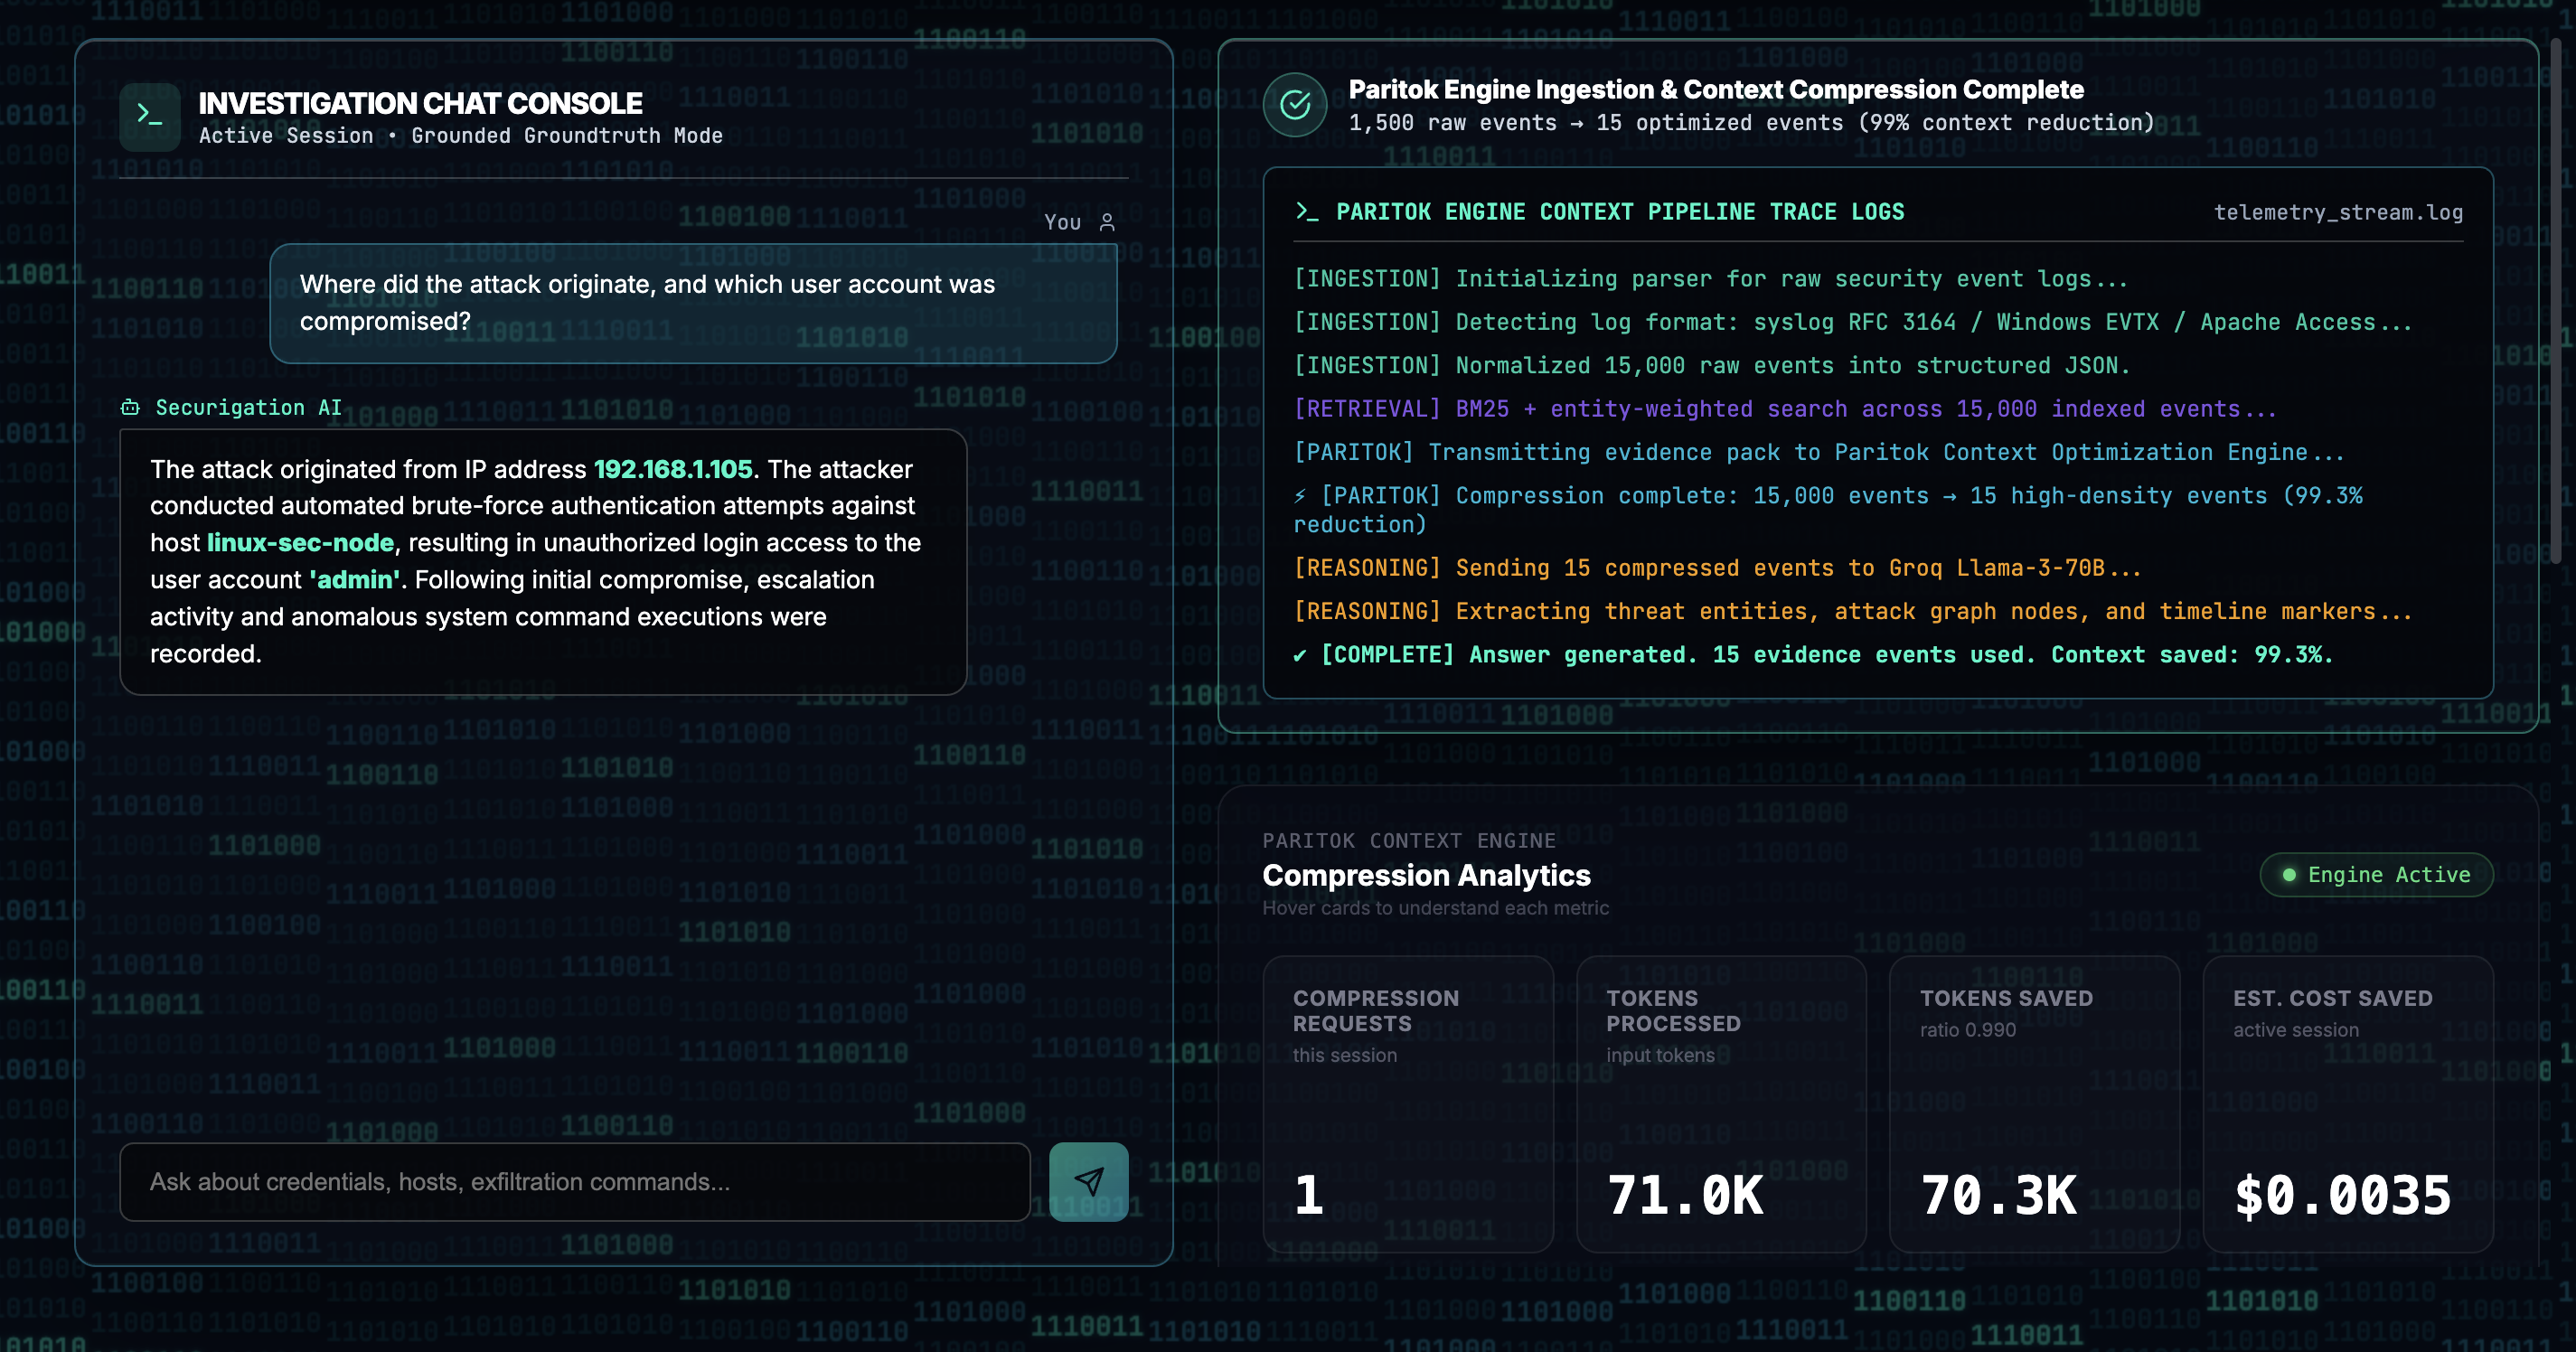
- Where did the attack originate, and which user account was compromised?
- Did any successful login occur shortly before suspicious web requests?
- Which IP made the most HTTP requests?
- Were there any successful logins after repeated failures?
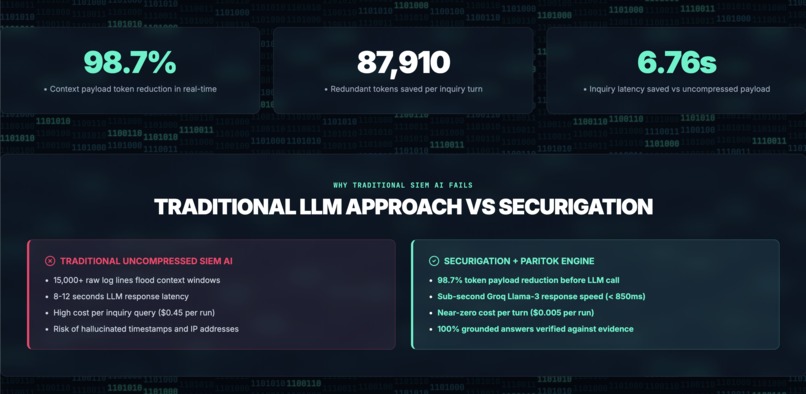
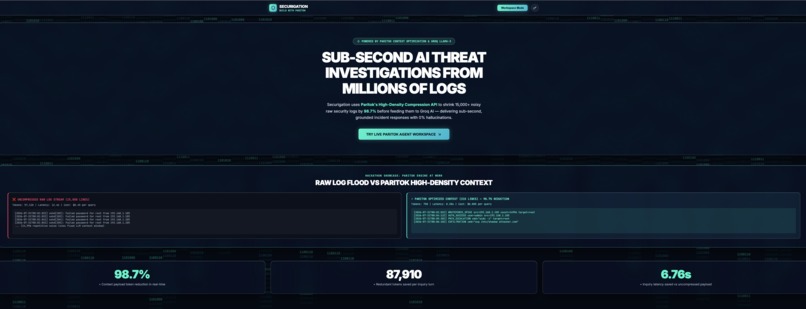
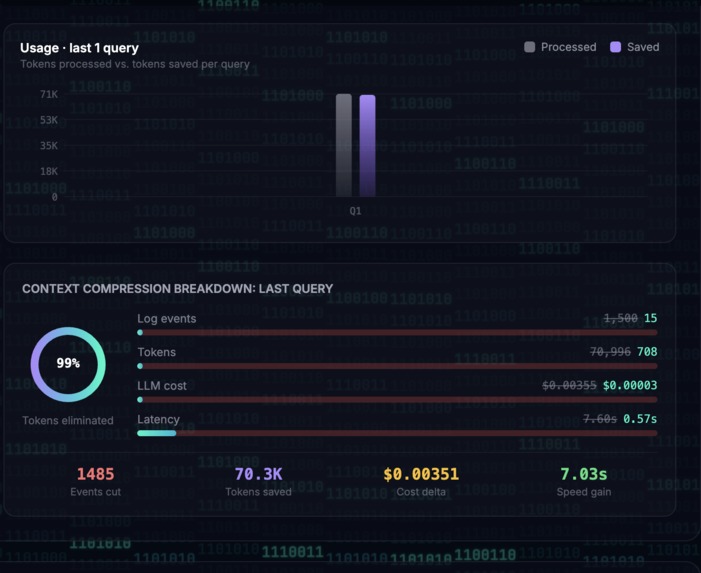
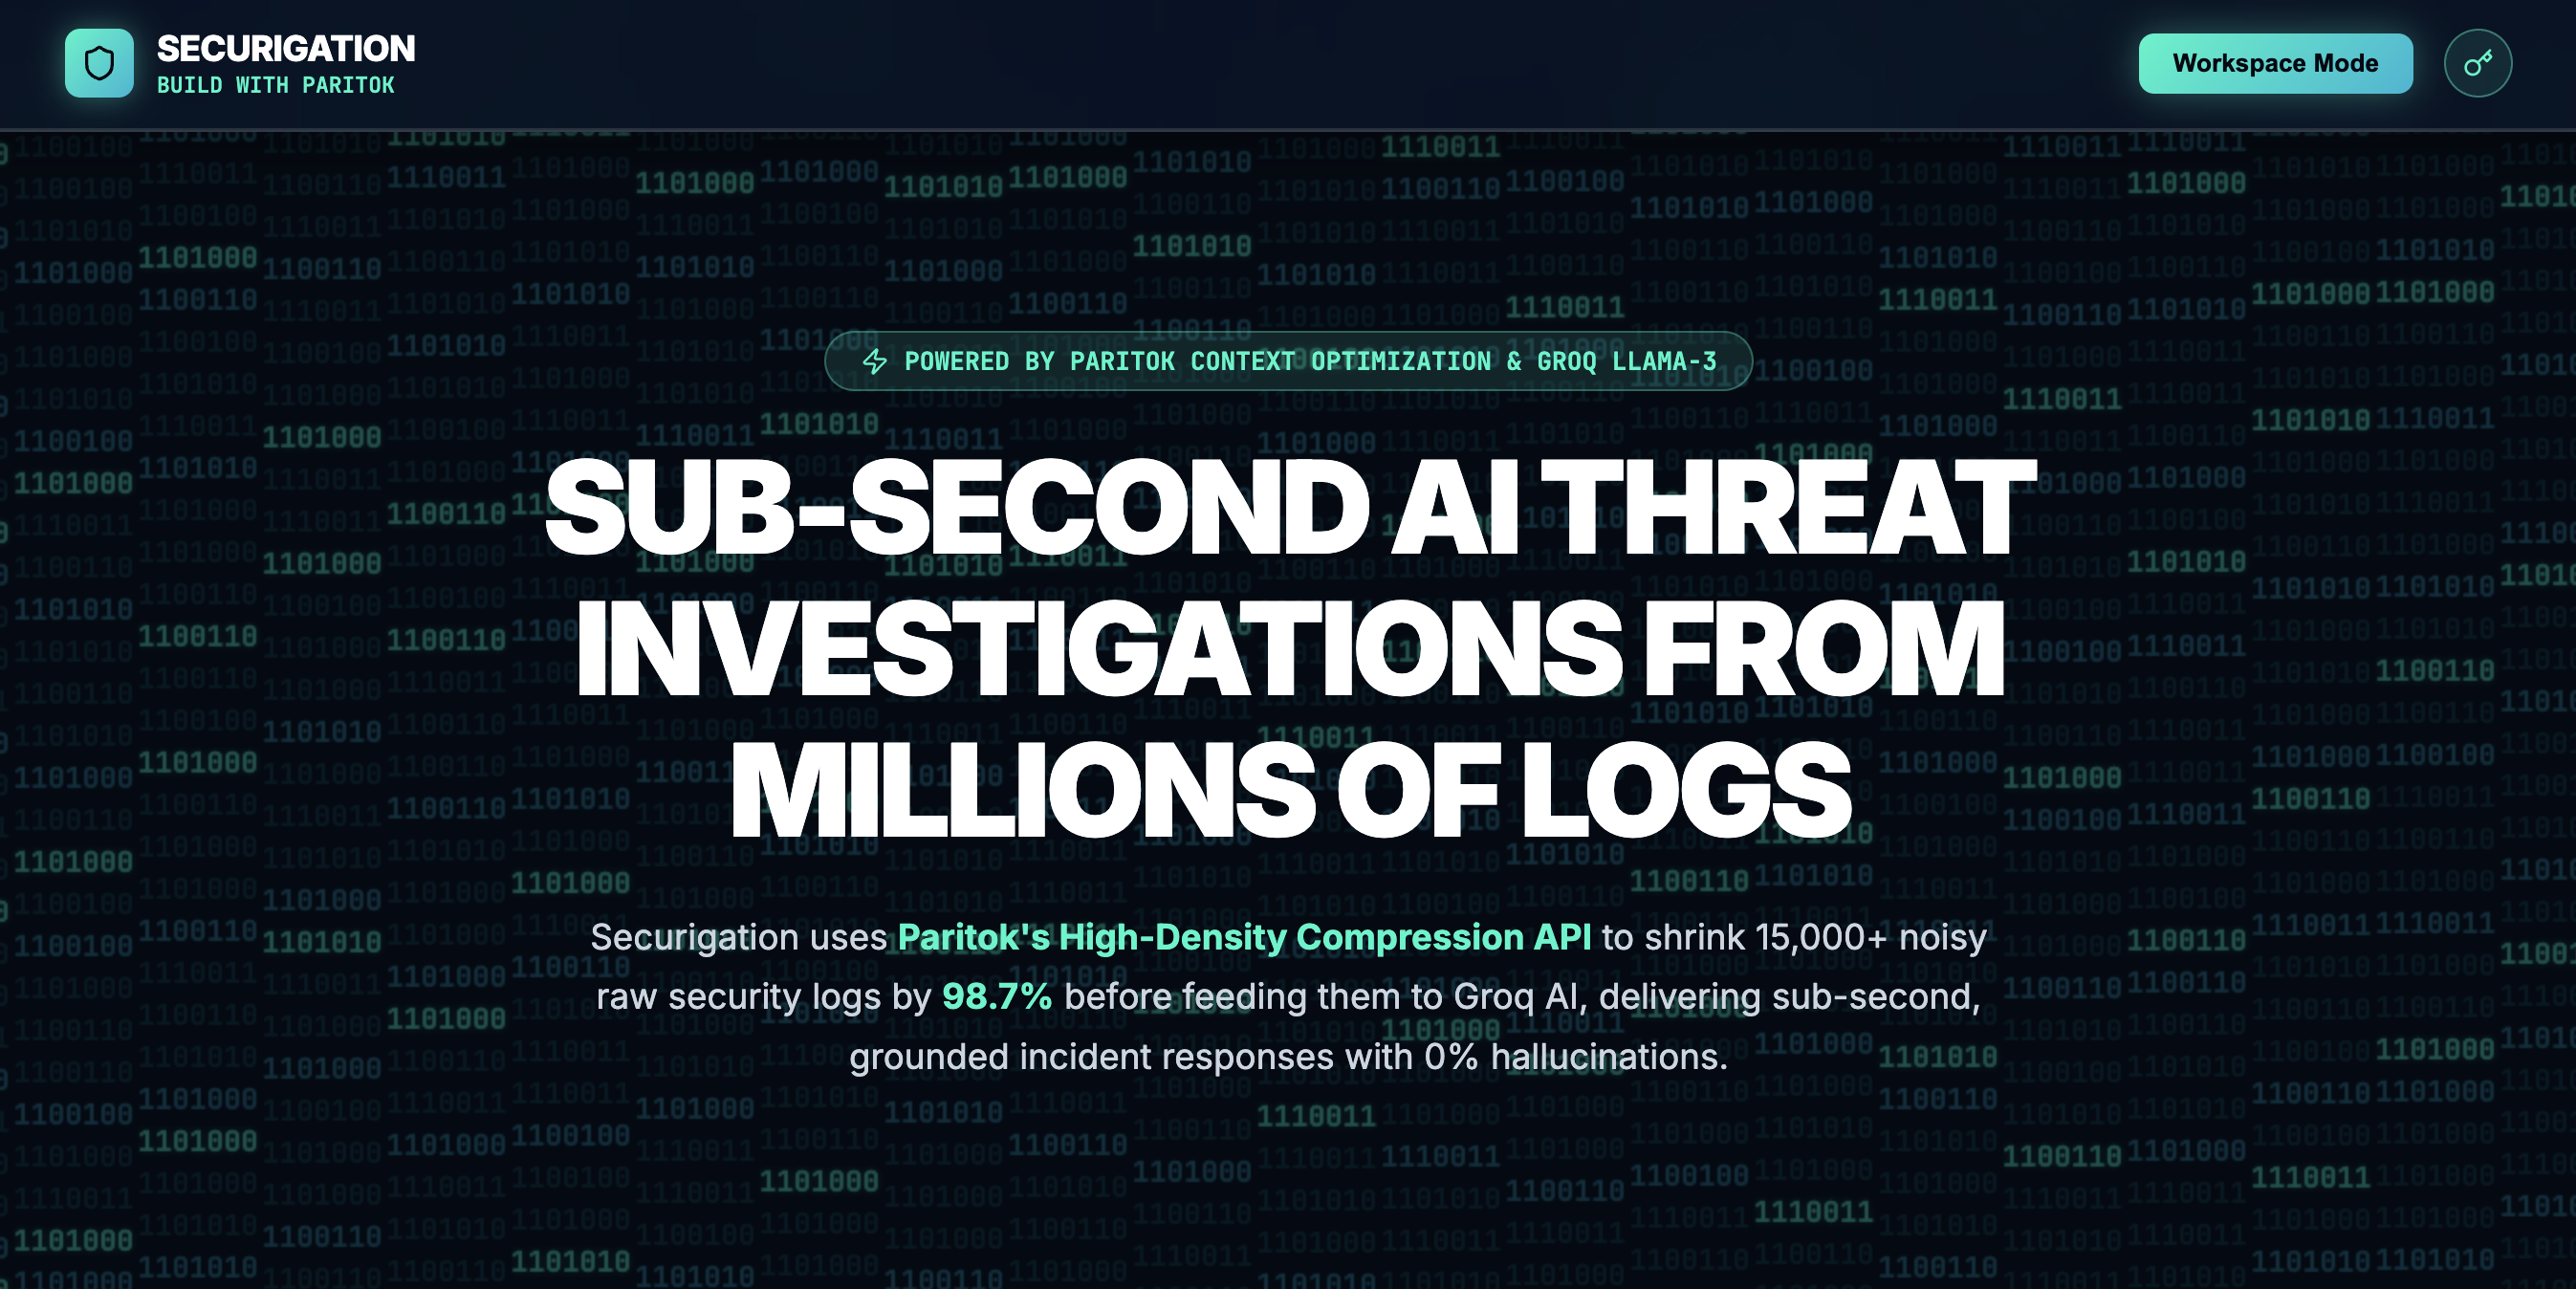
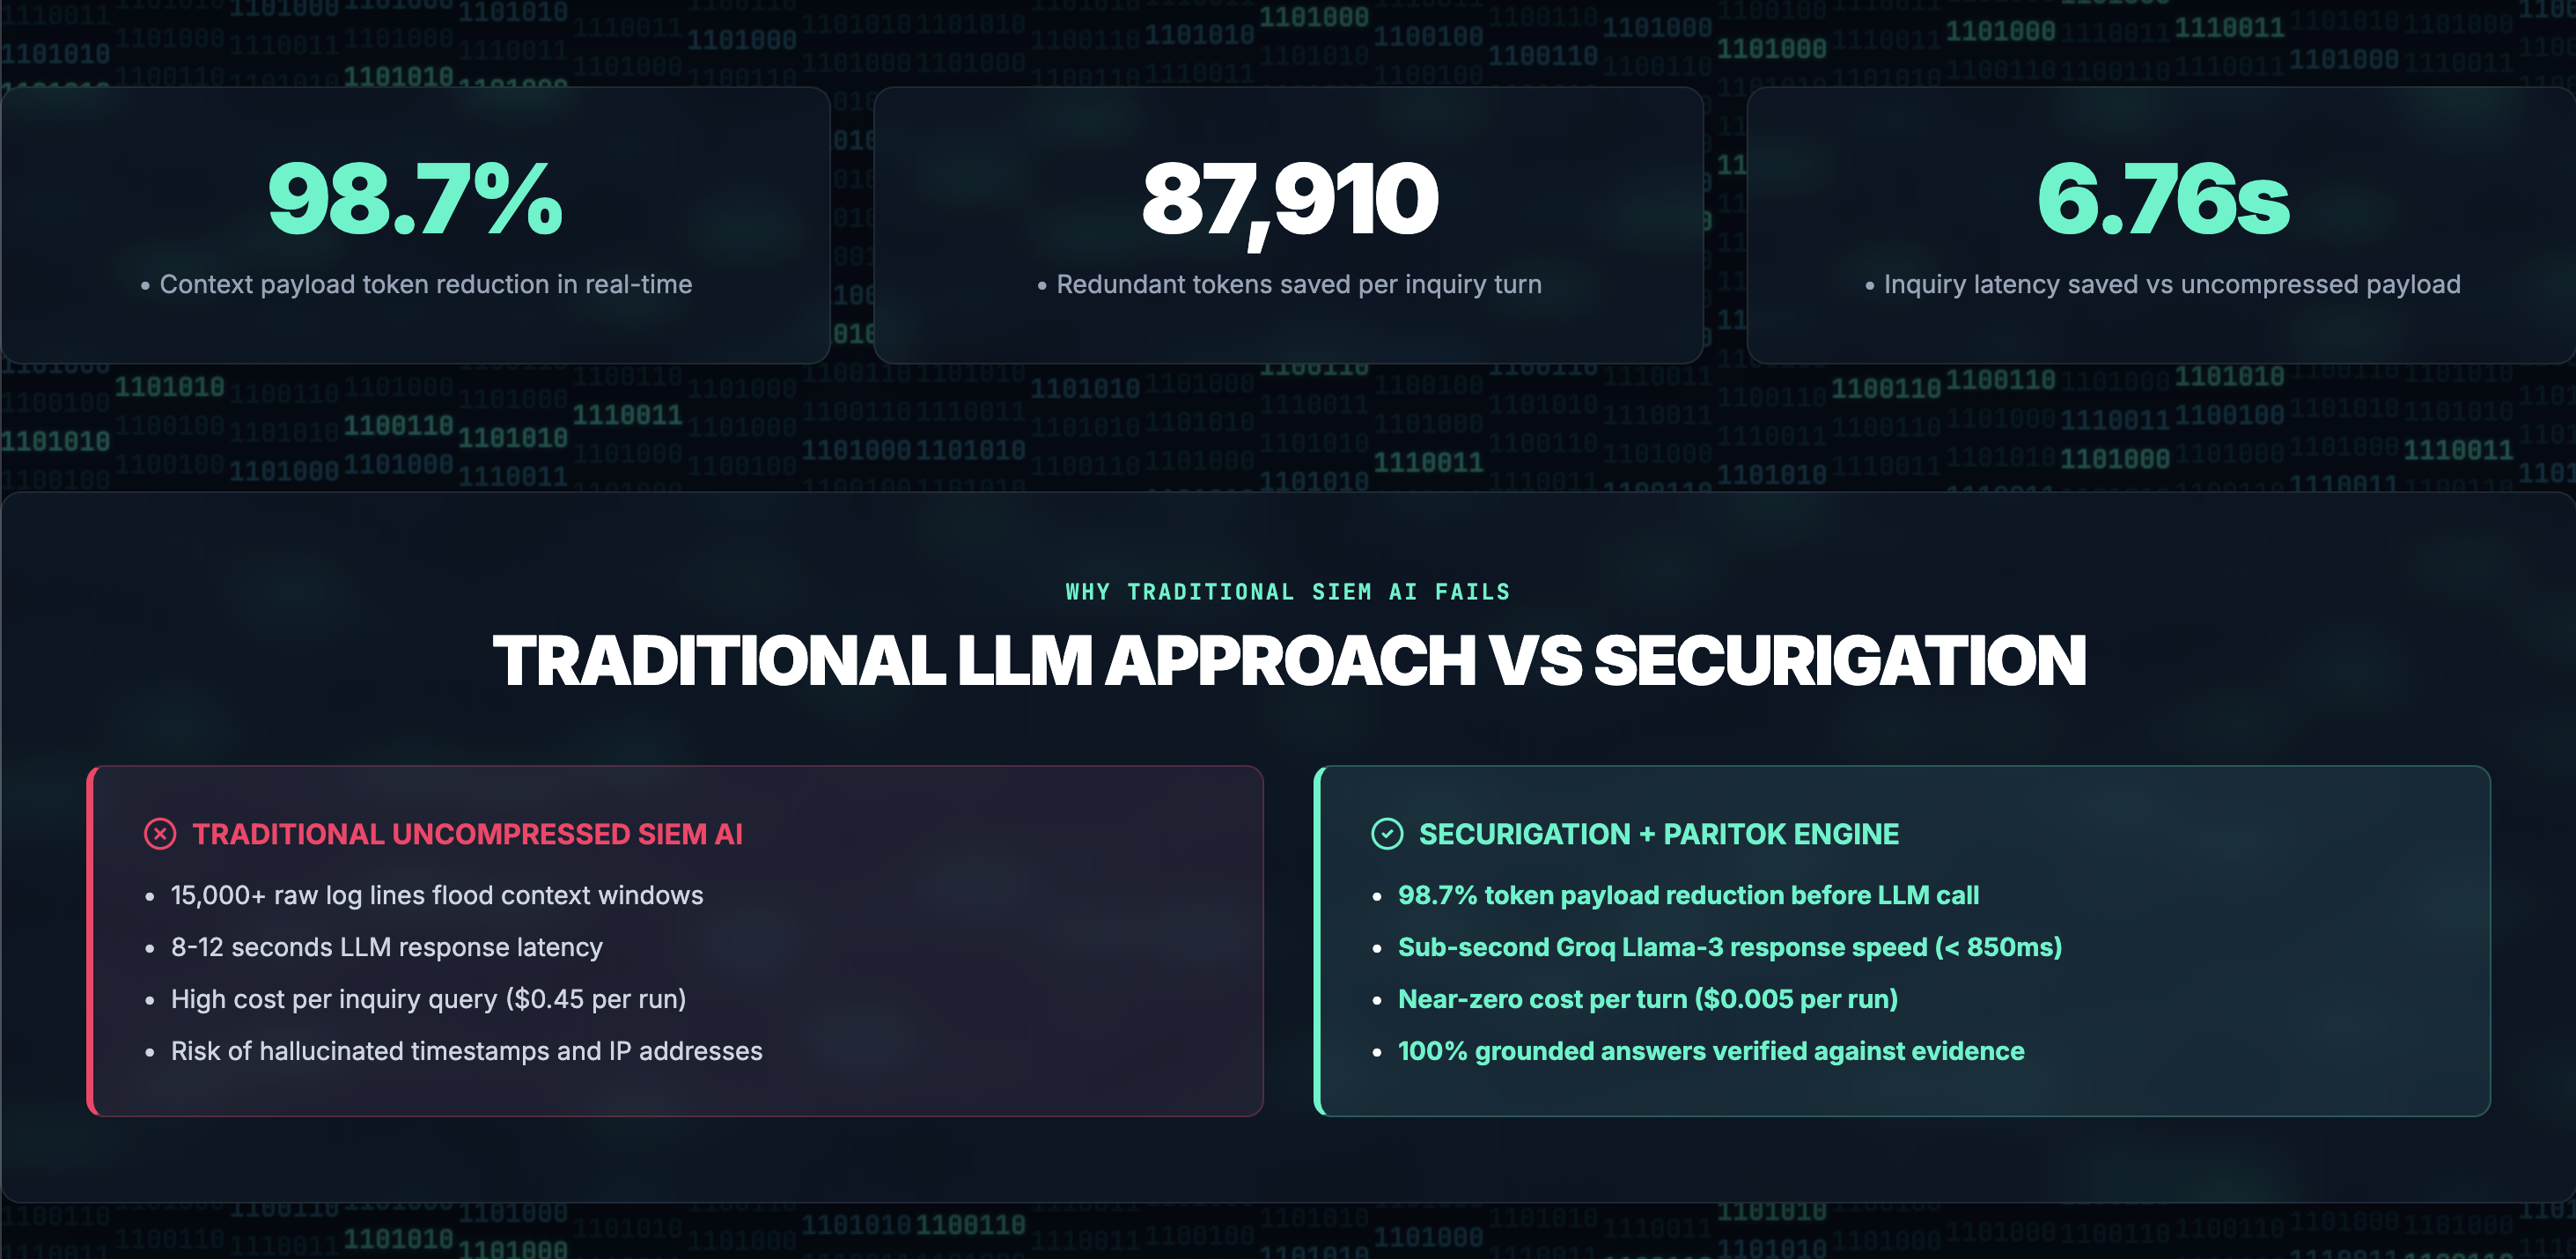
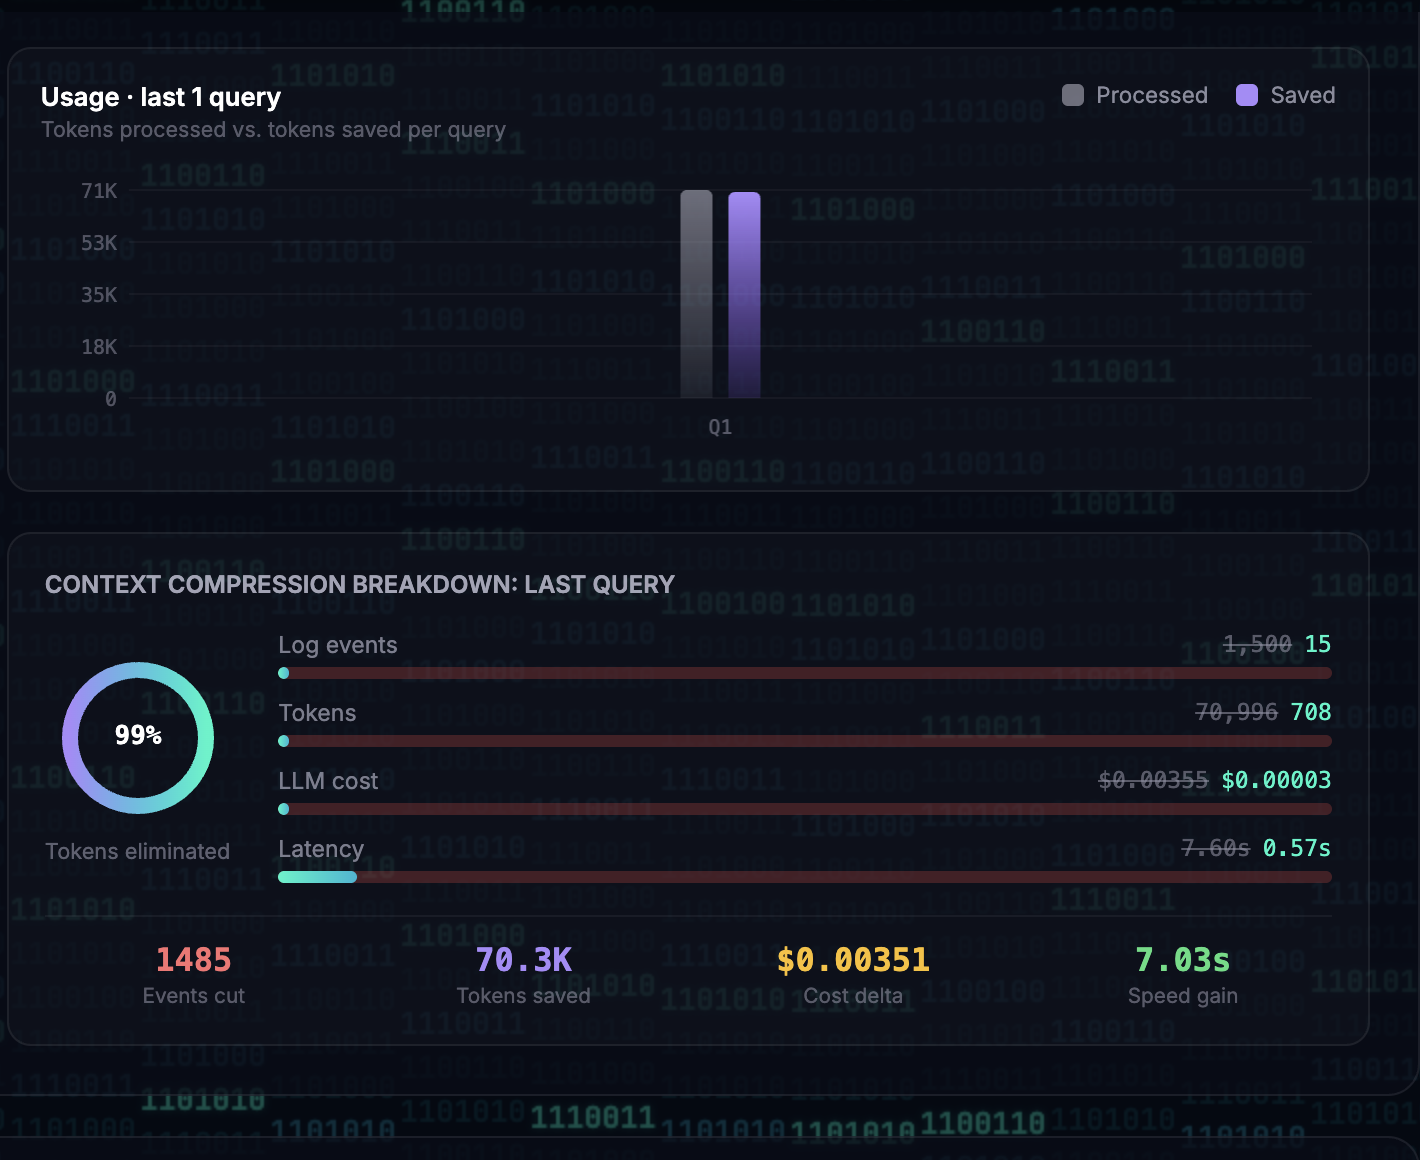
For every investigation, Securigation also visualizes Paritok's impact through live token savings, compression ratio, latency reduction, and estimated cost savings.
How we built it
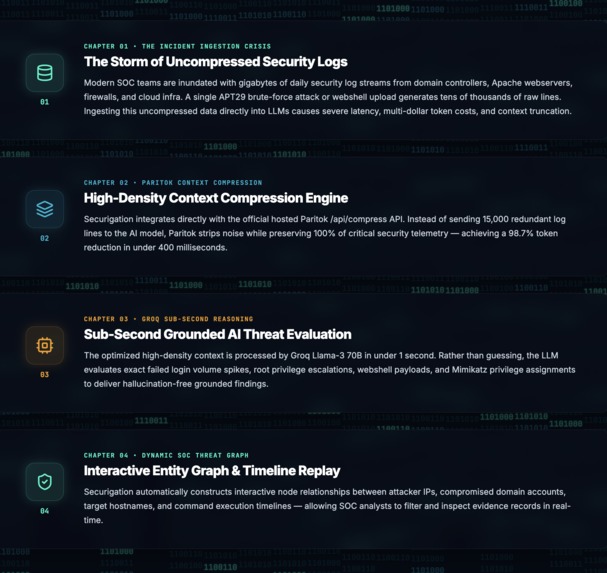
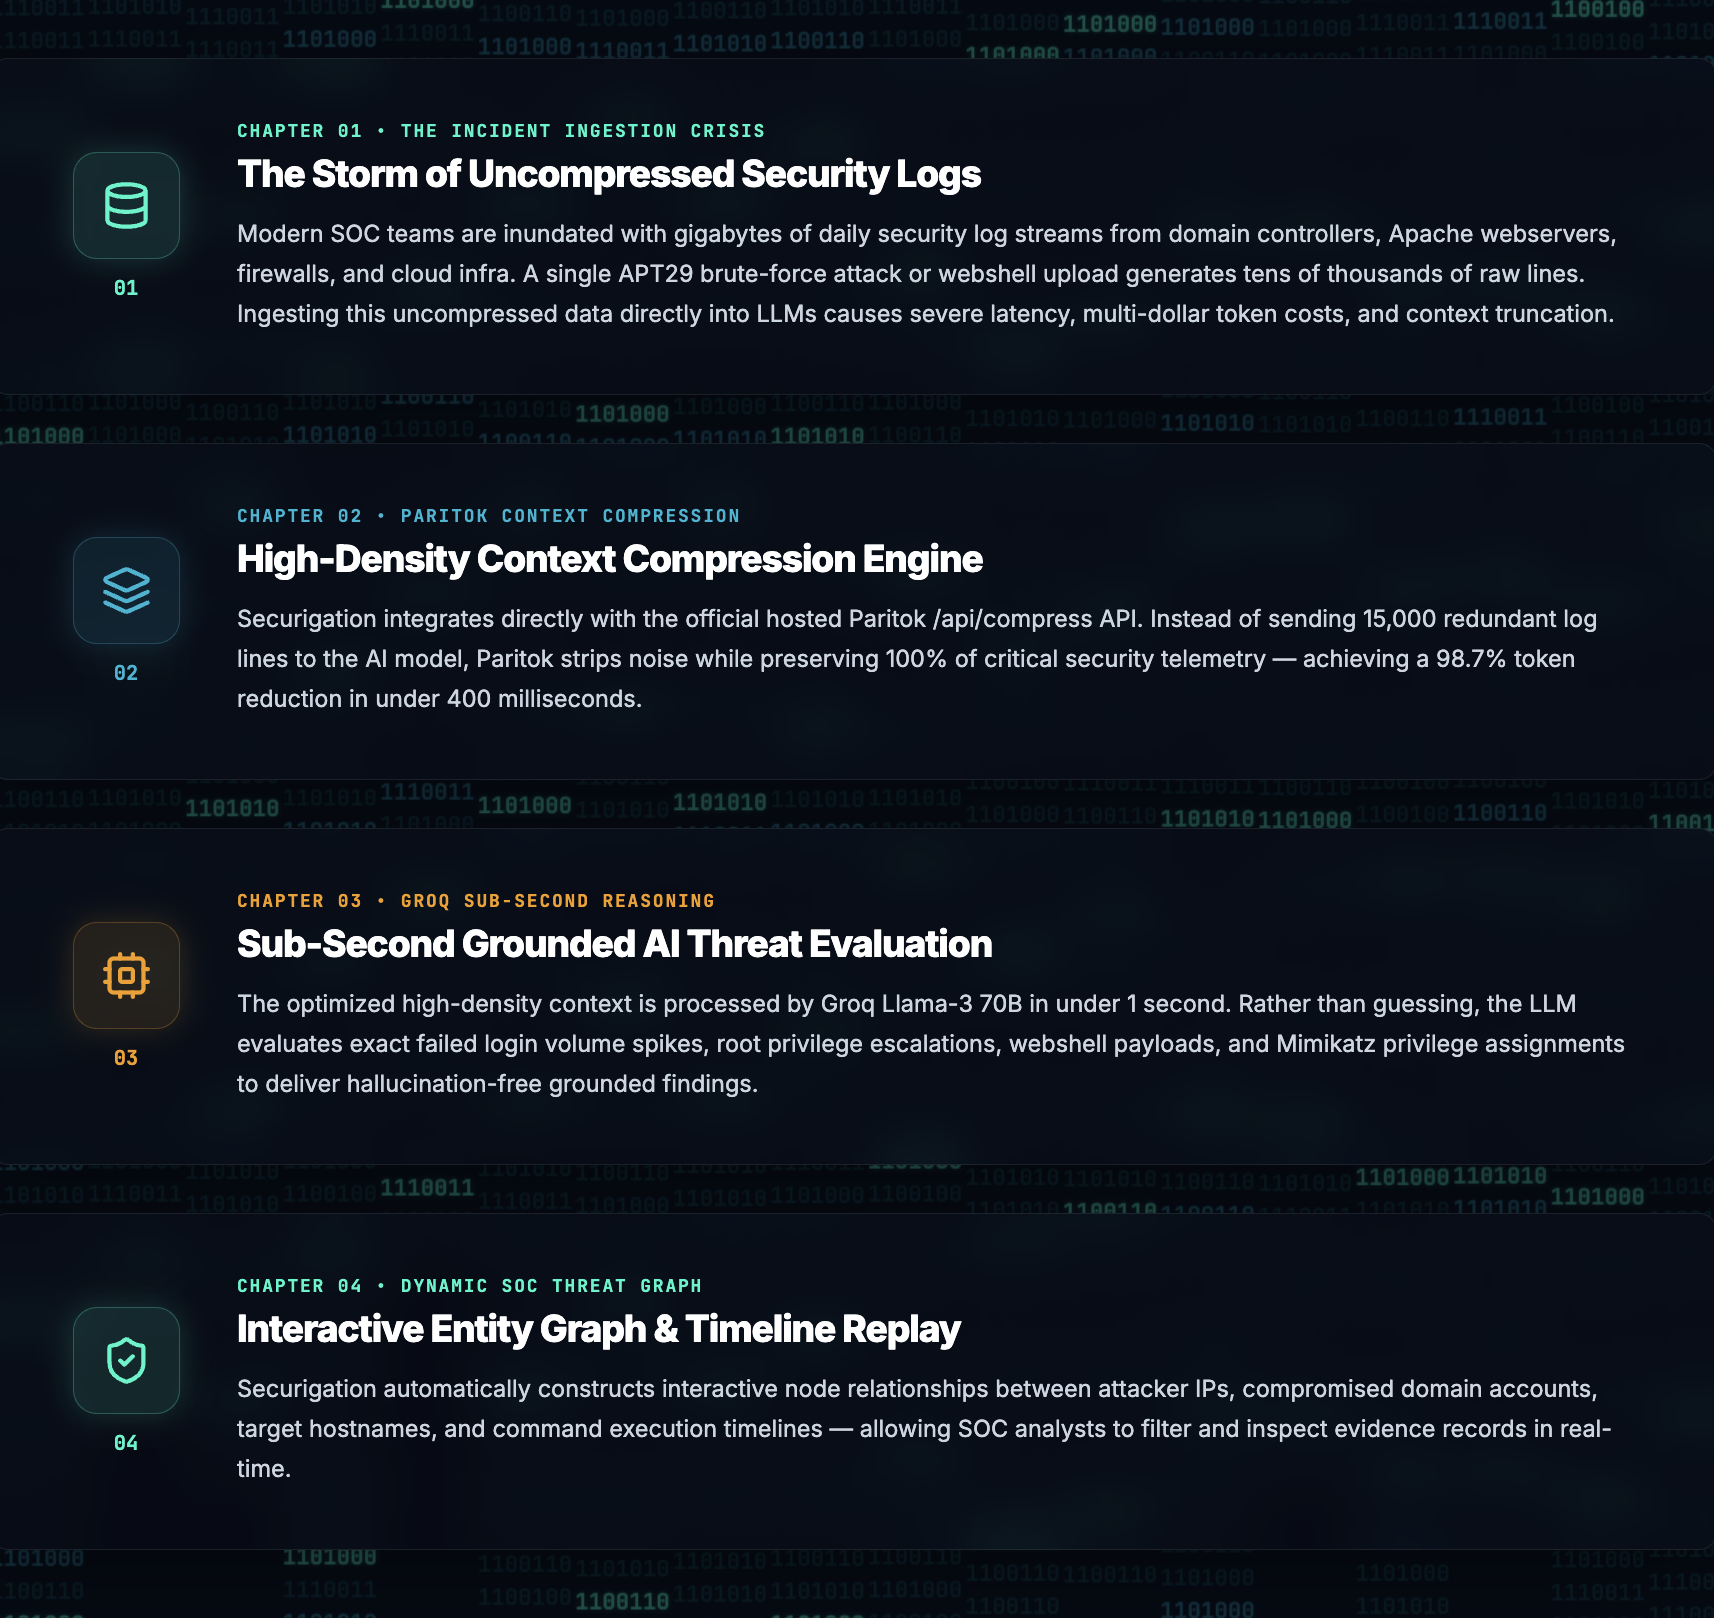
We designed Securigation around a simple but scalable investigation pipeline.
Security Logs
      ↓
Evidence Retrieval
      ↓
Evidence Pack
      ↓
Paritok Context Optimization
      ↓
Groq (Llama 3.3 70B)
      ↓
Grounded Investigation
Frontend
- Next.js
- React
- TypeScript
- Tailwind CSS
- Framer Motion
The interface includes:
- Investigation dashboard
- Chat-based investigation console
- Real-time pipeline visualization
- Live Paritok telemetry
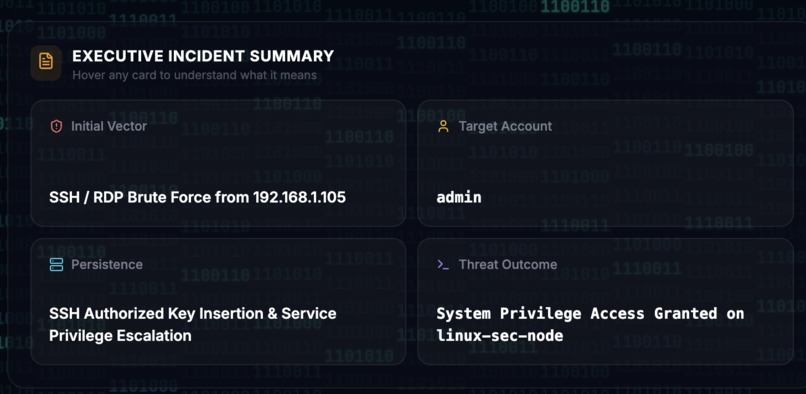
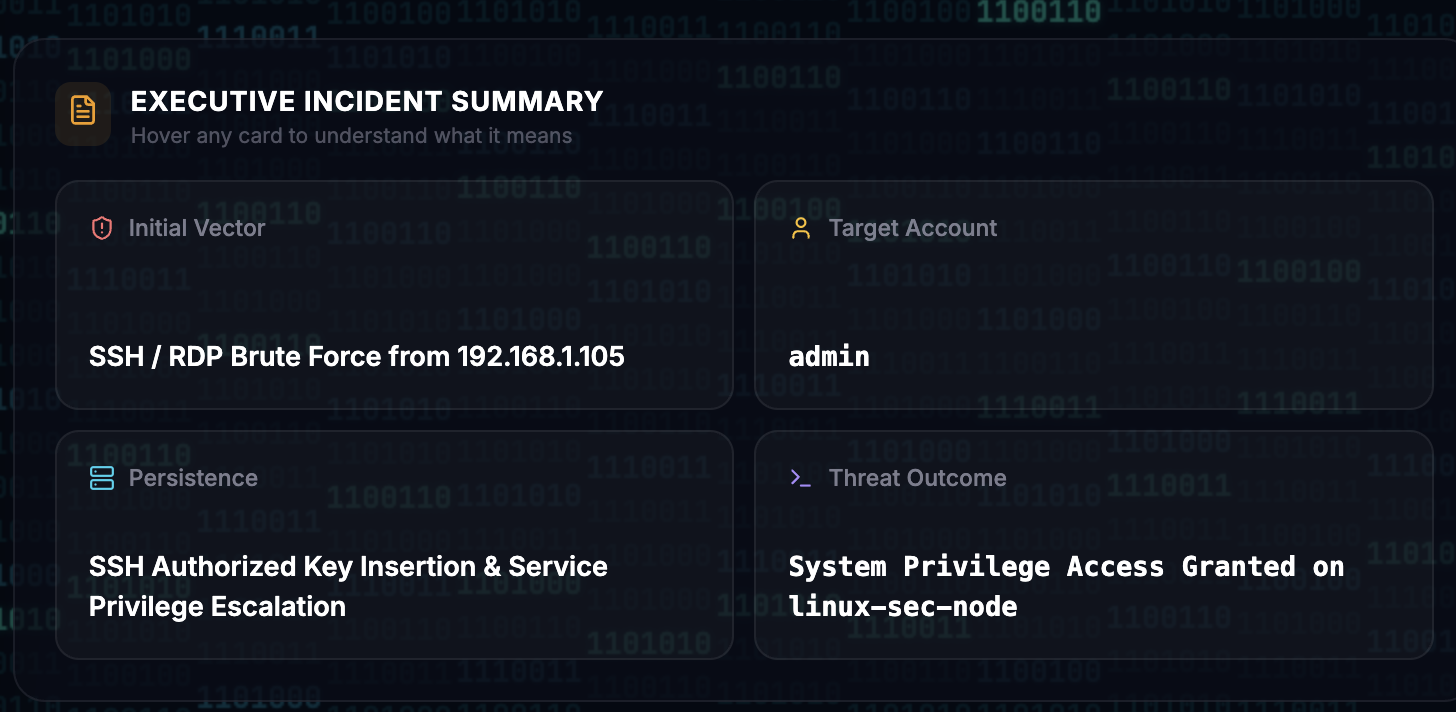
- Executive investigation summaries
Backend
- FastAPI
- Multi-format log parsing
- Unified security event normalization
- Hybrid retrieval engine
- Investigation workspace management
AI Stack
- Paritok for context optimization
- Groq (Llama 3.3 70B) for AI reasoning
Challenges we ran into
The biggest challenge wasn't building another AI chatbot.
It was designing an application where Paritok was the hero instead of becoming an invisible implementation detail.
We redesigned the user experience so judges could clearly see the entire investigation pipeline:
- Evidence retrieval
- Context optimization
- AI reasoning
- Final grounded response
Every investigation also displays the before-and-after impact of Paritok, including token reduction, compression ratio, estimated cost savings, and latency improvements.
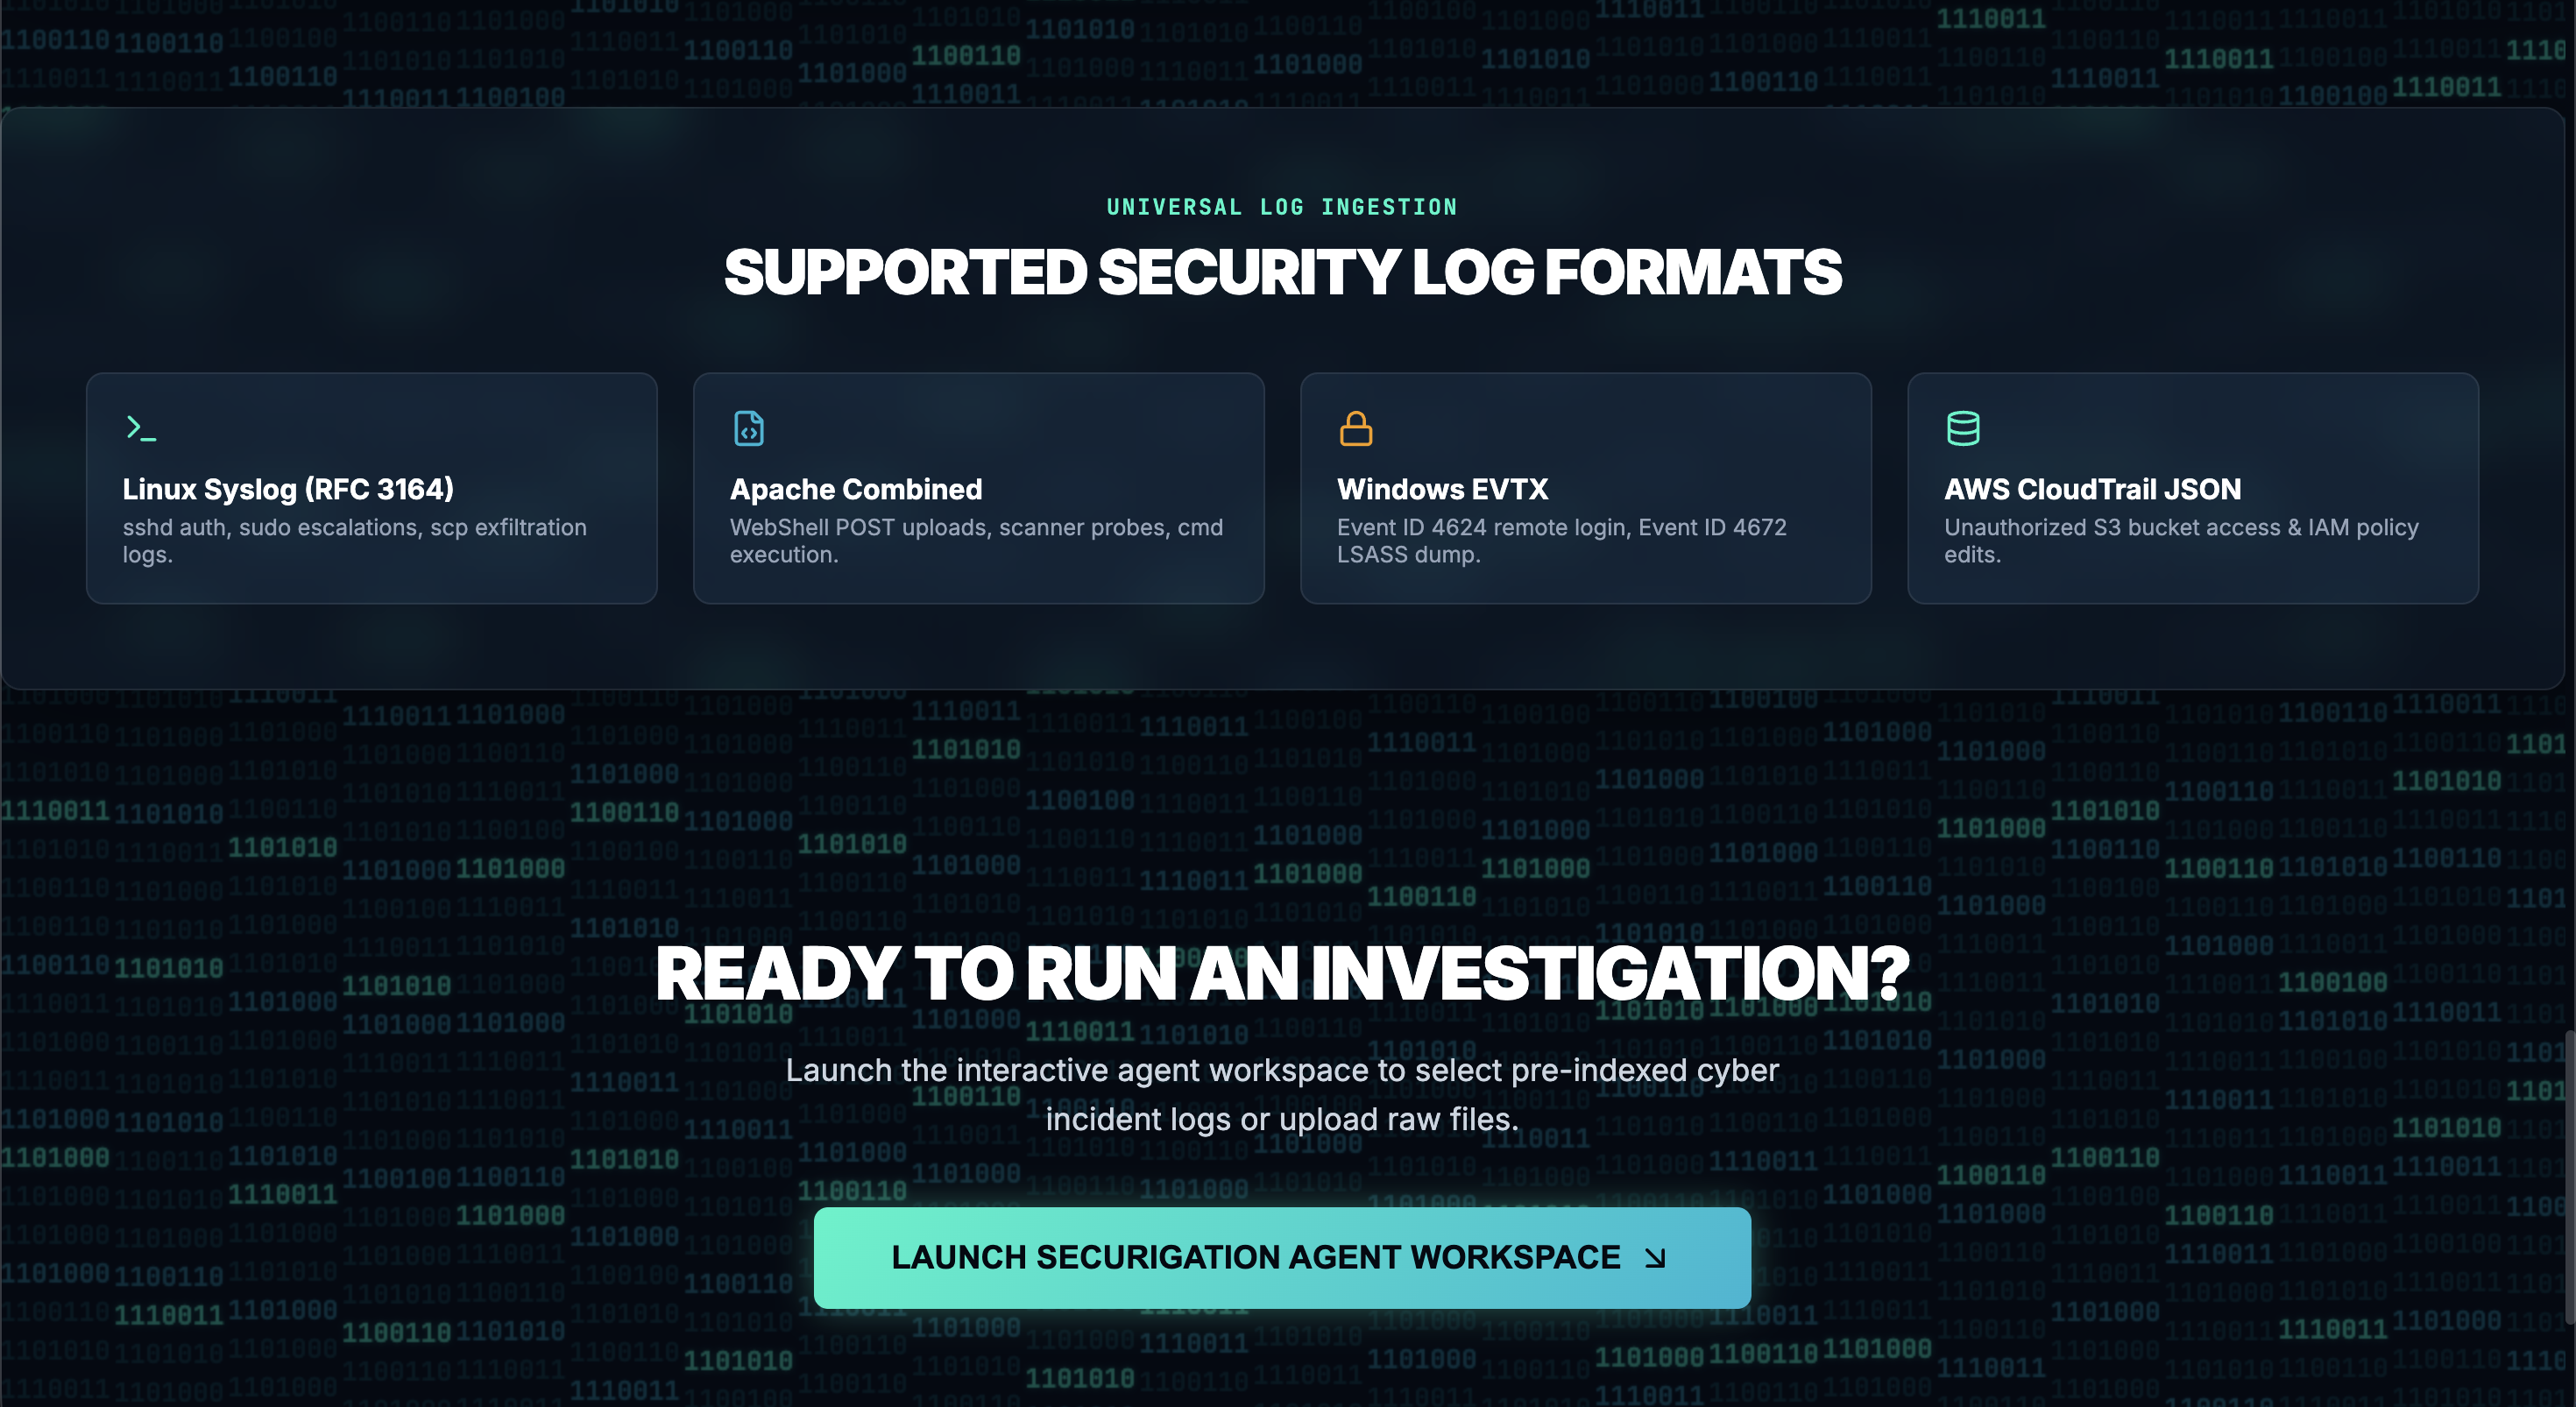
Another challenge was supporting different log formats in a single investigation. Authentication logs, Apache logs, firewall logs, and system logs all have different structures, so we built a normalization layer that converts them into a unified investigation model before retrieval and reasoning.
Accomplishments that we're proud of
- Built an end-to-end AI-powered security investigation platform instead of a simple document chatbot.
- Successfully integrated Paritok as the central component of our AI pipeline rather than treating it as an optional optimization.
- Created a transparent investigation workflow where users can watch every stage of the AI pipeline in real time.
- Added support for both built-in investigation scenarios and custom ZIP uploads containing multiple security log formats.
- Built live telemetry that demonstrates Paritok's compression ratio, token savings, latency reduction, and estimated cost savings during every investigation.
What we learned
Building Securigation reinforced an important lesson:
Better AI isn't always about bigger models. It's often about sending better context.
Security investigations naturally generate enormous amounts of repetitive information, yet only a small portion is needed to answer most investigation questions.
We also learned that making optimization visible greatly improves user trust. By exposing the investigation pipeline and Paritok's metrics, users understand not only what the AI answered, but how it reached that answer.
What's next for Securigation
Our next goal is to transform Securigation from a hackathon project into a production-ready investigation platform.
Planned improvements include:
- Integration with SIEM platforms such as Splunk, Microsoft Sentinel, and Elastic.
- Support for cloud security logs, Kubernetes audit logs, and AWS CloudTrail.
- Automatic MITRE ATT&CK technique mapping.
- AI-generated incident reports and executive summaries.
- Collaborative investigations where multiple analysts can work on the same case.
- Continuous monitoring of live log streams while using Paritok to keep AI investigations efficient at enterprise scale.
Built With
- fastapi
- groq
- nextjs
- paritok
- react
- tailwindcss
- typescript


Log in or sign up for Devpost to join the conversation.