-
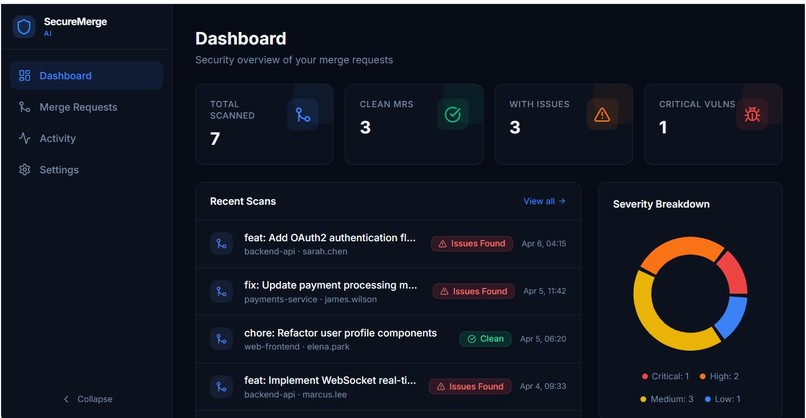
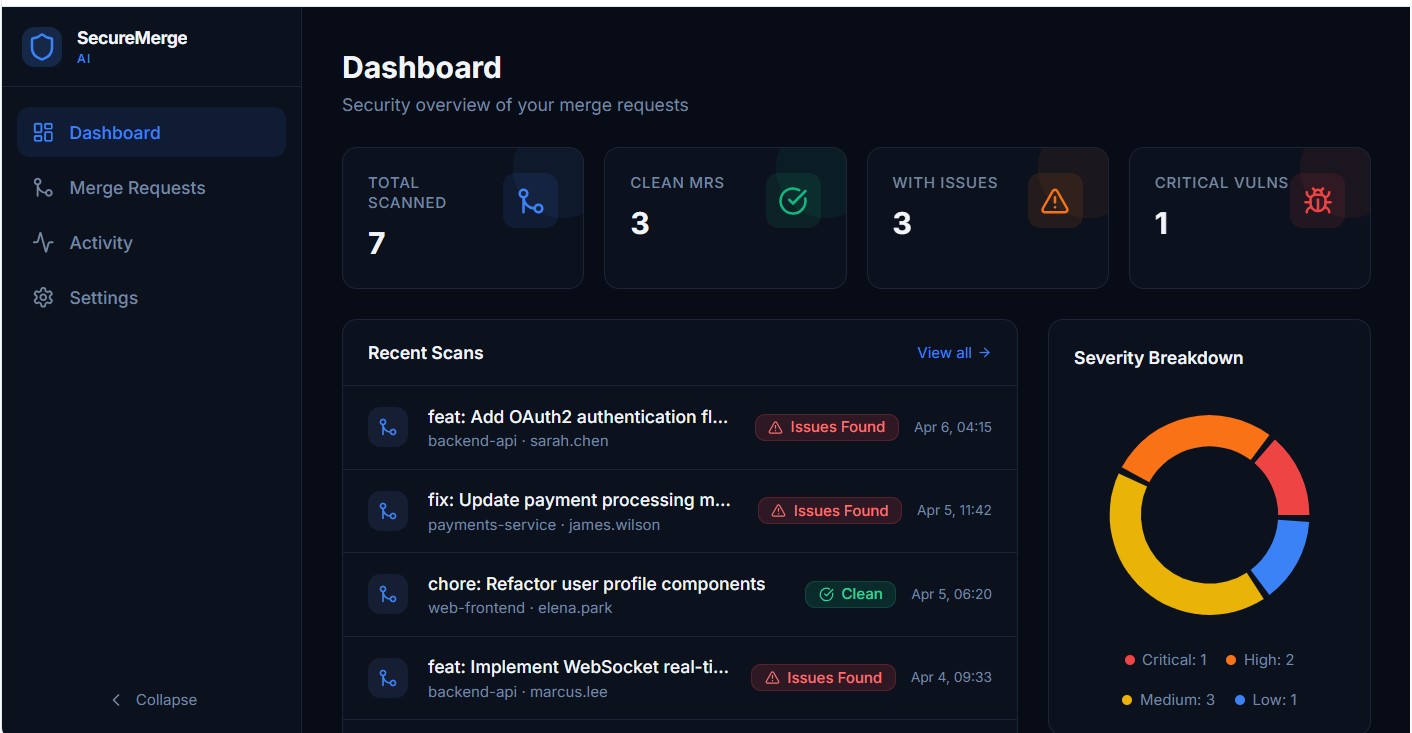
App while being used
Inspiration
SecureMerge AI was inspired by the growing number of security vulnerabilities that slip into production during fast-paced development cycles. Modern teams prioritize speed and frequent deployments, but manual code reviews often miss critical issues like exposed secrets, insecure dependencies, and injection risks. We wanted to build an intelligent system that acts as a real-time security layer inside the development workflow, ensuring safety without slowing down developers.
What it does
SecureMerge AI automatically analyzes every pull request and flags potential security risks before code is merged. It detects vulnerabilities, exposed credentials, and unsafe patterns, and provides clear, actionable feedback directly in the developer’s workflow. The goal is to help teams ship faster while maintaining strong security standards.
How we built it
We built SecureMerge AI as an AI-powered code review system integrated into the Git-based pull request workflow. When a PR is submitted, the system:
- Parses the code changes
- Analyzes them for security risks and sensitive patterns
- Uses AI to understand context and severity
- Generates structured feedback for developers
We focused on making the output simple, readable, and useful so developers can act on it immediately.
Challenges we ran into
One of the biggest challenges was reducing false positives. Early versions of the system flagged too many harmless patterns, which made the feedback less trustworthy. We iterated on improving context awareness so the model could better distinguish between real vulnerabilities and safe code patterns. Another challenge was balancing analysis depth vs. performance, ensuring the tool runs fast enough to fit naturally into CI/CD pipelines.
Accomplishments that we're proud of
We successfully built a system that integrates directly into the development workflow and provides real-time, meaningful security feedback on pull requests. We are especially proud of improving detection accuracy while keeping the tool lightweight and fast enough for practical use.
What we learned
We learned how important context is in code understanding, especially when applying AI to real-world engineering workflows. We also gained experience in vulnerability detection patterns, CI/CD integration concepts, and designing developer tools that prioritize usability over complexity. We further learned how small improvements in prompt design and filtering logic can significantly reduce noise and improve trust in AI-driven systems.
What's next for SecureMerge AI
Next, we plan to expand SecureMerge AI into a full developer security platform with deeper integrations into CI/CD pipelines, IDE plugins, and team dashboards. We also aim to improve multi-language support, enhance vulnerability classification, and introduce automated fix suggestions so developers can resolve issues with one click.

Log in or sign up for Devpost to join the conversation.