Inspiration
Challenges in Merge Requests.
What it does
Sample Output:
Key Changes Detected File Modified: README.md Change: Added a link to the onboarding issue in the README file.
Copy to clipboard Insert at cursor For instructions on how to get started take a look at the onboarding issue in this project
Security Analysis
- Hardcoded Secrets or Credentials ✅ PASS - No hardcoded secrets, API keys, passwords, or credentials detected.
- Vulnerabilities or Unsafe Patterns ✅ PASS - No unsafe code patterns detected. The change is purely documentation.
- Sensitive Data Exposure ✅ PASS - No sensitive data exposed. The link is a relative reference to an internal work item.
- Code Quality & Safety ✅ PASS - This is a documentation-only change with no code modifications.
- Compliance & Structure ✅ PASS - Commit message is clear and descriptive. The change follows documentation best practices.
Security Findings Total Issues Found: 0
Severity Count Details
🔴 HIGH 0 None
🟡 MEDIUM 0 None
🟢 LOW 0 None
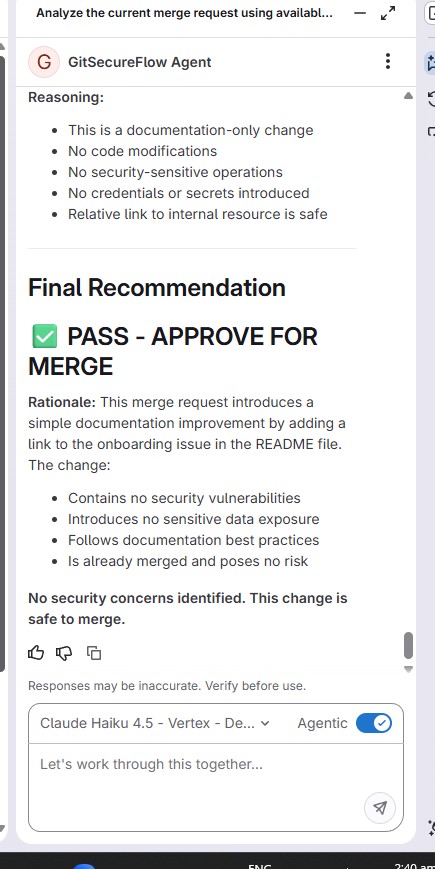
Risk Classification Overall Risk Level: 🟢 LOW Reasoning:
This is a documentation-only change No code modifications No security-sensitive operations No credentials or secrets introduced Relative link to internal resource is safe
Final Recommendation ✅ PASS - APPROVE FOR MERGE Rationale: This merge request introduces a simple documentation improvement by adding a link to the onboarding issue in the README file. The change:
Contains no security vulnerabilities Introduces no sensitive data exposure Follows documentation best practices Is already merged and poses no risk
No security concerns identified. This change is safe to merge.
How I built it
Gitlab Duo, Also tested outside the project group using Python.
Challenges I ran into
PErsonal Tokens, Approvals
Accomplishments that I'm proud of
It was able to run smoothly
What I learned
That you can use an Agent to act as teammate for SDLC
What's next for GitSecureFlow AI
Add more features if I have time
Built With
- gitlab

Log in or sign up for Devpost to join the conversation.