-
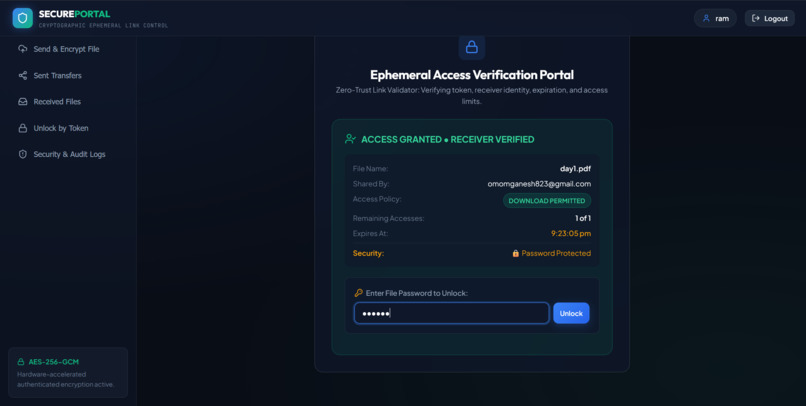
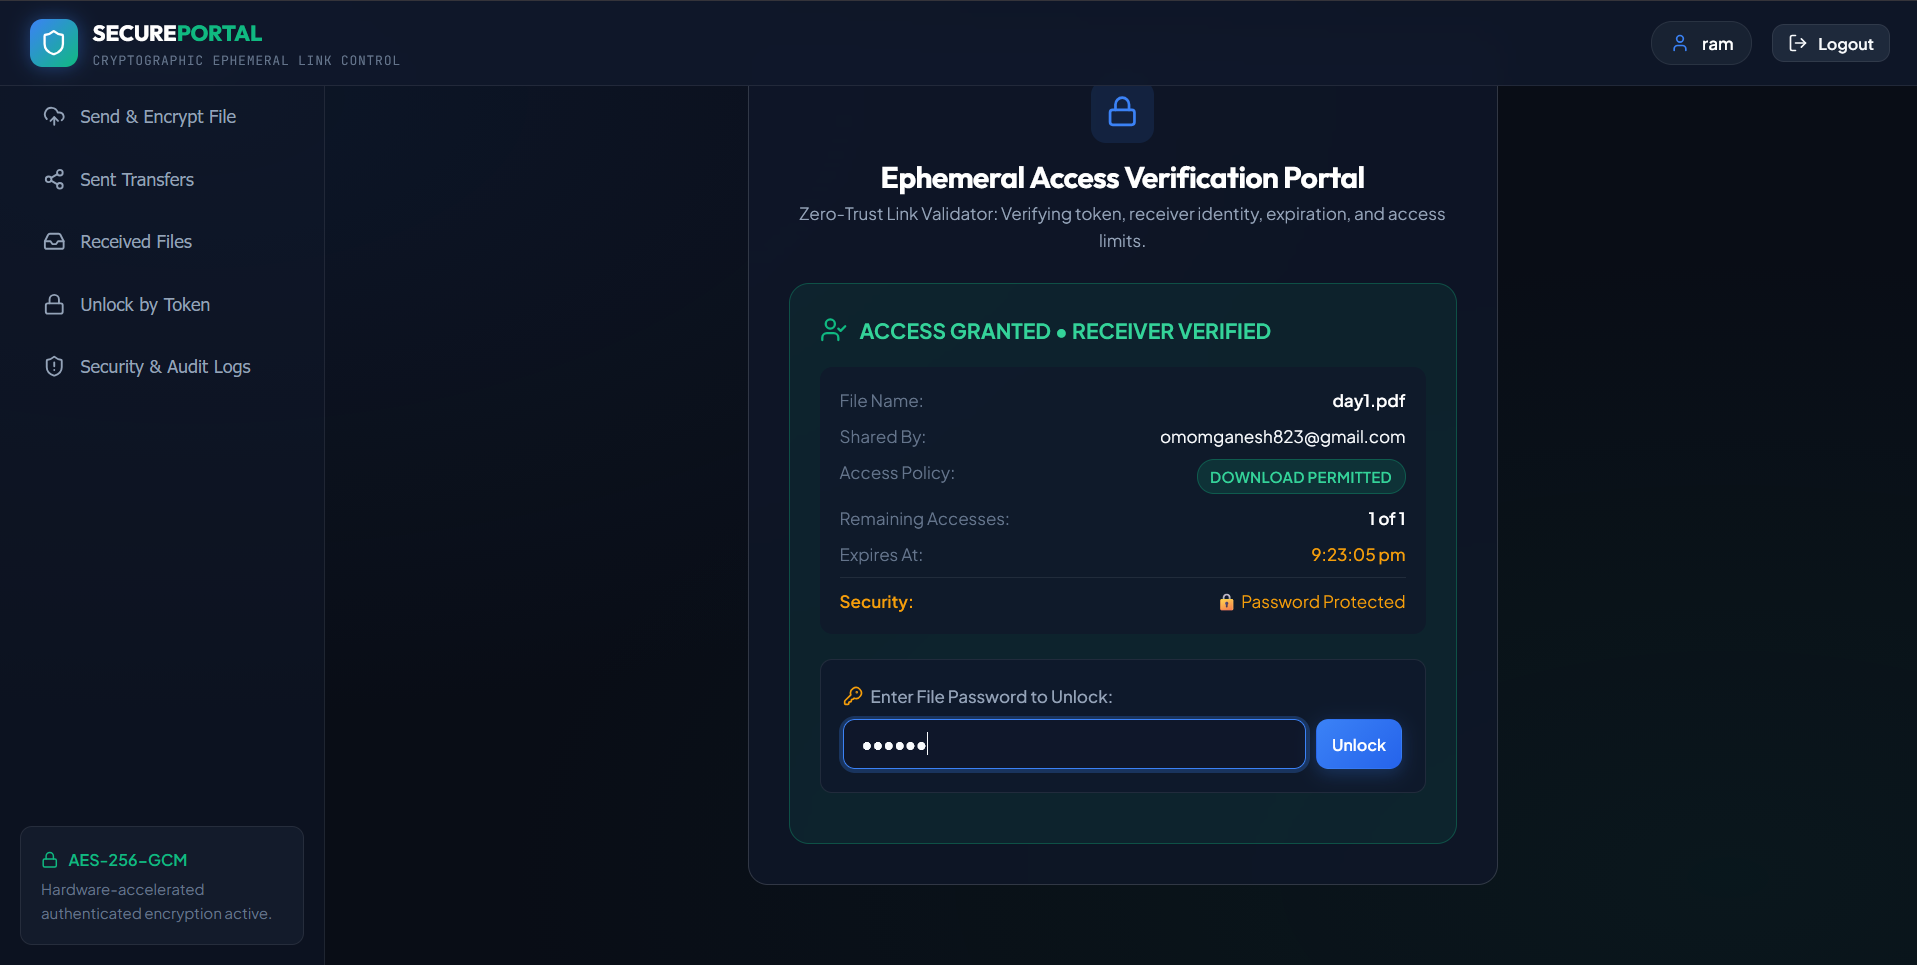
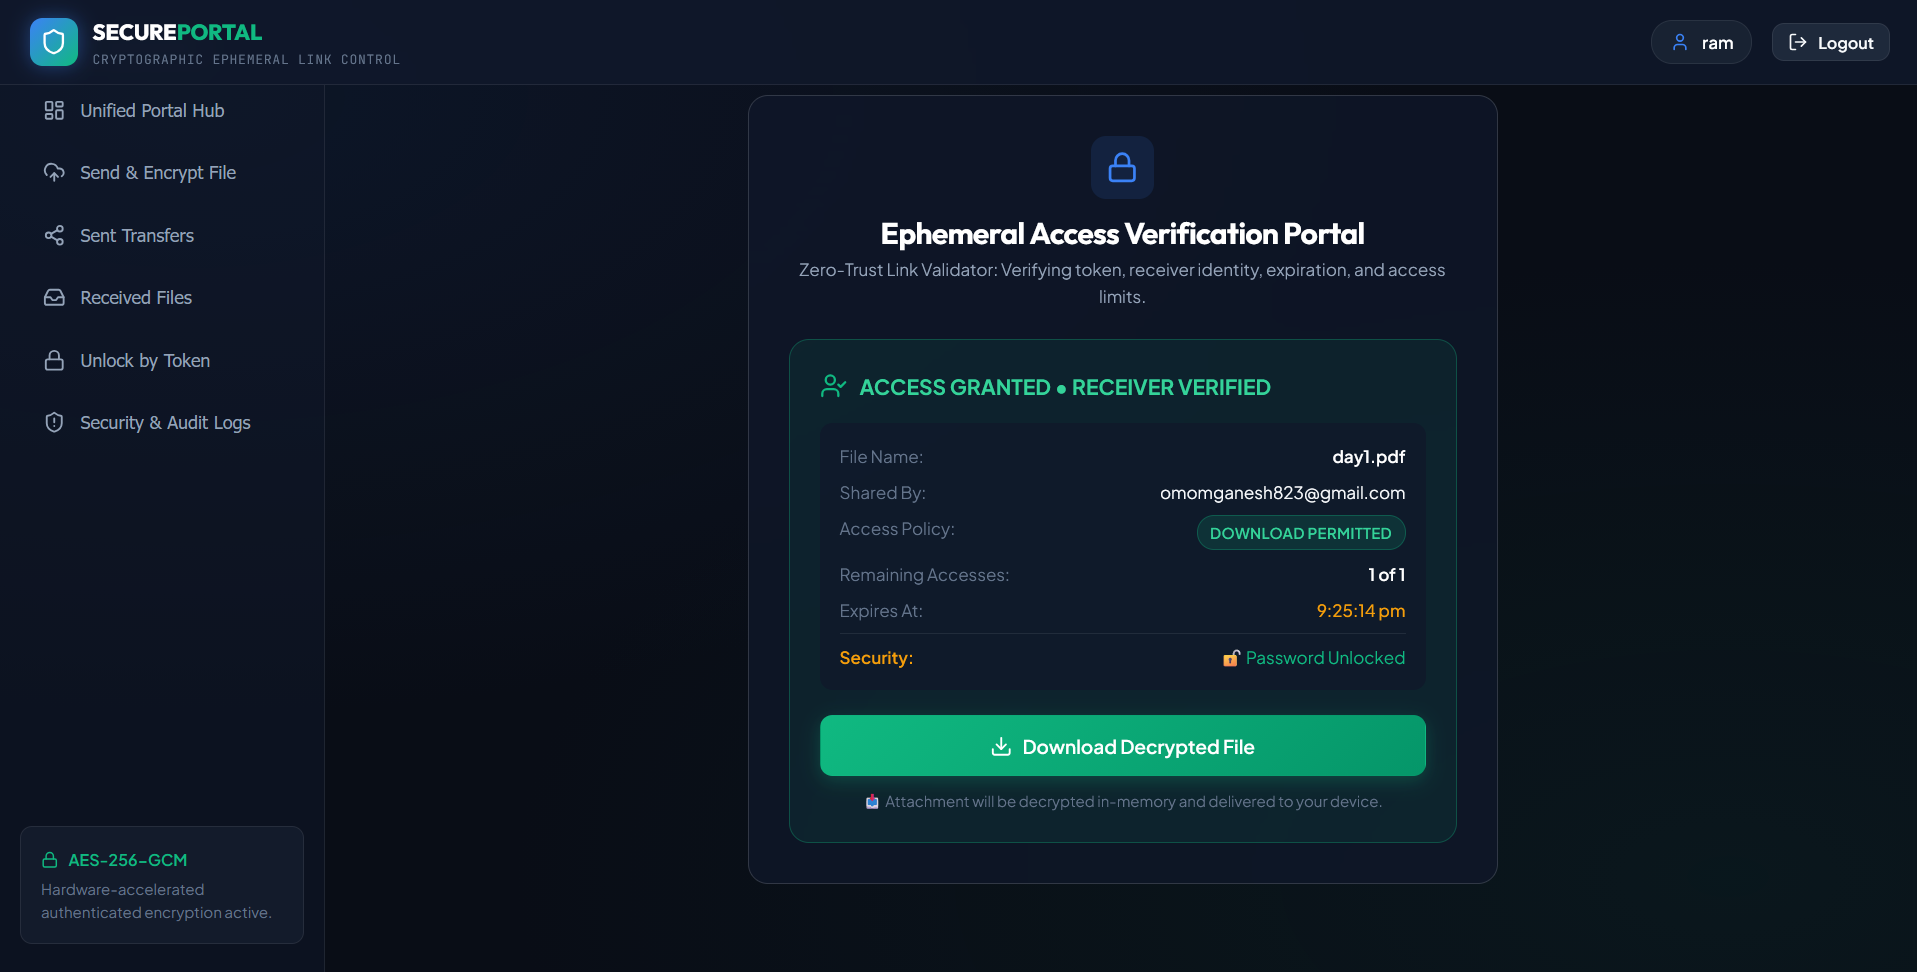
asking the password to open the file access
-
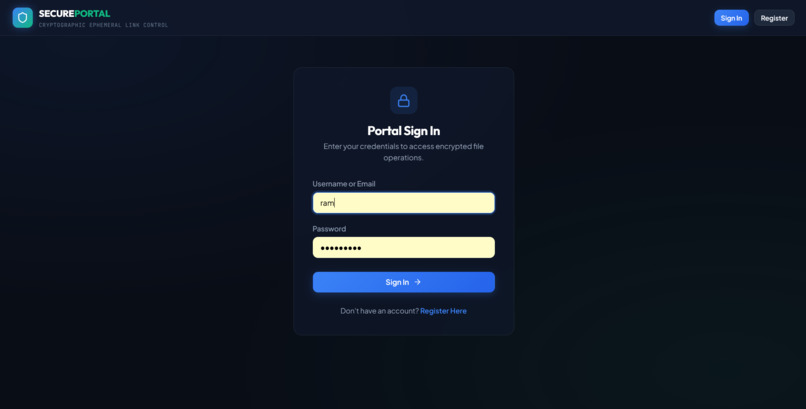
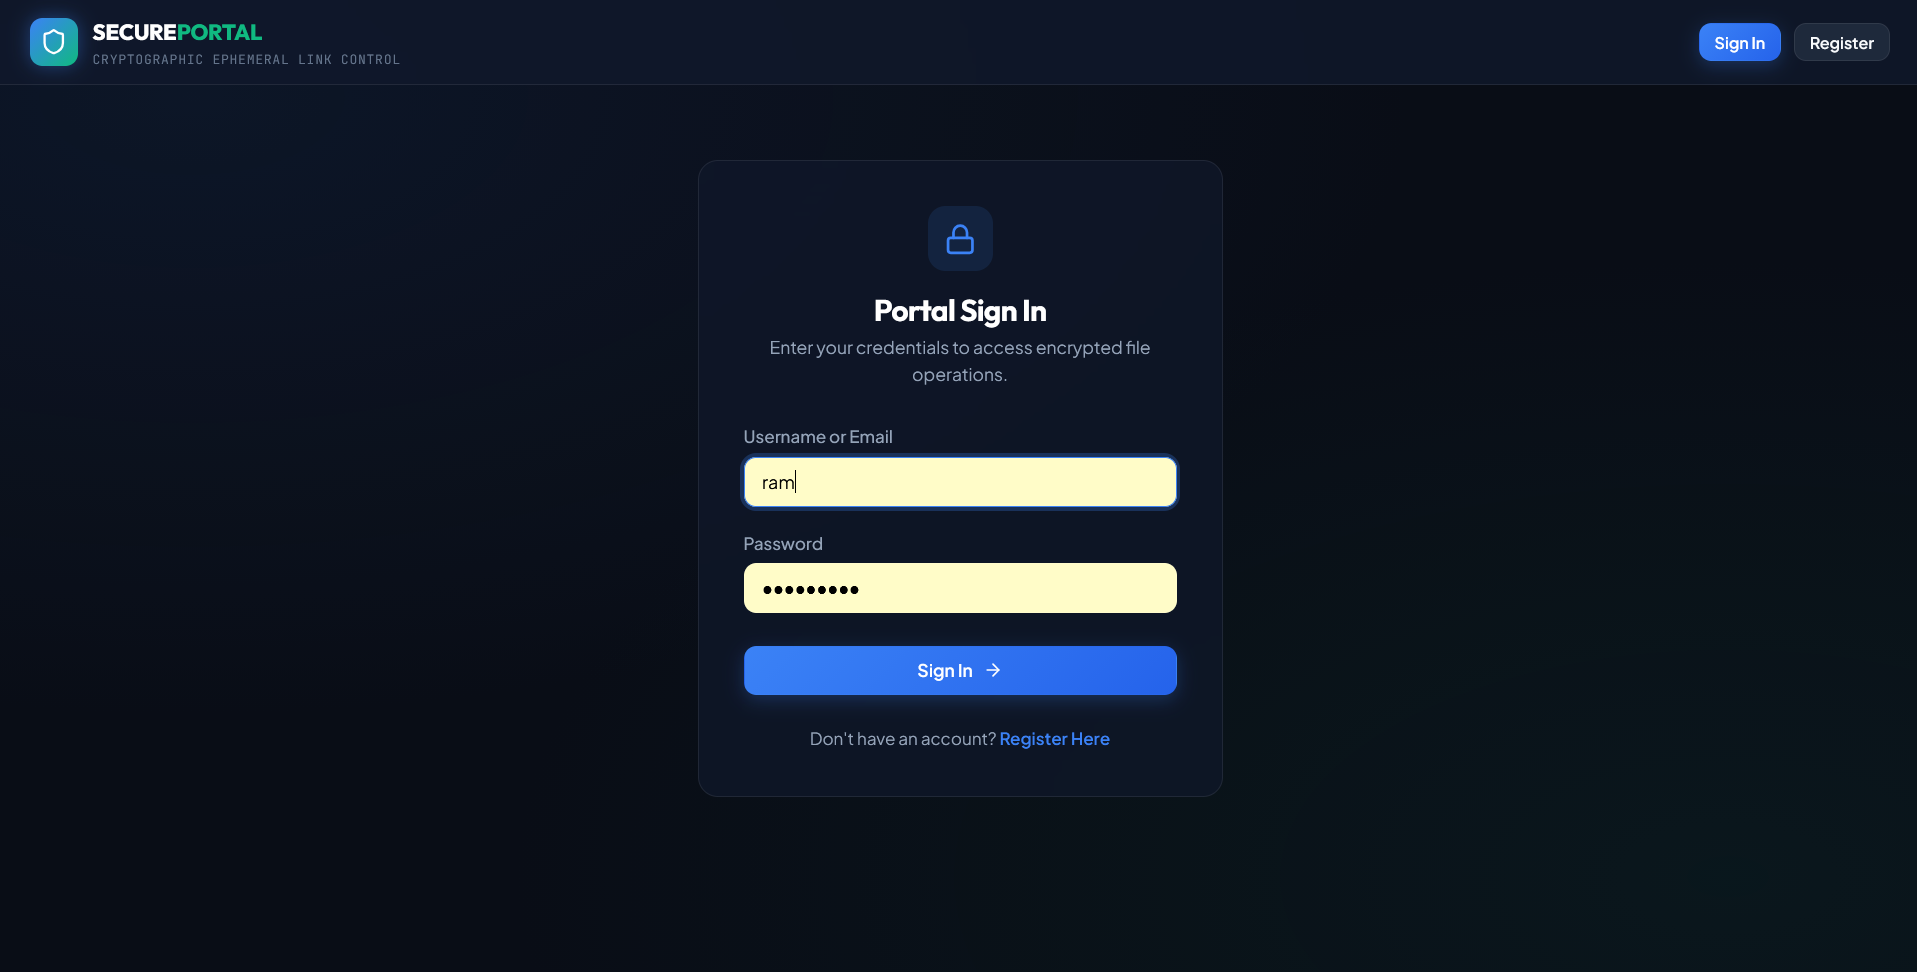
login page
-
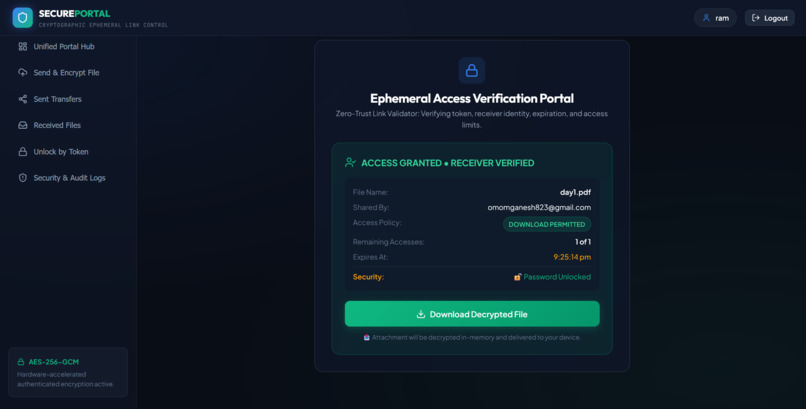
downloading the file
-
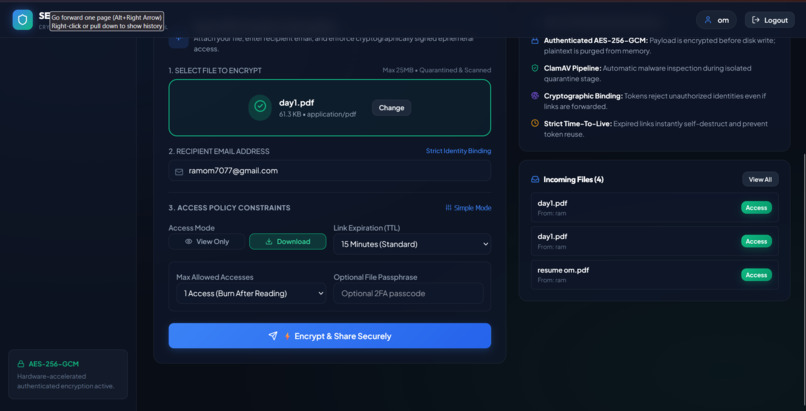
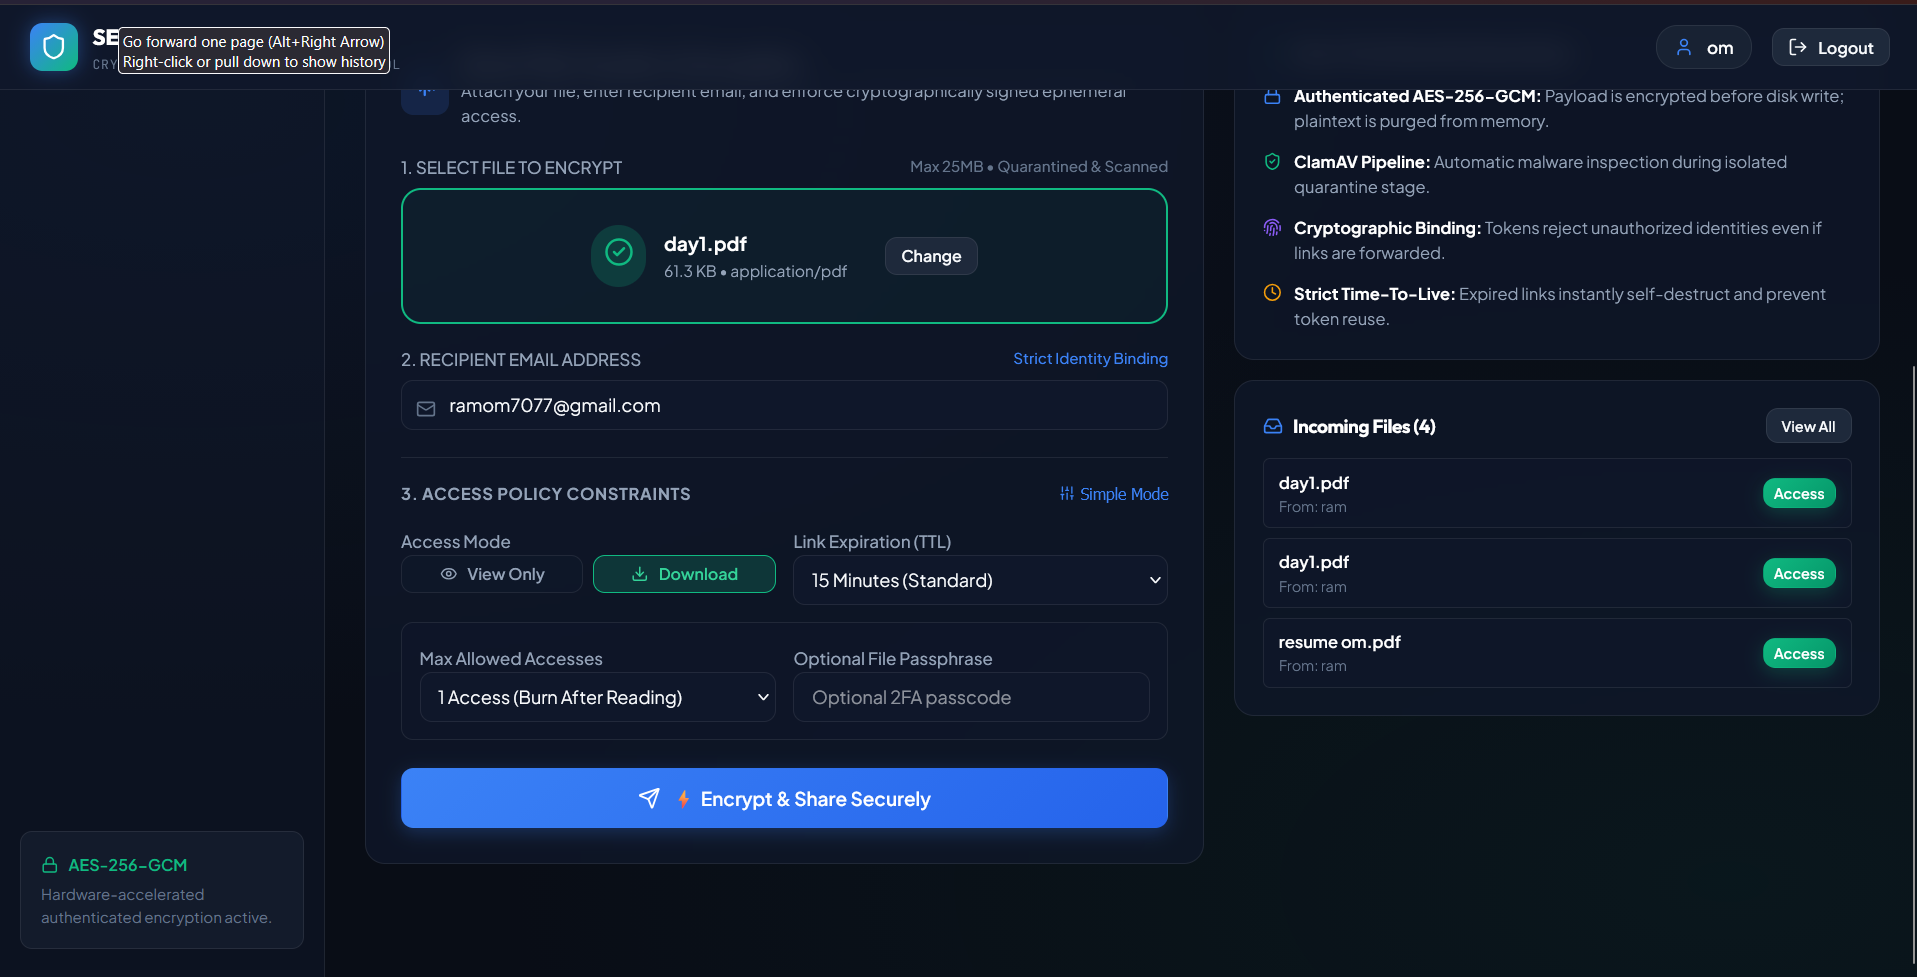
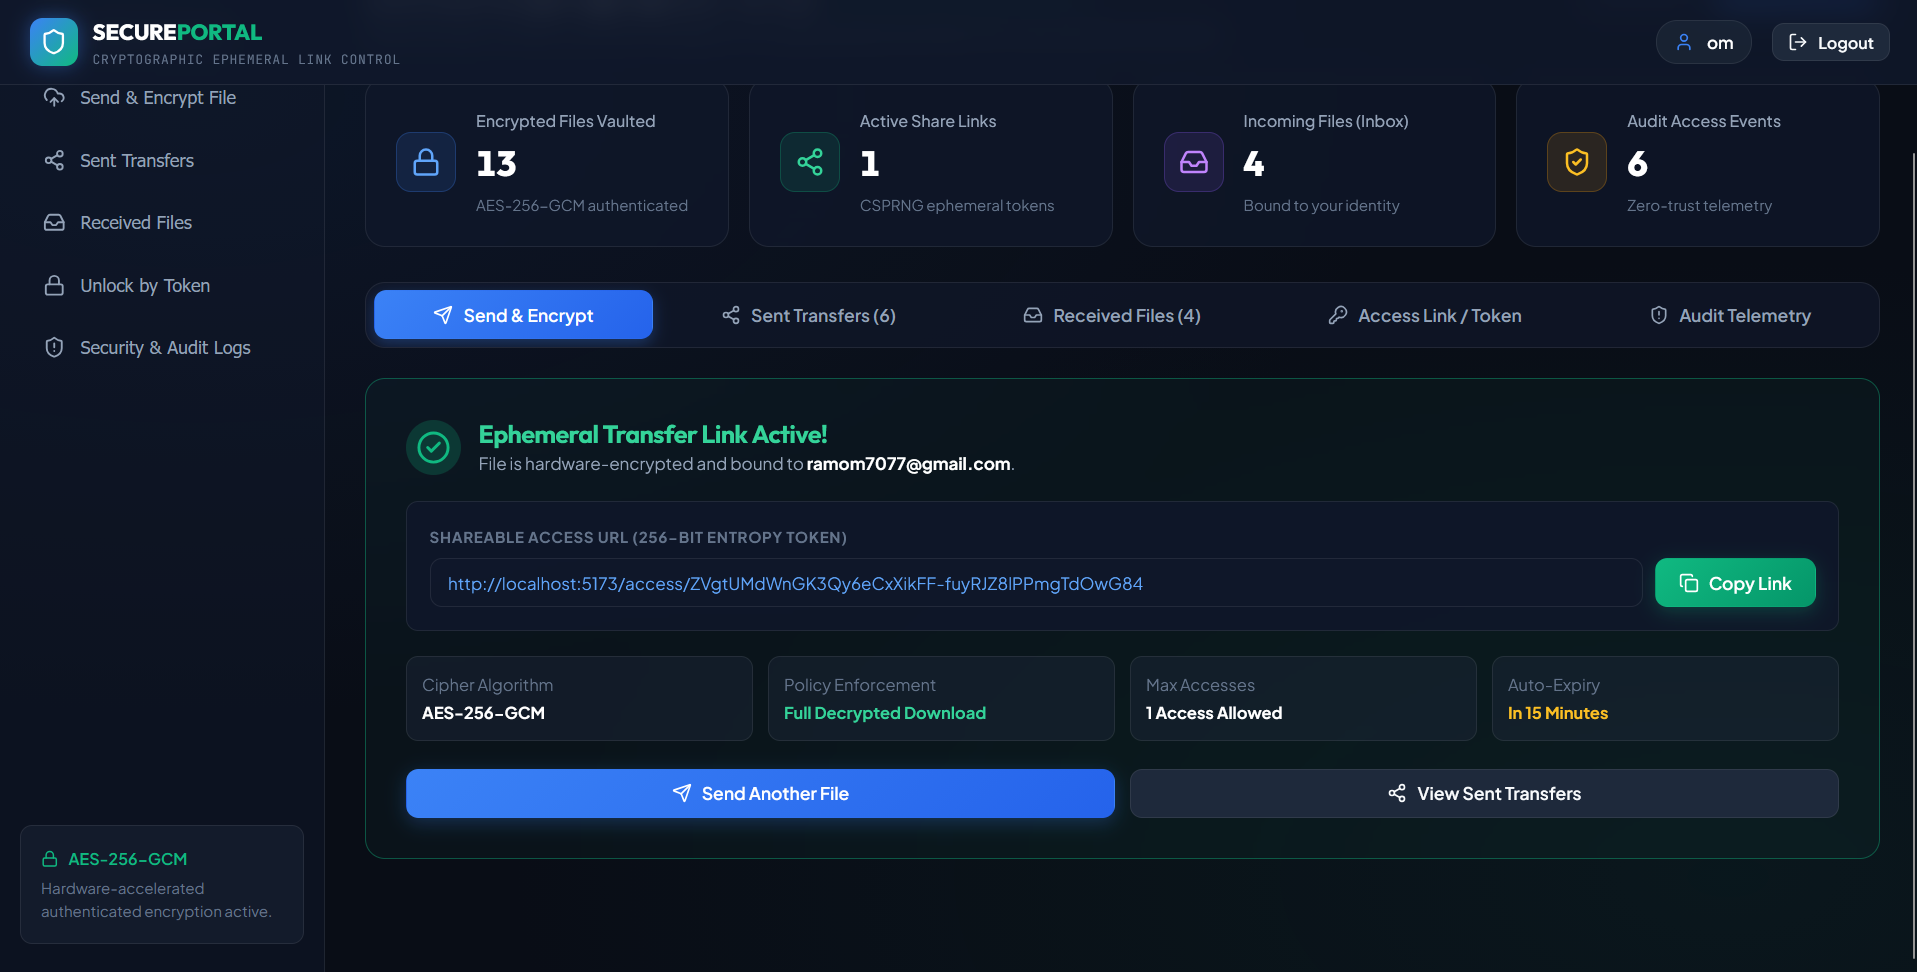
ui for uploading file
-
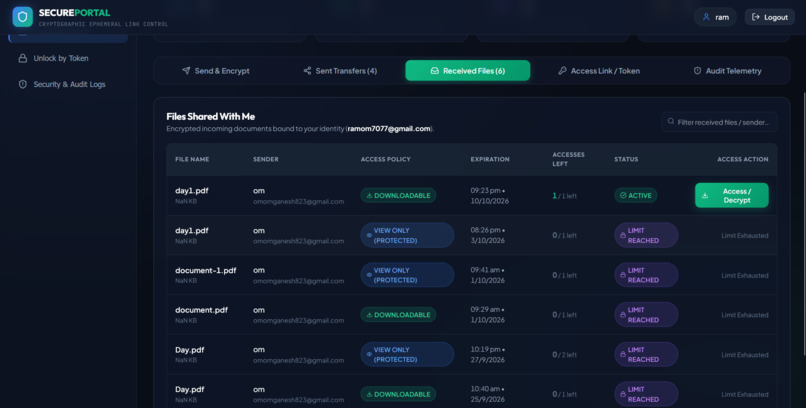
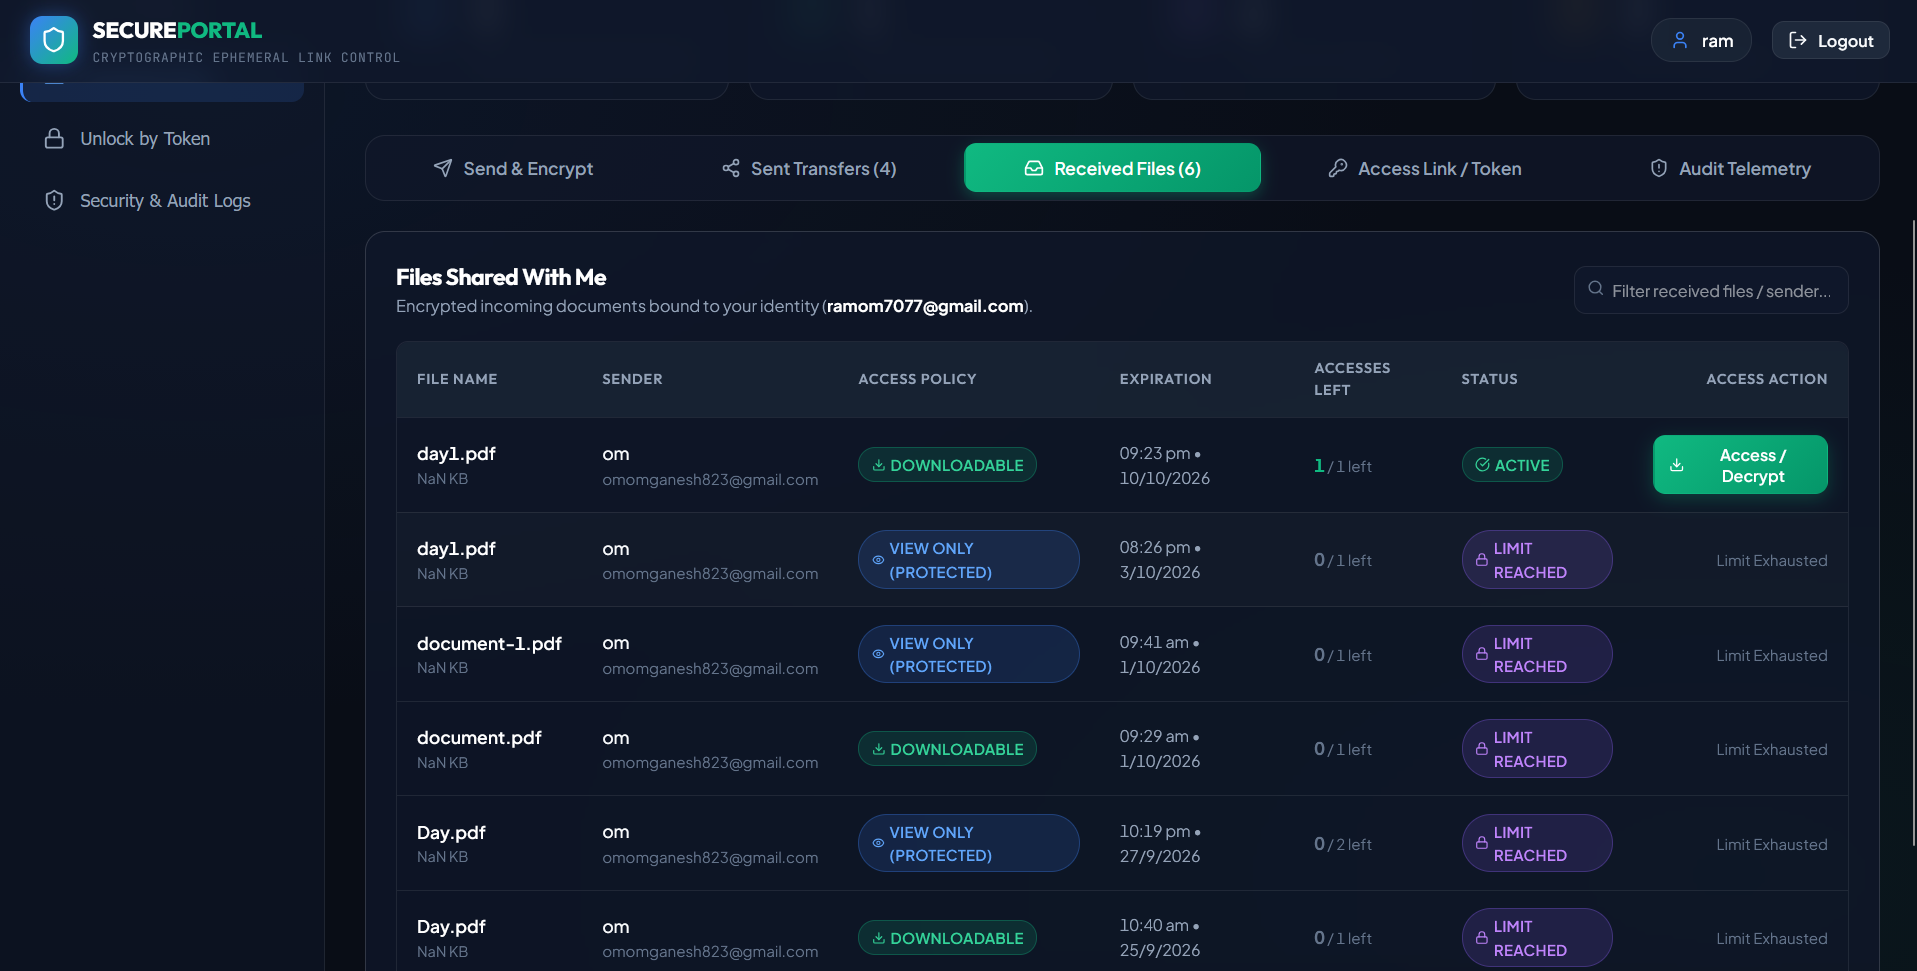
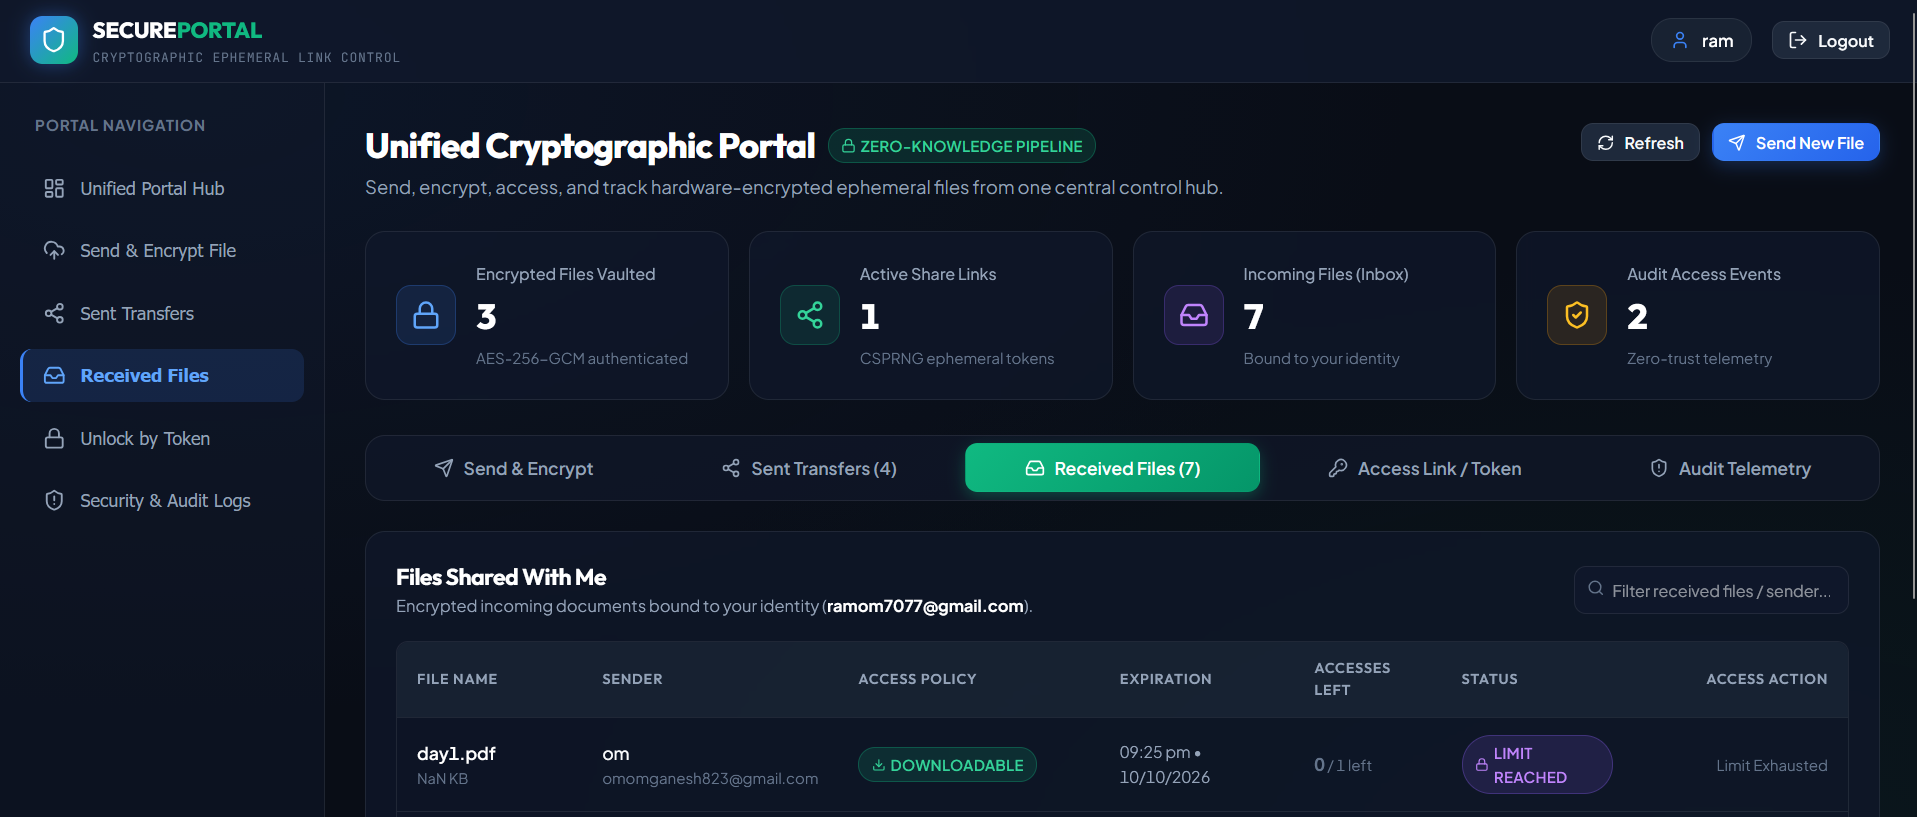
inbox for the file sent by the senders
-
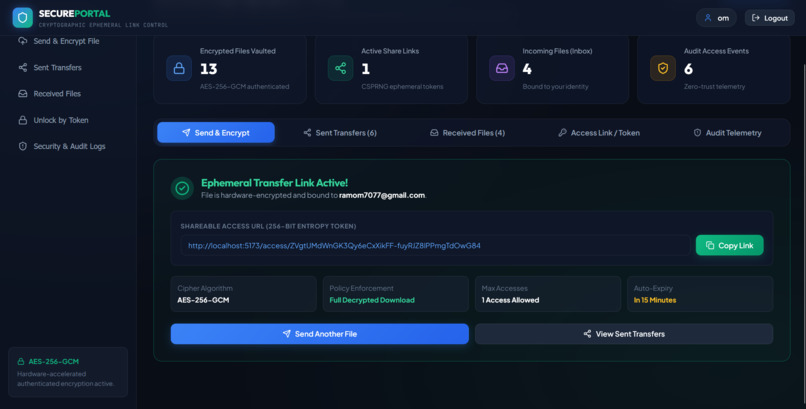
scanned and ready to send
-
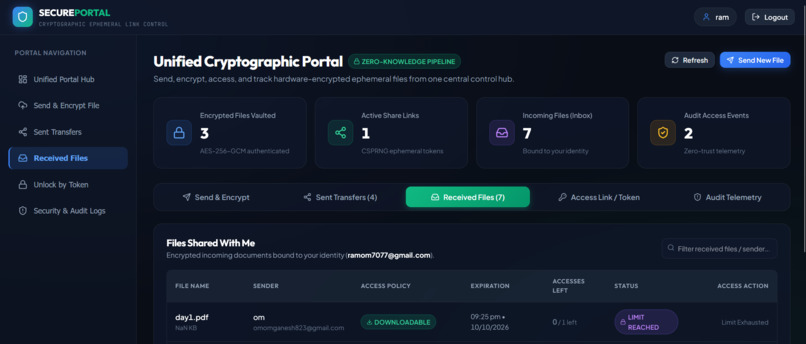
the limit will be reached
Inspiration
We share files online for college, work, and personal use, but sometimes we lose control over who can access them after sharing a link. This inspired us to build a secure file-sharing system that gives users better control over their files and helps protect sensitive information.
What it does
Secure File Exchange with Ephemeral Access Control allows users to share files securely using encryption and temporary access links. The sender can choose the intended receiver, select View Only or Download permission, set an expiry time, limit the number of accesses, and revoke access whenever needed. The system also checks receiver identity to prevent unauthorized users from accessing forwarded links. AI-based malware detection is planned to improve the identification of suspicious files.
How we built it
We designed the project as a web-based application with a frontend, backend, and database. Uploaded files are checked for possible malware before being encrypted using AES-256-GCM. The sender then sets the access permissions, and the system generates a secure temporary link. Whenever a receiver opens the link, the backend checks the receiver's identity, token validity, expiry time, access limit, and revocation status before allowing access.
Challenges we ran into
One of our main challenges was designing a system that could handle forwarded links and prevent unauthorized access. We also had to consider how to manage encryption, expiry times, access limits, and revocation together. Another important challenge was understanding the limitations of View Only access, because screenshots and copying cannot be completely prevented after a person legitimately views a file.
Accomplishments that we're proud of
We are proud of bringing important security features together in one project. The main features include file encryption, malware scanning, receiver verification, temporary links, access limits, expiry control, and manual revocation. We also designed dashboards to help users manage shared files and check their access status.
What we learned
Through this project, we learned about encryption, authentication, secure token generation, access control, and web application development. We also understood how frontend and backend components work together to protect files. Most importantly, we learned that security requires checking permissions at every important stage, not just creating a secure link.
What's next for Secure File Exchange with Ephemeral Access Control
Next, we plan to improve the project by integrating AI-based malware detection, strengthening security monitoring, and improving the user interface. We also want to test the system with different file types and access scenarios. Our long-term goal is to make file sharing safer, simpler, and more reliable while giving users greater control over who can access their files.
Built With
- aes-256-gcm
- ai
- clamav
- cryptography
- css
- cybersecurity
- django
- django-rest-framework
- github
- html
- javascript
- machine-learning
- postgresql
- python
- react
- rest-api

Log in or sign up for Devpost to join the conversation.