-
-
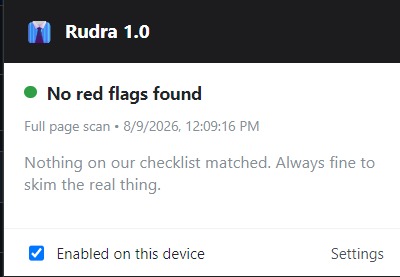
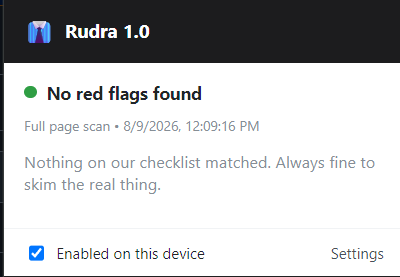
window when opened and no flags are found
-
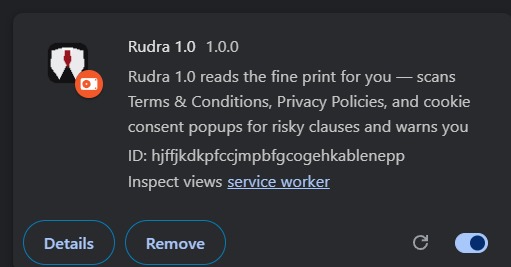
the main extenstion
-
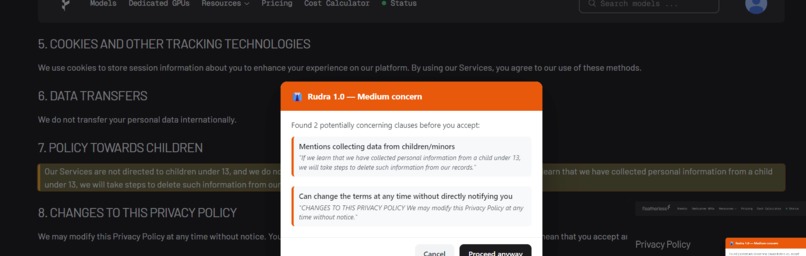
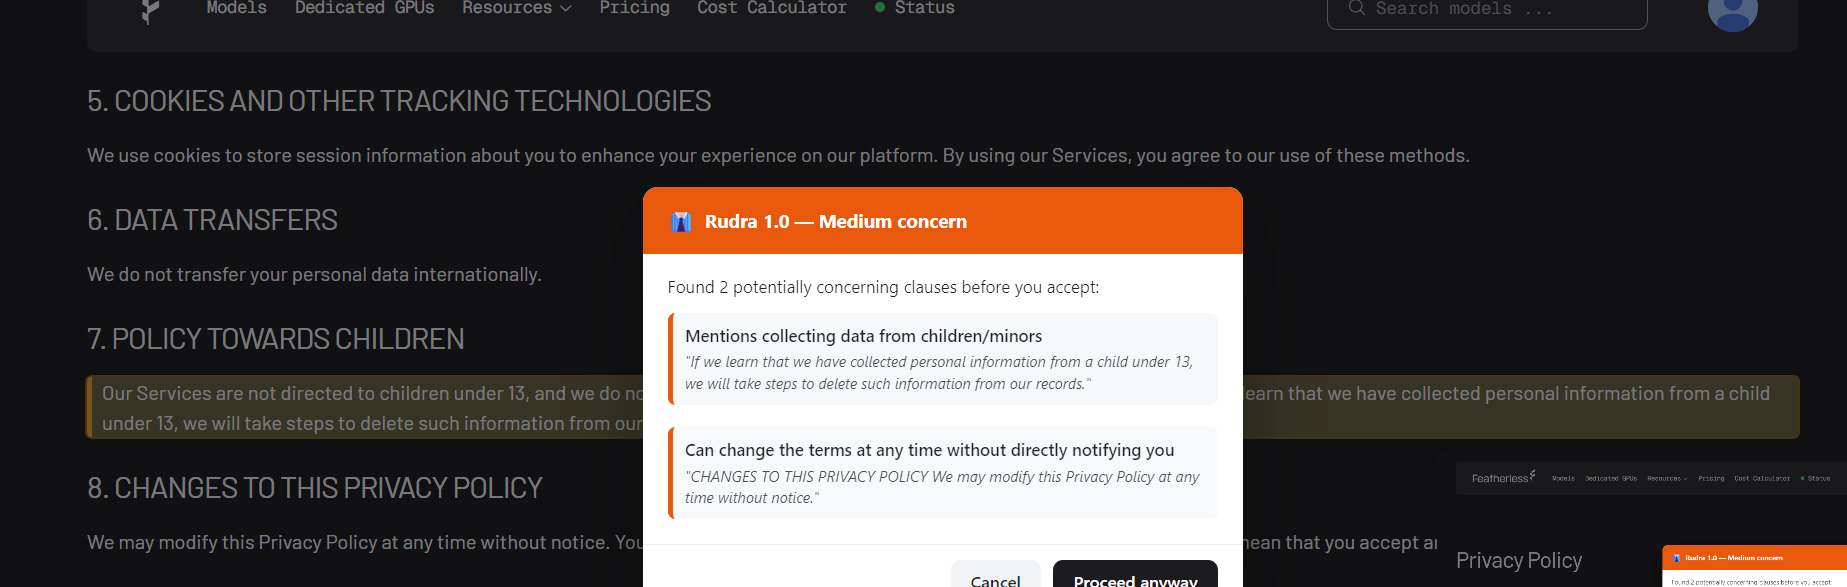
it highlights the part where the bad terms are written
-
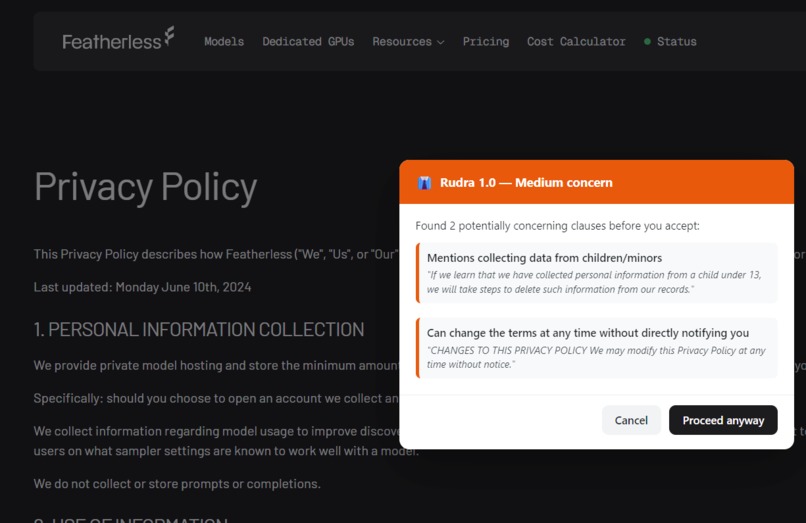
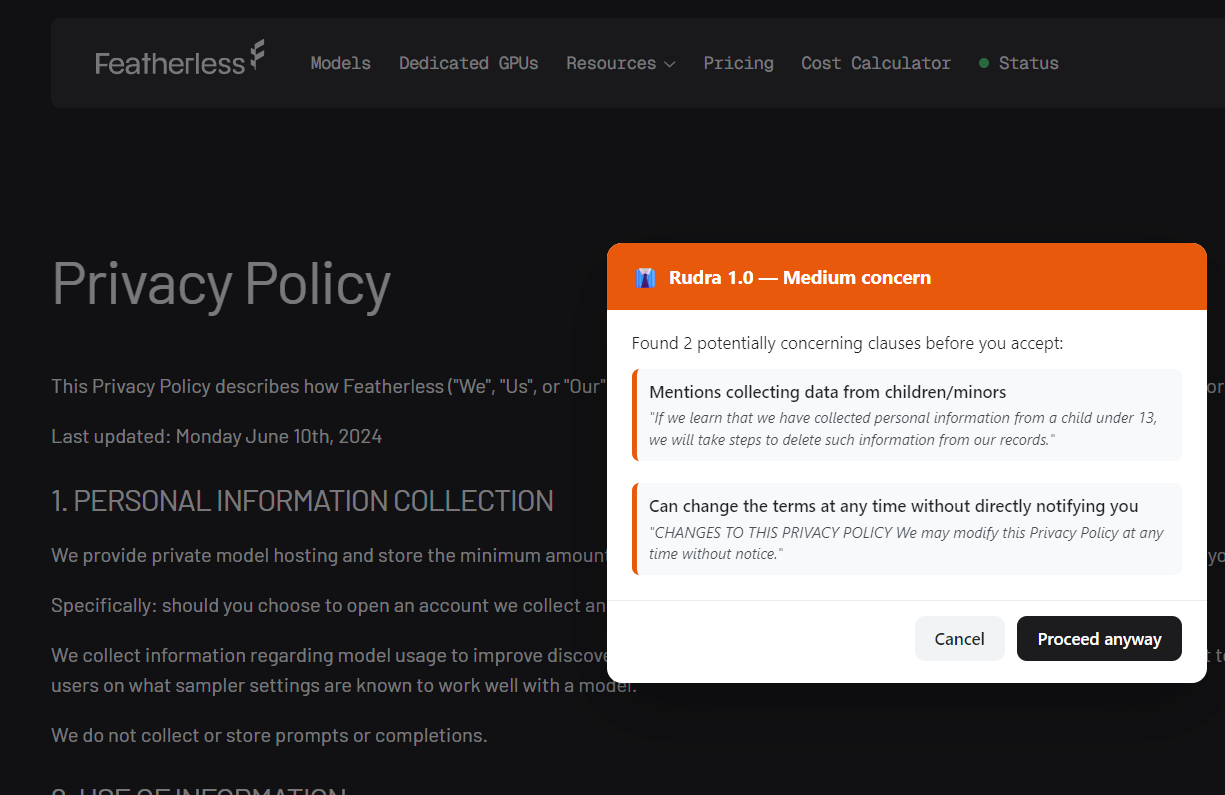
lists the bad terms
-
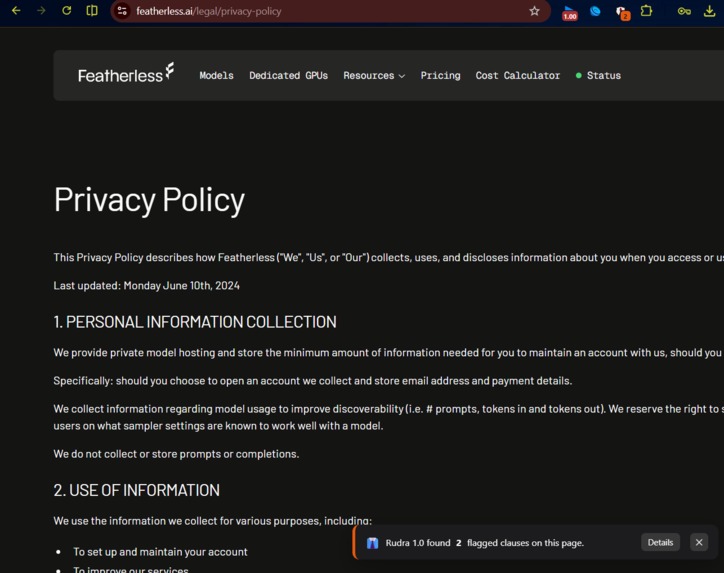
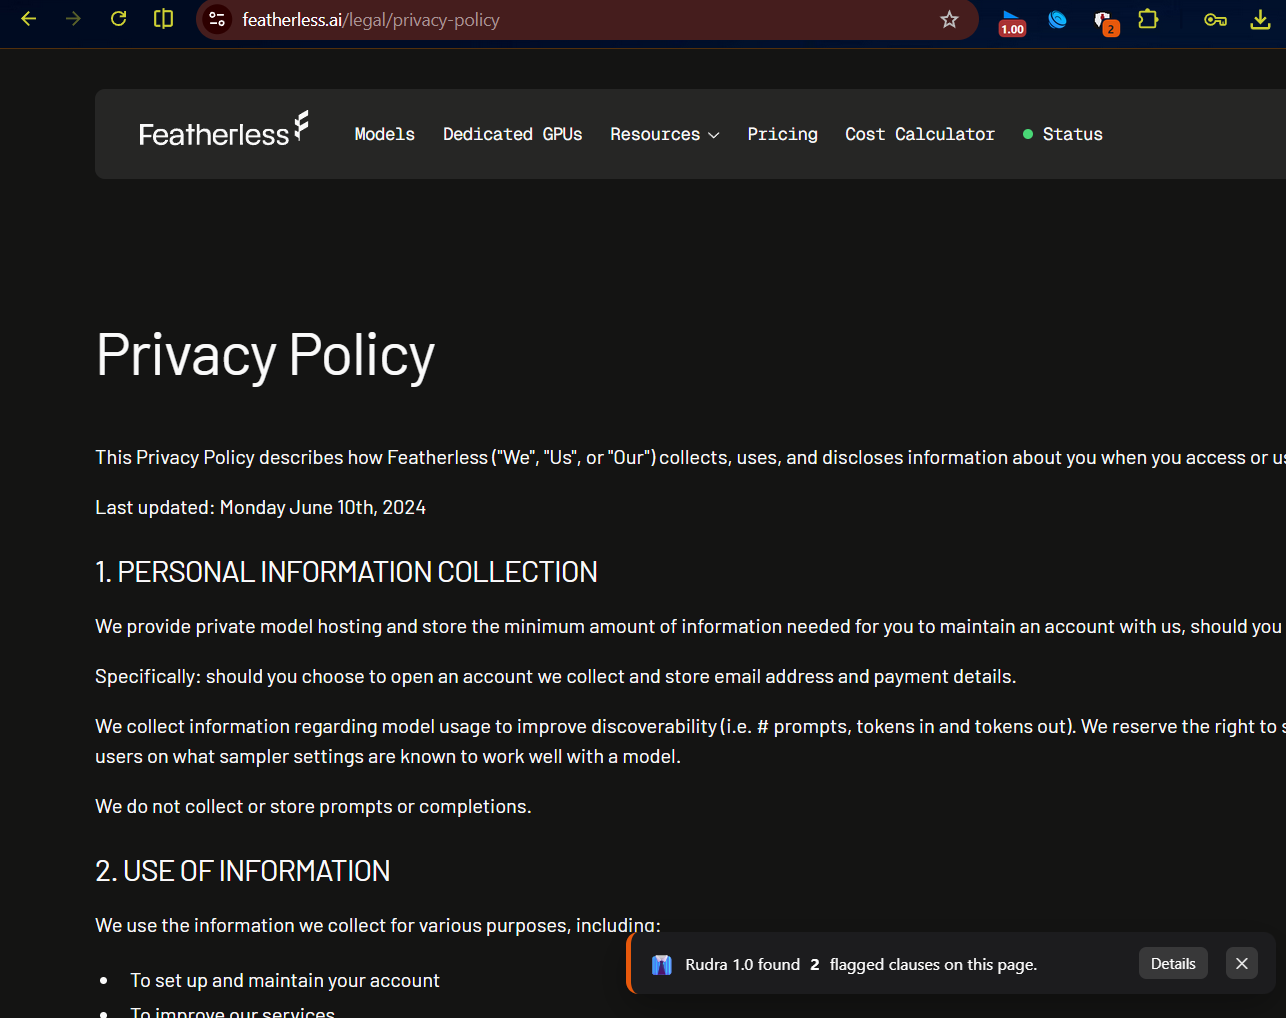
it shows as a pop up at the bottom
Inspiration Nobody has time to read 50-page privacy policies, so we blindly click "I Agree" and sign away our data. We wanted to build a tool that reads the fine print and warns you before you click.
What it does Rudra 1.0 is a Chrome extension that intercepts clicks on cookie "Accept" buttons and scans the page for red flags. It uses Featherless AI to give you a 1-10 risk score and a plain-English summary of what you're actually agreeing to.
How we built it We built a local regex engine in Vanilla JavaScript (Manifest V3) to instantly find risky clauses without sacrificing privacy. We then integrated the Featherless AI API (Qwen 2.5 model) to turn those raw clauses into a human-readable risk score and summary.
Challenges we ran into Highlighting text on the page was difficult because websites structure their HTML very differently, requiring a custom DOM traversal strategy. We also had to carefully tune the Featherless AI prompt to ensure it consistently returned perfectly formatted JSON.
Accomplishments that we're proud of We successfully combined fast local regex scanning with the Featherless AI API to create a tool that is both instant and highly intelligent. The UX of intercepting a cookie consent click just in time feels incredibly satisfying and protective.
What we learned We got a deep dive into modern Chrome Extension architecture, specifically Manifest V3 service workers and cross-script messaging. We also learned how to effectively use the Featherless AI API for structured data extraction.
What's next for Rudra 1.0 We plan to add a per-site allowlist and expand our local regex library to catch more subtle legal loopholes. Eventually, we want to publish it to the Chrome Web Store and use AI to summarize the entire policy rather than just flagged clauses.


Log in or sign up for Devpost to join the conversation.