-
-
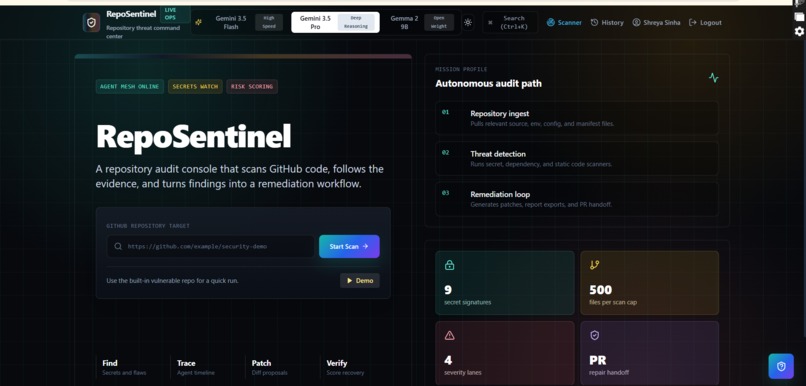
front
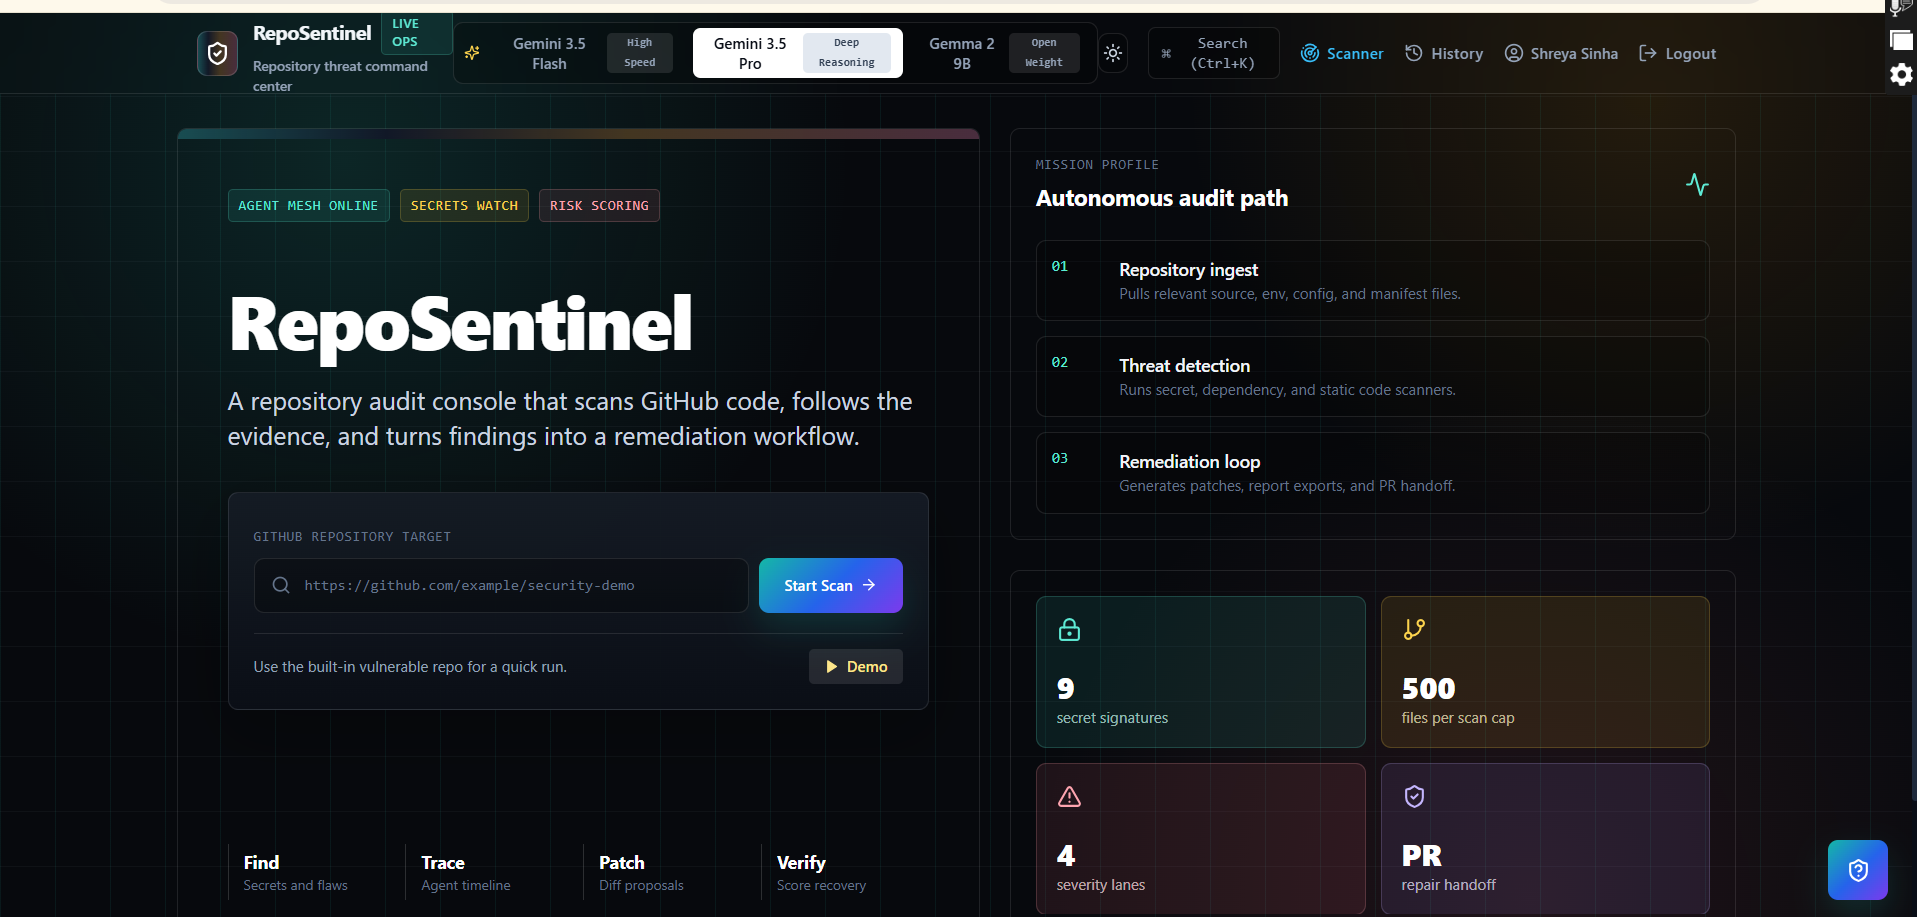
Inspiration
Modern software engineering teams work quickly. Checking for security issues is still a slow and hard task. Secret codes that are written directly into the code dangers, from database queries and old parts of the code that are not safe can accidentally get into the live software. Most security chatbots just give advice—they don't do the more complex steps needed to fix problems. We created RepoSentinel to change how security checks are done. It makes the process automatic. Lets the system fix problems on its own without needing help.
What it does
RepoSentinel is an AI security engineer that works beyond simple chat loops using a five‑step agentic pipeline:
FIND: RepoSentinel scans source code and dependency lists for hidden secrets such as AWS keys GitHub tokens, JWTs and database connection strings. RepoSentinel also looks for AST security problems, like SQL injection, unsafe
eval()and path traversal.INVESTIGATE: RepoSentinel uses Google Gemini 3.5 to examine redacted code snippets and judge the threat level and surrounding context.
FIX: RepoSentinel creates code patches and shows unified side‑by‑side git diffs.
HUMAN APPROVAL: RepoSentinel requires developer approval before making GitHub branches or opening Pull Requests.
VERIFY: RepoSentinel runs the automated security scanners again after fixes and checks that the score has improved for example from 42 to 100 out of 100.
How we built it
Multi-Agent Architecture: Created with sub-agents: SupervisorAgent, SecretDetectionAgent, CodeSecurityAgent, DependencyAgent, RiskAnalysisAgent, RemediationAgent and VerificationAgent.
AI Engine: Google Gemini 3.5 API (gemini-3.5-flash) for identifying threats and creating patches with Google Gemma model fallback (gemma-2-9b-it).
Frontend Dashboard: React.js, Vite, Tailwind CSS Lucide Icons and Axios.
Backend API: Node.js, Express.js and Google Generative AI SDK (@google/generative-ai).
Integration: GitHub REST API, for creating branches and Pull Requests.
Challenges we ran into
One must perform secret redaction before sending code snippets to AI endpoints. Full secret redaction guarantees zero-leakage security. At the time one must keep line numbers precise and keep git diff accuracy intact. All of this must work across -file repositories.
Accomplishments that we're proud of
I am building a functional full-stack application. This application runs the FIND → INVESTIGATE → FIX → VERIFY` security pipeline automatically in just a few seconds. The security pipeline also provides real-time telemetry and verifies the score as it works.
What we learned
How to separate the tasks of agents in a clear way handle changes, in the state when agents work in the background and use Gemini 3.5 to help with rewriting code automatically.
What's next for RepoSentinel – Autonomous AI Security Engineer
Built With
- ai-agents
- cybersecurity
- express.js
- gemini-3-5
- github-api
- google-gemini
- javascript
- node.js
- react
- tailwind-css
- vite

Log in or sign up for Devpost to join the conversation.