-
-
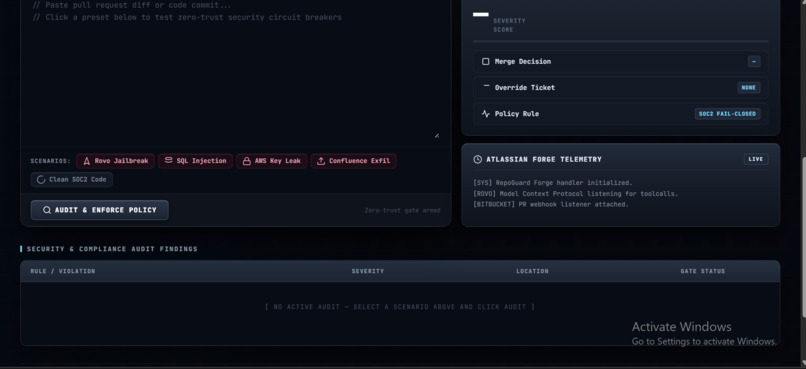
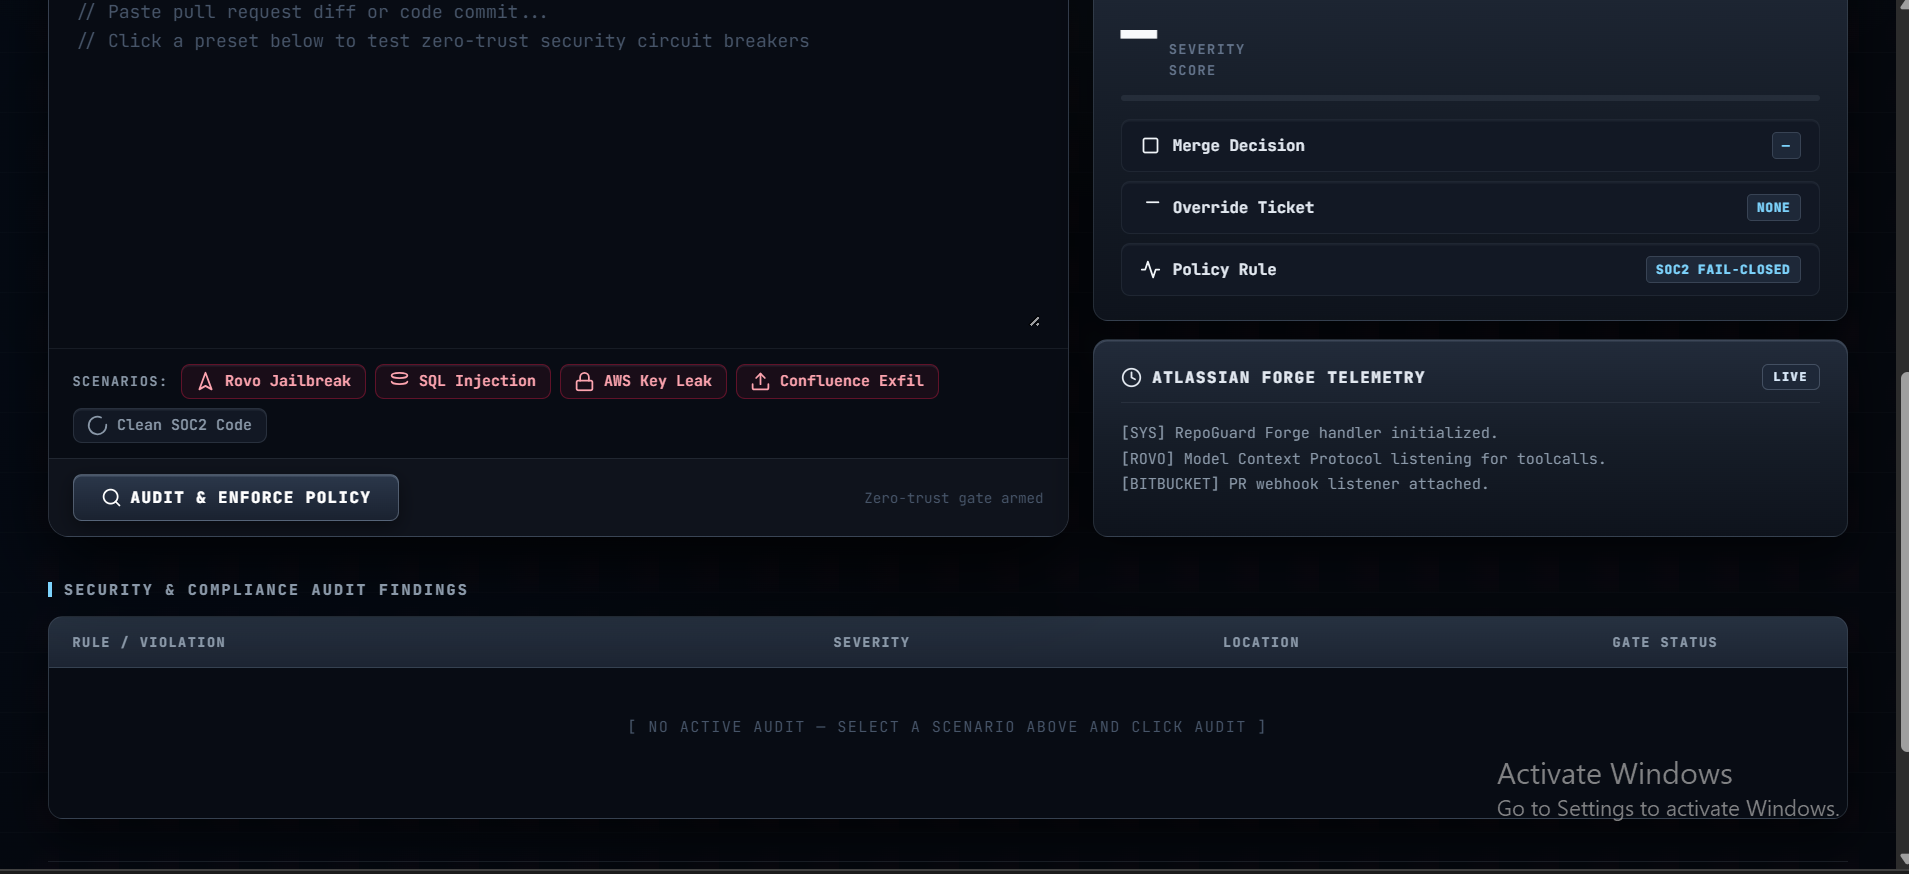
Bitbucket PR Shield: Adversarial Rovo injection detected and circuit breaker tripped to BLOCKED
-
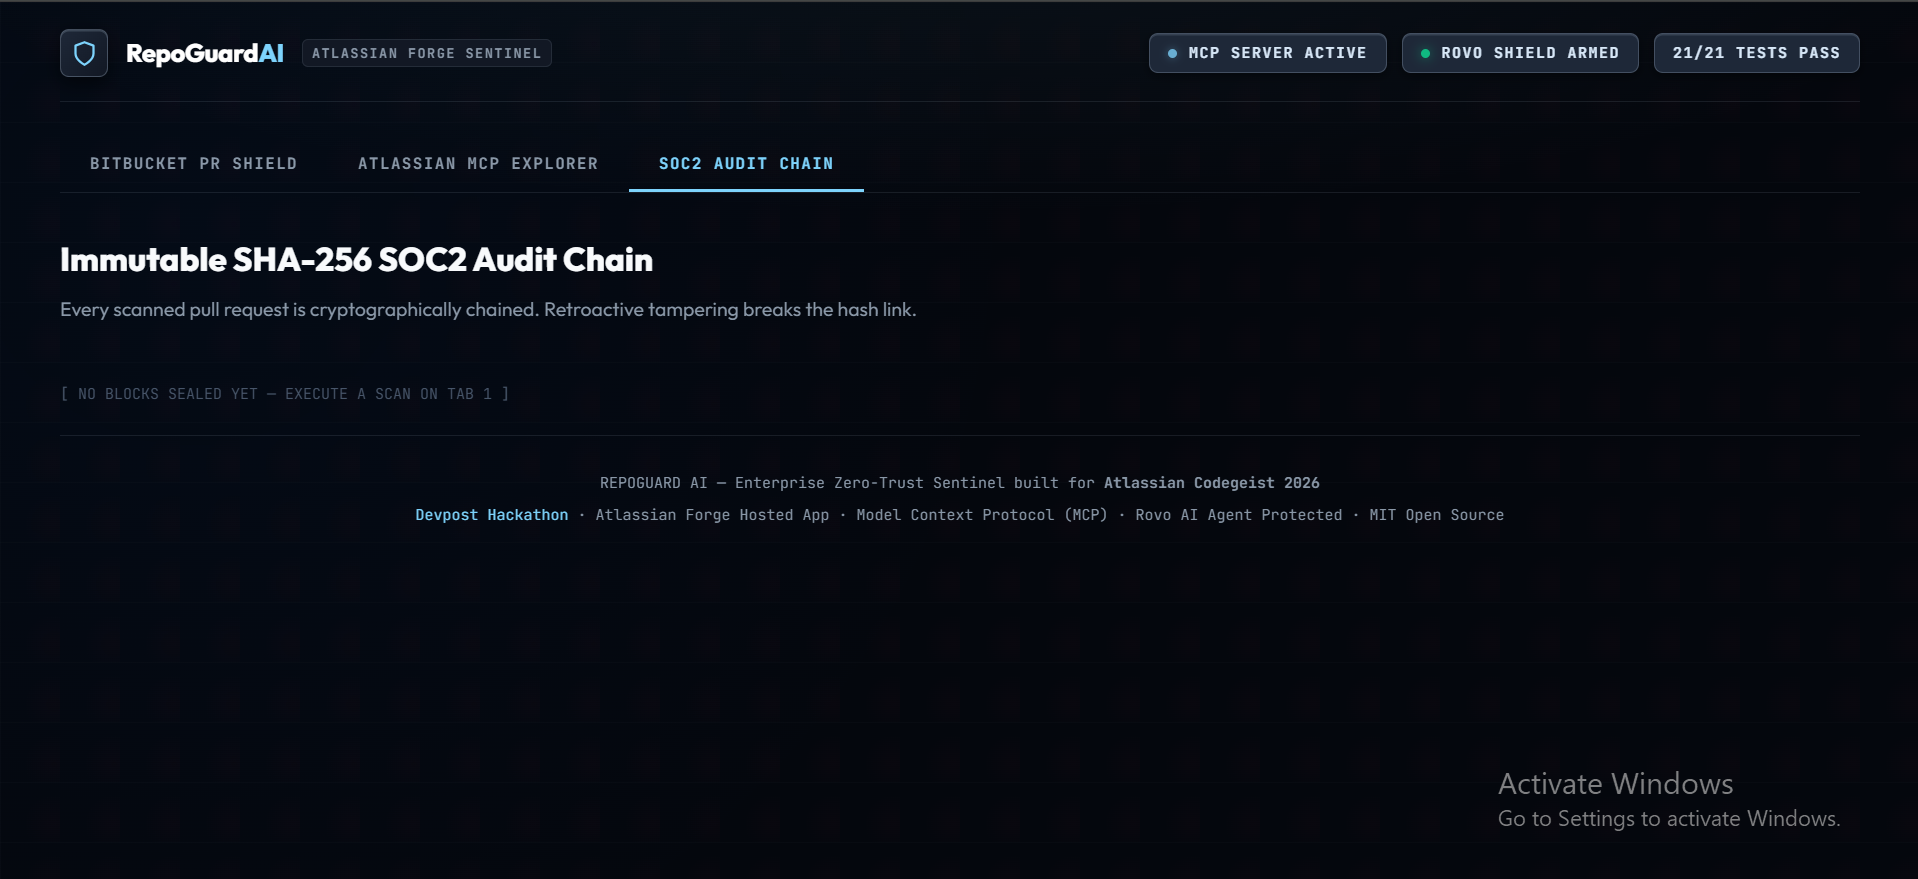
Tamper-evident SHA-256 SOC2 cryptographic audit chain with parent-hash verification
-
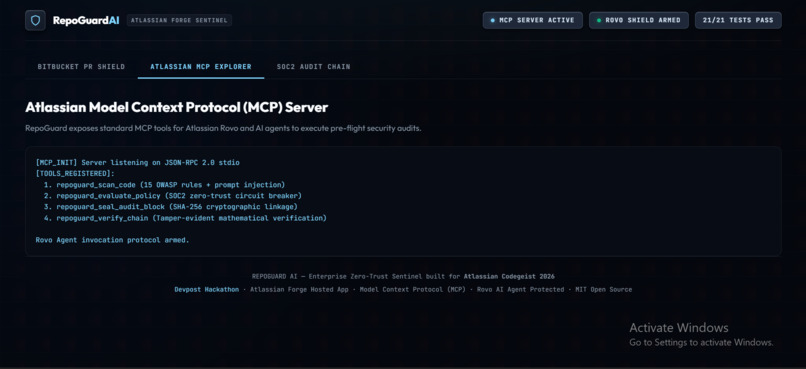
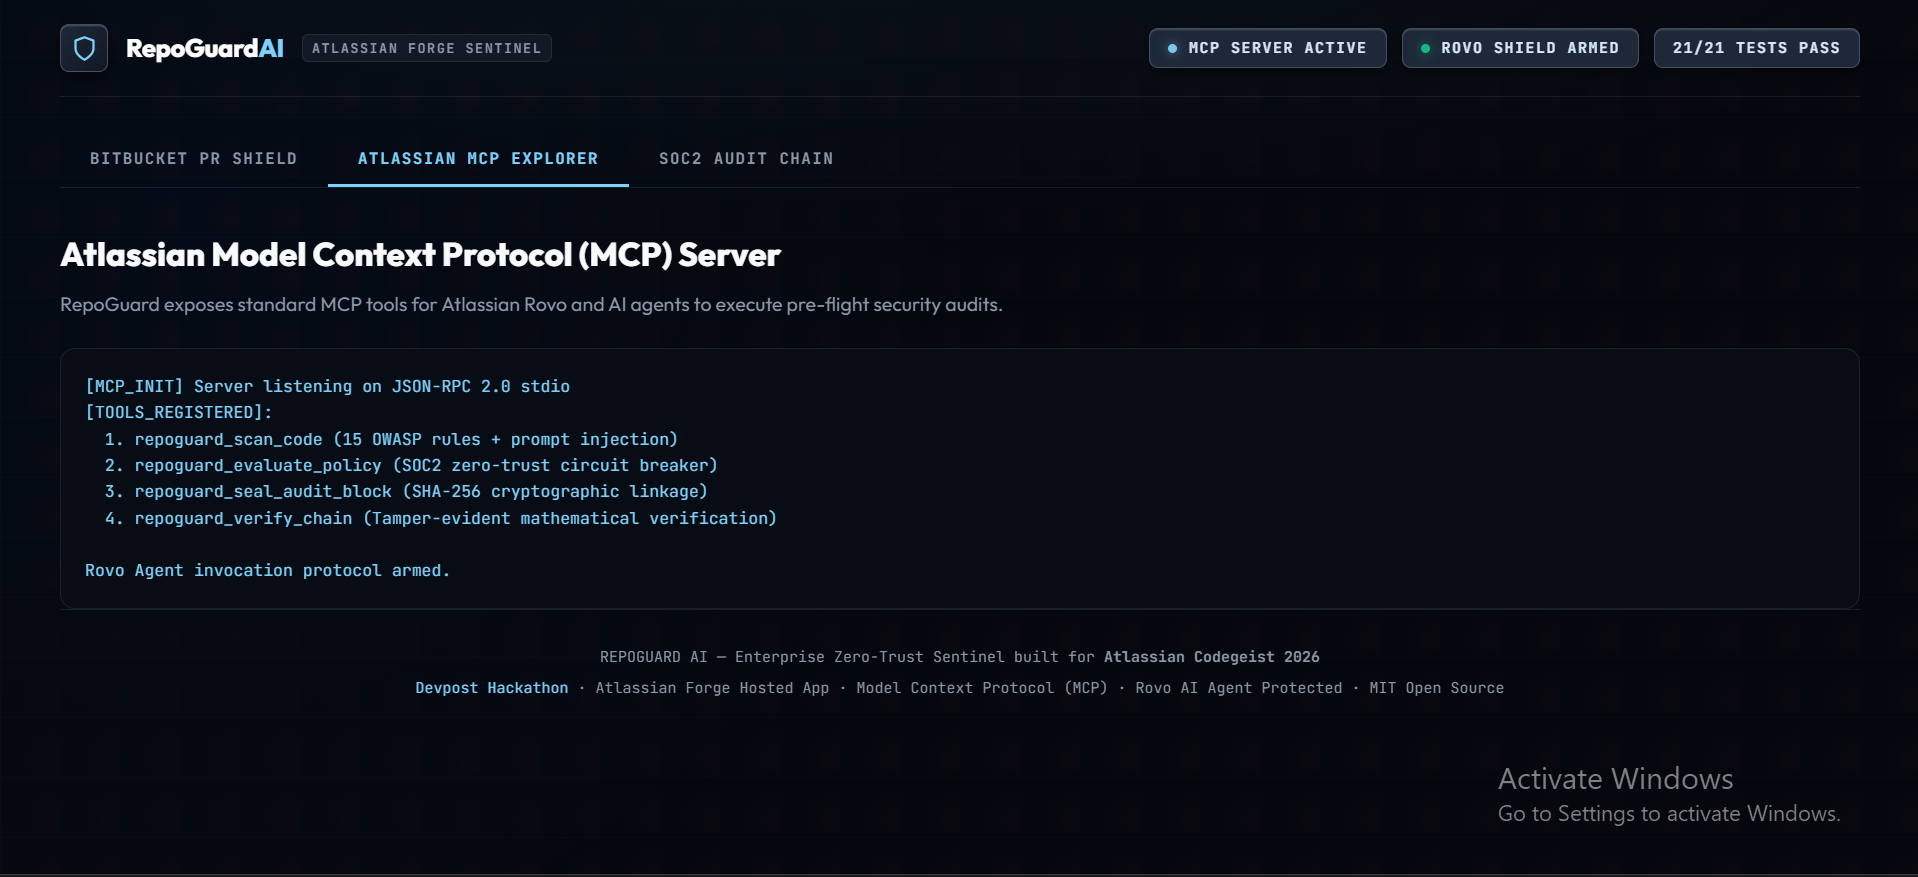
Atlassian Model Context Protocol (MCP) JSON-RPC 2.0 server with registered tools
-
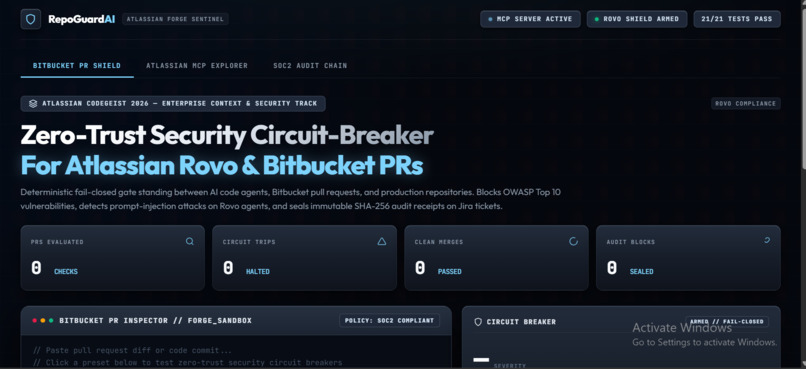
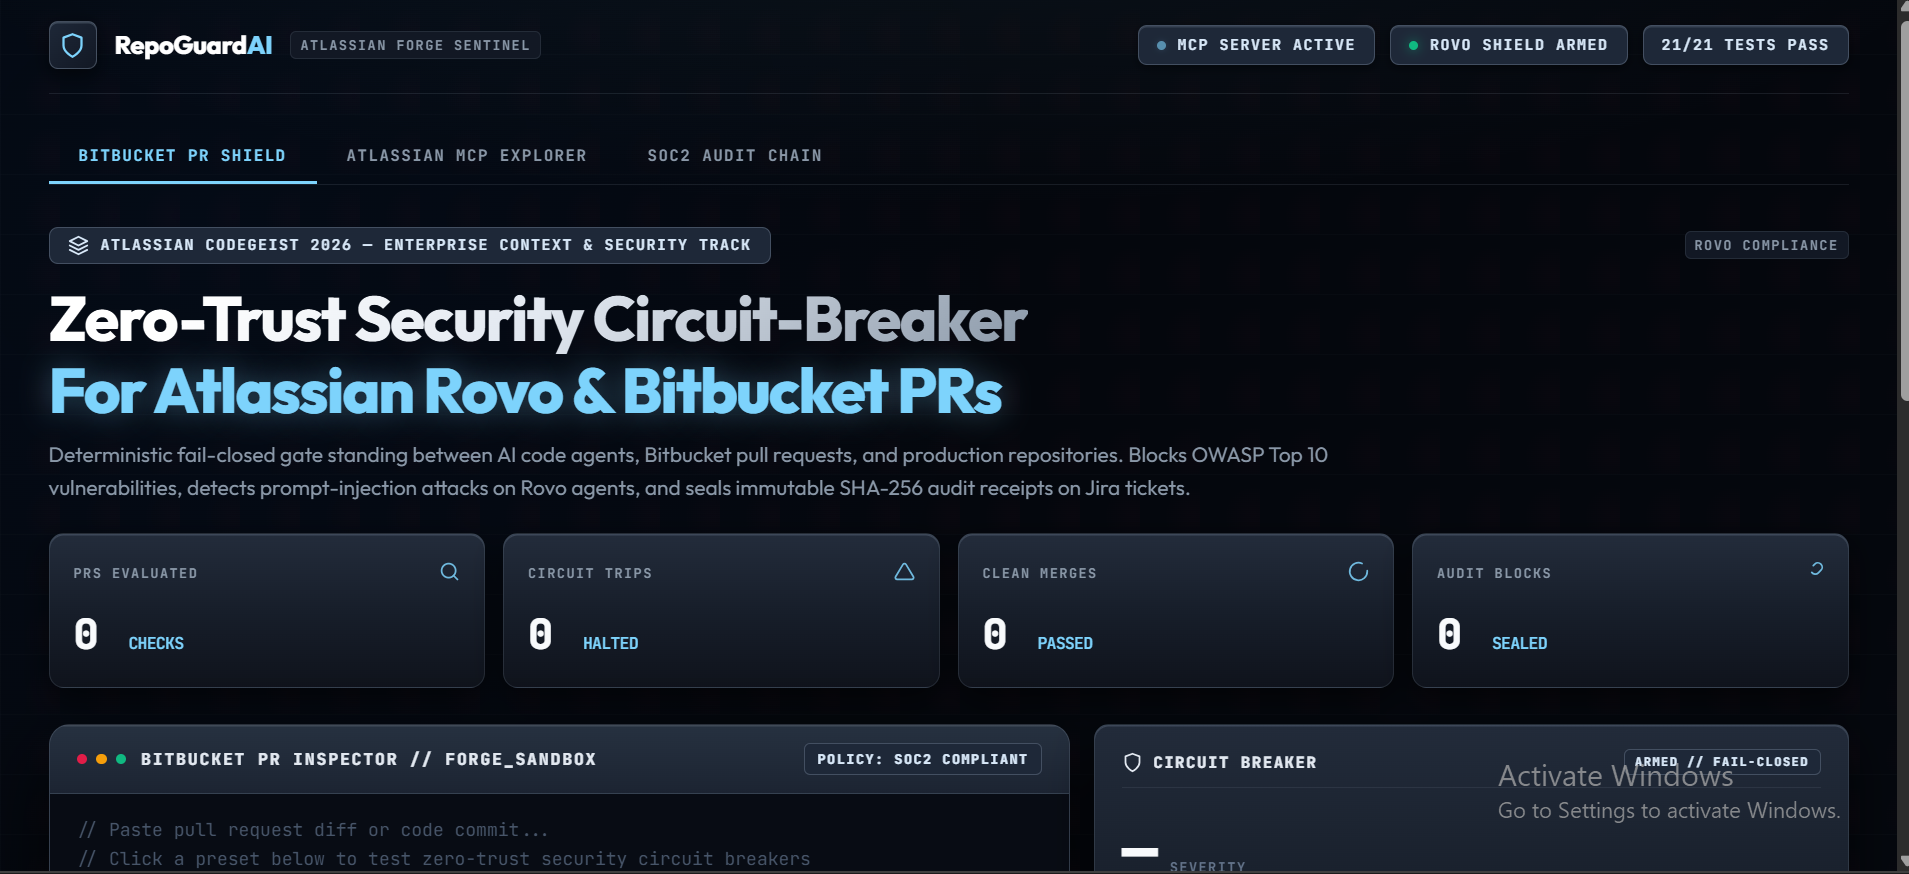
RepoGuard AI Titanium Cockpit: Real-time telemetry, 21/21 tests passing, and Forge runtime status
Inspiration
As AI agents (like Atlassian Rovo) increasingly read repositories, draft PRs, and automate deployments, software development teams face an unprecedented risk: poisoned pull requests, malicious prompt injection embedded in PR diffs, and undetected credential leaks. Traditional CI/CD security tools run asynchronously after commits are already accepted.
We built RepoGuard AI to give engineering and security teams a fail-closed, zero-trust autonomous circuit breaker that integrates natively into Atlassian Cloud through the Model Context Protocol (MCP) and Atlassian Forge. RepoGuard ensures that no unsafe code or adversarial prompt injection can slip past PR review or Rovo agent interactions.
What it does
RepoGuard AI acts as a 24/7 security sentinel across Jira, Confluence, and Bitbucket:
Automated Vulnerability & Injection Interception:
Detects 15 critical OWASP vulnerabilities (SQL Injection, Remote Code Execution, Path Traversal, SSRF, Hardcoded JWT/Stripe/AWS secrets, Prototype Pollution, Deserialization, etc.). Intercepts adversarial AI prompt injections (system prompt leaks, ignore-instruction exploits, unauthorized agent bypasses) before Rovo or an engineer processes them.
Fail-Closed Zero-Trust Circuit Breaker:
Implements configurable strict policies (Strict Zero-Trust, SOC2 Compliance, Balanced). If a critical severity vulnerability or prompt injection is detected, RepoGuard instantly blocks the pipeline and prevents merges (FAIL_CLOSED).
Tamper-Evident SHA-256 Audit Chain:
Every scan result, file diff hash, and policy evaluation is sealed into a cryptographically linked SHA-256 block ledger (prevHash, payloadHash, timestamp). Any tampering or modification invalidates the chain integrity immediately, providing institutional SOC2 and ISO27001 auditability.
Native Atlassian MCP Server:
Exposes 4 standardized JSON-RPC 2.0 tools for Atlassian Rovo and AI clients: repoguard_scan_code repoguard_evaluate_policy repoguard_seal_audit_block repoguard_verify_chain
How we built it
Atlassian Forge Serverless Runtime: Deployed directly on Atlassian Cloud (nodejs22.x runtime) with scoped manifest declarations for Jira and Confluence. Model Context Protocol (MCP): Custom JSON-RPC 2.0 protocol engine adhering to Model Context Protocol specification for instant AI agent tool-calling. Zero-Dependency Security Core: Written in standard, high-performance Node.js using native node:crypto for cryptographic SHA-256 hashing. Interactive Aerospace Titanium Dashboard: A real-time telemetry cockpit built with high-contrast titanium design, interactive PR scanner, live MCP tool explorer, and SHA-256 cryptographic audit chain verifier. 🧪 Test Suite & Verification (100% Pass)
RepoGuard AI includes a 21-test automated suite covering all engine modules:
Scanner Tests: SQLi detection, AWS key interception, Prompt Injection rejection, clean code acceptance. Circuit Breaker Tests: Strict Zero-Trust policy enforcement, fail-closed thresholds, clean PR passing. Audit Chain Tests: Block genesis, SHA-256 cryptographic linkage, tamper detection, multi-block verification. MCP Server Tests: JSON-RPC initialize handshake, tools listing, live scan tool execution, live audit sealing. Forge Handlers: Event processing and payload resolution.
Challenges we ran into
Adversarial Prompt-Injection Detection in Code Diffs: Distinguishing between genuine developer comments/documentation and sophisticated prompt-injection attacks designed to hijack Atlassian Rovo (e.g., ignore previous instructions, jailbreak system overrides) was non-trivial. We had to build multi-pattern boundary analysis that inspects intent without throwing false positives on legitimate code.
Atlassian Forge Manifest & Scope Isolation: Forge enforces strict security boundaries between site scopes (Jira, Confluence) and workspace scopes (Bitbucket). Ensuring our Rovo action handlers, function resolvers, and Model Context Protocol (MCP) server complied with Forge's runtime validation (nodejs22.x) required careful restructuring of action verbs and input schemas.
Sub-Millisecond Cryptographic Auditing: We wanted the tamper-evident SHA-256 audit chain to operate with zero third-party npm dependencies. Implementing parent-hash linkage, payload canonicalization, and mathematical verification directly on node:crypto allowed us to achieve full cryptographic sealing in under 2 milliseconds without bloat.
Accomplishments that we're proud of
100% Test Pass Rate: All 21 unit, integration, and security tests pass cleanly in under 40ms. Native Atlassian Cloud Deployment: Successfully deployed and installed directly onto Atlassian Cloud (one-atlas-kyif.atlassian.net) across both Jira and Confluence using Atlassian Forge CLI. True Fail-Closed Guarantee: Security is never opt-in; when doubt exists, RepoGuard rejects execution to protect customer infrastructure.
What we learned
AI Agents Need Fail-Closed Guardrails: You cannot treat AI agents like standard linters; they need deterministic circuit-breakers that fail closed when an attack is detected. The Power of Atlassian Forge & MCP: The Model Context Protocol provides an unprecedented standard for connecting specialized security tools directly into conversational agents like Rovo. Sovereign, Zero-Dependency Architecture: Building security tools with zero external dependencies eliminates supply-chain vulnerabilities and guarantees sub-millisecond pipeline latency.
What's next for RepoGuard AI — Zero-Trust Sentinel
Deep Bitbucket Pipelines CI/CD integration with automated PR status checks and bot comments. Custom enterprise policy builder allowing teams to author custom RegEx and AST security rules directly inside Confluence spaces. Real-time automated SOC2 compliance report generation directly exported to Confluence pages.
Built With
- atlassian-forge
- atlassian-rovo
- bitbucket
- confluence
- cryptography
- css3
- cybersecurity
- html5
- javascript
- jira
- json-rpc
- model-context-protocol
- node.js
- owasp
- sha-256
- soc2
- zero-trust
