Inspiration
AI coding agents can generate changes quickly, but who verifies their conclusions before those changes move toward production?
A successful CI pipeline does not necessarily mean a release is safe. Evidence might cover the wrong files, tests might not be properly attested, or an AI reviewer might accept another agent’s conclusions without independent scrutiny.
We built ReleaseGuard to address that gap: a human-governed AI review workflow with independently verified release evidence.
What it does
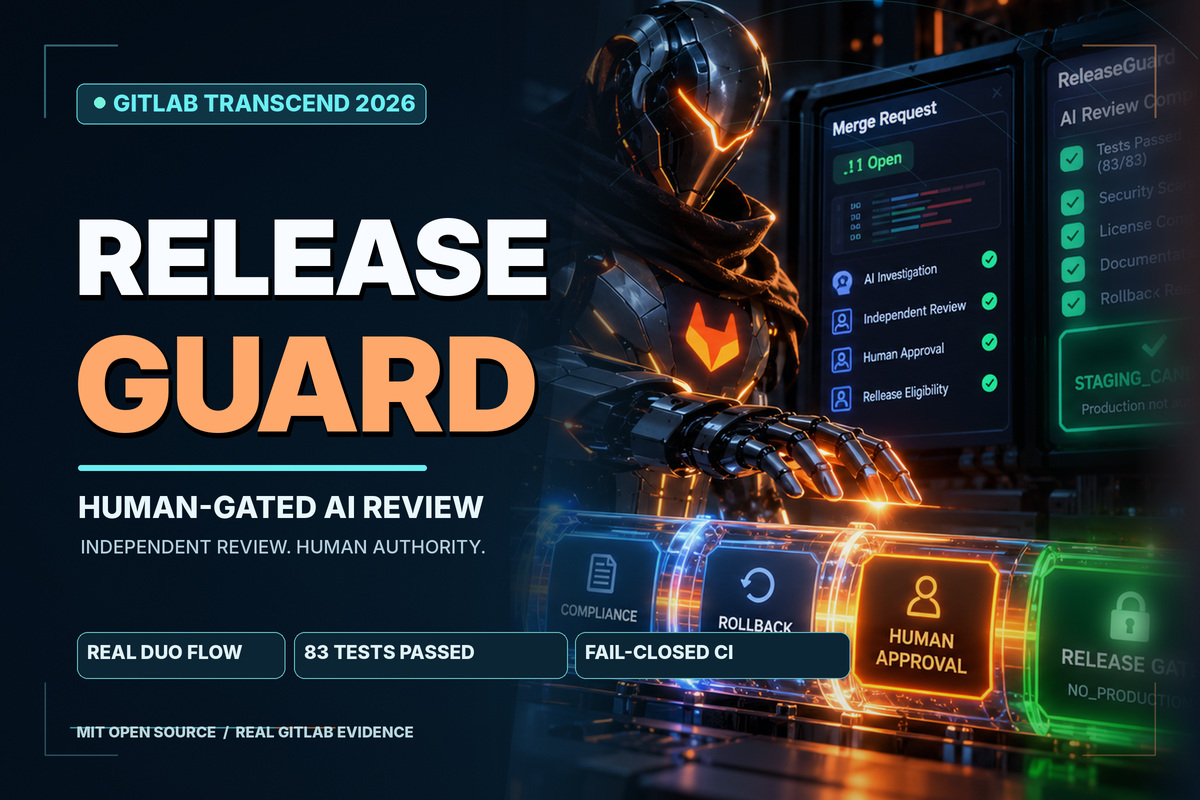
ReleaseGuard combines the GitLab Duo Agent Platform with a fail-closed GitLab CI/CD release gate.
Its workflow separates four responsibilities:
- Investigator: Examines a merge request and its supporting evidence.
- Independent Assessor: Challenges the investigation and identifies failed or unverified claims.
- Human Approval Gate: Requires explicit authorization before publishing an audit.
- Audit Publisher: Posts one approved review comment without autonomously merging or deploying code.
A separate CI pipeline validates tests, security scanning, licensing, documentation, rollback readiness, and release evidence.
The independent gate can issue STAGING_CANDIDATE or NO_GO. Neither decision authorizes production deployment.
How we built it
We developed ReleaseGuard inside the official GitLab Transcend hackathon workspace using Python, GitLab Duo, GitLab CI/CD, YAML, GitLab APIs, and Git.
The custom Duo flow contains multiple specialized agents and a human-input checkpoint. The CI pipeline performs deterministic validation rather than relying solely on AI-generated assessments.
Release evidence is tied to the actual GitLab commit, pipeline, and job. Source-file inventory checks prevent incomplete change scopes from passing unnoticed.
The complete source code is publicly available under the MIT license.
Real-world demonstration
ReleaseGuard was executed on GitLab, not merely simulated.
A real GitLab Duo review session, #9701090, investigated merge request !1. The independent assessor identified two genuine implementation weaknesses:
- The original evidence proposal covered only one source file.
- The test attestation hashed source code instead of actual test results.
We corrected both findings and reran the hosted CI pipeline.
Verified results:
- 83 passing tests, zero failures.
- All eight GitLab CI jobs successful.
- A real human-approved GitLab merge-request audit comment.
- Production permission remained disabled.
We also executed a controlled negative test. Six prerequisite jobs passed, but deliberately injected failed security evidence caused the independent gate to return NO_GO, skipping staging. This was an intentional evidence-injection test, not a vulnerability discovered by the scanner.
Challenges
Our most important challenge was proving that the system performed genuine, independently governed AI work.
Simply writing a workflow configuration wasn’t enough. We had to register and execute the real Duo flow, verify its human-approval behavior, and inspect actual CI artifacts.
The independent assessor also found defects in our own implementation. Addressing those findings improved the project’s integrity and demonstrated why independent review matters.
Accomplishments
We delivered a working human-gated multi-agent review, a published audit trail, a verified eight-job CI pipeline, 83 passing tests, and independently tested fail-closed release behavior.
Most importantly, the AI reviewer was able to challenge the original implementation and drive meaningful corrections.
What we learned
AI should accelerate engineering without bypassing accountability.
Independent reviewers must be able to disagree. Evidence must be verifiable. Human authorization must be specific. A passing build must never be confused with production approval.
What’s next
Future work includes stronger cryptographic attestations, additional security integrations, richer rollback verification, and separately authorized staging workflows.
Our long-term objective is to make governed AI delivery practical, transparent, and auditable for engineering teams.
Explore the project
Source code: https://gitlab.com/gitlab-ai-hackathon/transcend-october-2026/43487528/showcase
Video demonstration: https://www.youtube.com/watch?v=NqE-IRl5Wcg
Real human-approved audit: https://gitlab.com/gitlab-ai-hackathon/transcend-october-2026/43487528/showcase/-/merge_requests/1#note_4044417700
Successful CI pipeline: https://gitlab.com/gitlab-ai-hackathon/transcend-october-2026/43487528/showcase/-/pipelines/2964677508
Controlled NO_GO test: https://gitlab.com/gitlab-ai-hackathon/transcend-october-2026/43487528/showcase/-/pipelines/2964199953
Built With
- agents
- ai
- css3
- devsec
- devsecops
- duo
- gitlab
- html5
- javascript
- json
- python
- yaml

Log in or sign up for Devpost to join the conversation.