ReleaseGate — AI Advises. Evidence Decides. Humans Approve.
Inspiration
AI agents can review code, identify risks, and recommend releases. But recommendations alone are not sufficient grounds for deploying software.
A passing CI pipeline does not automatically mean a release is safe. An AI approval is not a security guarantee. And an incomplete evidence chain must never be treated as permission to proceed.
ReleaseGate addresses this gap: it transforms AI-assisted code review and verifiable CI evidence into deterministic, auditable release decisions—without surrendering human authority.
What It Does
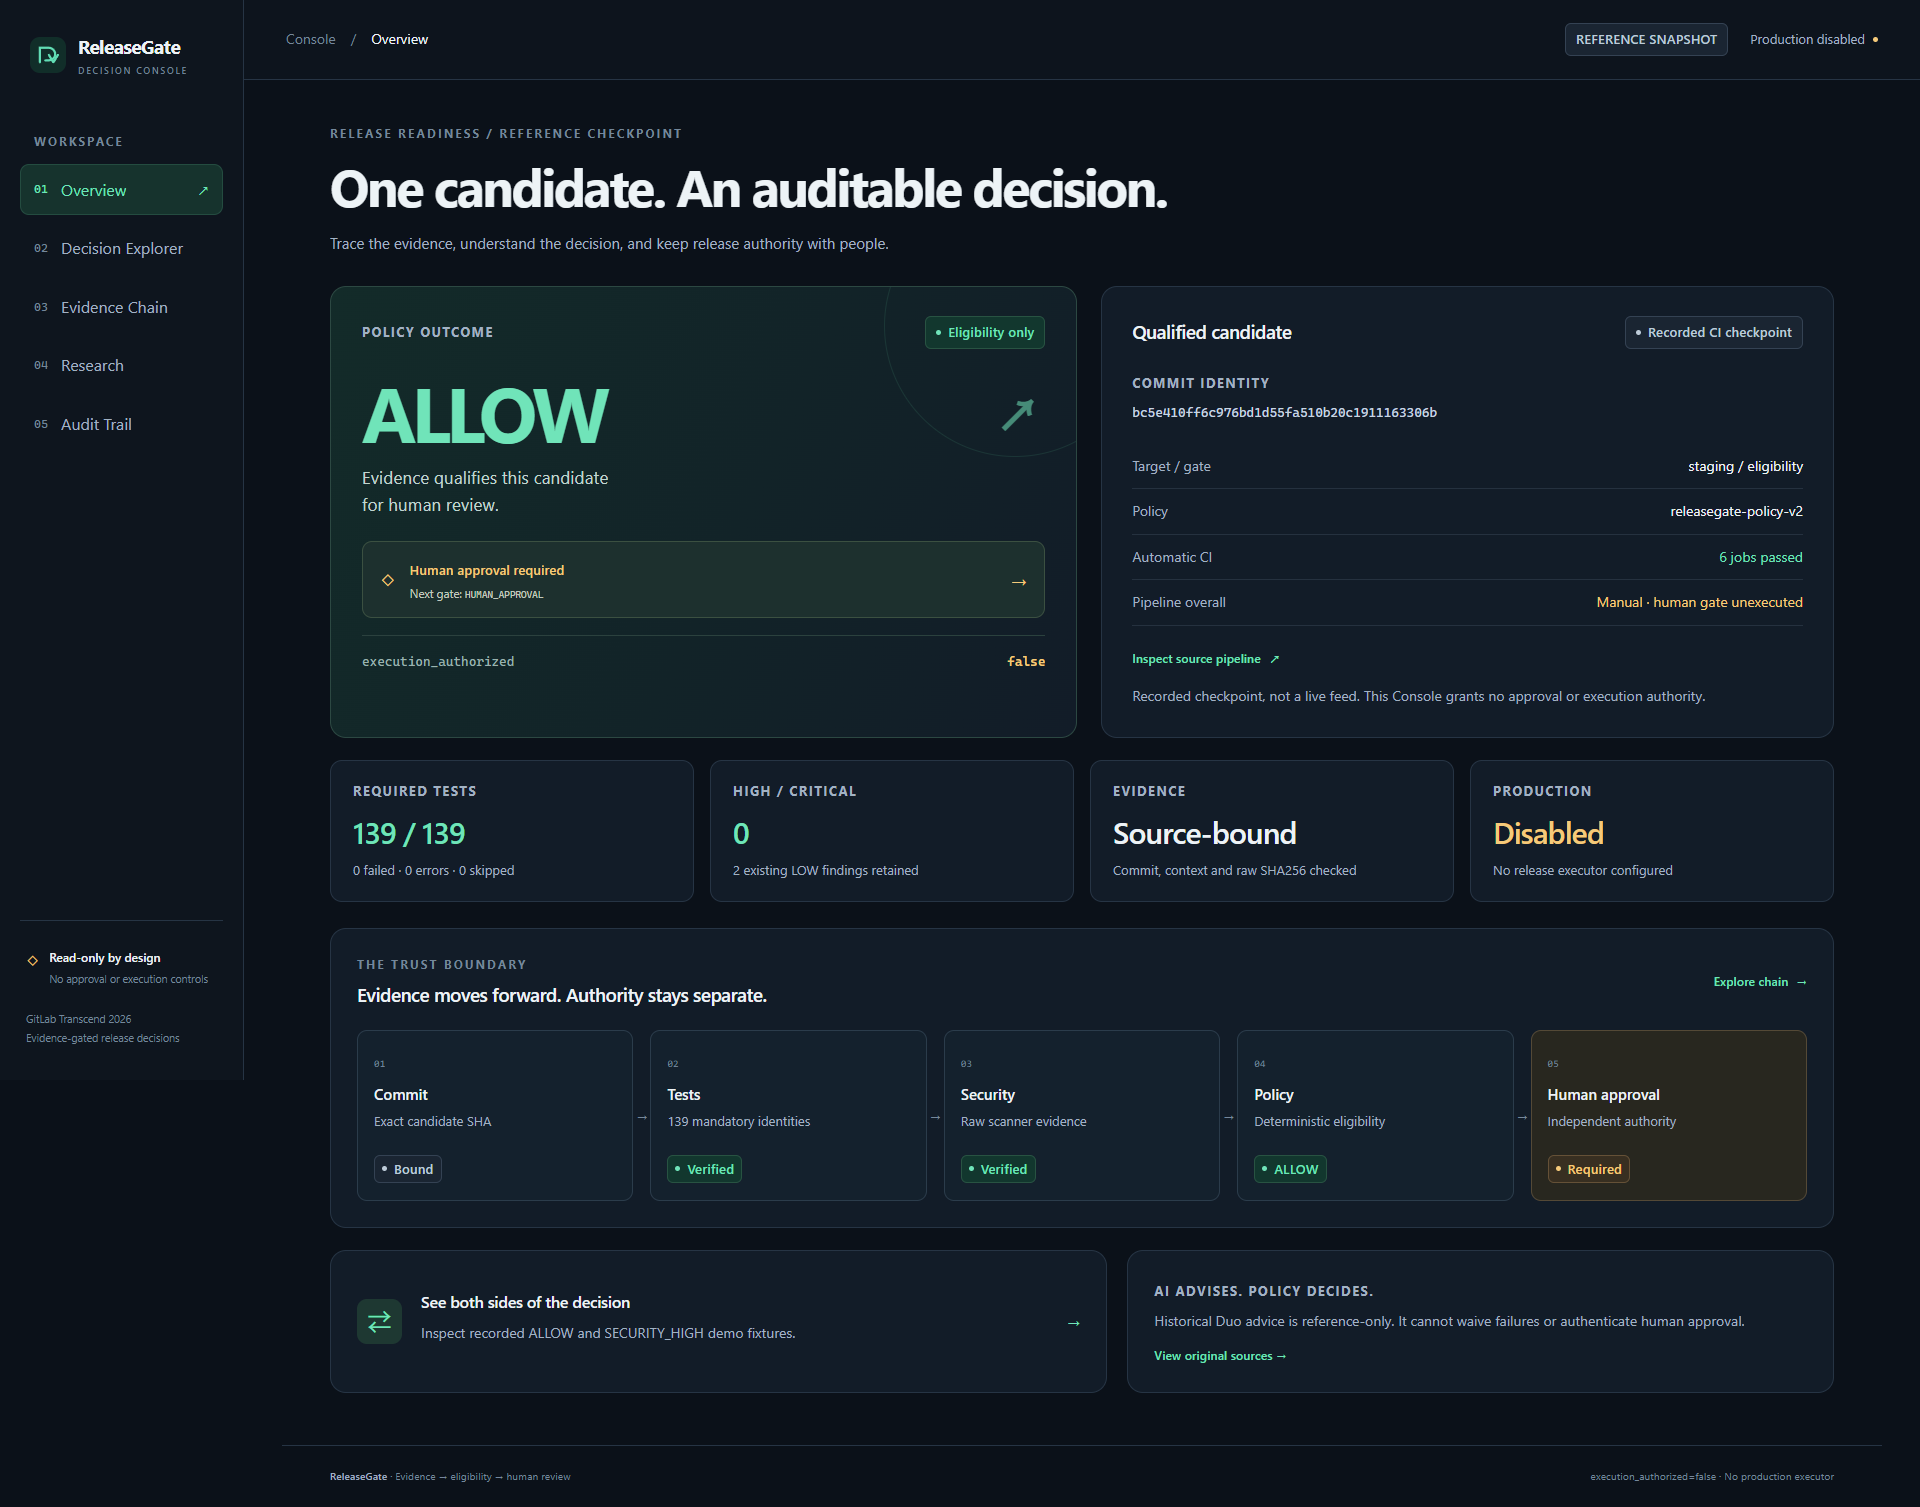
ReleaseGate is an evidence-gated release verification system integrated with GitLab's DevSecOps workflow.
It brings together five capabilities:
1. AI-Assisted Code Review
GitLab Duo Code Review Flow examines merge requests and identifies potential correctness and security issues.
AI findings inform development and remediation, but cannot override release policy.
2. Evidence-Bound Verification
ReleaseGate collects and validates evidence from actual automated tests, security scanners, and CI pipelines.
Evidence is associated with exact candidate identities and cryptographic hashes, helping prevent results from being applied to the wrong source revision.
Missing, inconsistent, or invalid evidence causes verification to fail closed.
3. Deterministic Release Decisions
A policy engine produces explicit outcomes:
- ALLOW: The candidate is eligible for human approval.
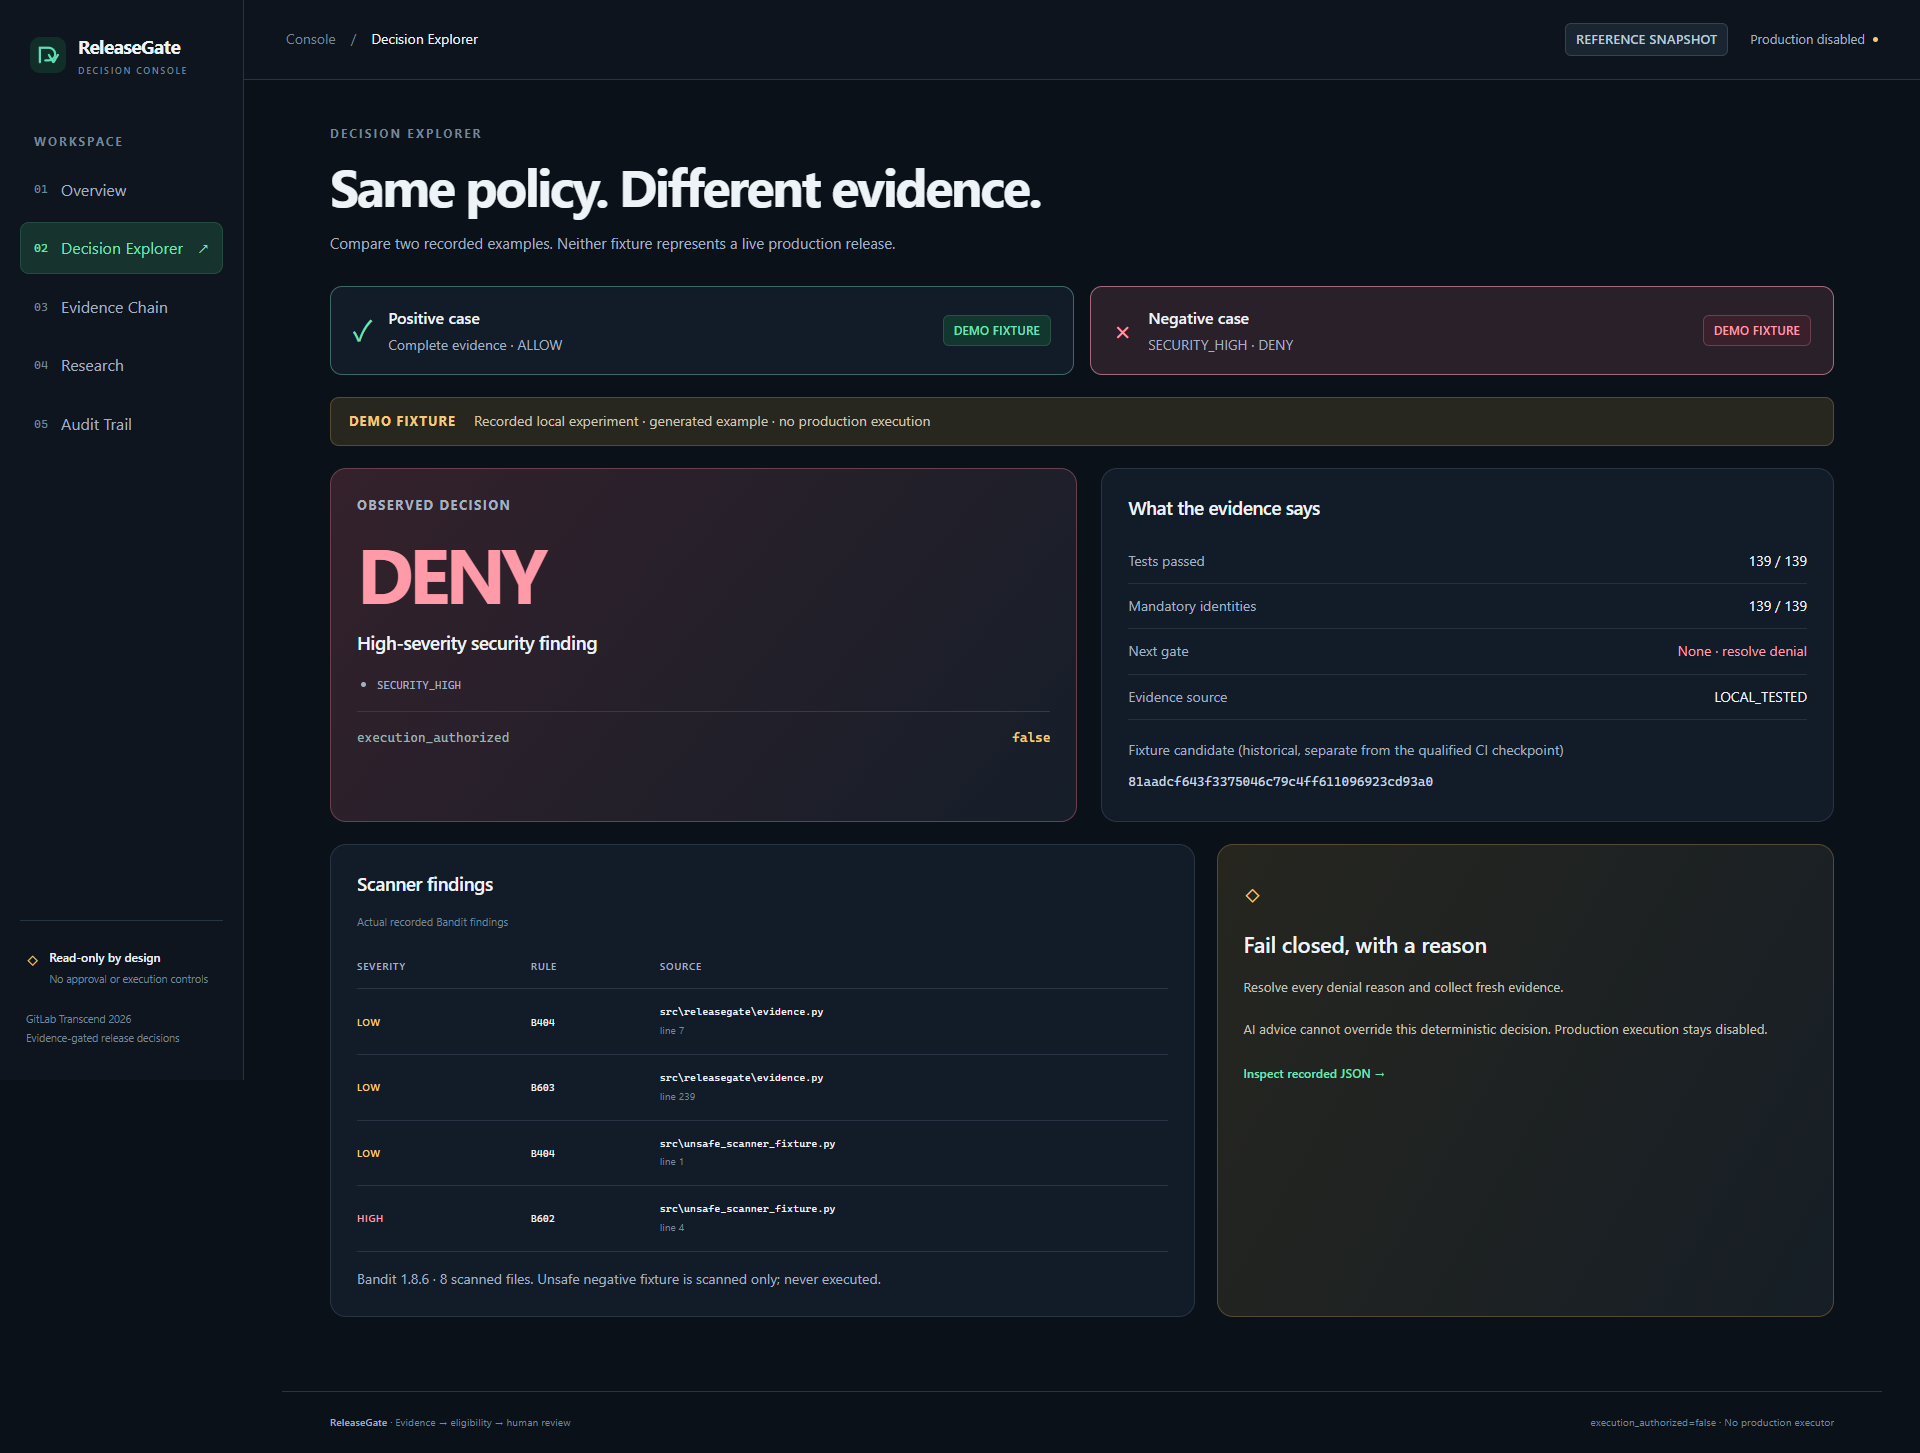
- DENY: The candidate is blocked, with recorded reasons.
A passing test suite cannot override a HIGH-severity security finding.
4. Independent Human Approval
ALLOW never means automatic deployment.
ReleaseGate keeps eligibility, human approval, and execution authority separate.
Production execution remains disabled in the submitted demonstration.
5. Auditable Decision Console
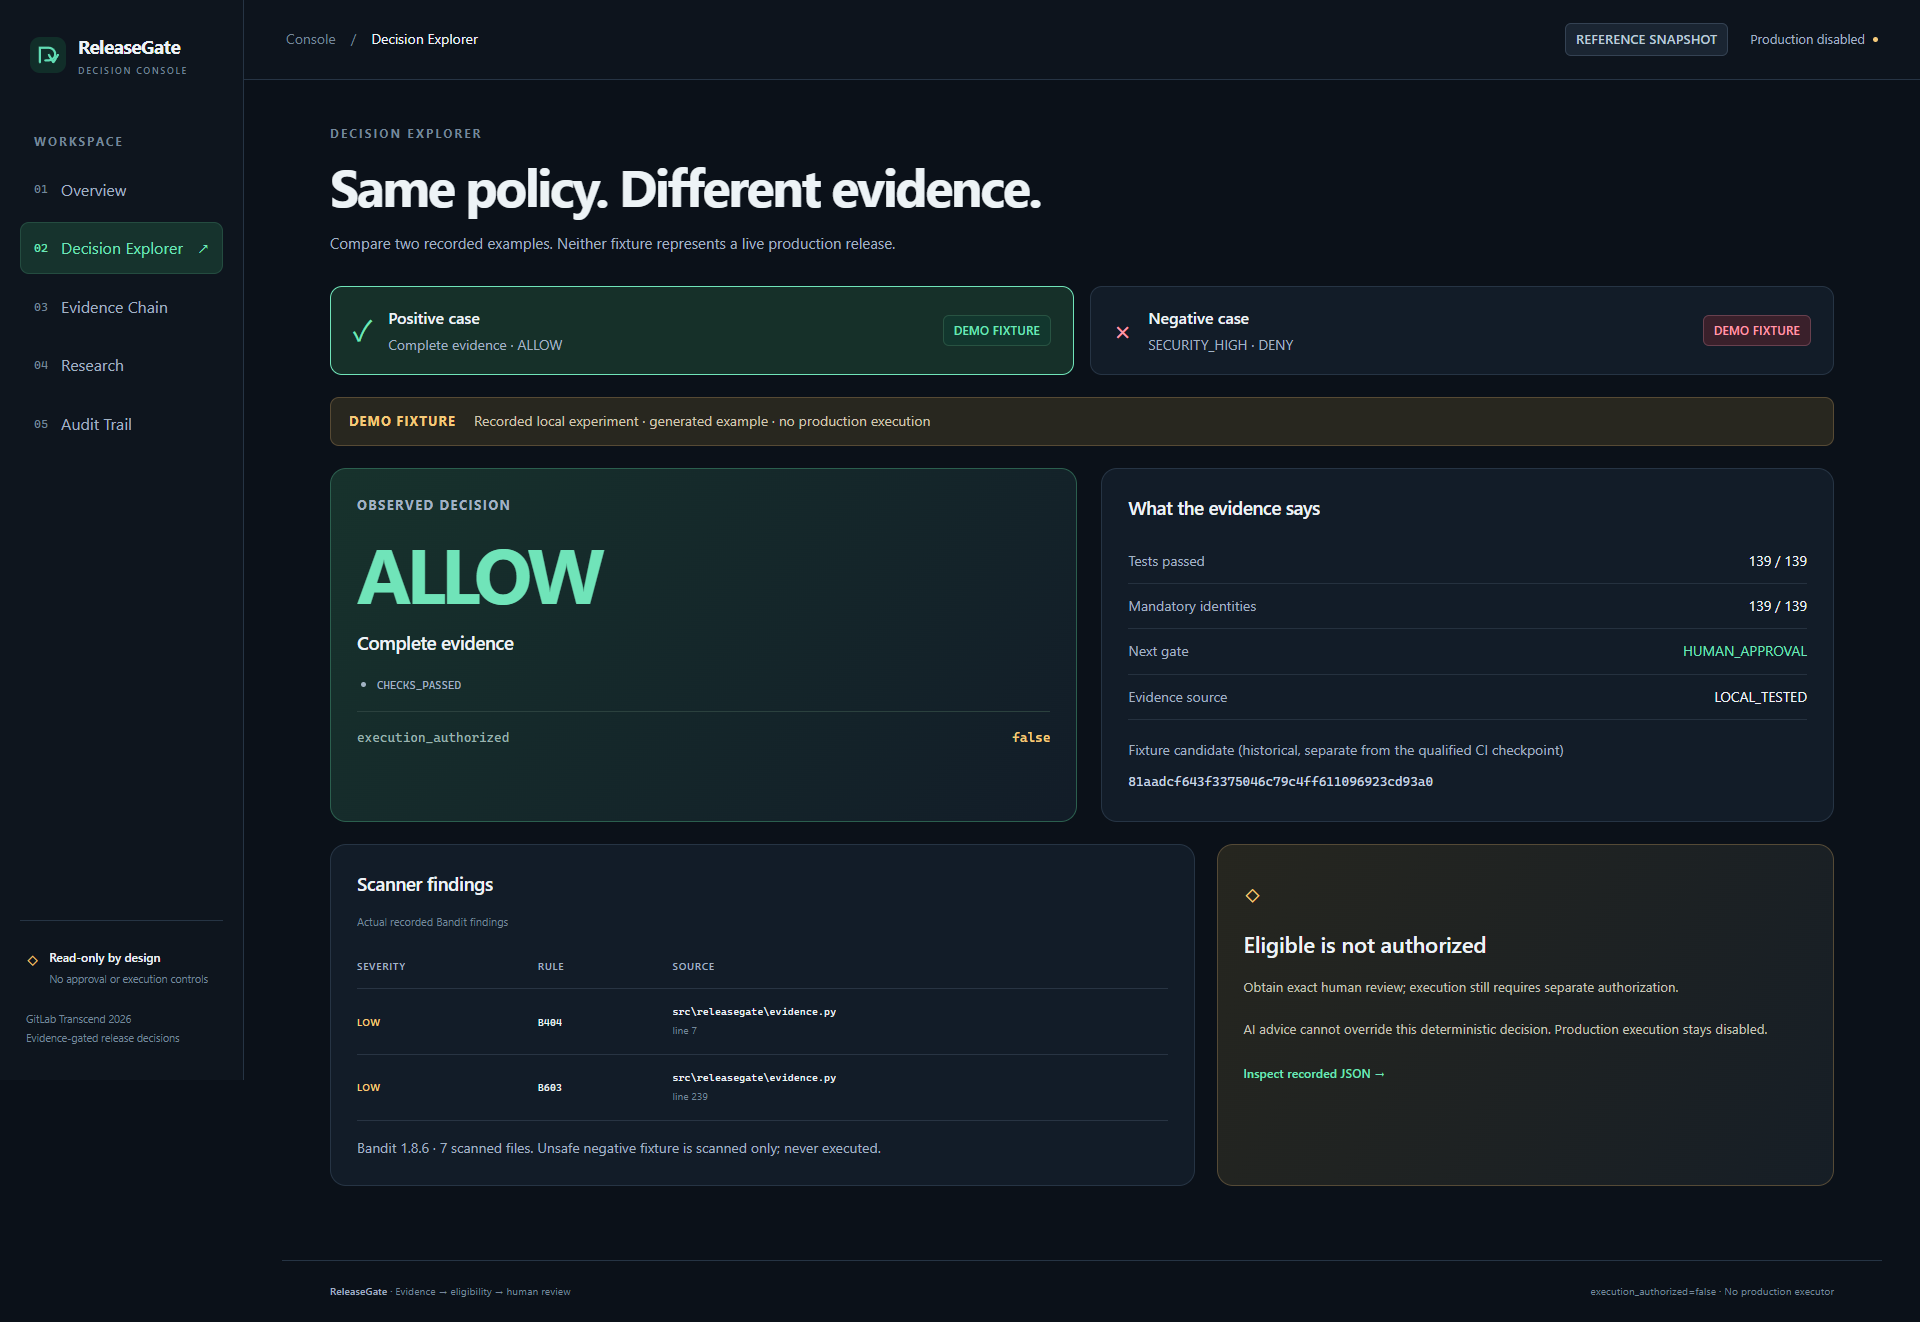
A visual console exposes release decisions, test evidence, scanner findings, candidate identities, and audit information.
Reviewers can compare successful and rejected cases to understand why the same policy produces different results.
How We Built It
ReleaseGate combines:
- GitLab CI/CD for automated verification and pipeline evidence.
- GitLab Duo Code Review Flow for AI-assisted review.
- Python for evidence validation and deterministic policy evaluation.
- pytest for automated correctness verification.
- Bandit for Python security scanning.
- SHA-256 evidence binding for integrity checks.
- JavaScript, HTML, and CSS for the interactive decision console.
- Docker and Azure Container Apps for the public demonstration deployment.
The workflow is intentionally evidence-first:
Source candidate → CI tests → Security scanning → Evidence validation → Policy decision → Human approval gate
AI provides advice. The policy engine evaluates the evidence. Human approval remains an independent authority.
What Makes ReleaseGate Different?
Most AI-assisted DevOps demonstrations emphasize how quickly an agent can take action.
ReleaseGate focuses on a more important question:
What evidence must exist before an AI-assisted system is even allowed to recommend proceeding?
Its distinctive design includes:
- Fail-closed verification: Unknown, missing, or inconsistent evidence never becomes an implicit approval.
- Source-bound evidence: Decisions are tied to candidate identities and verifiable artifacts.
- Security-aware decisions: HIGH and CRITICAL findings are evaluated independently of passing tests.
- Human authority: Eligibility never grants permission to execute a production release.
- Transparent auditability: Decisions include evidence and explicit reasons rather than opaque AI confidence scores.
Proof That It Works
The project has been validated through actual automated testing and GitLab workflow evidence.
Key results include:
- 139 mandatory test identities validated.
- 218 Python tests passing in the verified deployment source.
- 9 additional JavaScript behavior tests passing.
- 42/42 expected classifications across 14 research scenarios repeated three times.
- Genuine Bandit findings retained and evaluated.
- GitLab CI pipeline history demonstrating automated verification.
- GitLab Duo review findings followed by corrective changes and retesting.
Both positive and negative cases were tested.
In the positive case, complete qualifying evidence produces ALLOW while retaining the human approval requirement.
In the negative case, a genuine HIGH-severity security finding produces DENY—even when mandatory tests pass.
Unsafe demonstration fixtures are scanned, not executed.
No production deployment was authorized or performed.
Challenges and Lessons Learned
The hardest challenge was separating three concepts that are often conflated:
- AI recommendations.
- Evidence-based release eligibility.
- Actual permission to deploy.
We also had to ensure that test evidence could not silently become detached from the source candidate it was supposed to represent.
Another challenge was presenting meaningful verification evidence publicly without exposing unrestricted server-side code execution.
These challenges reinforced a fundamental principle:
Trustworthy AI automation needs explicit boundaries, reproducible evidence, and independently enforced authority.
What We Built During the Hackathon
For the GitLab Transcend submission period, we developed and validated GitLab-centered review and verification workflows, exercised GitLab Duo review, strengthened the evidence and policy gates, expanded test coverage, and prepared the public decision console and deployment.
The public demo is deployed on Azure Container Apps using Docker Hub and Azure CLI.
The demonstration video shows the actual verification workflow. The public console provides a separate way to explore decisions and supporting evidence.
What's Next
Future development will extend these controls to more supervised release workflows while preserving the same evidence and approval boundaries.
The long-term goal is not to eliminate human judgment.
It is to ensure that every automated recommendation is explainable, every release decision is evidence-backed, and every consequential action has the authority it requires.
Explore ReleaseGate
Live public demo:
https://releasegate-public-demo.yellowtree-4e6734d2.australiaeast.azurecontainerapps.io
GitLab hackathon project:
https://gitlab.com/gitlab-ai-hackathon/transcend-october-2026/43343080/showcase
Original open-source repository:
https://github.com/miku-wwl/agentic-release-gate
Demo video:
https://youtu.be/HtQ_aaH5PbM

Log in or sign up for Devpost to join the conversation.