What is Raksa?
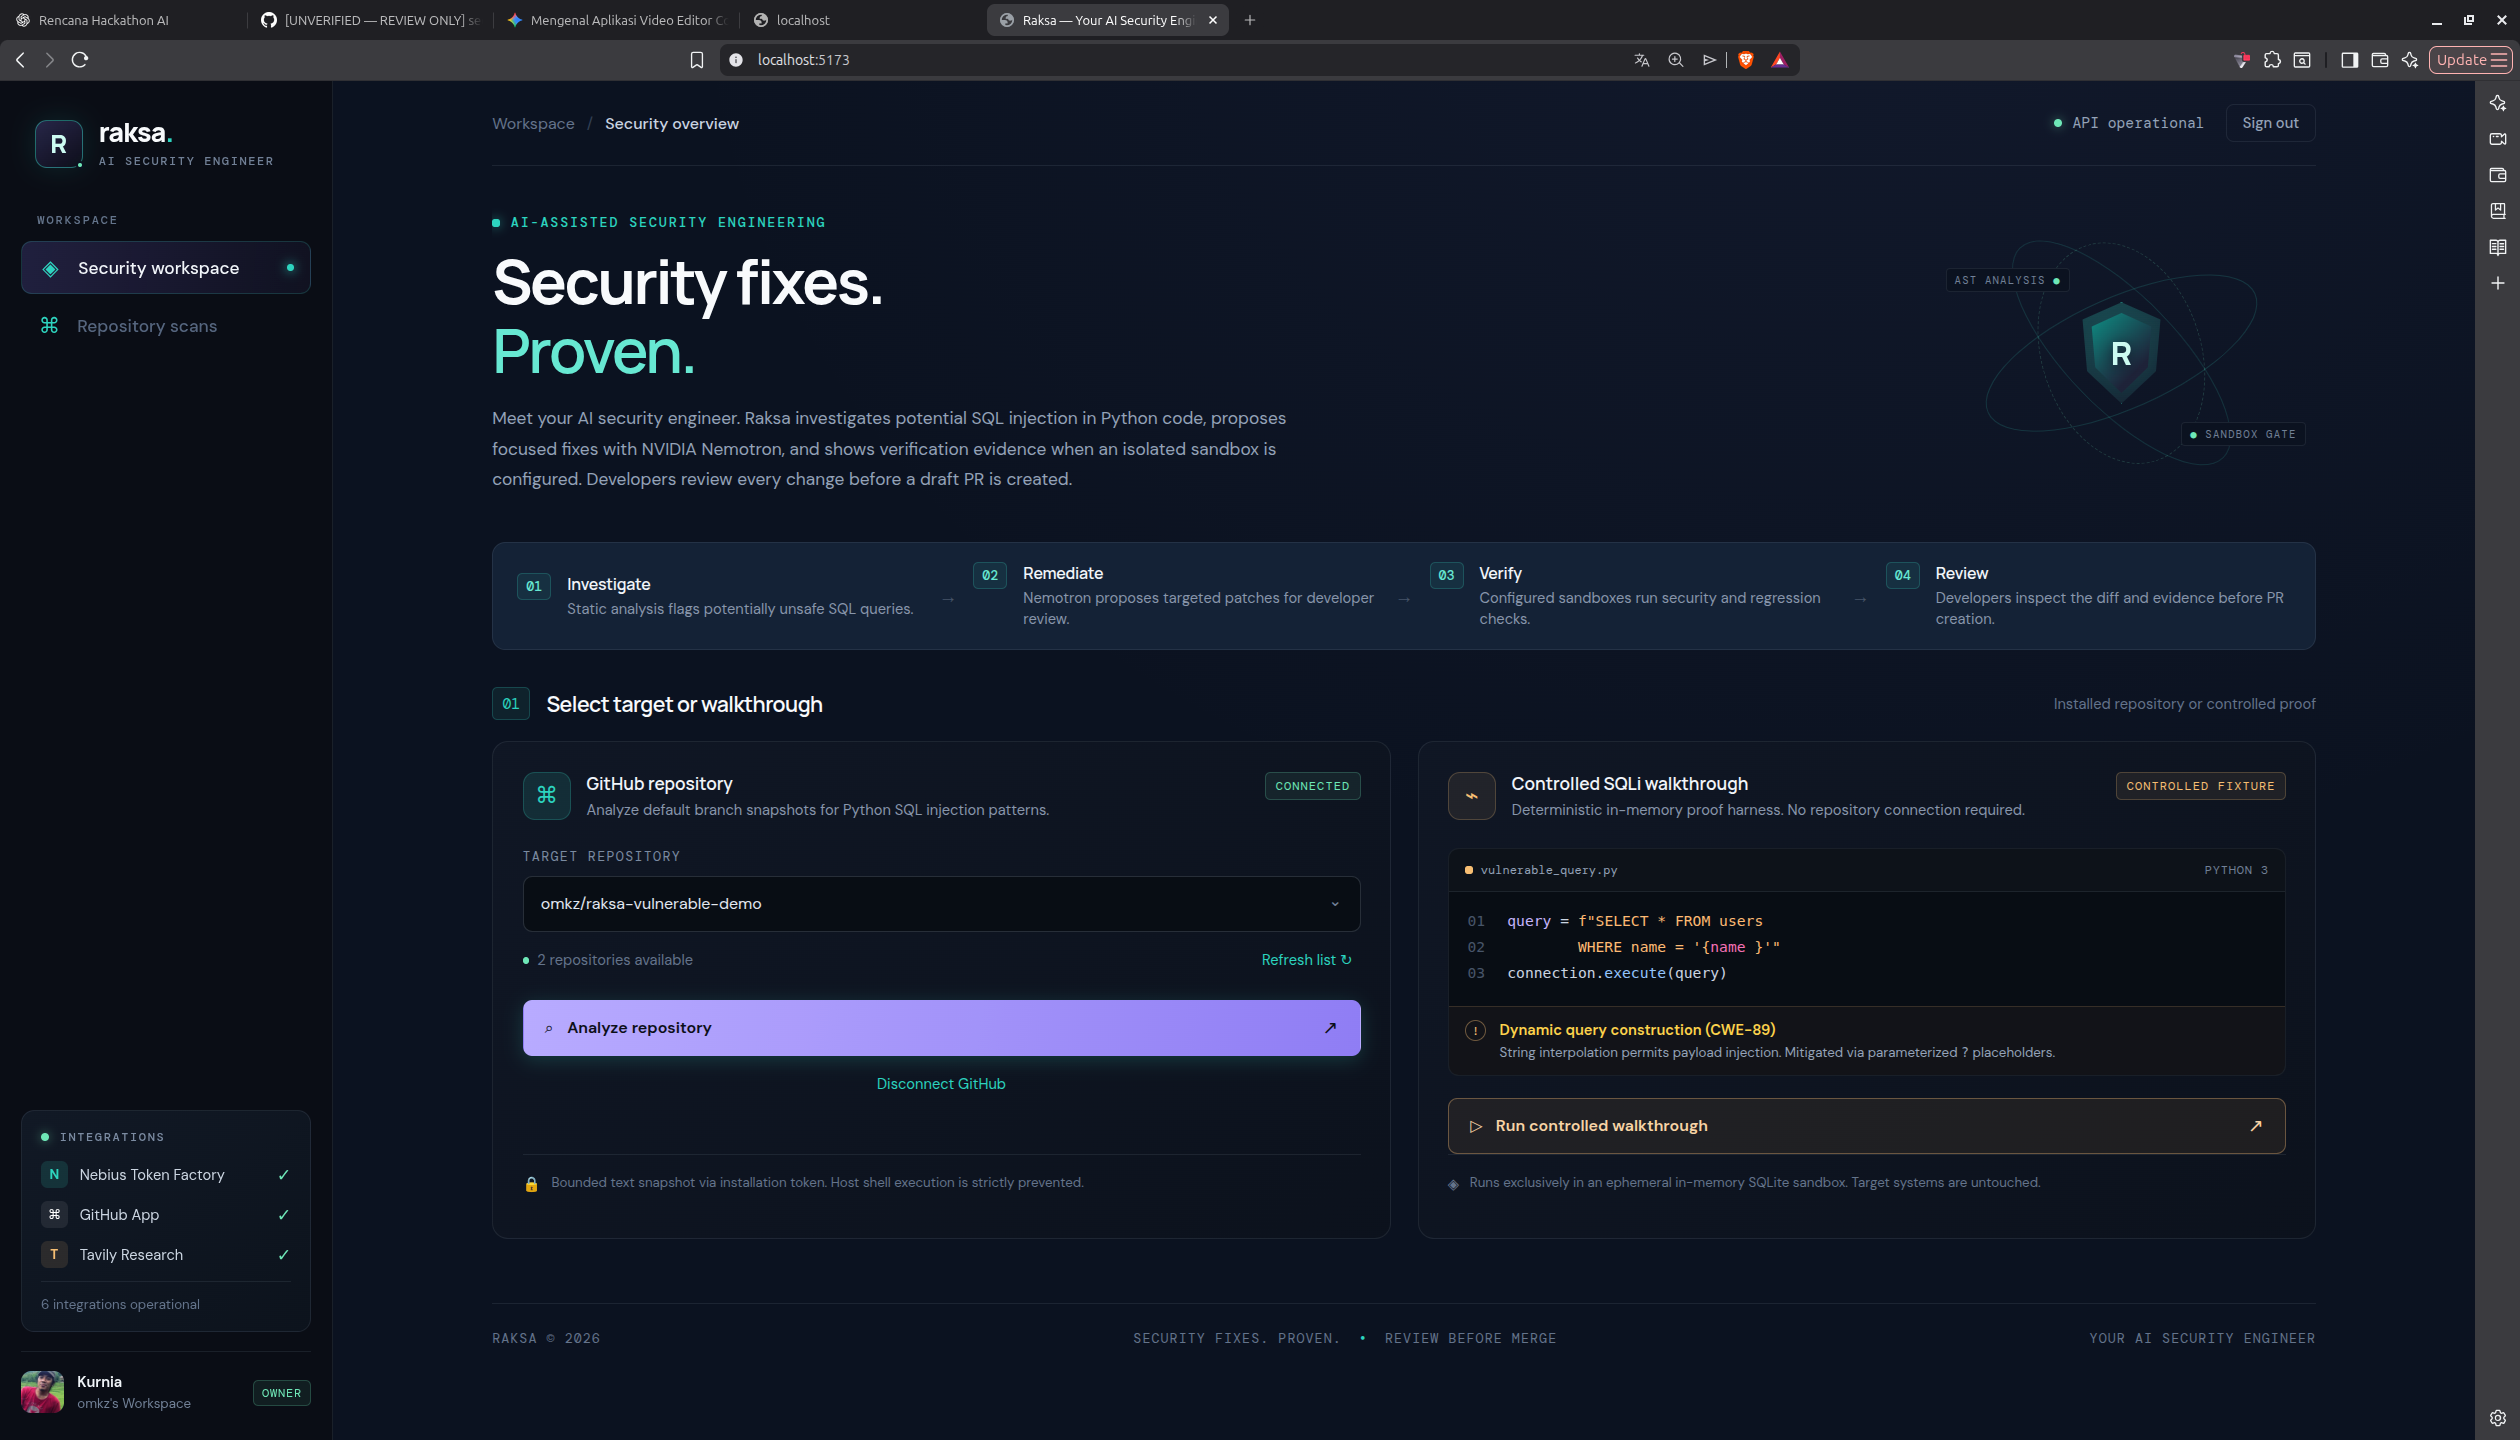
Raksa helps developers fix security issues found in GitHub repositories. It scans source code, uses NVIDIA Nemotron 3 Super through Nebius Token Factory to propose patches, and shows what was actually verified before a developer approves a Draft Pull Request.
How it works
- Connect a GitHub repository and run a source-code scan.
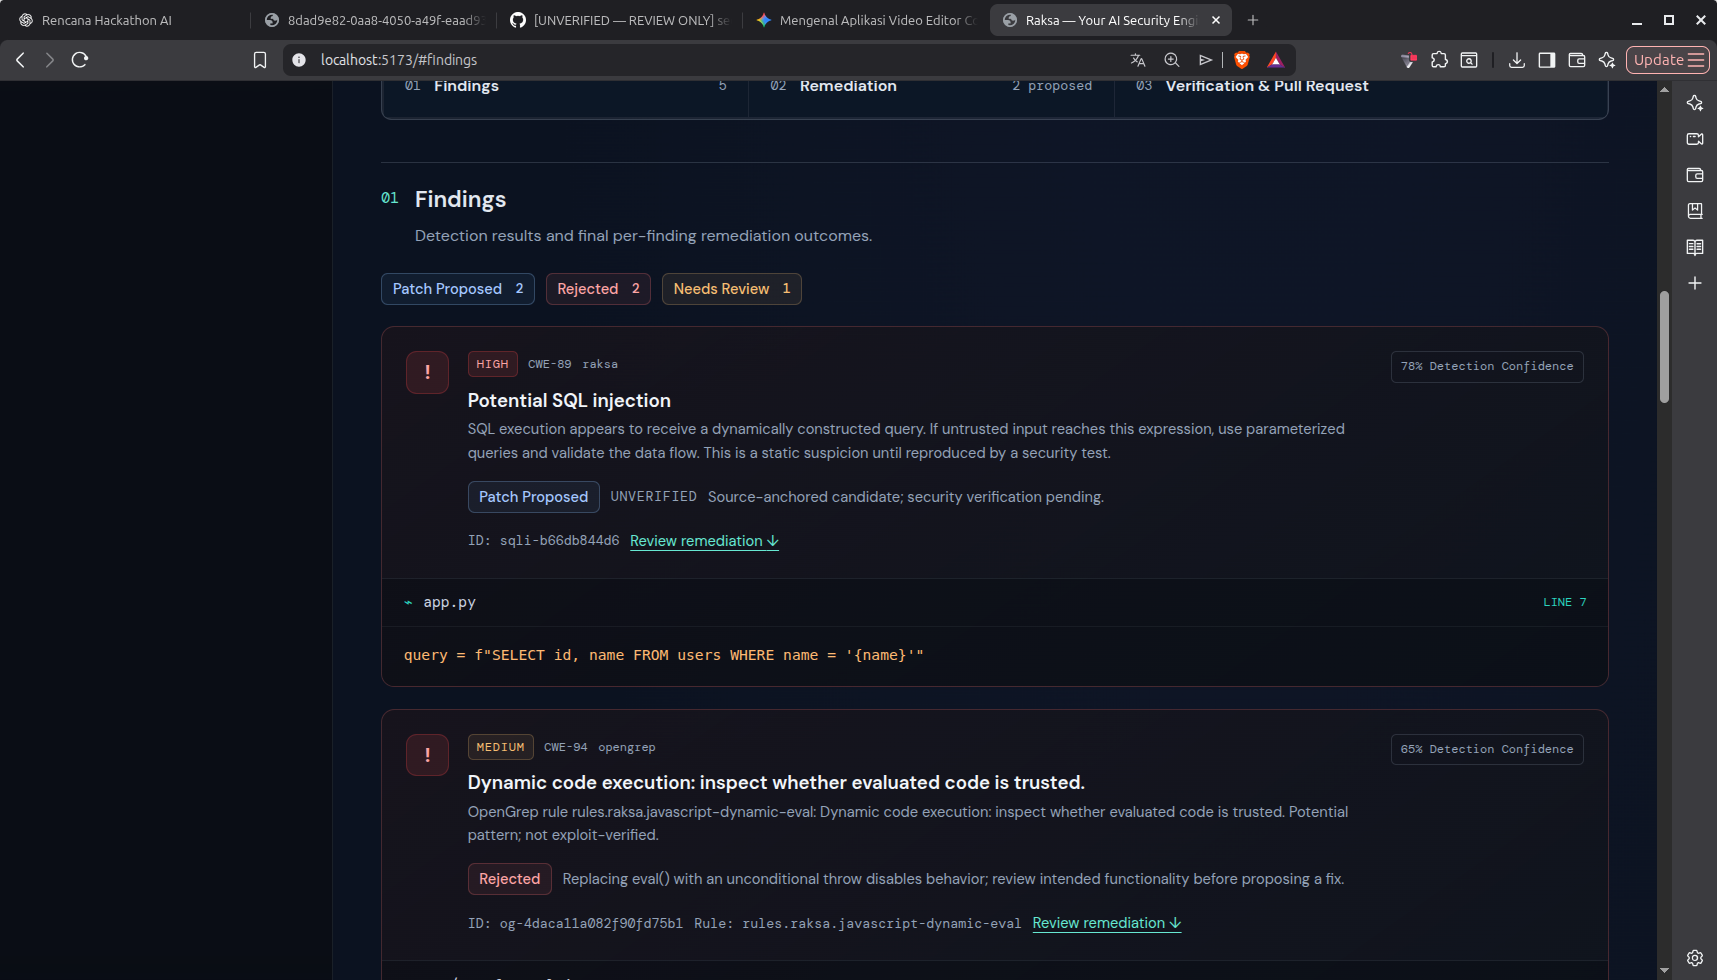
- Review potential vulnerabilities found by Python AST checks and optional OpenGrep rules.
- Let Nemotron suggest focused code changes. When a safe fix needs information about the application's security policy, Raksa can ask for context or decline to patch.
- Inspect the diff and verification results. Checks that were not run are clearly marked.
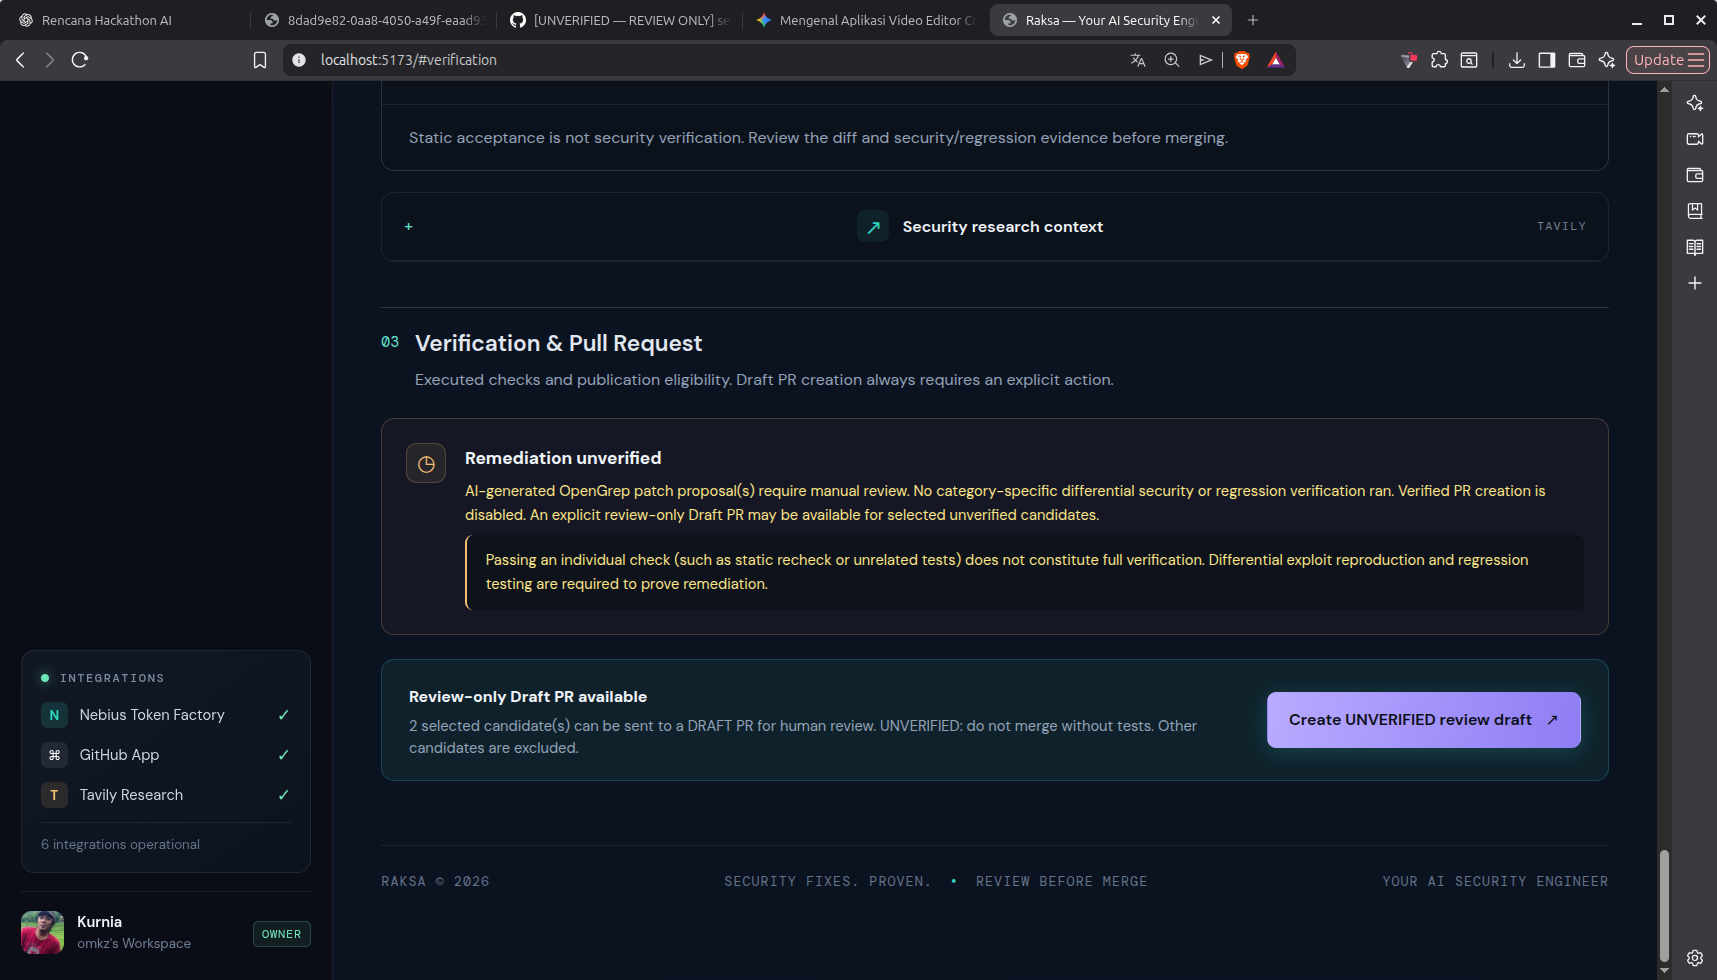
- Approve a review-only GitHub Draft PR. Raksa does not push to the default branch or auto-merge.
Tavily is used optionally to retrieve security guidance from OWASP and MITRE for SQL injection findings.
Working example
We scanned an intentionally vulnerable Python/JavaScript repository and found five potential issues: SQL injection, XSS, path traversal, command injection, and unsafe dynamic evaluation.
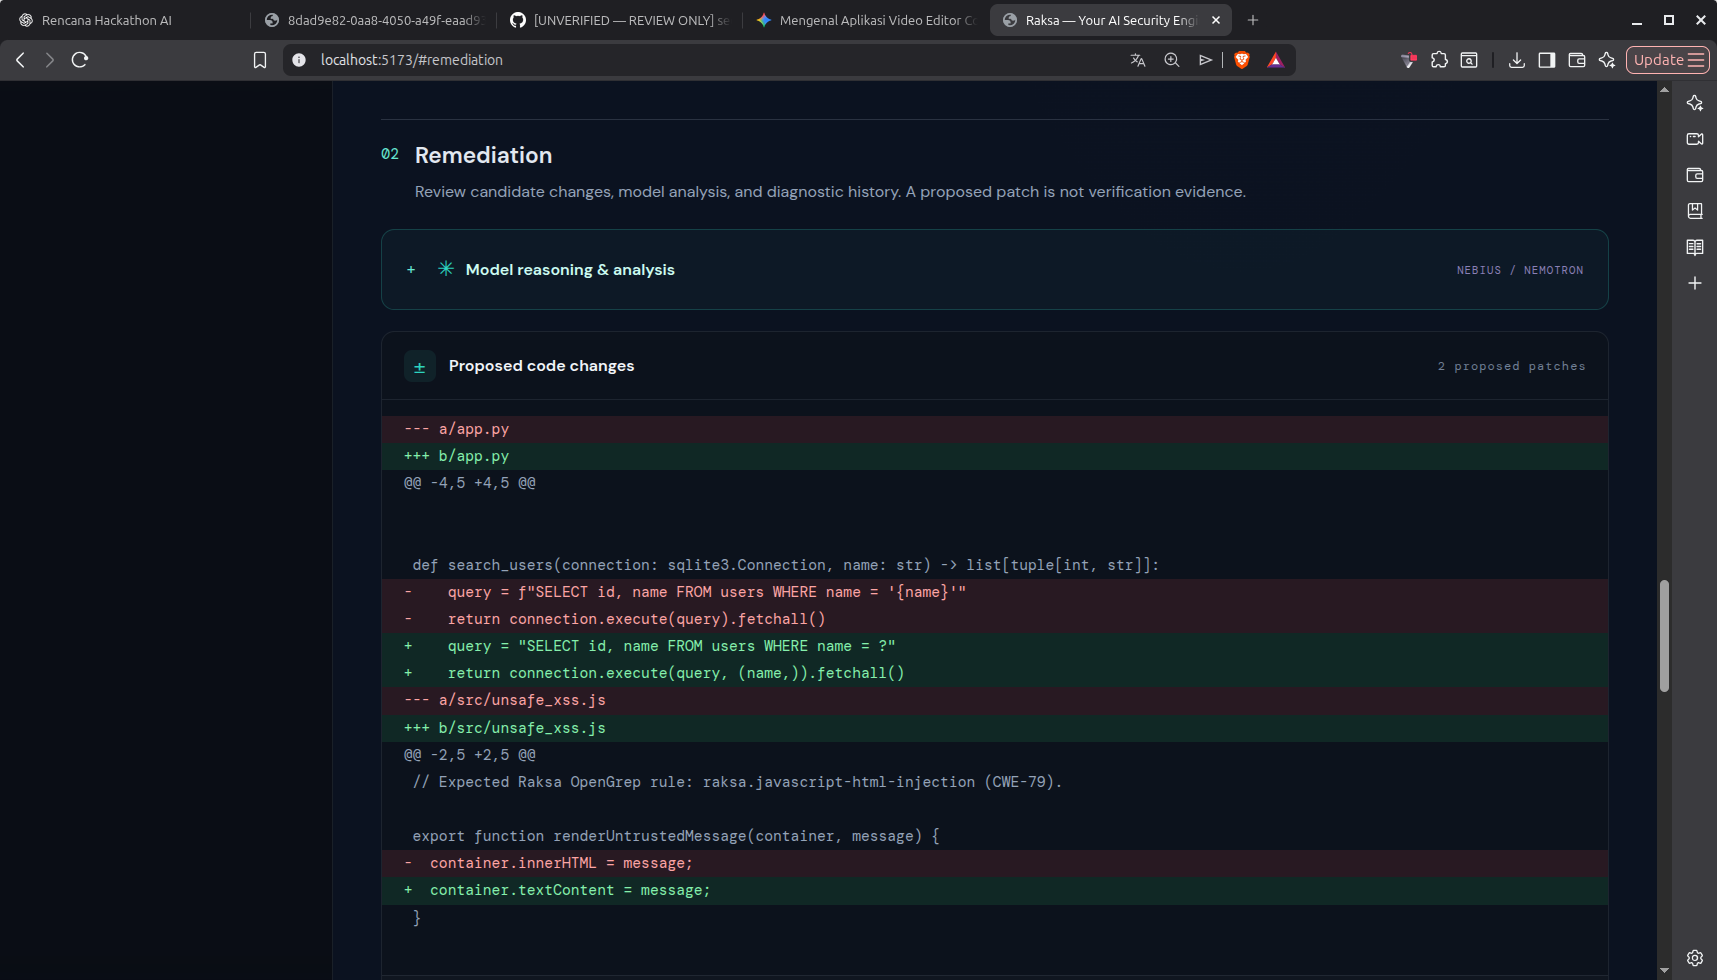
Nemotron proposed two focused changes: parameterized SQL in app.py and textContent instead of innerHTML in src/unsafe_xss.js. Raksa then created a real Draft PR through its GitHub App:
The PR is marked UNVERIFIED — REVIEW ONLY. No category-specific exploit or regression tests were run for those patches, so they still need human review. The vulnerable repository is for static scanning only and must not be executed or deployed.
Built with
- NVIDIA Nemotron 3 Super 120B-A12B via Nebius Token Factory for code reasoning and patch proposals
- Python, FastAPI, PostgreSQL for scanning and orchestration
- React, TypeScript for the dashboard
- GitHub App for repository access and Draft PRs
- OpenGrep (optional) for additional static security rules
- Tavily (optional) for sourced security references
- Docker / Nebius sandbox for supported isolated verification workflows
Challenges and limitations
The main challenge was keeping AI-generated changes within the intended source-code boundaries and separating proposed fixes from proven fixes. We added checks for patch context, syntax, repository revision, and human approval.
Raksa is an early-stage tool, not a full security audit. Its OpenGrep ruleset and verification coverage are still limited.
Source: https://github.com/omkz/raksa
Demo repository: https://github.com/omkz/raksa-vulnerable-demo
Built With
- docker
- fastapi
- github-api
- github-app
- nebius-token-factory
- nemotron-3-super
- nvidia-nemotron
- opengrep
- postgresql
- pydantic
- pytest
- python
- react
- sqlalchemy
- tavily
- typescript
- vite
