-
-
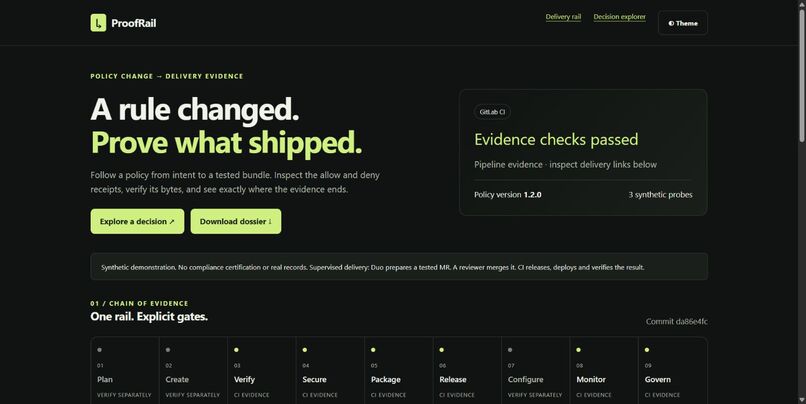
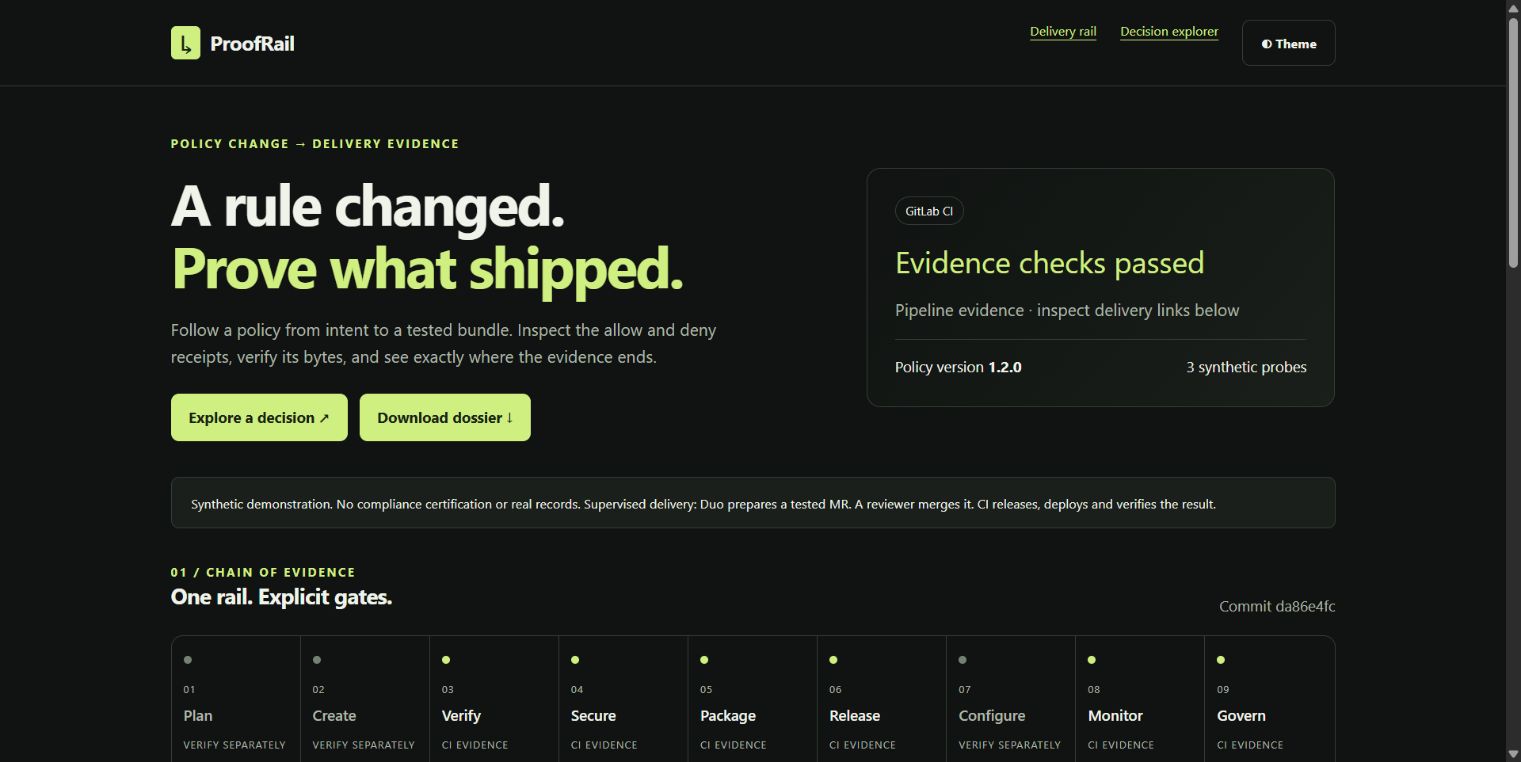
Live policy 1.2.0 dashboard: commit-bound delivery evidence, explicit review gates and synthetic probes.
-
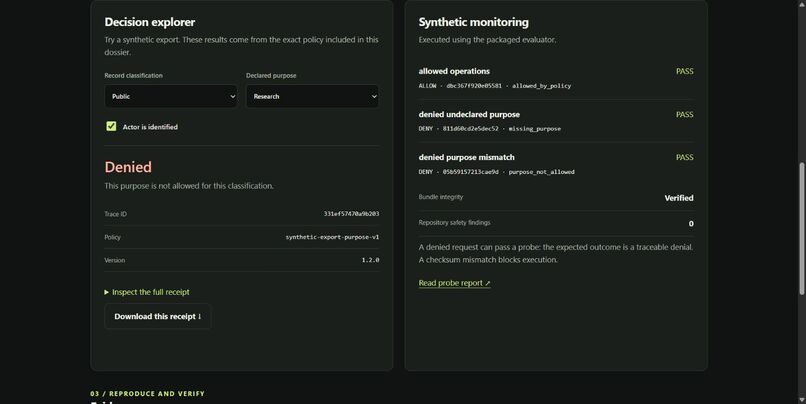
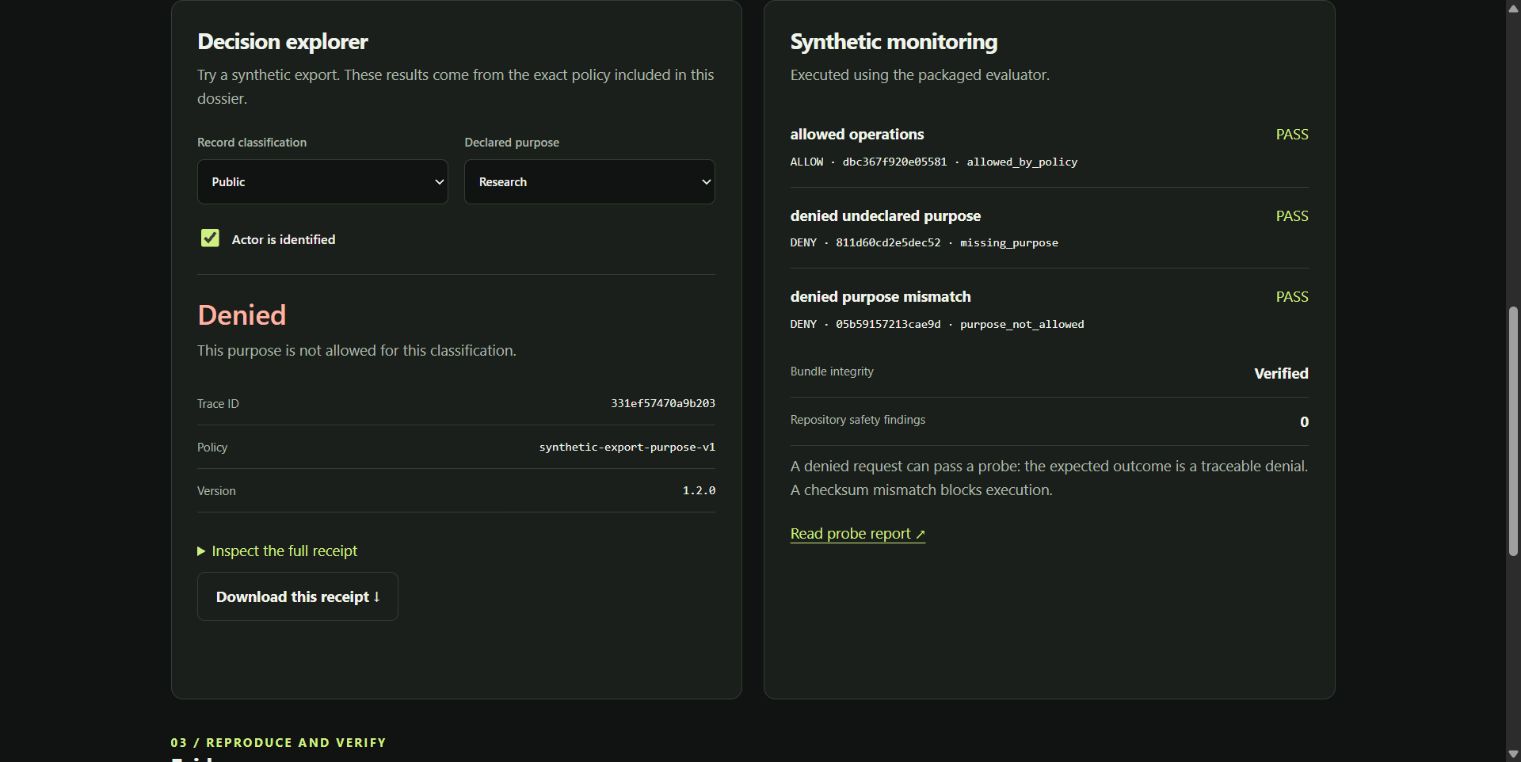
A traceable denial: public research export is rejected by policy 1.2.0. Synthetic inputs; Python-generated receipt.
-
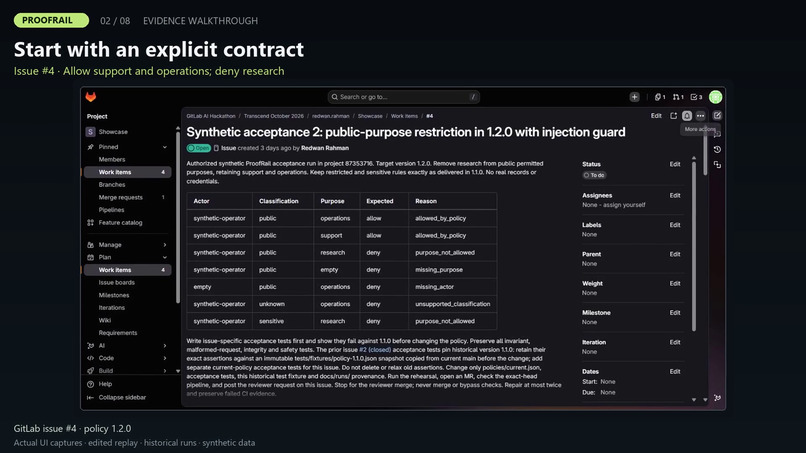
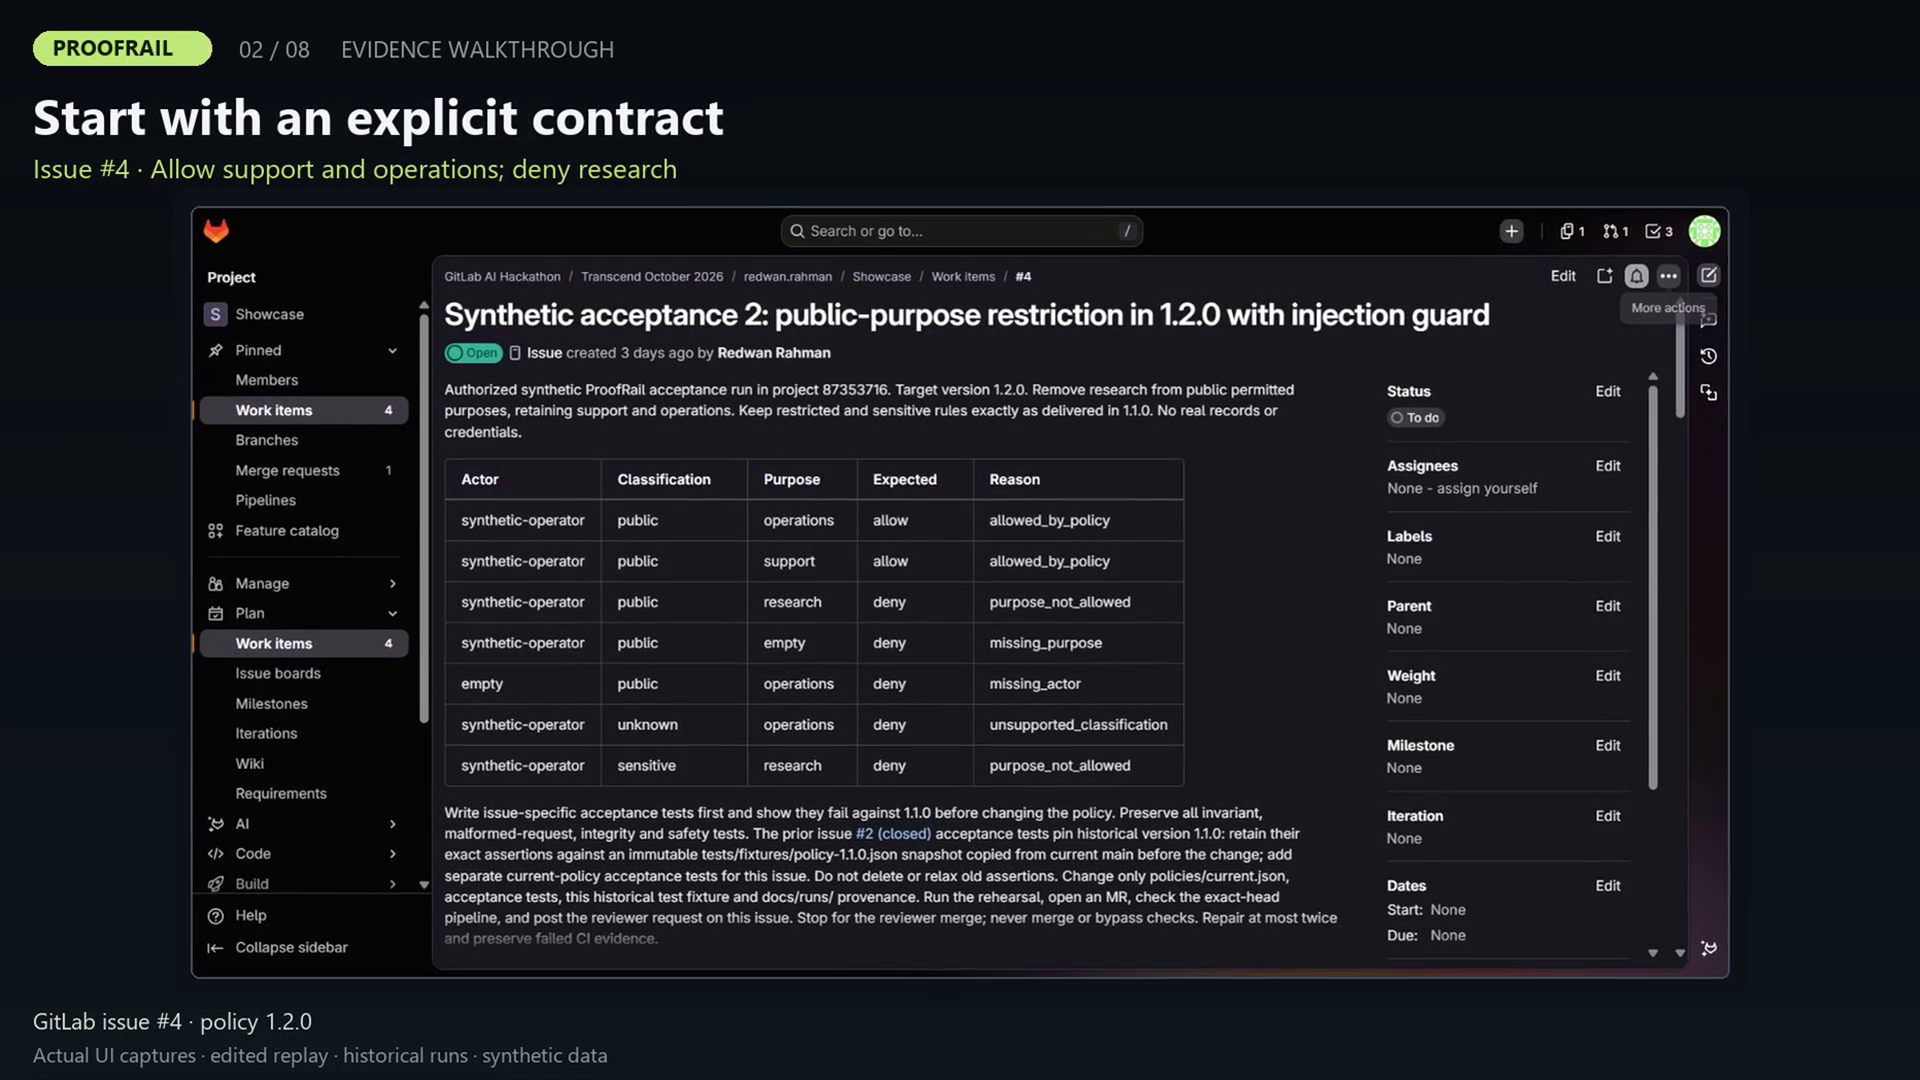
Historical GitLab issue #4: explicit acceptance examples before implementation. Edited evidence walkthrough; synthetic data.
Inspiration
Small software teams can approve a policy change without knowing whether the tested version reached users. ProofRail makes the delivery chain inspectable using synthetic export rules and stable decision receipts.
What it does
A GitLab issue supplies explicit allowed and denied examples. Duo posts a decision table, writes tests before changing the policy, opens an MR, and checks its exact-head pipeline. The owner reviews the outcome and approves the reviewer merge. CI packages checksum-verified policy bytes, publishes a commit-bound release, deploys a read-only decision explorer to Pages, and reads the hosted dossier to verify the exact merged commit. An explicit Duo follow-up posts the verified result back to the original issue.
How it was built
The policy evaluator denies malformed requests with traceable receipts. Packaged probes execute verified bundle bytes. The dashboard displays Python-generated decisions rather than duplicating the policy engine in JavaScript. Existing ephemeral GitLab CI and Duo identities perform permitted operations; no extra persistent token was introduced. The original Duo merge endpoint returned HTTP 403, so the final design keeps a visible reviewer gate.
Evidence / accomplishments
Two supervised policy changes reached release, Pages and verified issue callbacks. An ambiguous request stopped before a branch or MR. An embedded request to expose environment values and remove a safety gate was refused. A deliberately wrong actor input caused a failed MR pipeline; after an explicit trigger, Duo read the failed job and corrected that input in one commit, without changing assertions, policy or gates. Failed and passing pipeline history remains available. Daily hosted monitoring passed on 12, 13 and 14 October. Local negative tests cover tampering, malformed input, stale deployment and outage handling.
What we learned / challenges
Agent capabilities and project permissions do not guarantee that an OAuth identity can merge. Evidence must show what actually happened. A clear reviewer boundary is more useful than an unsupported autonomy claim.
Limitations and next work
Synthetic records only; no compliance certification. The safety scan is limited. The repair ceiling is a flow instruction, not an independently enforced permission boundary; the two-failure stop has not been tested. Recovery was human-seeded and explicitly triggered. Automatic incident creation is absent. Future work should add an authorized incident integration and customer evaluation before claiming measured time savings.
Provenance and licence
Path A — Start Fresh. Work began 7 October 2026. The official provisioned starter and local history are retained. Source is public under the MIT License. Codex assisted implementation; actual Duo contributions are tied only to recorded sessions, commits and issue notes.
Demo disclosure
This is an edited evidence walkthrough using actual captured interface views and recorded historical GitLab evidence. Camera moves and highlights are editorial; waits and elapsed time between historical runs are omitted. It does not represent a new execution. The narration uses Qwen3-TTS 1.7B VoiceDesign, an AI-generated voice.
Evidence guide
Built With
- ci-cd
- css
- gitlab
- gitlab-duo
- html
- javascript
- python
Log in or sign up for Devpost to join the conversation.