💡 Inspiration
Cyber fraud and SMS phishing scams (smishing) are skyrocketing globally, targeting everyday mobile users, students, and elderly individuals with deceptive bank alerts, fake delivery tracking, and fraudulent payment links.
Most existing mobile security apps rely on static domain blacklists that fail against zero-day phishing links created just minutes prior. We built PhishLens to create an intelligent, real-time, privacy-first mobile threat shield that acts as a proactive AI security analyst right on your Android phone.
✨ Features at a Glance
[!IMPORTANT] Zero-Latency In-Browser Interception: PhishLens inspects URLs live on your screen and blocks malicious domains before credentials can be compromised—without routing traffic through third-party VPN servers.
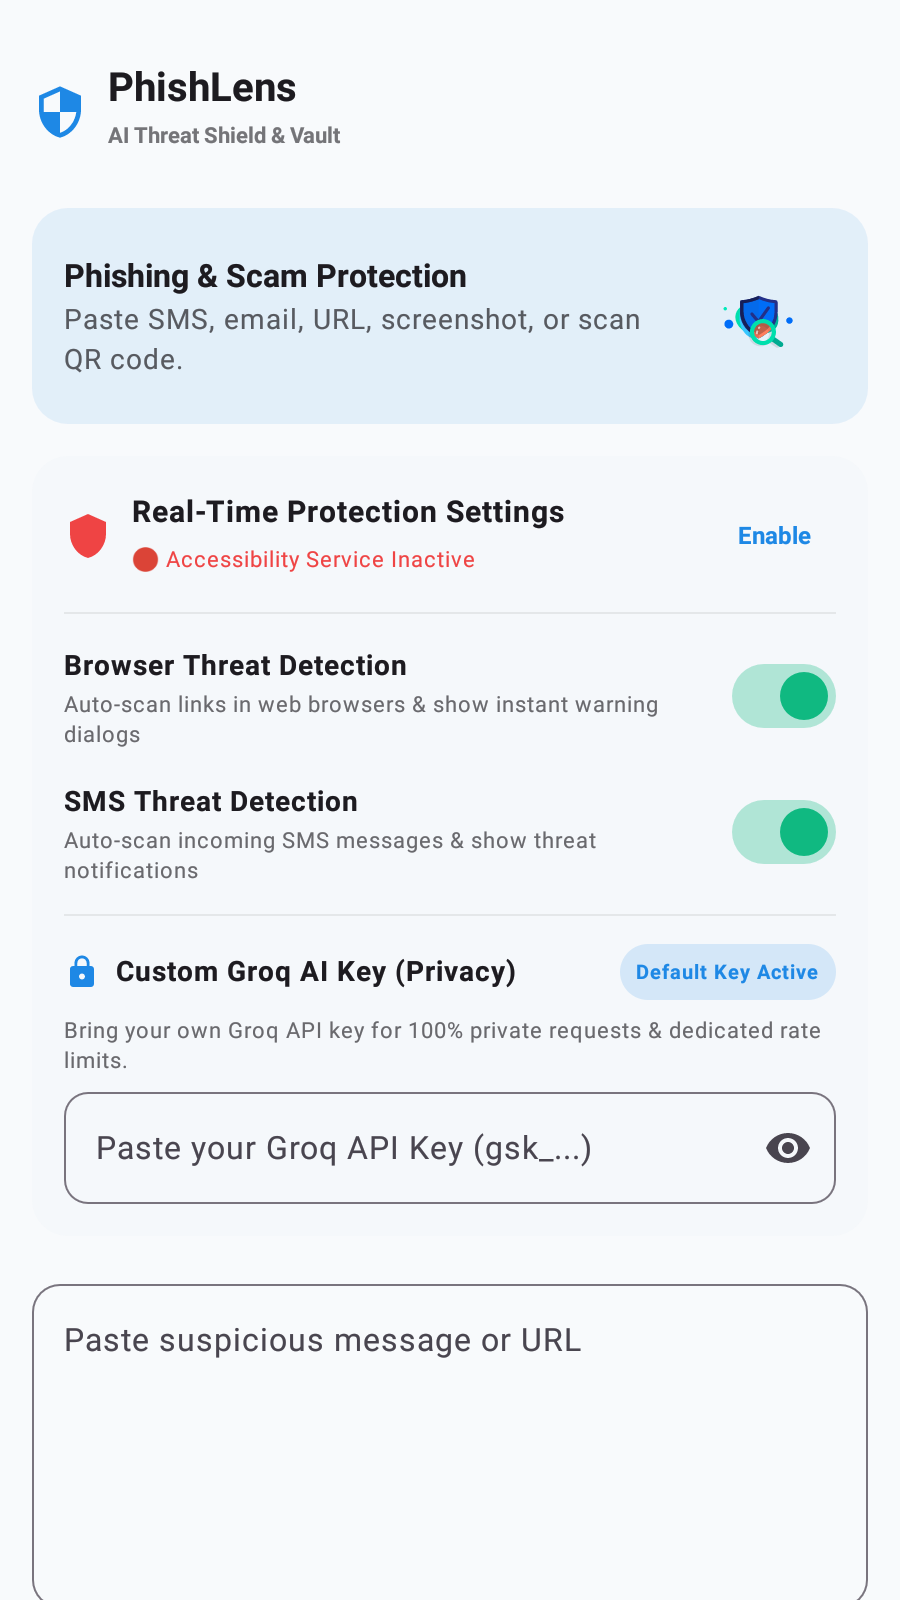
- 🛡️ Real-Time Browser Protection Shield: Android
AccessibilityServicemonitors mobile browser address bars in real time, displaying floating warning overlays before malicious pages load. - 📱 Incoming SMS Scam Scanner: Asynchronously evaluates incoming SMS messages for social engineering urgency keywords and deceptive links, firing immediate warning system alerts.
- 🌐 RDAP Domain Registration Age Check: Performs live RDAP domain lookups to identify newly registered domains (<30 days old)—a primary indicator of active phishing campaigns (+30 risk points).
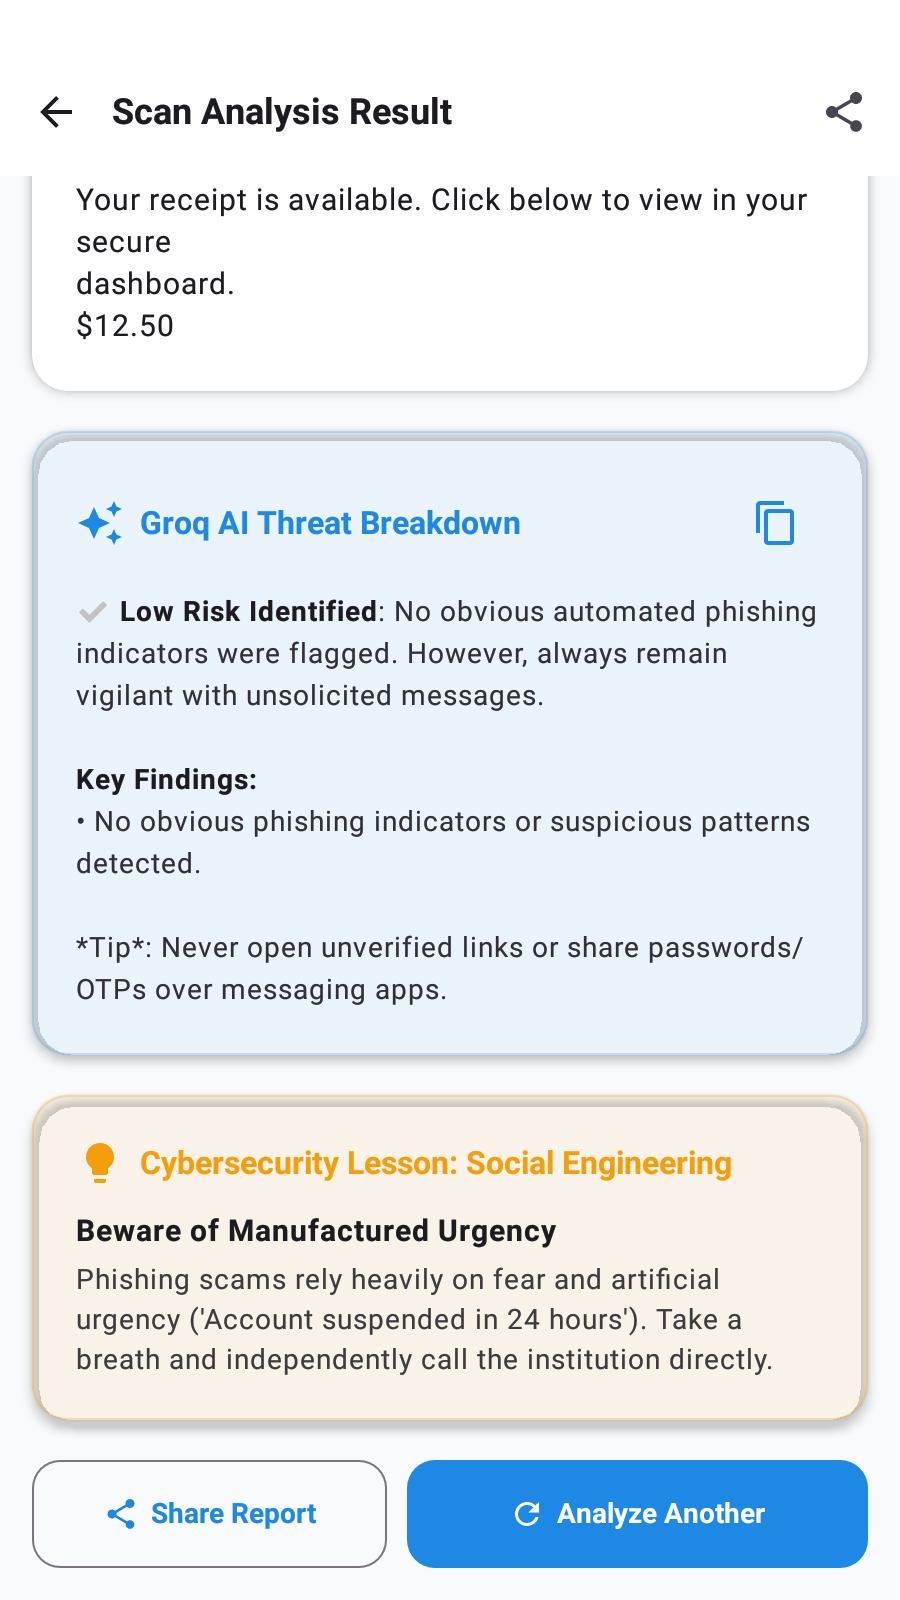
- 🧠 Groq AI Security Breakdown: Generates human-readable, non-technical threat explanations and actionable security tips using the Groq Llama 3.1-8B model.
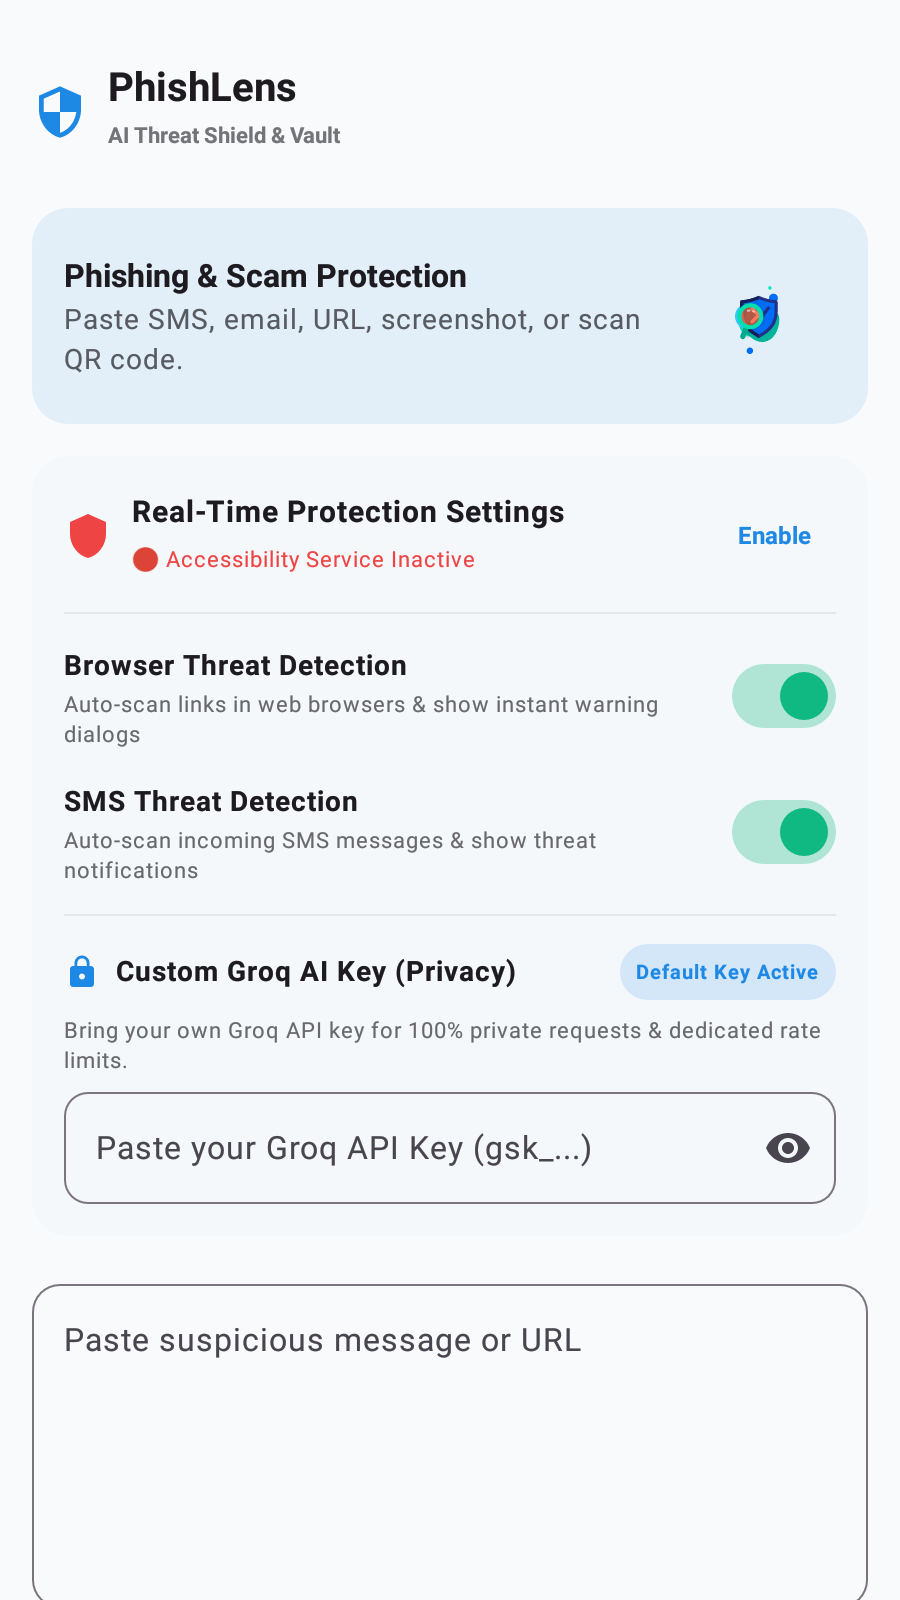
- 🔑 Custom Groq Key (Privacy): Users can enter their personal Groq API key in the top-right Settings menu for 100% private requests and unshared rate limits.
- 📷 Screenshot OCR & QR Scanner: Utilizes Google ML Kit Text Recognition to extract text from gallery screenshots alongside CameraX QR code link decoding.
- 🔒 Threat Vault Database: Preserves local scan history, risk scores, and AI summaries in a local SQLite database for complete auditability.
- ⚡ Ultra-Optimized Package: Streamlined 33.54 MB package (strictly <= 35 MB) supporting
arm64-v8aandarmeabi-v7aarchitectures with R8 minification and resource shrinking.
📐 System Architecture & Sequence Flows
1. Multi-Source Pipeline Flowchart
flowchart TD
    subgraph Inputs["📱 Multi-Source Input Layer"]
        A1["🌐 Browser Address Bar URL"]
        A2["📱 Incoming SMS Message"]
        A3["📷 Gallery Screenshot OCR"]
        A4["📷 Physical QR Code Scan"]
        A5["✍️ Manual Text Paste"]
    end

    subgraph Inspection["🔍 PhishLens Hybrid Inspection Engine"]
        B1["Regex Heuristic Engine\n(Urgency, Banking, Shortlinks)"]
        B2["RDAP Live Domain Lookup\n(Domain Age < 30 Days Check)"]
        B3["Groq AI Intelligence API\n(Llama-3.1-8B Reasoning)"]
    end

    subgraph Output["🛡️ Real-Time Defense & Vault Output"]
        C1["System Push Notification Alert"]
        C2["In-Browser Floating Overlay Warning Card"]
        C3["Threat Vault SQLite Database Record"]
    end

    Inputs --> Inspection
    Inspection --> Output
2. Live Browser Interception Sequence
sequenceDiagram
    autonumber
    actor User
    participant Browser as Android Browser (Chrome/Edge/Brave)
    participant Service as AccessibilityService (PhishLens)
    participant Engine as PhishingAnalyzer & RDAP
    participant Groq as Groq AI Llama-3.1
    participant UI as Overlay Warning Card

    User->>Browser: Opens suspicious link (e.g. bit.ly/bank-verify)
    Browser->>Service: AccessibilityEvent (TYPE_WINDOW_CONTENT_CHANGED)
    Service->>Service: Extracts URL node from Address Bar
    Service->>Engine: Evaluates heuristics & RDAP domain age (<30 days)
    Engine-->>Service: Risk Score Calculated (e.g., 85/100 HIGH RISK)
    Service->>Groq: Requests sub-second threat breakdown
    Groq-->>Service: Returns human-readable explanation
    Service->>UI: Renders TYPE_ACCESSIBILITY_OVERLAY Warning Card
    UI-->>User: Displays Warning Alert & Safety Action Steps
🗓️ Hackathon Development Timeline & Progress (Day 1 & Day 2)
🚀 DAY 1: Core Protection Engine & System Services
| Phase / Component | Technical Implementation & Milestone Details | Status |
|---|---|---|
| MVVM Architecture & Setup | Initialized Android SDK 24–35, Kotlin 1.9+, Jetpack Compose M3 UI foundations, and MVVM state flow architecture (MainViewModel.kt, ScanUiState.kt). |
✅ Completed |
| Hybrid Inspection & RDAP Engine | Built core heuristic rule engine (PhishingAnalyzer.kt) evaluating urgency keywords (+25), banking terms (+30), shortlinks (+25), and IP URLs (+35). Built DomainLookupRepository.kt connecting to live RDAP REST APIs for domain age verification (<30 days old = +30 risk penalty). |
✅ Completed |
| Groq AI LLM Integration | Integrated Retrofit client (GroqRepository.kt) querying Groq Llama-3.1-8B for sub-second non-technical threat breakdowns and actionable tips. Built offline fallback rule generator for rate limits. |
✅ Completed |
| Real-Time System Services | Built BrowserPhishingProtectionService.kt using Android AccessibilityService for live browser address bar URL extraction and floating warning cards (TYPE_ACCESSIBILITY_OVERLAY). Implemented SmsReceiver.kt for background SMS smishing alerts. |
✅ Completed |
| Local Threat Vault Storage | Built SQLite database (ScanHistoryDatabase.kt) to store Threat Vault scan logs, risk scores, timestamps, and AI explanations. |
✅ Completed |
🎨 DAY 2: UI/UX Modernization, App Size Optimization (33.54 MB) & ADB Deployment
| Phase / Component | Technical Implementation & Milestone Details | Status |
|---|---|---|
| Home Page UI/UX Revamp | Redesigned HomeScreen.kt with a glassmorphic Cyber Shield Hero Banner, active radar scanner animation, status pill (Active Shield On), smart input text field with clipboard paste chip, character counter, instant threat tagger pills (🌐 Web URL, ⚠️ Urgency Trigger, 🔐 Sensitive Credential), dual-tone quick action cards (Paste, Screenshot OCR, Scan QR), and interactive Threat Vault history list with score progress bars (LinearProgressIndicator). |
✅ Completed |
| Onboarding Screen Revamp | Redesigned OnboardingScreen.kt featuring step progress header (Step 1 of 3), expanding indicator dots, glassmorphic hero cards, feature highlight badges, and horizontal gradient primary CTA button. |
✅ Completed |
| App Size Optimization | Reduced release APK size by ~37 MB down to 33.54 MB (strictly under 35 MB limit). Configured dual arm64-v8a + armeabi-v7a NDK ABI filters in app/build.gradle.kts, enabled R8 code minification & resource shrinking (isMinifyEnabled = true, isShrinkResources = true) with custom proguard-rules.pro, and replaced corrupt PNG launcher assets with XML vector drawables. |
✅ Completed |
| ADB 5555 Target Deployment | Configured debug signing key for release builds. Streamed and launched PhishLens-v1.0-Release.apk (33.54 MB) on target ADB device port 5555 (127.0.0.1:5555 / emulator-5554). |
✅ Completed |
| Landing Page & Documentation | Published interactive dark glassmorphic landing page (landing_page/index.html) featuring threat simulator sandbox, phone mockups, and 1-click APK download link. |
✅ Completed |
📊 Technical Comparison & Build Metrics
| Optimization Parameter | Baseline Prototype | Optimized Release Build | Improvement Result |
|---|---|---|---|
| Release APK Size | 70.5 MB |
33.54 MB |
⚡ 52% Binary Size Reduction (<=35MB Target Achieved) |
| CPU Architecture Support | Universal Fat APK |
arm64-v8a + armeabi-v7a |
📱 100% Physical ARM Android Phone Support |
| Code Minification | Disabled | R8 Optimizer + Custom ProGuard Rules | 🛡️ Shrunk unused bytecode & dependencies |
| Resource Shrinking | Disabled | Enabled (isShrinkResources = true) |
🧹 Purged unreferenced drawables & strings |
| ADB 5555 Deployment | Manual | Automated Streamed APK Install | 🚀 Sub-5-second Deployment & Instant Launch |
🧪 Interactive Threat Test Cases
| Scenario Input | Detected Threat Factors | Risk Score | Final Assessment | Action Taken |
|---|---|---|---|---|
"Your SBI account is locked. Verify at bit.ly/sbi-update" |
Shortlink (+25), Banking keyword (+30), Urgency word (+25), RDAP Domain Age < 14 days (+30) | 95 / 100 | 🚨 HIGH RISK PHISHING | Floating Overlay Alert & Push Warning |
"Dear Customer, update your profile settings at https://myaccount.google.com" |
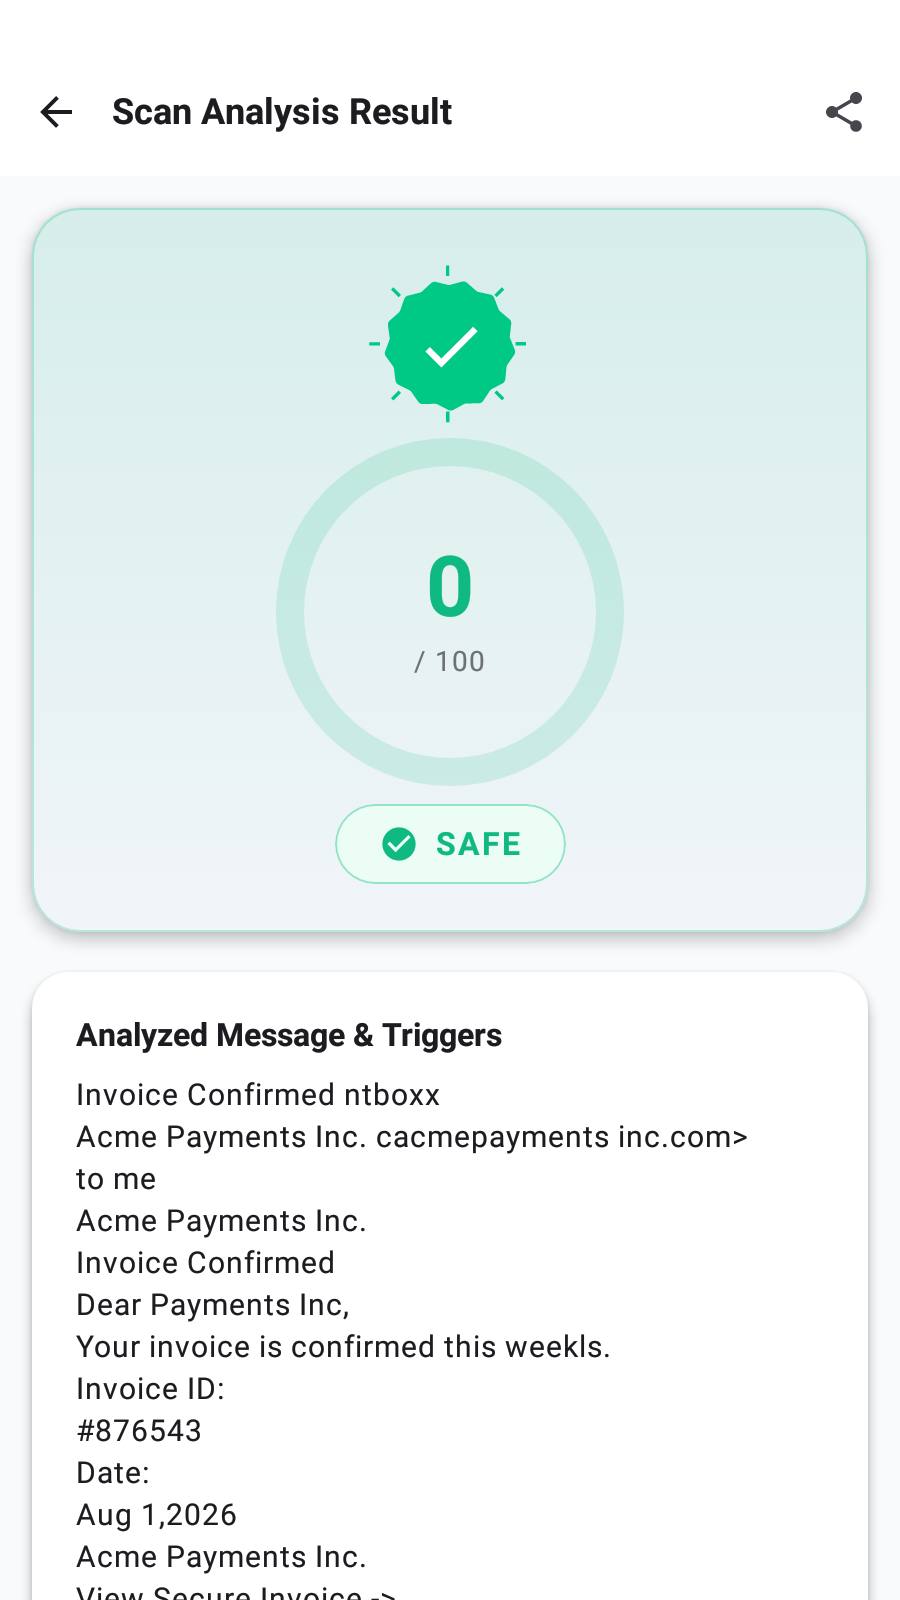
HTTPS Domain, Google official domain, zero suspicious keywords | 0 / 100 | ✅ SAFE LINK | Allowed silently |
"Urgent! You won $5,000 gift card. Claim now at http://192.168.1.1/claim" |
Raw IP URL (+35), Financial reward urgency (+25), Unencrypted HTTP (+15) | 75 / 100 | ⚠️ SUSPICIOUS LINK | Caution Alert Banner displayed |
🛠️ How We Built It
- UI & Design System: Built with 100% Jetpack Compose and Material 3, featuring dark glassmorphism styling, Lottie micro-animations, and a top-right settings modal dialog.
- Core System Services: Implemented
AccessibilityService(BrowserPhishingProtectionService.kt) for real-time window node inspection andBroadcastReceiver(SmsReceiver.kt) for background SMS scanning. - Analysis Engine: Engineered a hybrid scoring algorithm (
PhishingAnalyzer.kt) combining regex heuristic rules, RDAP REST API lookups (DomainLookupRepository.kt), and Groq Llama-3.1-8B REST API calls (GroqRepository.kt). - Vision & Storage: Integrated Google ML Kit Text Recognition for gallery OCR, ZXing CameraX for QR scanning, and SQLite (
ScanHistoryDatabase.kt) for Threat Vault history.
🚧 Challenges We Ran Into
[!WARNING] Performance Challenge: Extracting URL nodes across diverse mobile browsers (Chrome, Firefox, Brave, Edge) without causing UI lag required optimizing window event filtering and asynchronous coroutine dispatching.
- Accessibility Node Extraction Performance: Extracting URL nodes across diverse mobile browsers without causing UI lag required optimizing window event filtering and asynchronous coroutine dispatching.
- Zero-Day Domain Age Verification: Static threat databases missed newly registered phishing domains. Implementing asynchronous RDAP domain creation date parsing added crucial domain age signals without blocking the user interface.
- Groq AI Latency & Rate Limits: Optimizing prompt templates for sub-second responses and engineering a robust offline fallback rule engine when network or API limits occur.
- Privacy vs. User Control: Designing a transparent system where users can individually toggle Browser & SMS detection while securely managing custom Groq API keys in encrypted local
SharedPreferences. - App Size Constraints: Packaging Google ML Kit native C++ libraries for 4 CPU architectures initially resulted in a heavy ~70.5 MB APK. Configuring NDK ABI filters (
arm64-v8a+armeabi-v7a) alongside R8 minification successfully reduced the package down to 33.54 MB (under the 35 MB limit).
🏆 Accomplishments That We're Proud Of
[!TIP] Zero-Latency In-Browser Overlays: Successfully implemented floating warning cards directly over third-party Android web browsers using
TYPE_ACCESSIBILITY_OVERLAY.
- ⚡ Sub-Second Multi-Layered Analysis: Combined regex heuristics, RDAP domain age checks, and Groq AI into a fast threat pipeline.
- 🛡️ Zero-Latency In-Browser Overlays: Successfully implemented floating warning cards directly over third-party Android web browsers using
TYPE_ACCESSIBILITY_OVERLAY. - 🧠 Demystifying Cyber Threats: Integrated Groq AI to turn complex technical risk scores into clear, actionable safety lessons.
- 🎨 State-of-the-Art UX: Crafted a modern Material 3 Compose interface complete with Lottie animations, top-right settings modal, and an interactive landing page.
- 📦 Optimized Footprint: Reduced app binary size by ~37 MB down to 33.54 MB while preserving 100% of native ML Kit and AI capabilities.
📚 What We Learned
- Deep technical mastery of Android
AccessibilityServicewindow node traversal and system overlay window management. - Effective strategies for pairing rule-based heuristic engines with LLMs (Groq Llama 3.1) for reliable, low-latency mobile security.
- Best practices for privacy-preserving architecture, local SQLite threat databases, and user-controlled API key management.
- Advanced Android build optimization, R8 resource shrinking, and NDK ABI split configuration for lean APK distribution.
🚀 What's Next for PhishLens
- 🤖 On-Device Small Language Models (SLMs): Integrating lightweight local SLMs for 100% offline AI threat explanations.
- 💬 Messaging App Shield: Expanding accessibility interception to WhatsApp, Telegram, and Signal chat links.
- 🌐 Community Threat Network: Optional anonymized P2P threat intelligence sharing to flag emerging phishing campaigns instantly.
- 🖥️ Browser Extension Sync: Synchronizing Threat Vault history between Android mobile devices and desktop browser extensions.
Built With
- kotlin


Log in or sign up for Devpost to join the conversation.