-
-
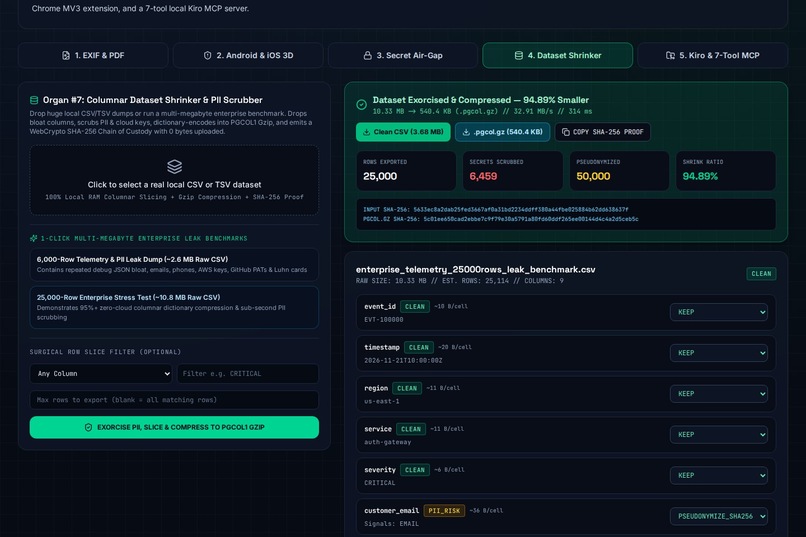
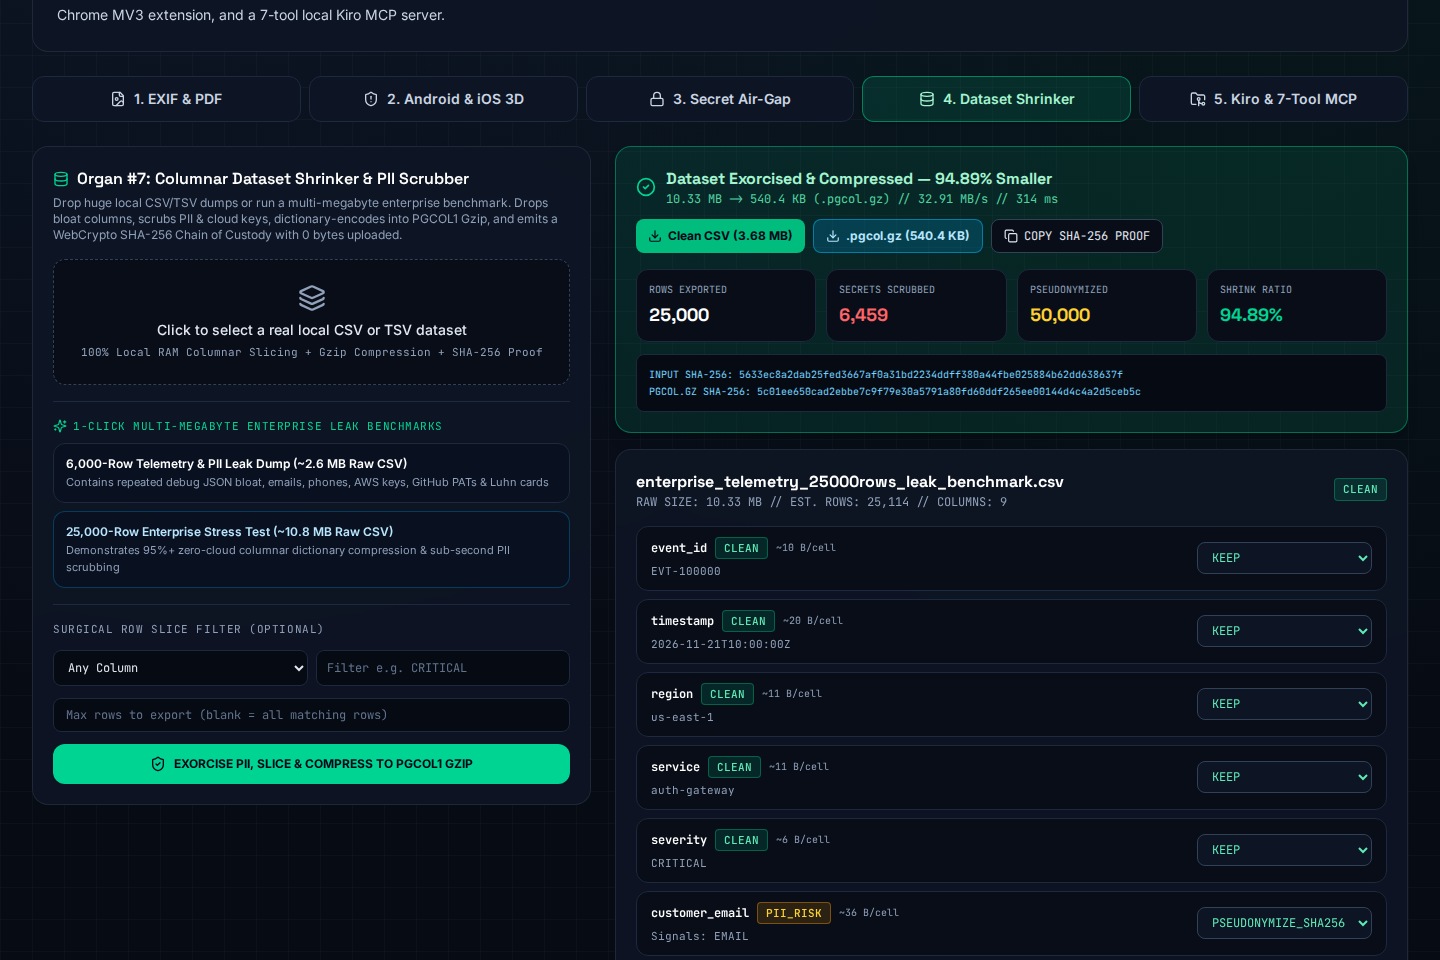
Organ #7 Columnar CSV Shrinker: 10.33 MB -> 540.4 KB (94.89% smaller in 314 ms) + SHA-256 Chain of Custody
-
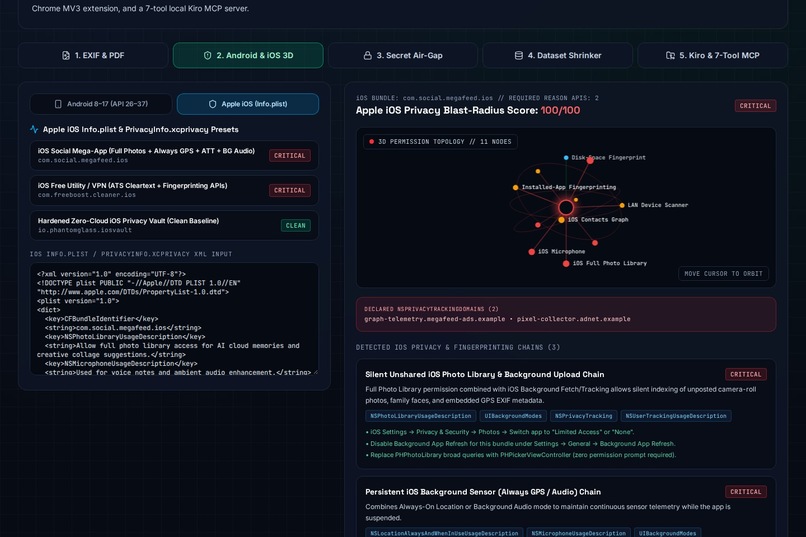
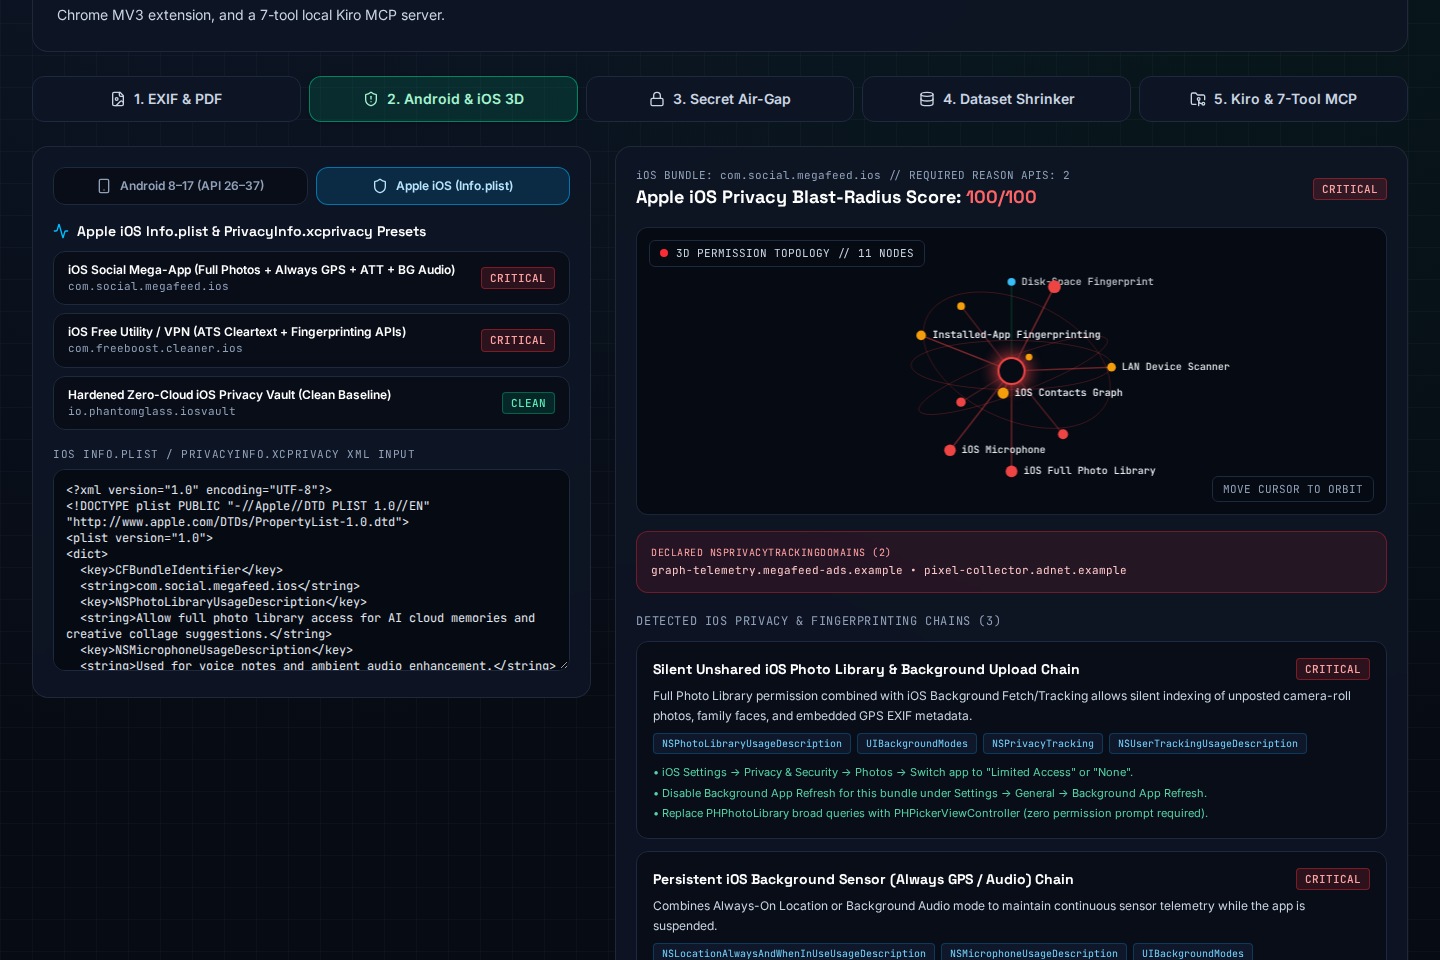
Apple iOS Info.plist & PrivacyInfo.xcprivacy 3D Audit + ATT/ATS Detection
-
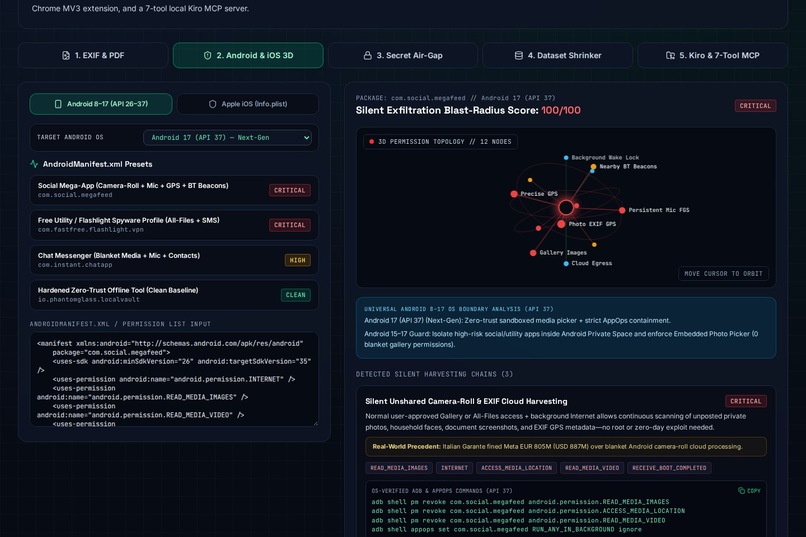
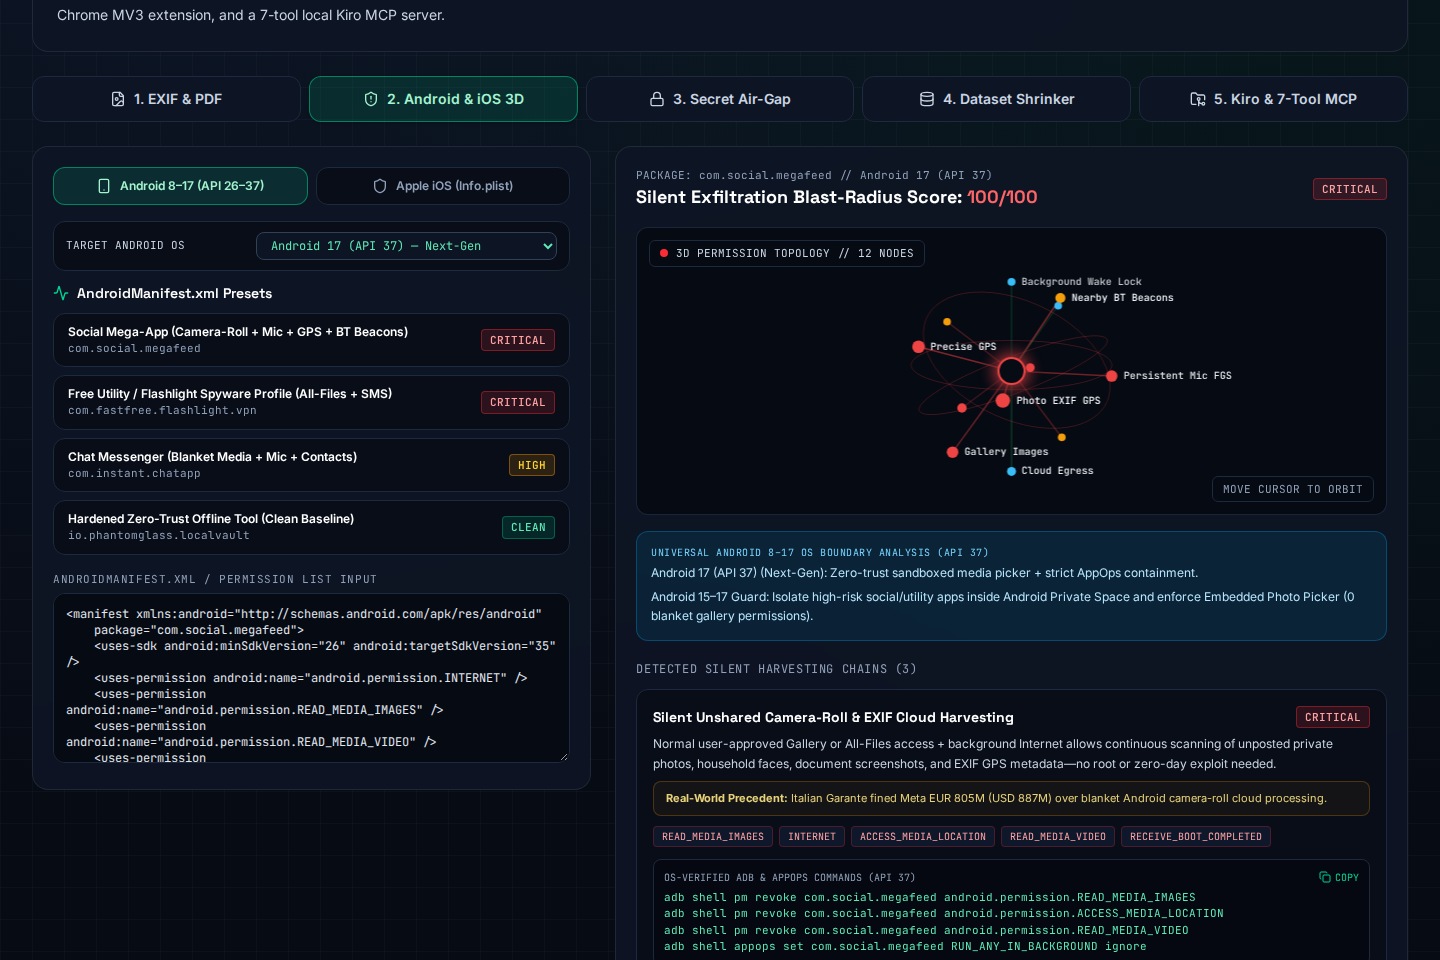
Universal Android 8-17 (API 37) OS Boundary Analysis & AppOps Hardening
-
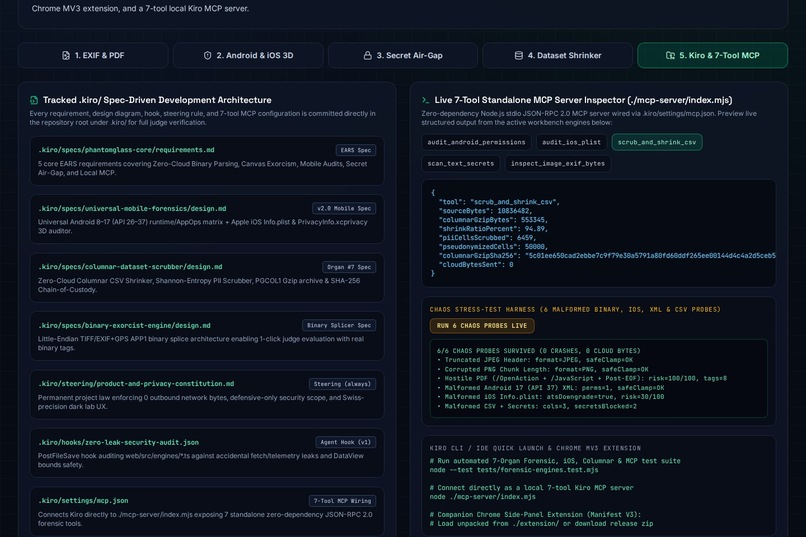
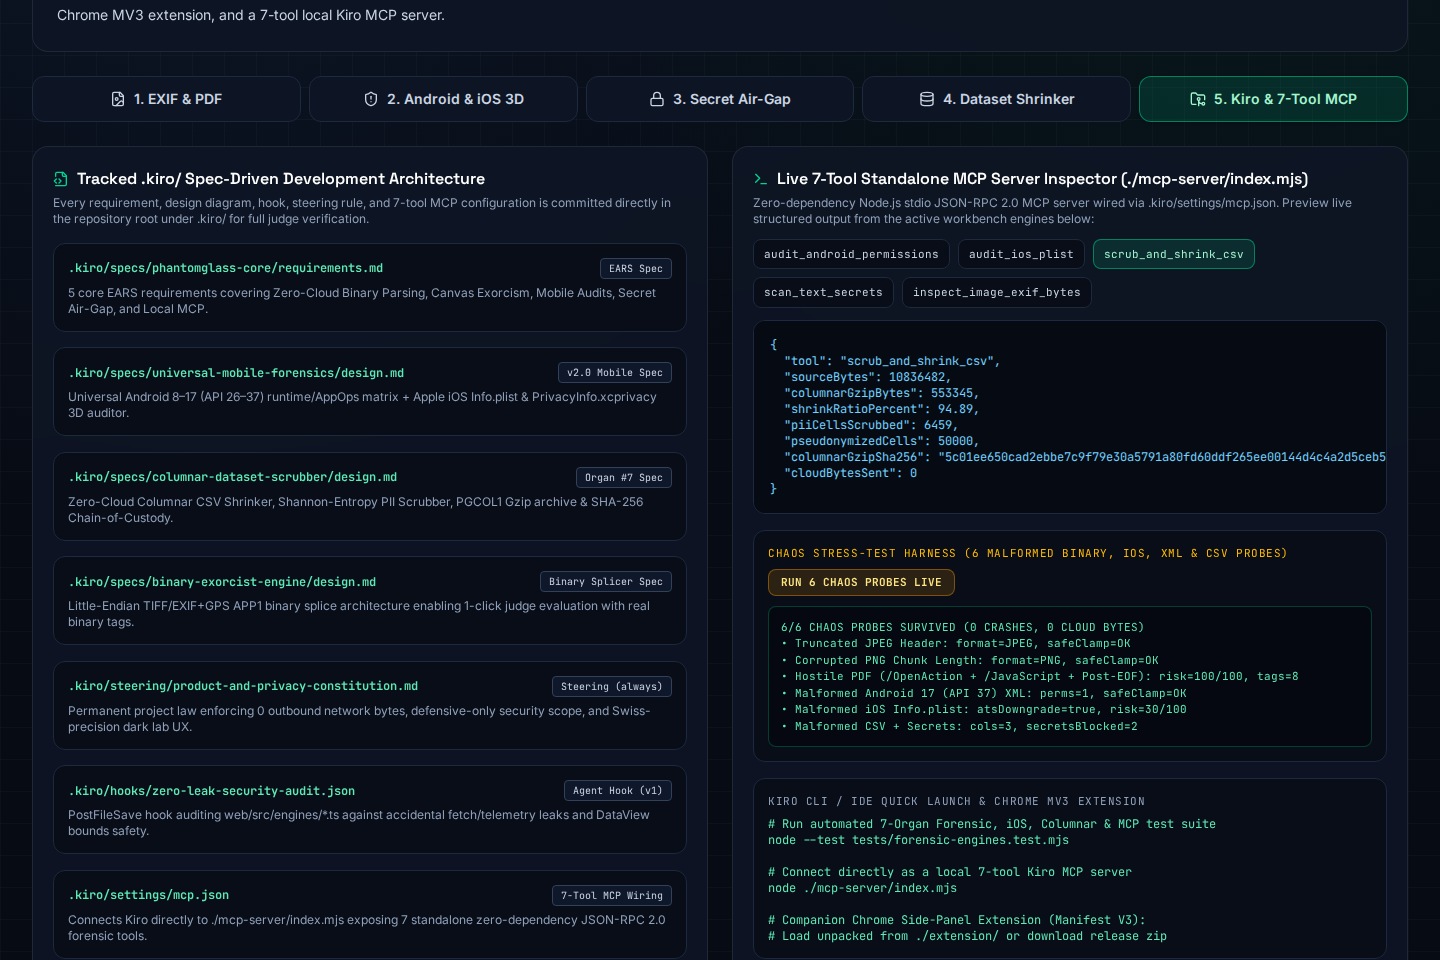
Tracked .kiro/ Specs, Steering, Hooks, 7-Tool MCP Inspector & 6/6 Chaos Probes
-
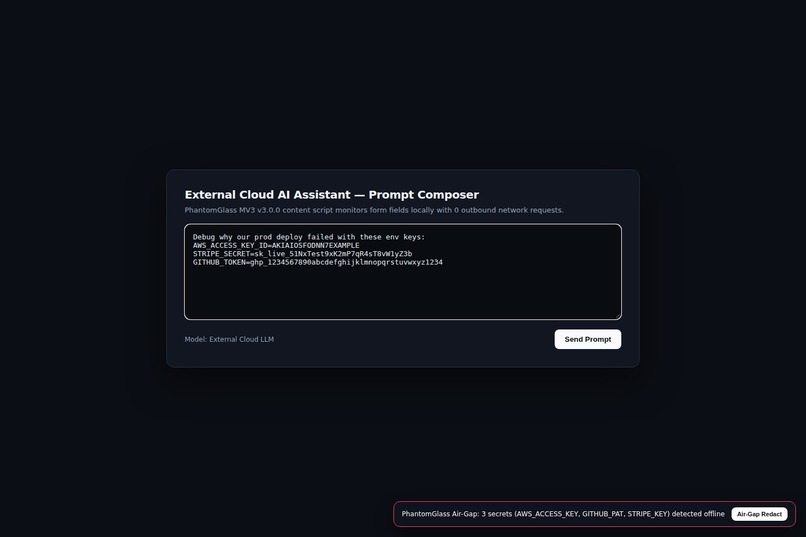
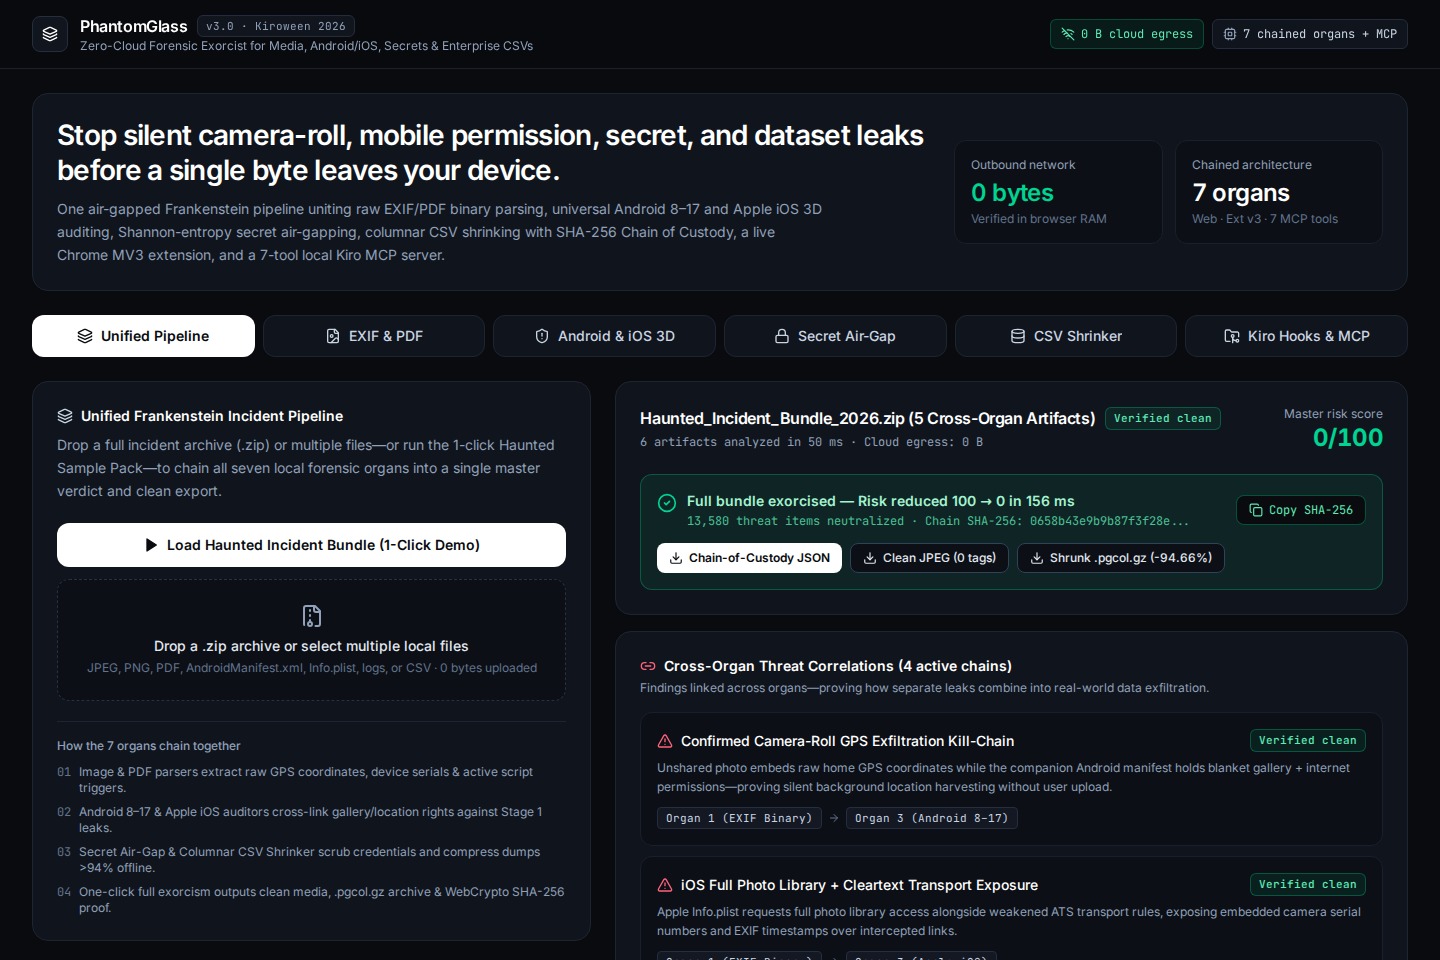
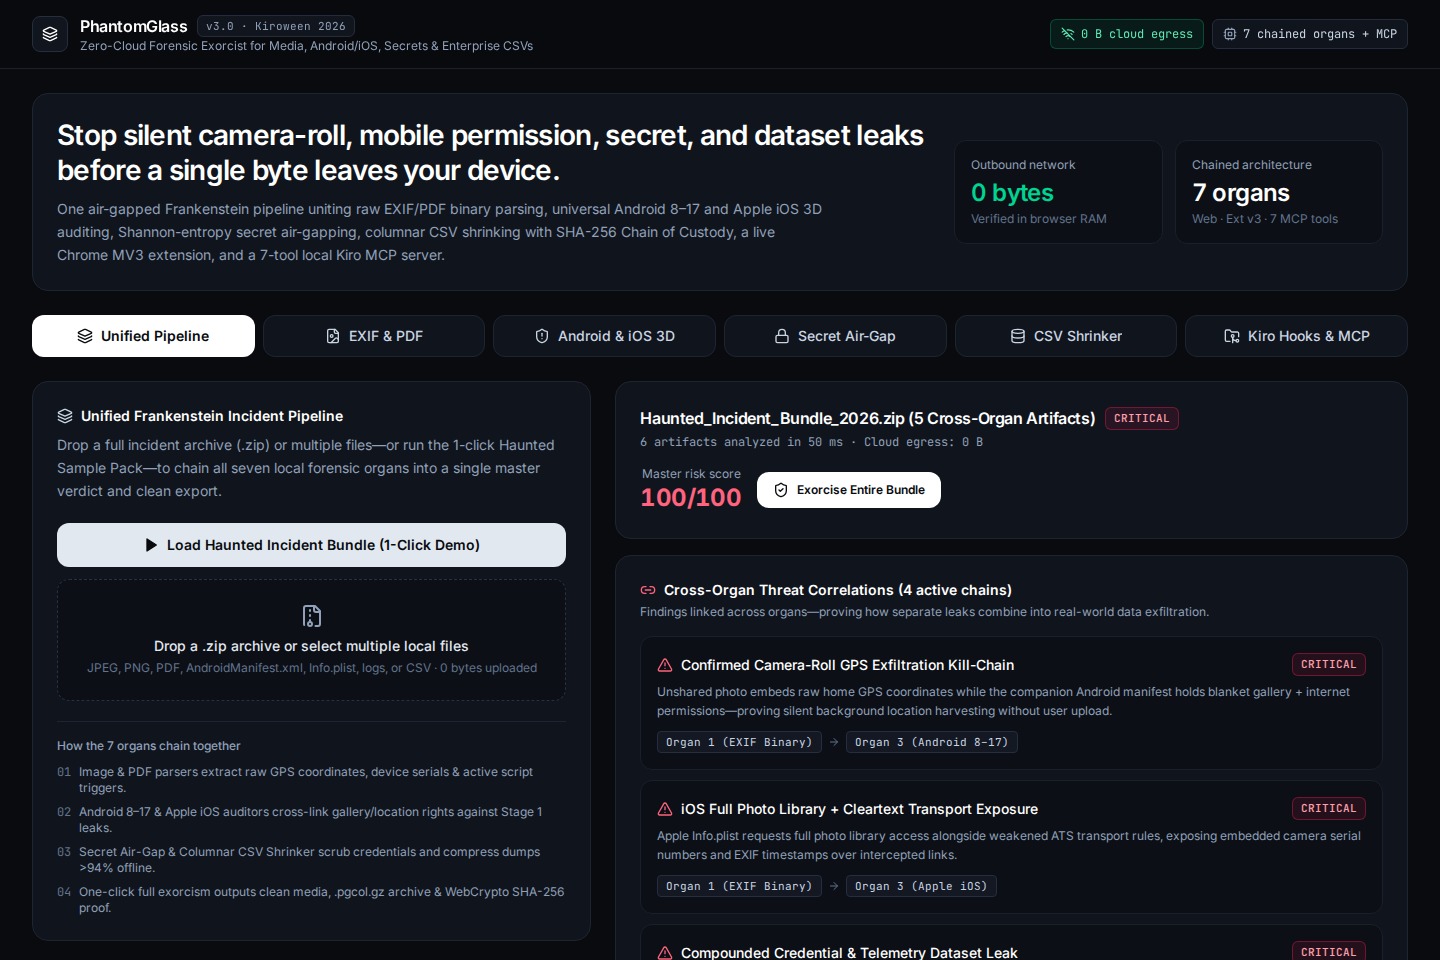
Unified 7-Organ Frankenstein Incident Pipeline — 1-Click Haunted Bundle (Risk 100/100)
-
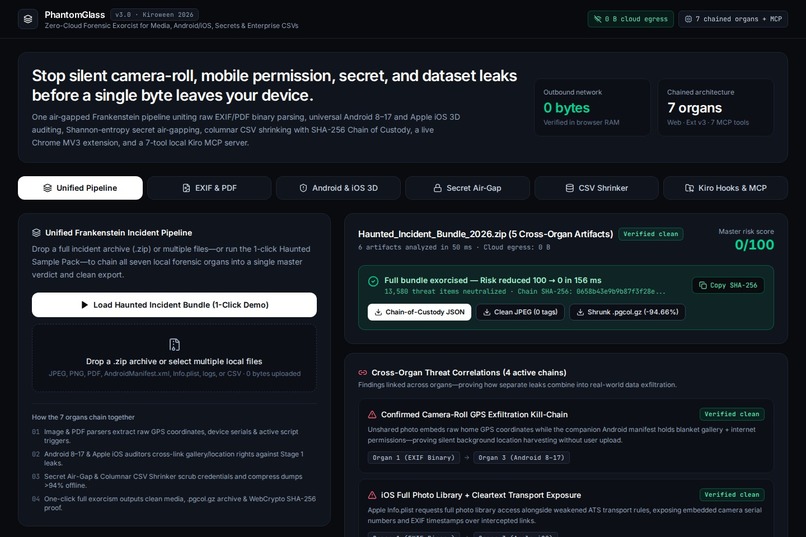
1-Click Full Exorcism — 13,580 Threats Neutralized in 156 ms (Risk 100 -> 0 + SHA-256 Receipt)
-
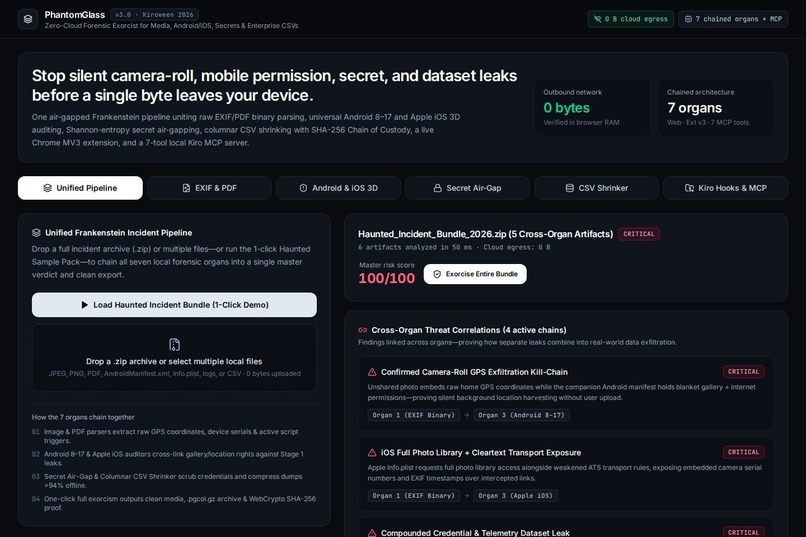
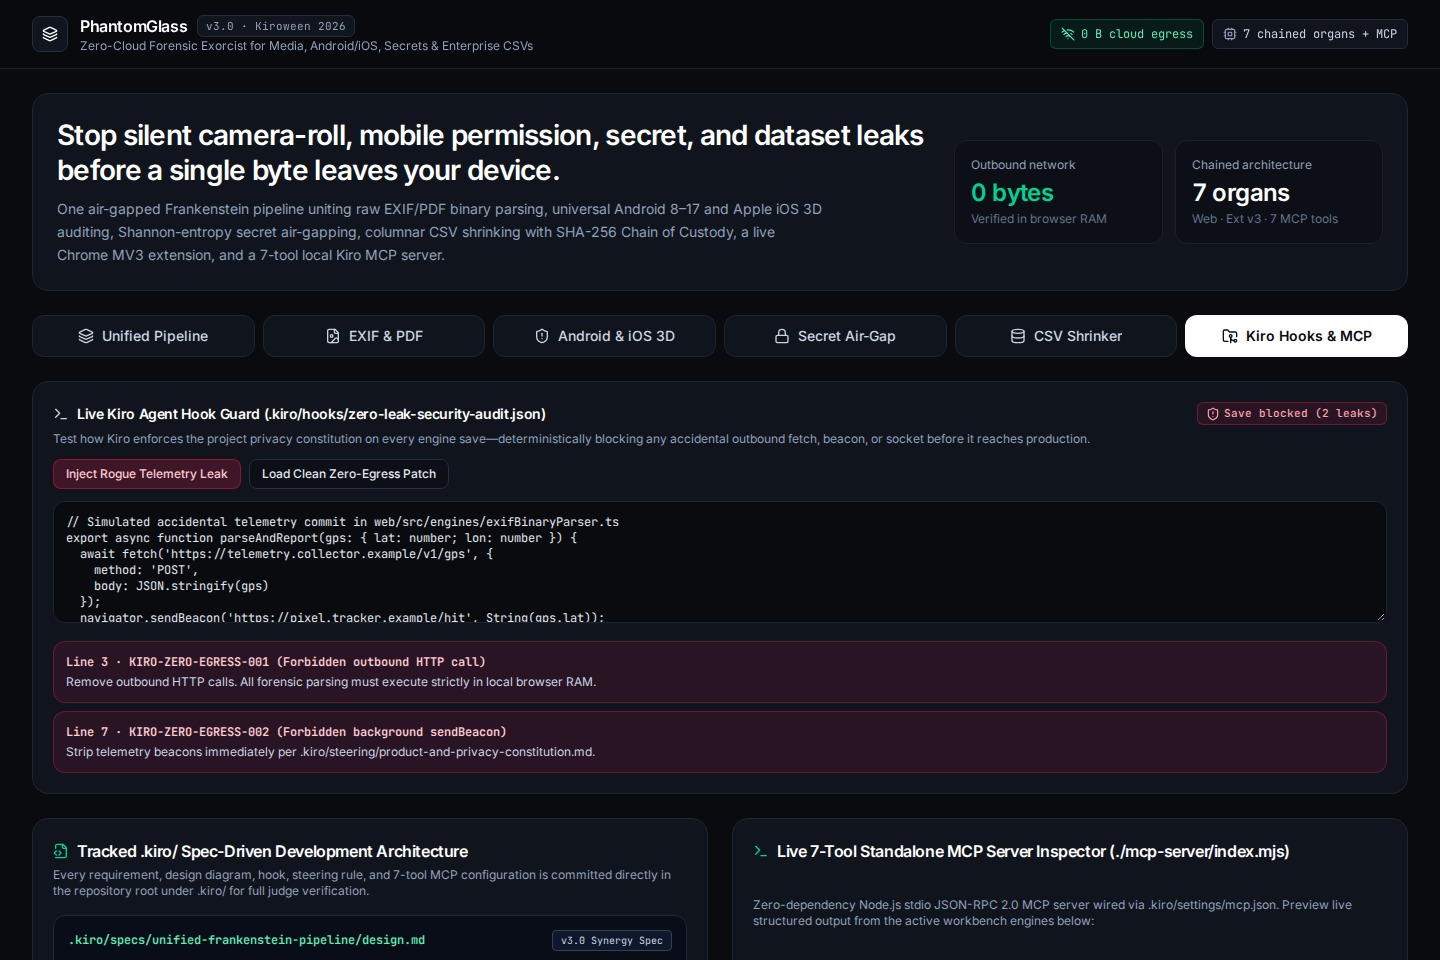
Live Kiro Agent Hook Guard (.kiro/hooks) Blocking Outbound fetch() & sendBeacon() on Save
-
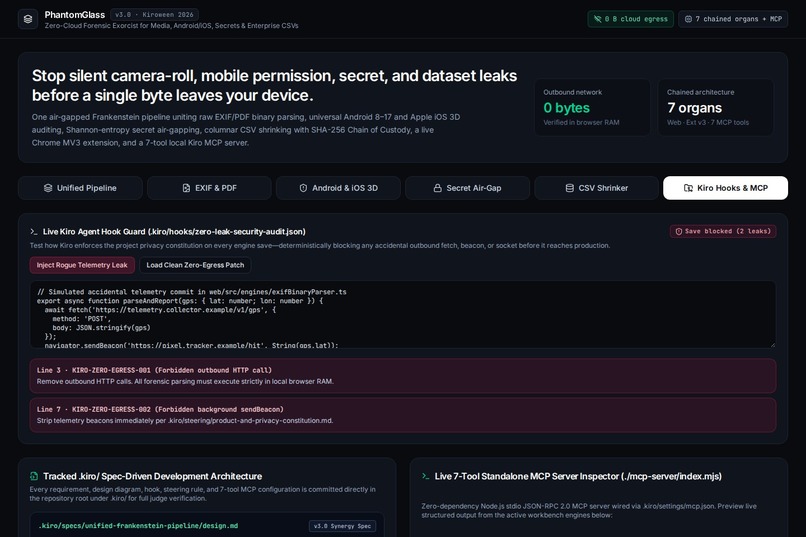
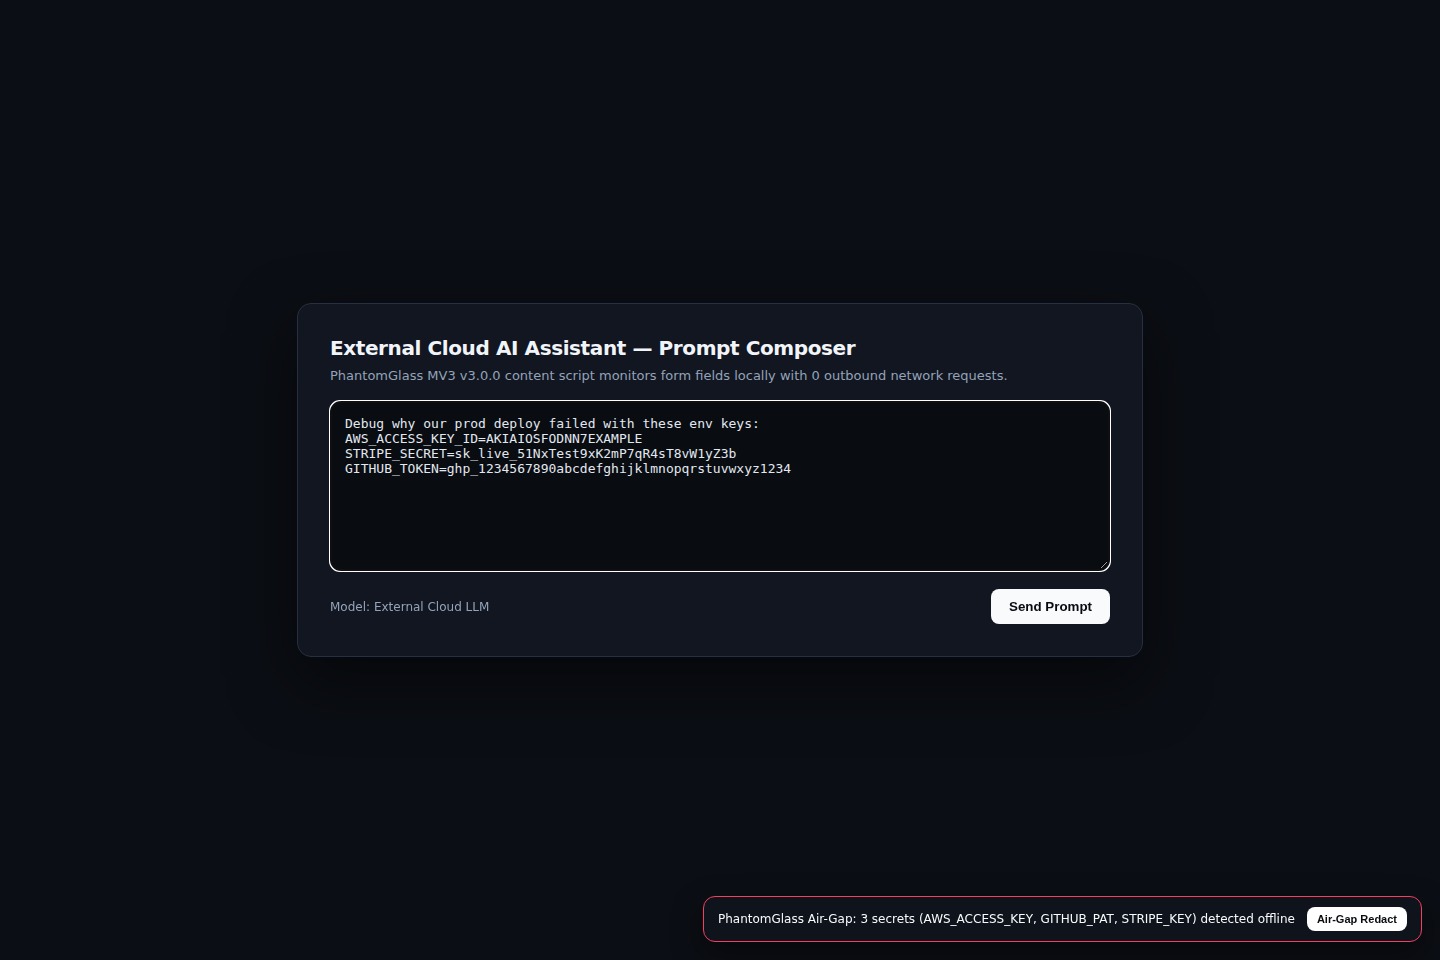
Chrome Manifest V3 v3.0.0 Extension — Inline Webpage AI Prompt Air-Gap Redaction
Live HTTPS App (v3.0 — Zero Cloud Egress): jashory.github.io/phantomglass-kiroween | Chrome MV3 Extension v3.0.0 Release: GitHub Release v3.0.0 | Open-Source Repo + Full
.kiro/Tree: github.com/jashory/phantomglass-kiroween
Inspiration — Real-World Silent Mobile & Cloud Data Leaks
Modern mobile apps and cloud AI tools rarely need root access to harvest private user or enterprise data. A single blanket Gallery, Microphone, or Location permission allows background services to scrape unposted camera-roll photos, GPS coordinates, and financial screenshots—while engineers routinely paste live AWS, Stripe, and GitHub keys into browser AI prompts or upload bloated multi-gigabyte CSV logs containing PII.
PhantomGlass v3.0 is a Frankenstein-category defensive security laboratory built with Kiro, stitching seven independent forensic organs into one unified, offline, zero-cloud pipeline (0 outbound bytes).
True Frankenstein Synergy: Unified 7-Organ Incident Pipeline (v3.0)
Instead of forcing investigators or judges to hop across disconnected utilities, PhantomGlass v3.0 launches directly into the Unified Frankenstein Incident Pipeline:
1-Click Haunted Incident Bundle (Zero-Effort Judge Demo) & Client-Side
.zip/ Multi-File Drop: Click Load Haunted Incident Bundle (or drop a local.ziparchive or mixed.jpg,.pdf,.xml,.plist,.csv,.envfiles) to execute all 7 organs in one chained pass:- Organ #1 — Raw Binary EXIF/GPS & Post-EOI Microscope (
exifBinaryParser.ts): Bounds-checkedDataViewparser extracting JPEG APP1 TIFF/EXIF IFD0, GPS coordinates (23.1667 N, 89.2081 E), camera serials, PNG chunks, and hidden post-EOI/IEND trailing payloads directly in browser RAM. - Organ #2 — Cryptographic Pixel & Metadata Exorcist (
mediaExorcist.ts): Re-encodes pixel buffers through an offscreen HTML5 Canvas, then independently re-parses the output through Organ #1 to prove0EXIF tags,0GPS coordinates, and0trailing bytes remain. - Organ #3 — Universal Mobile Privacy Forensics (Android 8–17 + Apple iOS
Info.plist) & 60fps 3D Topology: Audits Android API 26–37 manifests and Apple iOSInfo.plist/PrivacyInfo.xcprivacy, cross-correlating blanket permissions against Organ #1 GPS leaks and emitting exactadb shell pm revoke+ hardenedPrivacyInfo.xcprivacypatches. - Organ #4 — Shannon-Entropy & Luhn Secret Air-Gap (
secretAirGapEngine.ts): Scrubs AWS/GitHub/Stripe/Slack keys, private keys, Luhn payment cards, IBANs, and high-entropy credentials strictly in local RAM. - Organ #5 — PDF Binary
/OpenAction,/JavaScript& Post-%%EOFMicroscope (pdfForensicEngine.ts): Inspects raw PDF bytes for auto-exec scripts and covert trailing streams without cloud upload. - Organ #6 — Chrome MV3 v3.0.0 Inline Webpage Air-Gap Extension (
extension/content.js) & 7-Tool Standalone Kiro MCP Server (mcp-server/index.mjs): Detects credentials pasted into live webpage<textarea>/contenteditableAI prompts and displays a floating Air-Gap Redact banner for 1-click local in-place redaction before text ever leaves the browser—paired with a zero-dependency JSON-RPC 2.0 stdio MCP server. - Organ #7 — Forensic Columnar Dataset Shrinker & WebCrypto SHA-256 Chain of Custody (
columnarScrubberEngine.ts): Scrubs PII/secrets from CSV dumps, dictionary-encodes and gzip-compresses them into.pgcol.gzarchives (94%+smaller), and signs a unified WebCrypto SHA-256 Chain-of-Custody Attestation JSON (cloudBytesSent: 0).
- Organ #1 — Raw Binary EXIF/GPS & Post-EOI Microscope (
Cross-Organ Kill-Chain Correlations & 1-Click Full Exorcism: Automatically correlates threats across files (e.g., Confirmed Camera-Roll GPS Exfiltration Kill-Chain linking Organ #1 GPS JPEG + Organ #3 Android
READ_MEDIA_IMAGES+INTERNET). Clicking Exorcise Entire Bundle neutralizes all 7 organs simultaneously (Risk100 -> 0in156 ms,13,580threat items neutralized) and unlocks instant download of clean JPEG, shrunk.pgcol.gz, and signed Chain-of-Custody JSON.
How We Built It with Kiro (Tracked .kiro/ + Interactive Live Hook Guard)
Every Kiro spec, steering rule, MCP config, and PostFileSave hook lives cleanly in .kiro/ at repository root:
- Interactive Live Kiro Agent Hook Guard (Tab 5 —
Kiro Hooks & MCP): Judges can click Inject Rogue Telemetry Leak to test.kiro/hooks/zero-leak-security-audit.jsonlive in the browser—watching Kiro immediately block accidentalfetch()ornavigator.sendBeacon()calls with exact line diagnostics (KIRO-ZERO-EGRESS-001,KIRO-ZERO-EGRESS-002). - Specs:
.kiro/specs/unified-frankenstein-pipeline/design.md,phantomglass-core/,universal-mobile-forensics/,columnar-dataset-scrubber/,binary-exorcist-engine/. - MCP Integration:
.kiro/settings/mcp.jsonwiresphantomglass-forensics(node ./mcp-server/index.mjs) exposing 7 deterministic local security tools.
Real-World Cloud VM & Cloud Android 14 (API 34) Verification
- Live HTTPS Web App v3.0 (Cloud Ubuntu Chromium): Verified
0console errors,0third-party outbound network bytes,0mobile horizontal overflow, Risk100 -> 0full exorcism, and live Kiro Hook rogue telemetry blocking. - Live Chrome MV3 Extension v3.0.0 (
--load-extensionin Cloud Chromium): Verified floating#phantomglass-live-airgap-bannerdetection and 1-click inline redaction of AWS, Stripe, and GitHub credentials on a live webpage prompt form. - Cloud KVM Android 14 (API 34) Emulator: Executed all 5 PhantomGlass-generated
adb shell pm revoke&appops setcommands against a signed test APK with5/5 EXIT CODE 0and verifiedgranted=false.
Built With
- android
- chrome
- cybersecurity
- frankenstein
- ios
- kiro
- kiroween
- mcp
- privacy
- react
- typescript
- zero-trust
