-
-
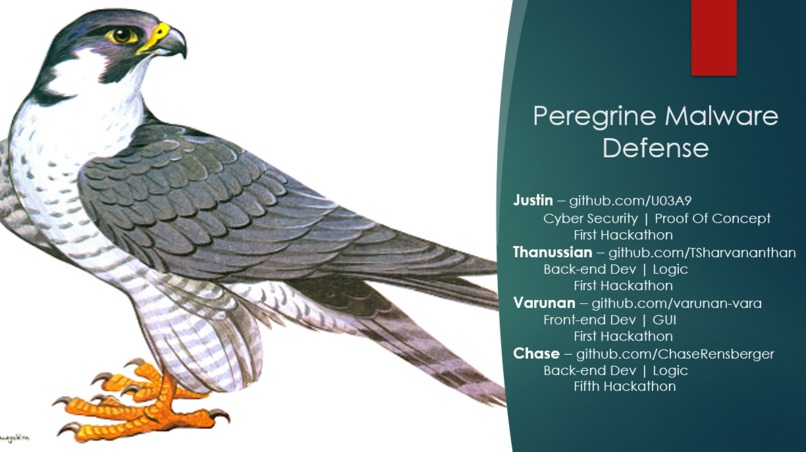
Team mates

Inspiration
This concept came to fruition after watching multiple people come into the Tech Haven discord complaining about different security issues. Anything from token stealers to IP grabbers or even RATs being downloaded by unsuspecting members.
In order to really run this idea home, I think it’s important to frame the problem we’re trying to address: Discord is a sort of breeding ground for phishing and malicious activity against otherwise uninformed end users. Bad actors are constantly posting malicious executables, fake nitro gift alerts, token stealers, and IP grabbing phishing sites. Sometimes, the goal is to compromise a system with a RAT (Remote Access Trojan), and other times it’s to steal Discord account tokens from administrators in order to take over a Discord server. Immediately after getting into contact with my team members and explaining the vision and goals of the bot, these professionals instantly saw opportunities to apply best practices to not only improve the code behind the bot, but also ways to improve accessibility and reliability through implementing a GUI and the potential of implementing a database to store past results. Improving runtime, responsiveness, and making it easier to add new features in the future.
What it does
This bot listens for URLs posted in a Discord server and submits them to the Hybrid-Analysis website from CrowdStrike.
How I built it
The bot is written in Python and was quickly jumbled together at the start of this hackathon so that I could provide a Proof of Concept to developers, so it was far from ready for actual use let alone at scale. This is now being cleaned up and brought in line with better practices by our back end developers, and a GUI has been developed by our front end developer using JavaScript and React. We are utilizing Discord.py library to handle the bot and the VxAPI.py library to make calls to the HybridAnalysis API.
Challenges I ran into
The biggest challenge I ran into was coding the bot itself. While I was able to get a working PoC to demo to our team, I was making calls to the API in a way that was neither optimized nor best practice. Another challenge I ran into was integrating the code in a way that it could handle a mass of URLs in one post, multiple URLs at a given time, and reliably updating the message blocks.
Accomplishments that I'm proud of
I'm proud of how quickly this group of strangers came together and rallied behind the concept. Personally, I've learned quite a bit about how AWS works and more about JSON data than I knew previously. Being a holiday weekend we quickly worked together to push this project into a state where we can showcase it to you all.
What I learned
Personally, I've learned quite a bit about AWS, JSON data structures, NoSQL tables, and best practices related to file structure and efficiency in Python code.
What's next for Peregrine Discord Bot
We have a whole list of ideas for features to add to the bot. Our first focus will be adding in both a static and custom whitelist to reduce bot intervention on known good websites, followed by implementing a NoSQL database that we can query for previously scanned URLs, track user behaviors, and provide more actionable data to Discord administrators.
--- KEEP IN MIND THAT IF YOU CHOOSE TO RUN THIS CODE YOU WILL NEED A DISCORD DEVELOPER BOT WITH A TOKEN AND A HYBRID ANALYSIS PUBLIC API TOKEN FOR THE CONFIGURATION FILES. THESE TOKENS HAVE BEEN SCRUBBED FOR SECURITY ---


Log in or sign up for Devpost to join the conversation.