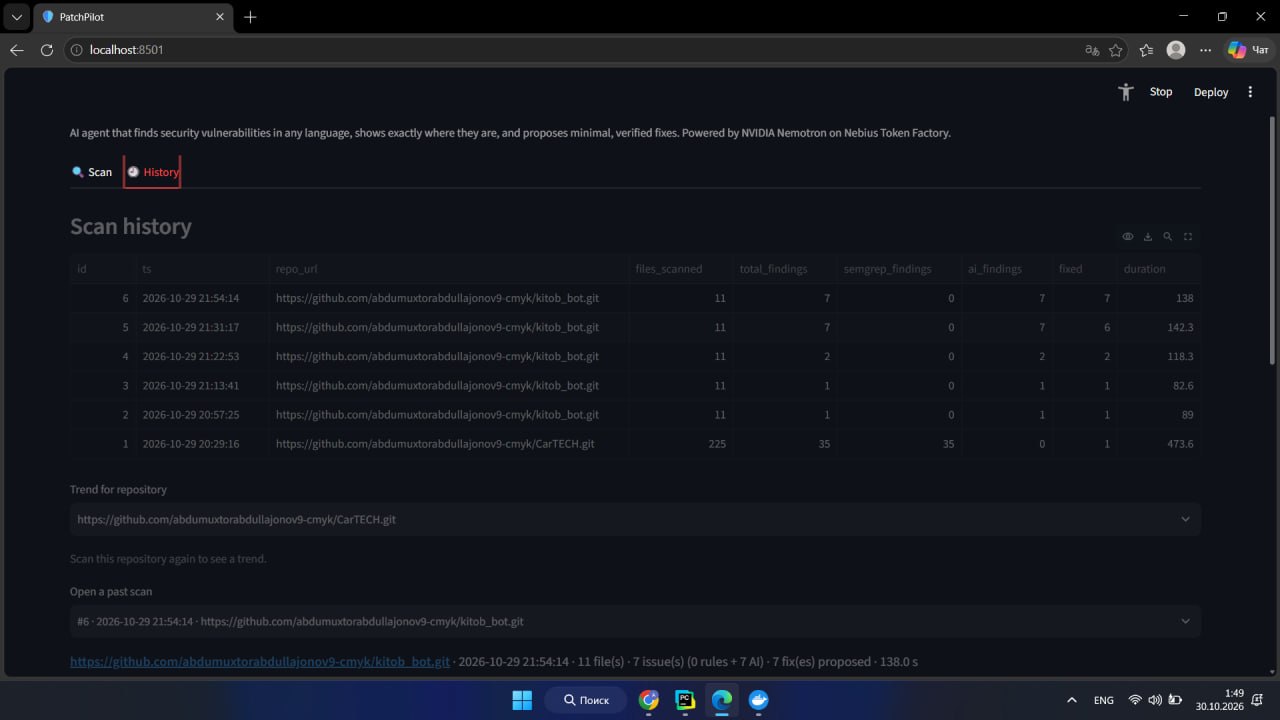
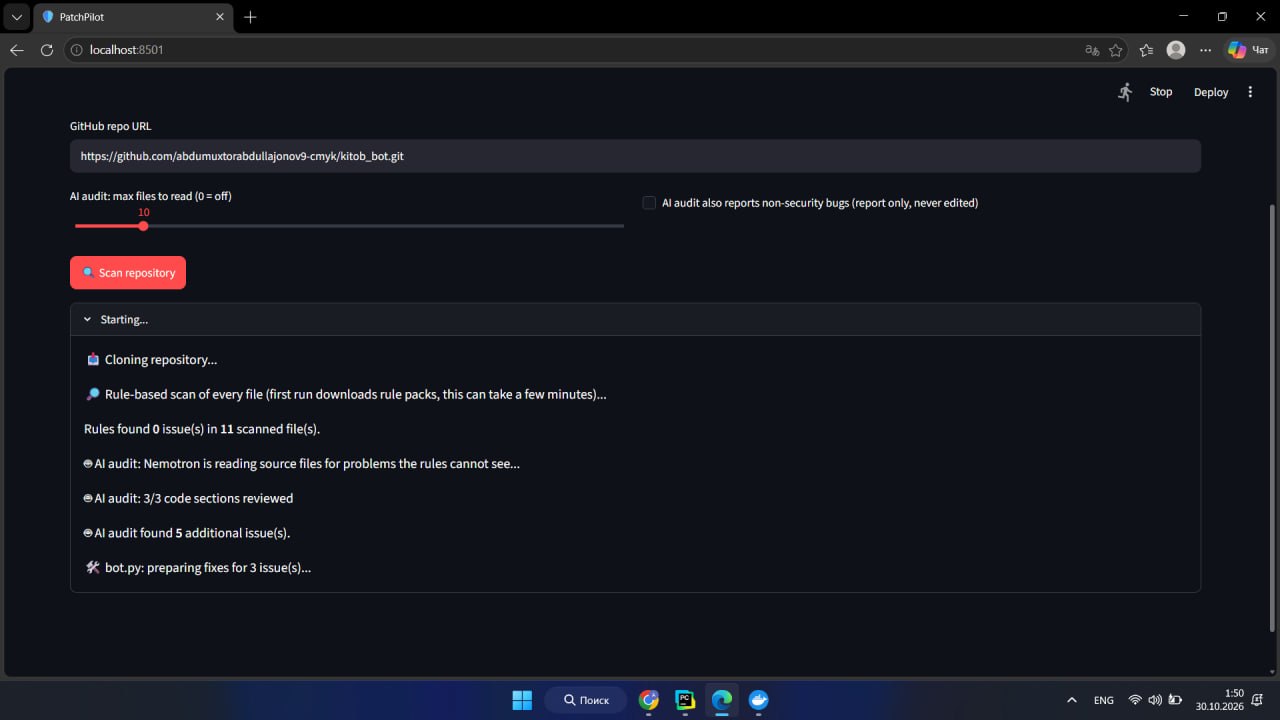
Static analyzers find security problems but leave the fixing to developers. LLM auto-fixers fix them but often rewrite half a file and cannot prove the result is safe. PatchPilot combines both. Semgrep (12 rule packs plus custom rules) and a Nemotron-3-Super source audit find vulnerabilities, including logic-level issues that rules miss. Nemotron-3-Ultra then writes a minimal patch from only the lines around each finding. Every fix passes guardrails: a 40-line size limit, syntax validation, a Semgrep re-scan, and checks that reject unsafe code. Known issues such as CSRF tokens and missing SRI hashes are fixed by deterministic code, not by the model. Secrets, vendored files and non-security bugs are report-only. Risky fixes (for example a view that becomes POST-only) get a visible warning. Nothing is pushed without human review of every diff.
PatchPilot
Autonomous security auditing and auto-fixing pipeline powered by NVIDIA Nemotron on Nebius AI Cloud.
Updates

Leave feedback in the comments!
Log in or sign up for Devpost to join the conversation.