-
-
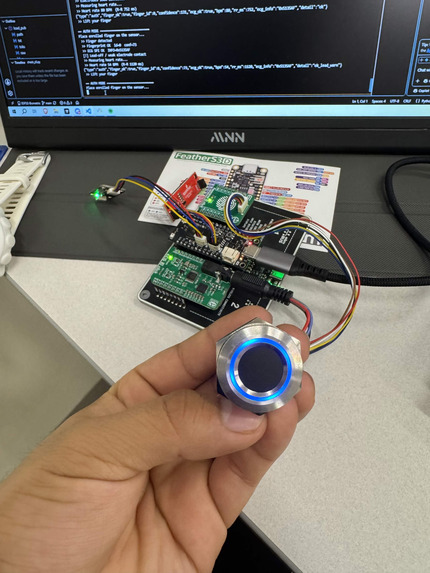
fingerprint sensor
-
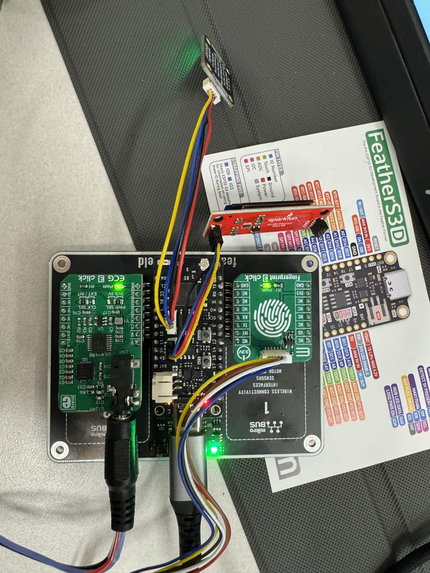
techstack
-
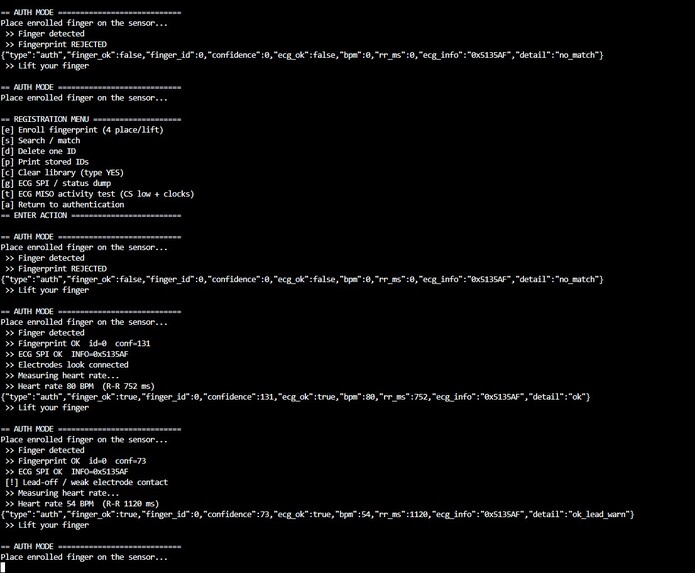
continuous biometric check dashboard
-
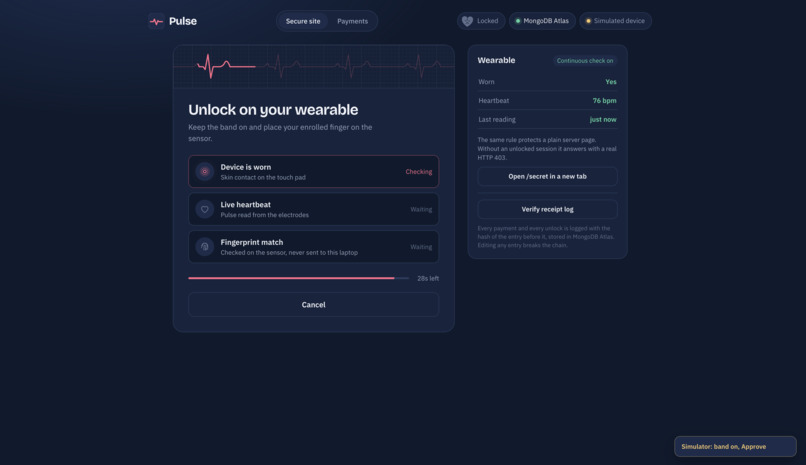
base page
-
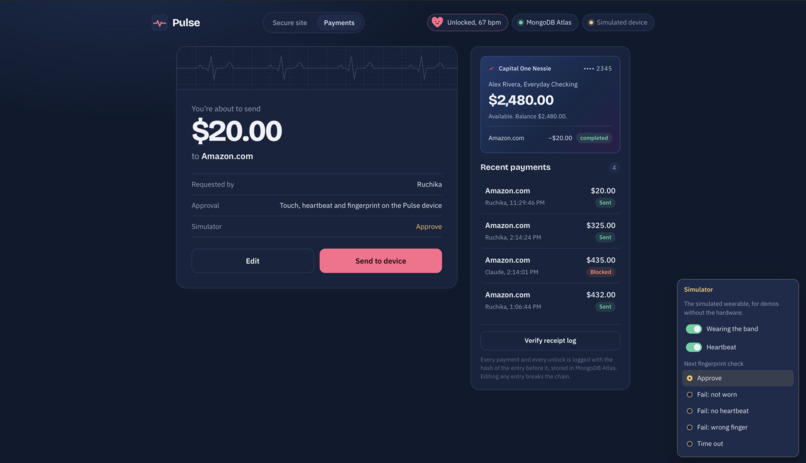
payment portal request
-
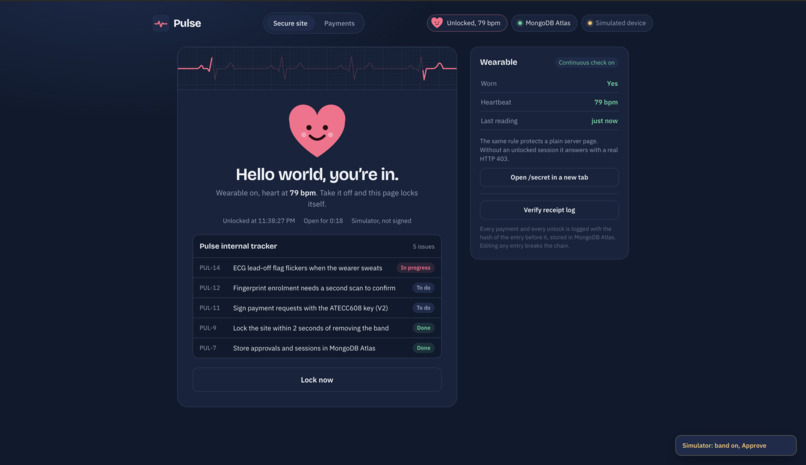
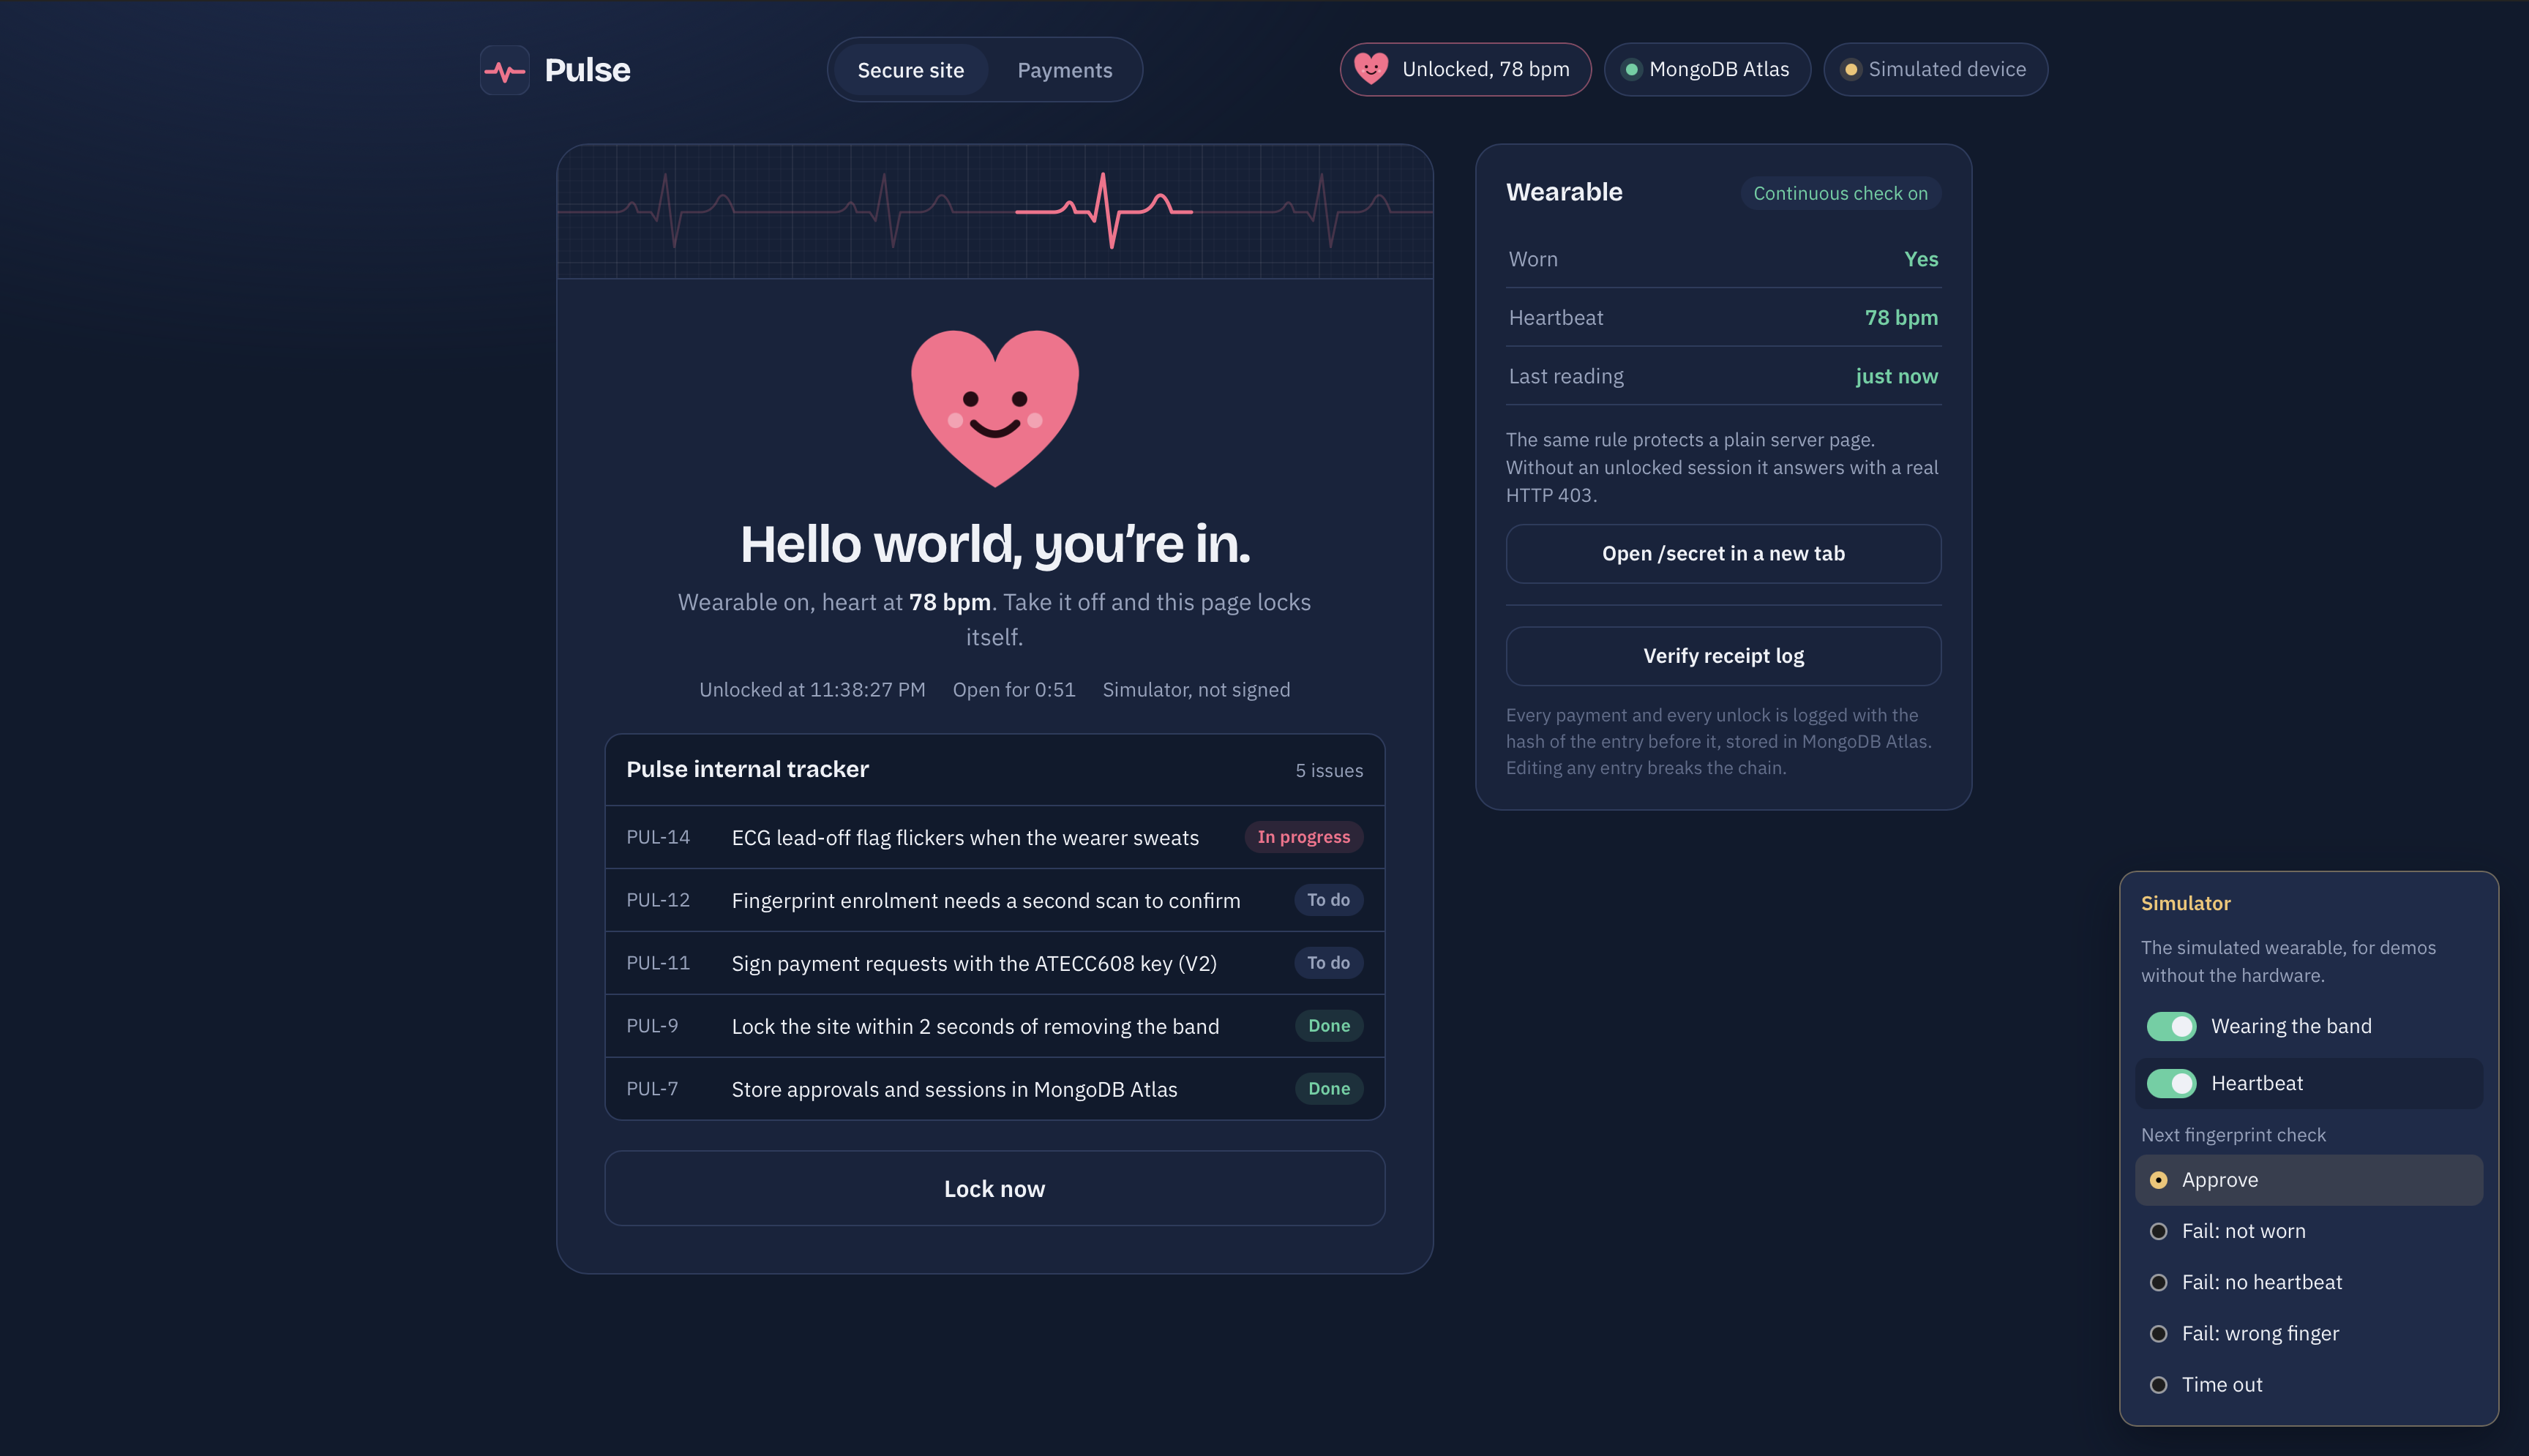
login success
-
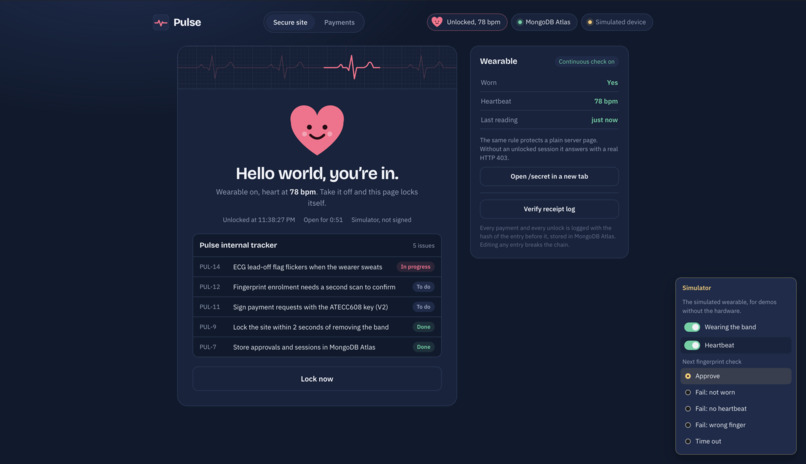
simulated cases
-
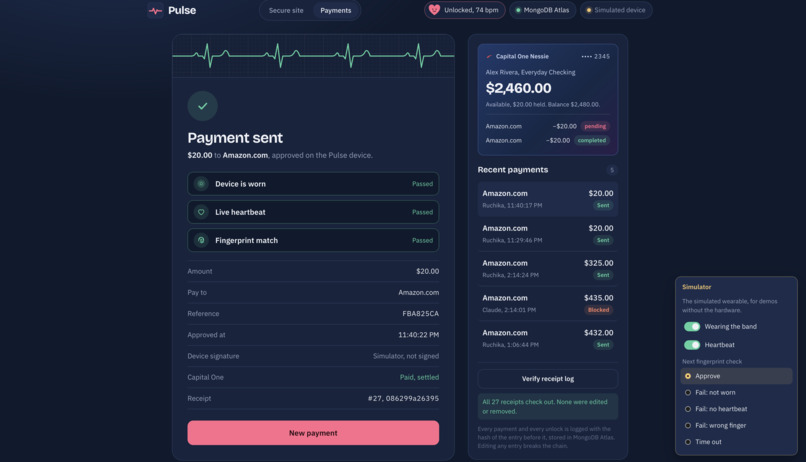
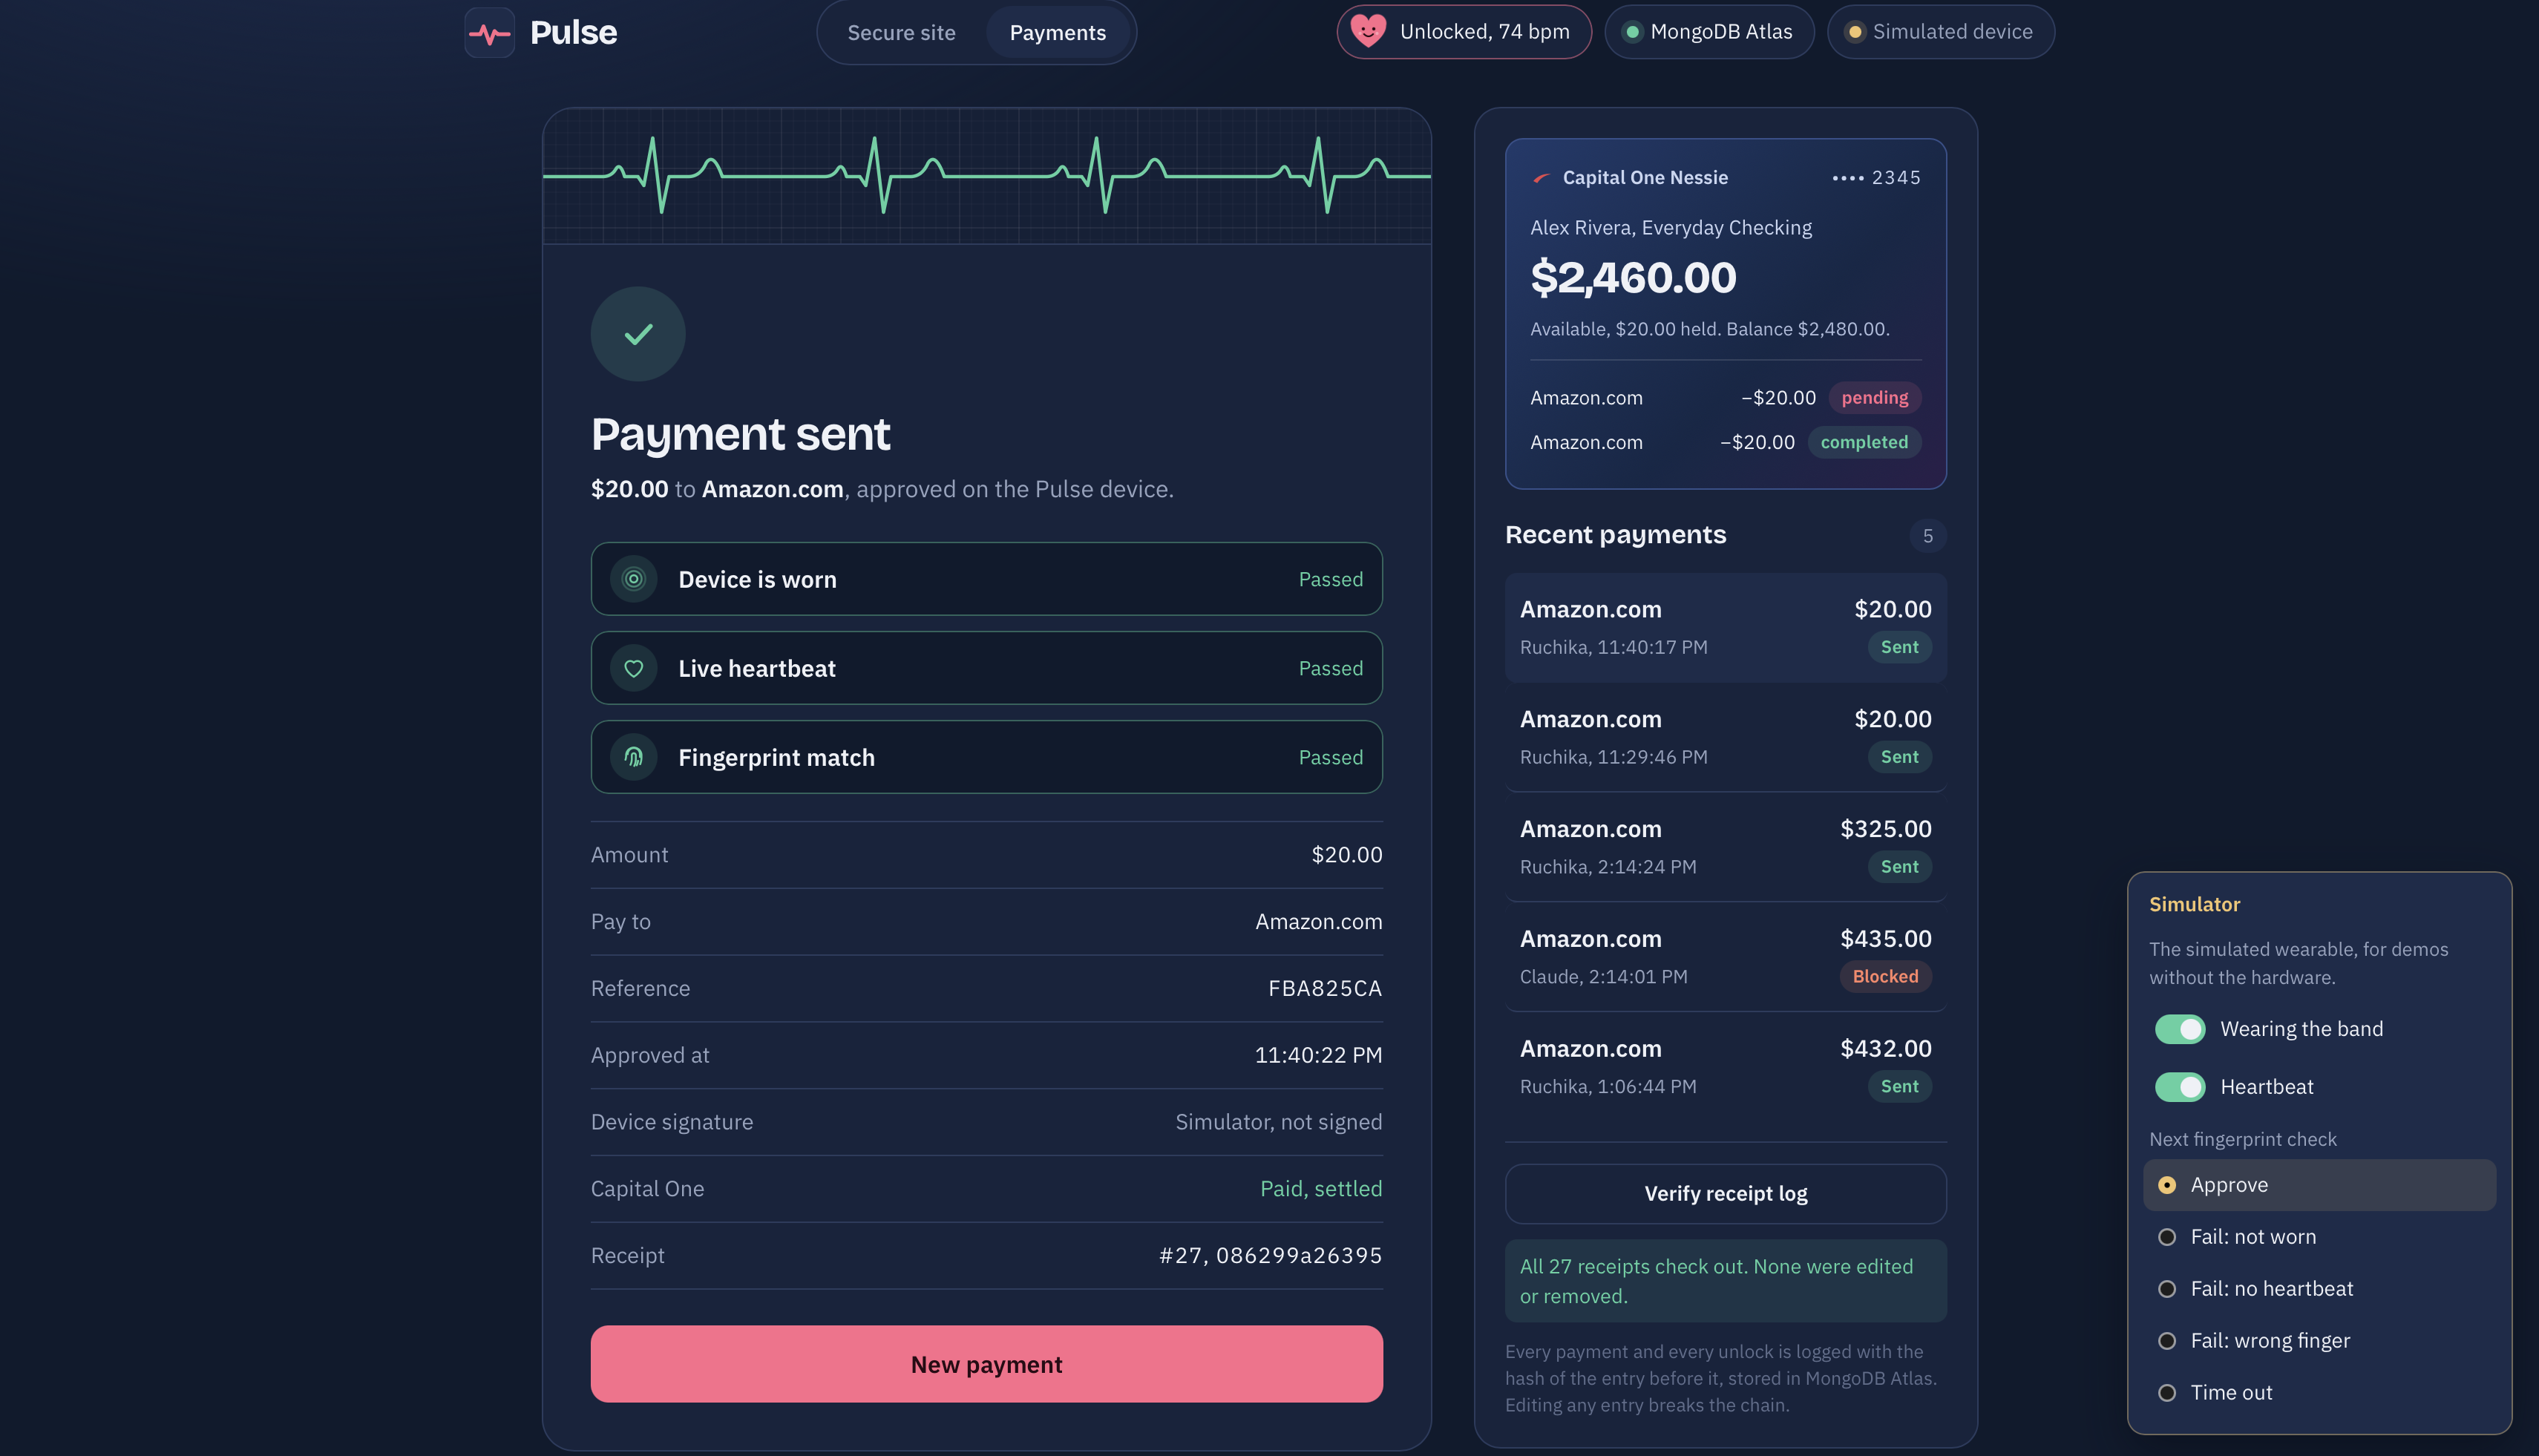
receipt log is stored
-
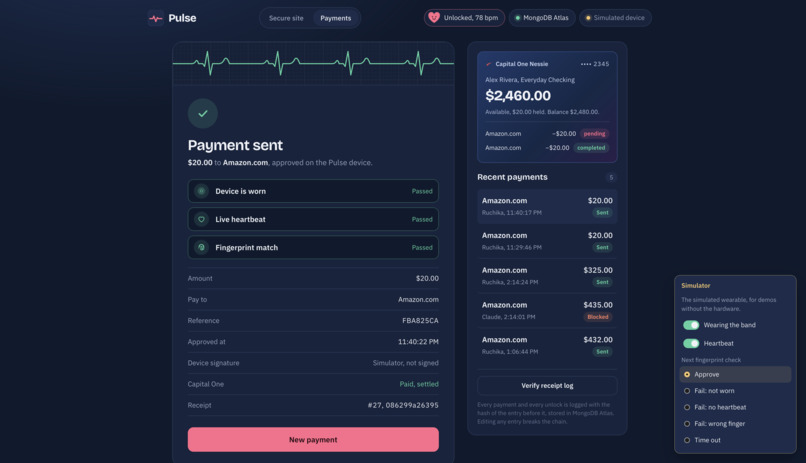
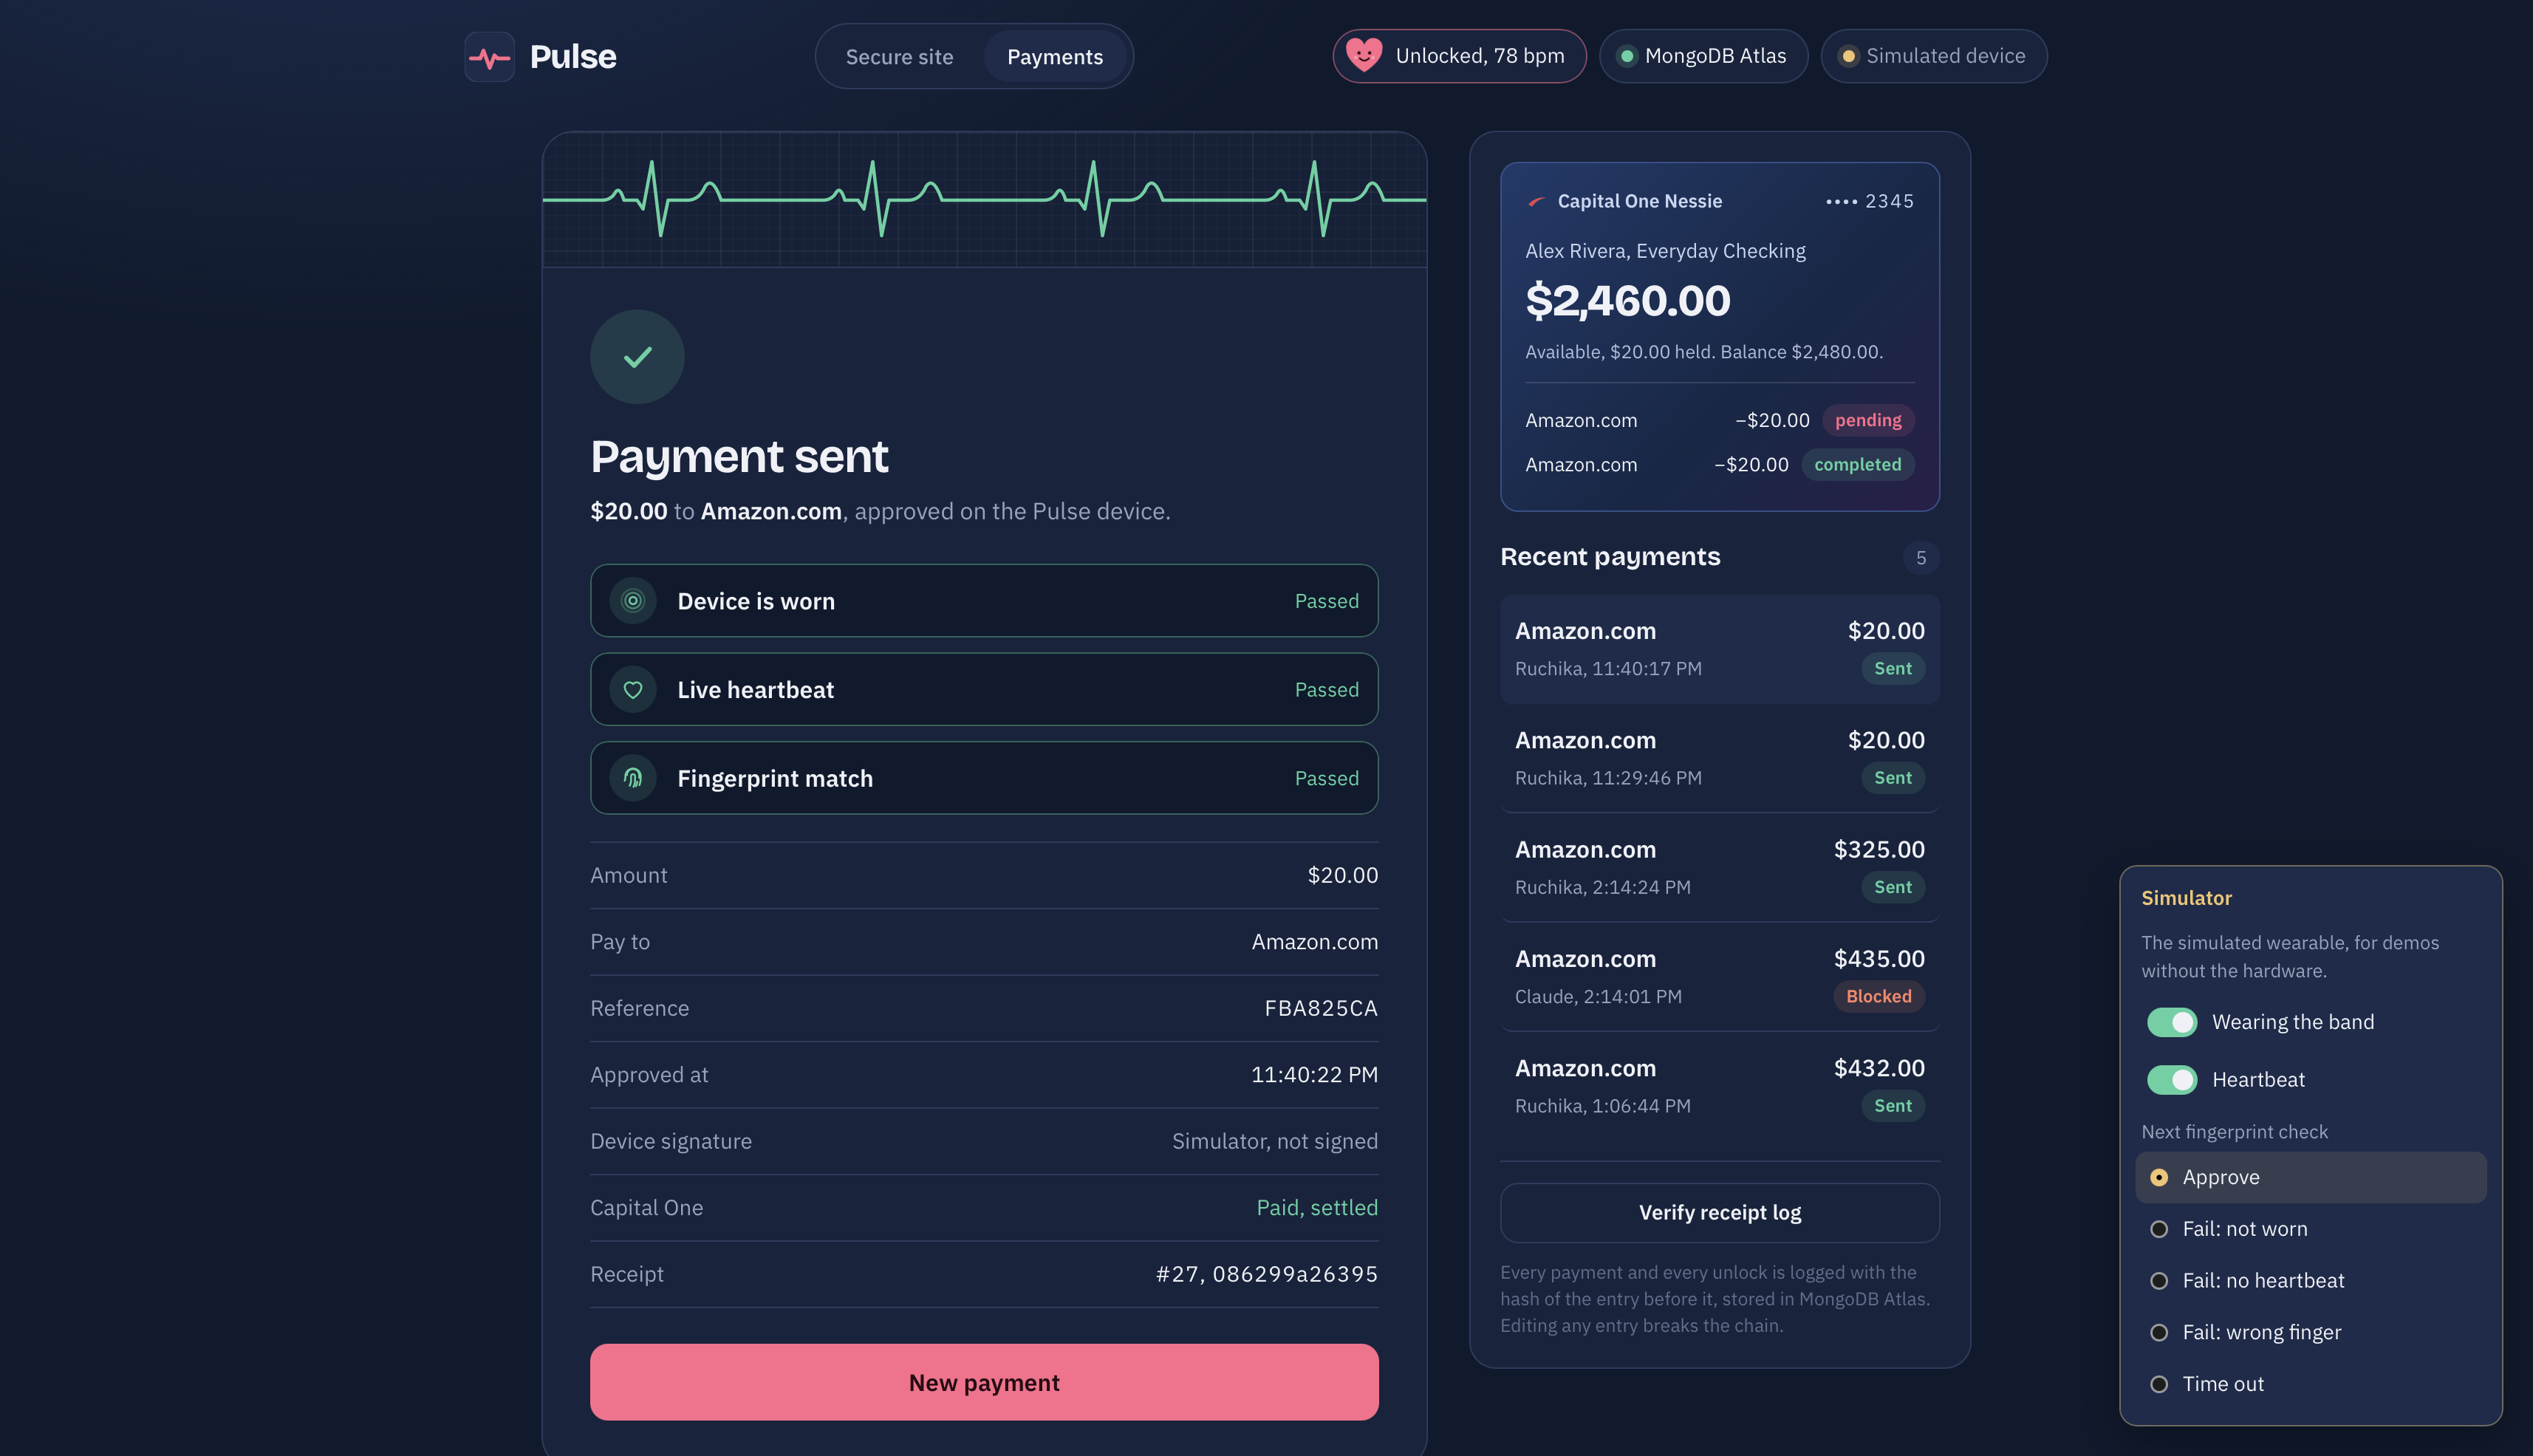
all humanity checks are successful on device, payment gets sent
-
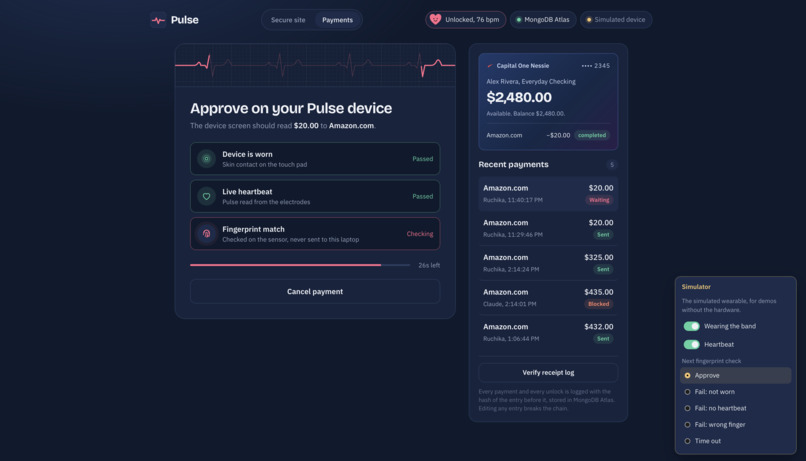
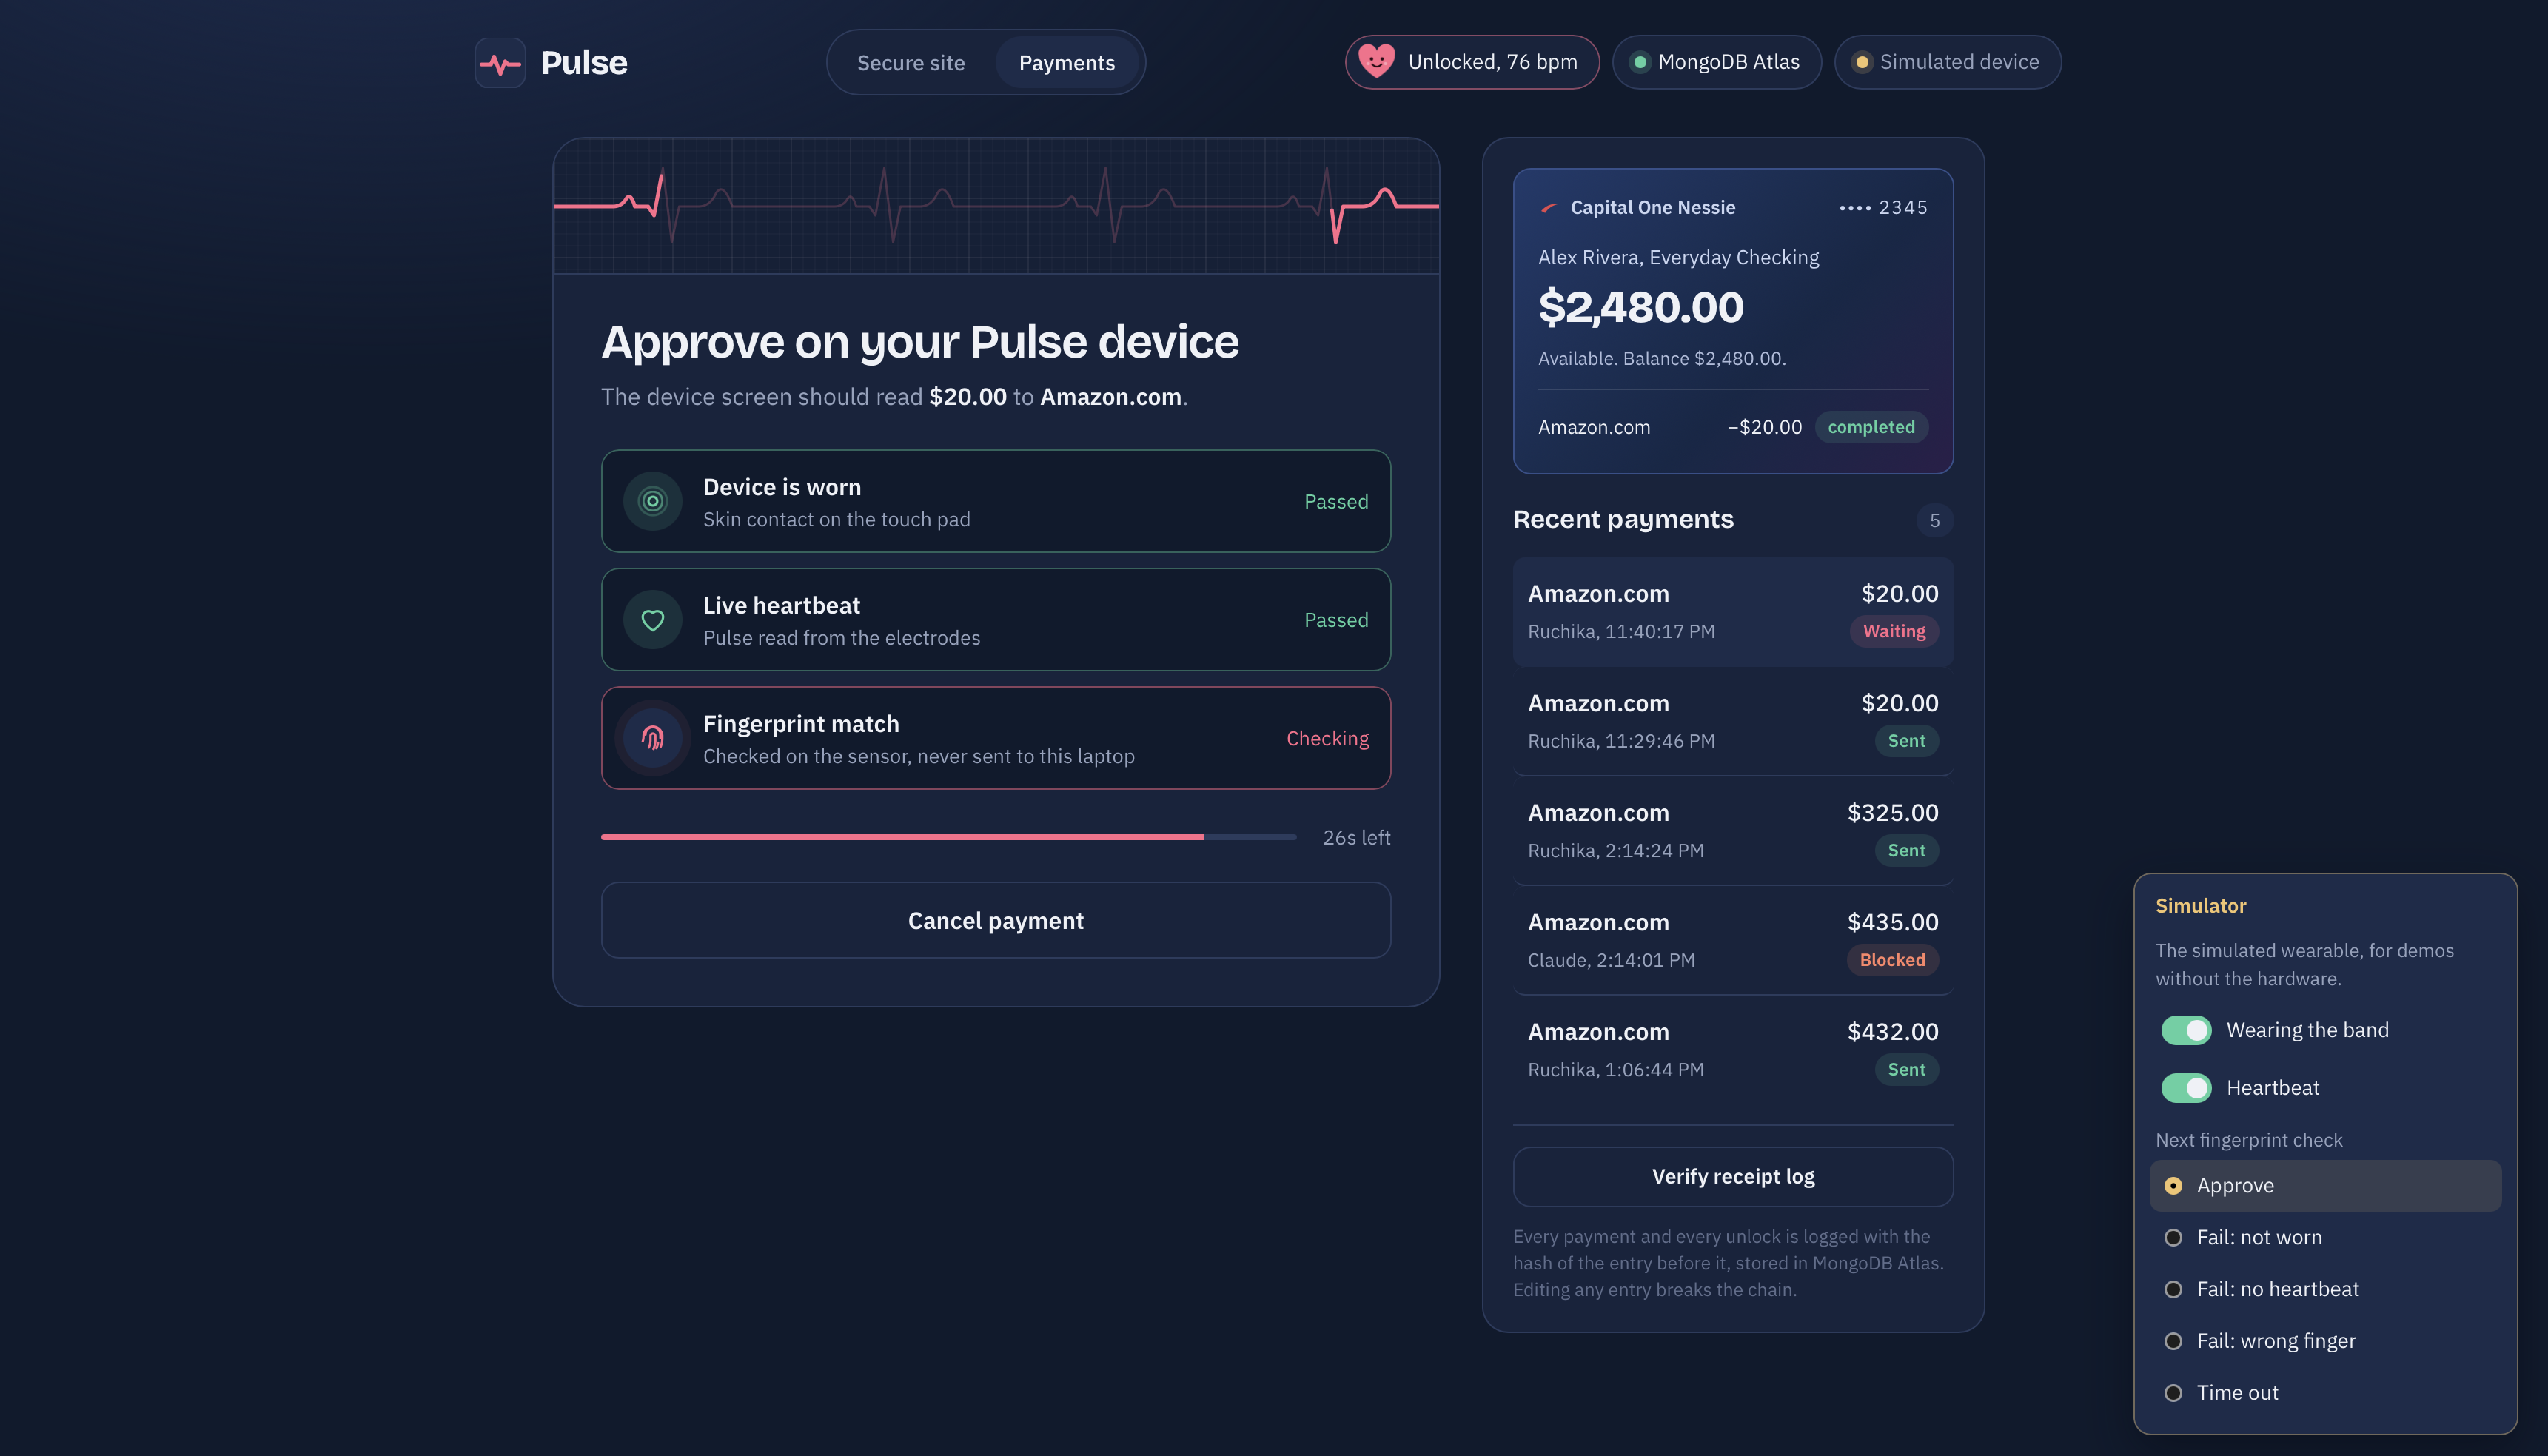
device bound request pending
-
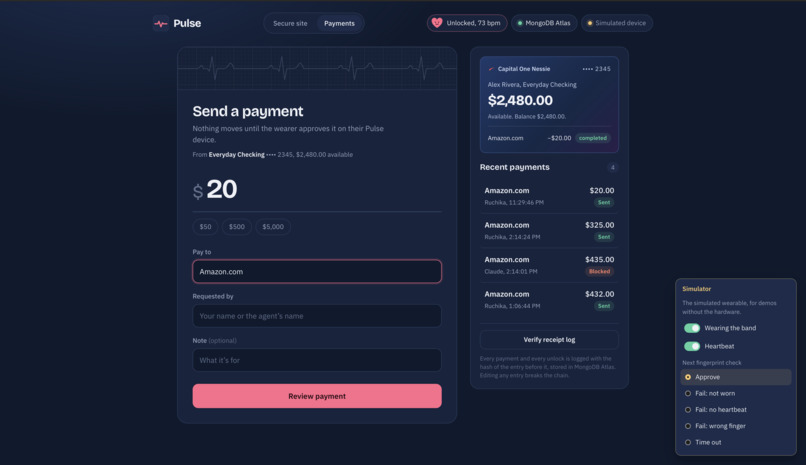
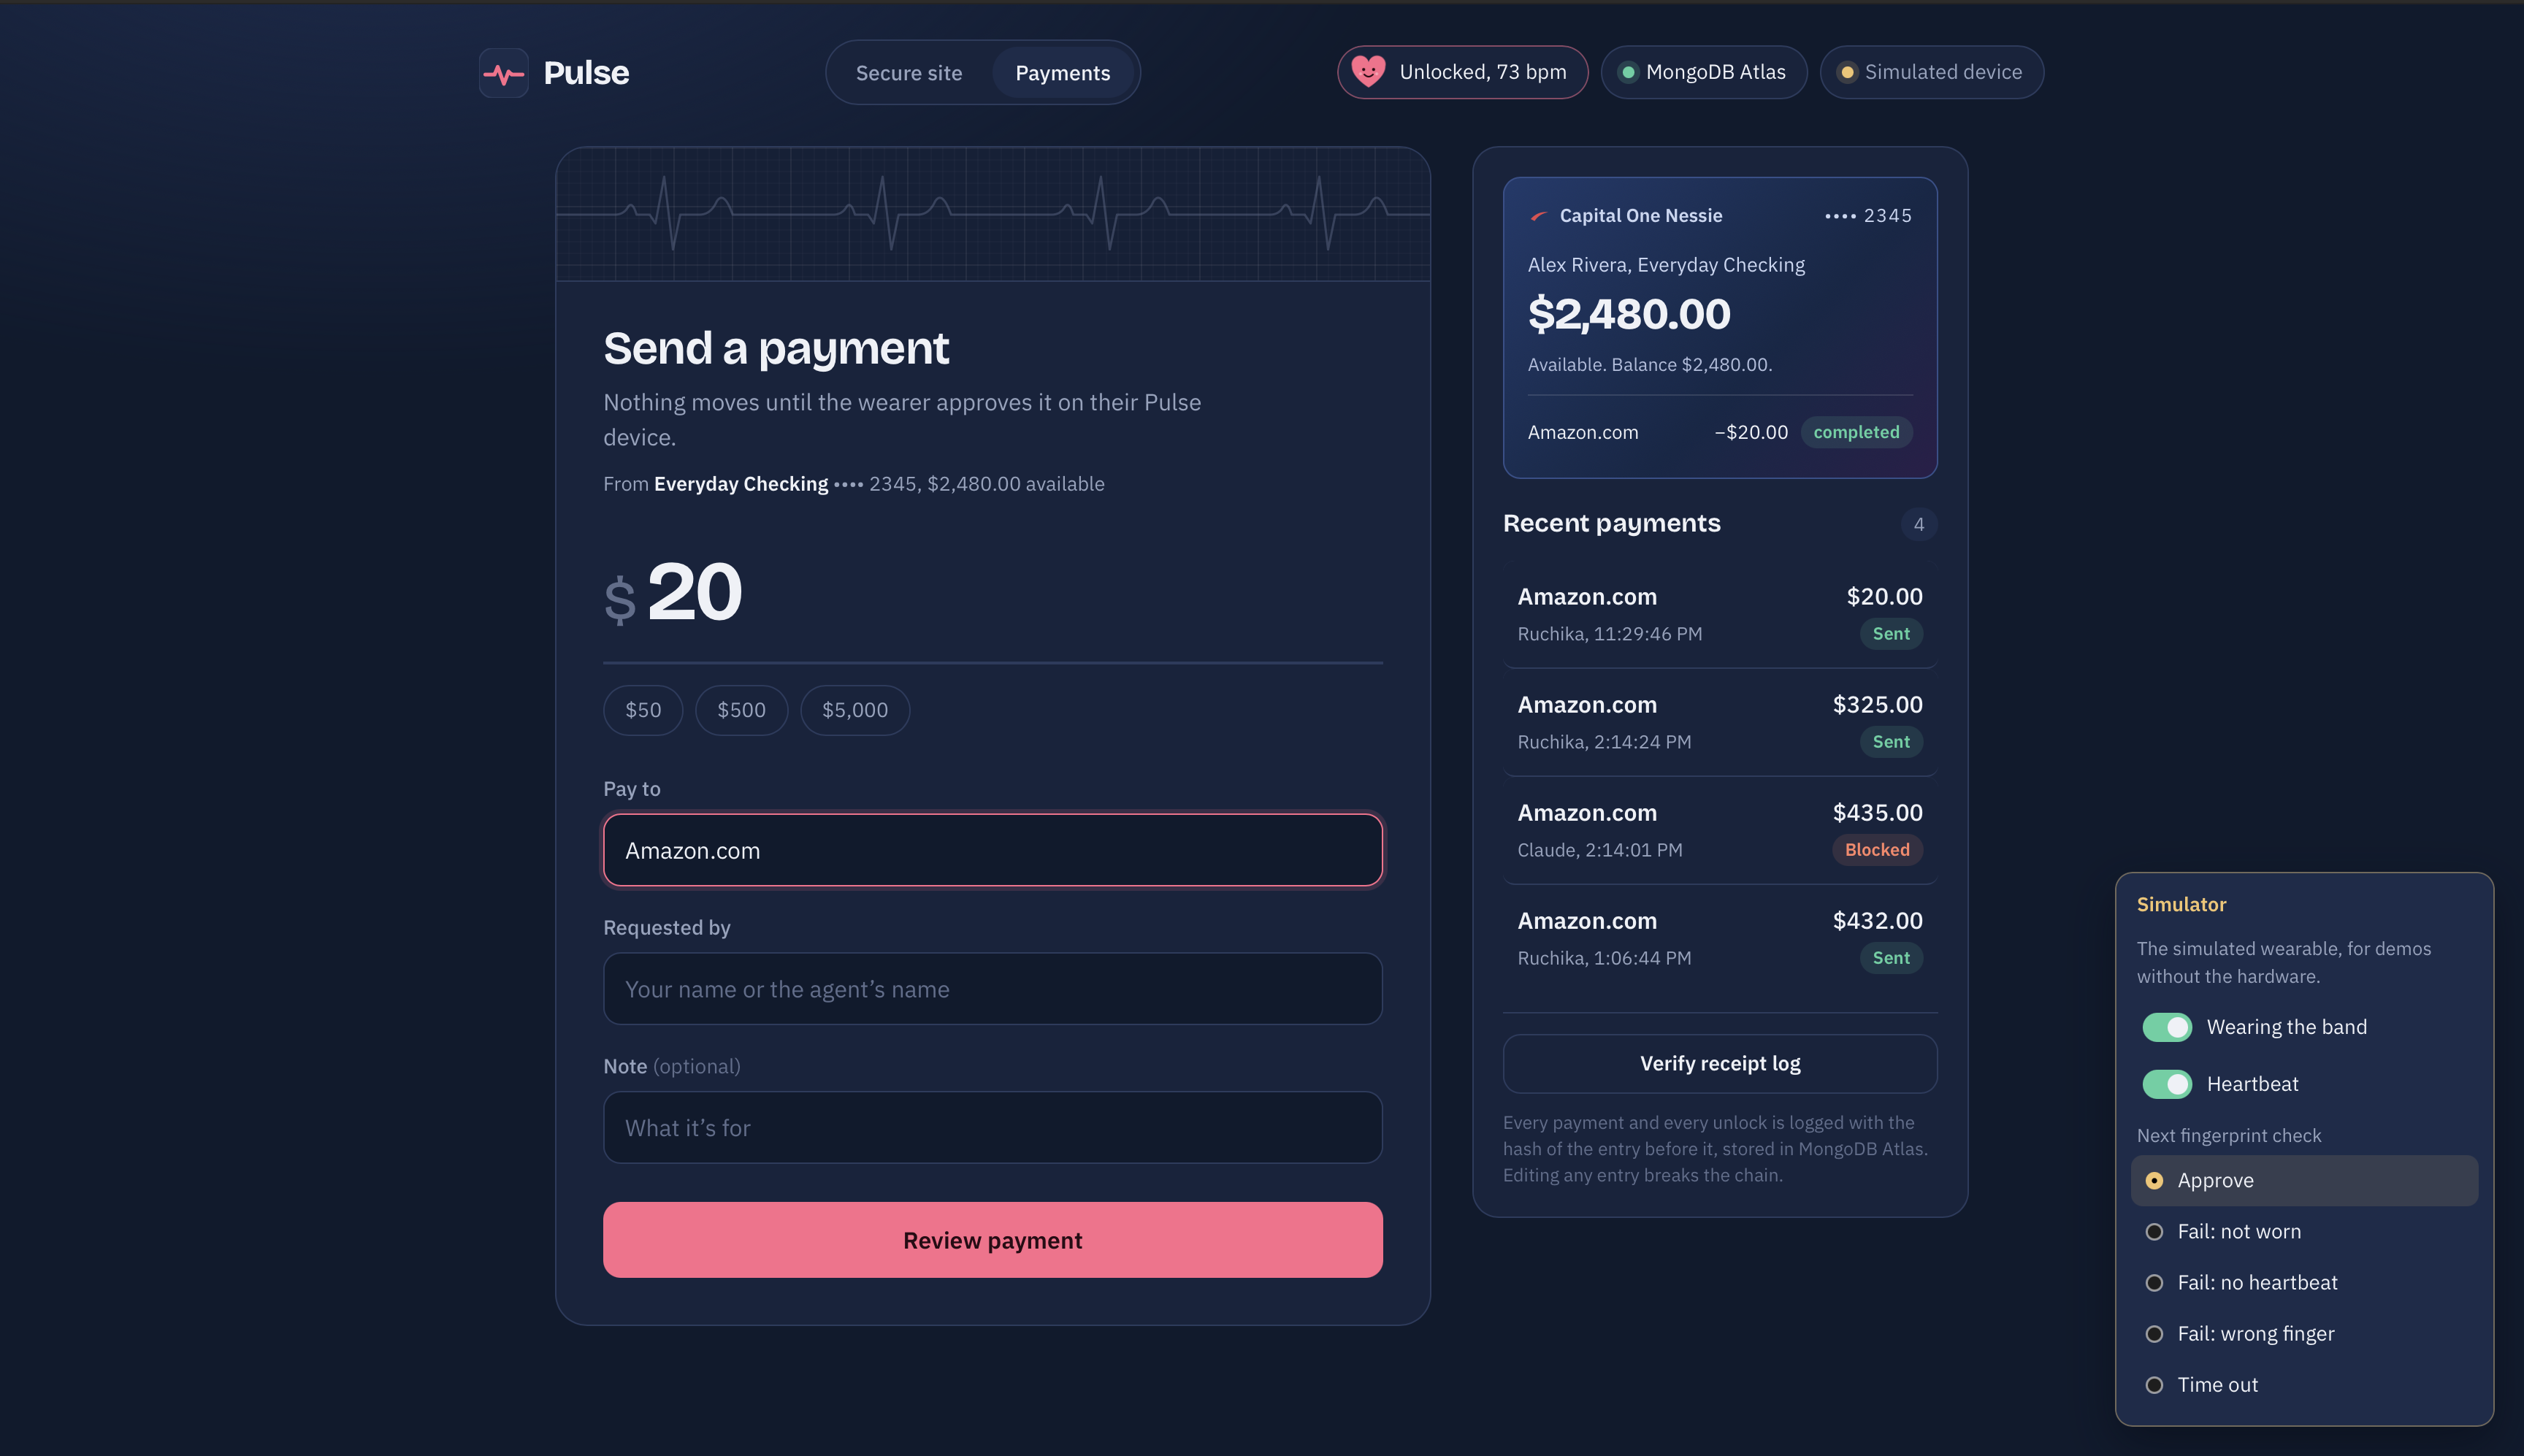
payment portal
-
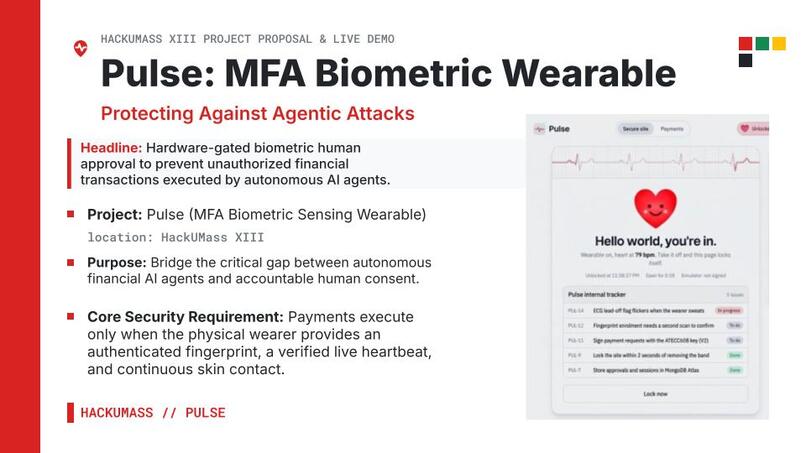
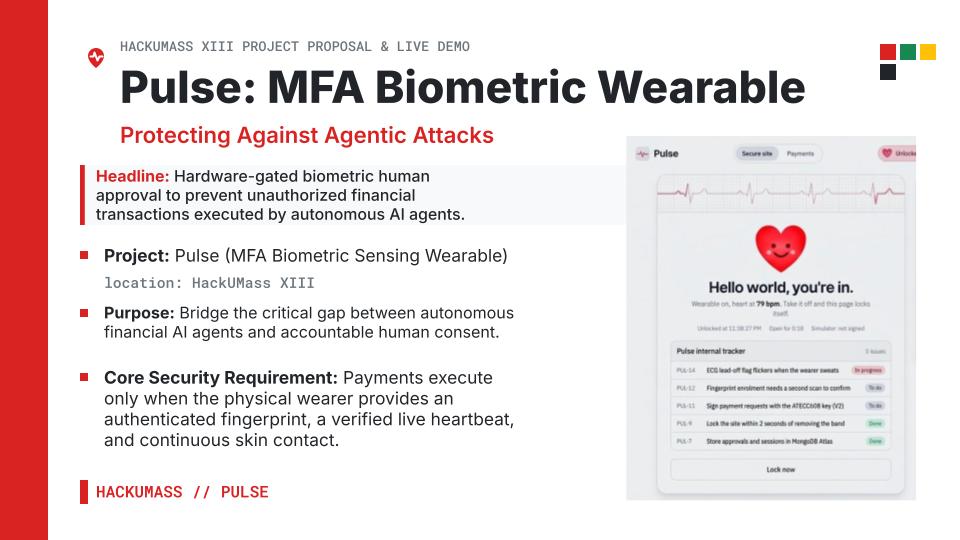
Explanation slide
-
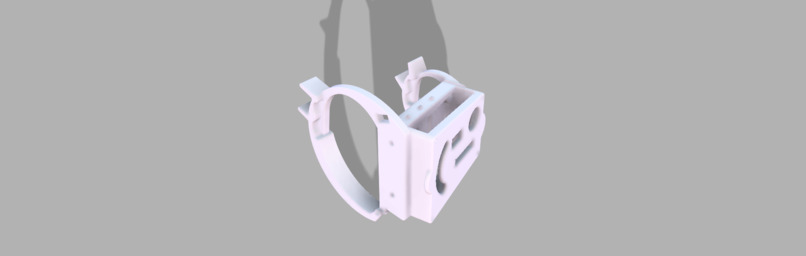
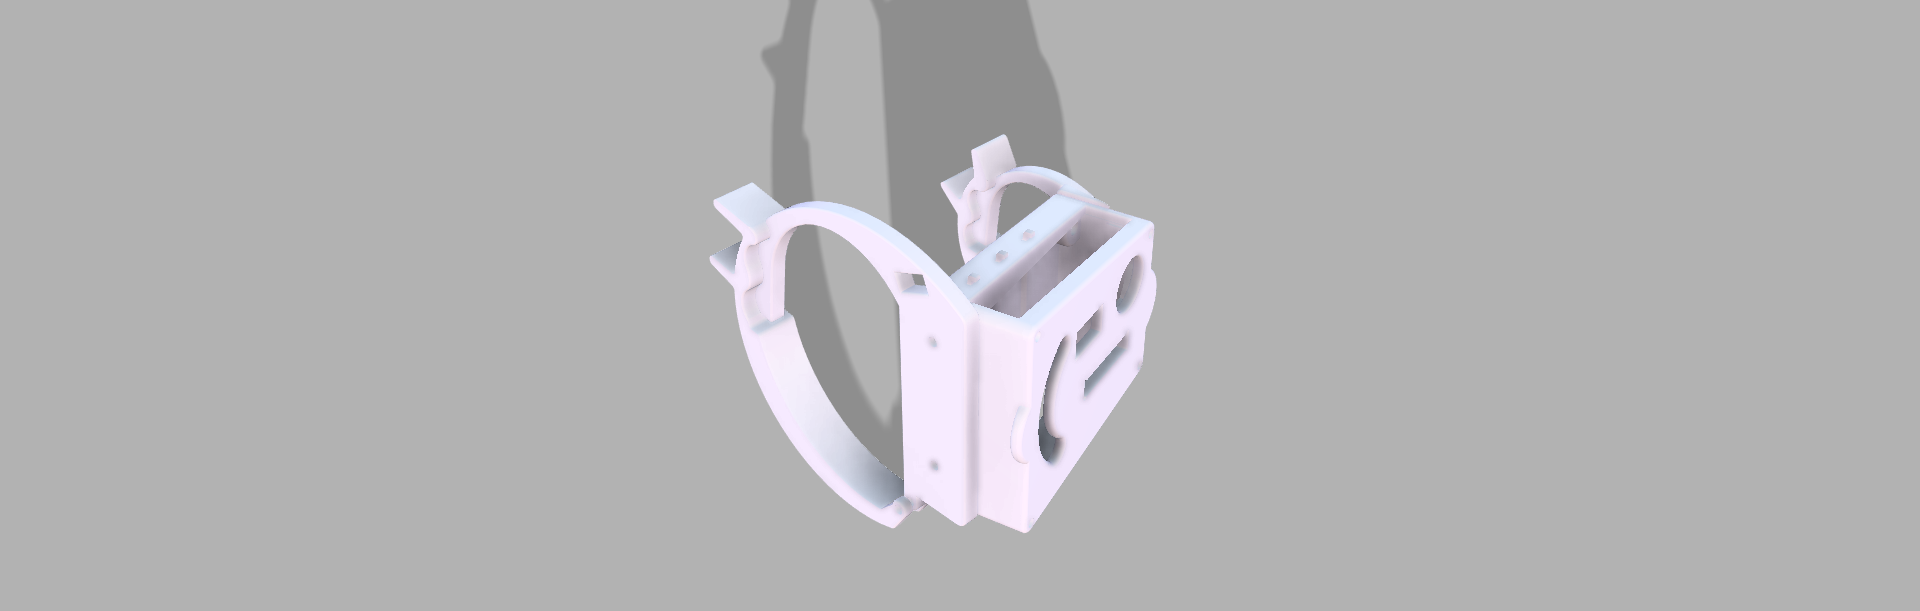
cad enclosure
-
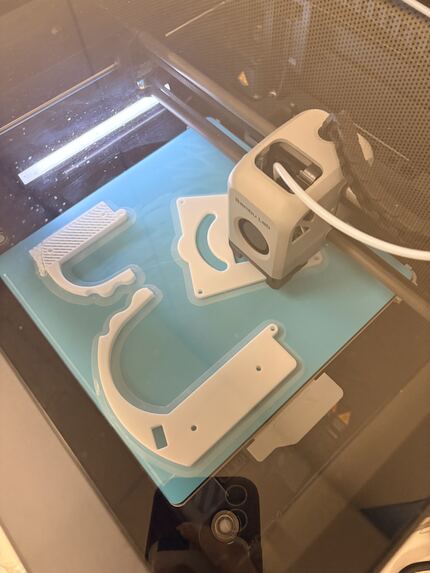
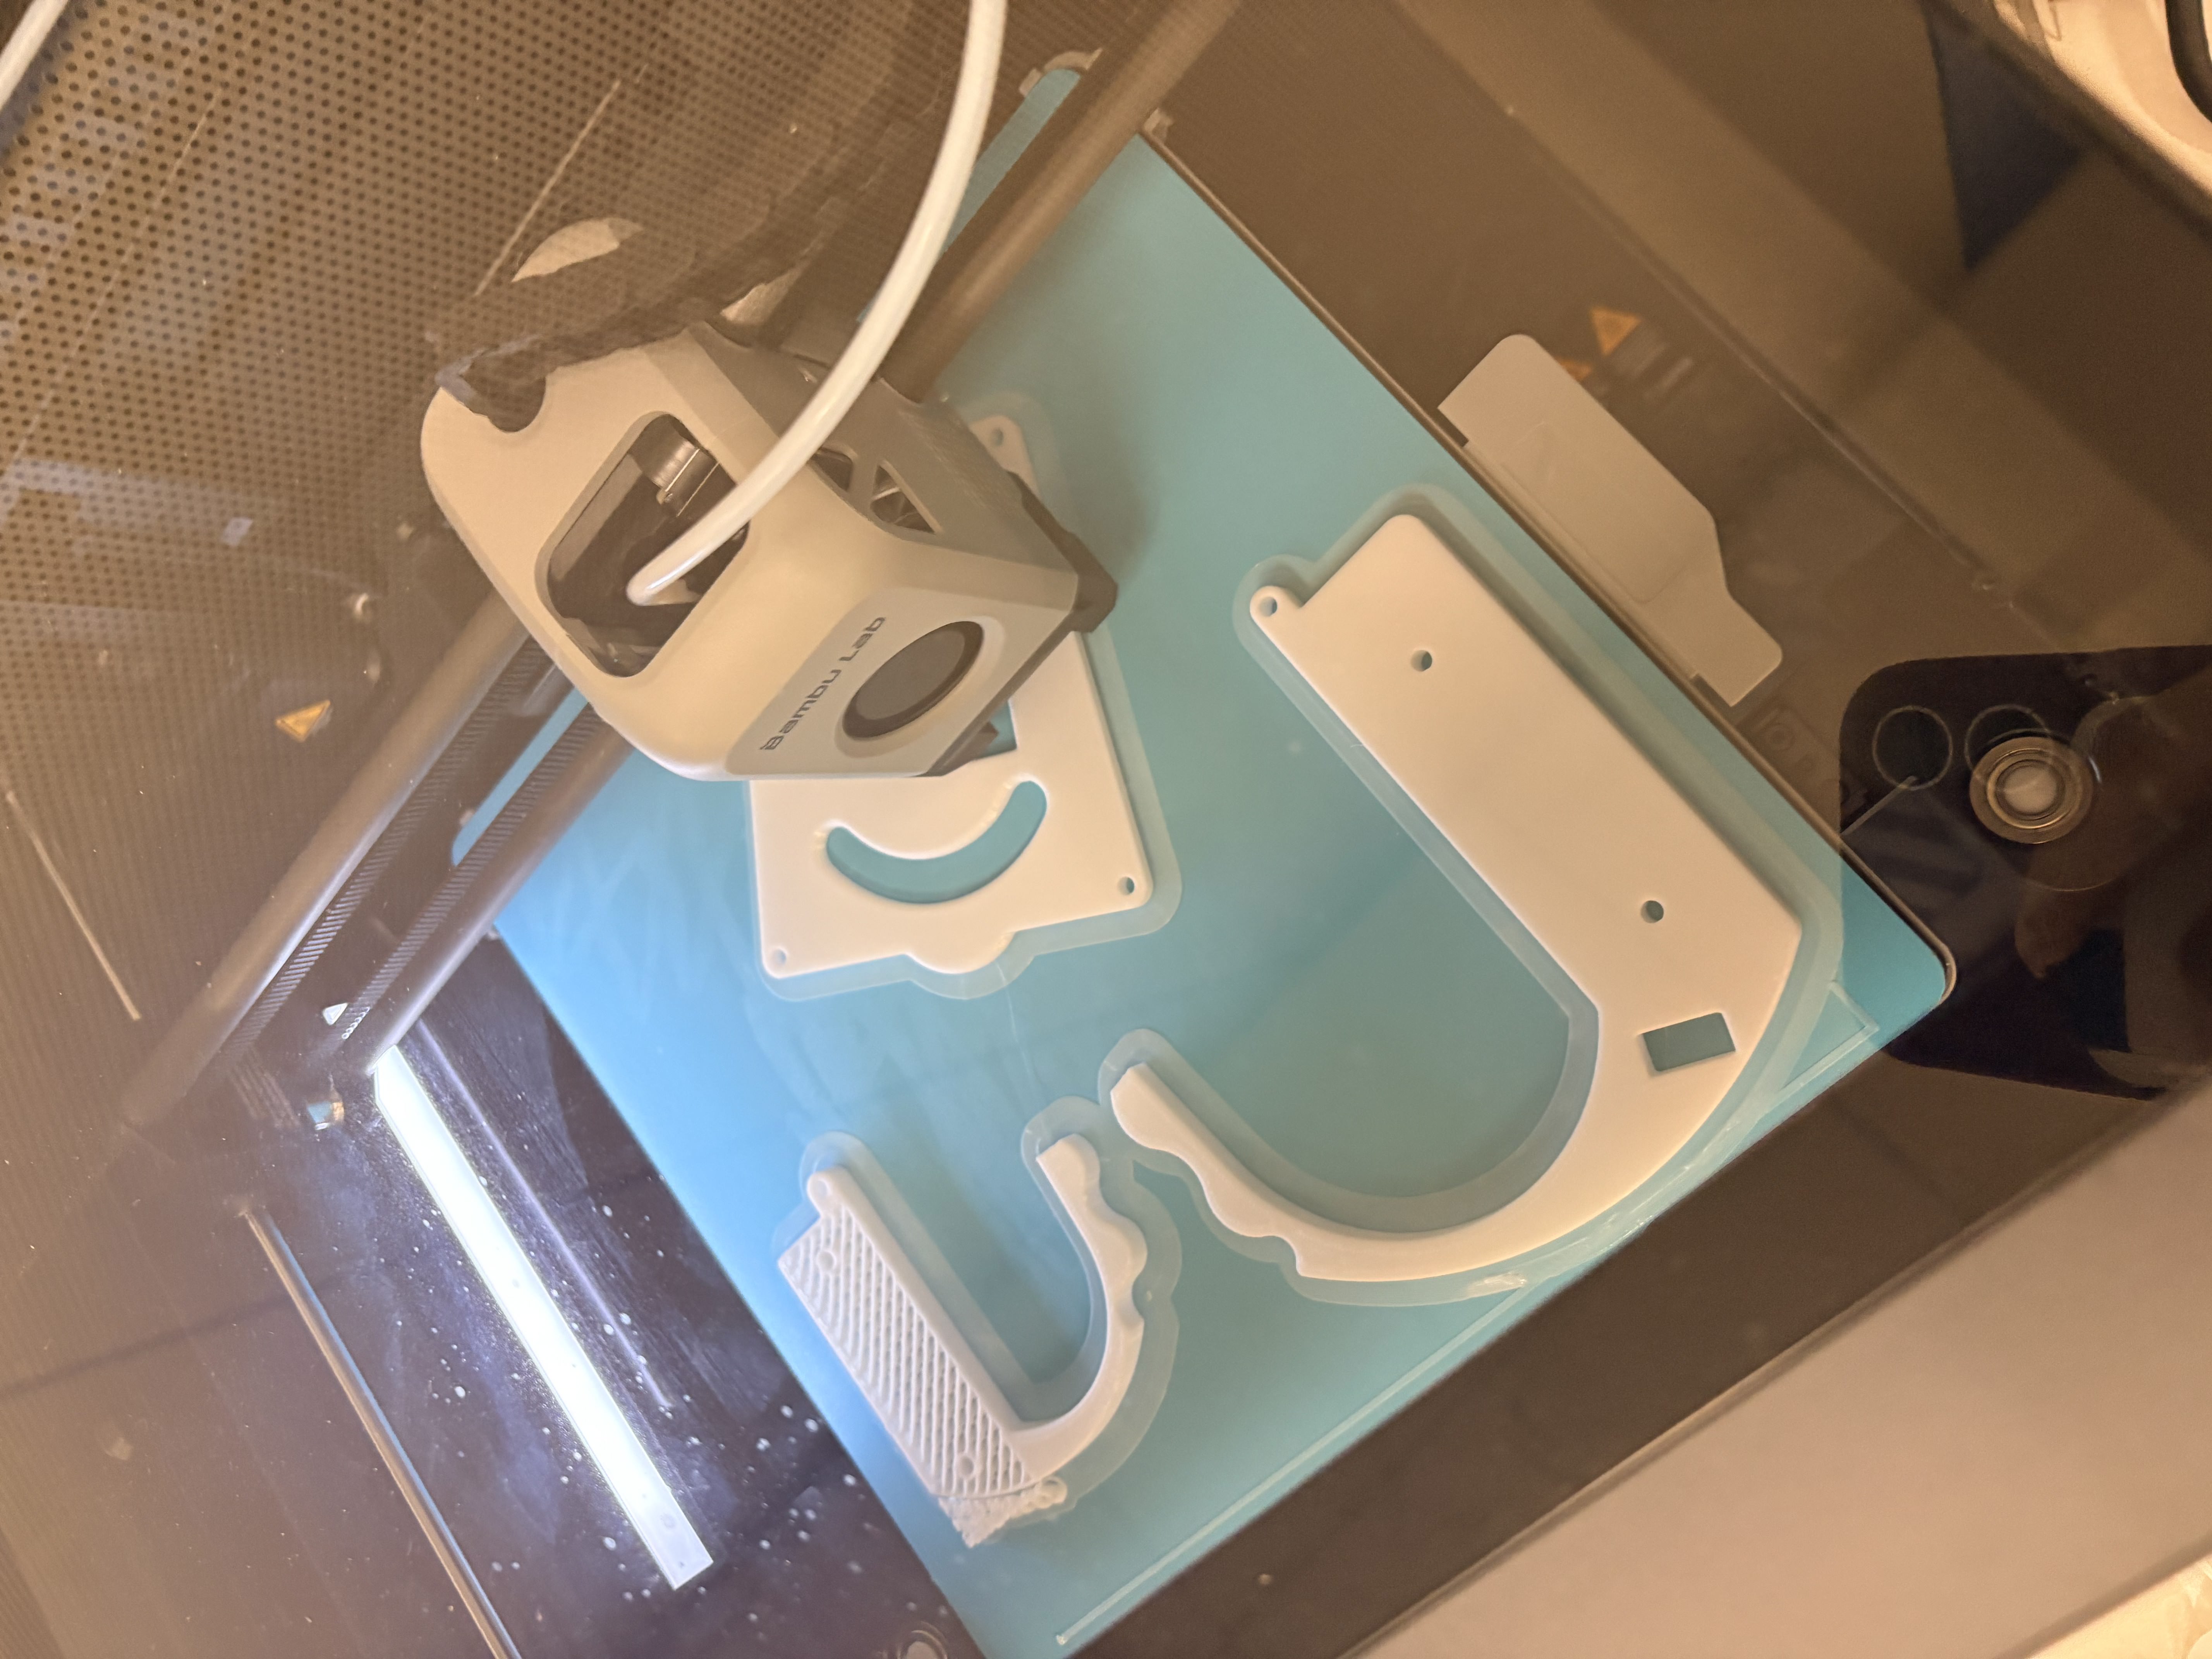
Pulse wearable enclosure: custom PETG wrist-mount parts printed on a Bambu Lab (designed in Fusion 360)
The Agentic threat on the Horizon...
Last month Binance lost billions, also thousands of compromised agents making moves in bank accounts were recorded, and sources say AI is the on track to be the greatest risk towards digital banking in 2027. Many companies have made their own attempts at human verification technology to protect against these types of vulnerabilities. Yubikey Bio is a cryptographically secure passkey with onboard biometric checking at login, not continuous. For Nymi, constant ecg pulse checking to keep a login session active allows pharma workers with PPE to have interact in secure environments without constantly using pass keys.
The future of Human verification...
Therefore we believe that the best way to prove presence, liveness, and identity is to use onboard biometric sensing with encryption to securely authorize human intent and use. We've created a simulated payment portal, NoHeartNoCart, with populated customer information that sends a request towards our wearable device, the "Pulse".
How it works
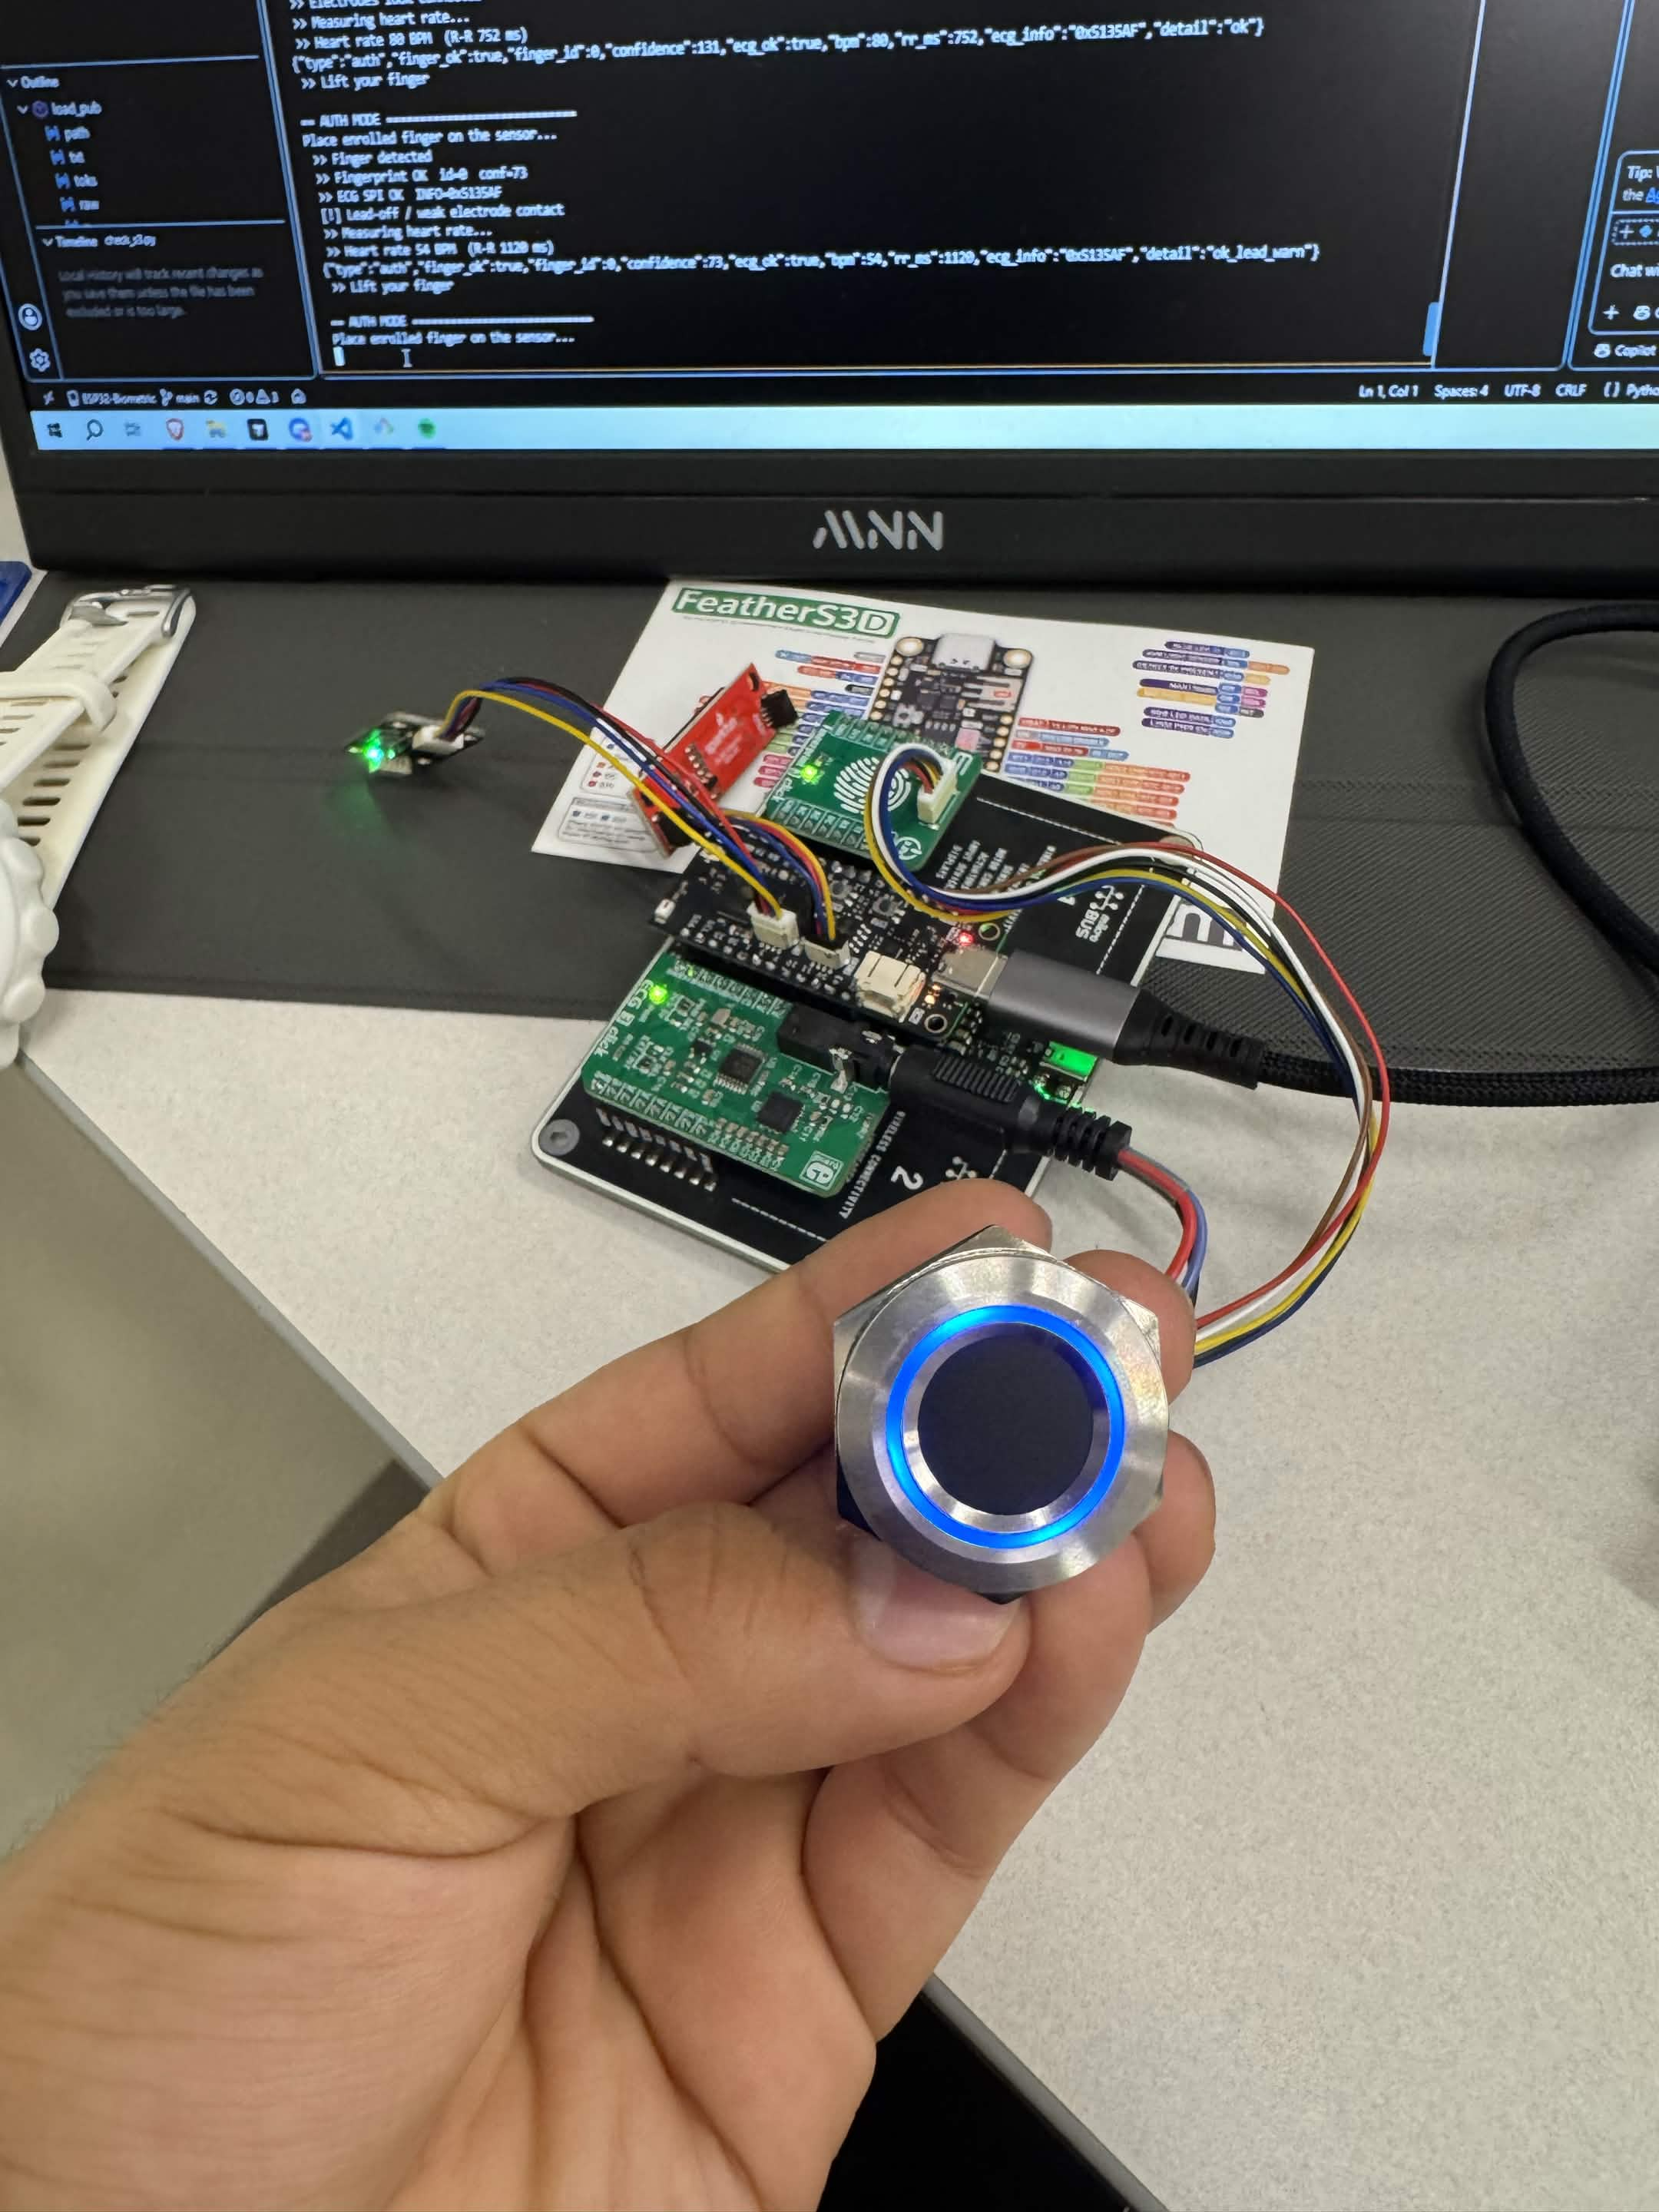
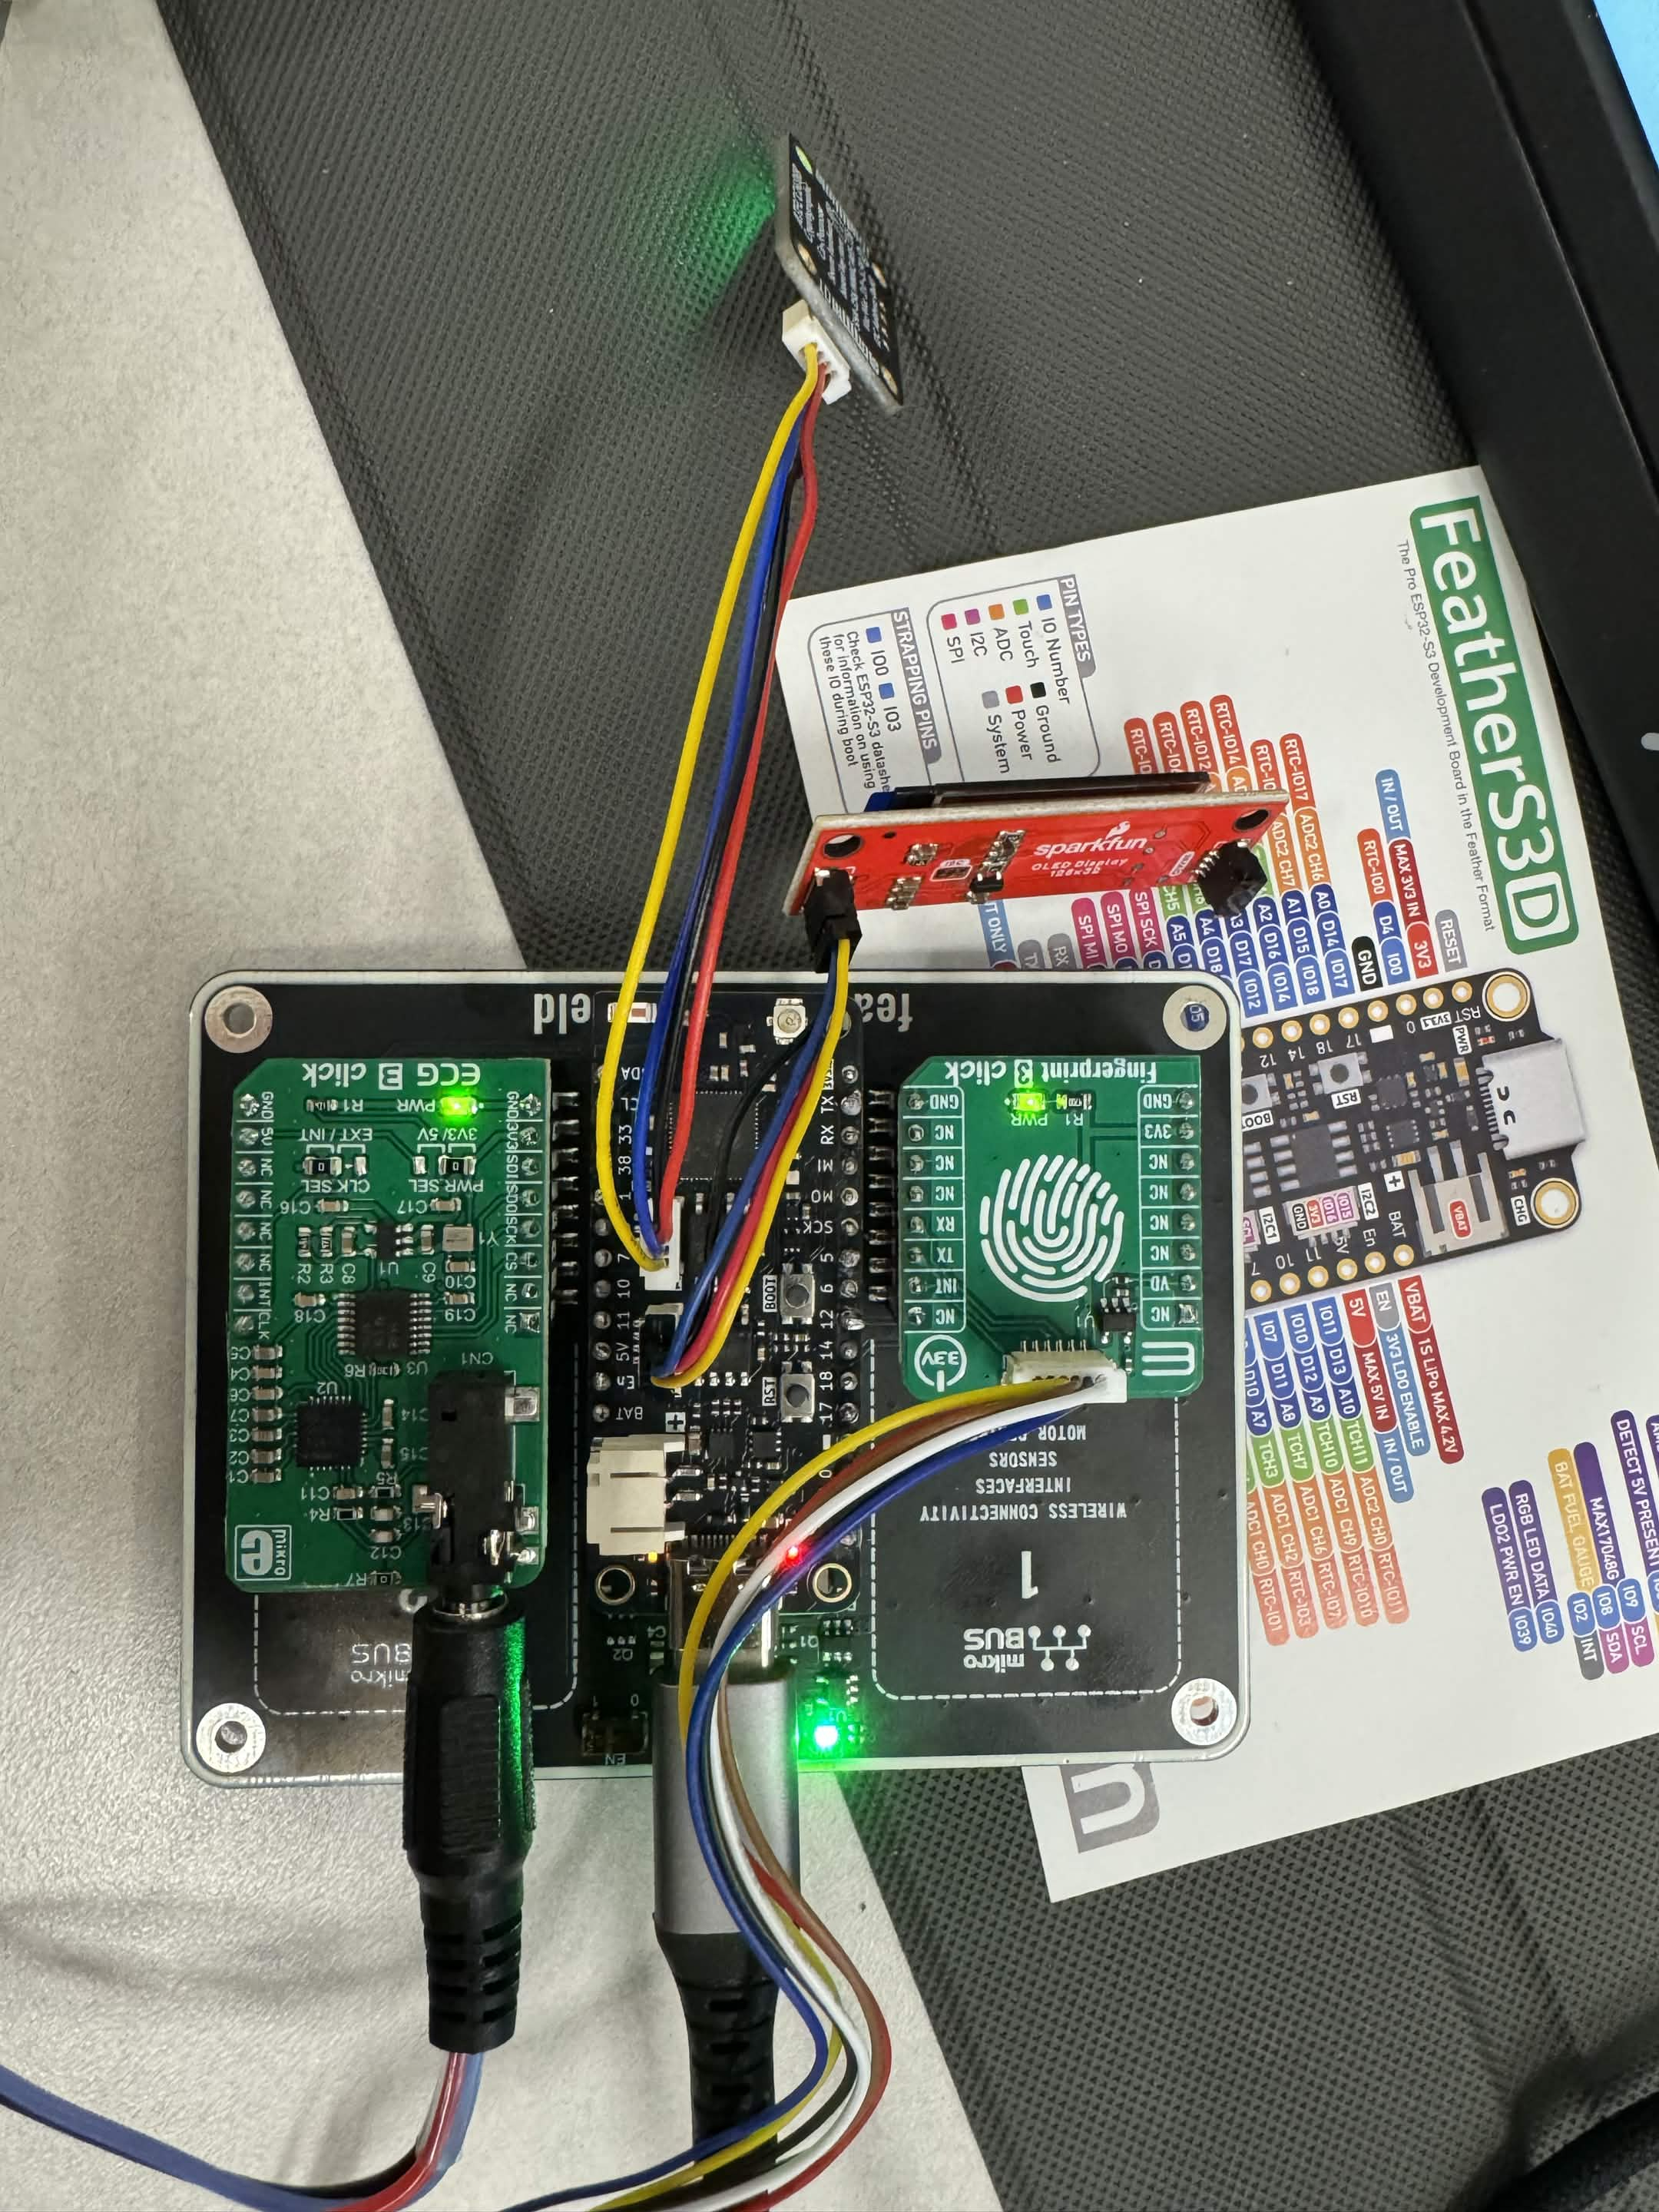
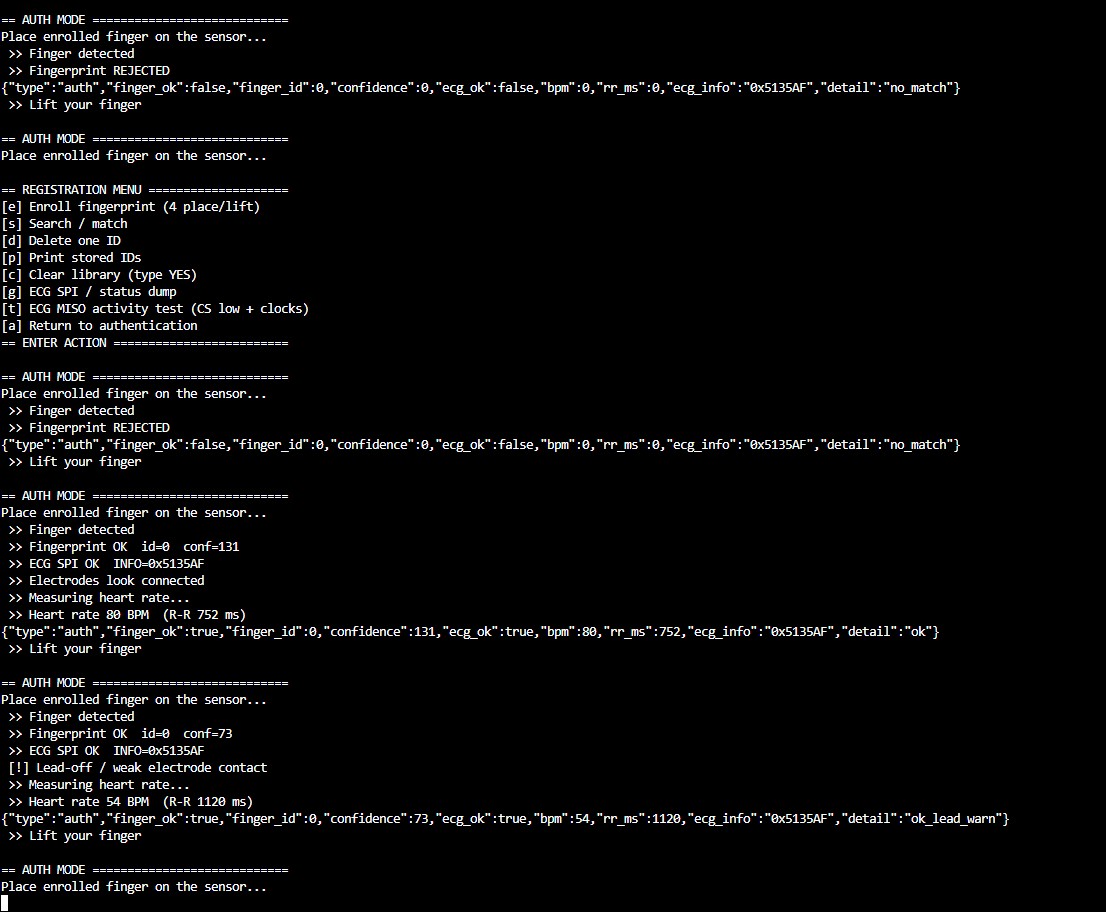
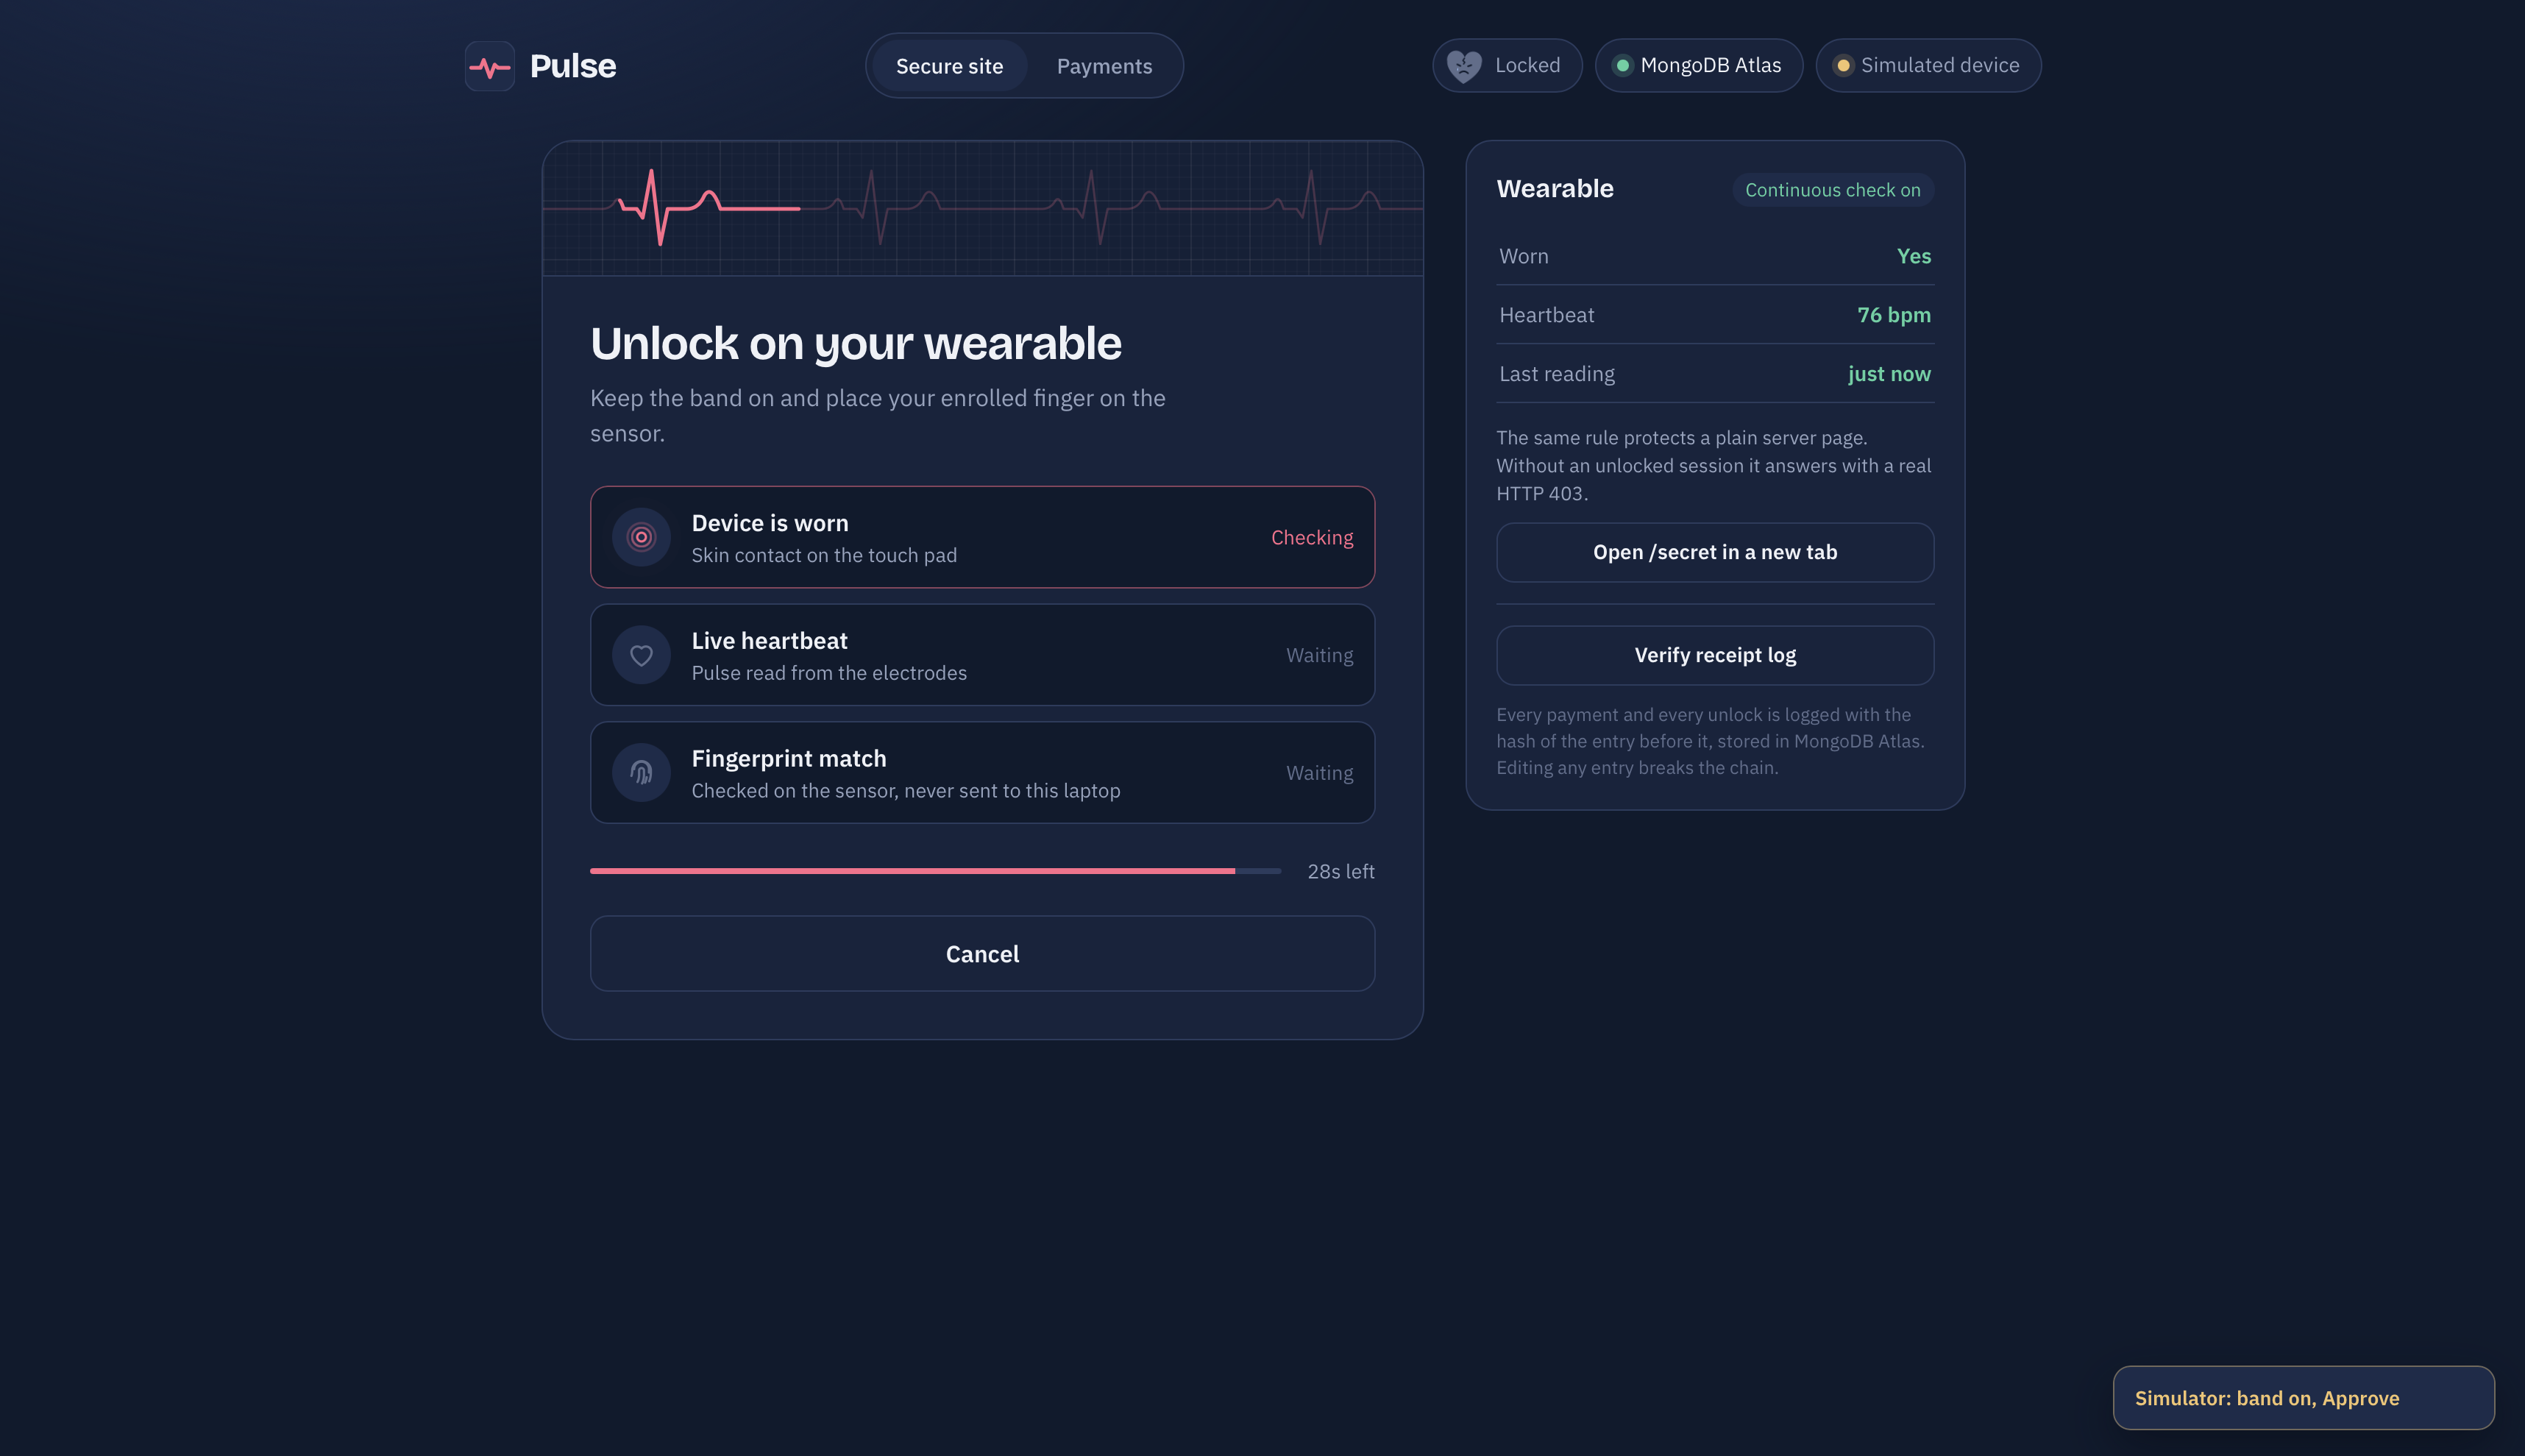
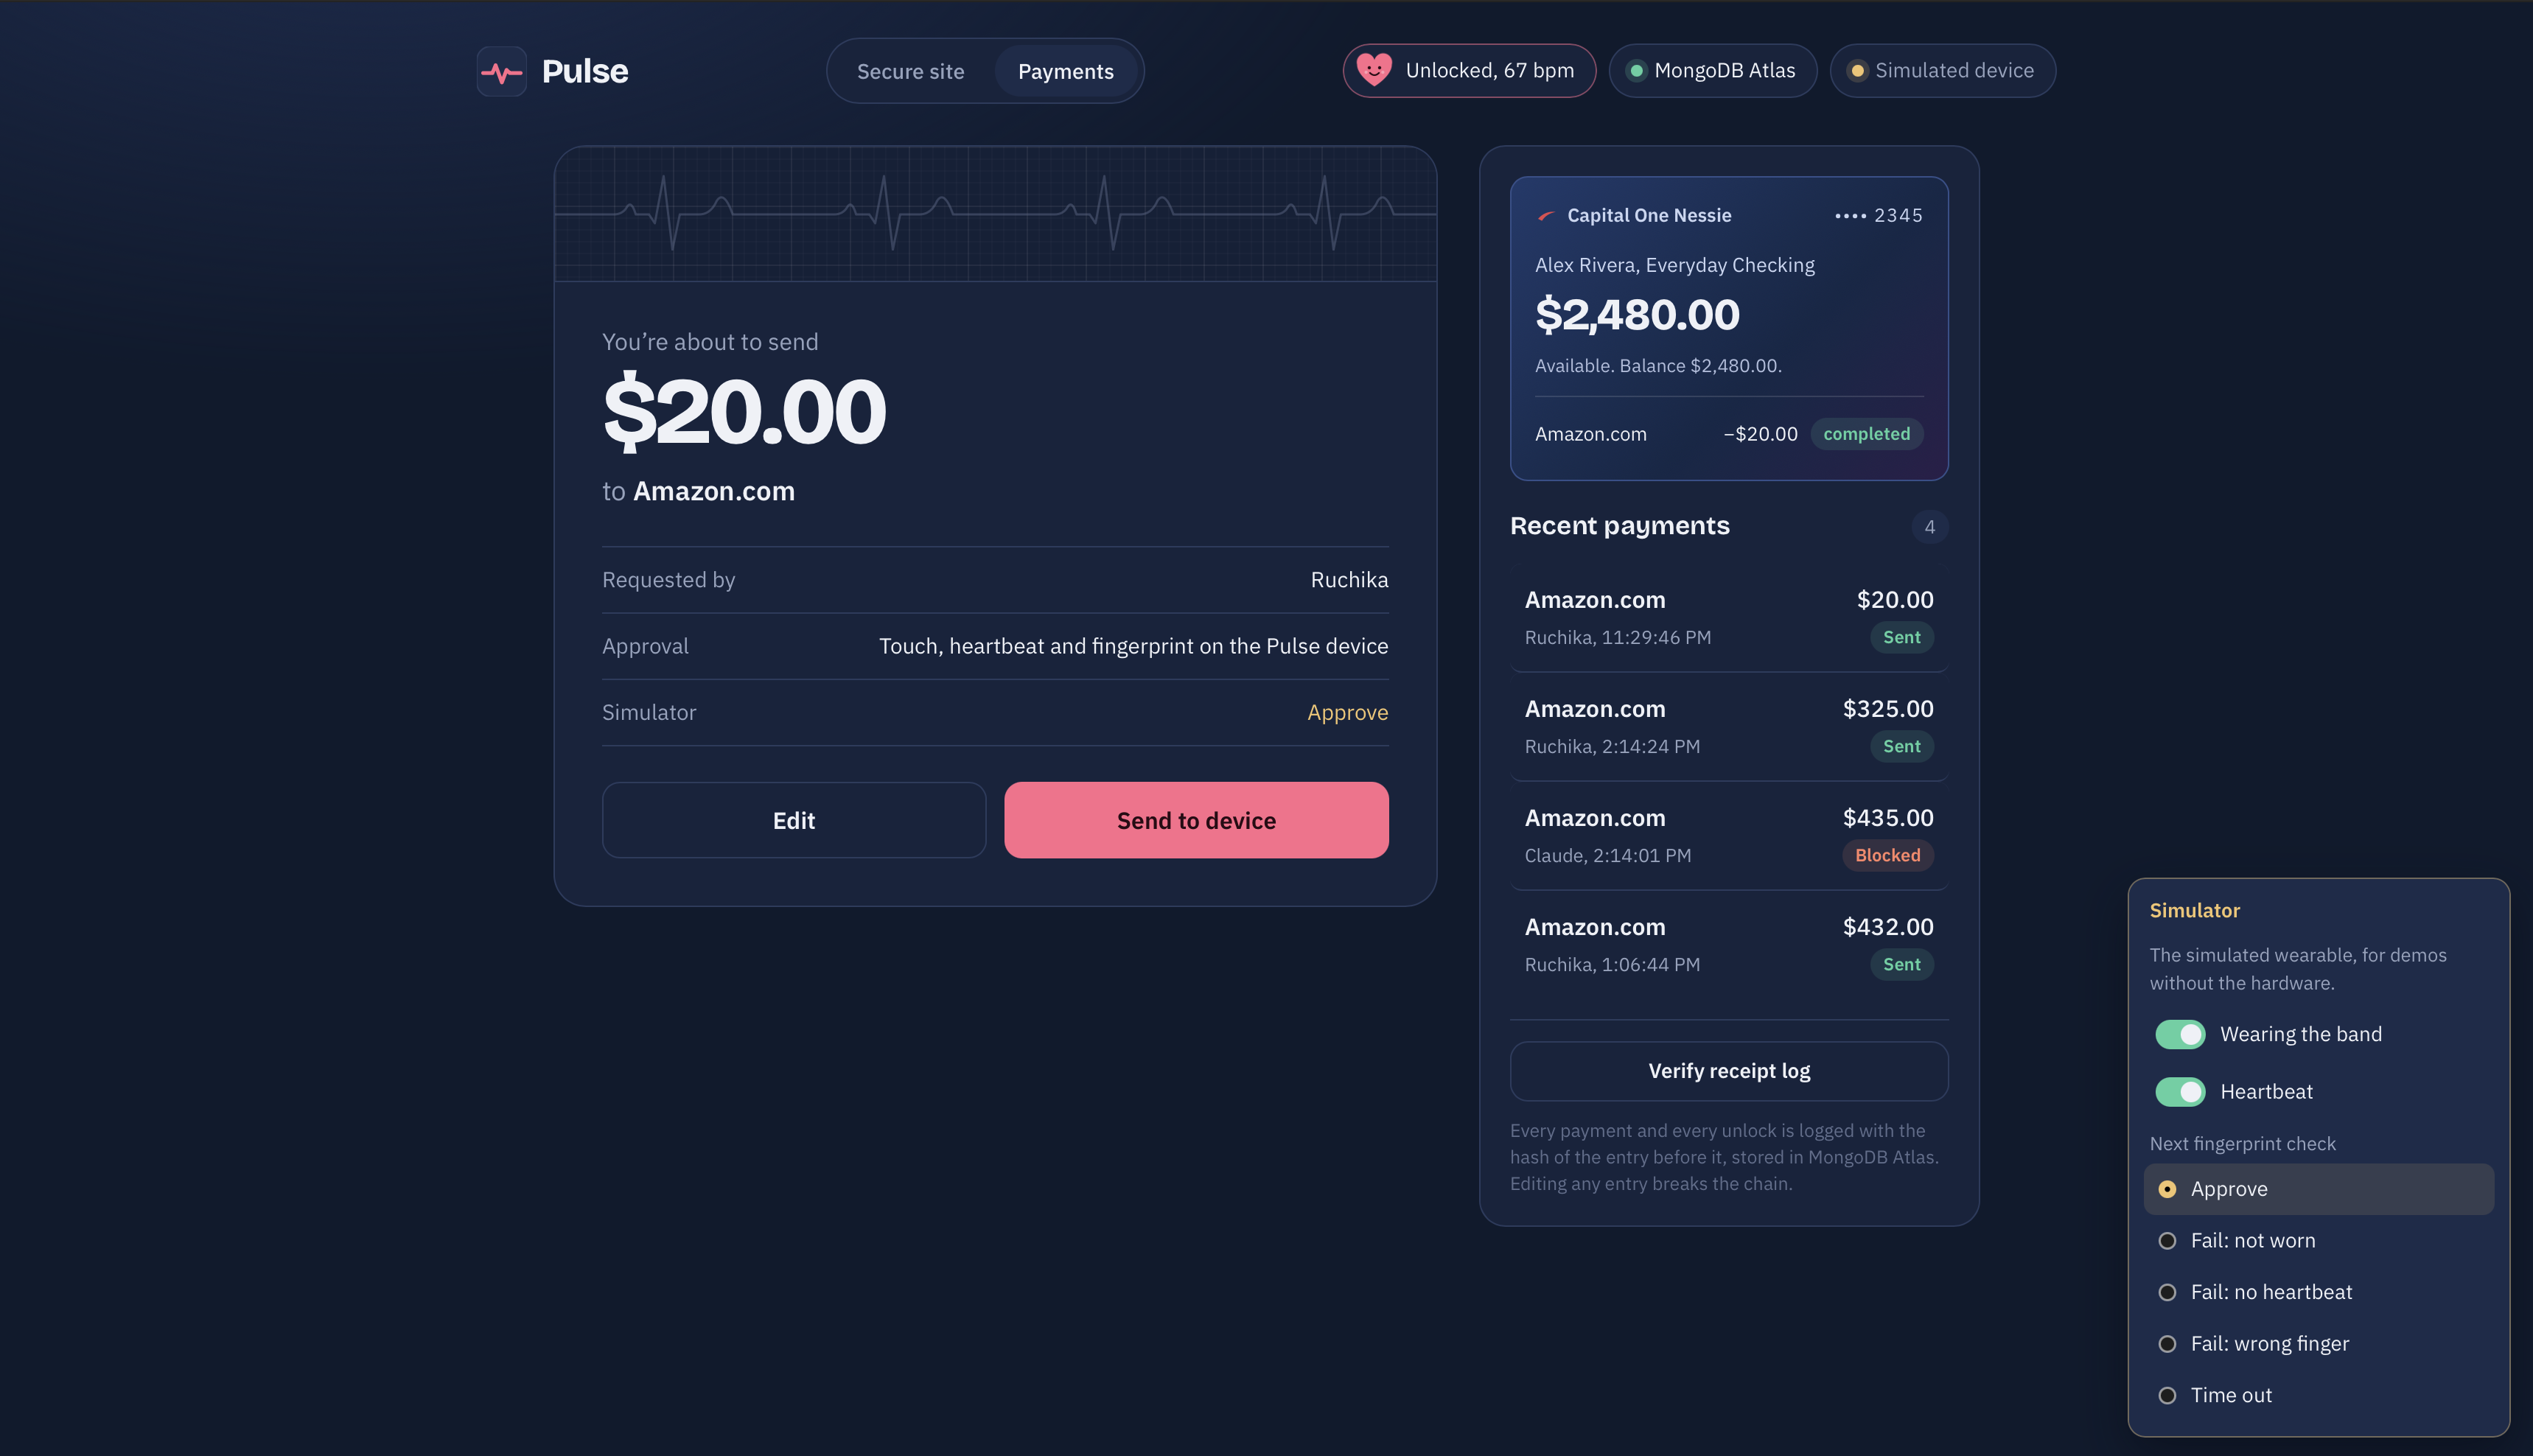
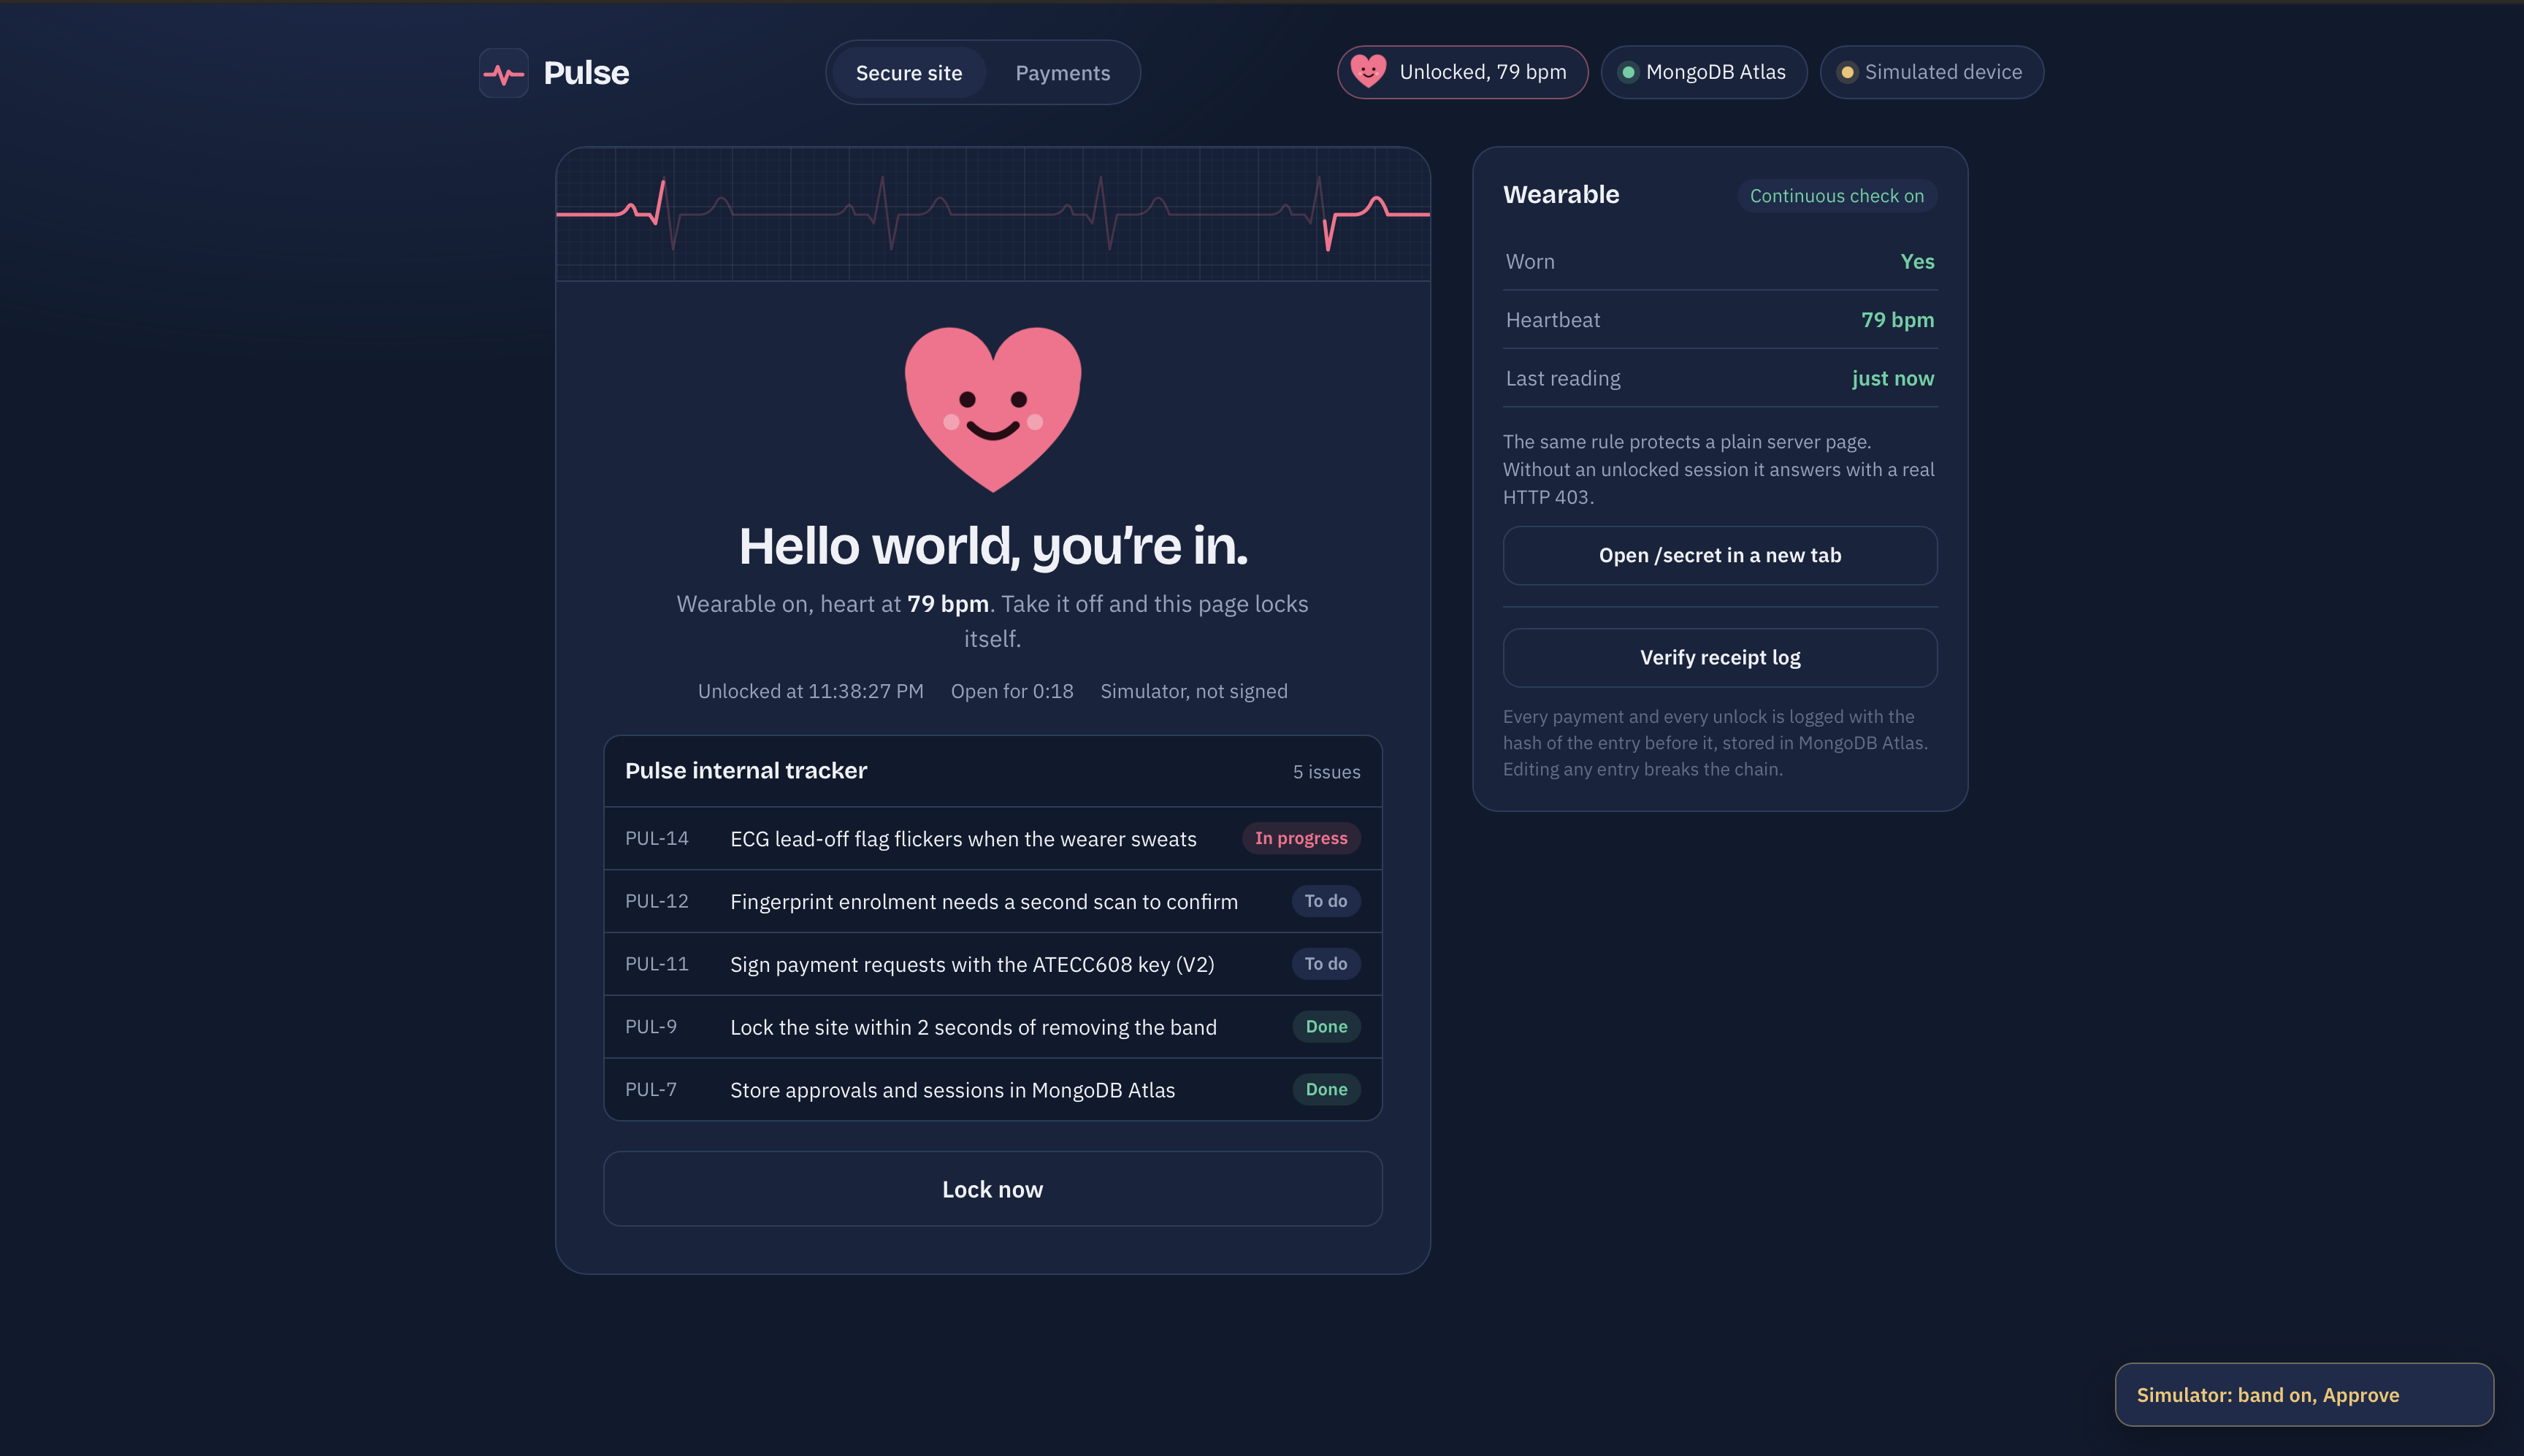
When an AI agent requests a payment on NoHeartNoCart, the backend (Python/FastAPI) opens the purchase at Capital One via the Nessie API, where the funds are held, and queues the request for the wearable. The Pulse polls over Wi-Fi through our Cloudflare Tunnel at noheartnocart.biz, shows the payee and amount on its OLED, and runs three checks: presence and liveness from a live ECG heartbeat (MAX30003), then identity with an on-sensor fingerprint match (R503). The fingerprint never leaves the sensor. Only if every check passes does the ATECC608 secure element sign SHA-256(request + "|authorized") with an ECDSA P-256 key that can never leave the chip. The server verifies that signature against the device’s public key before telling Capital One to settle, so a compromised laptop can’t forge an approval, change the amount, or replay an old one. A failed check declines the purchase and releases the hold. Every unlock and payment is written to MongoDB Atlas as a SHA-256 hash-chained receipt: editing any record breaks the chain, and the site’s “Verify receipt log” pinpoints the tampered entry. The same wearable also gates a protected website that returns a real HTTP 403 until you unlock with your pulse.
Secure, Transparent, and Responsive...
We built the device using enterprise grade biometric sensors. Our tech stack includes the ESP32S3 Pro, ECG 3 click, R503 fingerprint sensor, and an Attec608B cryptographic processor. All these put together on a feather shield powered by a LiPo battery encased in a temperature resistant PETG enclosure grant a secure and quick experience to login and approve transactions. Provider name and requested amount is displayed on the OLED display and an interactive controller layout let's you accept or deny the request.
Hurdles and how we overcame them...
Some of the biggest challenges we ran into included firmware compatibility between the microcontrollers, and cable compatibility between the sensors. Some other difficulties were our encryption protocols and were set up across the server and wearable. Continuous presence without false lockouts involved determining the difference between inconsistent readings and actually taking the device off, this hurdle made us look into timed lockouts to address the data.
Milestones and what makes us Shine...
We're really proud of our authentication protocol system design and the failure cases we've implemented to protect against tampering and penetration attempts. Furthermore our Human-in-the-loop design brings back supervised actionable items that ensure an auditable transaction record.
What we learned...
We've learned the importance of proper system design and interdisciplinary work. Our project involved Cybersecurity, software engineering, electrical design, and mechanical engineering; all of which came together for a deliverable that could be demo'd. Moving forward we will implement our new found understanding of encryption protocols, database hosting, and biomedical sensing to further refine our projects to products.
What's next for NoHeartNoCart
Our next steps are to continue to iterate and provide our project for the better good of the people. We plan to ship Pulse as a drop-in human-approval layer for agentic payments: an SDK so any agent framework can require a signed human approval above a spending threshold, per-device key enrollment and rotation, continuous presence with tuned lead-off detection so sessions lock the moment the band comes off, and a smaller, battery-optimized enclosure for all-day wear.
Built With
- autodesk-fusion-360
- c++
- cloudflare
- cursor
- cybersecurity
- github
- javascript
- nessie
- orca-slicer
- python
- react
- troubleshooting


