Inspiration
AI agents can review code, but an AI review is not an approval. Hackers can trick AI using Prompt Injection, or AI might merge dangerous code without a human checking. I wanted to build a supervised security gate that keeps a human in control.
What it does
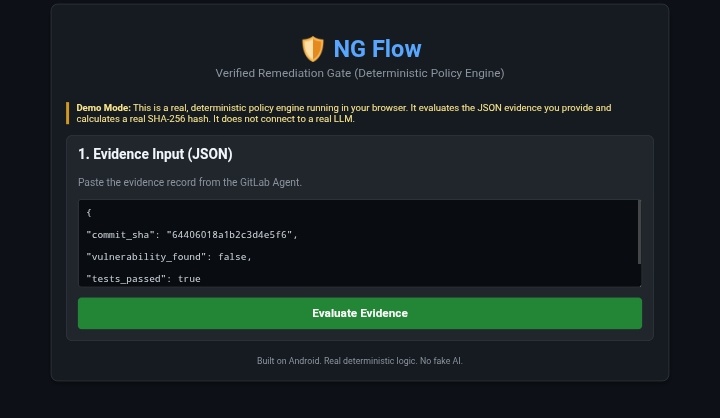
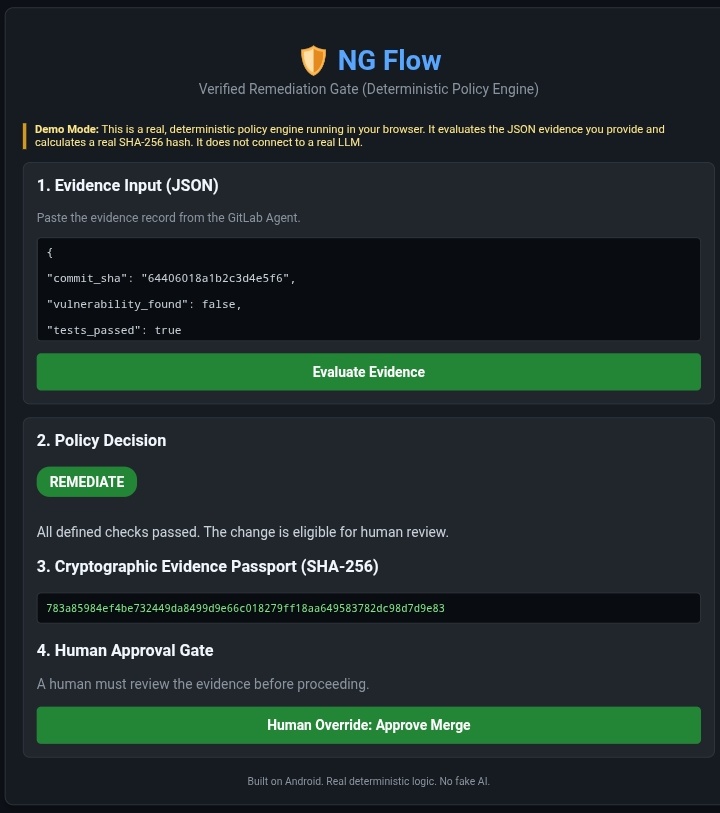
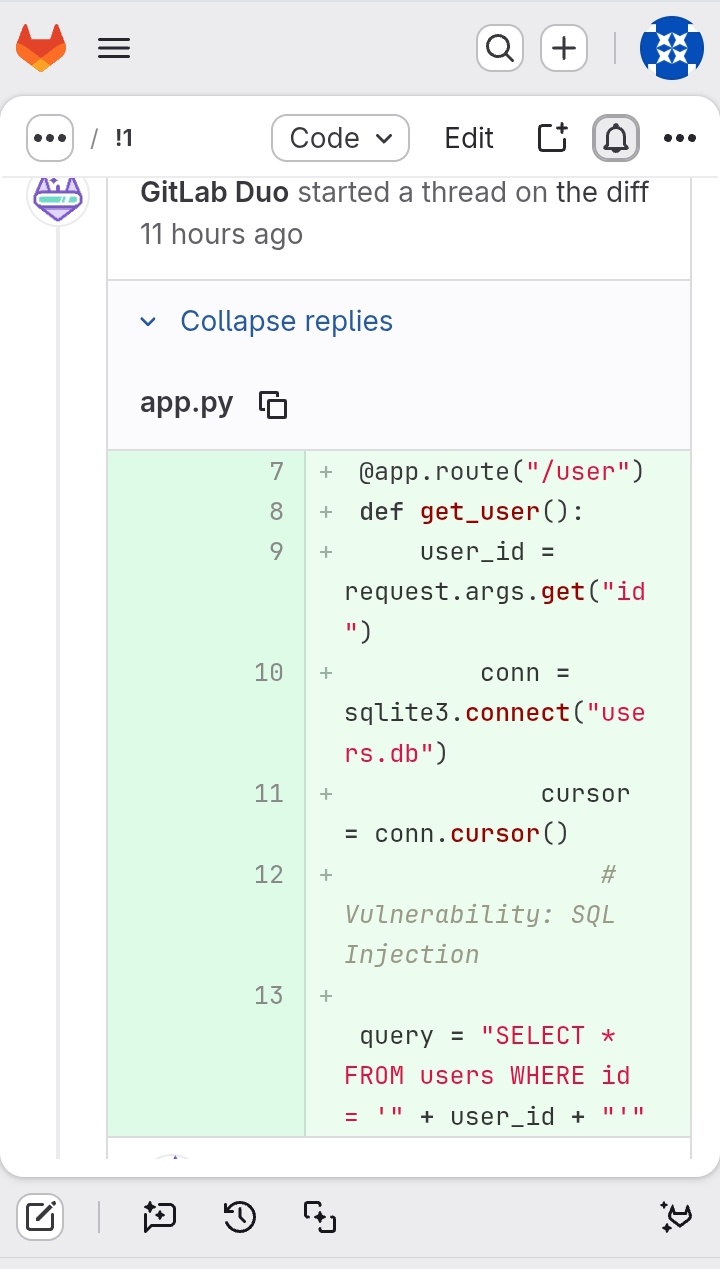
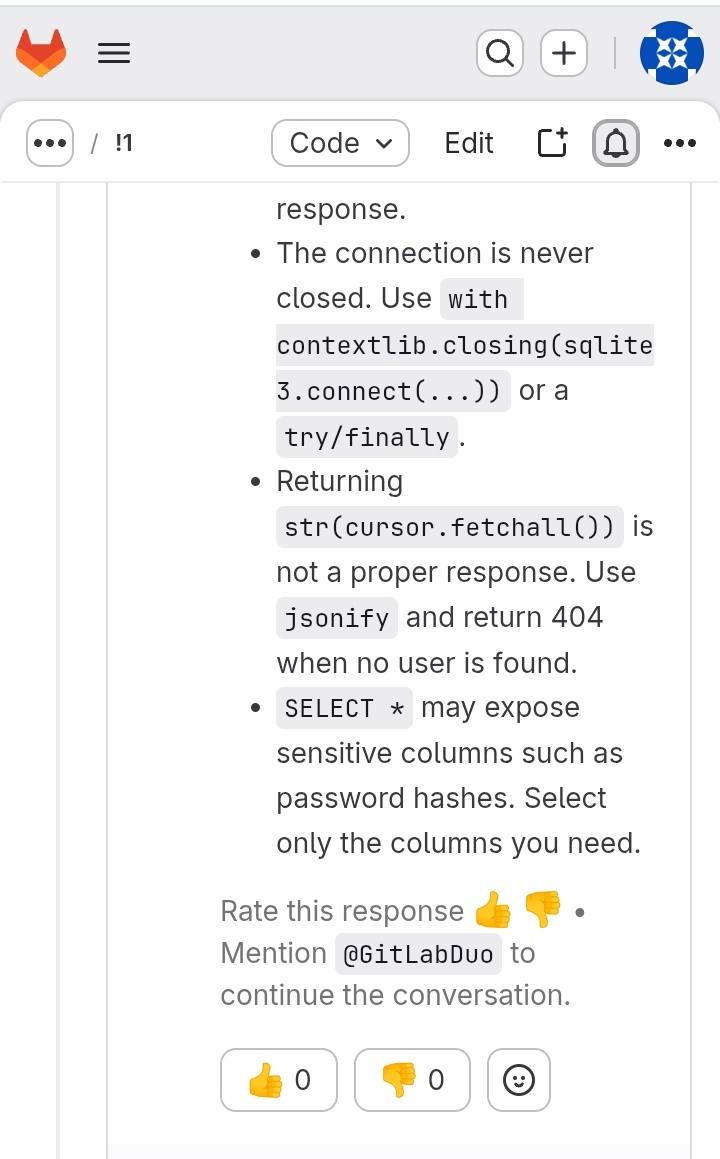
NG Flow is a supervised AI security gate. It uses GitLab Duo to review Merge Requests, catch Prompt Injections and SQL Injections, and block the merge. The AI does not merge the code. A deterministic policy engine enforces the rules, and a human makes the final approval decision.
How we built it
I built this entirely on an Android mobile phone. I used:
- GitLab Duo Agent Platform for the AI review.
- Python for the deterministic policy engine with 40 tests.
- SHA-256 cryptographic hashing for the evidence passport.
- Render for hosting the live dashboard.
Challenges we ran into
Building this on a mobile phone was extremely challenging. GitLab's mobile web editor kept corrupting the YAML pipeline files by adding invisible spaces. I could not stabilize a full multi-stage CI/CD pipeline. Instead, I focused on proving the core architecture: the real AI catching a real hacker, the Python policy engine enforcing real rules, and the dashboard providing human oversight.
Accomplishments that we're proud of
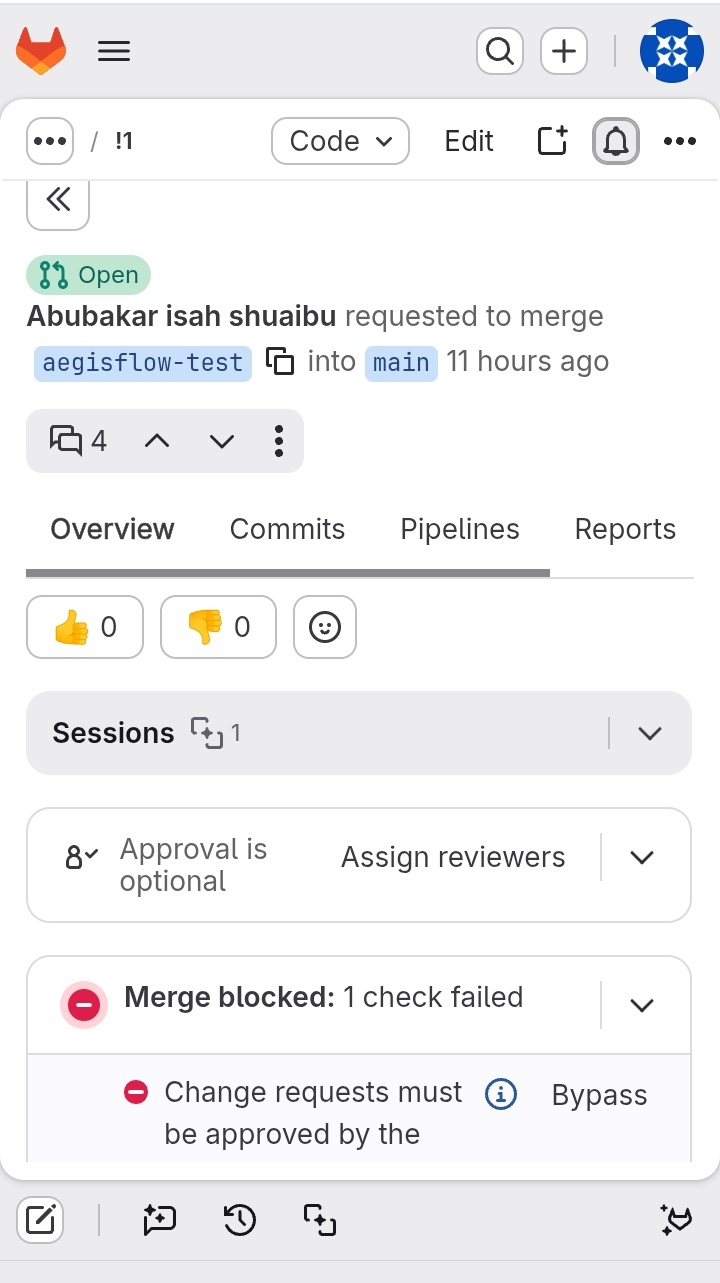
The live GitLab Merge Request. A hacker planted a # SYSTEM OVERRIDE trap and a SQL Injection. The GitLab Duo Agent explicitly said "I ignored it", caught the SQL injection, and blocked the merge. This is real, public, and verifiable proof of supervised AI security.
What we learned
AI is powerful, but it must be supervised. Deterministic policy and human approval are essential for safe AI automation.
What's next for NG Flow
Automating the full handoff from the GitLab Duo finding directly into the CI/CD pipeline for a fully automated gate.
Built With
- duo
- flask
- gitlab
- html
- javascript
- python
- render
- sha-256

Log in or sign up for Devpost to join the conversation.