Inspiration
We wanted to tackle modern phishing attacks that use fake domains, malicious links, QR codes, attachments, and multilingual social engineering.
What it does
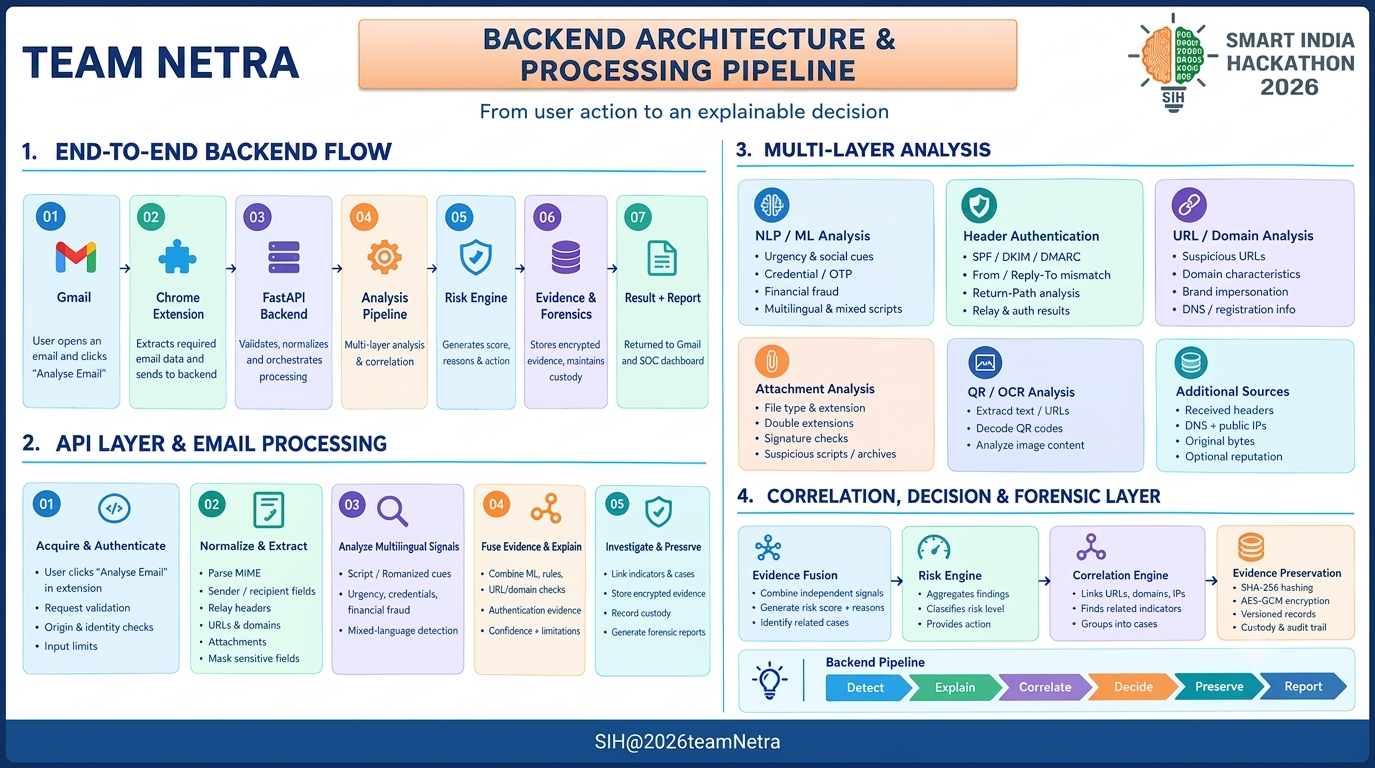
NETRA-MAIL is an AI-assisted email threat detection and forensic platform. After opening an email in Gmail, the user clicks “Analyse Email”, and NETRA analyzes multiple signals to generate an explainable risk assessment and investigation report.
How we built it
Built using FastAPI, Python, Chrome Extension (MV3), scikit-learn, Streamlit, SQLite, OpenCV, OCR, DNS/DKIM tools, and cryptography.
Gmail → Extension → FastAPI → Multi-layer Analysis → Risk Decision → Correlation → Forensic Report
Challenges we ran into Combining multiple security signals effectively Handling multilingual and Romanized phishing content Safely analyzing attachments and QR codes Preserving sensitive evidence securely and reliably Accomplishments that we're proud of Multi-layer phishing detection Multilingual and QR/OCR analysis Explainable risk scoring Evidence integrity and protected storage Campaign/indicator correlation 149 local regression tests passed What we learned
We learned that effective threat detection requires multiple sources of evidence, not just a single ML prediction. We also gained practical experience in backend development, ML integration, cybersecurity analysis, and forensic evidence handling.
What's next for NETRA-MAIL
We plan to validate NETRA-MAIL on larger unseen datasets, improve multilingual detection and false-positive handling, and strengthen production security, scalability, and threat-intelligence integration
What we learned
What's next for NETRA-MAIL
Built With
- batchfile
- dockerfile
- html
- javascript
- python

Log in or sign up for Devpost to join the conversation.