Inspiration
Every developer ships bugs and security holes because the feedback loop is too slow. Manual code review is a bottleneck, and real security audits are expensive. We wanted an agent that thinks like a senior security engineer — one that doesn't just report problems, but actually fixes them and proves the fix with tests.
What it does
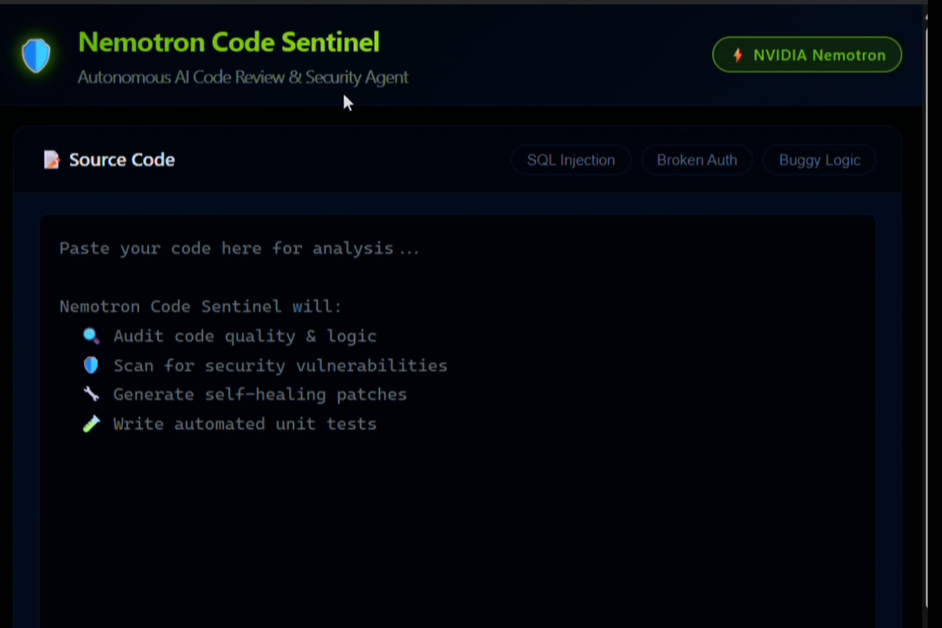
Nemotron Code Sentinel is an autonomous AI code-review agent with four modes:
- Code Audit — quality, logic bugs, performance, dead code, anti-patterns
- Security Scan — OWASP Top 10 and CWE vulnerabilities with severity, attack vector, and exact fix
- Auto-Patch — generates a complete self-healed version of the code with a side-by-side diff viewer
- Test Generator — writes a full unit-test suite covering happy paths, edge cases, and errors
Every result exposes Nemotron's full chain-of-thought reasoning trace, so you can see exactly how the model reached its conclusion. Reports, patches, and tests are all downloadable.
How we built it
- Backend: Node.js + Express (
/api/analyze,/api/fullscan,/api/health) - Frontend: vanilla HTML/CSS/JS — code editor, mode selector, reasoning-trace viewer, diff viewer, downloads
- Model: NVIDIA Nemotron 3.5 Lightning (reasoning model) via NVIDIA NIM's OpenAI-compatible API
- Agent layer: four specialized prompt pipelines (
agent/prompts.js), an orchestrator (agent/analyzer.js), and a resilient client (agent/client.js) with timeouts, retries, and 429 handling - Deployment flexibility:
LLM_BASE_URLandLLM_API_KEYare configurable, so the same code runs on NVIDIA NIM or Nebius Token Factory
Challenges we ran into
- Getting Nemotron to return consistent structured Markdown across four very different tasks
- Separating
reasoning_content(the chain of thought) fromcontent(the final answer) - Building a safe diff viewer without a heavy library, including XSS-safe rendering of model output with DOMPurify
- Handling long reasoning calls: we added a 2-minute timeout, one retry, and explicit 429 backoff
Accomplishments that we're proud of
- A fully working end-to-end agent — paste code, get a vulnerability report, a patched file, and a test suite
- Transparent reasoning instead of a black-box answer
- One-click downloads for reports, patches, and tests
- A clean, dependency-light UI that runs locally in seconds
What we learned
- Reasoning models need careful prompt scaffolding to produce parseable output
- Timeouts and retries are essential for long chain-of-thought calls
- Security tooling must itself be secure — sanitizing model-generated HTML is non-negotiable
What's next for Nemotron Code Sentinel
- GitHub Pull Request integration (review + auto-fix PRs)
- A VS Code extension
- Multi-file / whole-repository scanning
- CI/CD pipeline hooks to block vulnerable commits


Log in or sign up for Devpost to join the conversation.