-
-
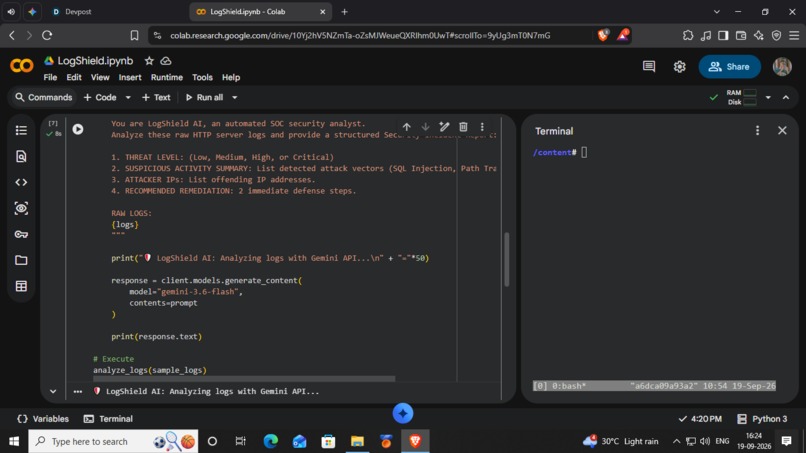
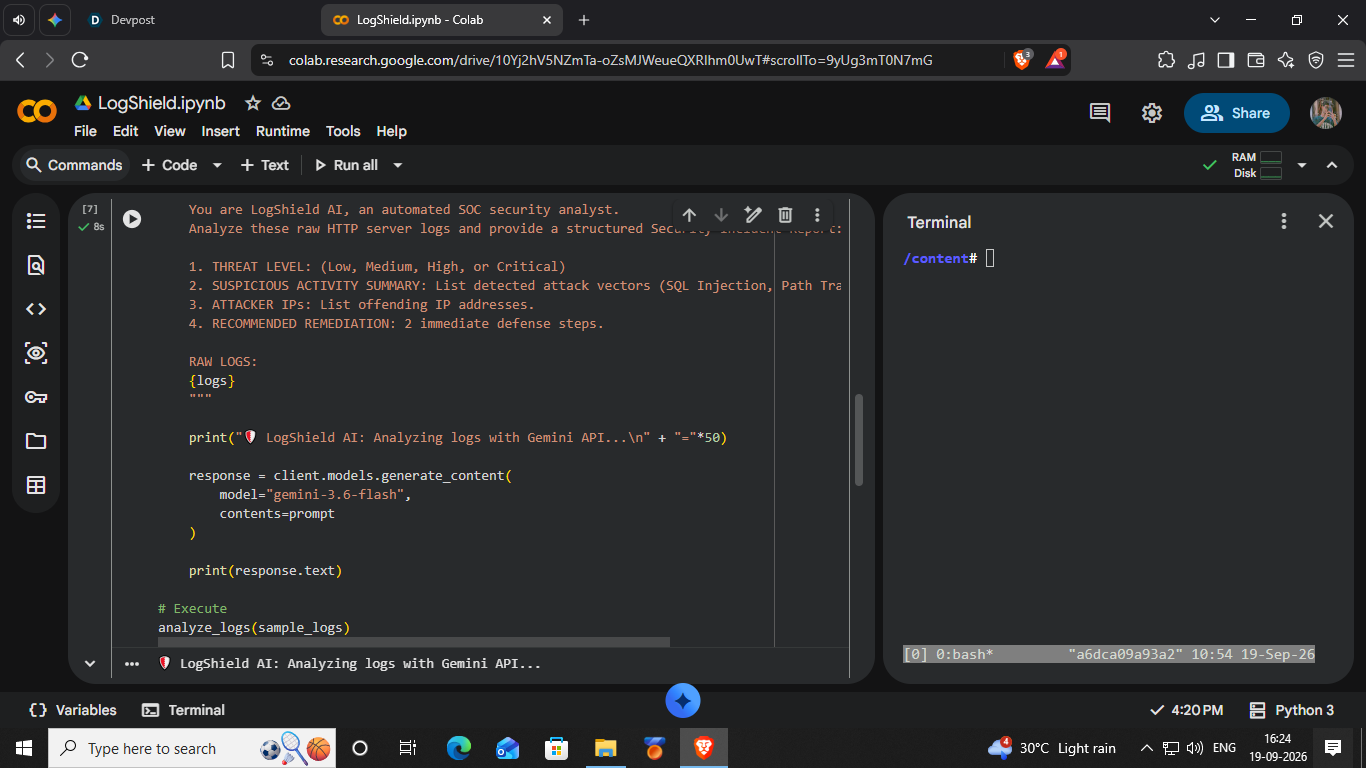
The execution cell making the client.models.generate_content() call.
-
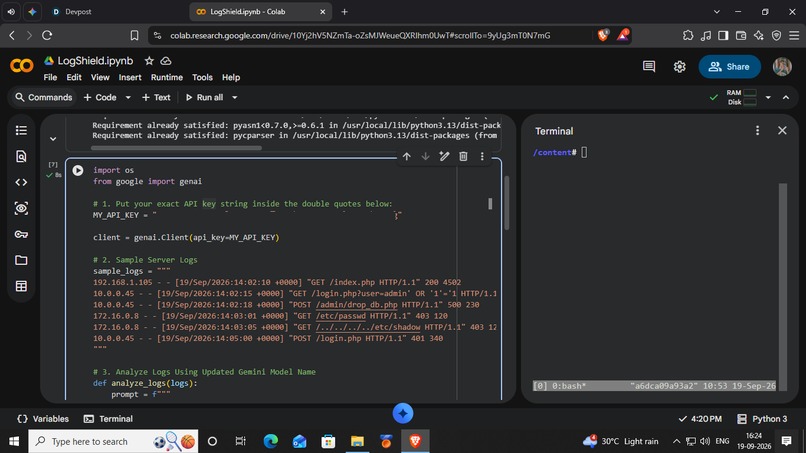
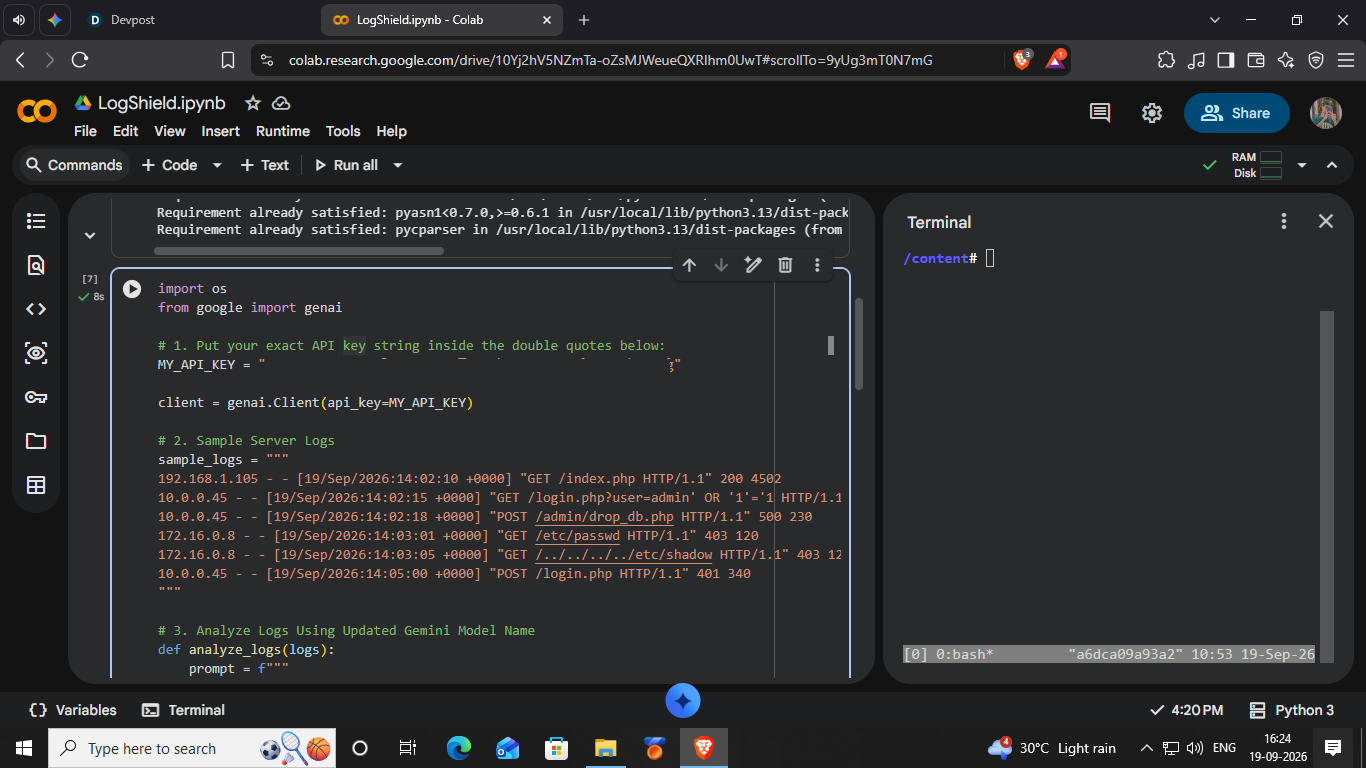
The complete code block showing the import statement, Gemini client initialization, and raw HTTP log setup.
-
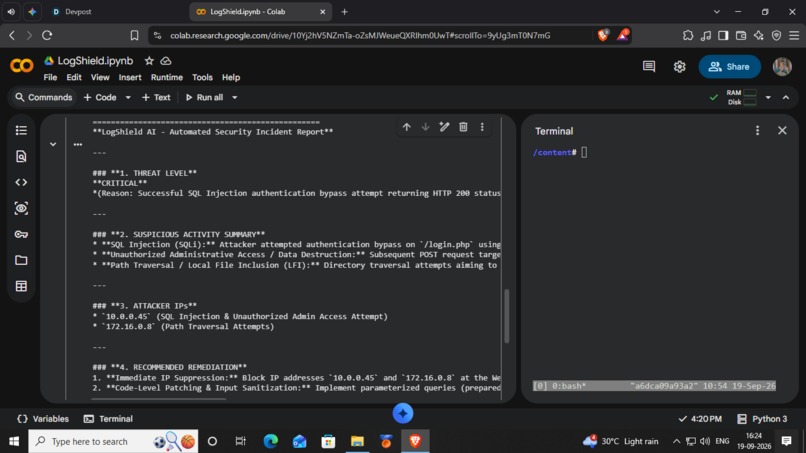
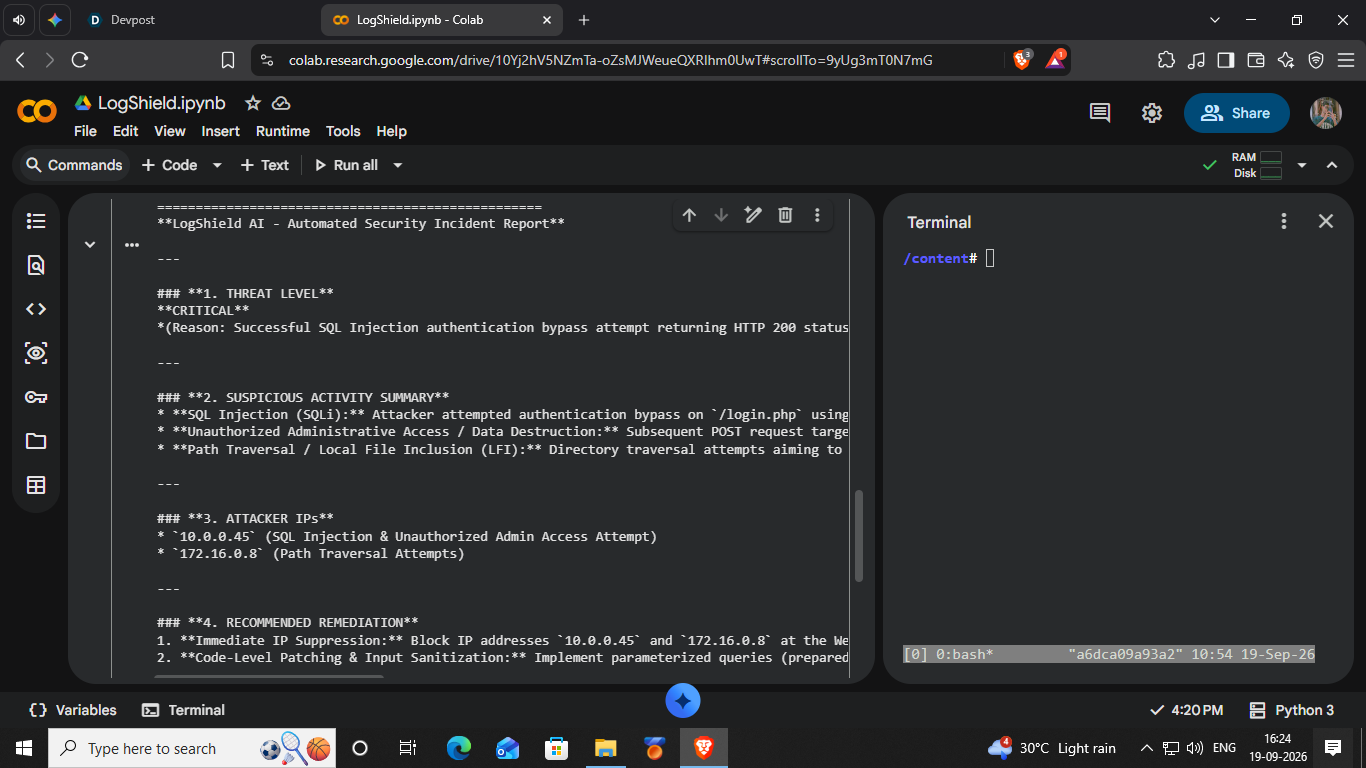
The structured output showing THREAT LEVEL, SUSPICIOUS ACTIVITY SUMMARY, ATTACKER IPs, and RECOMMENDED REMEDIATION.
-
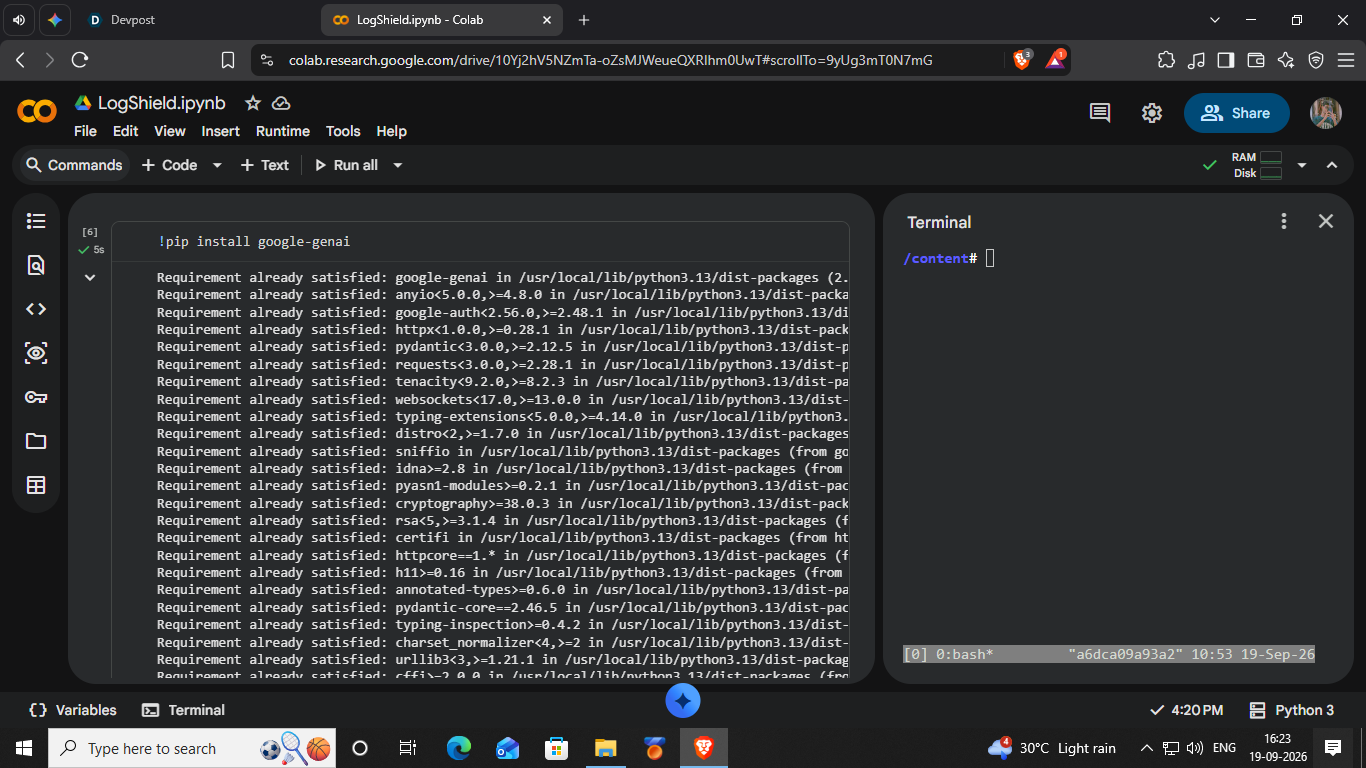
The package installation process.
Inspiration
Modern web applications generate massive volumes of server access logs every second. Security Operation Center (SOC) teams are often overwhelmed by false positives and manual log analysis when looking for malicious activity. We built LogShield AI to showcase how Large Language Models can act as an automated, instant SOC analyst that parses raw HTTP logs and flags active cyber threats in real time.
What it does
LogShield AI takes raw server access logs and analyzes them using the Google Gemini API. It automatically detects common cyber attack patterns, including:
- SQL Injection (SQLi) attempts in URL query strings.
- Path Traversal / Directory Traversal attacks targeting restricted files (e.g.,
/etc/passwd). - Brute Force & Unauthorized Access attempts on admin routes.
It instantly outputs a structured Security Incident Report containing:
- Overall Threat Level (Low, Medium, High, Critical)
- Suspicious Activity Summary
- Attacker IP Identification
- Recommended Immediate Remediation Steps
How we built it
- Python: Core scripting language for data ingestion and response handling.
- Google Gemini API (
google-genaiSDK): Powered by the latest Gemini model for high-accuracy contextual threat detection and structured security report generation. - Google Colab: Cloud runtime environment for rapid prototyping and executable code delivery.
Challenges we ran into
- Prompt engineering to ensure Gemini consistently categorizes threat severity level and identifies exact attacker IPs from raw log strings.
- Upgrading to the latest
google-genaiPython SDK interface and handling modern model specifications.
Accomplishments that we're proud of
- Successfully built a functional, end-to-end AI security tool in Google Colab that parses unstructured log data into clear, actionable SOC intelligence in seconds.
What's next for LogShield AI
- Integrating live log streams via webhooks or syslog adapters.
- Auto-executing firewall IP blocklists (e.g., Cloudflare/AWS Security Groups) based on Gemini threat ratings.
Built With
- ai
- cybersecurity
- google-colab
- google-gemini-api
- python

Log in or sign up for Devpost to join the conversation.