-
-
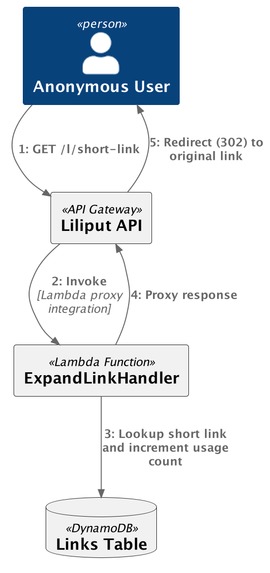
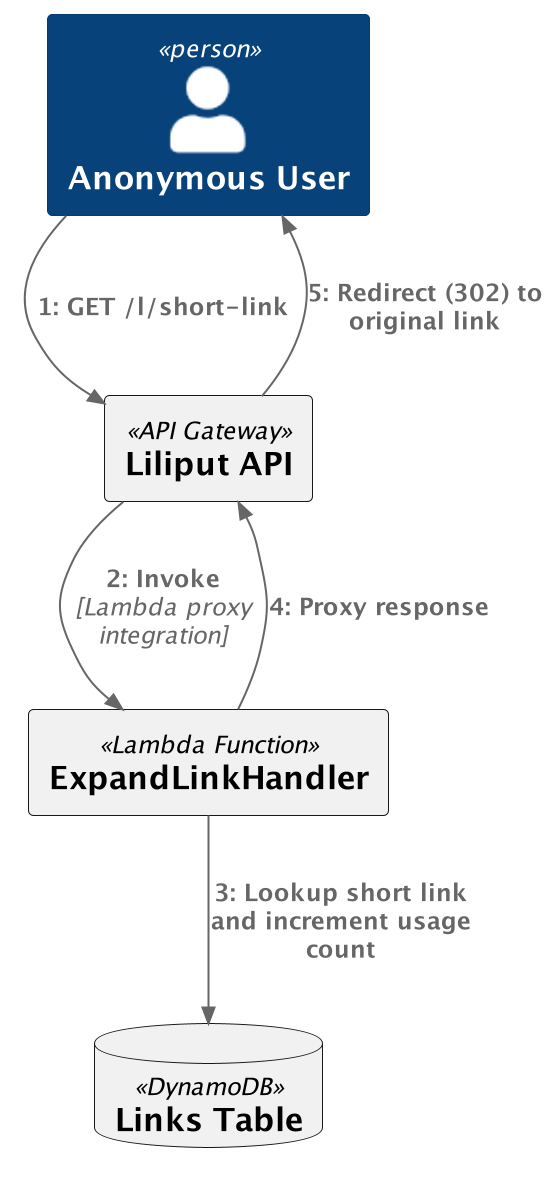
Visiting a short link
-
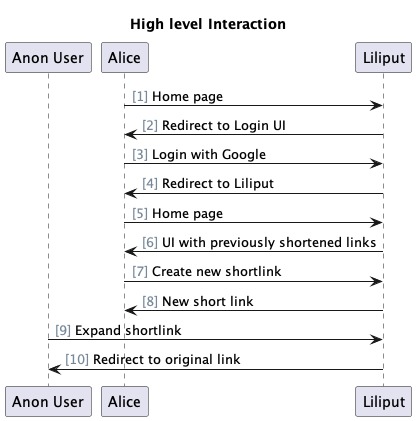
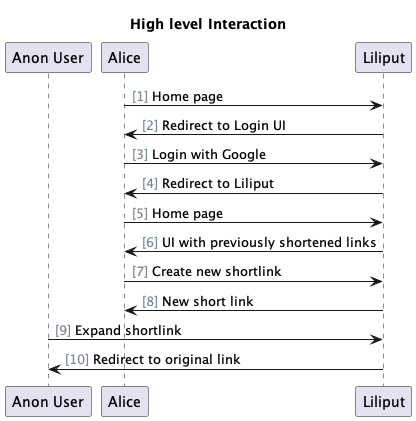
High level interaction with the user
-
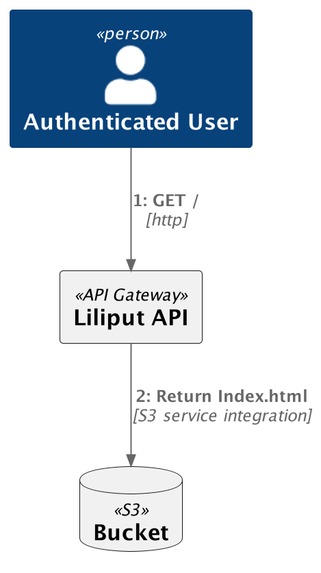
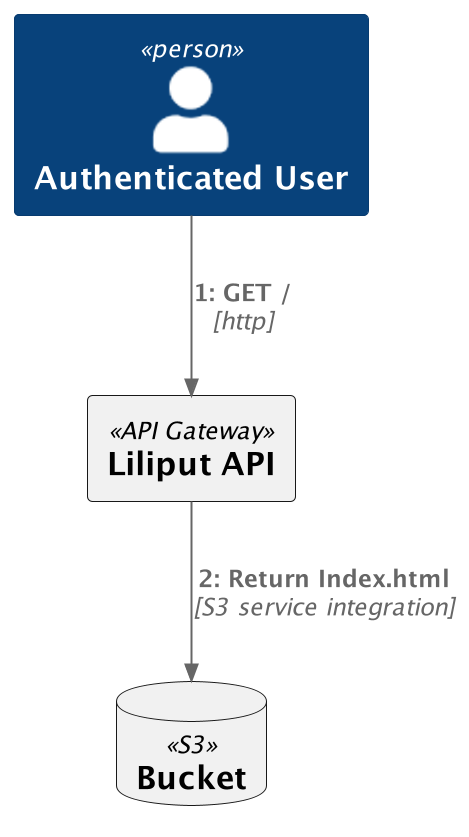
Serving of static files
-
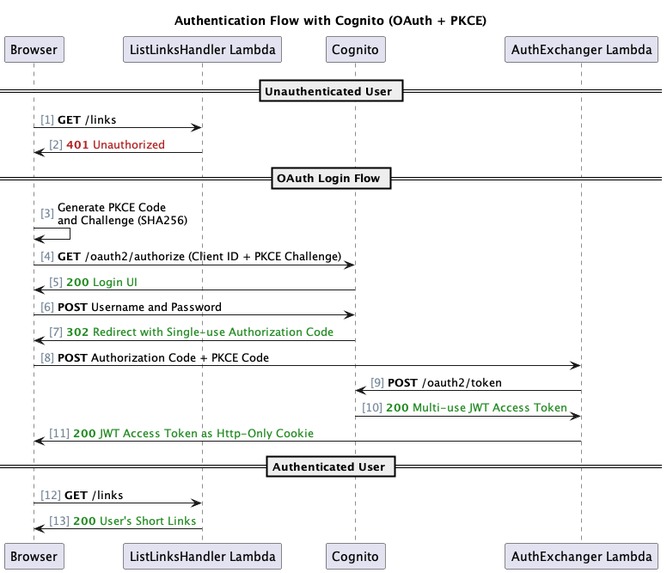
Authentication flow
-
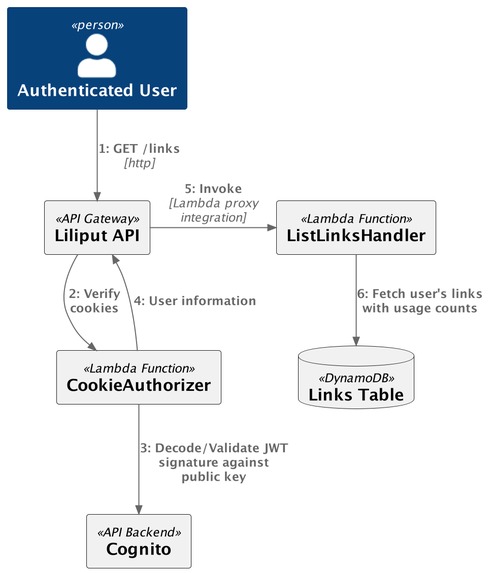
Showing list of previously created links
Inspiration
I wanted to learn how to use DynamoDB and AWS Lambda. I decided to build a URL shortener called Liliput, which is not an uncommon project but I wanted to focus specifically on
- Security: All operations in Liliput put security as a primary concern.
- Atomicity and uniqueness of short links: DynamoDB supports atomic counters, that is used in the link generation logic
What it does
Liliput is a secure, serverless shortener of URLs with the following features:
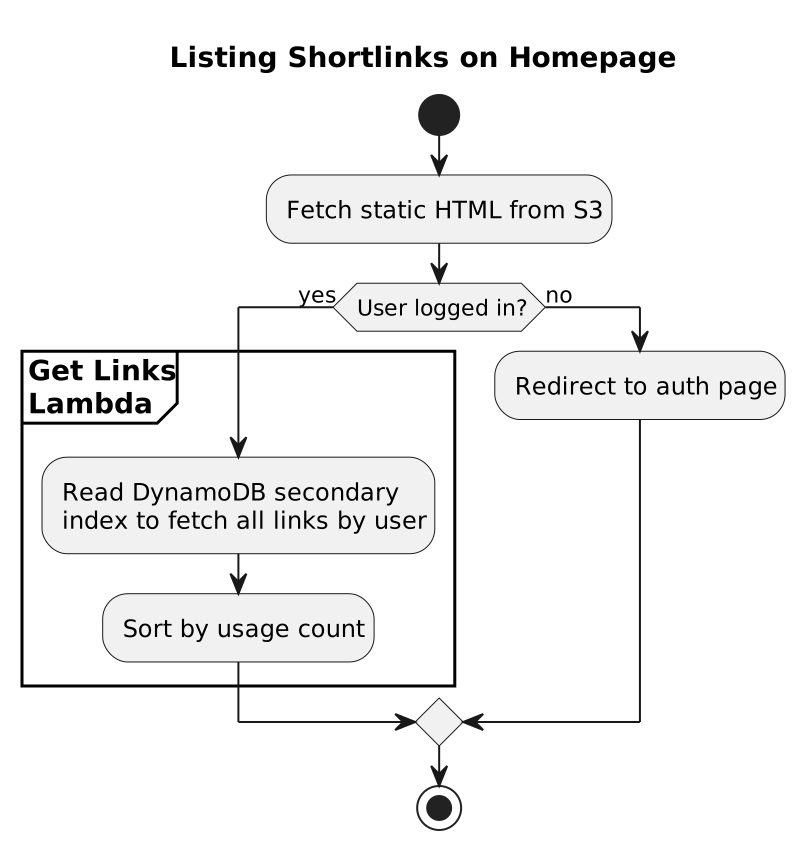
- Logged-in users can create links and view their previously created links
- Anonymous users can visit shortlinks
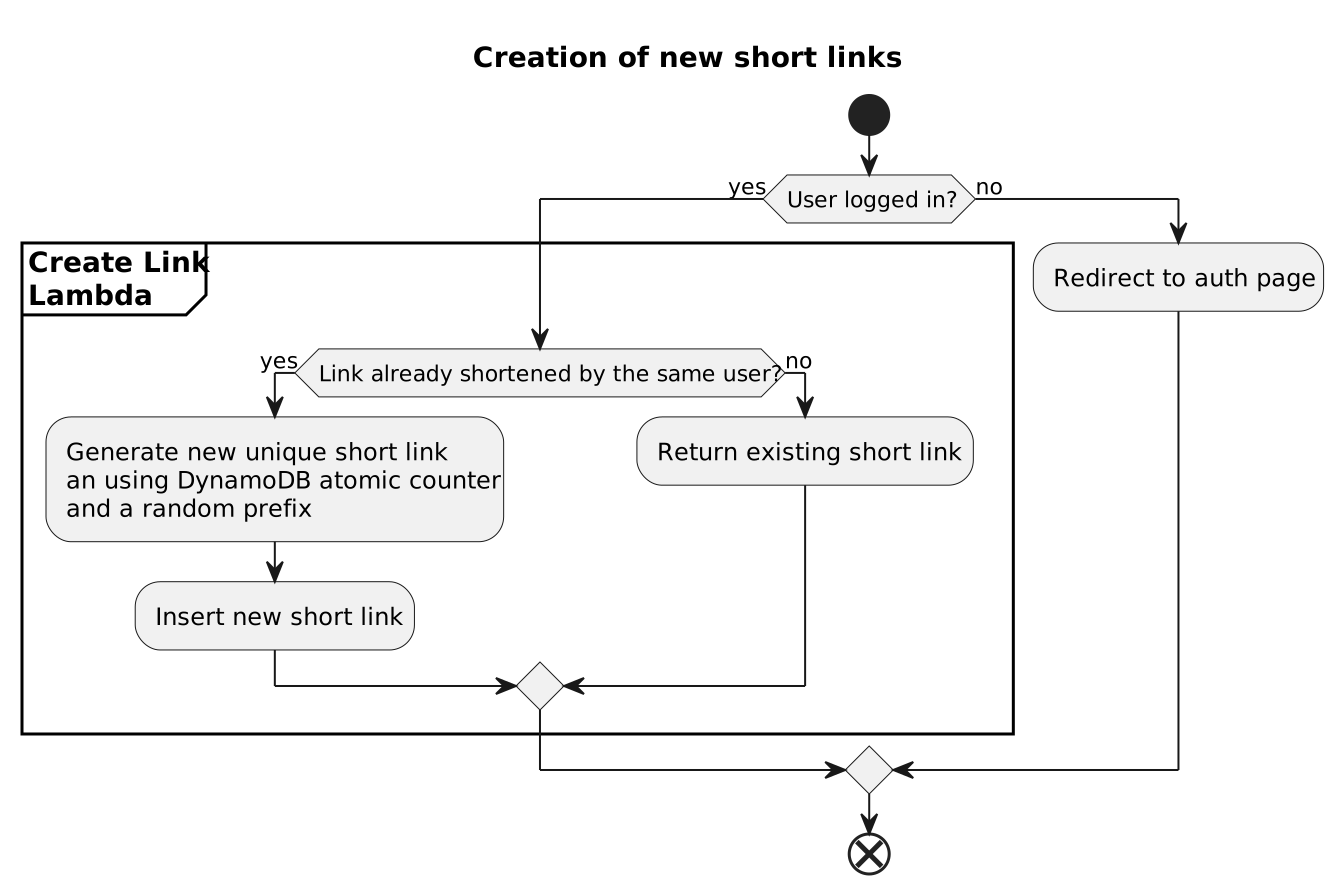
- All short links are unique to a user - if the same long link is shorted multiple times, the same short URL is returned
- Usage counts (expansion count) are tracked and displayed on the UI
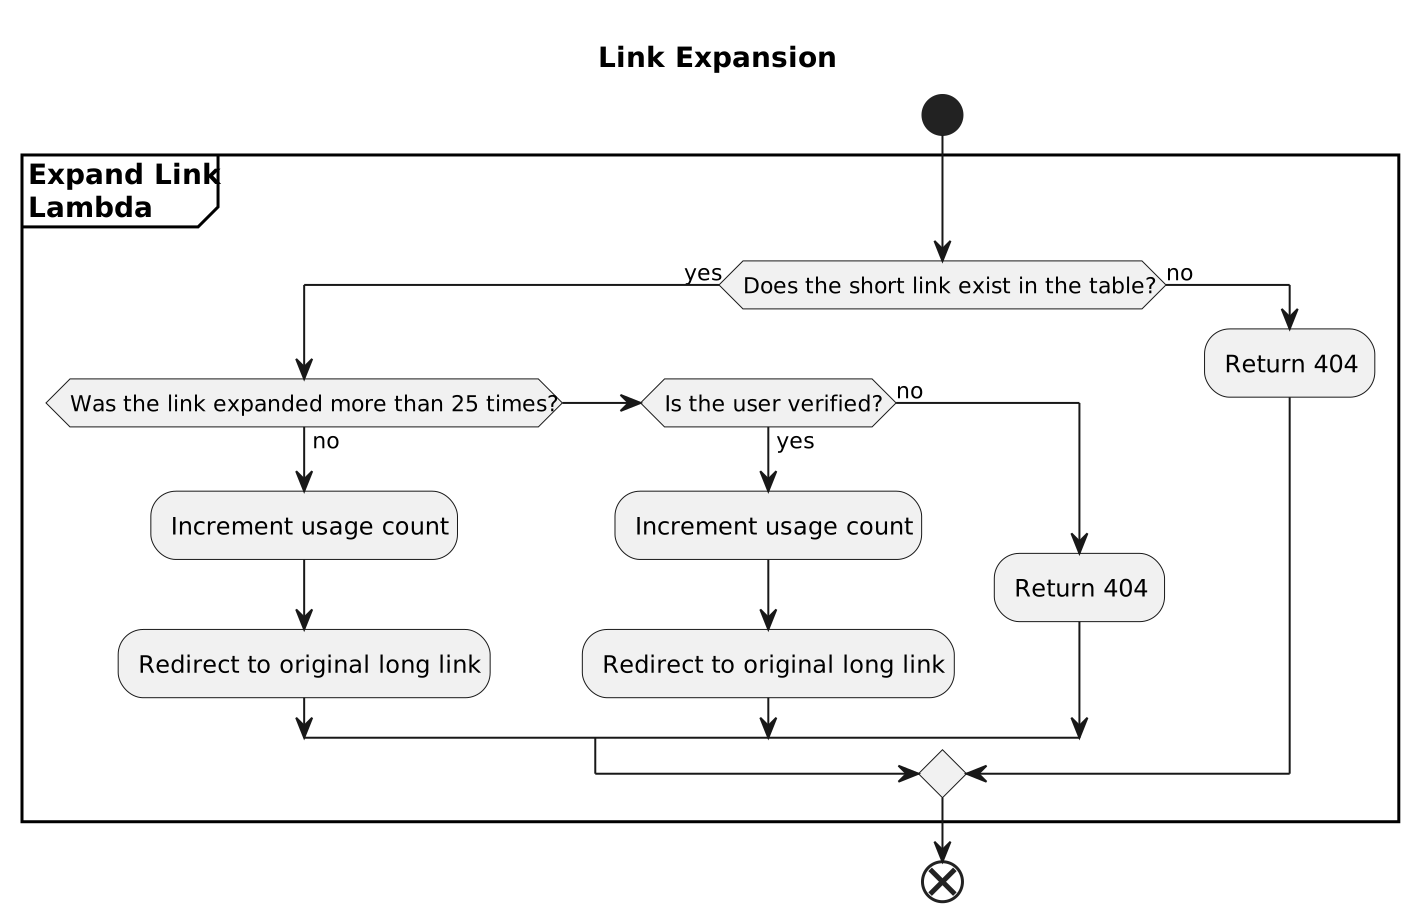
- Links can be expanded at most 25 times to prevent illegitimate usage (spam and phishing)
- Verified users can create links that can be expanded unlimited times (verification process is through the source code)
Focus on Security
This application is secure because:
- To create short links, you need a valid Google account
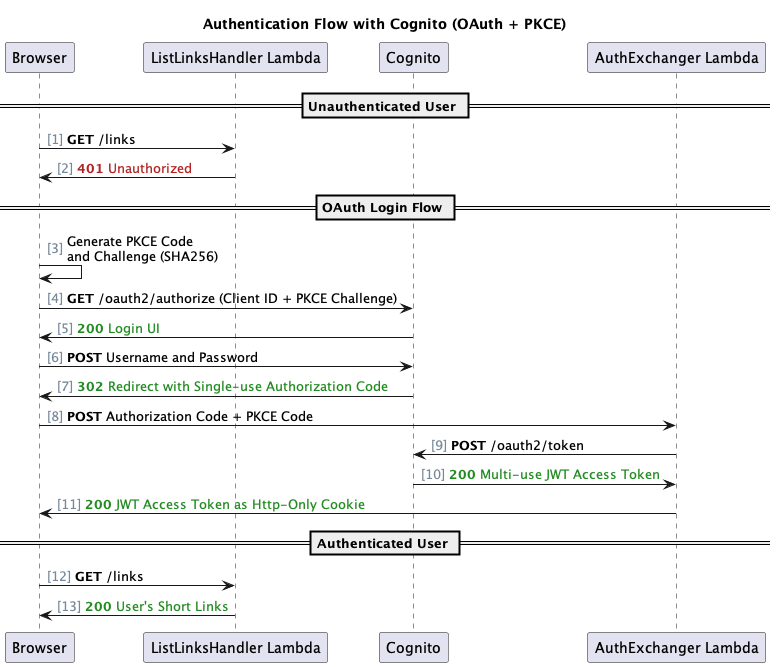
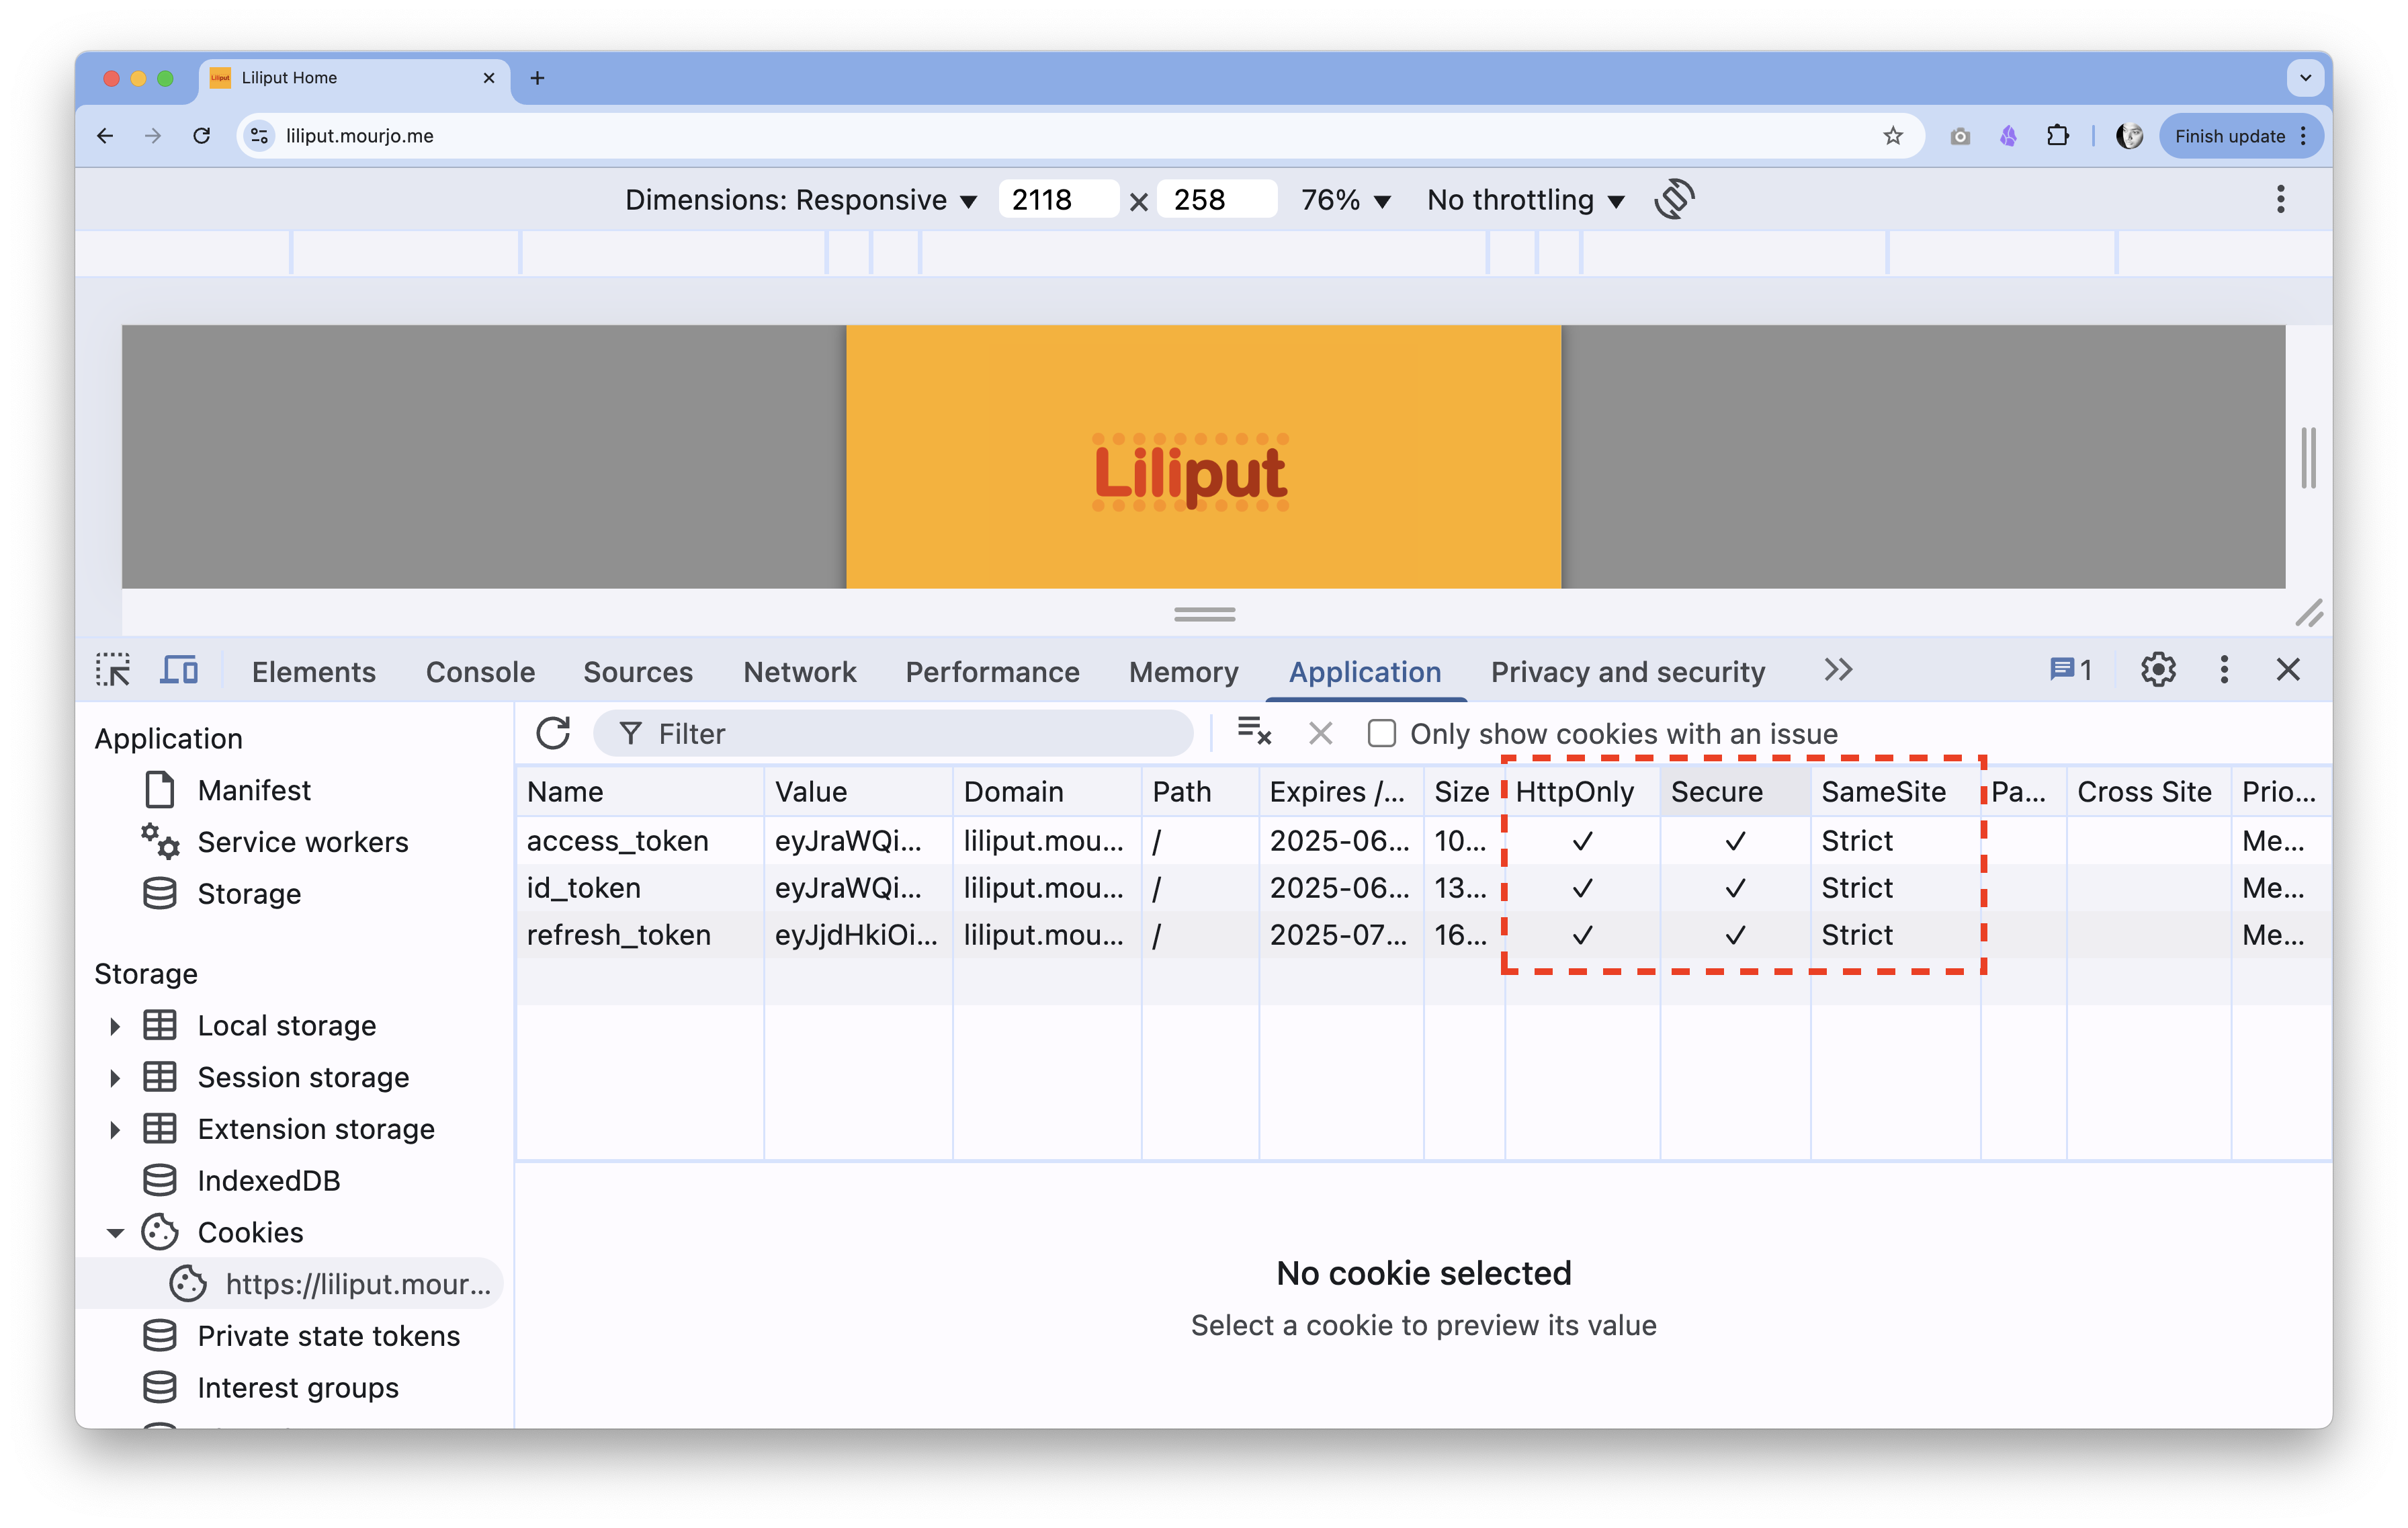
- Signing into Google uses the OAuth 2.0 with PKCE
- All cookies are HTTP-only (Javascript cannot access it)
- Links can only be expanded 25 times to prevent misuse, unless the user is verified
- All APIs are rate limited and alerts for when rate limit is breached
How we built it
The system uses:
- DynamoDB for storage
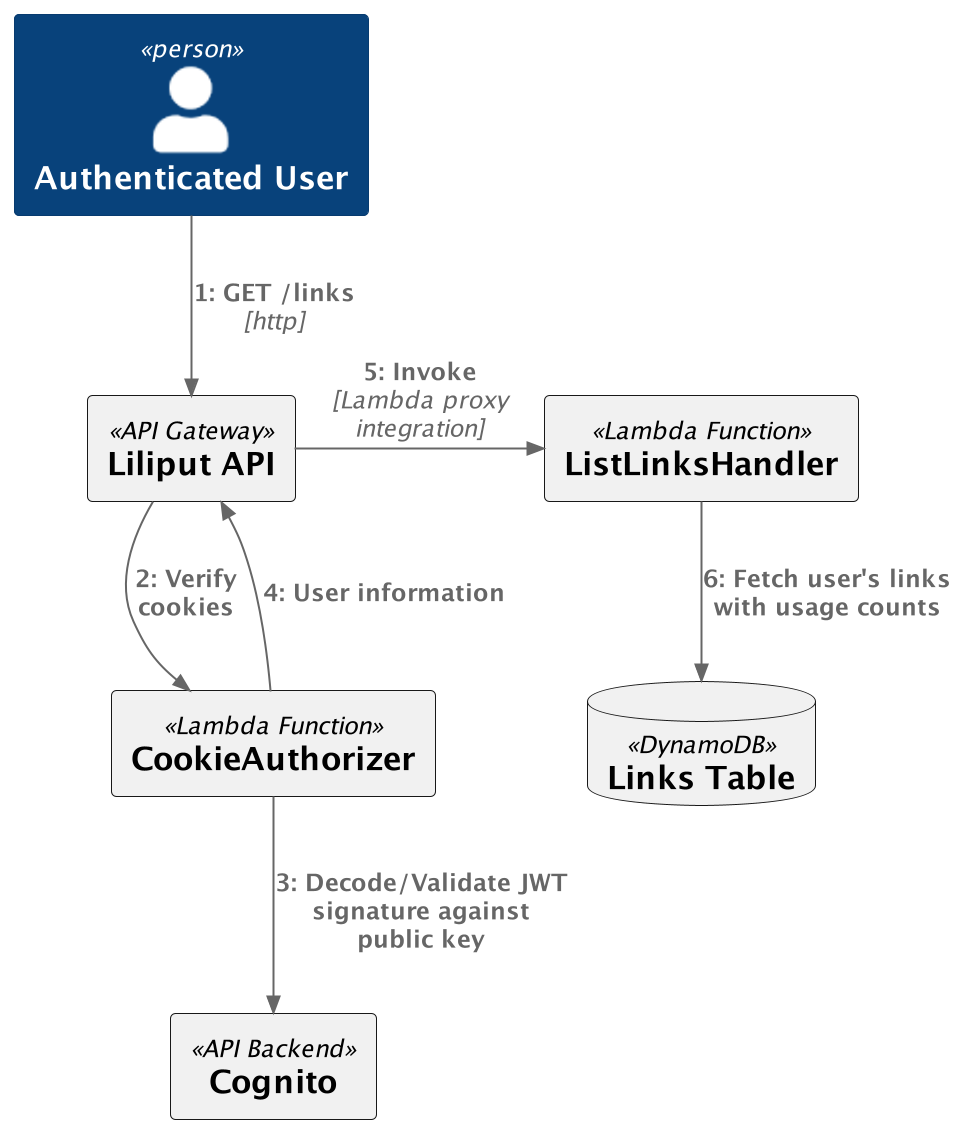
- Amazon Cognito and Google Oauth for login flows
- Lambda functions for logic implementation (shown below)
- API gateway for mapping lambda functions to routes
- Authorizer in API gateway with another Lambda function
- Public DNS (liliput.mourjo.me) for APIs
| Logged in Flows | Anonymous flows |
|---|---|
 |
 |
 |
Challenges we ran into
- Slow startup with Java based Lambda functions
- Managing login state in a single-page Javascript between the OAuth dance
What we learned
- Amazon Cognito integration with Google OAuth
- Authorizer middleware in API gateway with Lambda function
- Generating IAM policy document for giving access to only verified users
What's next for Liliput
- Verification without source code change
- Disable link expansions explicitly
- Switching between multiple Google accounts
- Searching for links shortened

Log in or sign up for Devpost to join the conversation.