-
-
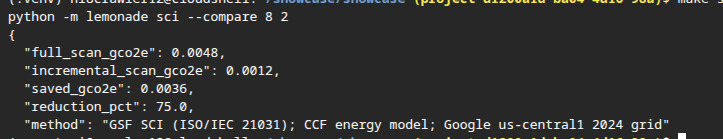
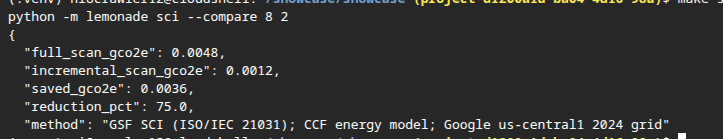
sci - emissions saved per run compared to incumbents
-
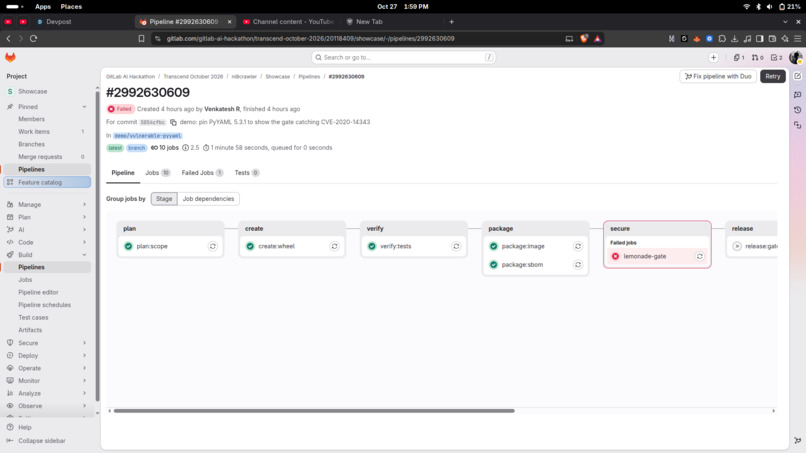
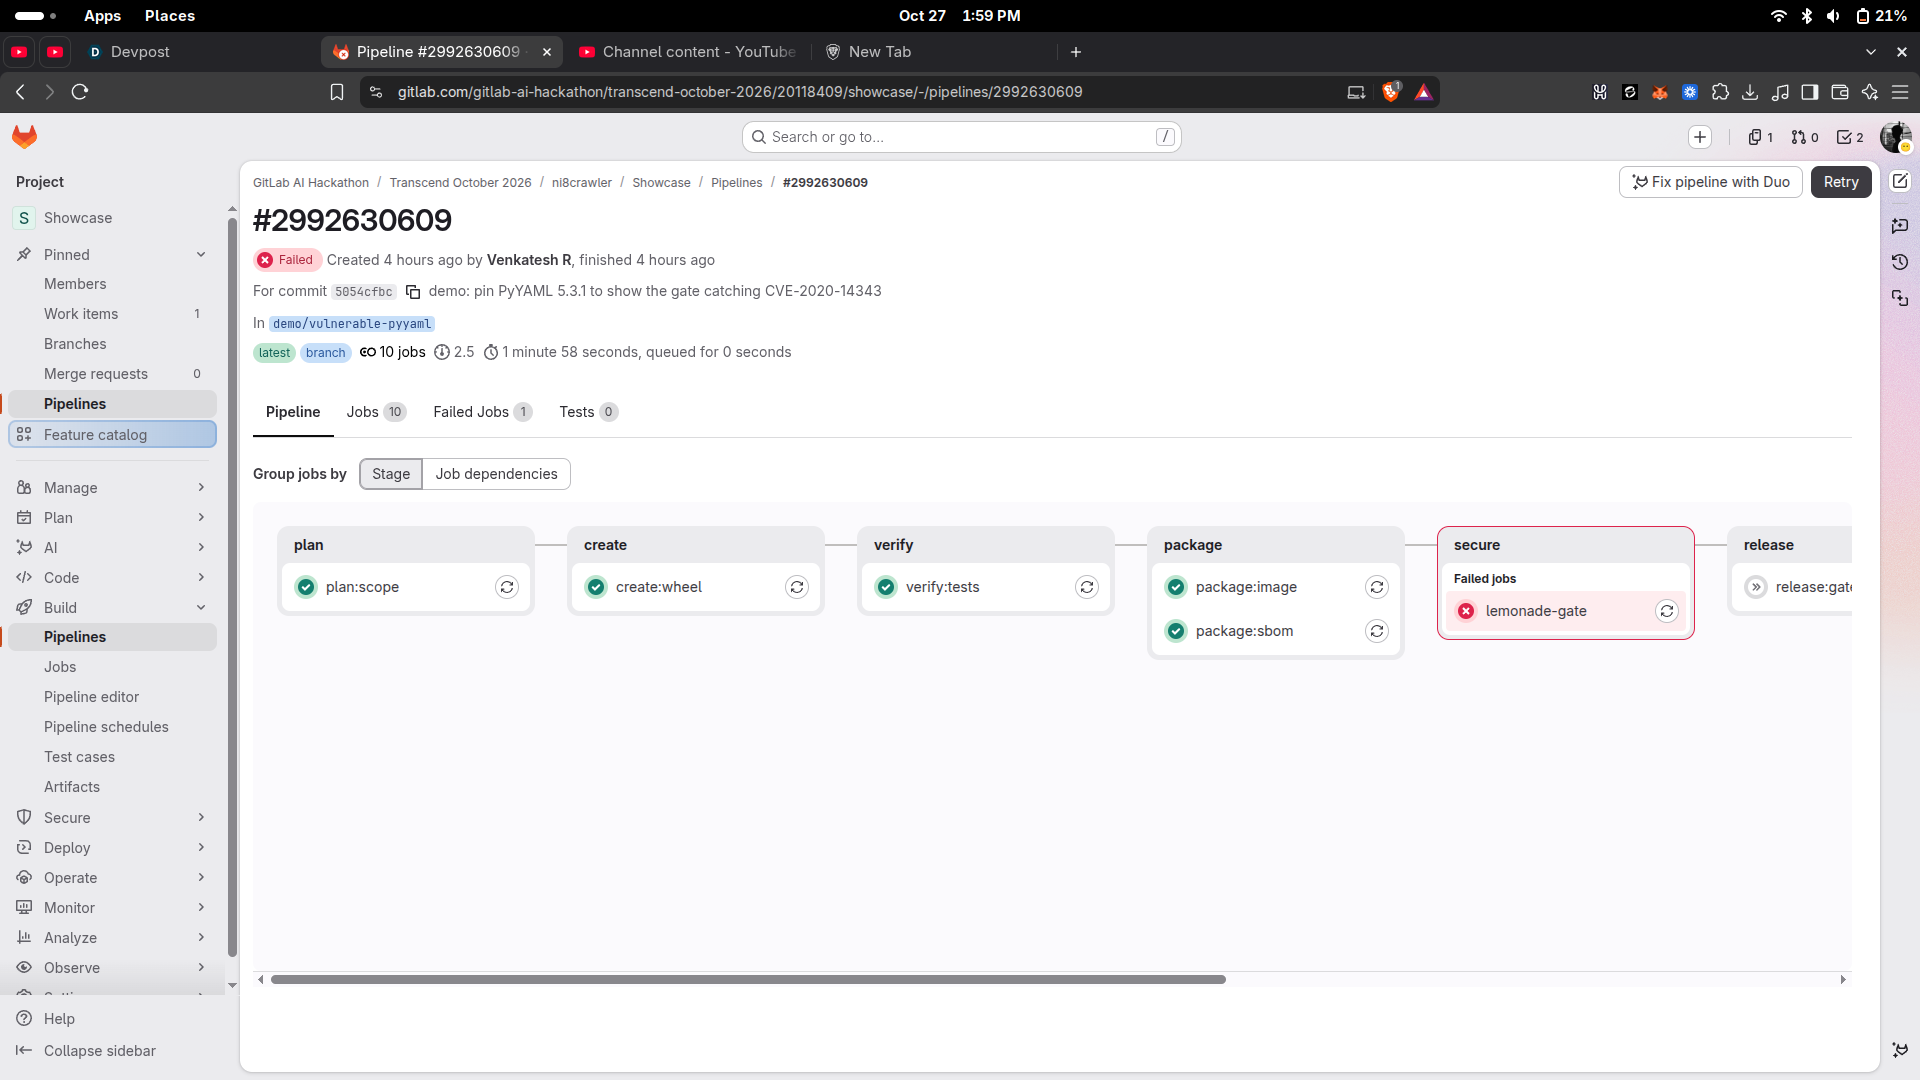
dependency injection - pipeline stop
-
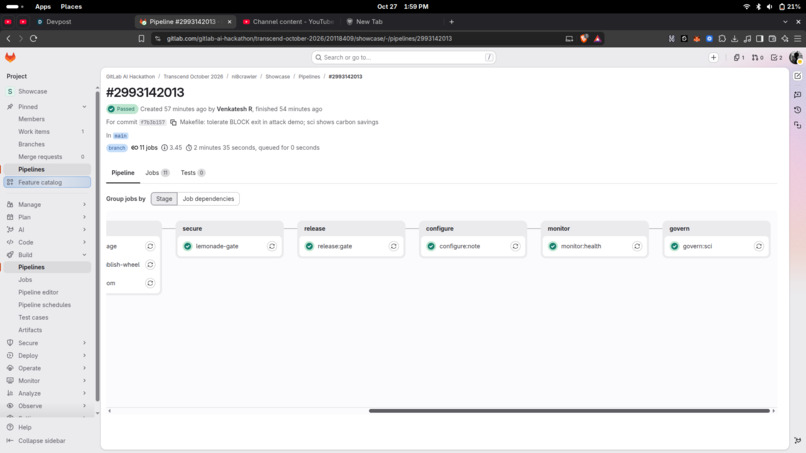
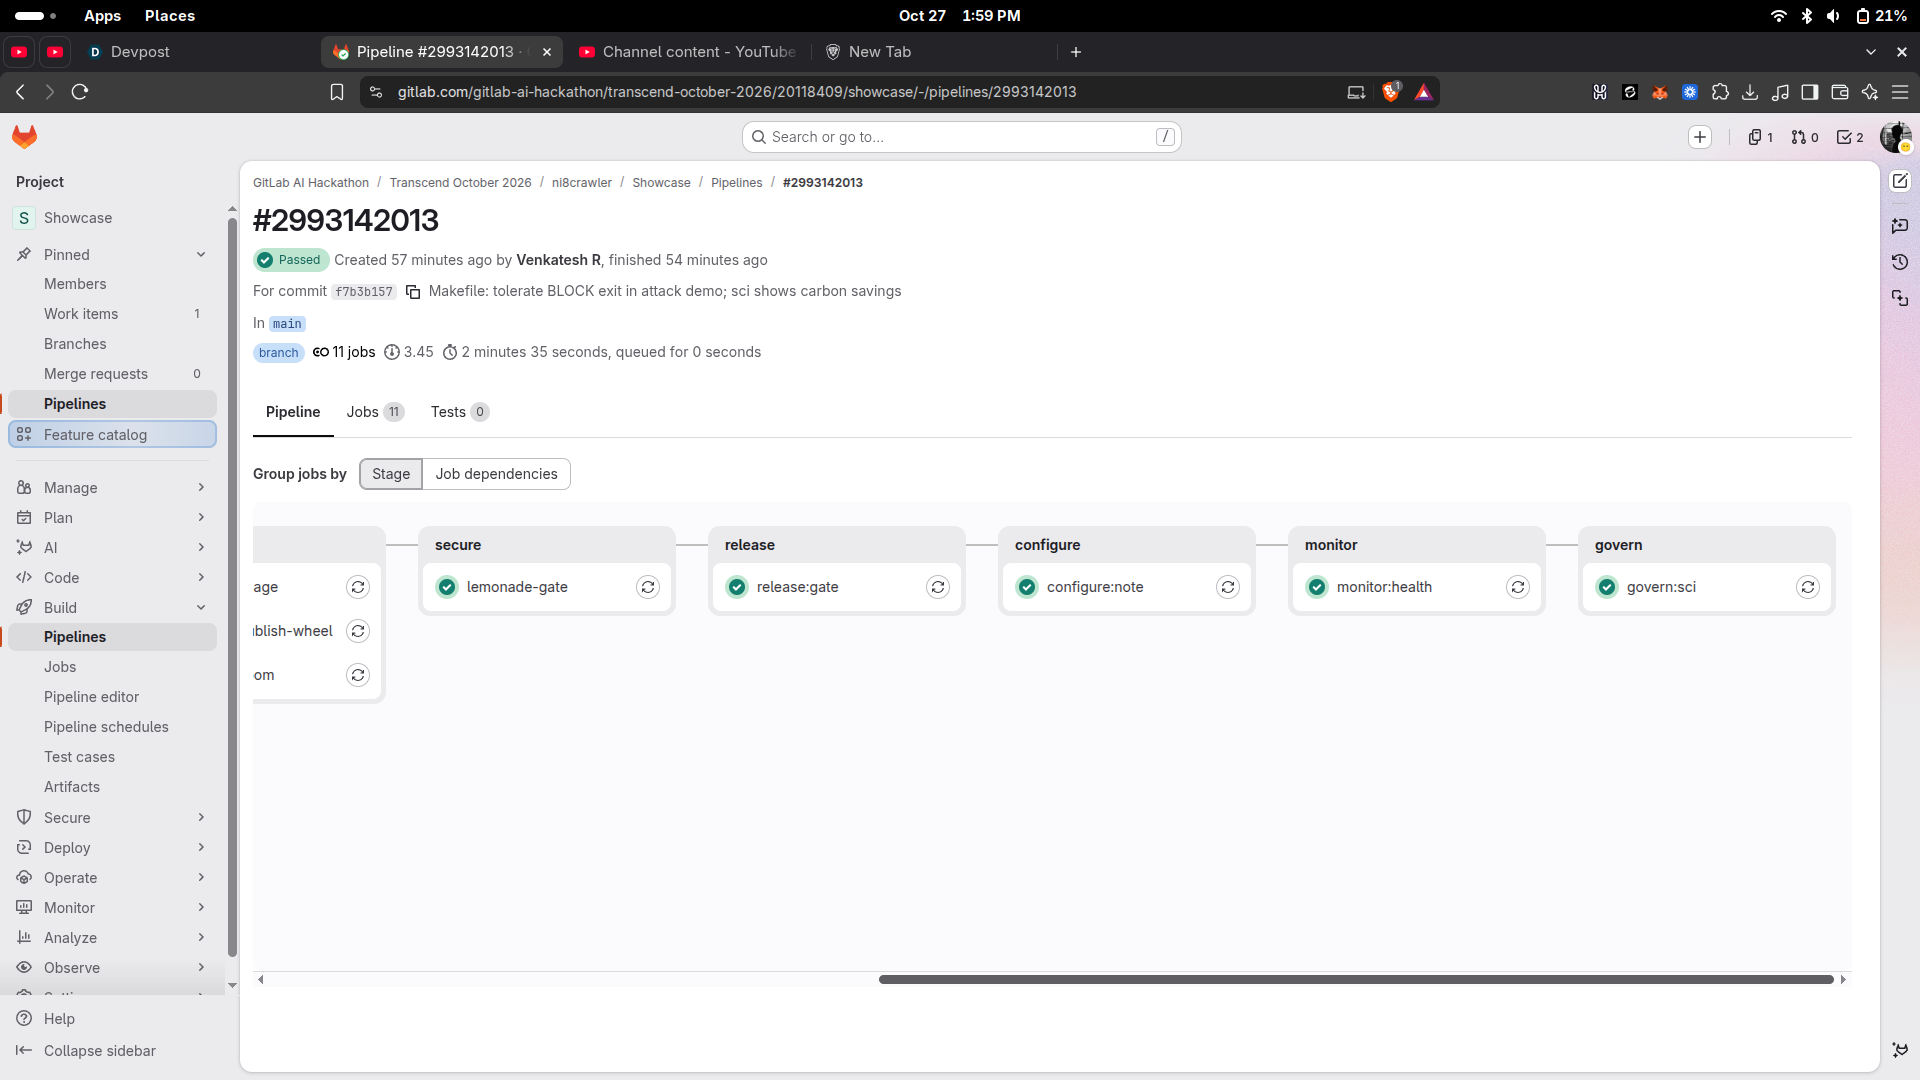
9 stage pipeline
-
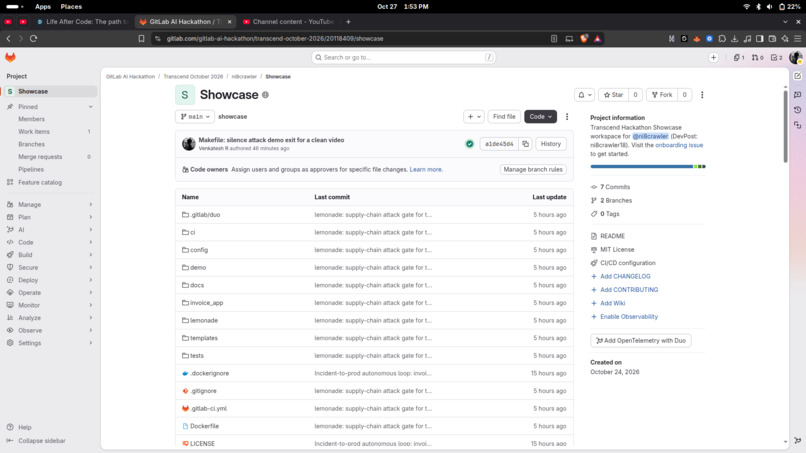
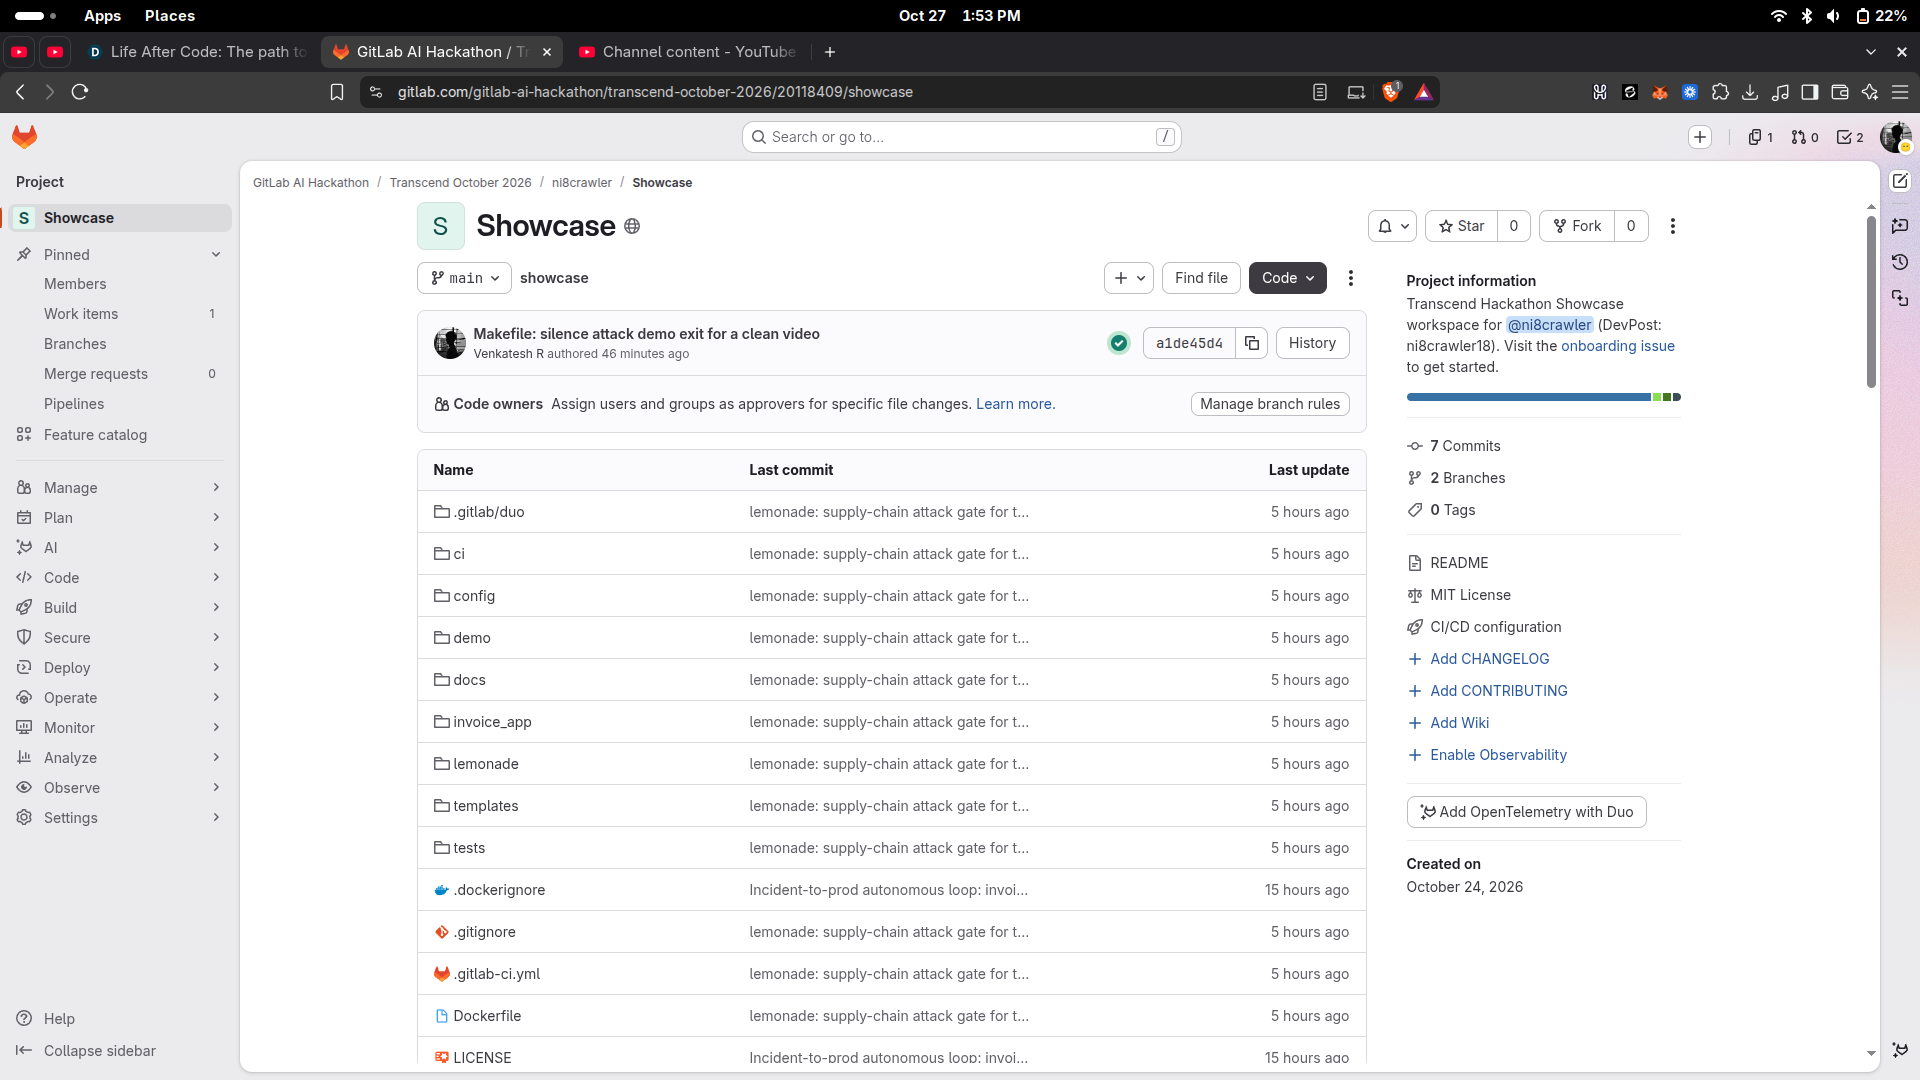
overall codebase in gitlab workspace
Inspiration
Writing code is easy now. The risk moved to what ships with it. Every change pulls in other people's packages, and the last weeks of 2026 brought a wave of new CVEs, RCEs, and outright supply-chain attacks: malicious package updates, typosquats, and compromised maintainer accounts. The painful part is that normal dependency bots upgrade on "newer is better," so they walk straight into a malicious new version. We wanted a gate that stops the bad dependency before it reaches production, right inside GitLab.
What it does
Lemonade checks every dependency a change adds or upgrades, and every dependency already deployed, and returns one of four verdicts: allow, warn, quarantine, or block. It decides from evidence, not from a guess:
- Known advisories, queried live from OSV.dev, with the severity computed from the CVSS vector (not trusted from a feed). A high or critical issue is a block.
- Behavioral supply-chain-attack signals that advisory lookups miss because the bad version is newer: typosquatting, brand-new dependencies, freshly published releases, and dangerous install-time code in a vendored package.
The verdict is made by deterministic code. GitLab Duo agents only explain a finding and open the fix; they can never change a verdict or edit the gate that judges them. Lemonade runs across all nine GitLab DevSecOps stages and installs on any project as a pip package or a GitLab CI/CD component.
How we built it
- A standard-library Python gate (CVSS calculator, OSV client, behavioral heuristics, verdict engine, CLI), packaged as an installable wheel with a
lemonadecommand. - A reusable GitLab CI/CD component that contributes a merge-request gate and a scheduled monitor that re-scans the deployed lockfile for newly disclosed advisories and opens an incident issue.
- A nine-stage GitLab pipeline: build the wheel, run tests, build the container and SBOM, publish the wheel, run the gate, release, deploy, monitor, and govern with a Software Carbon Intensity ledger.
- GitLab Duo agents and flows for explain, remediate, and govern.
- A small FastAPI invoice service as the demo workload, deployed on Google Cloud.
Challenges we ran into
- Google Cloud billing (error OR_BACR2_59) blocked a Cloud Run deploy at the last minute, so we pivoted to Cloud Shell to still run the app on Google Cloud.
- Computing the CVSS base score correctly from the vector string, so severity is derived, not trusted.
- Getting typosquat detection right (edit-distance edge cases like transpositions).
- Keeping the main branch green and deployable while still proving the gate catches a real CVE, which we solved with a fail-first vulnerable branch.
- A local Python 3.14 could not build some wheels, so we validated everything in Python 3.12 containers.
Accomplishments that we're proud of
- It blocks a real RCE live (PyYAML 5.3.1, CVE-2020-14343, CVSS 9.8) and also blocks attacks that have no CVE yet (typosquats and a malicious install hook).
- The verdict is code, and the autonomy lowers itself: a known-CVE fix can go hands-off, but a suspected attack drops to assisted and waits for a human.
- It is a real product, not a one-off: an installable wheel plus a CI/CD component that drops into any GitLab repo.
- Full nine-stage coverage, an SBOM, and a measured ~75% energy reduction by scanning only what changed.
What we learned
- Supply-chain defense needs behavior, not just advisory lookups. The dangerous package is often the newest one.
- Trust boundaries matter: the thing that judges a change must not be editable by that change.
- A standard-library gate is fast, portable, and low-carbon, which made the sustainability story real instead of a slogan.
What's next for Lemonade
- More ecosystems through OSV: npm, Go, Maven, and more.
- Live signals: maintainer changes, release provenance, and sigstore/SLSA verification.
- Publish to the GitLab CI/CD Catalog and to PyPI so anyone can install it in one line.
- Policy configuration, allowlists, and VEX output for auditors.
Built With
- cloud-run
- cloud-shell
- cvss
- cyclonedx
- devsecops
- docker
- fastapi
- gitlab
- gitlab-ci-cd
- gitlab-duo-agent-platform
- google-cloud
- green-software
- makefile
- osv.dev
- pydantic
- pytest
- python
- pyyaml
- sbom
- software-carbon-intensity
- supply-chain-security
- uvicorn

Log in or sign up for Devpost to join the conversation.