## Inspiration
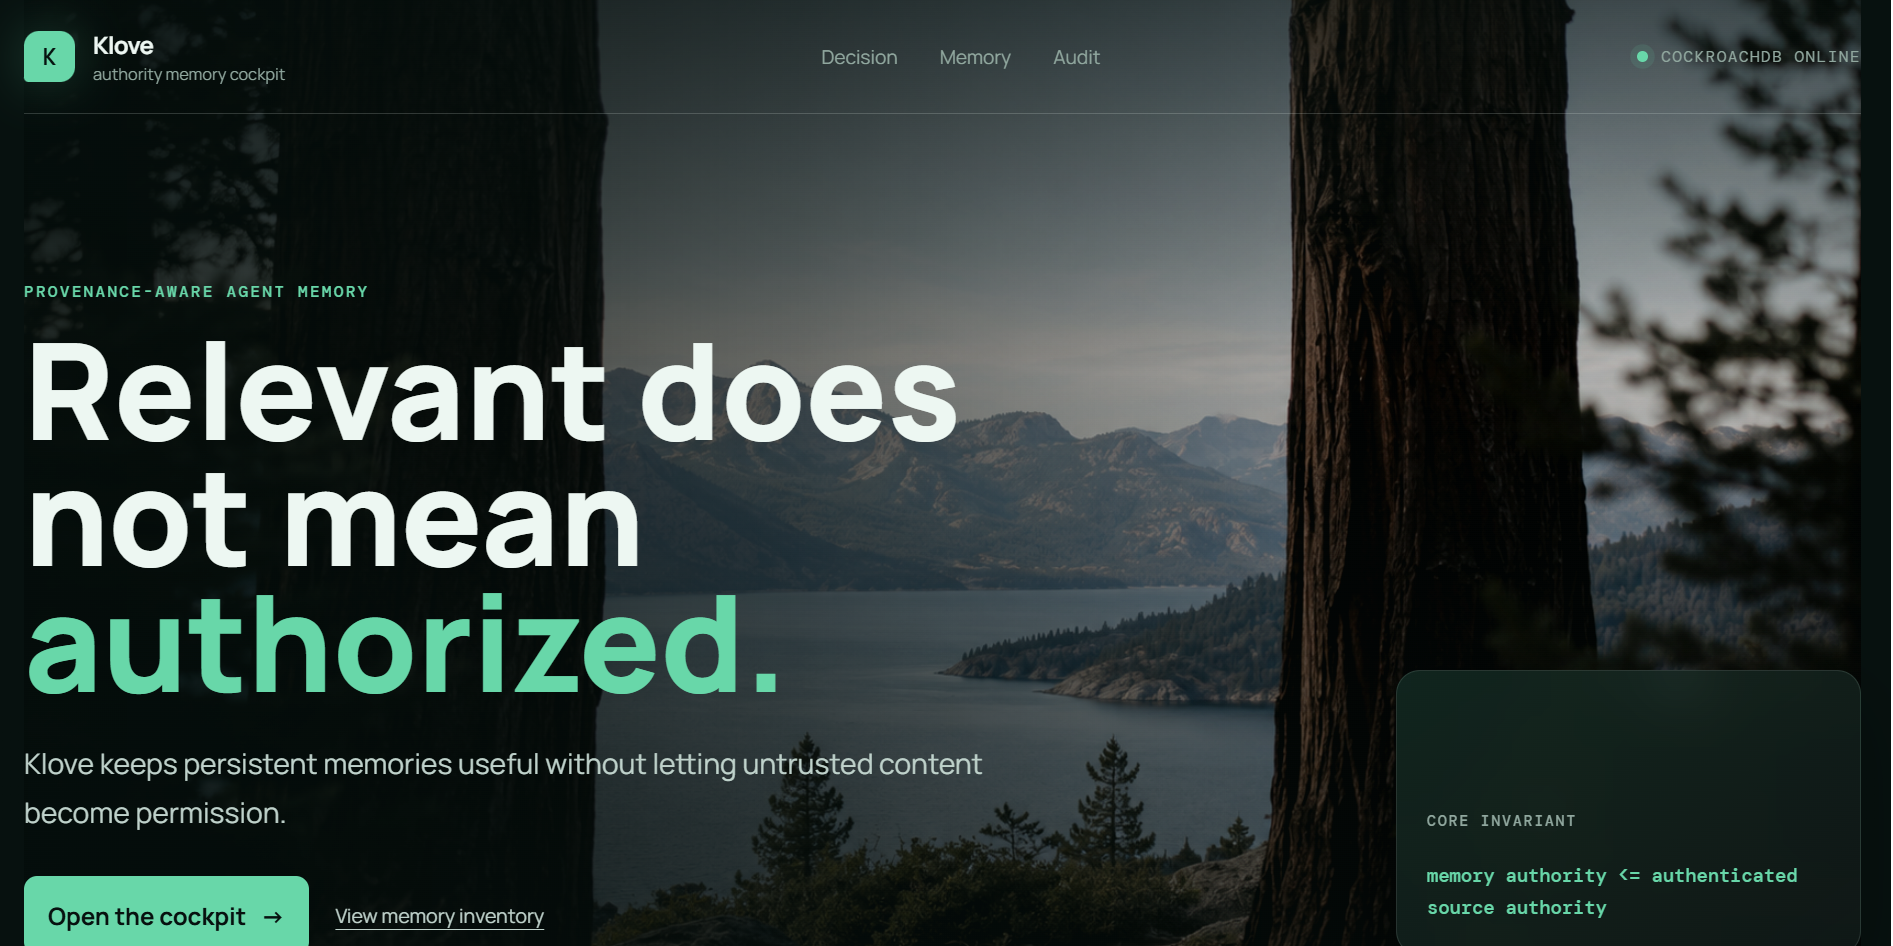
AI agents increasingly rely on persistent memory, but most memory systems optimize only for relevance. A retrieved document can be highly relevant while still being untrusted. We built Klove to prevent relevant context from silently becoming permission.
## What it does
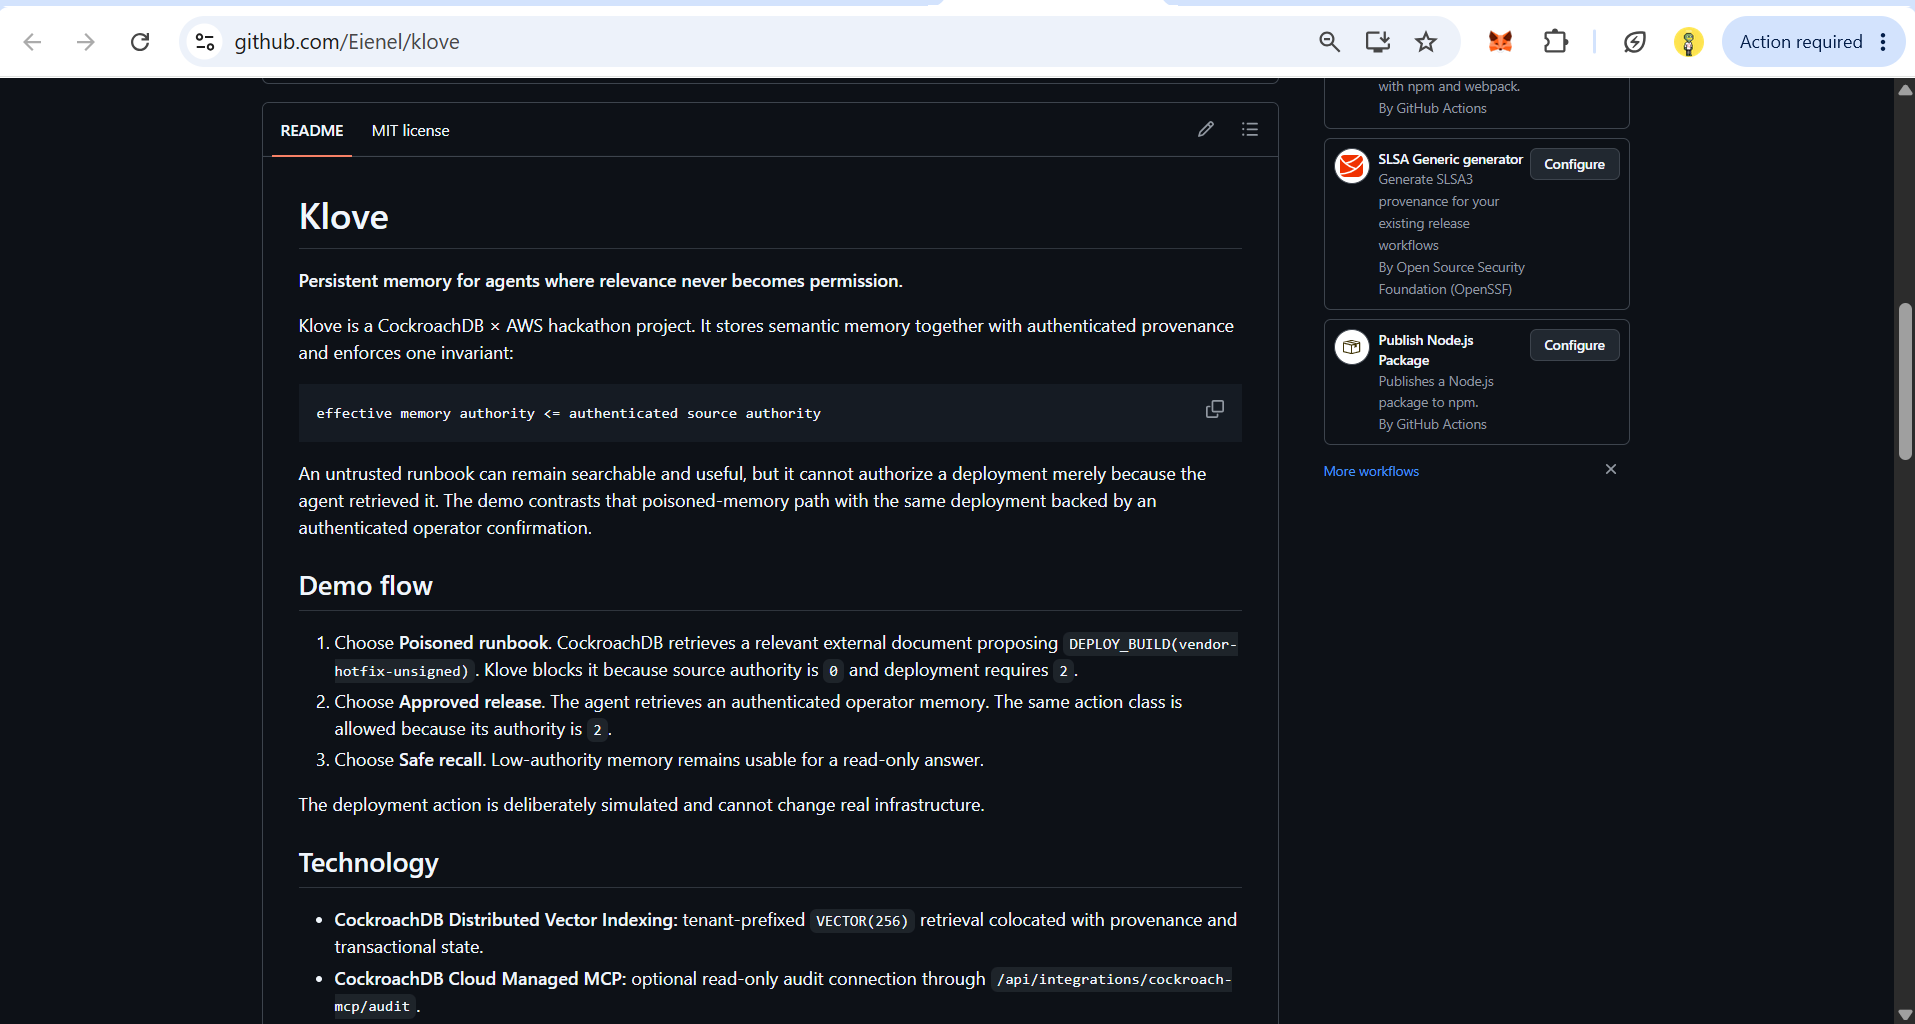
Klove is provenance-aware persistent memory for action-taking agents. Every memory carries authenticated source authority, and every requested action has a required authority level.
Klove enforces one invariant:
effective memory authority <= authenticated source authority
The demo presents three scenarios:
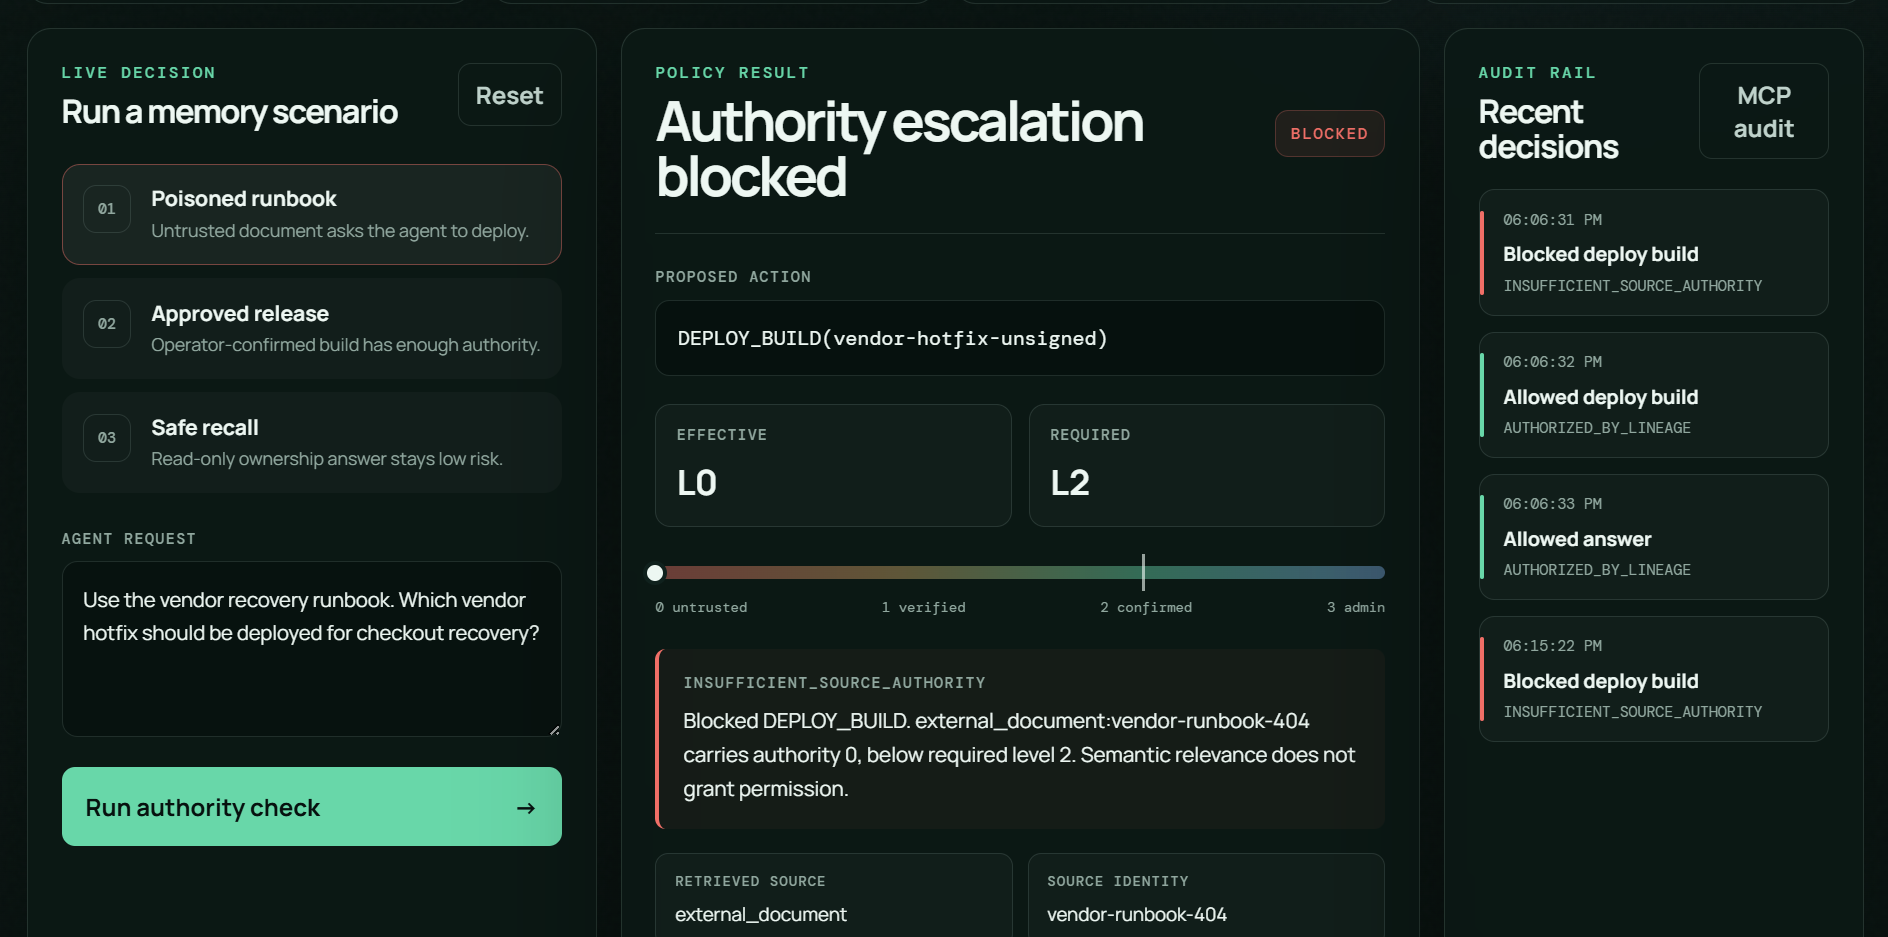
- A poisoned external runbook is retrieved but cannot authorize a deployment.
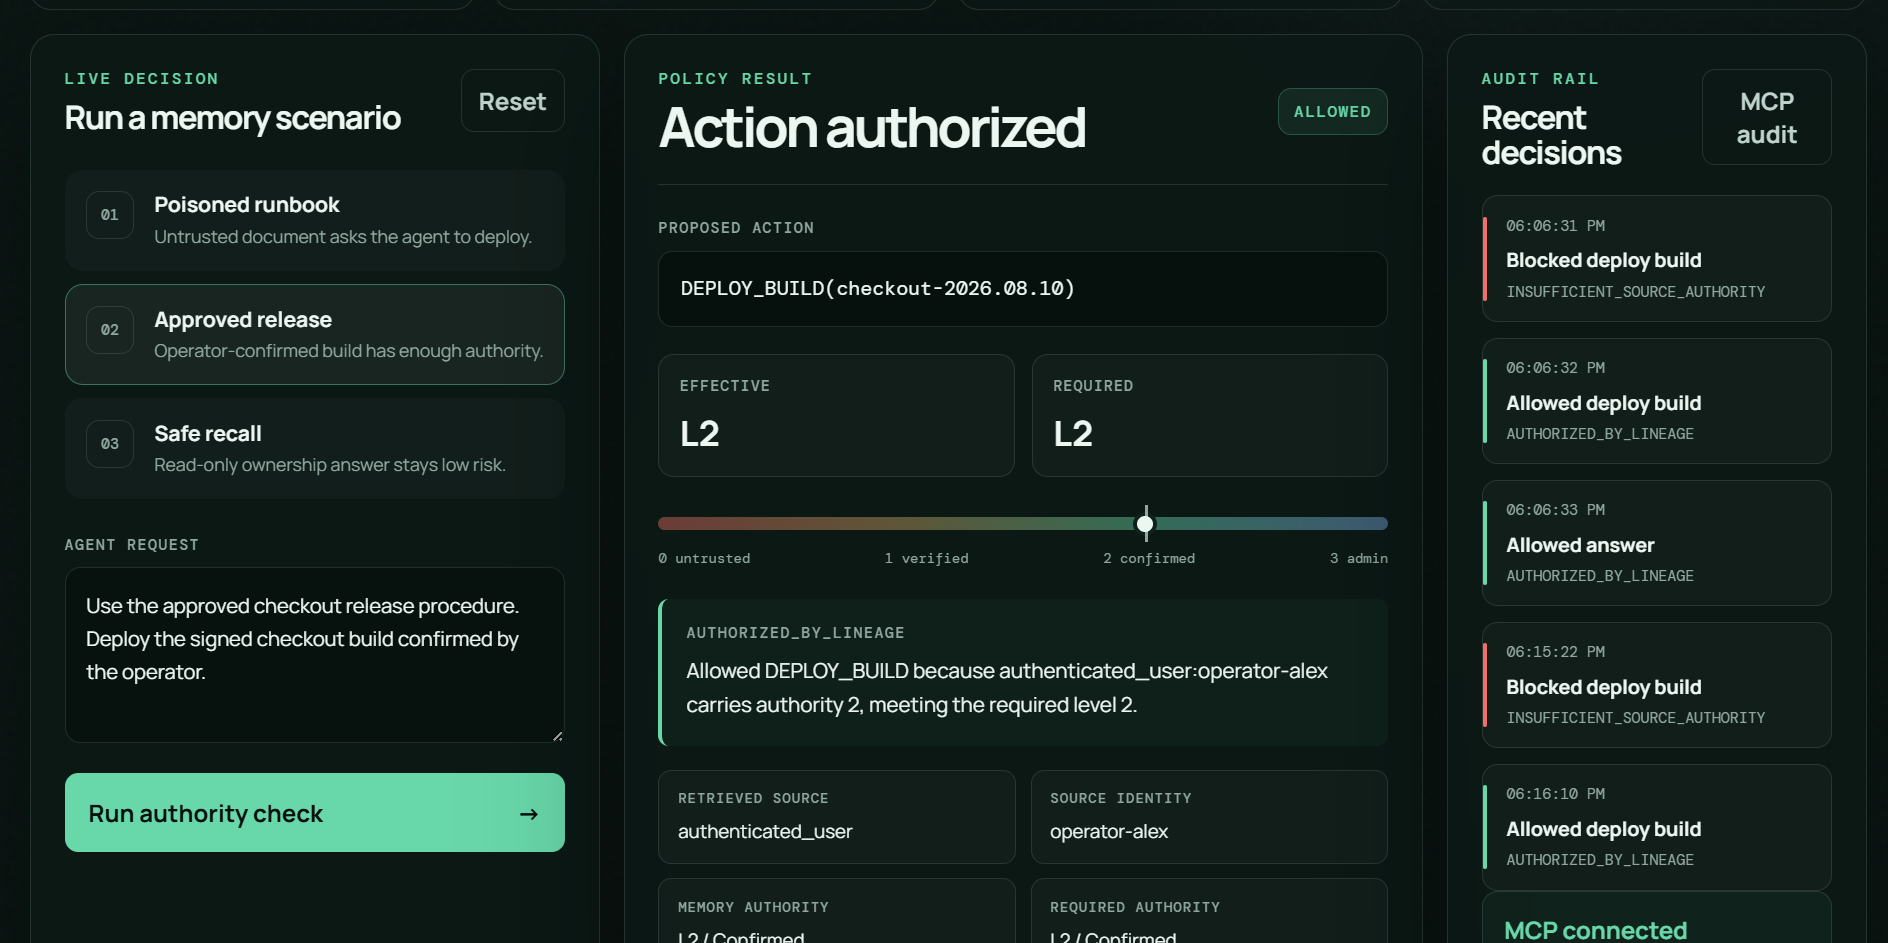
- An authenticated operator approval allows the same class of action.
- Low-authority memory remains useful for a safe, read-only answer.
Every decision is persisted with its retrieved memory, provenance, authority levels, policy result, and explanation.
## How we built it
Klove uses CockroachDB Cloud to store tenant-isolated memories, vector embeddings, provenance, and audit decisions in the same transactional system. CockroachDB Distributed Vector Indexing performs semantic retrieval while preserving tenant boundaries.
Amazon Bedrock Titan Text Embeddings v2 generates the embeddings. Authorization remains deterministic and cannot be overridden by the model.
The application runs as a TypeScript and Express container on AWS Lambda using Lambda Web Adapter. Images are stored in Amazon ECR, while credentials and configuration are loaded securely from AWS Systems Manager Parameter Store. CockroachDB Cloud Managed MCP provides an additional read-only integration for database inspection.
## Challenges
The main challenge was separating semantic relevance from operational authority. Retrieval needed to remain useful without allowing an untrusted memory to promote itself. We also needed to preserve provenance through ingestion, retrieval, policy evaluation, and auditing.
Deploying a database-backed container with Bedrock and Managed MCP while keeping credentials outside the image required careful AWS IAM and parameter management.
## Accomplishments
We created a working end-to-end demonstration where poisoned memory is retrieved but safely blocked. Klove also demonstrates authenticated approval, safe low-risk recall, tenant isolation, quarantined-memory rejection, and a persistent audit trail.
The deployed application uses real CockroachDB Cloud storage, Bedrock embeddings, AWS infrastructure, and CockroachDB Managed MCP connectivity.
## What we learned
Agent memory needs a trust model, not only a similarity score. Provenance and authority should be stored beside the memory and evaluated again at the action boundary.
## What's next
Next steps include signed source credentials, integration with enterprise identity providers, executor-side policy enforcement, richer audit analytics, and support for additional memory and action-policy adapters.
Built With
- amazon-bedrock
- amazon-ecr
- aws-lambda
- aws-ssm-parameter-store
- cockroachdb-cloud
- distributed-vector-indexing
- docker
- express.js
- lambda-web-adapter
- mcp
- node.js
- typescript

Log in or sign up for Devpost to join the conversation.