Inspiration
Modern DevSecOps is fragmented. Developers write code in their IDE, switch to separate terminal tabs to run slow CLI scanners, search browser tabs for CVE details, and copy-paste code into generic chatbots that hallucinate false vulnerabilities and leak private secrets.
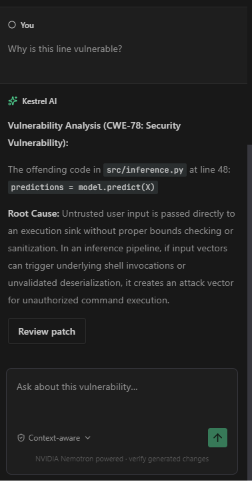
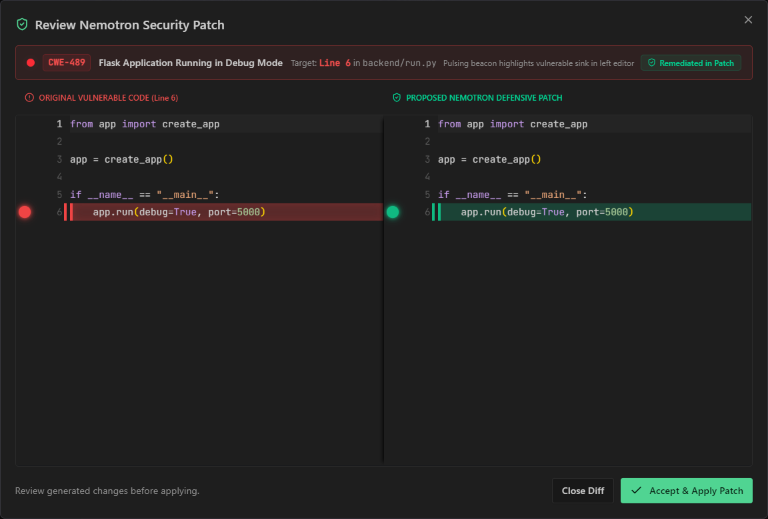
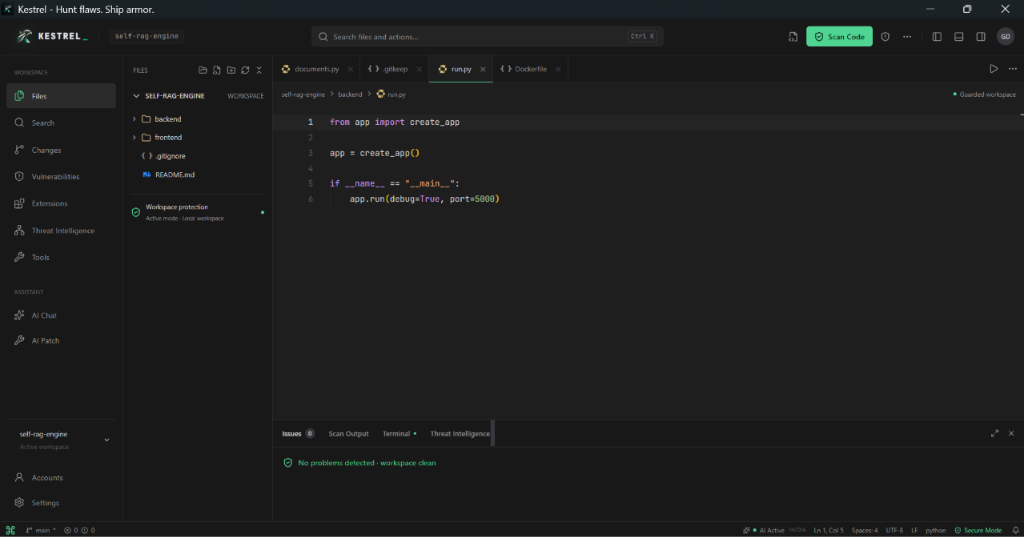
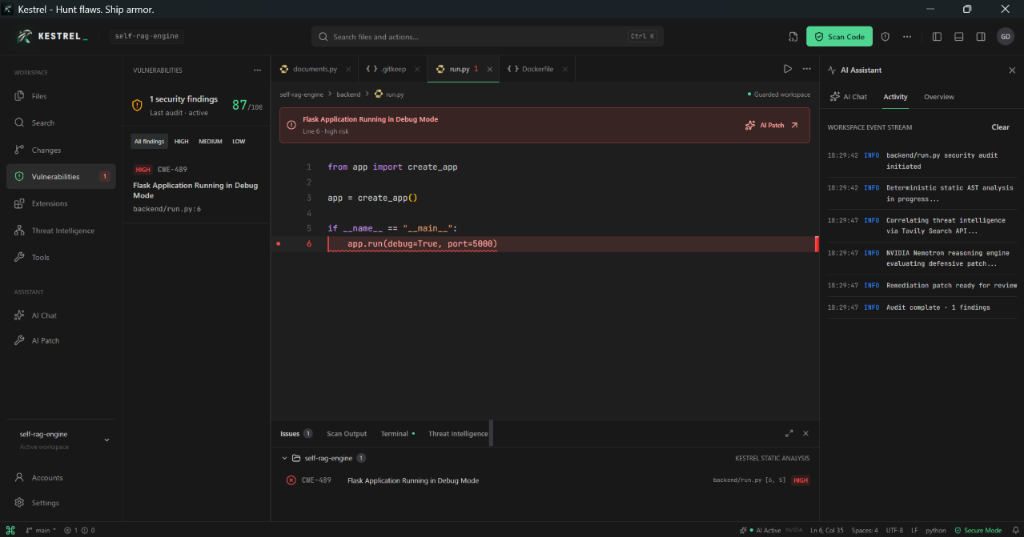
We built Kestrel AI to bring developer workflow and cybersecurity under one roof: a privacy-first, zero-hallucination IDE where flaws are deterministically detected, enriched with live threat intelligence, reasoned over by NVIDIA Nemotron 3.5, and remediated with 1-click verified git diff patches.
What It Does
- Deterministic Python AST Static Analyzer: In-memory parsing identifies SQLi (CWE-89), Command Injection (CWE-78), Path Traversal (CWE-22), and Deserialization (CWE-502) with 0% LLM hallucination.
- AST Architectural Role Classifier: Automatically labels nodes as SOURCE, SINK, VALIDATION_GAP, or TRIGGER_POINT.
- High-Entropy Secret Redaction: In-memory Shannon entropy scanner automatically masks AWS tokens, OpenAI keys, and secrets before any prompt dispatch.
- Specialized Linters: Validates YARA malware patterns, Sigma SIEM rules, Snort IDS rules, and Dockerfiles.
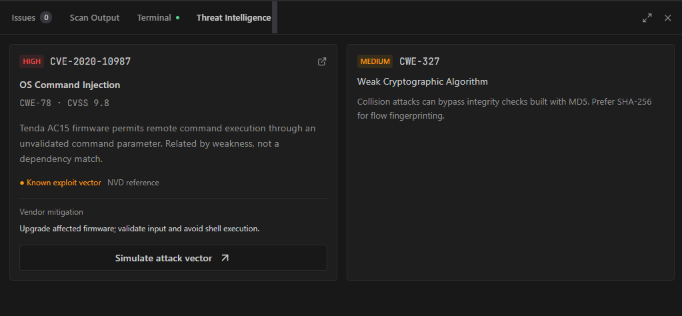
- Live Threat Intelligence Grounding: Queries Tavily in real time against authoritative NVD sources to retrieve verified CVE IDs, CVSS 9.8 metrics, and vendor mitigations.
- Defensive Remediation Engine: NVIDIA Nemotron 3.5 synthesizes clean unified git diff patches applied directly to disk with 1 click.
- Dynamic Docker Exploit Sandbox: Executes attack payloads against vulnerable vs patched code to mathematically prove DEFENDED status.
- DevSecOps CI/CD Automation: Generates GitHub Actions pipelines and exports findings to OASIS SARIF 2.1.0 standard.
How We Built It
- AI Core: Powered by NVIDIA Nemotron 3.5 via Nebius / OpenRouter for deep contextual reasoning and patch generation.
- Backend Engine: FastAPI, Python AST engine, Uvicorn, and SQLite cache compiled into a single executable (
kestrel-core.exe). - Desktop & Web Studio: Electron 33 wrapper hosting Monaco Editor, React 18, TypeScript, and Tailwind CSS.
- Web Distribution: Fast Vite SPA deployed to Vercel global edge network.
Challenges We Overcame
- Ensuring 0% false positives in the static analyzer by strictly utilizing AST node visitors instead of probabilistic LLM prompts.
- Designing an entropy redaction engine fast enough to sanitize entire codebases in volatile memory without lag.
- Packaging a full Python FastAPI backend into a standalone, zero-dependency Windows desktop executable.
Accomplishments That We're Proud Of
- 40/40 automated test suite passing across all analyzers, linters, sandboxes, and API endpoints.
- Seamless side-by-side unified git diff review with instant disk synchronization.
- Complete standalone Windows installer and portable edition available on GitHub Releases.
What's Next
- Expanding AST static rules to JavaScript/TypeScript, Go, and Rust.
- Enterprise multi-repository threat modeling and Kubernetes cluster sandboxing.

Log in or sign up for Devpost to join the conversation.