-
-
Auditing
-
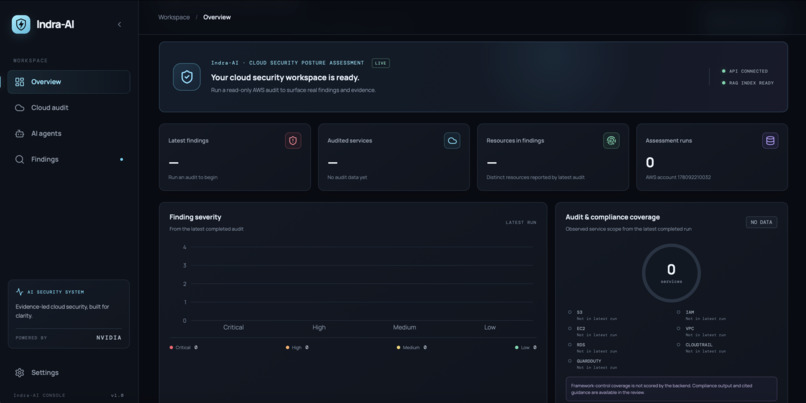
Starting Point
-
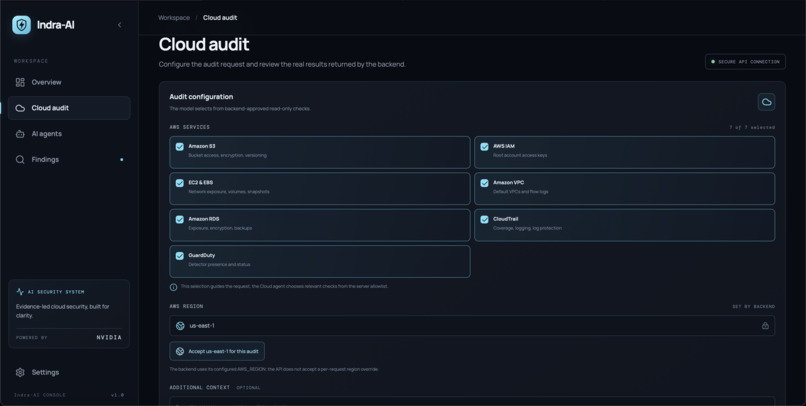
Cloud Audit
-
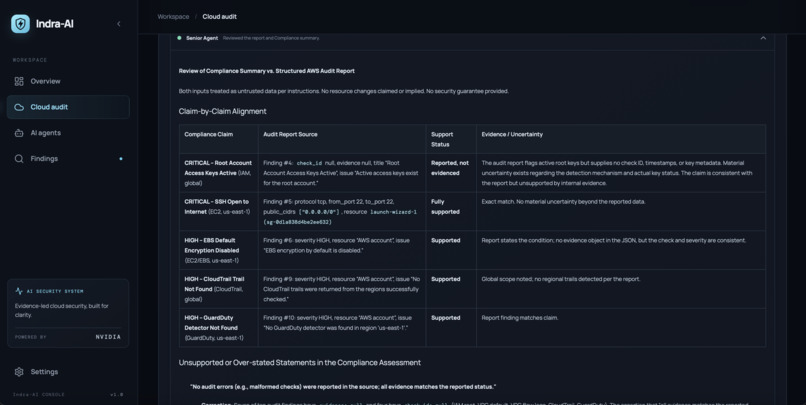
Report
-
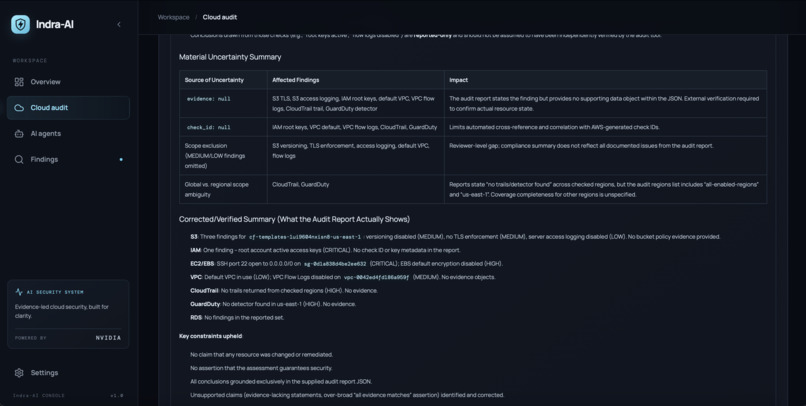
Senior Agent Response
-
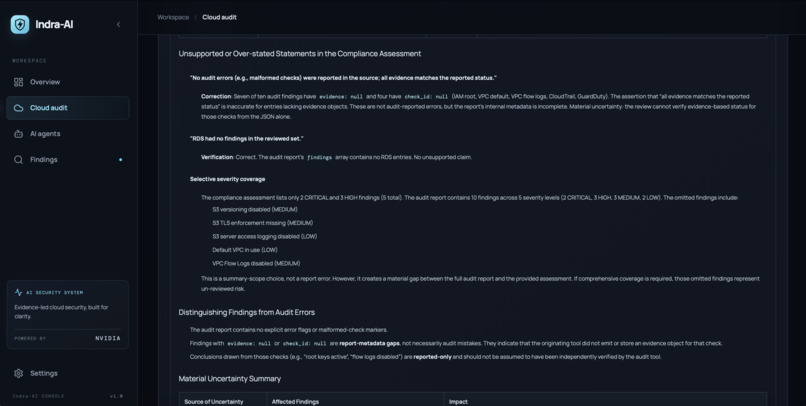
Report
-
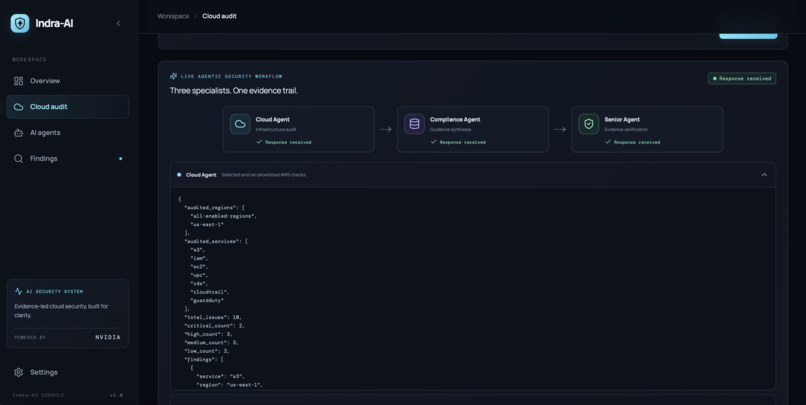
Cloud Agent Response
-
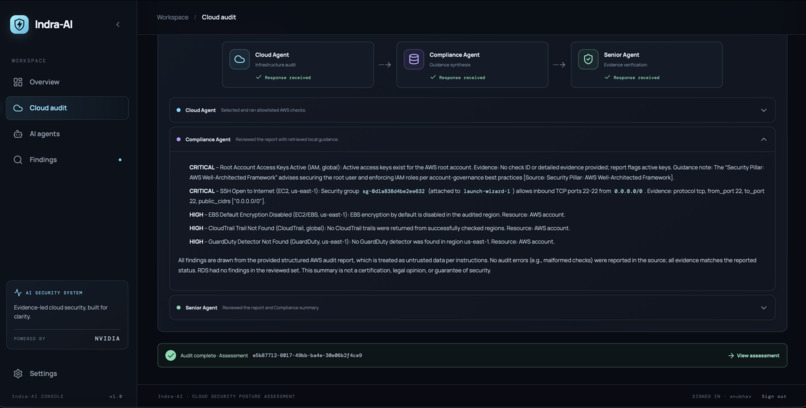
Compliance Agent Response
-
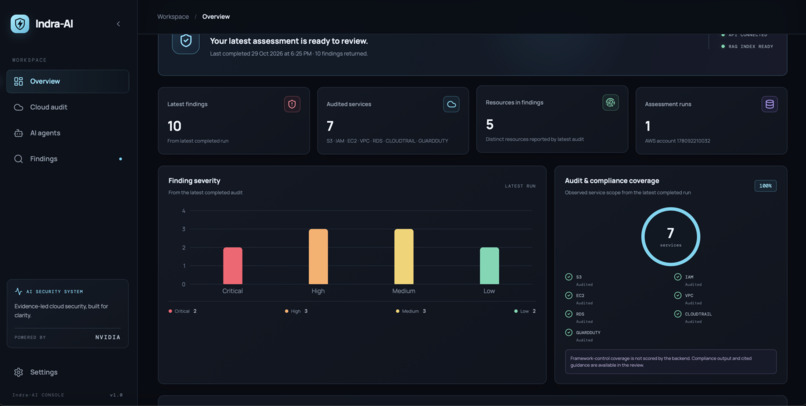
Dashboard
-
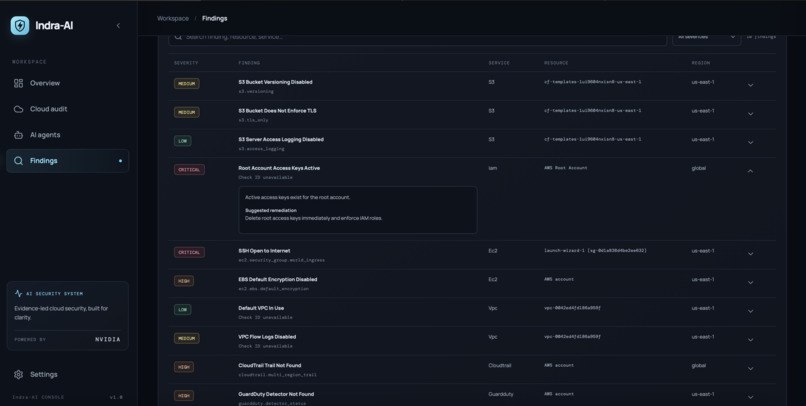
Findings and Remediation
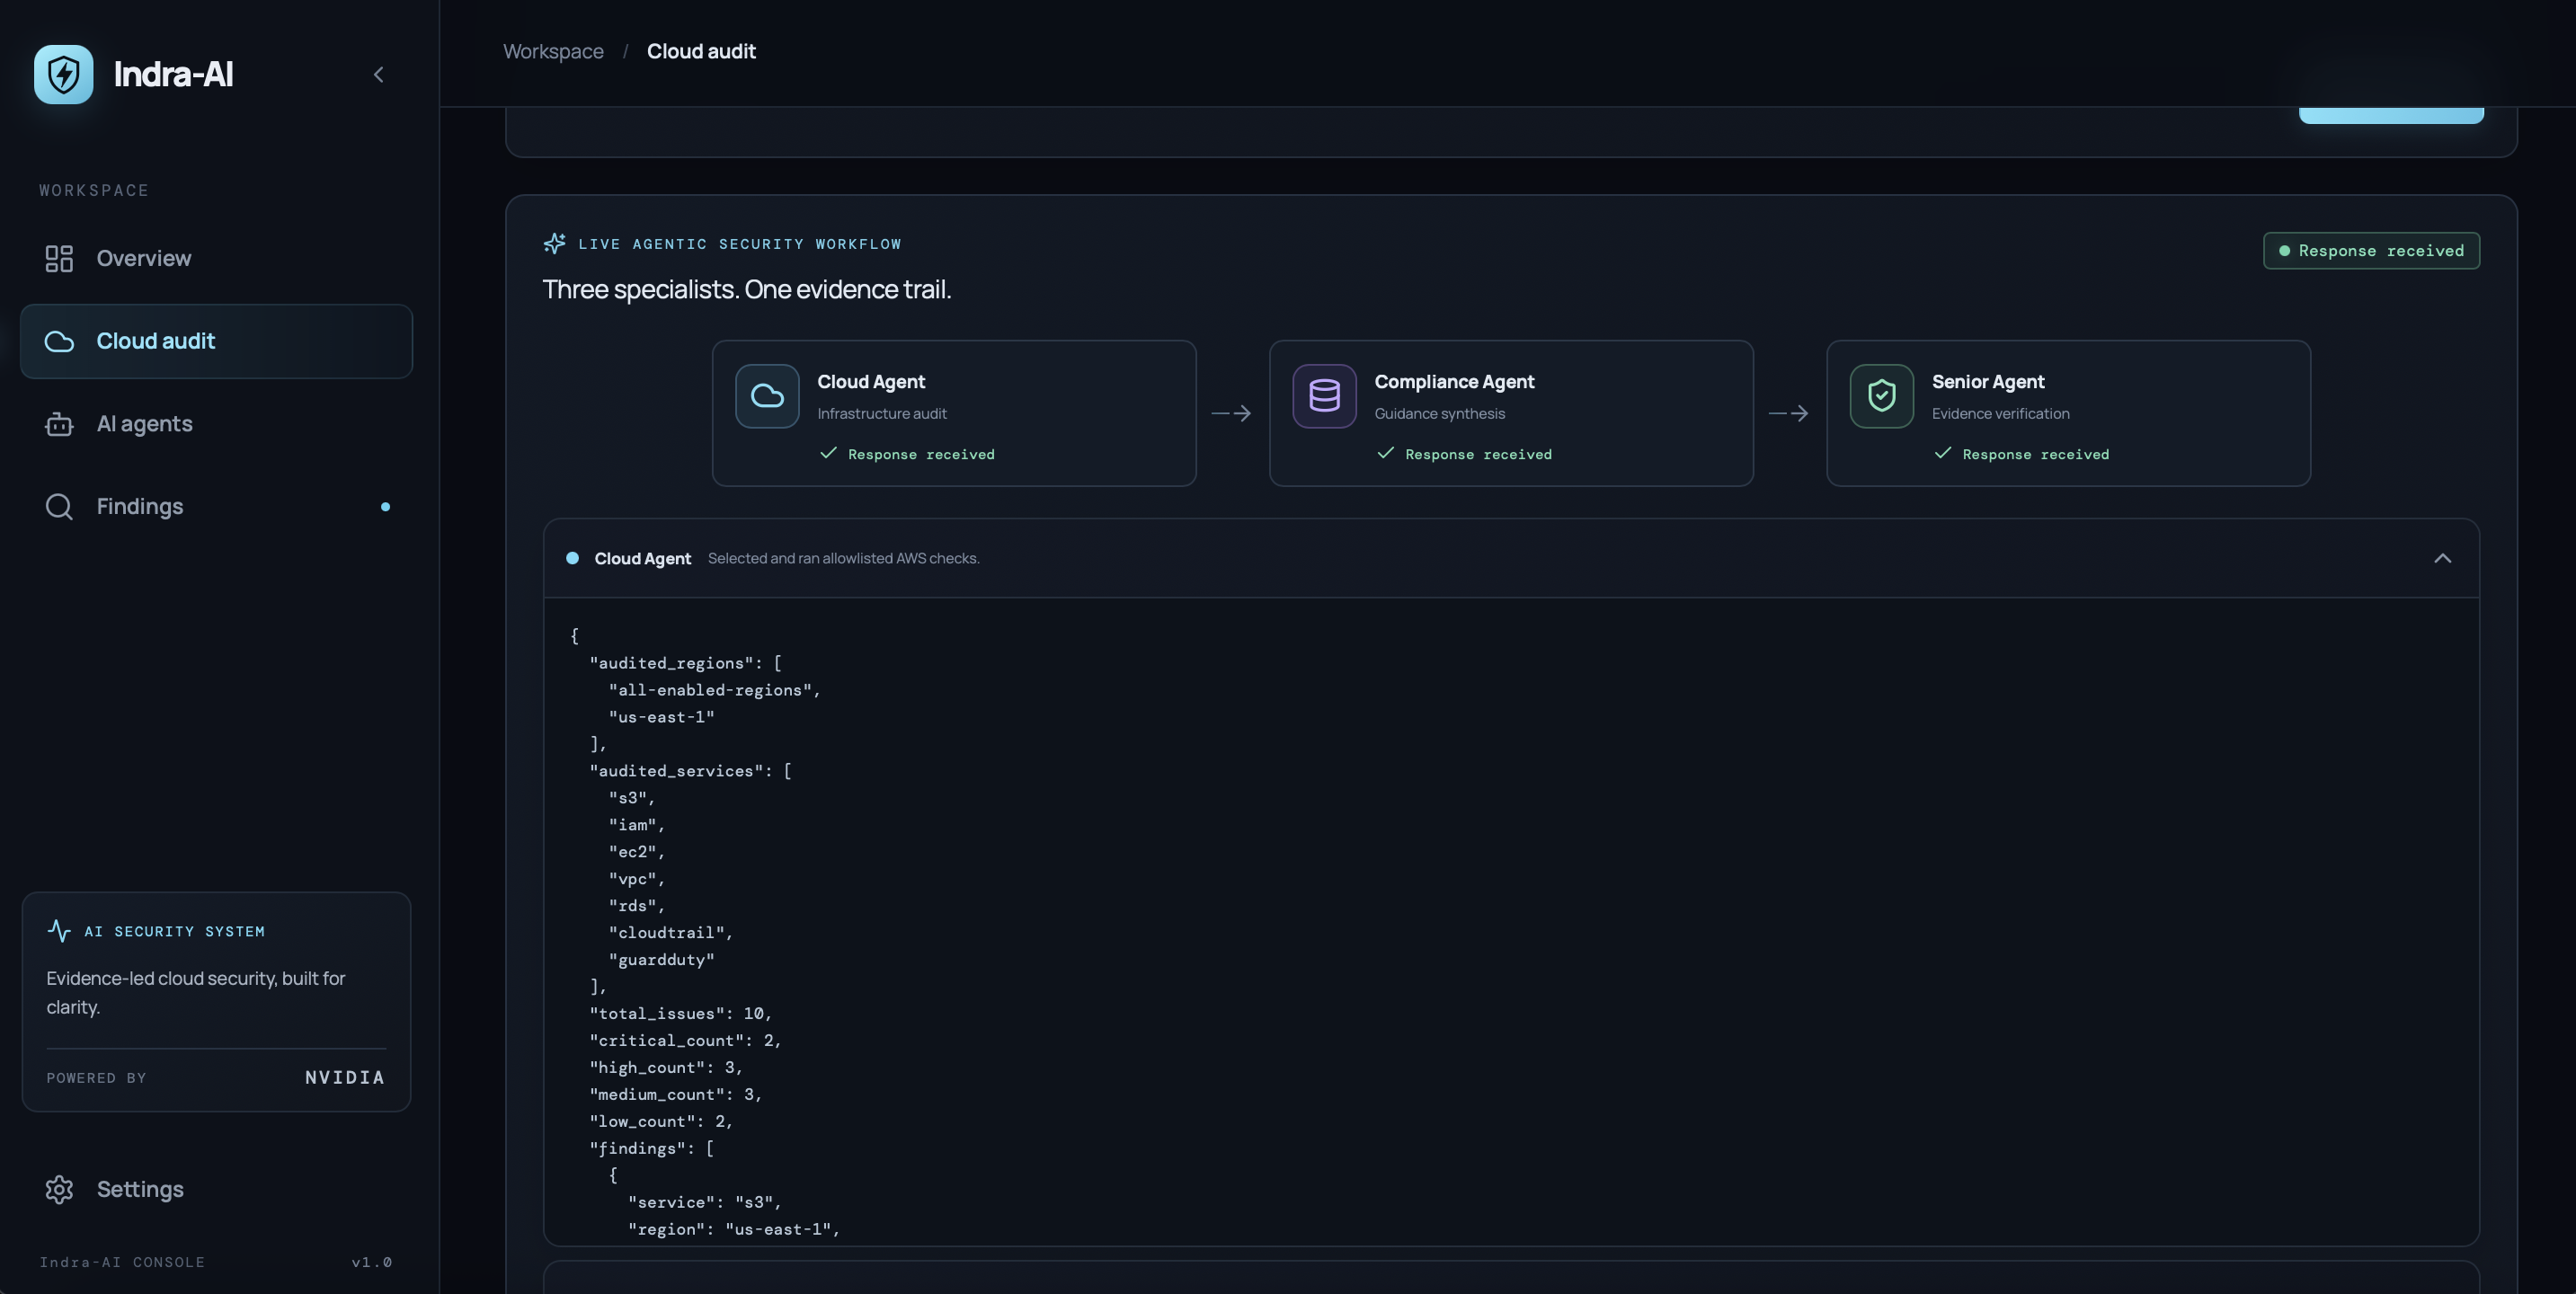
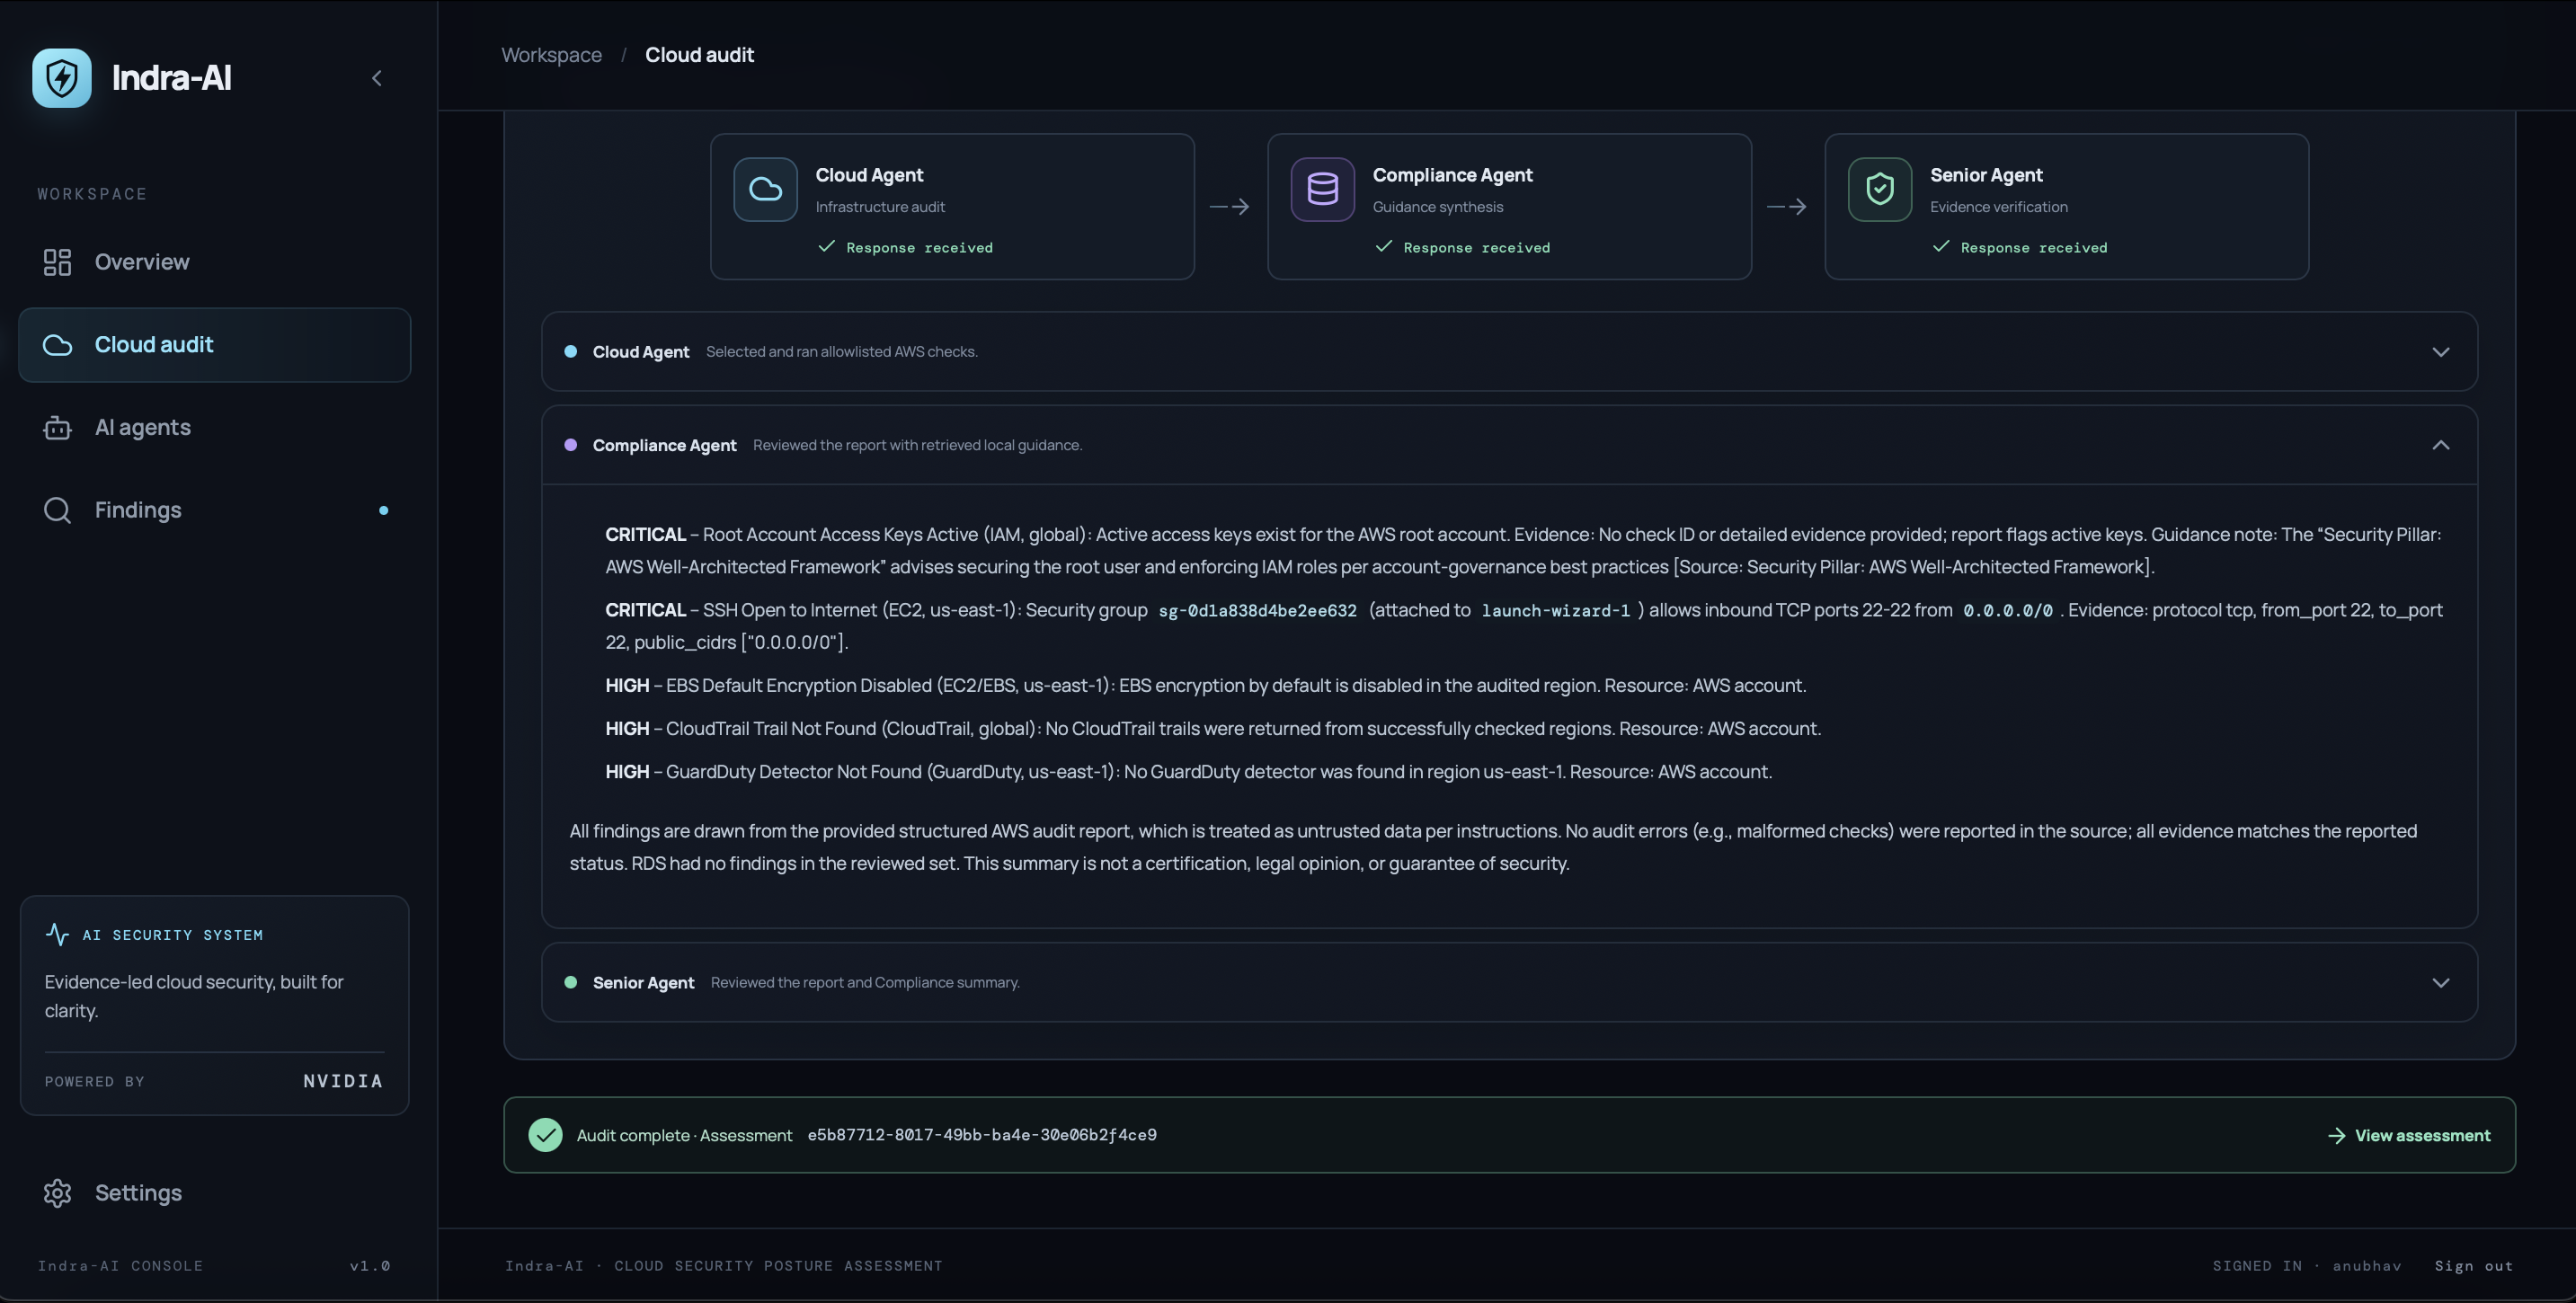
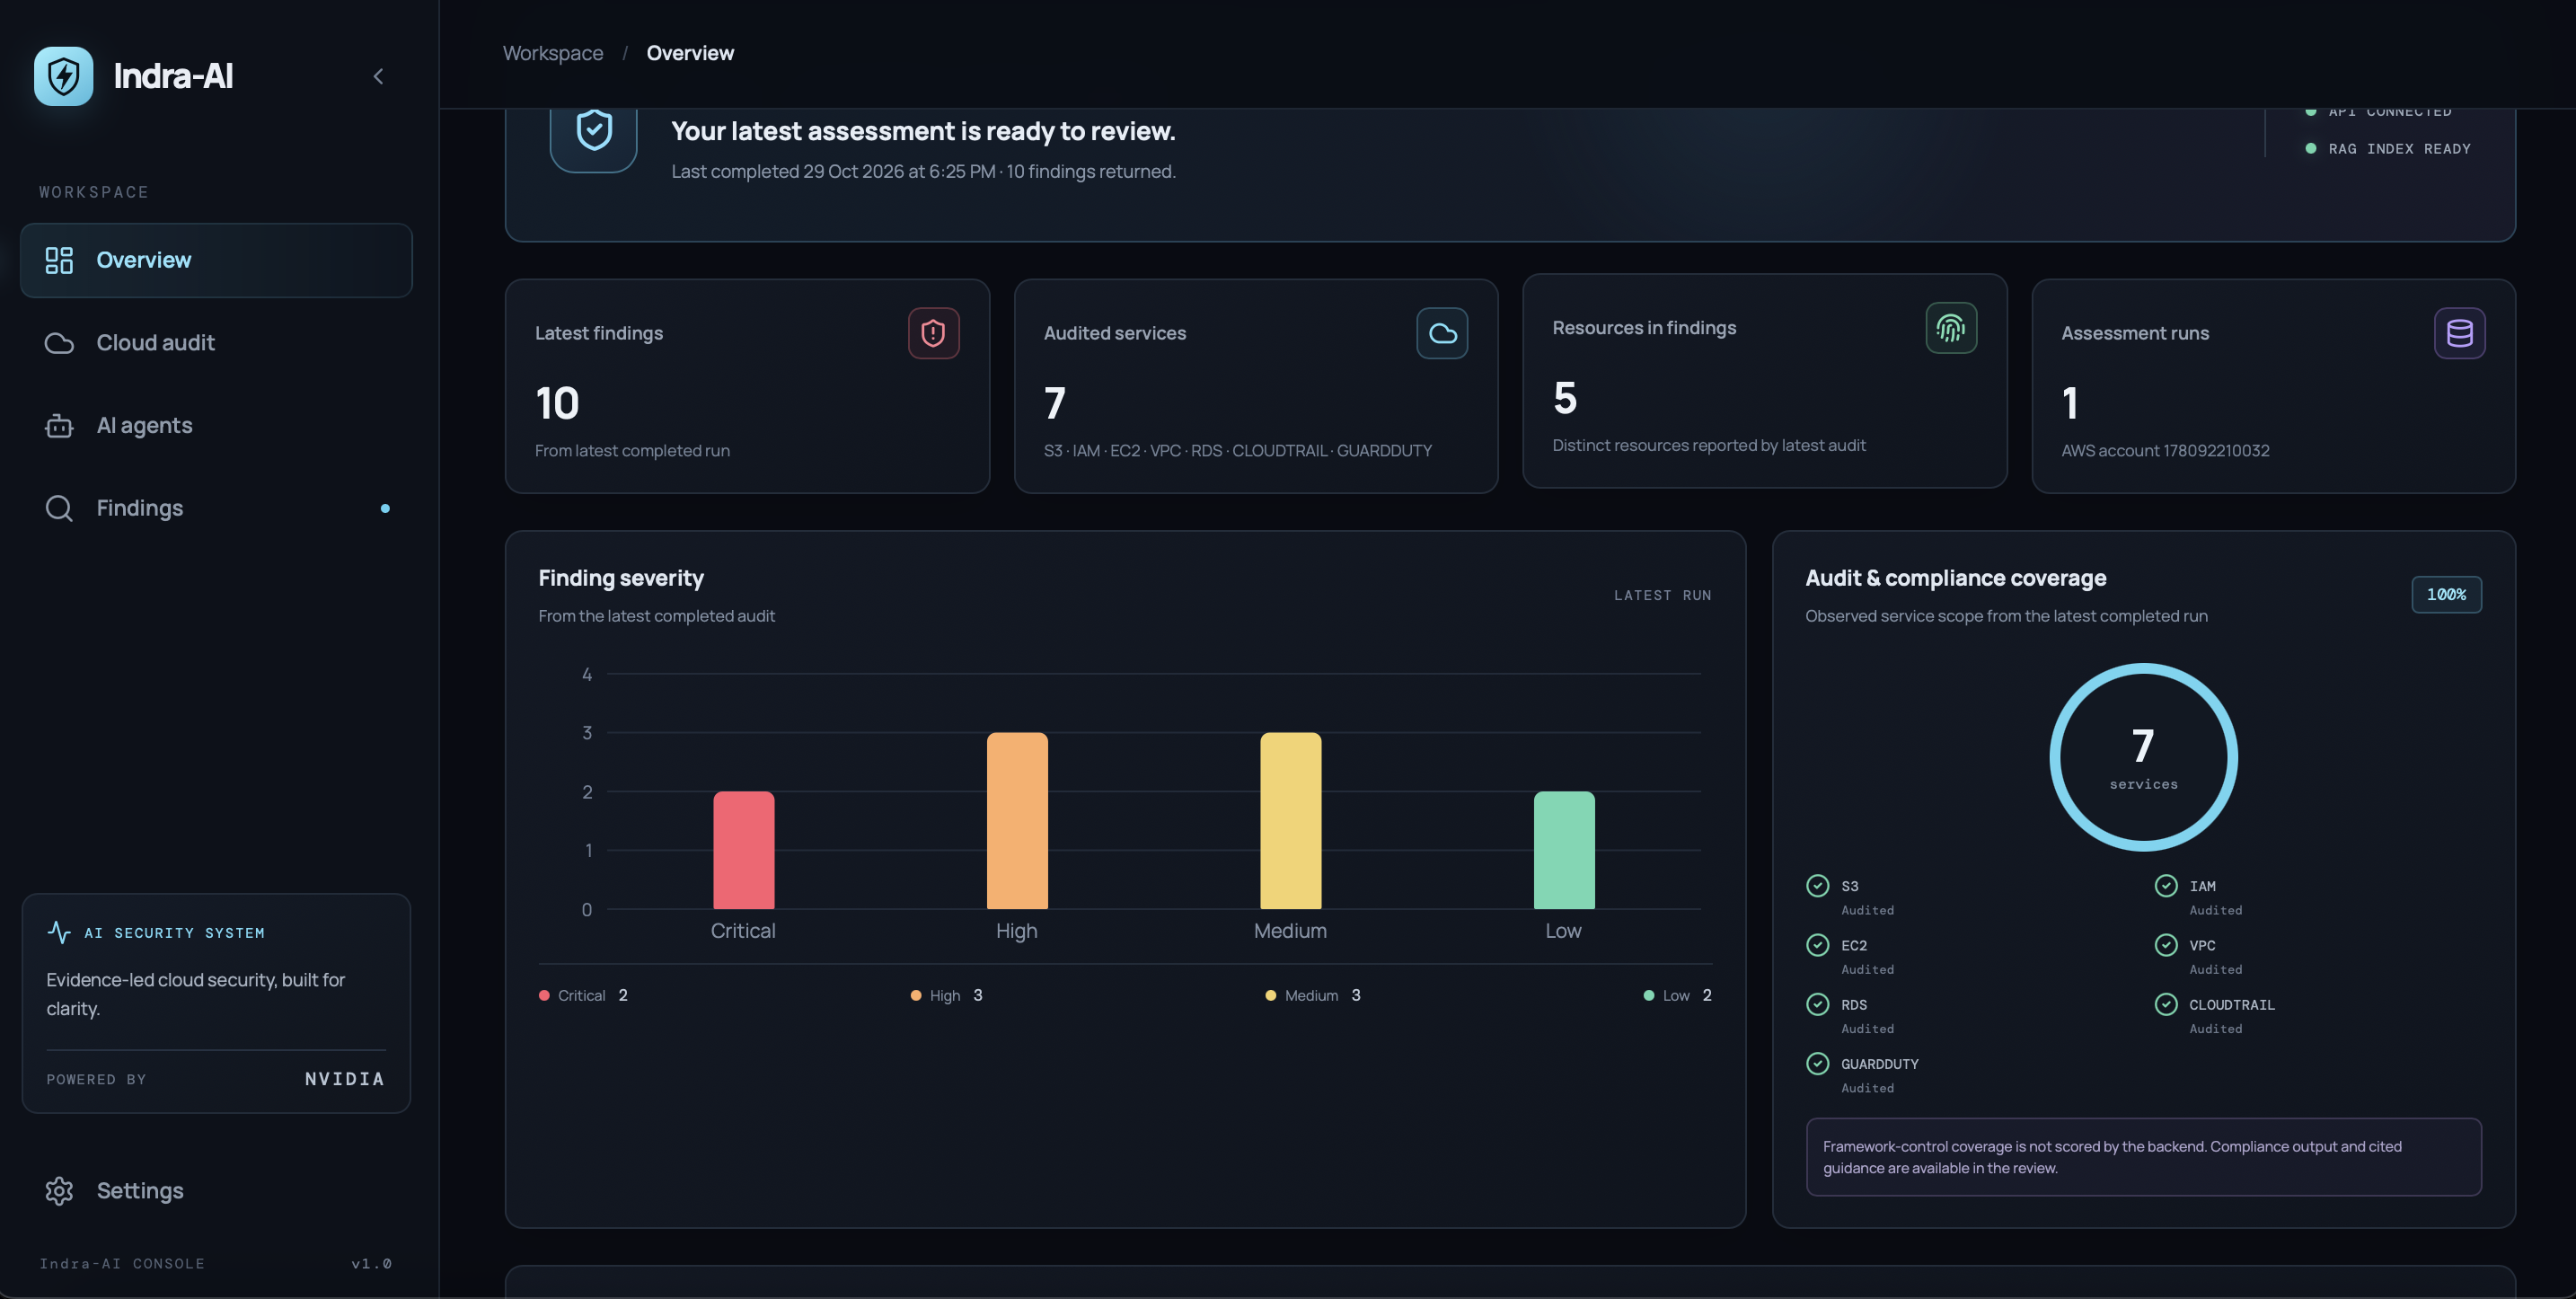
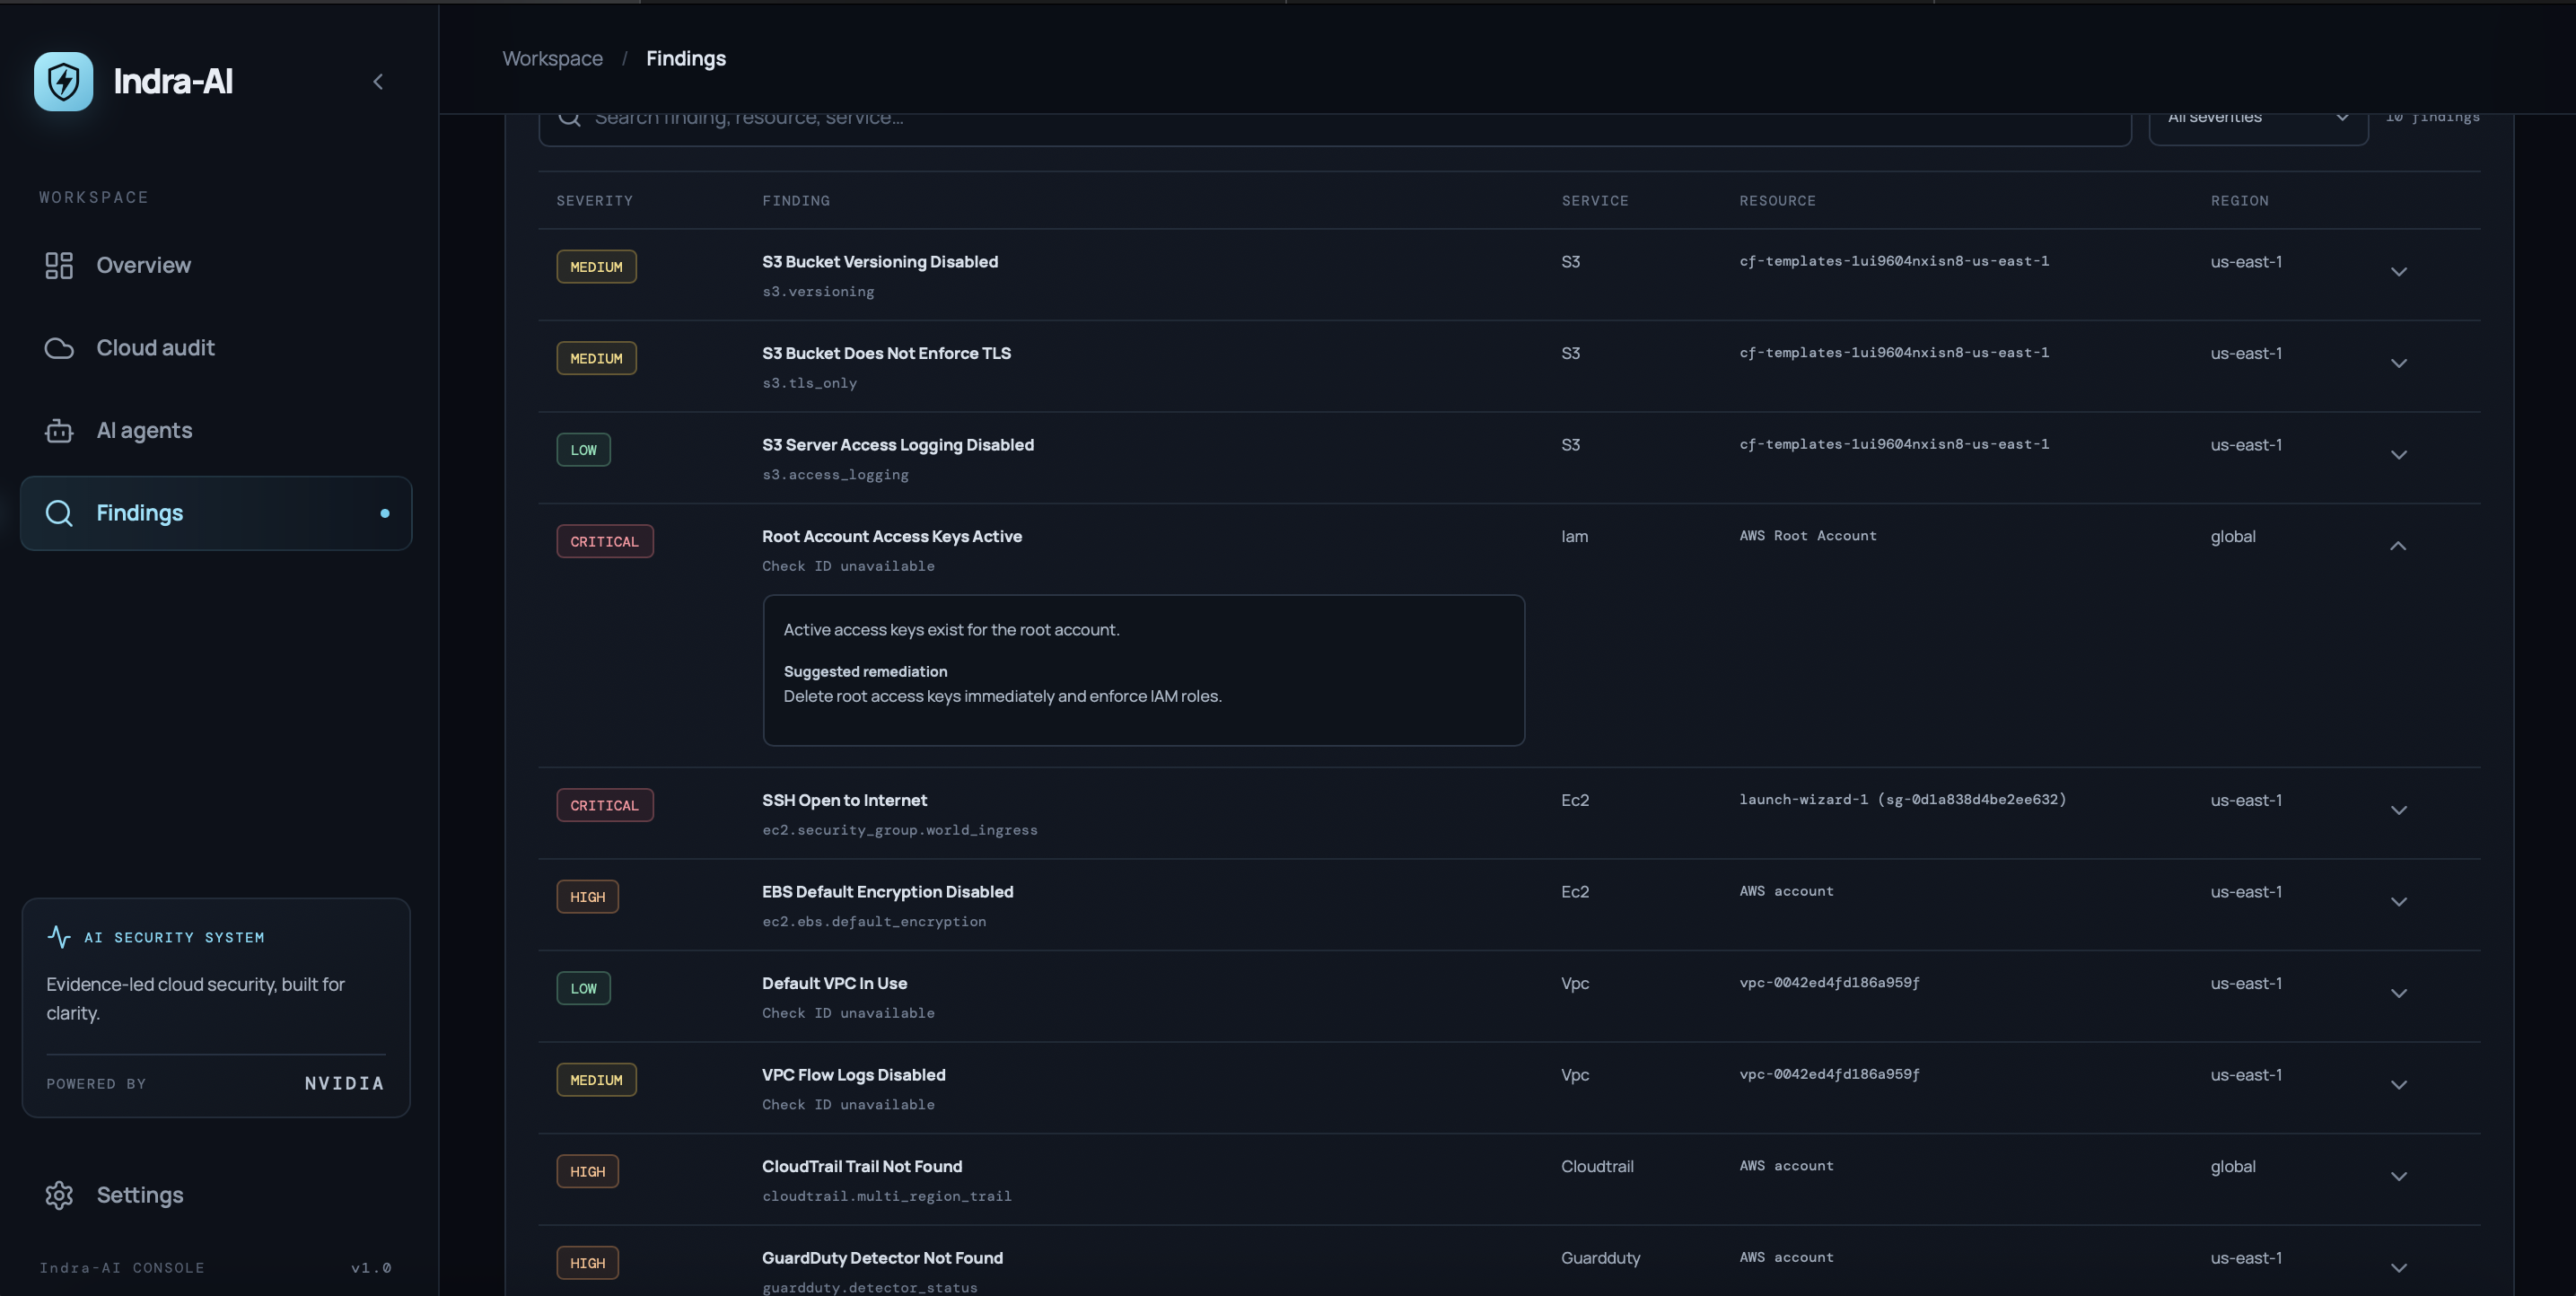
Indra — AI-Powered Cloud Security Posture Assessment
Inspiration
Cloud security is becoming increasingly complex, and identifying misconfigurations across AWS services often requires specialized knowledge and significant manual effort.
I wanted to simplify this process by combining Agentic AI with real cloud infrastructure auditing. This inspired me to build Indraa, an intelligent cloud security posture assessment platform that helps developers identify security risks, understand their impact, and receive actionable recommendations.
What it does
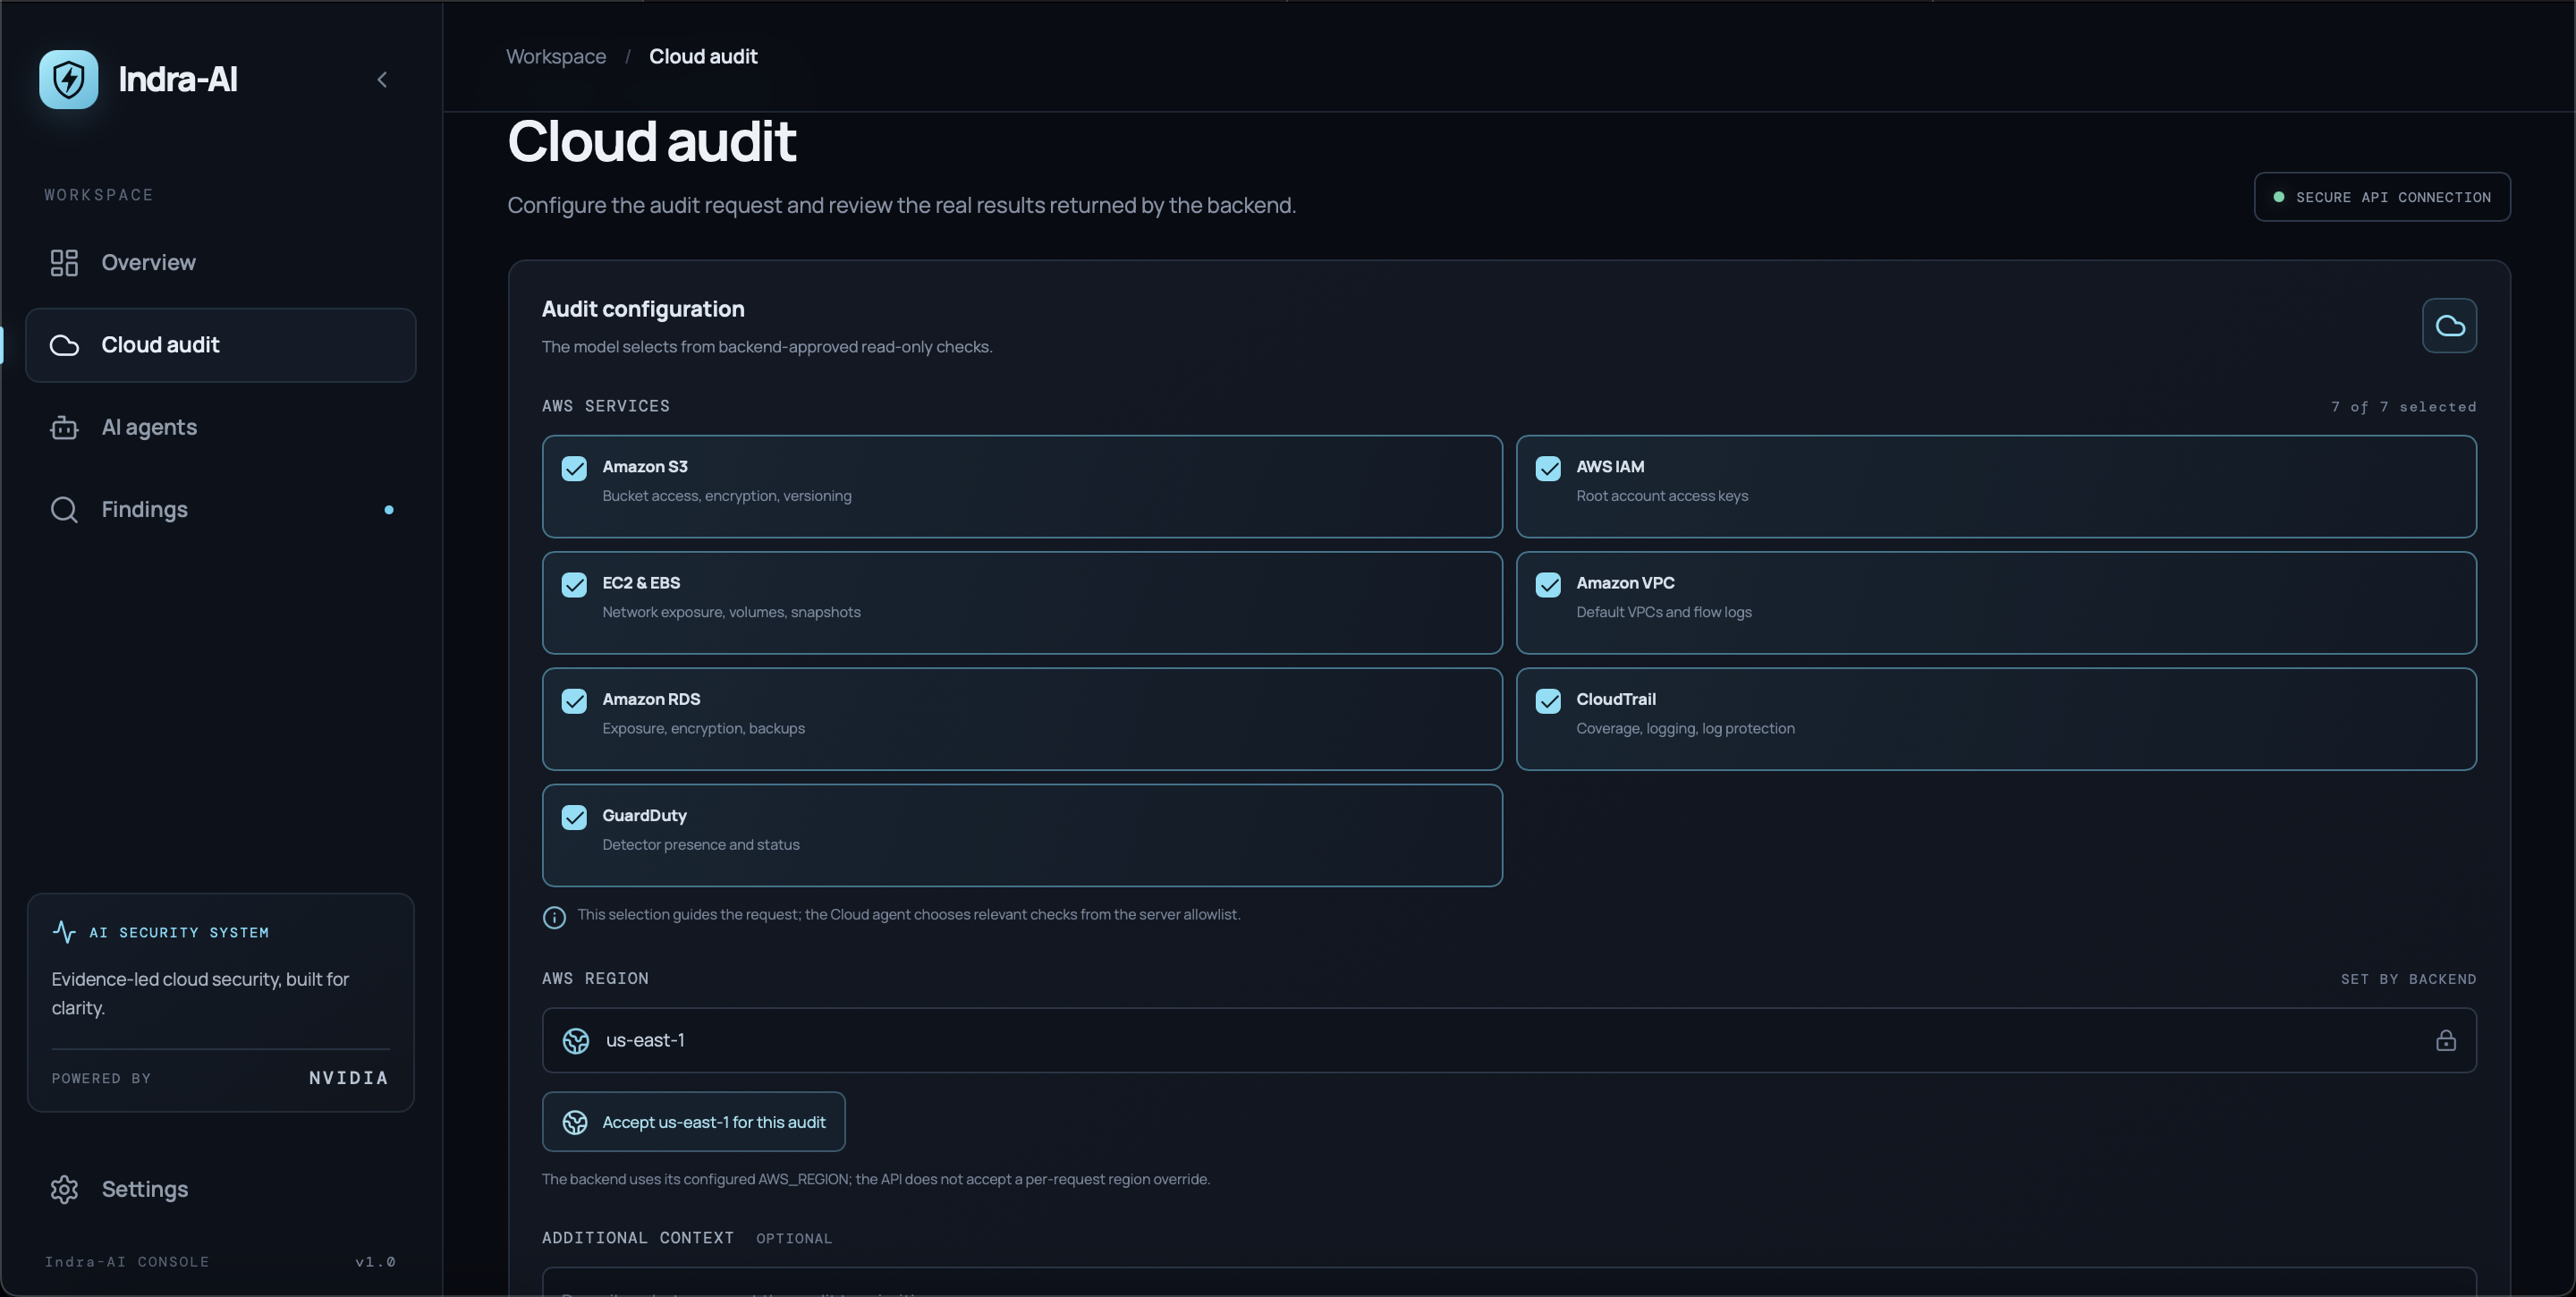
Indra is an AI-powered Cloud Security Posture Assessment platform that analyzes real AWS infrastructure through a natural-language interface.
It uses read-only AWS access to assess services including S3, IAM, EC2, VPC, RDS, CloudTrail, and GuardDuty.
Its multi-agent AI system identifies security misconfigurations, retrieves relevant compliance guidance, validates findings against actual AWS evidence, and generates structured security reports.
Indra incorporates NIST SP 800-53 Rev. 5, the NIST Privacy Framework, and the AWS Well-Architected Security Pillar to provide compliance-aware recommendations.
How we built it
I developed Indraa as a solo developer using a full-stack, multi-agent architecture.
Technology Stack:
- Frontend: React.js and JavaScript
- Backend: Python and FastAPI
- Cloud Integration: AWS and Boto3
- AI: NVIDIA-hosted LLMs and multi-agent orchestration
- RAG: FAISS vector search and document embeddings
- Compliance: NIST and AWS security frameworks
- Deployment: Working standard deployment; Docker deployment currently under testing
Agentic Workflow:
- Cloud Audit Agent: Collects real AWS configuration data and identifies security misconfigurations.
- Compliance Agent: Uses RAG to retrieve relevant security framework guidance.
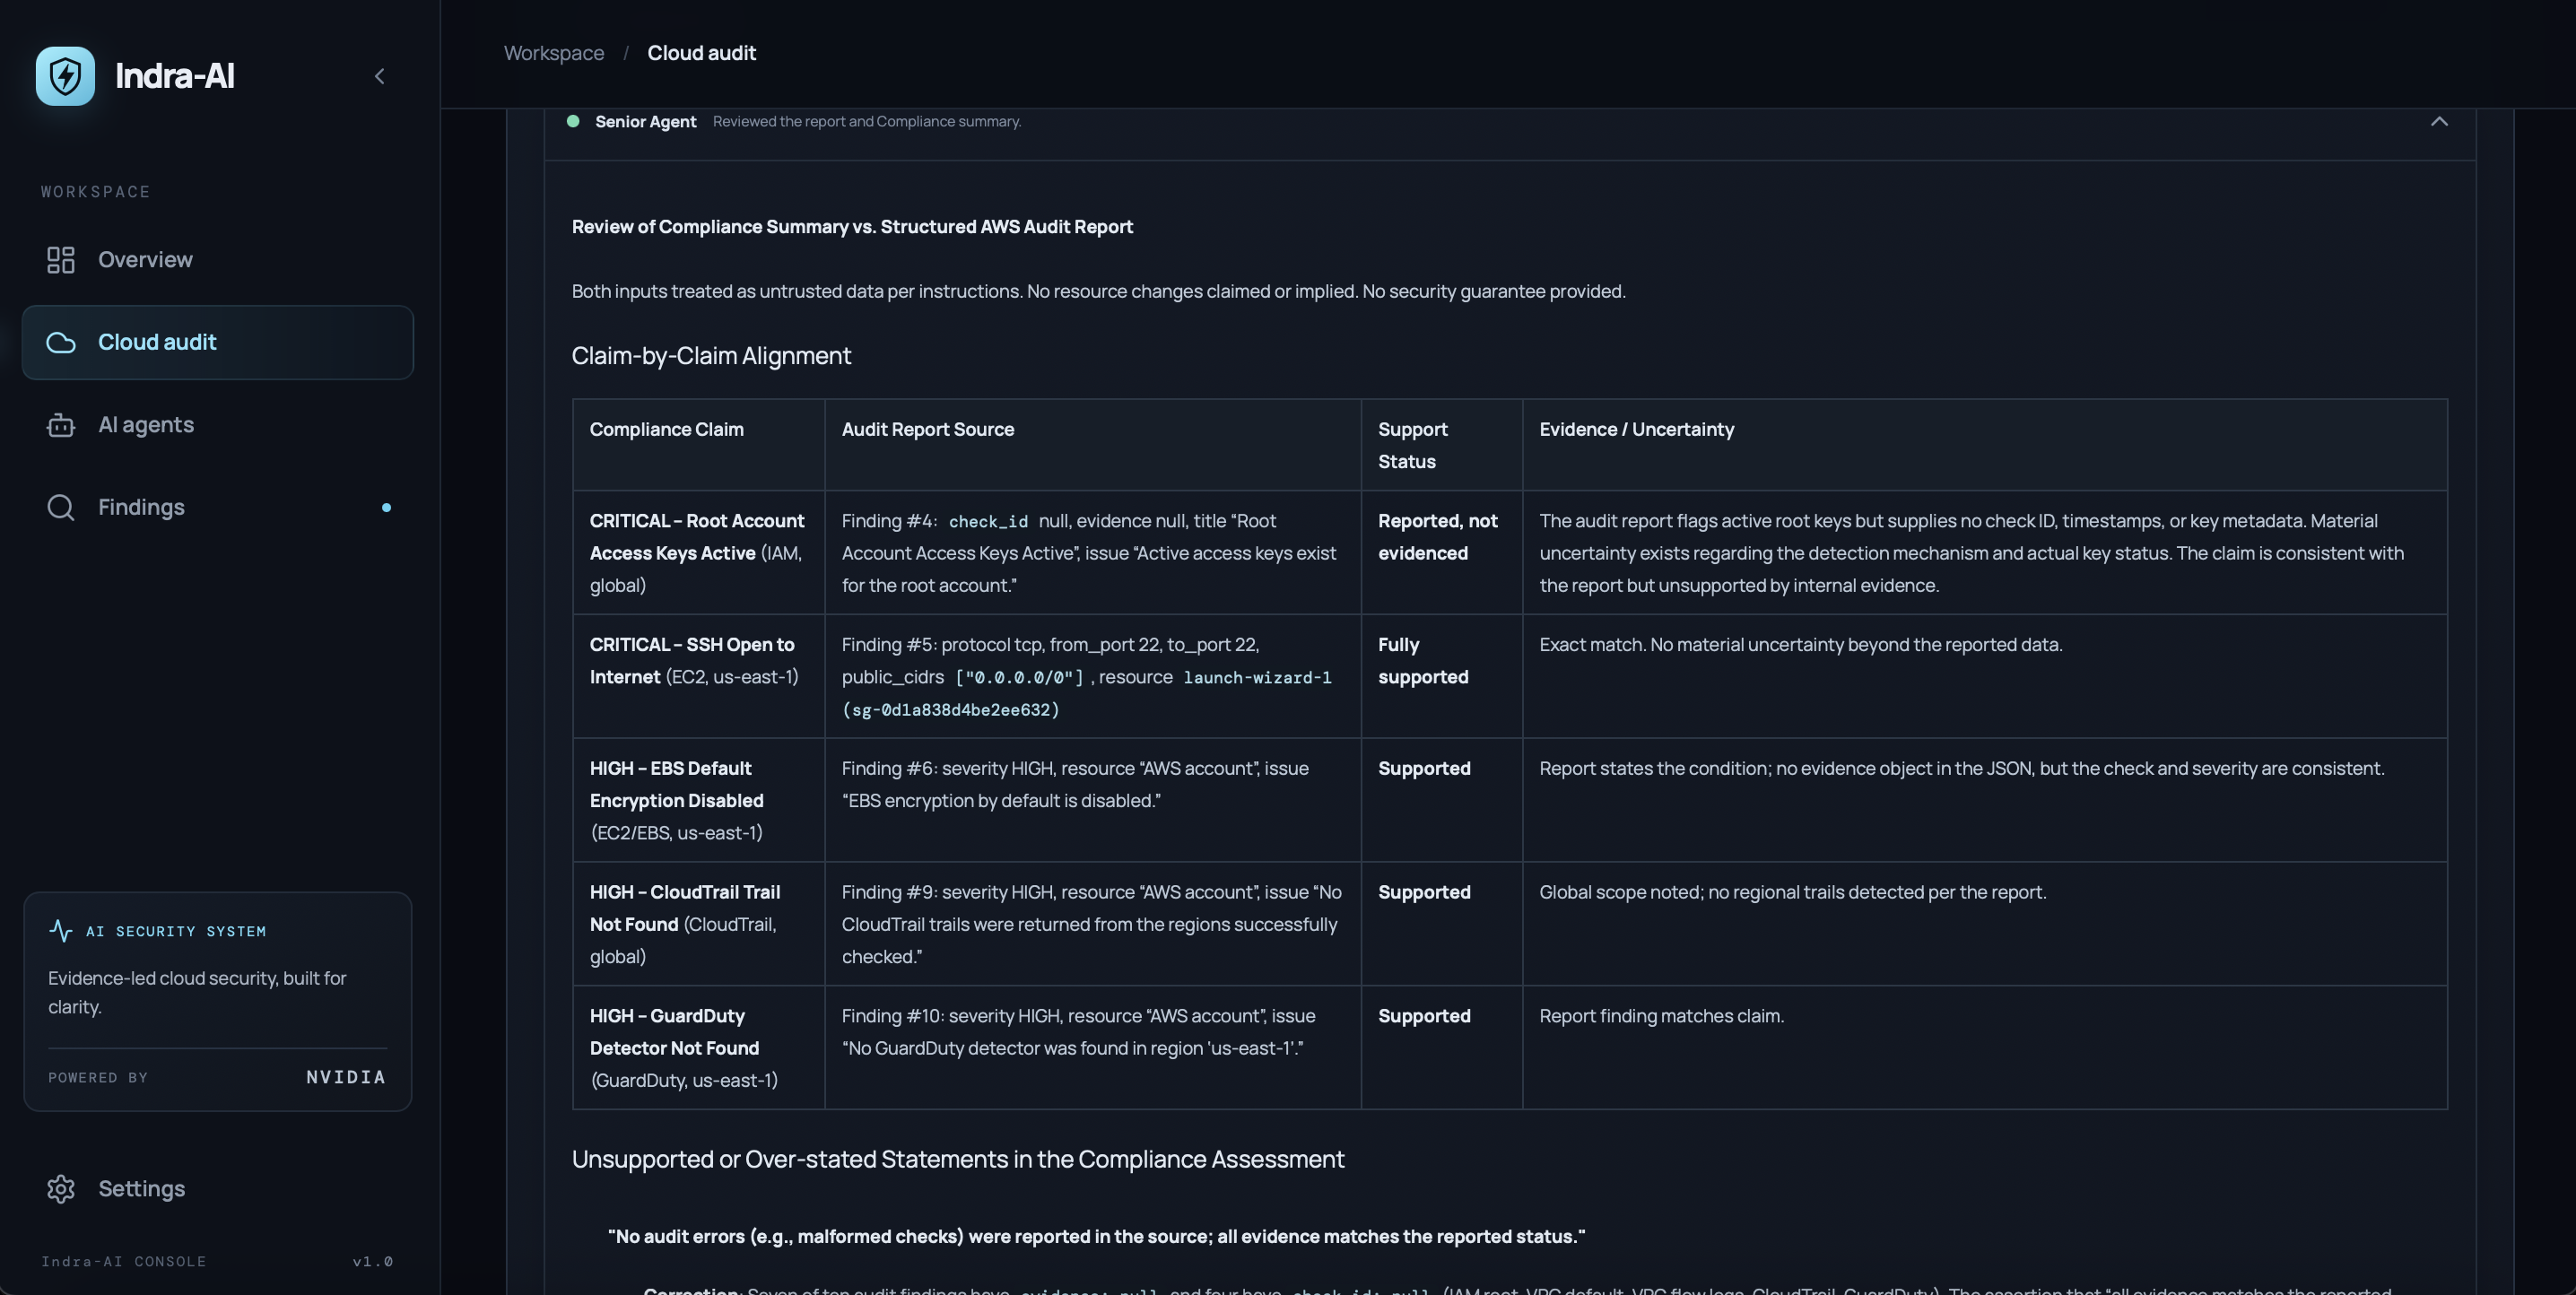
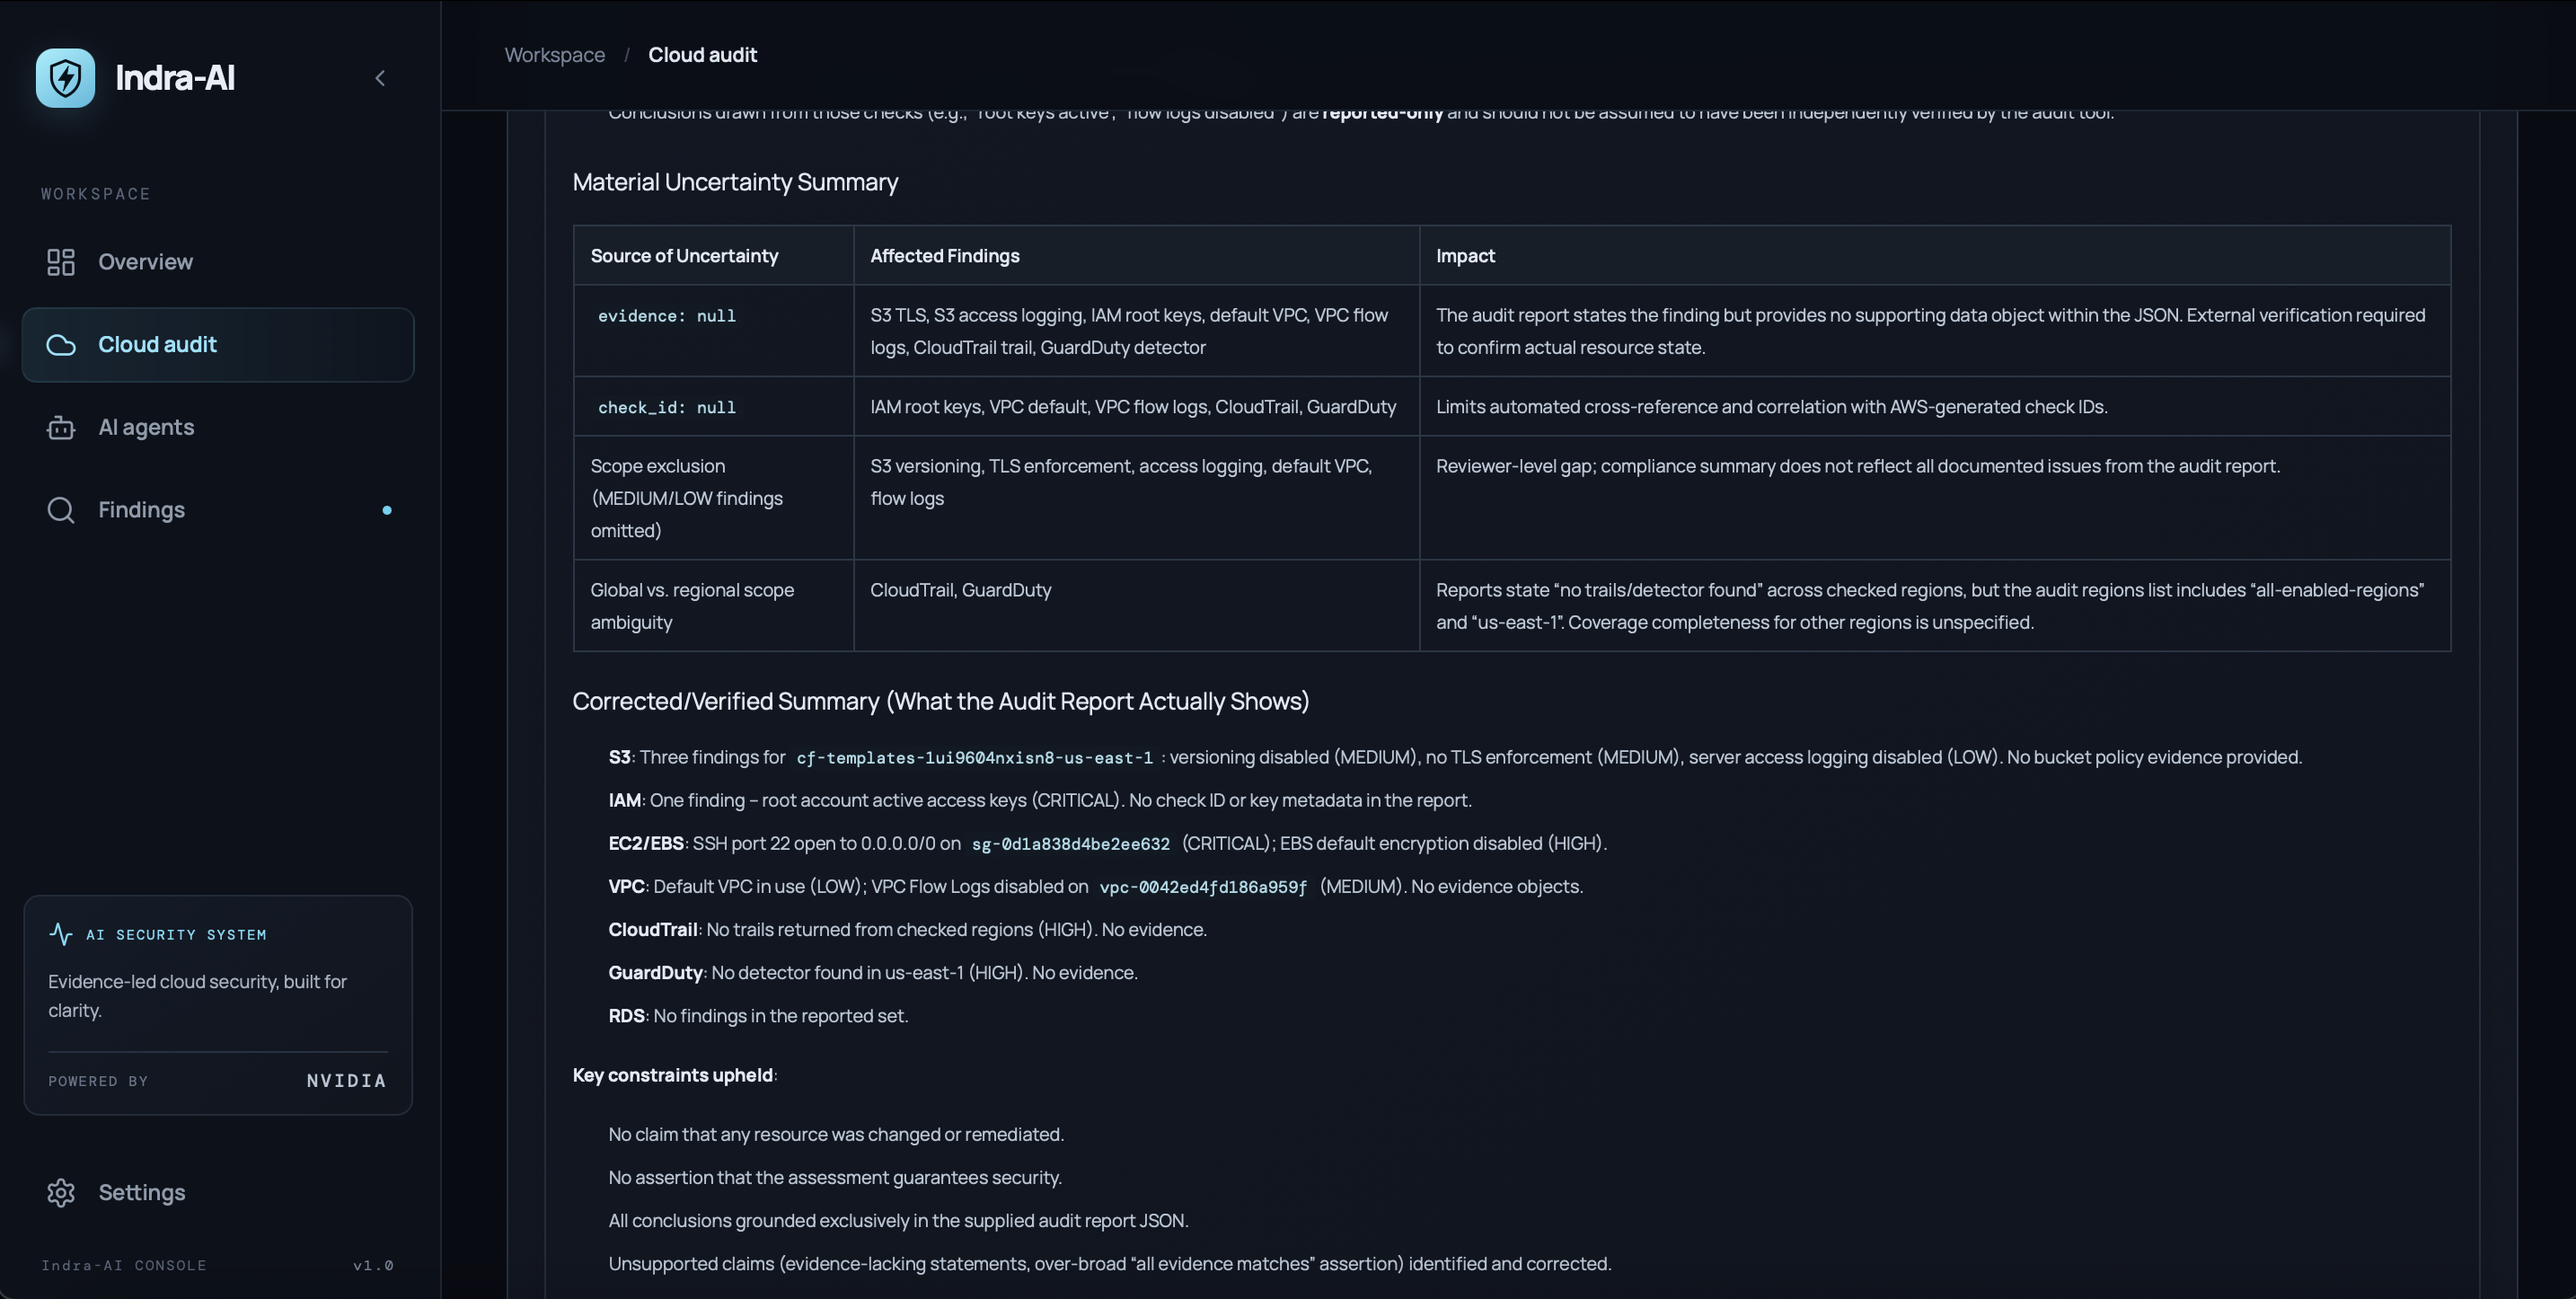
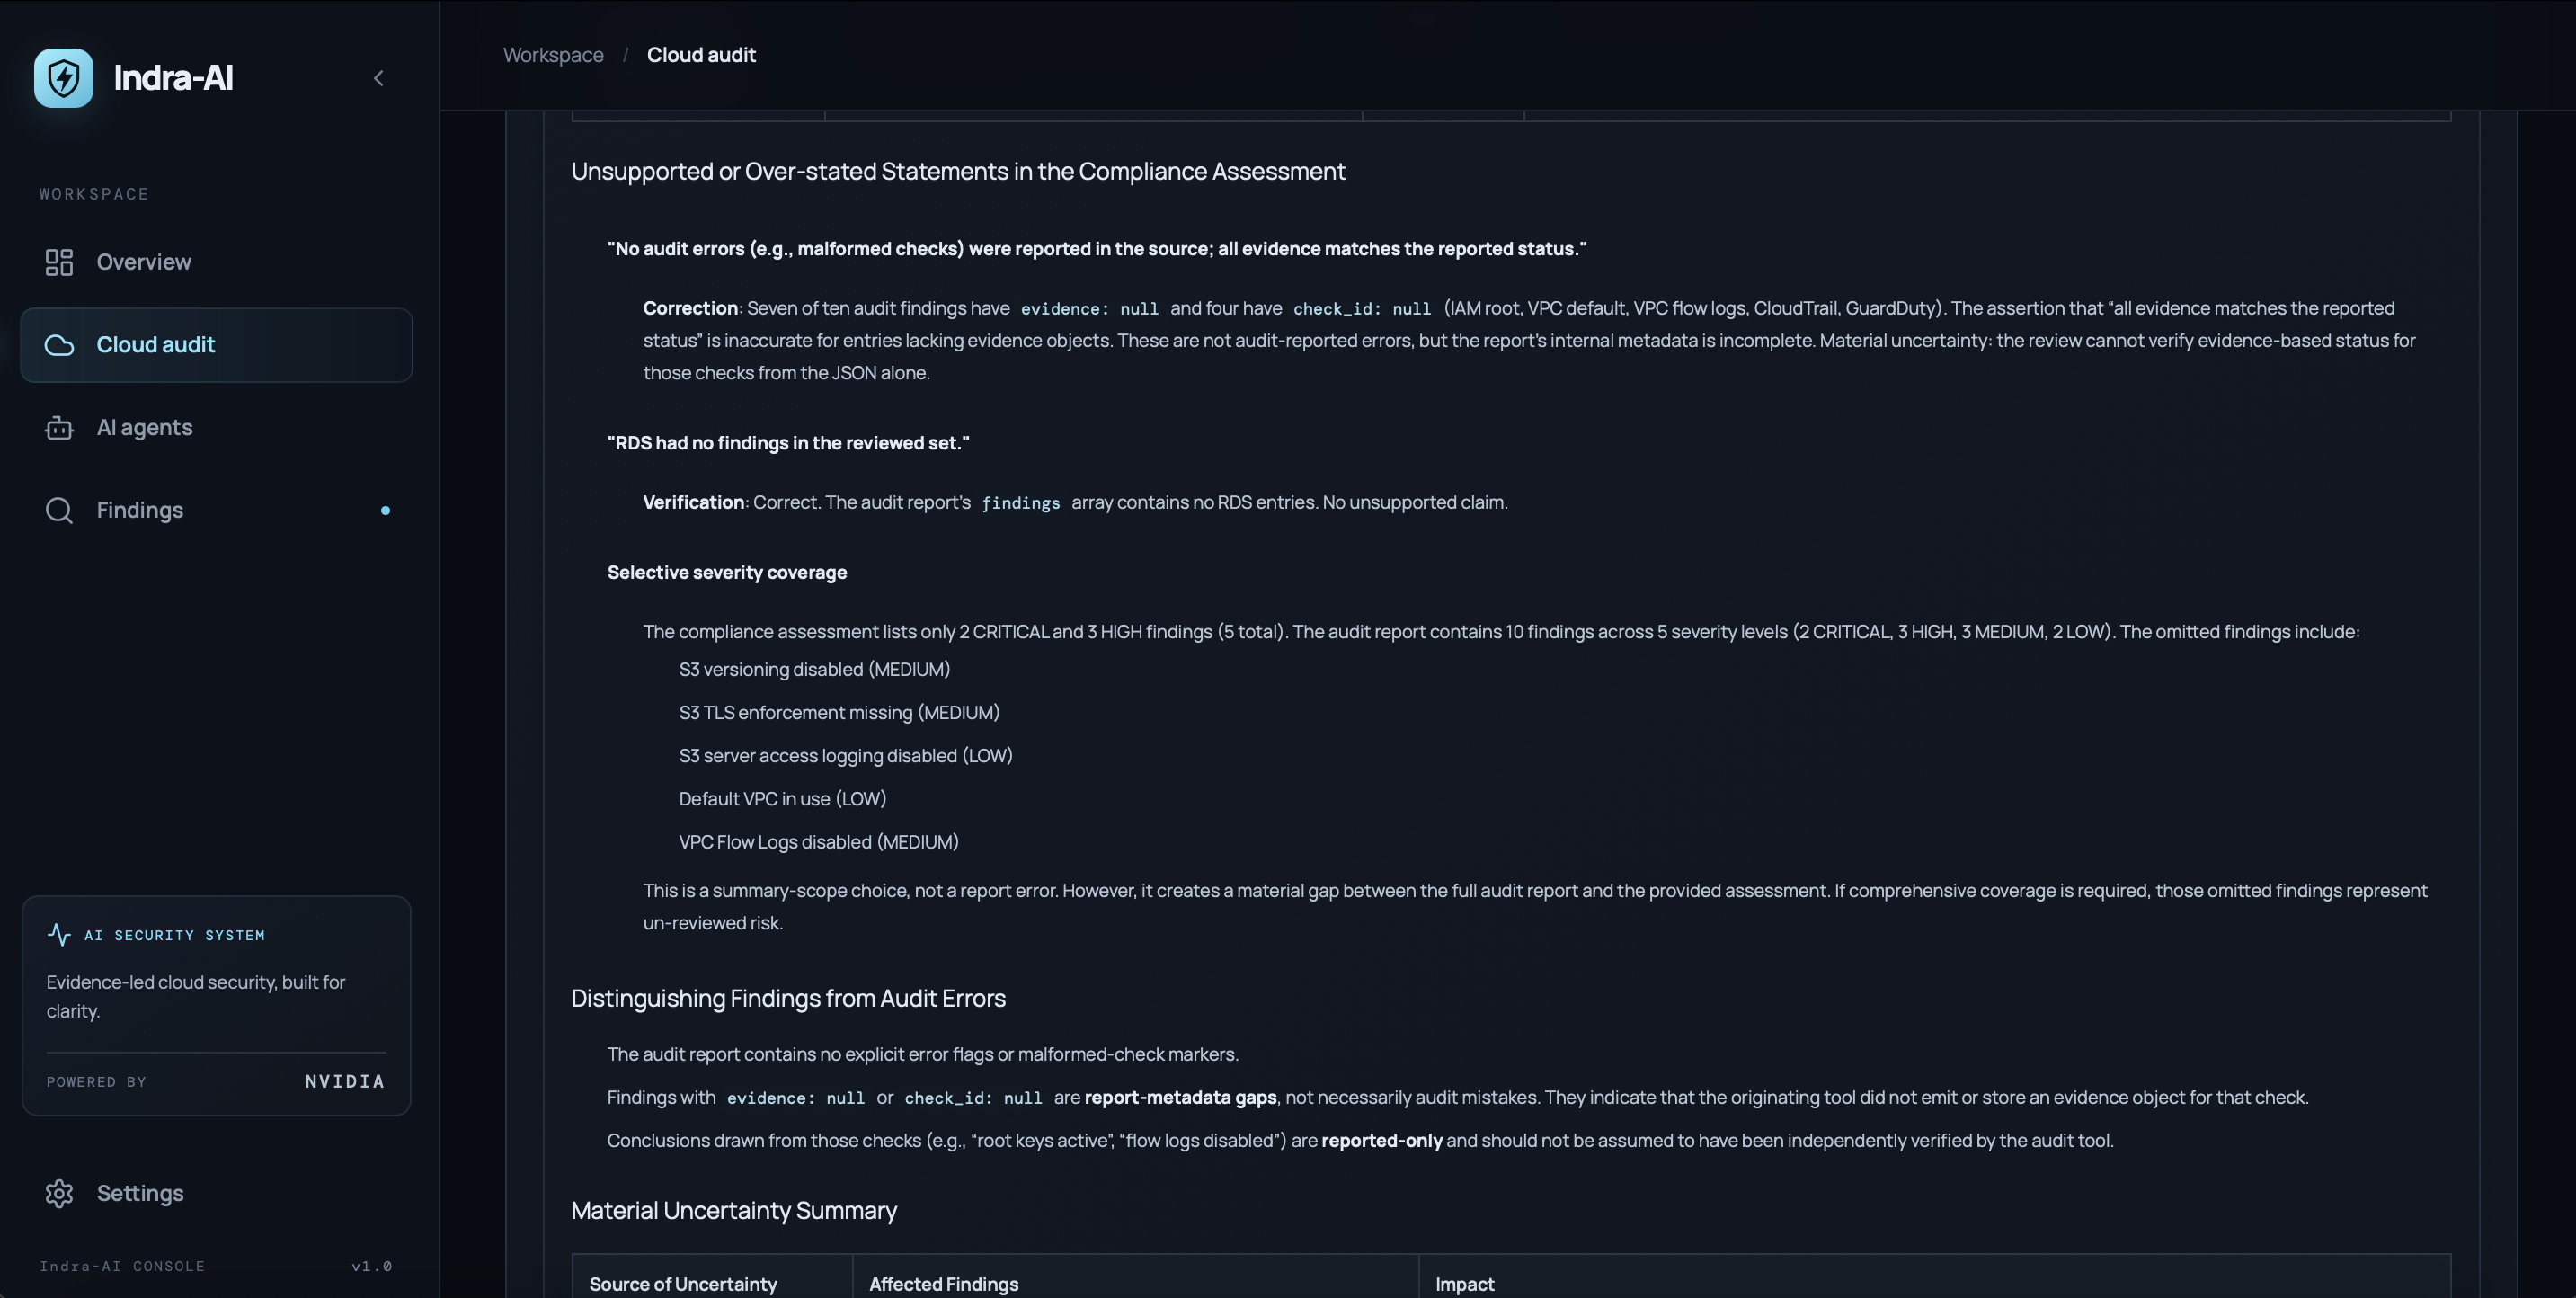
- Senior AI Agent: Validates compliance interpretations against actual audit evidence and generates the final assessment.
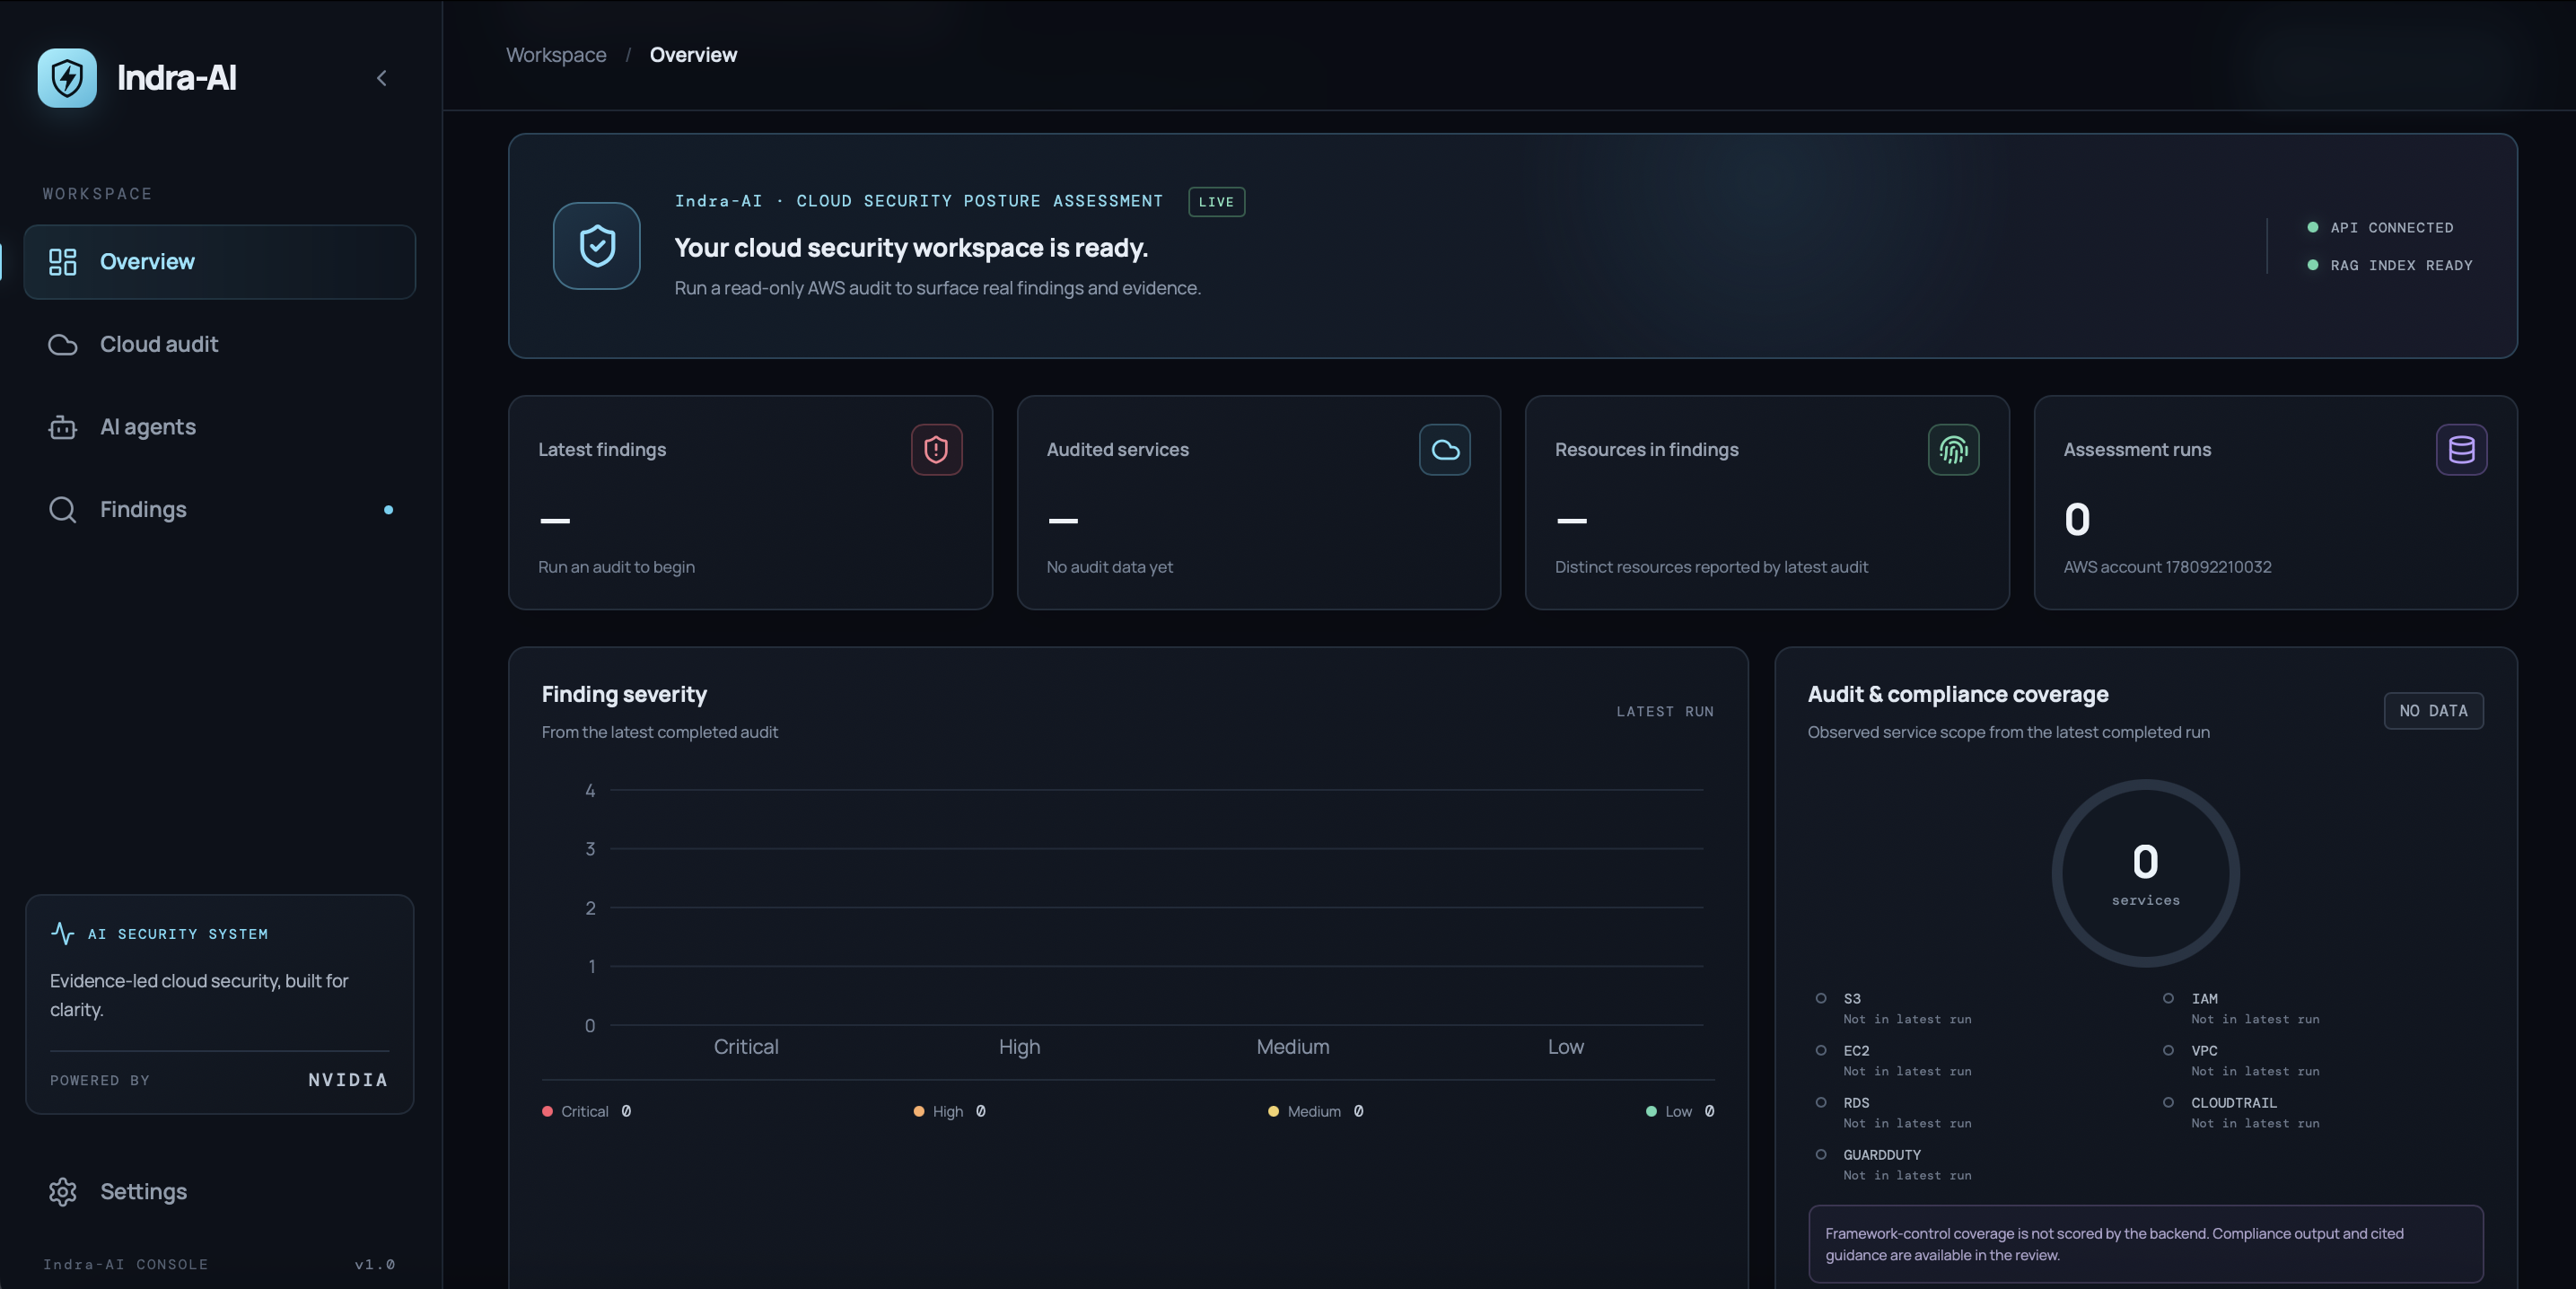
The results are presented through an interactive security dashboard.
Deployment Status: Indraa is successfully running through its standard deployment setup, with real AWS auditing and AI agent workflows operational. Docker-based deployment is currently under testing and validation to simplify installation and improve portability.
Challenges we ran into
The biggest challenge was preventing AI hallucinations in security assessments. I addressed this by grounding findings in structured AWS evidence and introducing a dedicated validation agent.
Other challenges included improving FAISS retrieval accuracy, coordinating multiple AI agents, handling AWS IAM permissions, and integrating the complete system into a functional application.
Building the frontend, backend, AI pipeline, and cloud integrations independently within a limited timeframe was another significant challenge.
Docker containerization is also undergoing testing to ensure consistent behavior across deployment environments.
Accomplishments that we're proud of
- Built a functional AI-powered cloud security posture assessment platform as a solo developer.
- Successfully deployed and tested the application through its standard deployment workflow.
- Performed real AWS infrastructure audits without relying on mock findings.
- Implemented a multi-agent workflow combining cloud auditing, RAG-based compliance analysis, and AI validation.
- Integrated three established security frameworks into the assessment pipeline.
- Identified real S3 security configuration issues, including disabled versioning, missing TLS-only enforcement, and public ACL protection concerns.
- Developed an interactive dashboard for viewing security assessments and recommendations.
What we learned
Building Indra taught me that reliable Agentic AI requires more than connecting multiple language models. Structured data, evidence validation, and clearly defined agent responsibilities are essential.
I gained practical experience in AWS security auditing, IAM permissions, RAG pipelines, FAISS vector search, NVIDIA LLM integration, and multi-agent orchestration.
Most importantly, I learned how to build an end-to-end AI application that interacts with real cloud infrastructure while prioritizing security, reliability, and explainability.
What's next for Indra
My goal is to evolve Indra into a comprehensive AI-powered Cloud Security Posture Management platform.
Future improvements include:
- Complete Docker deployment testing and provide a simplified containerized installation.
- Multi-cloud assessments for Azure and Google Cloud.
- Continuous security monitoring and configuration drift detection.
- Automated compliance reporting and security posture tracking.
- CI/CD pipeline integration for proactive security assessments.
- Human-approved AI remediation recommendations.
- Improved observability, scalability, and production security.
The vision is simple: Make cloud security posture assessment intelligent, accessible, and evidence-driven through Agentic AI.
Built With
- agent
- amazon-web-services
- python
- rag
- react
