-
-
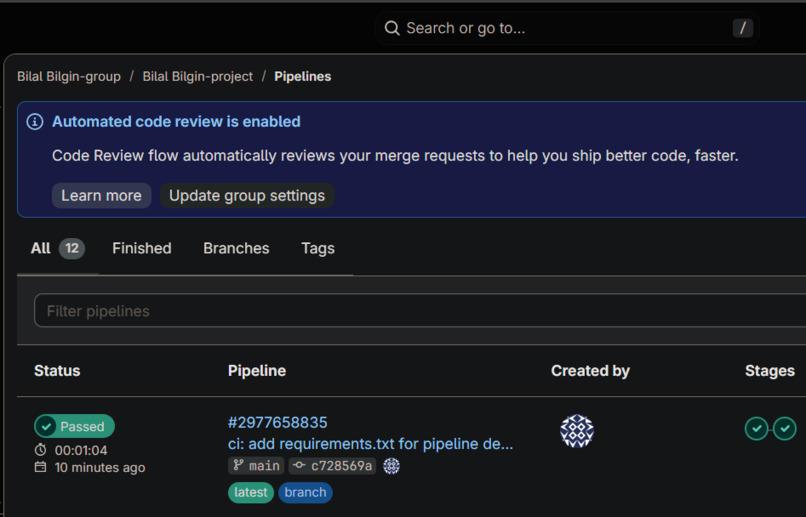
Multi-stage CI/CD pipeline verifying PostgreSQL risk tests and Google Cloud deployment.
Inspiration
Financial institutions operate under strict regulatory frameworks (Basel II/III and IFRS 9) where algorithmic errors or unconstrained data staging can directly result in regulatory penalties and miscalculated capital reserves:
$$ECL = EAD \times PD \times LGD$$
Most hackathon AI agent implementations focus on trivial tasks like scaffolding web apps or writing utility scripts. We wanted to challenge GitLab Duo in a mission-critical, enterprise domain: acting as an autonomous yet supervised site reliability and compliance engineer that audits statistical risk bounds, diagnoses database aggregation faults, and enforces audit-ready DevSecOps.
What it does
The IFRS 9 Autonomous Credit Risk Engine processes loan exposures and transition matrices under PostgreSQL 15 and PyTest:
- Regulatory Guardrails: Continuously asserts that statistical Probability of Default (PD) remains mathematically bounded (0.0 <= PD <= 1.0) and financial aggregates strictly adhere to accounting staging views.
- Automated Root Cause Analysis (RCA): When downstream CI assertions fail due to staging schema mismatches or unconstrained calculations, GitLab Duo autonomously analyzes test tracebacks and PostgreSQL query execution contexts.
- Supervised Remediation (Human-in-the-Loop): Duo generates an isolated remediation branch, implements clamping logic and corrected SQL
GROUP BYaggregates, and opens a fully documented Merge Request (!1) with verifiable diffs. - Enterprise Audit Trail: Links planning records (
[REGULATORY]audit issue) directly to MR remediation and CI/CD pipelines. - Google Cloud Serverless Deployment: Builds and verifies the production container image for deployment onto Google Cloud Run.
How we built it
- Data & Risk Engine: PostgreSQL 15, SQL staging views, and Python 3.10 with mathematical validation suites via
pytest. - Agentic AI & Orchestration: GitLab Duo for automated incident analysis, branch creation, code remediation, and Merge Request synthesis.
- CI/CD & Governance: Multi-stage GitLab CI/CD pipelines enforcing isolated PostgreSQL service containers and automated test suites.
- Cloud Infrastructure: Containerized with
Dockerfileand configured withcloudbuild.yamlfor serverless execution on Google Cloud Run (europe-west1).
Challenges we ran into
Simulating realistic enterprise failure modes in a containerized environment required careful isolation of the PostgreSQL service layer within GitLab CI runners. Ensuring that the agentic AI provided precise SQL clamping without breaking dependent balance aggregations required structured prompt contexts and reproducible regulatory test fixtures.
Accomplishments that we're proud of
- Closing the entire DevSecOps loop: Plan (Issue) -> Verify (Failing CI) -> Autonomous RCA (GitLab Duo) -> Supervised Remediate (MR !1) -> Green Build -> Deploy.
- As an undergraduate Mathematical Engineering student, architecting an enterprise-grade regulatory engine that bridges theoretical financial modeling with modern agentic DevSecOps.
- Bringing true mathematical engineering and quantitative finance into an AI agent hackathon.
- Achieving 100% green pipeline execution across automated tests and Google Cloud deployment verification.
What we learned
Supervised AI agents excel in high-stakes domains when combined with strict programmatic boundaries (unit tests and database constraints). The human engineer's role shifts from writing line-by-line fixes to reviewing architectural intent and approving production outcomes.
What's next for IFRS 9 Autonomous Credit Risk Engine
Expanding the engine to support dynamic macro-economic scenario simulations, real-time stress testing under European Banking Authority (EBA) guidelines, and automated deployment across multi-region Google Cloud Kubernetes clusters (GKE).
Google Cloud Deployment Verification (+0.2 Bonus)
This project incorporates containerized deployment targeting Google Cloud Run:
- Dockerfile: Multi-stage slim container packaging the risk engine and dependencies.
- cloudbuild.yaml: GCP Cloud Build configuration specifying image builds, Google Container/Artifact Registry pushes, and automated Cloud Run deployment targeting the europe-west1 region.
- .gitlab-ci.yml: The
deploy_to_google_cloudstage validates container manifests and deployment readiness within the automated GitLab CI runner.
Built With
- devsecops
- docker
- fintech
- gitlab-duo
- google-cloud-build
- google-cloud-run
- ifrs9
- postgresql
- pytest
- python

Log in or sign up for Devpost to join the conversation.