Inspiration
Web applications can contain security vulnerabilities that are difficult to identify, verify, and prioritize. We wanted to make security assessment more organized by bringing different scanning methods and actionable results into one platform.
What it does
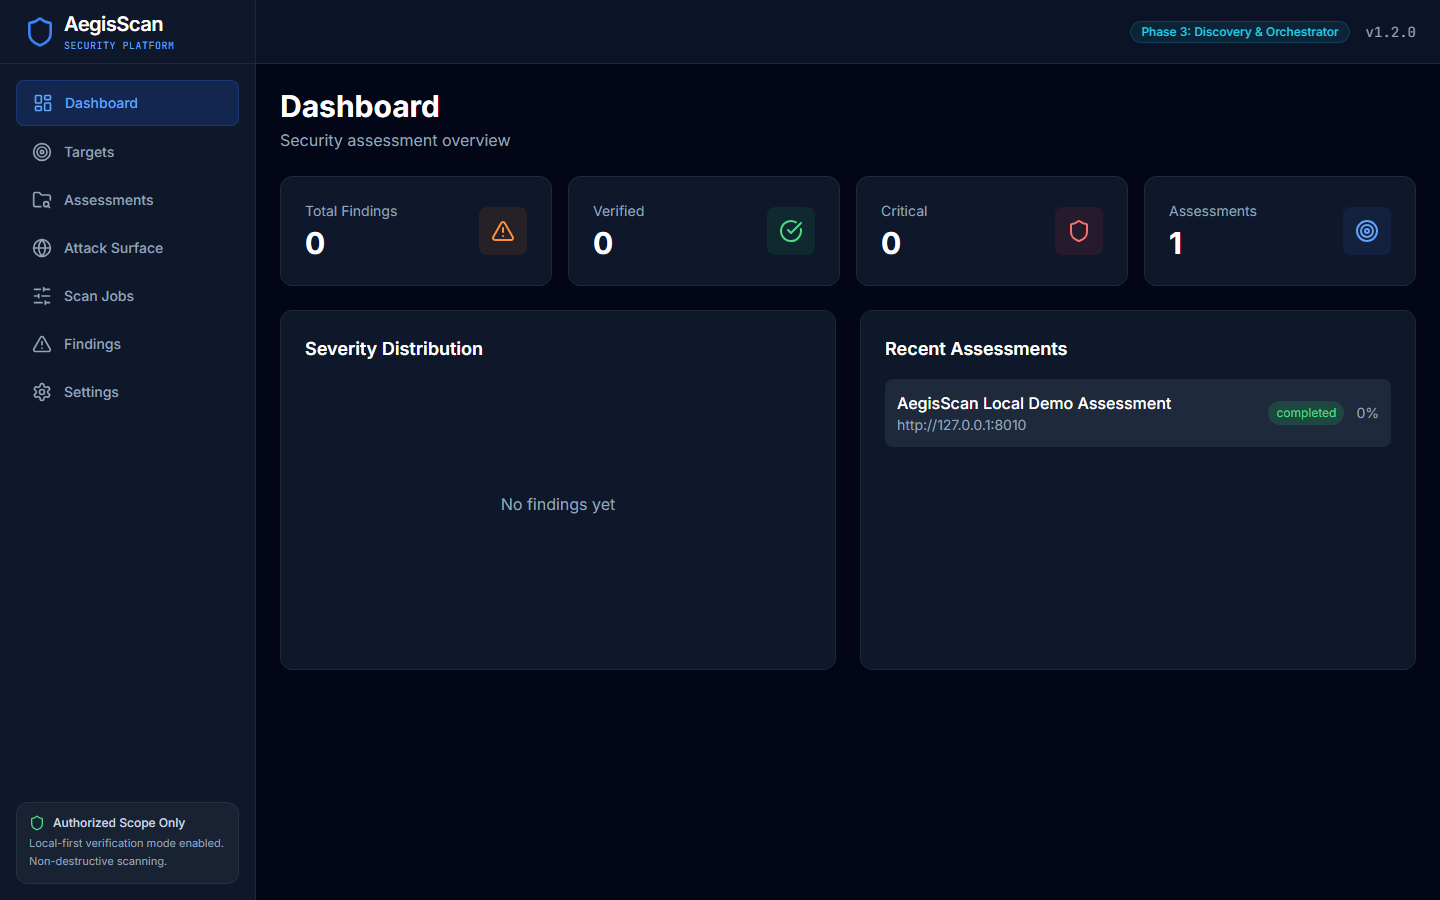
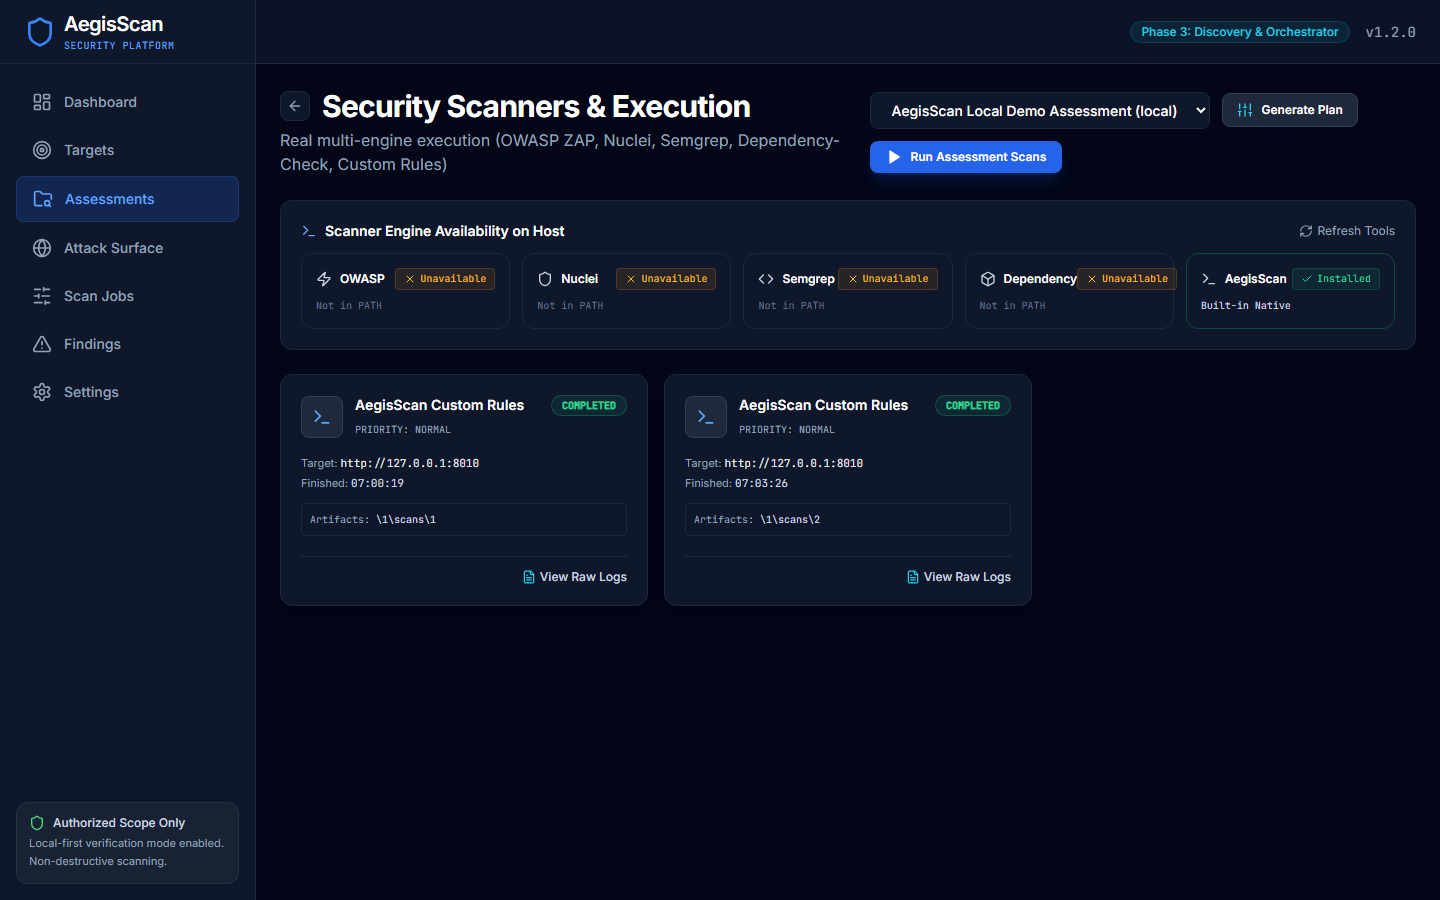
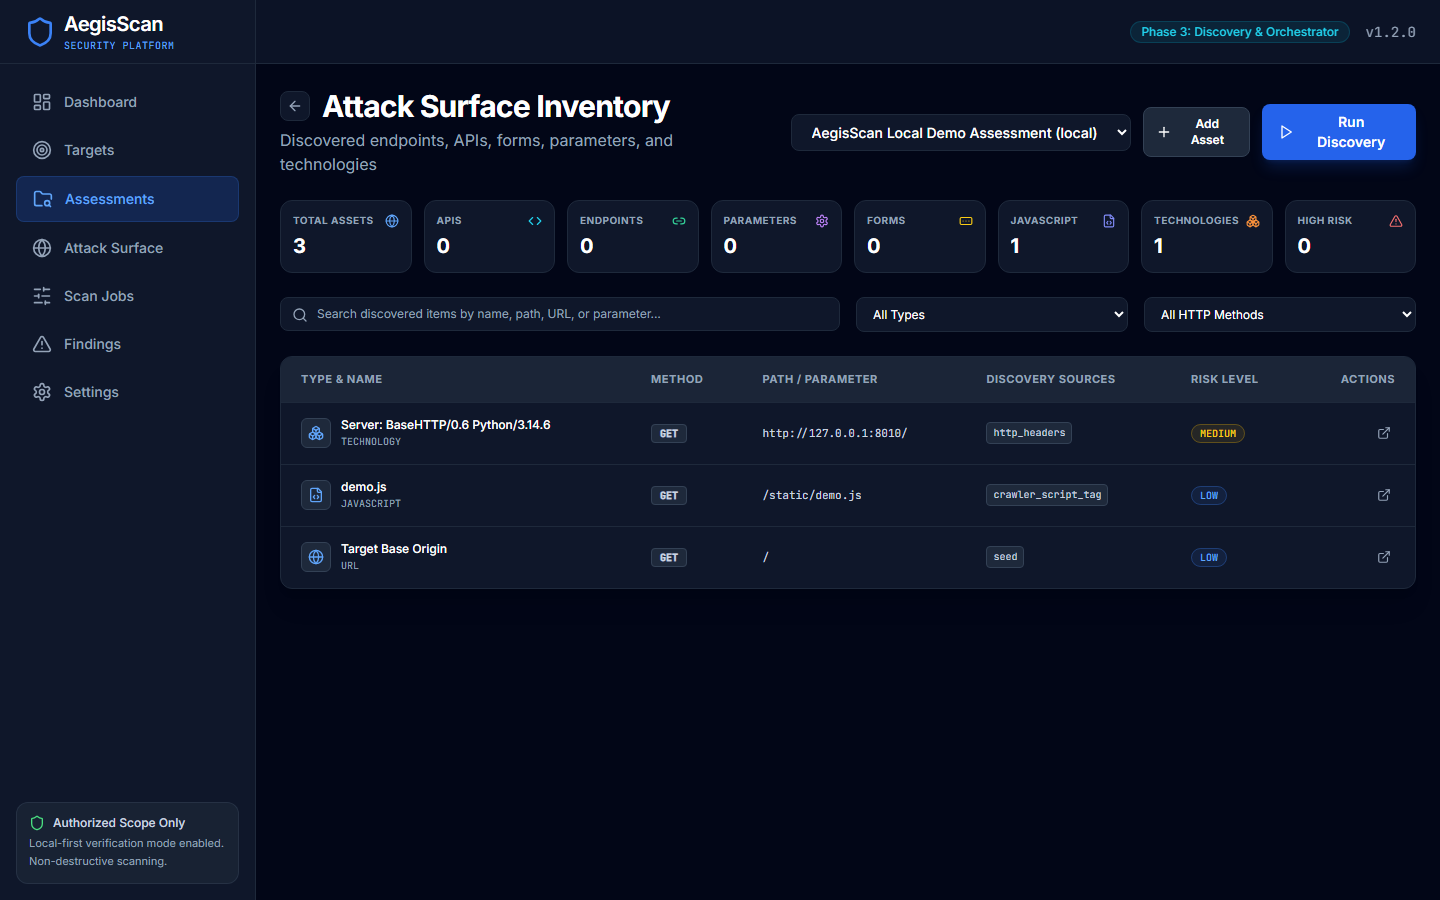
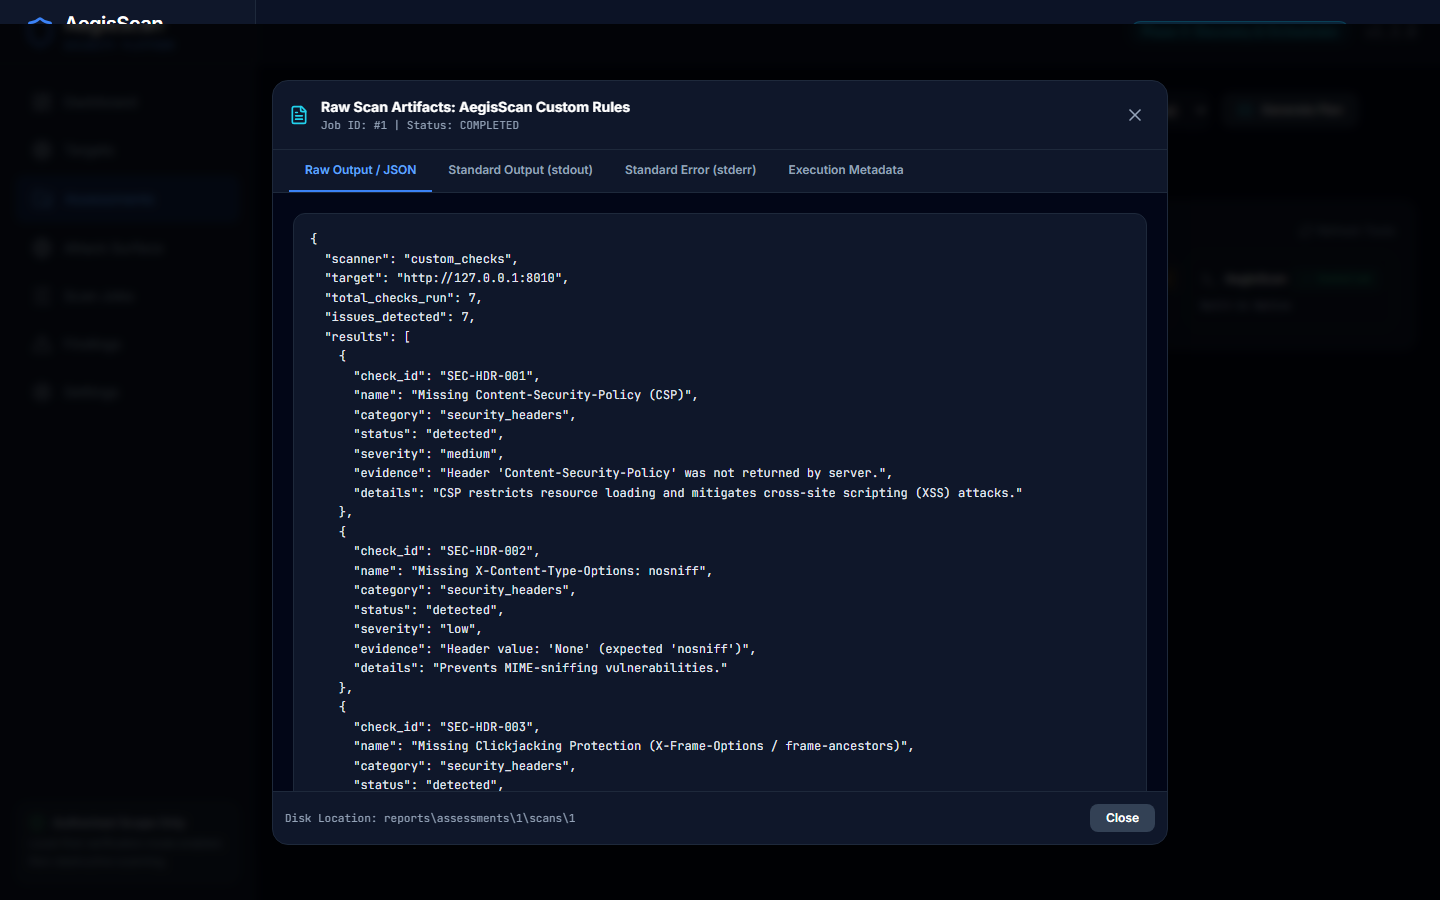
Aegis-Scan is an application security assessment platform that helps developers identify potential vulnerabilities, consolidate findings from different security checks, evaluate risk, and understand how to fix issues. Its goal is to turn scattered security results into clear, actionable guidance.
How we built it
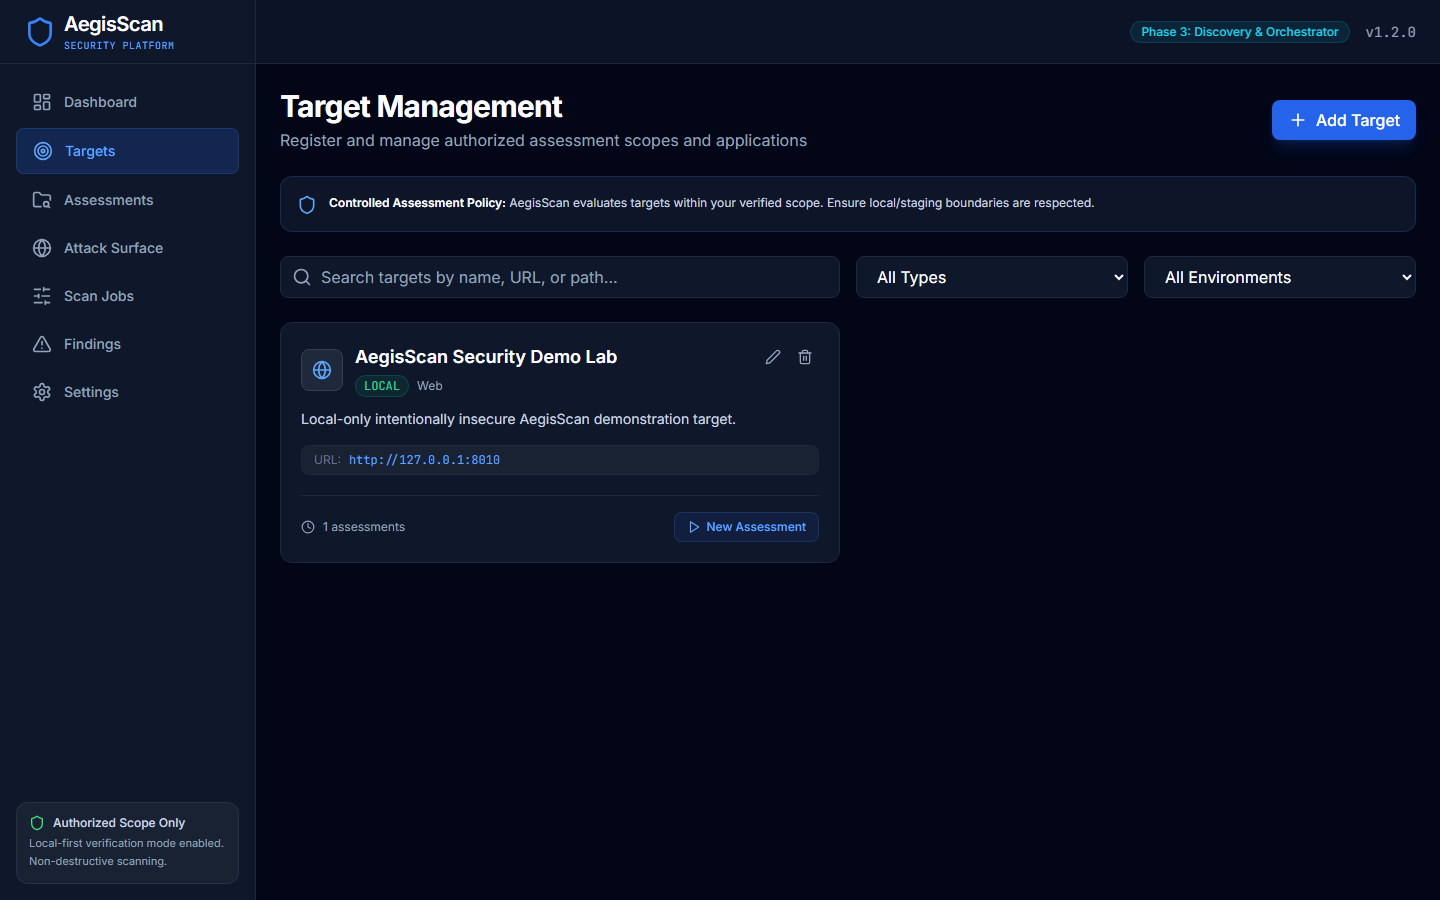
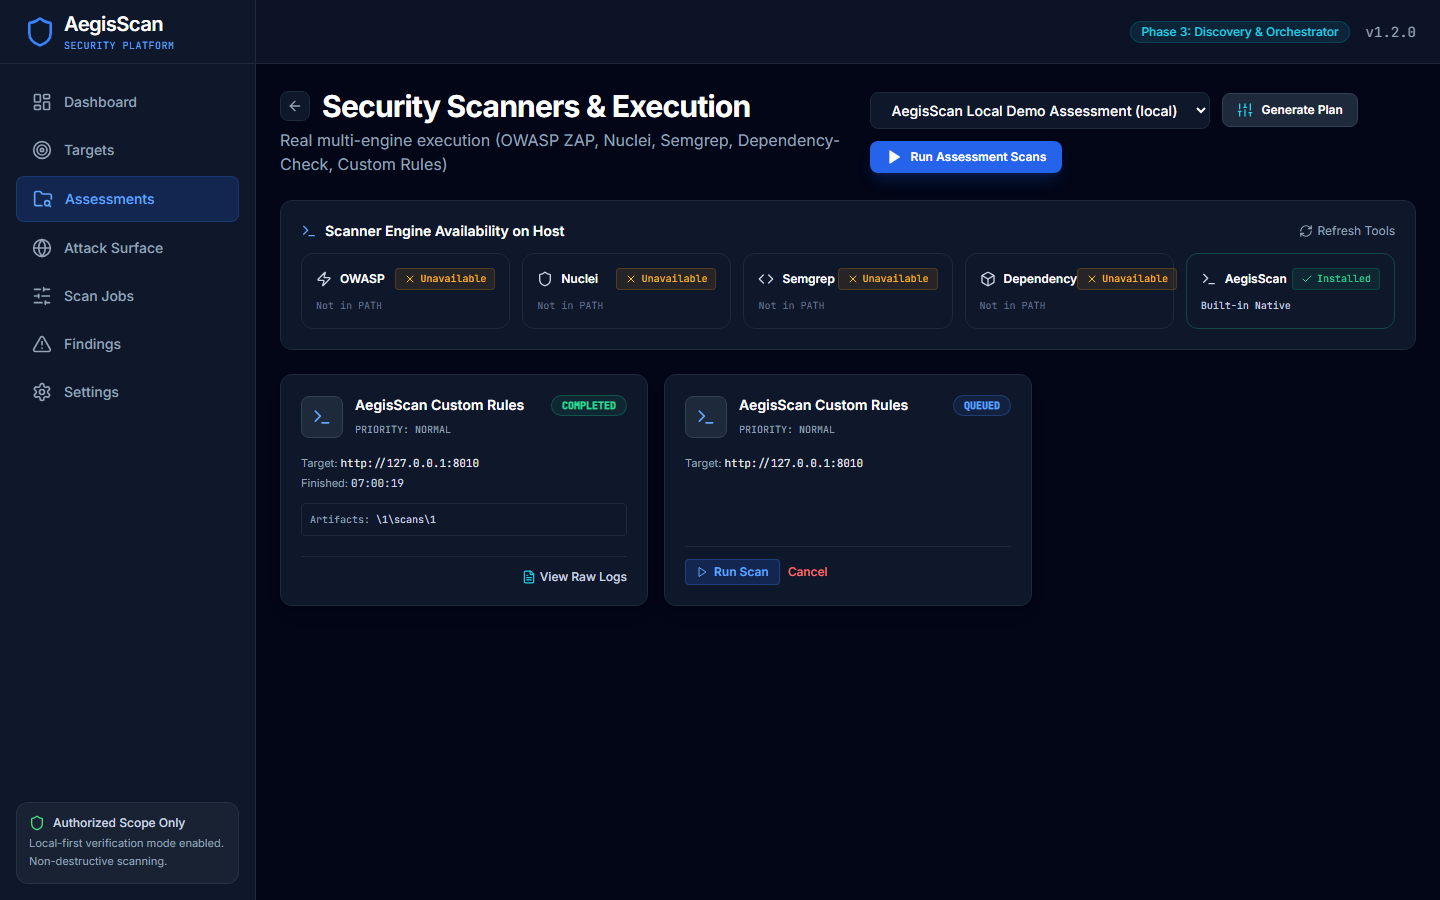
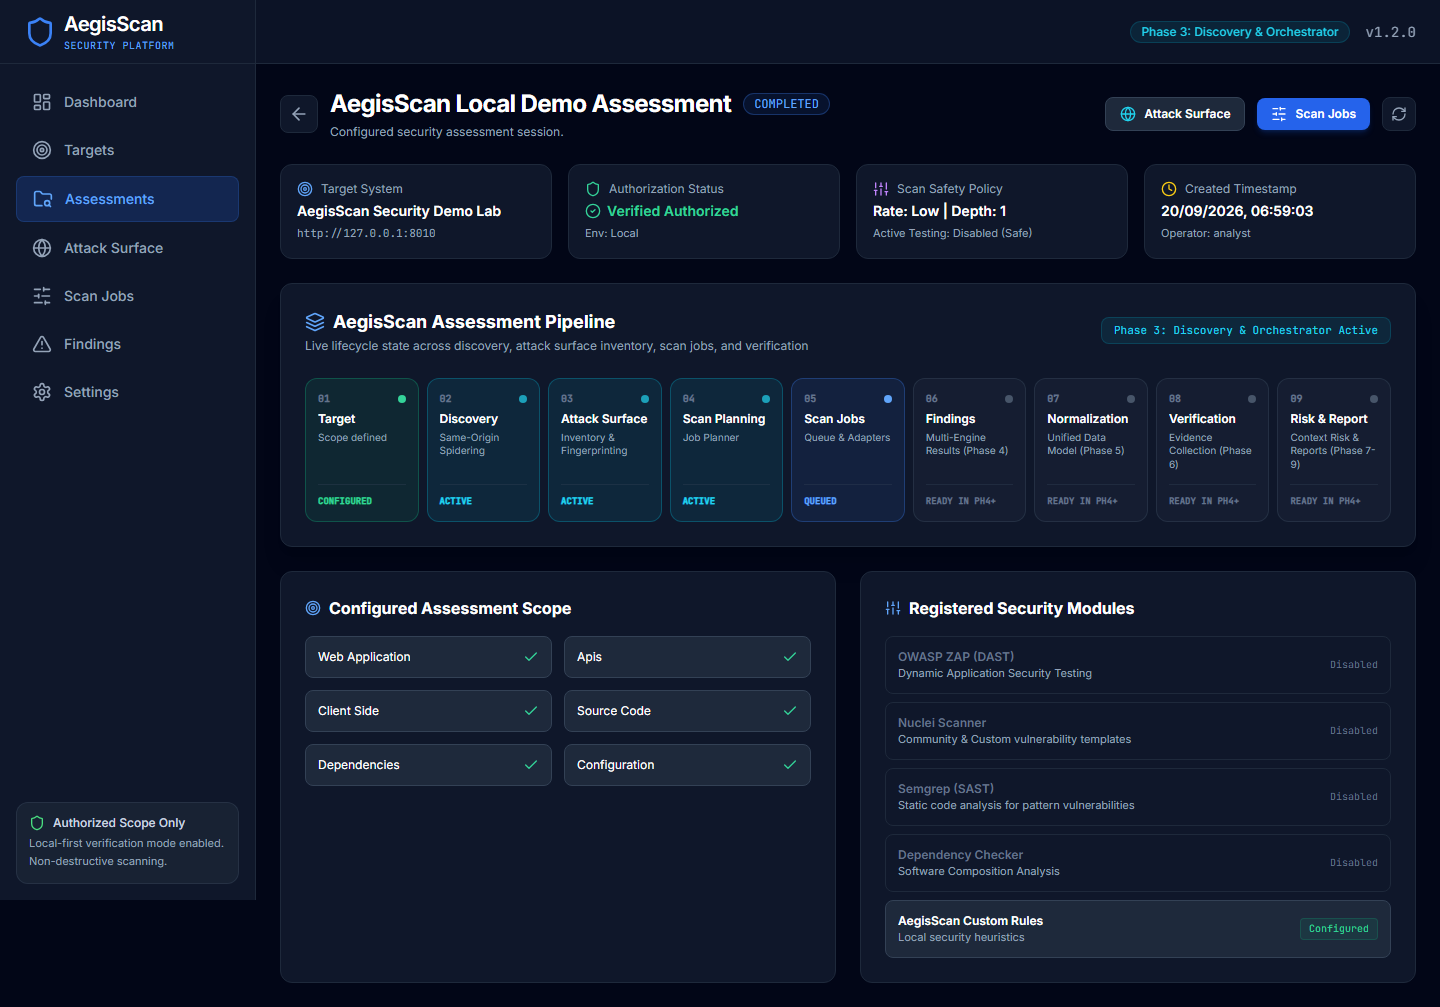
We developed Aegis-Scan as a local-first platform with a modular architecture for target management, security scanning, finding normalization, correlation, verification, risk assessment, and reporting. The workflow is designed to connect assessment results with supporting evidence and remediation recommendations.
Challenges we faced
One of the main challenges was bringing different types of security findings into a consistent format while keeping the results understandable and useful. We also had to balance scanning capabilities, evidence quality, usability, and safe assessment practices.
What we learned
Building Aegis-Scan helped us understand the importance of validating security findings instead of relying only on scanner output. We also learned how modular design and clear reporting can make security tools more practical for developers.
What's next
We aim to improve scanner integrations, strengthen finding verification, expand reporting capabilities, and make Aegis-Scan easier for developers to deploy and use.
Built With
- ai
- api
- fastapi
- mcp
- python
- react
- rest
- typescript

