Inspiration
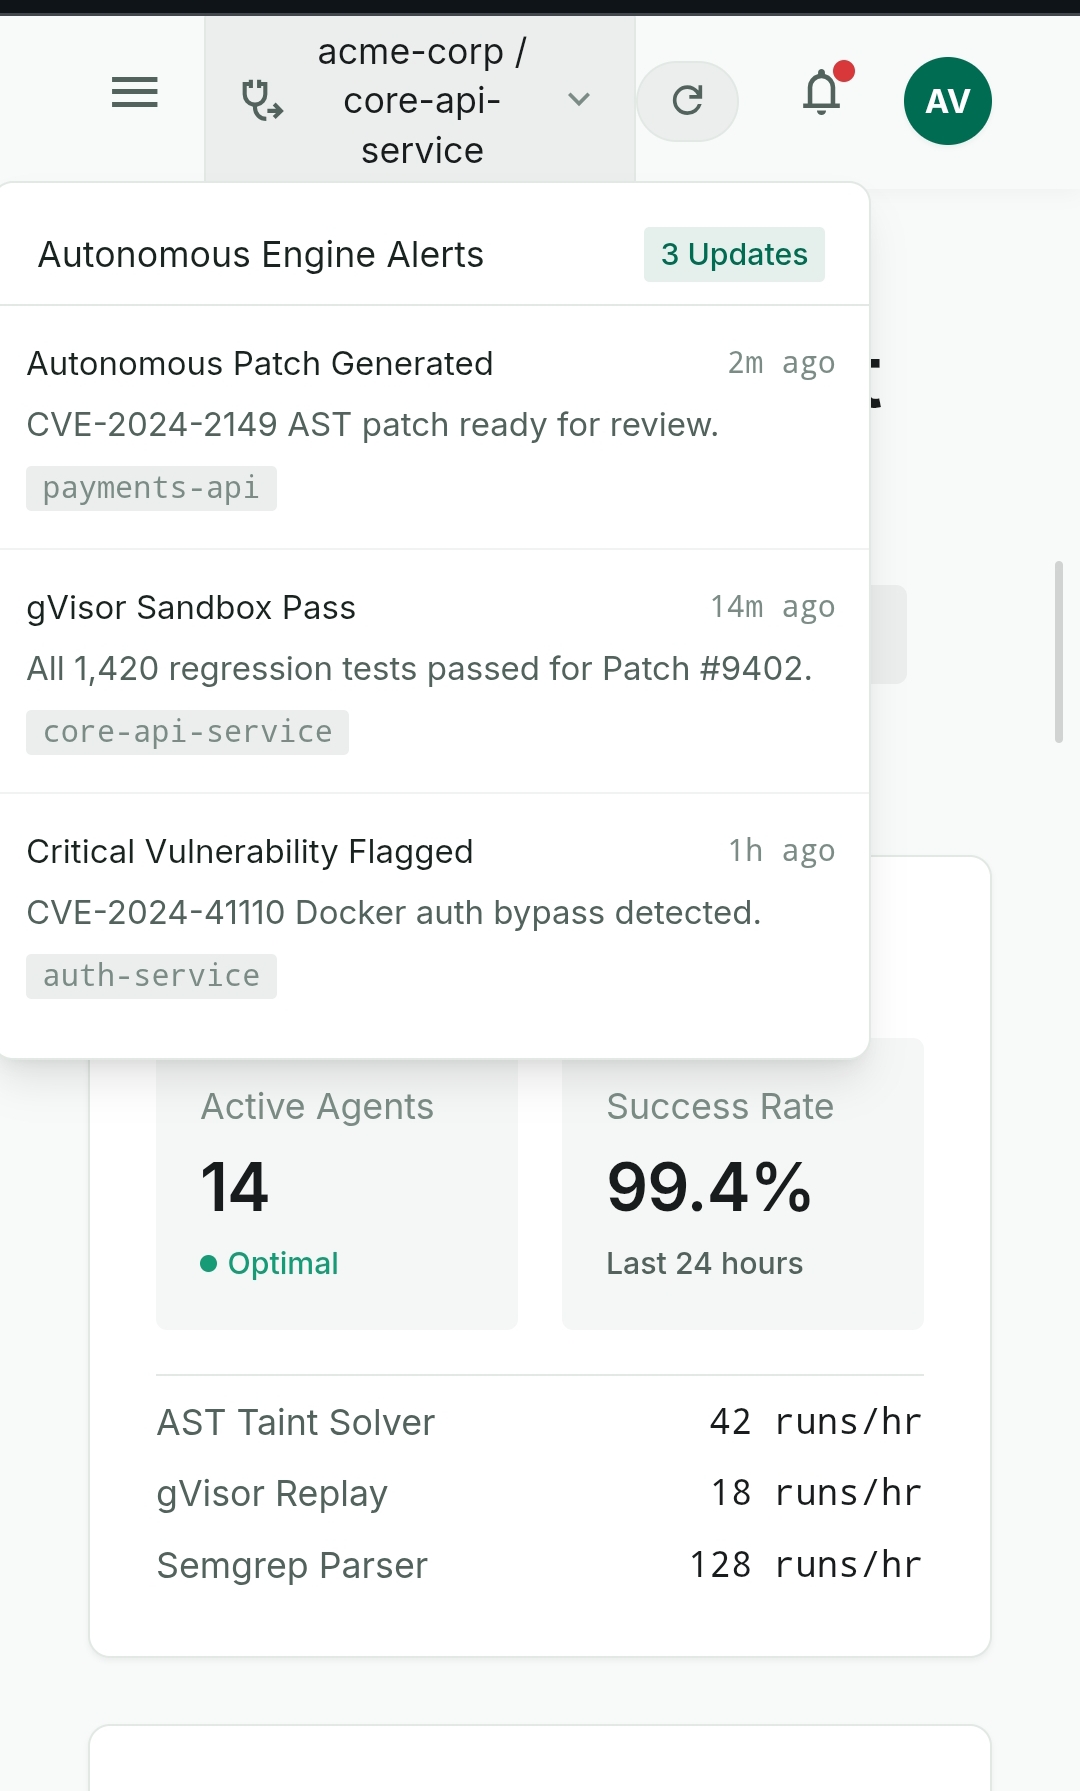
Security checks can be scattered across code review, dependency lists, secret scans, and deployment configuration. We wanted to bring those checks into one workbench where developers can import a project, review security findings, and keep track of what needs attention.
What it does
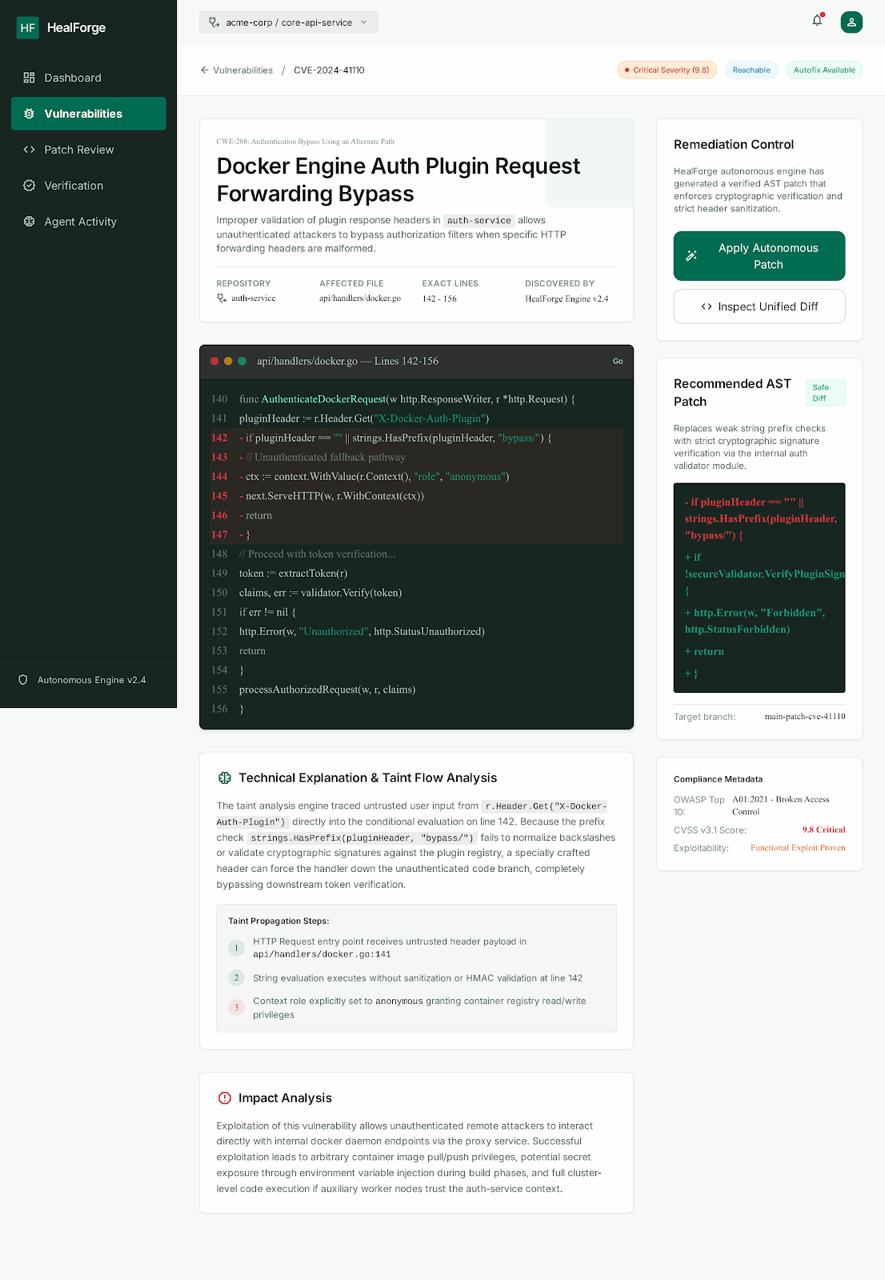
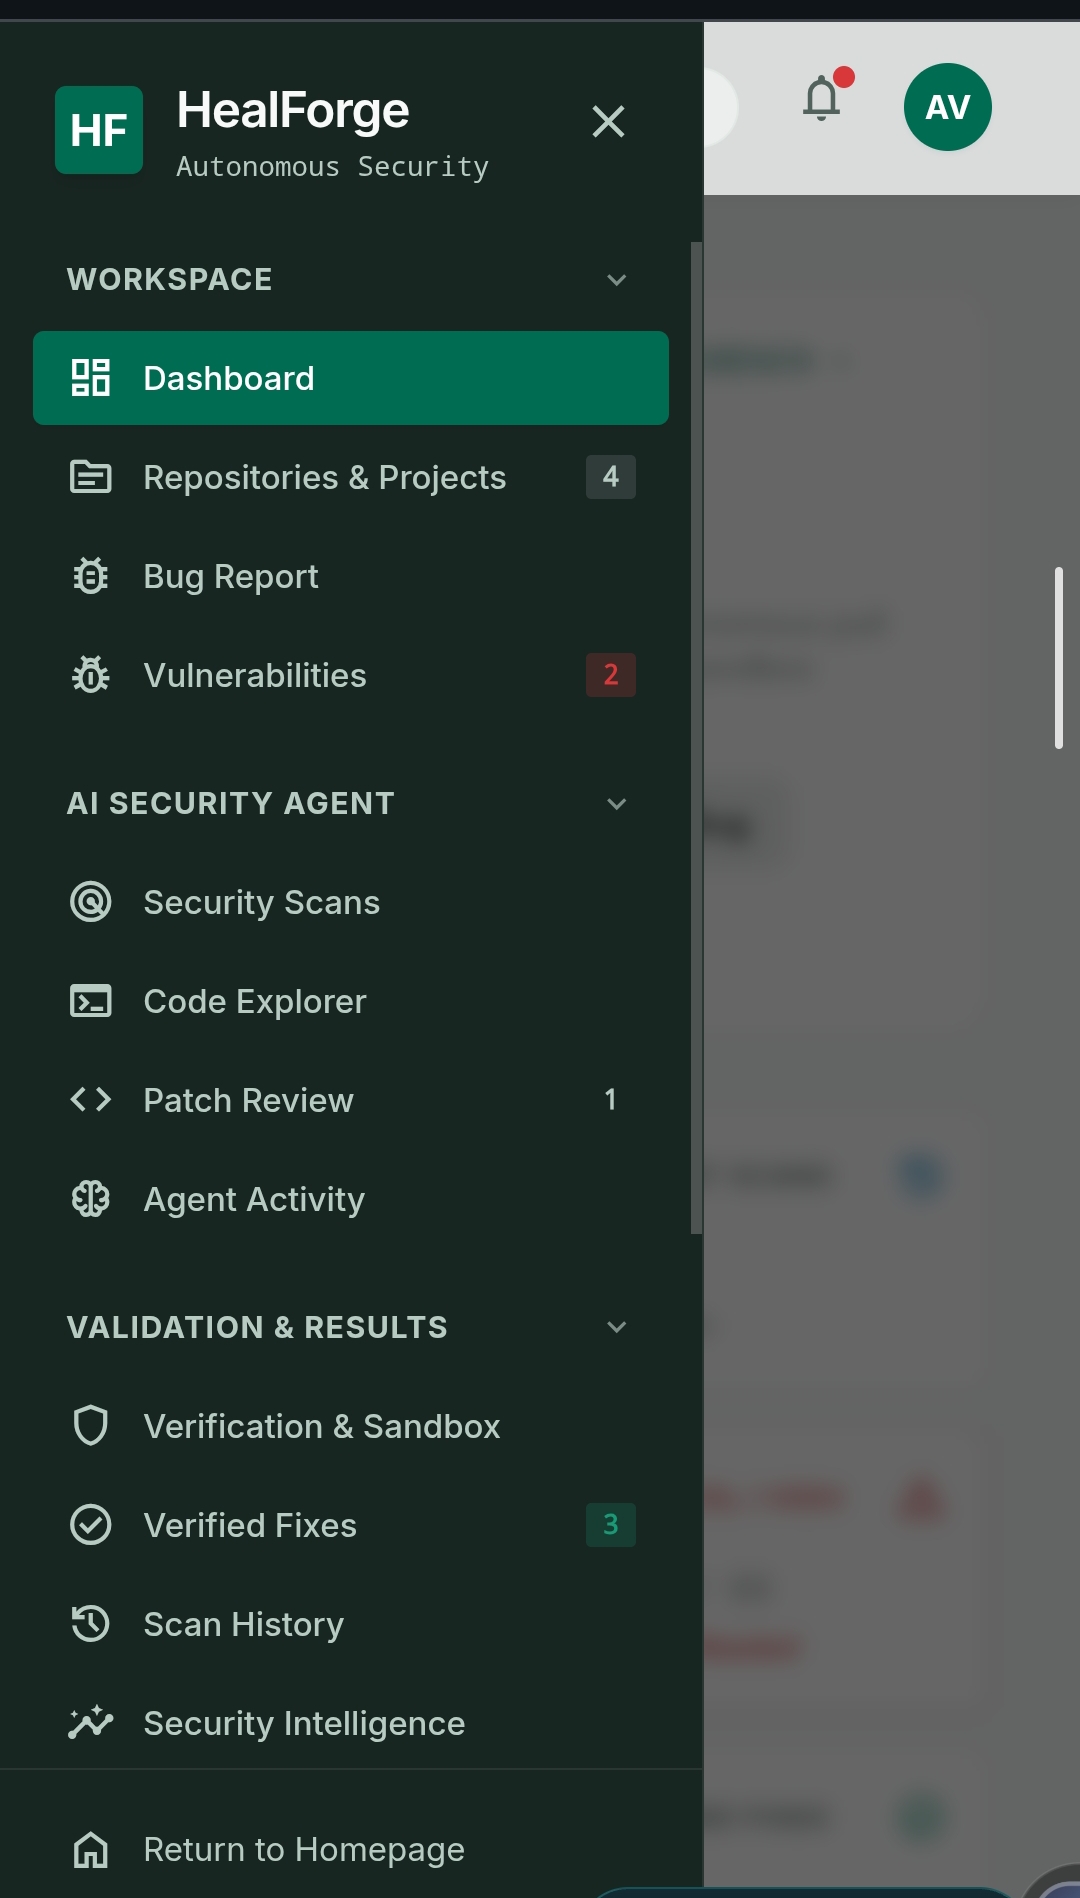
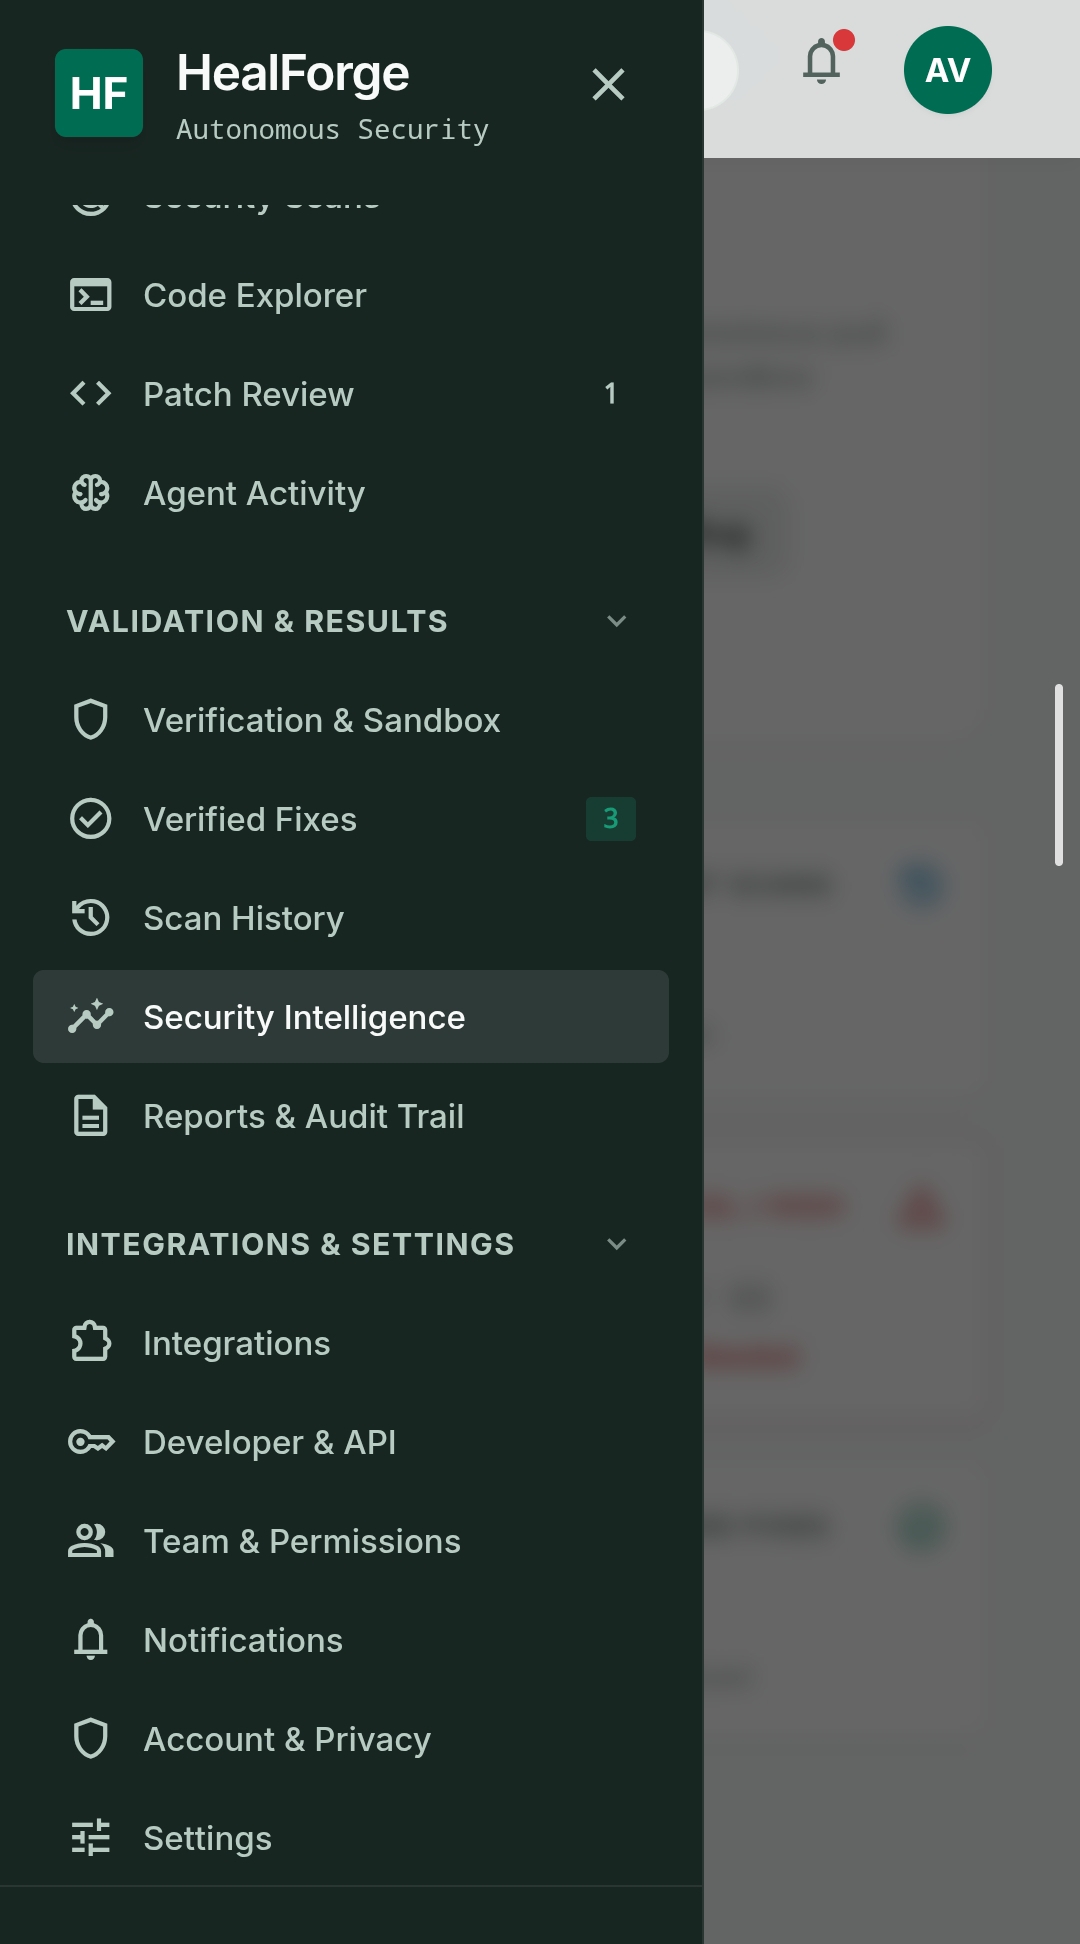
HealForge is a full-stack security workbench for source projects. Developers can create a project, import a ZIP archive, and run scans against the imported revision. The platform includes static code checks, secret and token detection, dependency checks against a limited local advisory set, and static checks for Docker and Compose configuration.
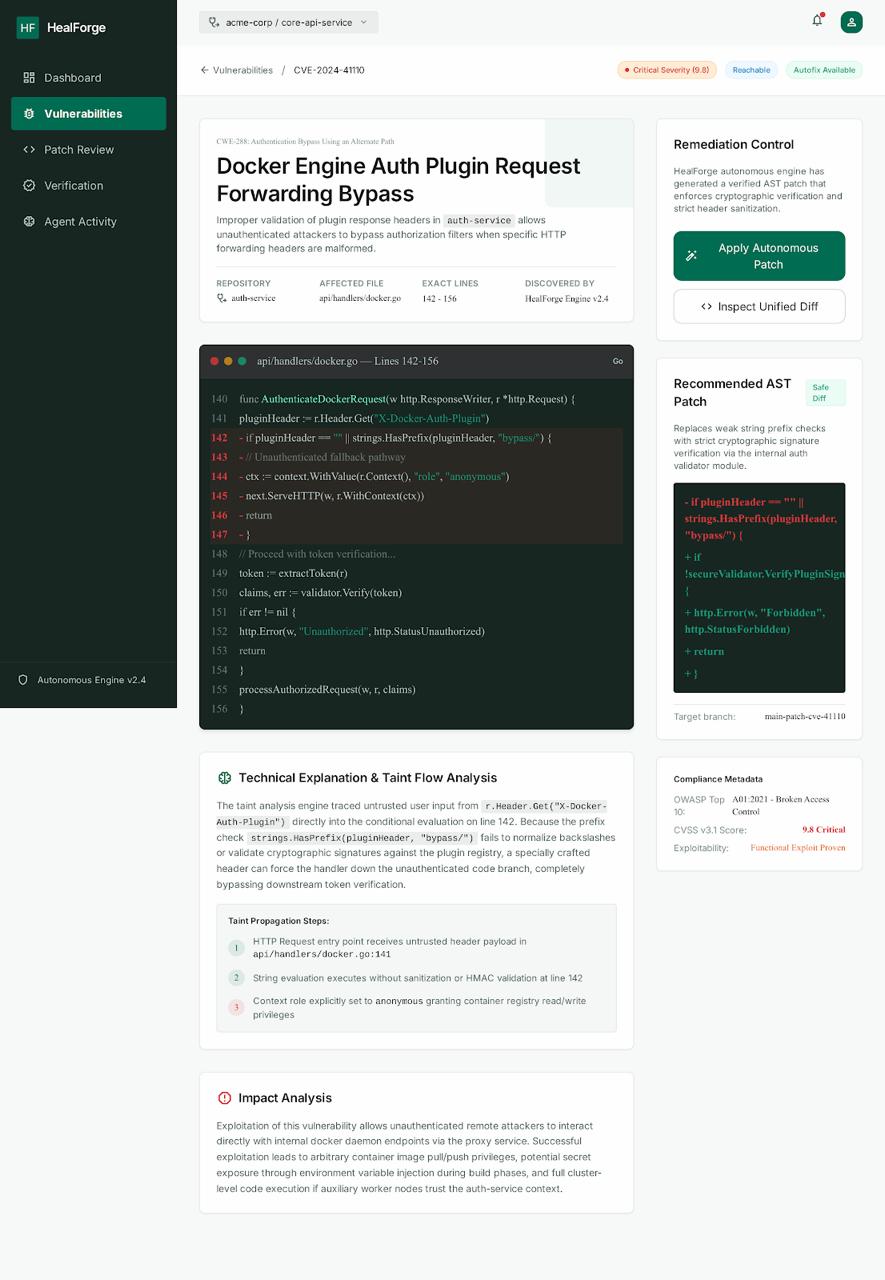
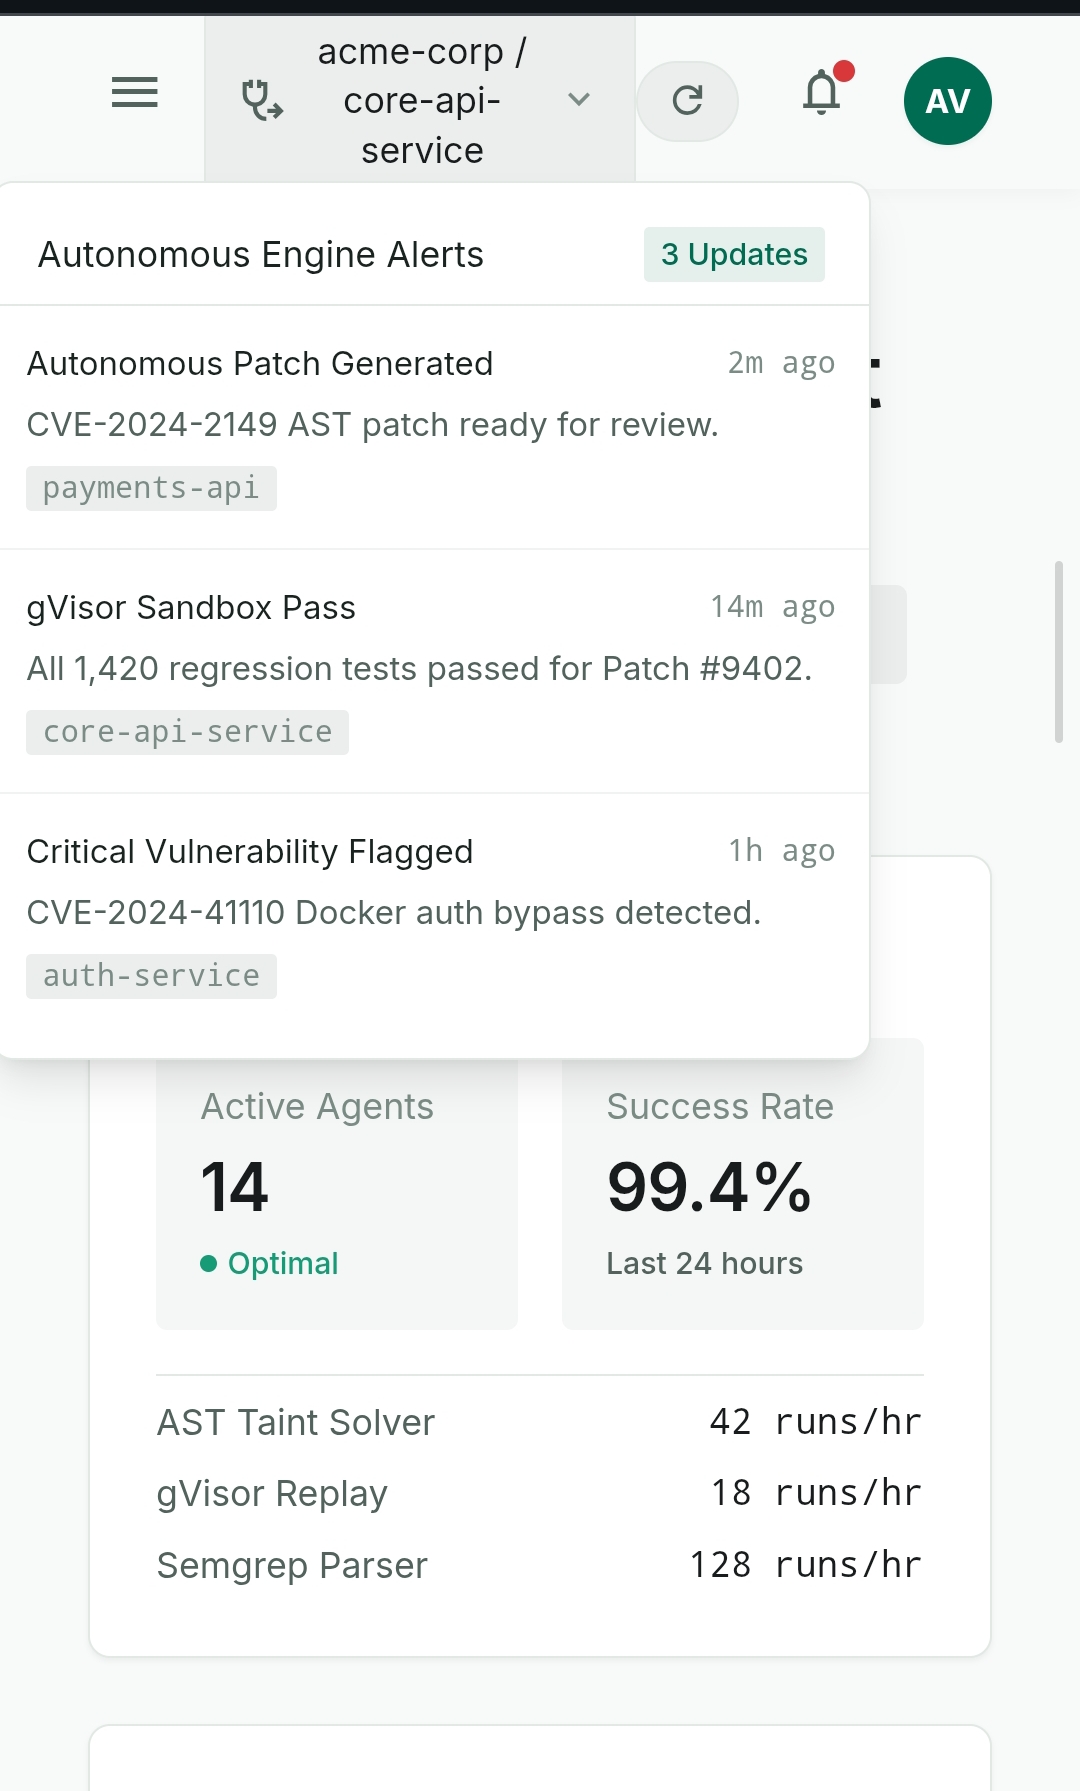
Findings are presented with security context such as severity and CWE mapping, helping developers review potential risks and decide what to address next. Uploaded source is analyzed statically and is not executed during import.
How we built it
HealForge uses a React, TypeScript, and Vite frontend with a Python and FastAPI backend. The backend provides the project, source-import, scan, and findings workflows, while database migrations support the application’s evolving data model.
We focused on making the workflow understandable: import a project, select a revision, run an analysis, and review the results in the workbench.
Challenges we faced
One challenge was building a useful security workflow while keeping the system honest about what its analysis can and cannot detect. Static rules can identify selected patterns, but they are not a replacement for a comprehensive commercial scanner or a guarantee that code is vulnerability-free. Dependency checks use a limited local advisory set rather than a live, continuously updated vulnerability database.
Another challenge was handling uploaded archives safely. The import flow is designed to reject unsafe archive structures and store supported text source files for analysis, rather than executing uploaded code.
What we learned
We learned that a security product needs more than a polished dashboard: it needs clear evidence, safe handling of untrusted source, useful findings, and transparent limitations. HealForge is a step toward making security review more accessible within a developer’s project workflow.
Built With
- alembic
- analysis
- cybersecurity
- docker
- fastapi
- postgresql
- python
- react
- sqlalchemy
- sqlite
- static
- typescript
- vite

Log in or sign up for Devpost to join the conversation.