Inspiration
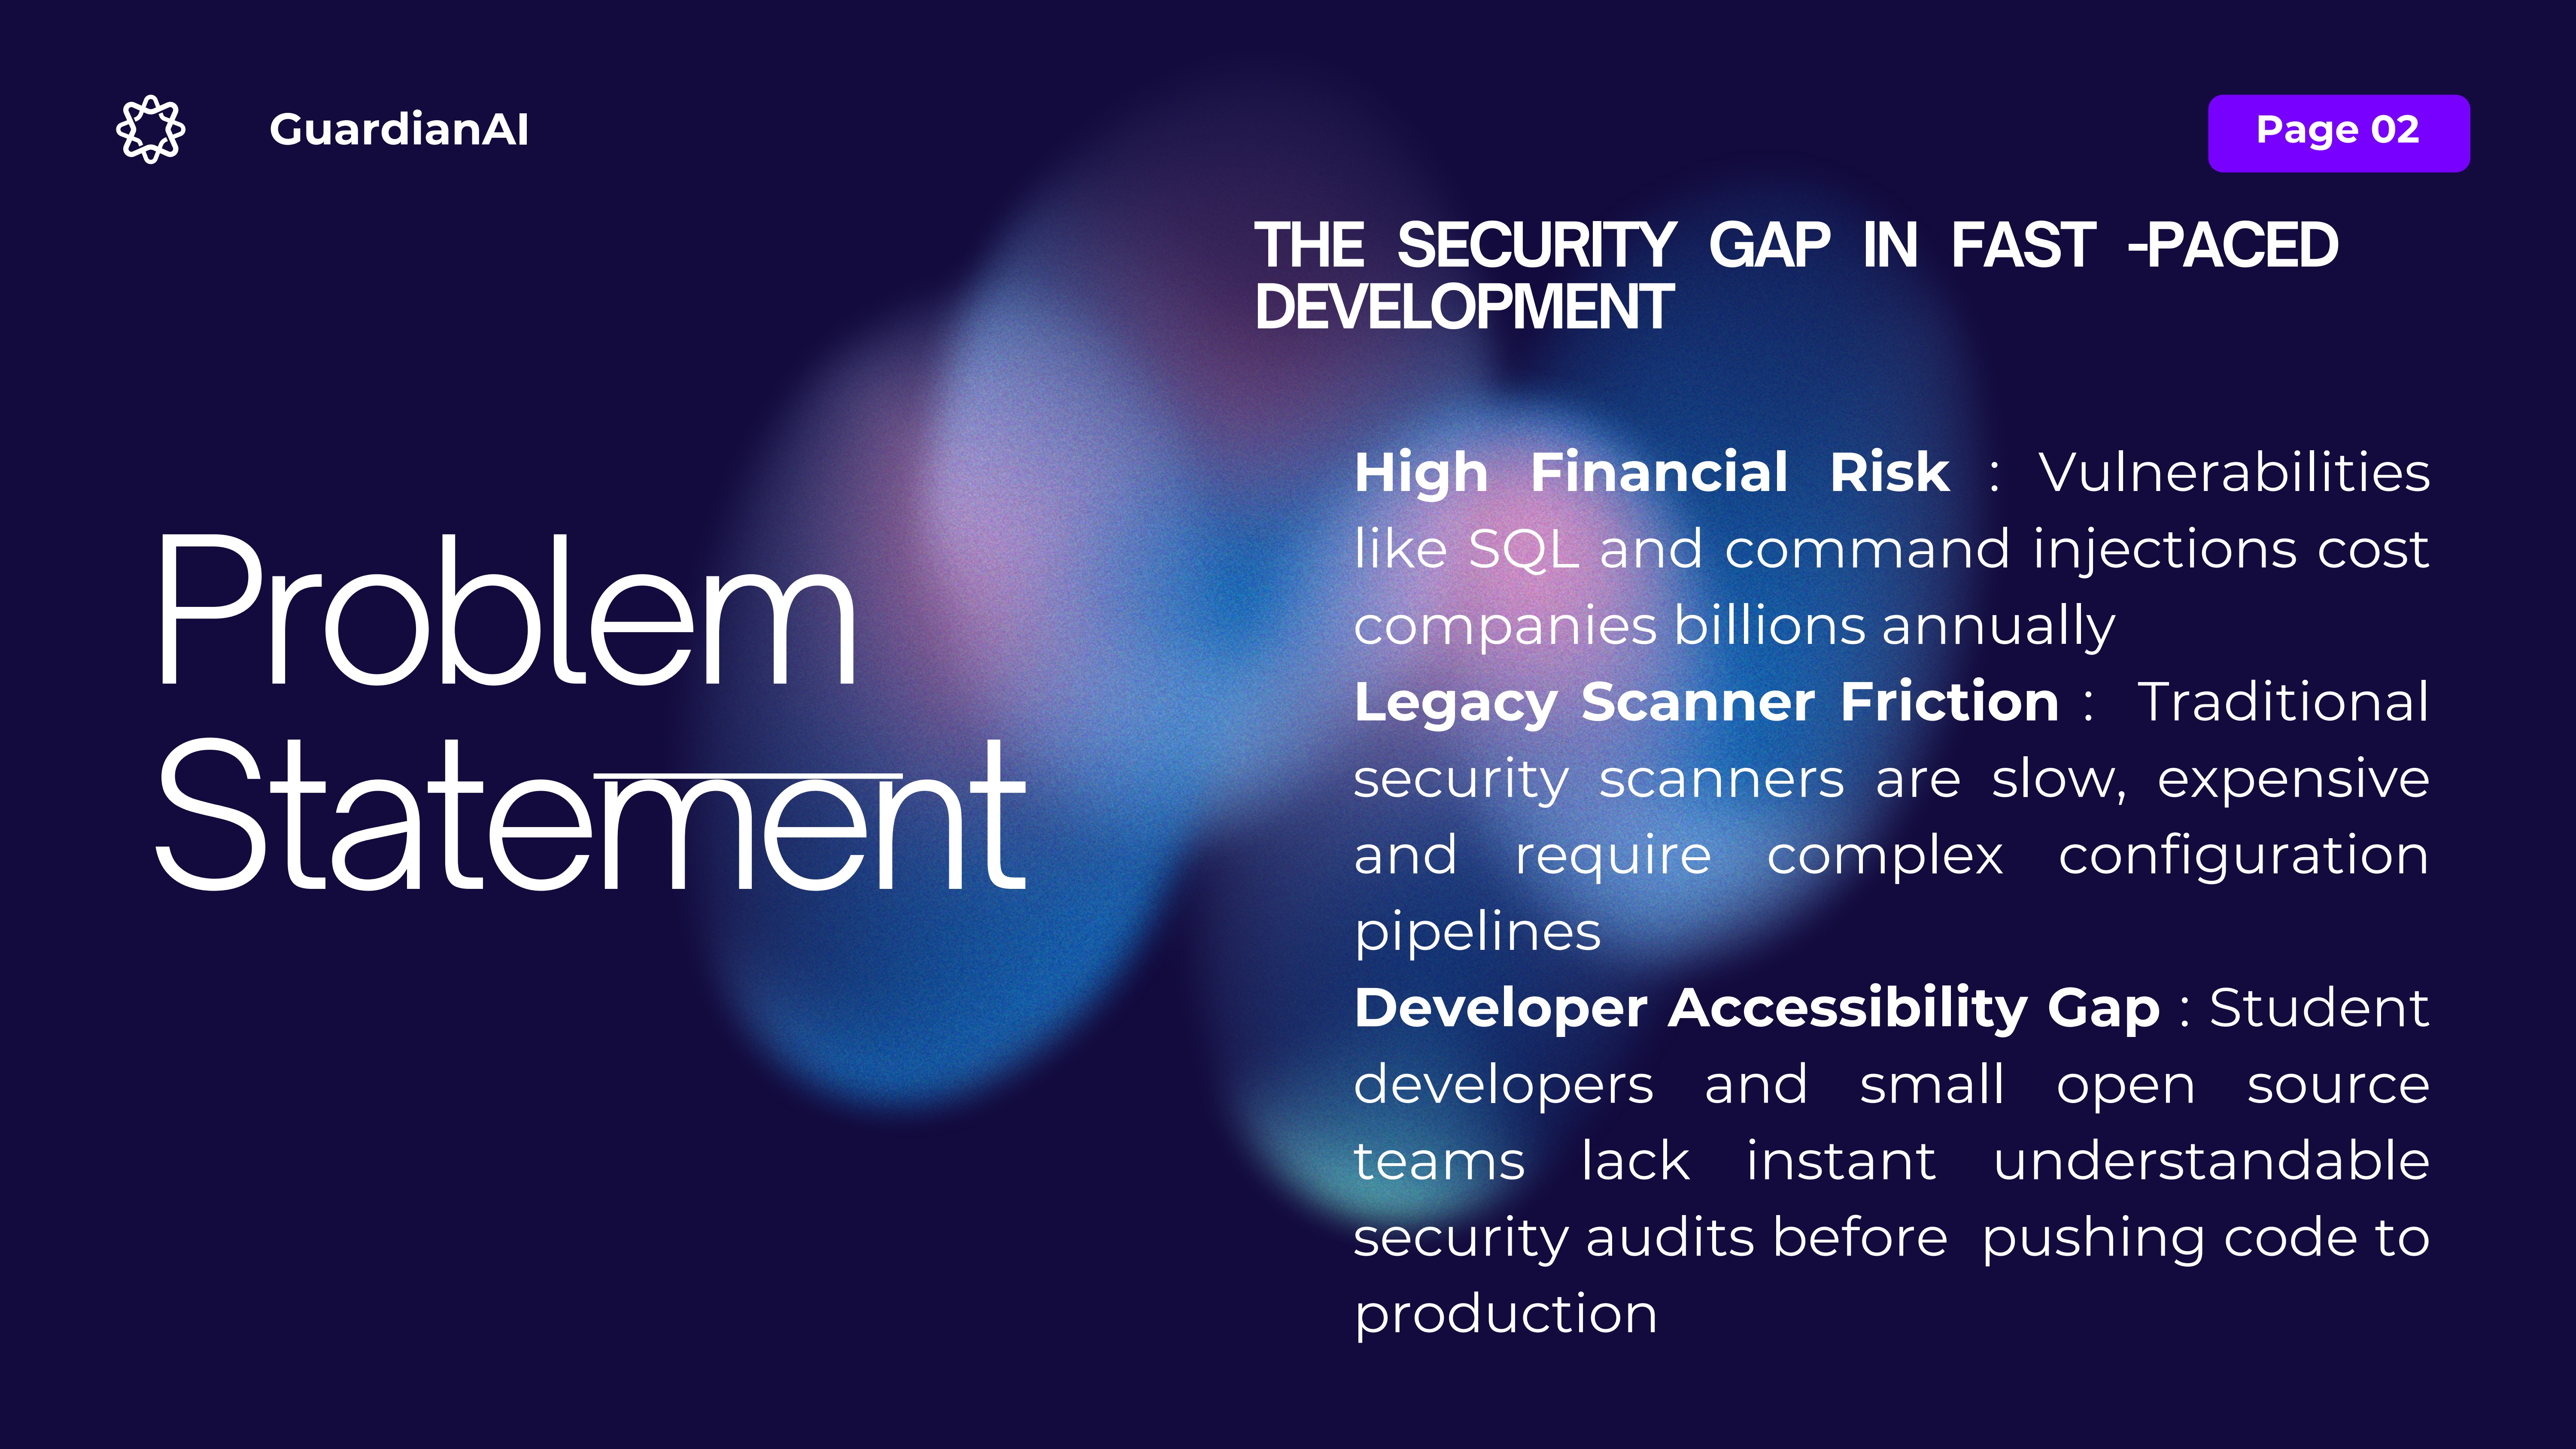
Modern software development moves fast, but security is often an afterthought in traditional CI/CD workflows. We built GUARDIAN-AI-DevSecOps to bridge the gap between development speed and security enforcement by embedding AI-driven security checks directly into the DevSecOps pipeline.
What it does
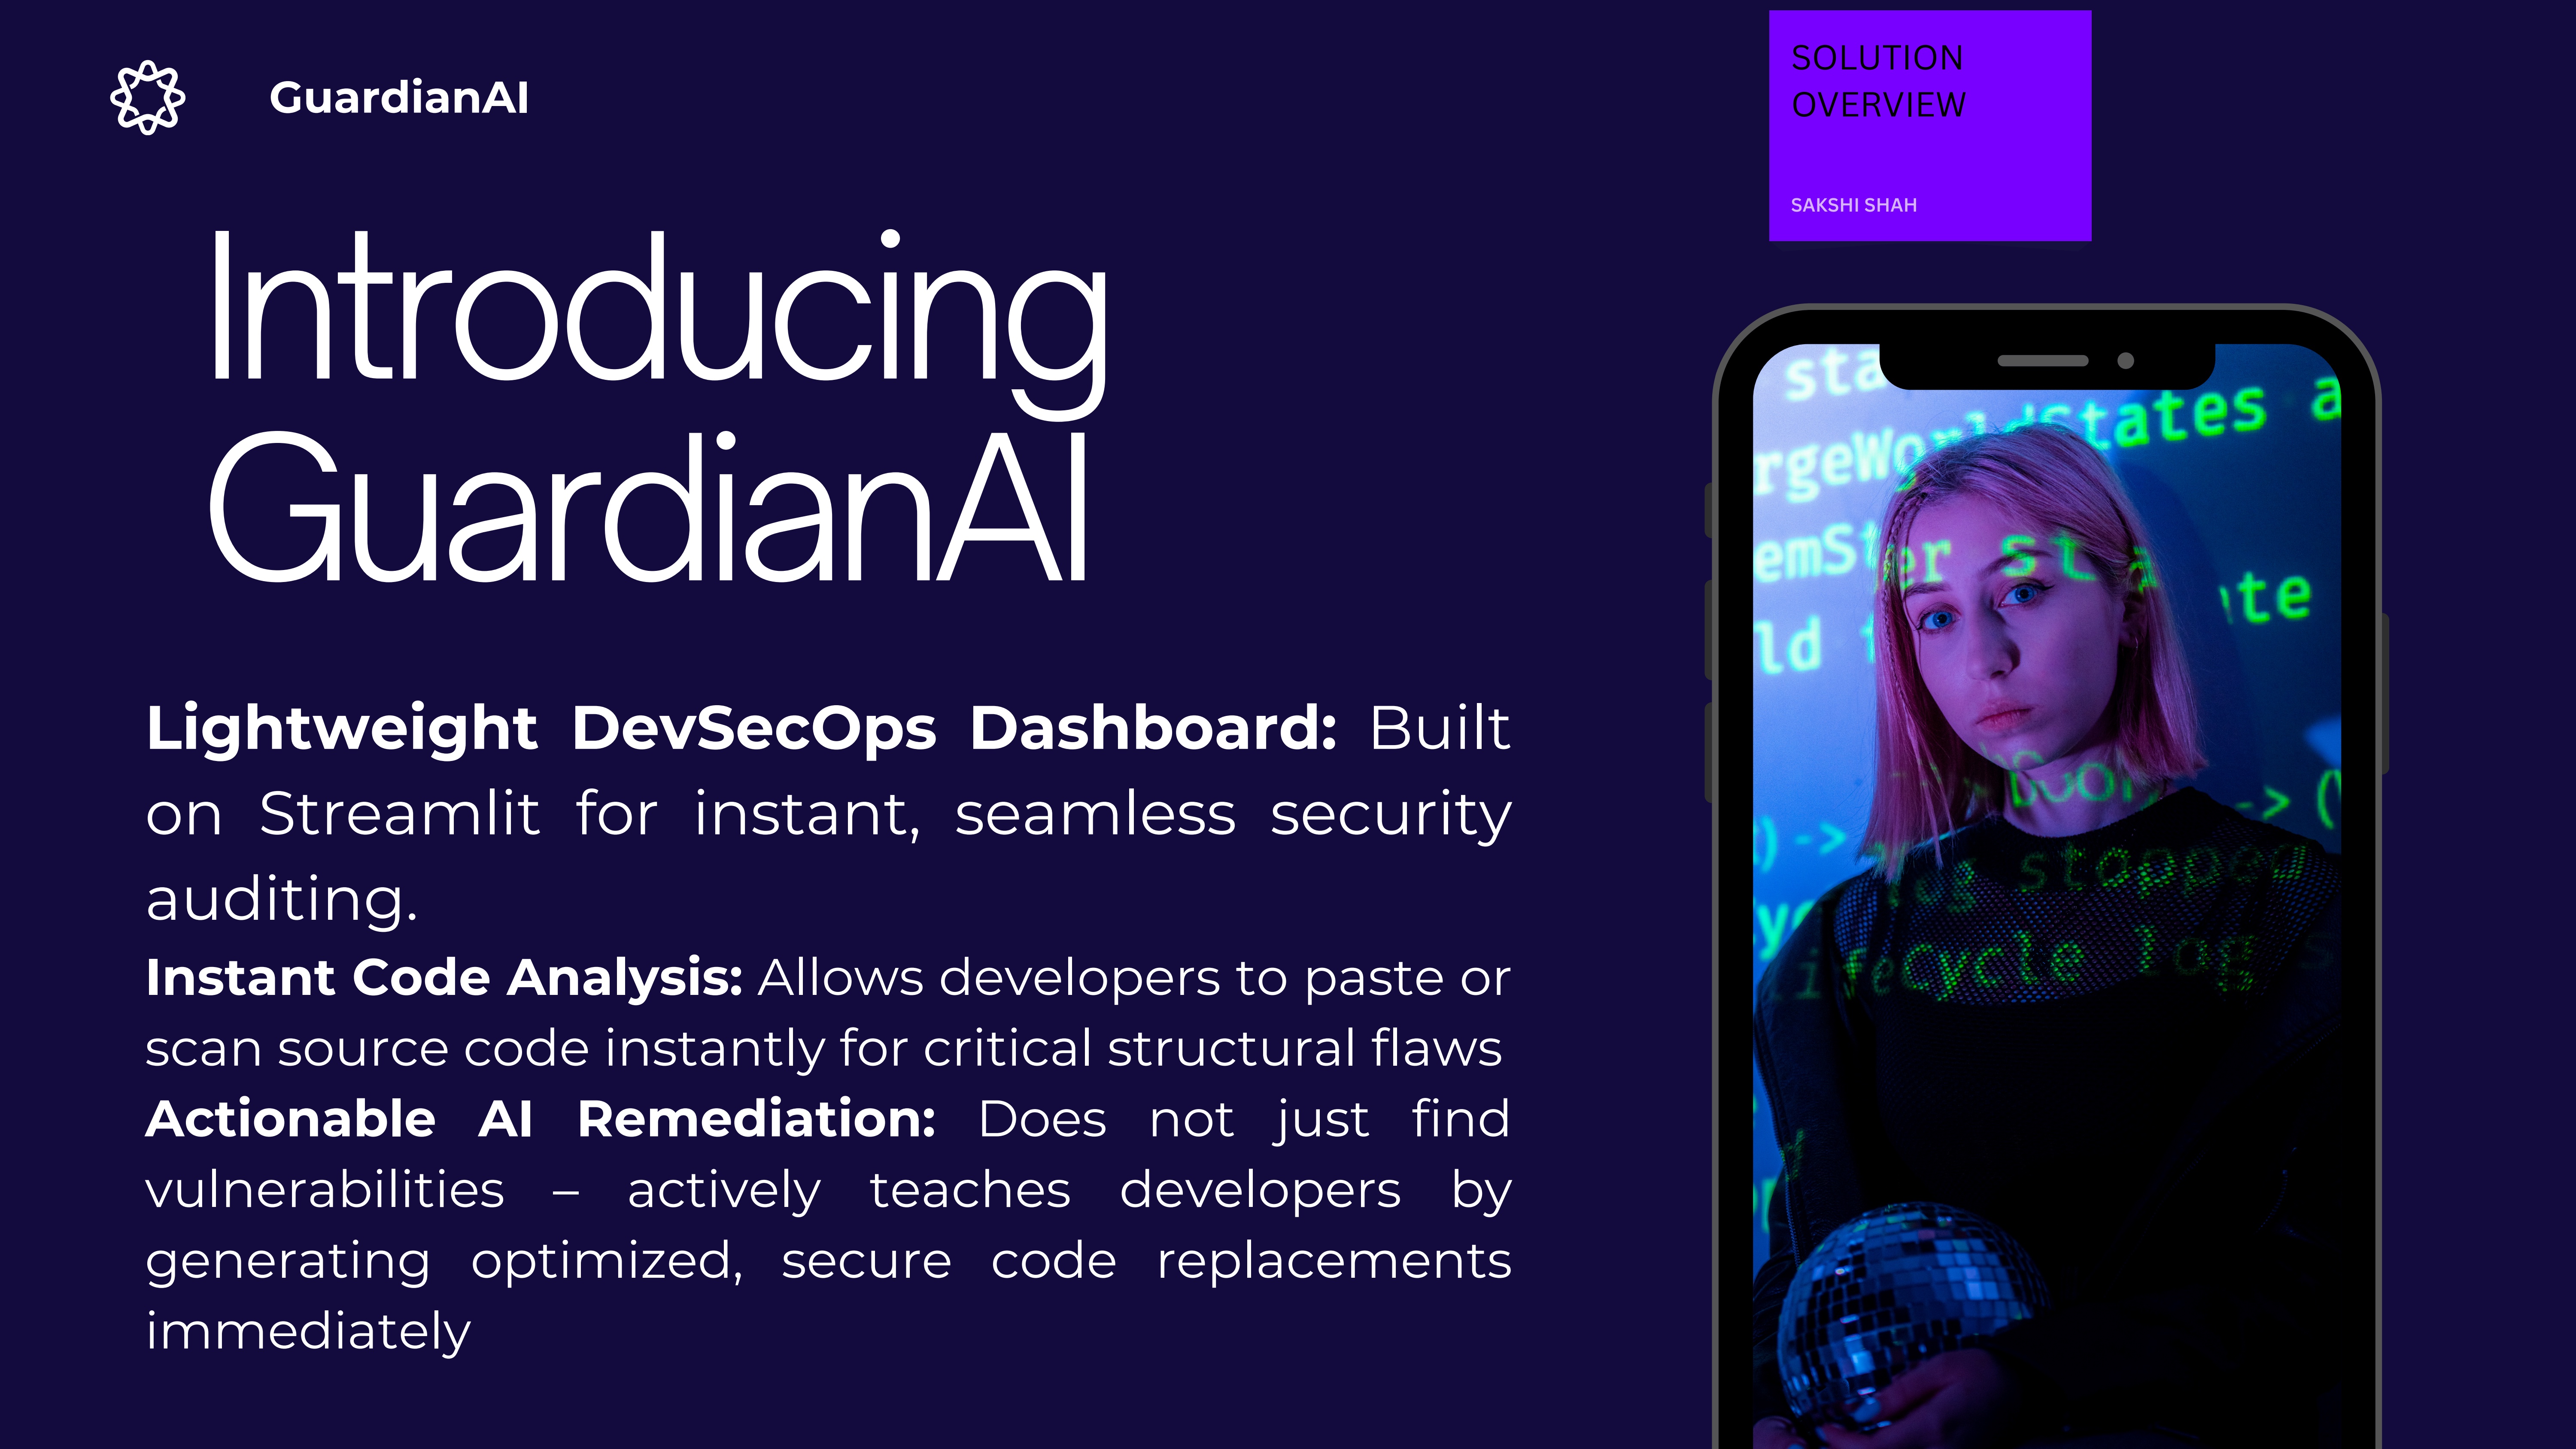
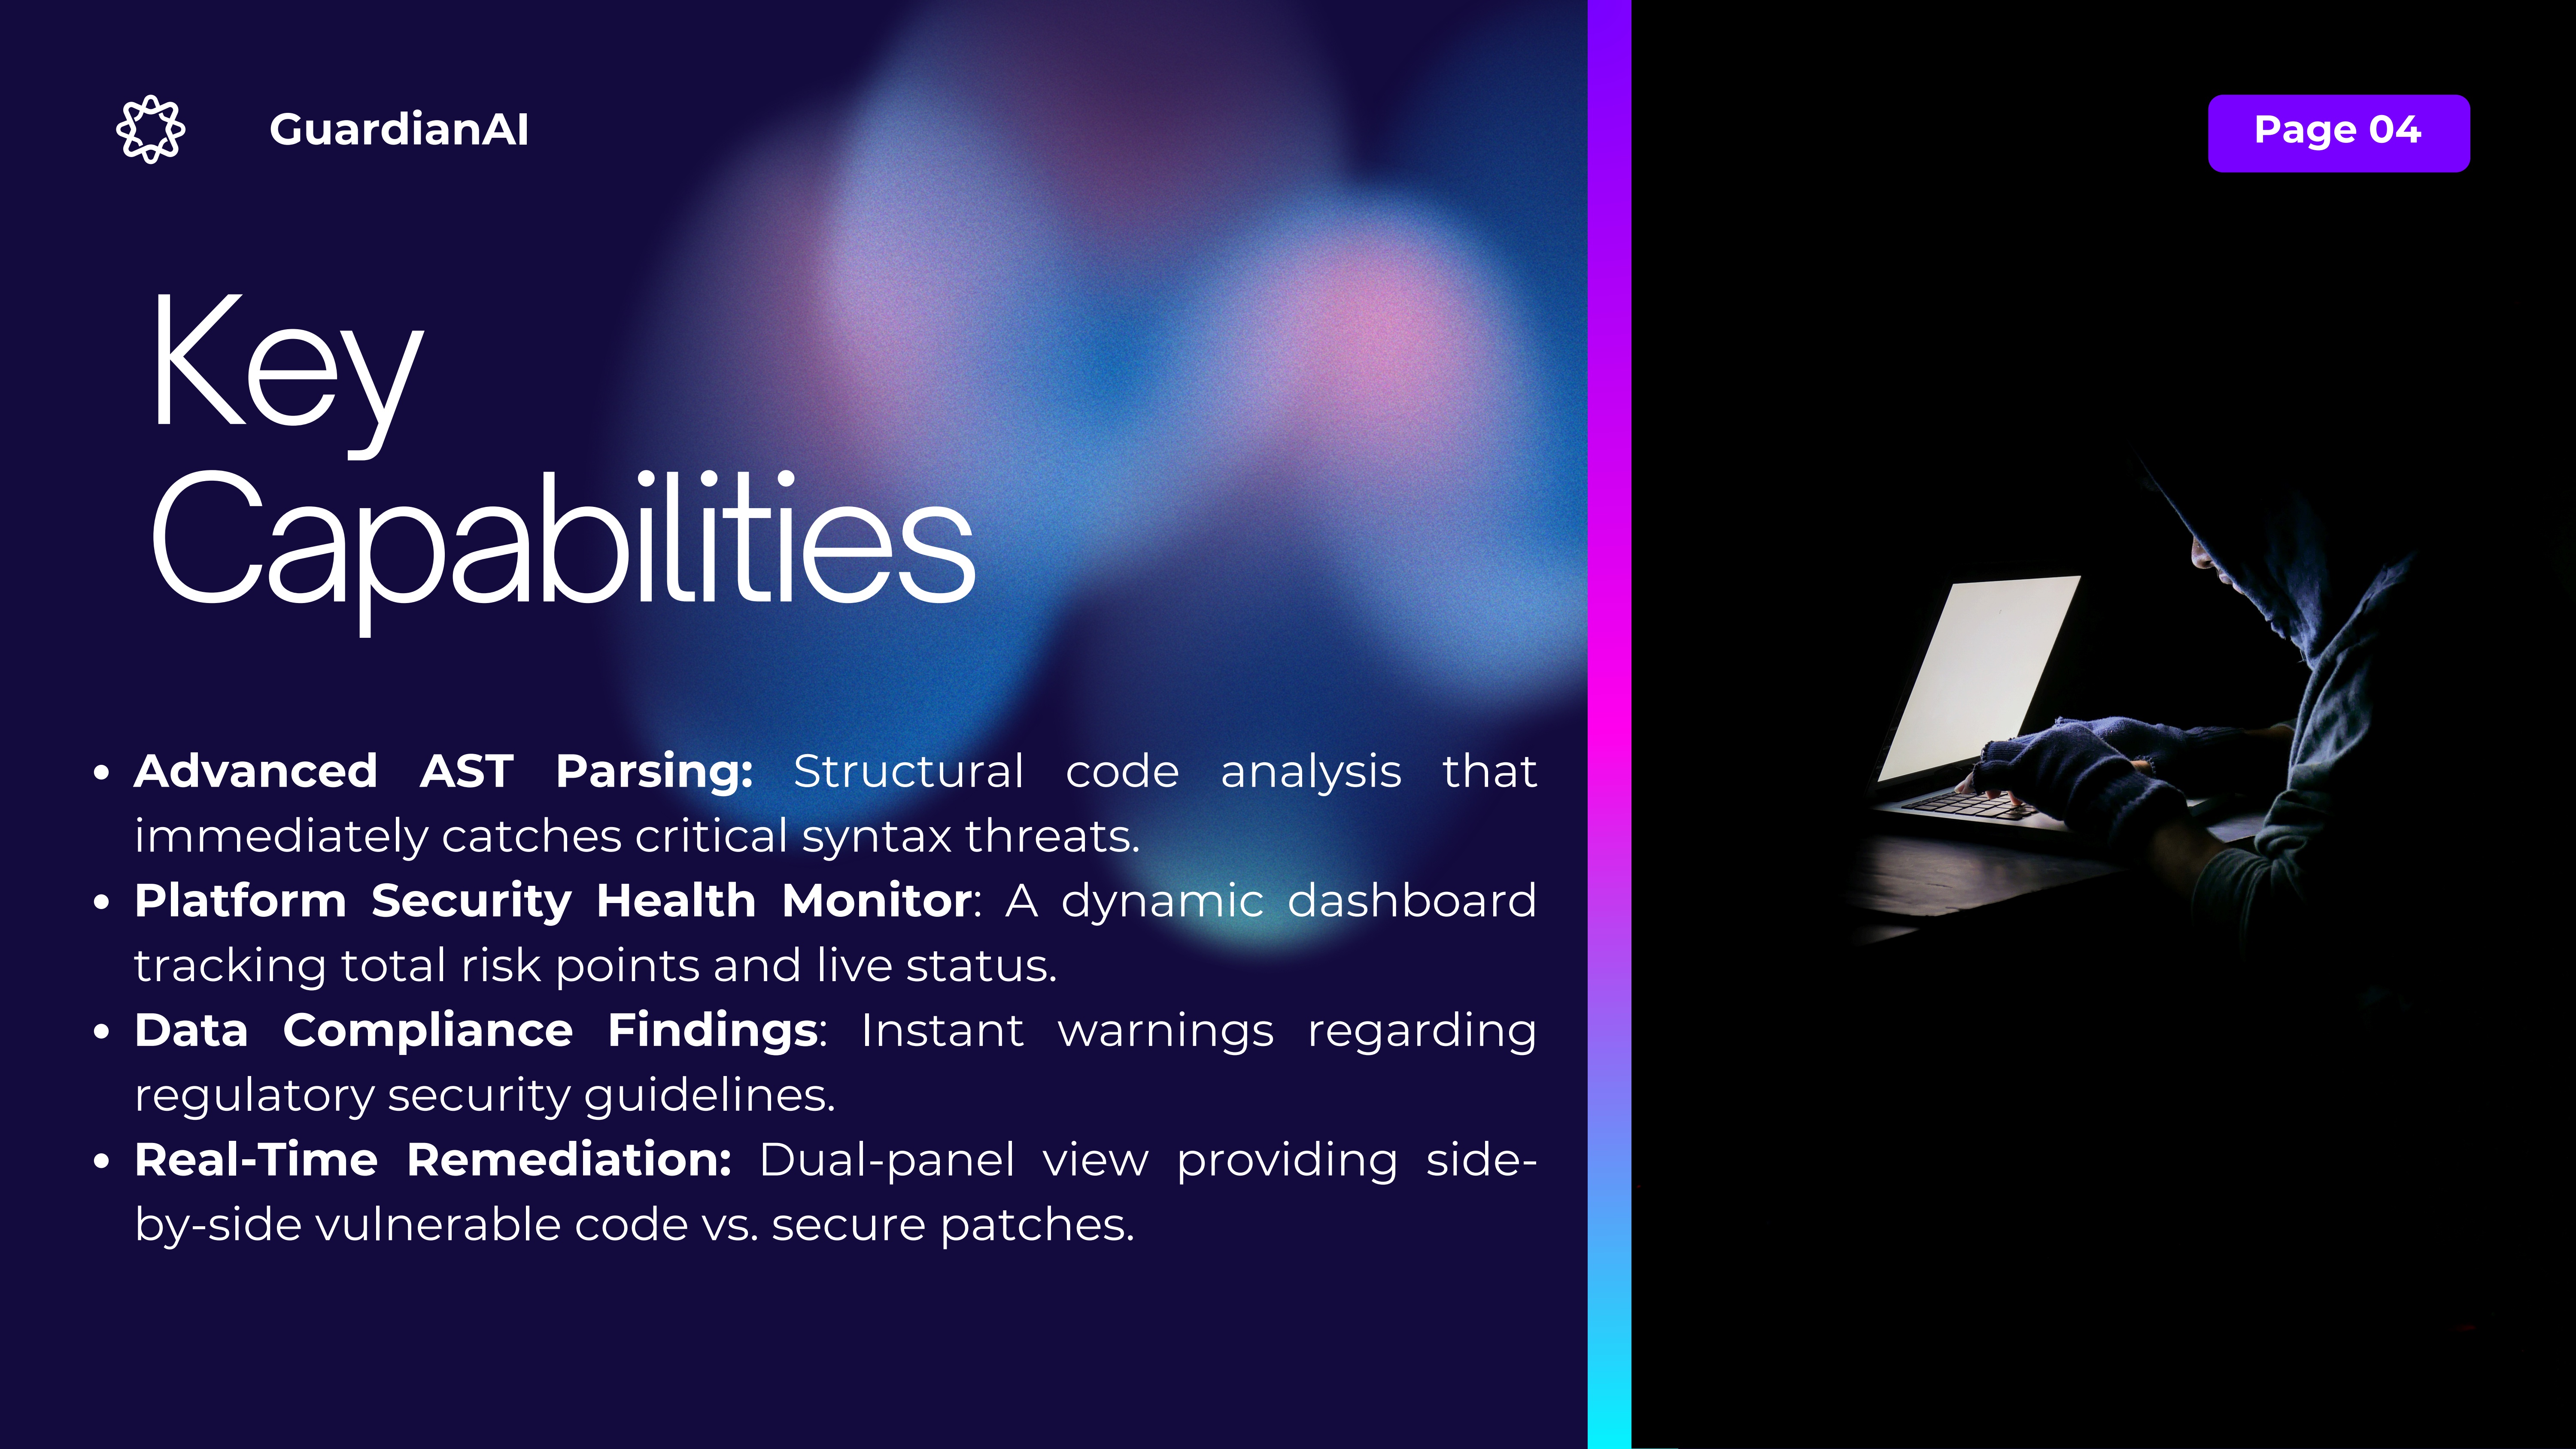
GUARDIAN-AI-DevSecOps is an automated, secure CI/CD pipeline designed to protect applications throughout their lifecycle. Key features include:
- Automated Security Scanning: SAST/DAST and dependency checks to identify vulnerabilities early.
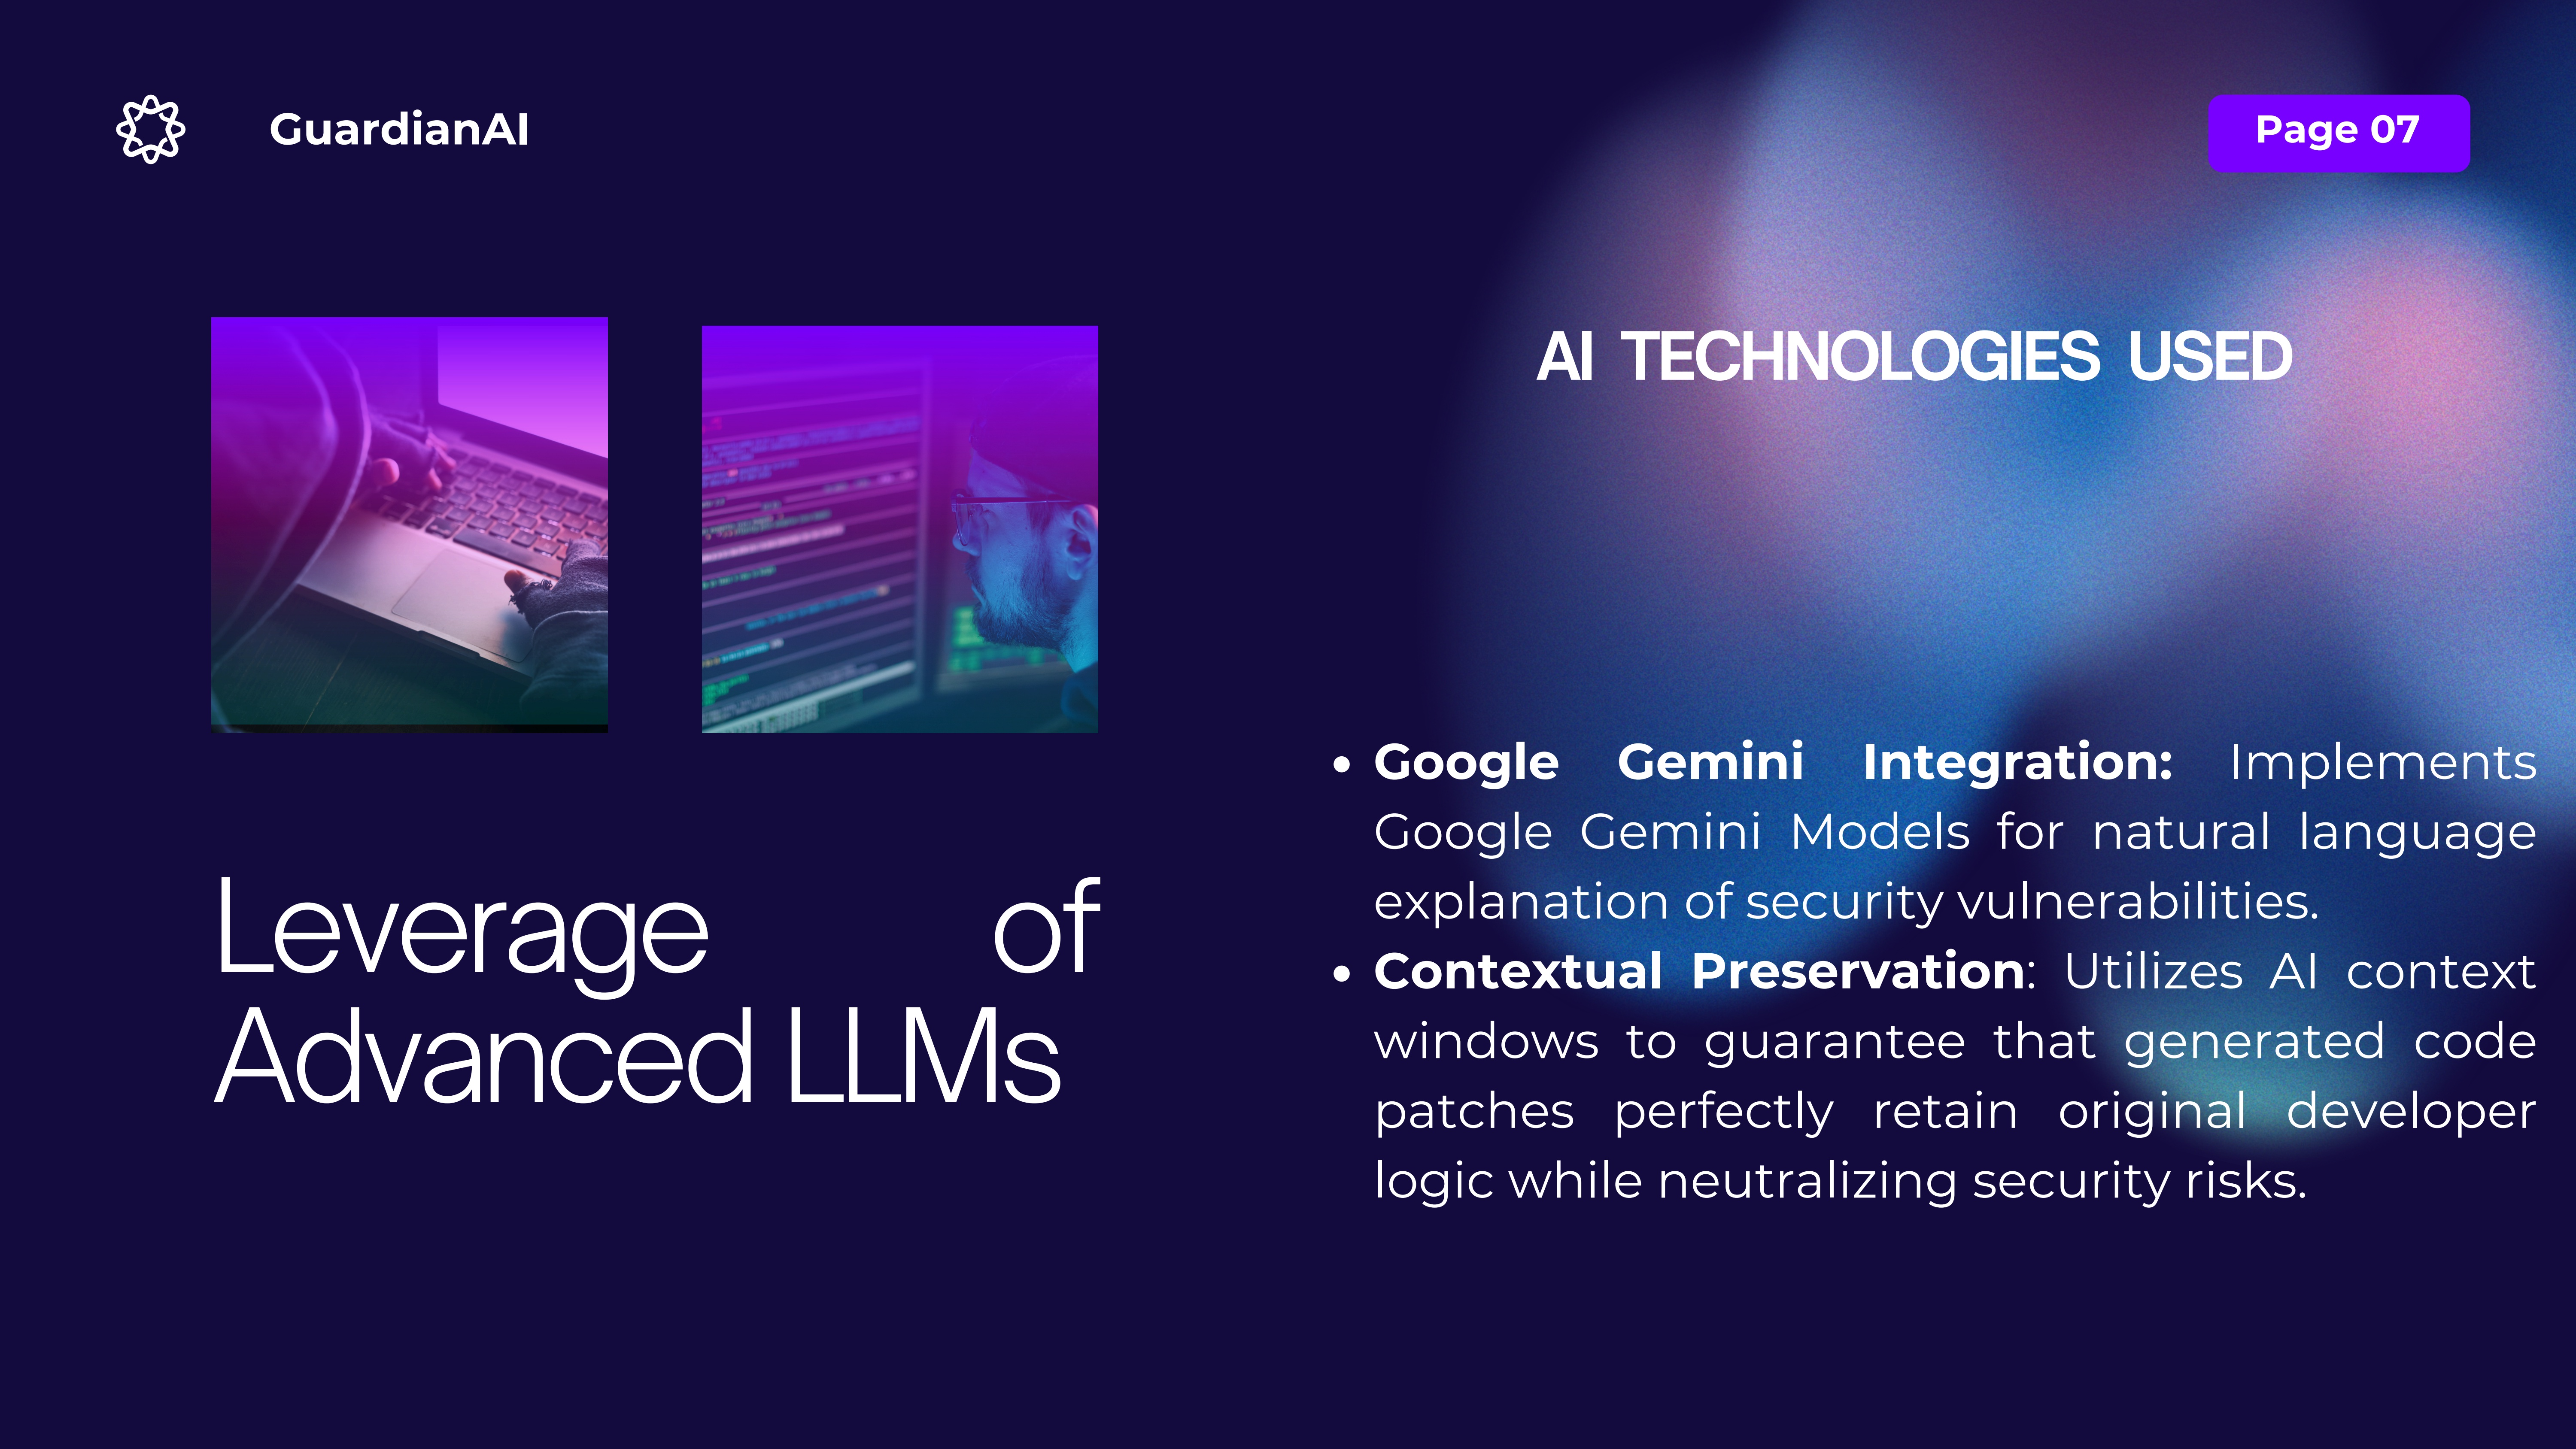
- AI Security Analytics: Intelligent log analysis and automated threat triage using AI/ML models.
- Pipeline Integration: Seamless integration with containerized applications and deployment environments.
How we built it
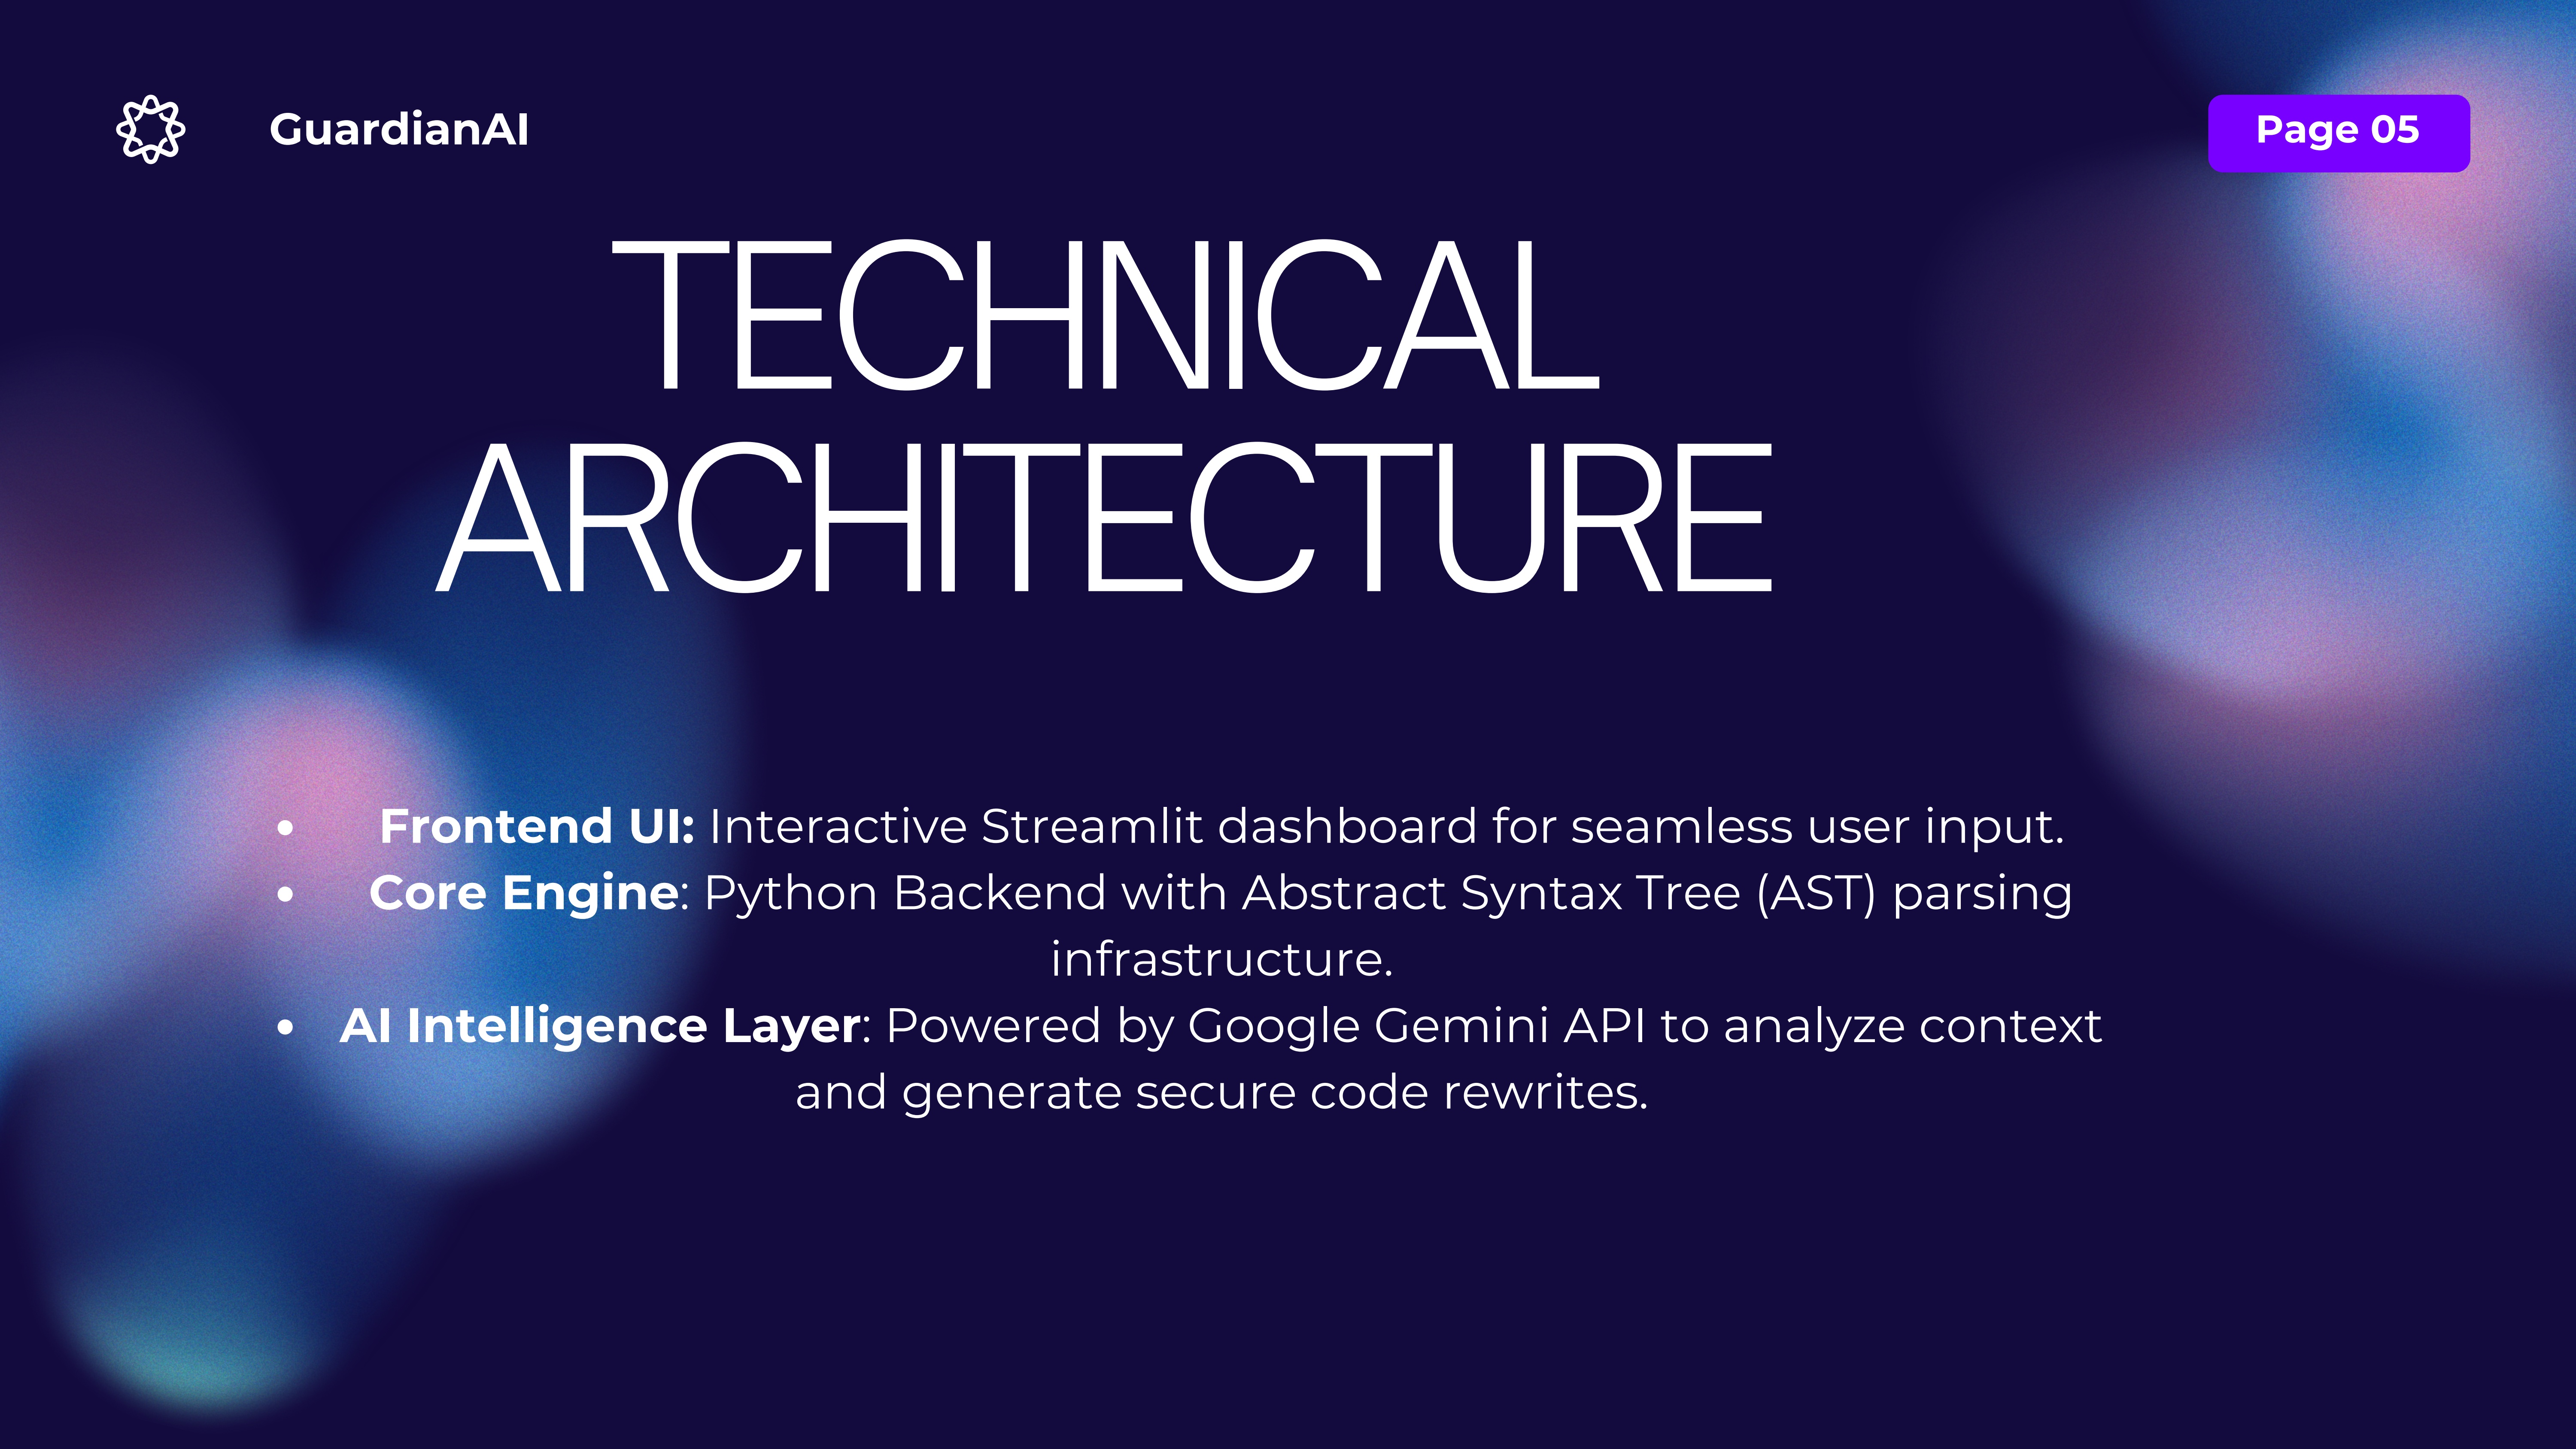
- DevOps & Infrastructure: Docker, Kubernetes, and GitHub Actions for continuous integration and delivery.
- Security Tooling: SonarQube, Trivy, and OWASP ZAP integrated into the pipeline workflow.
- Core Stack: Python and FastAPI to orchestrate security workflows and AI model predictions.
Challenges we ran into
- Managing pipeline execution speed without sacrificing deep security analysis.
- Fine-tuning AI insights to reduce false positives in automated security logs.
What's next for GUARDIAN-AI-DevSecOps
- Expanding support for multi-cloud deployments.
- Implementing automated self-healing patches for common security vulnerabilities.
