-
-
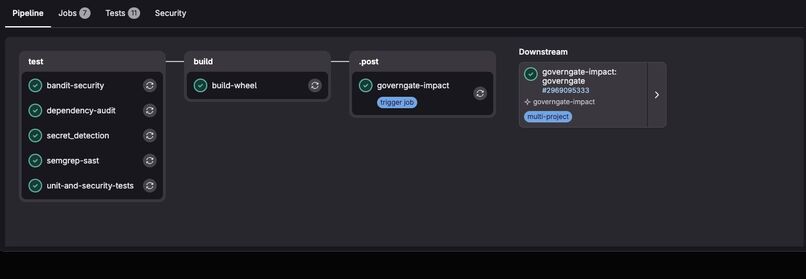
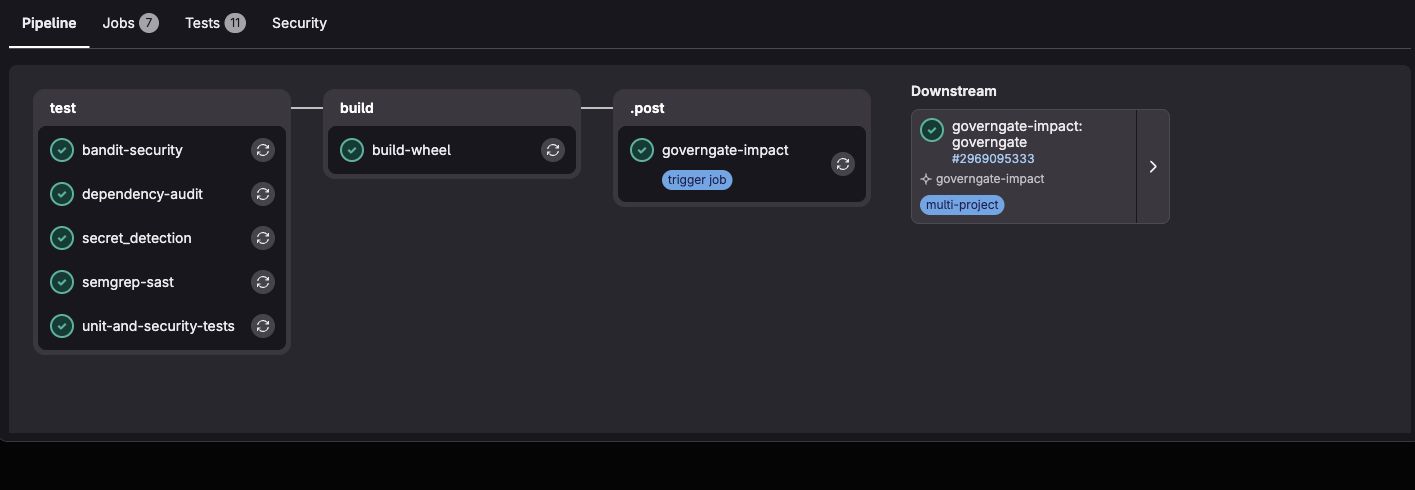
Passing SDK pipeline
-
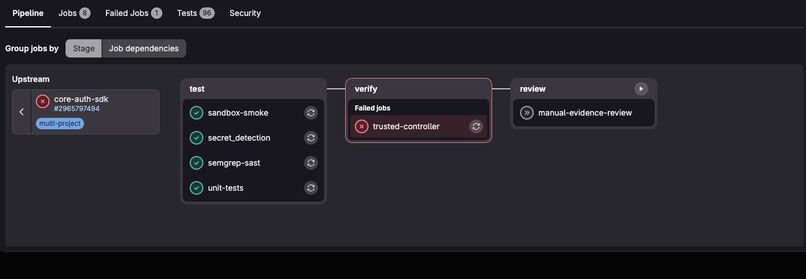
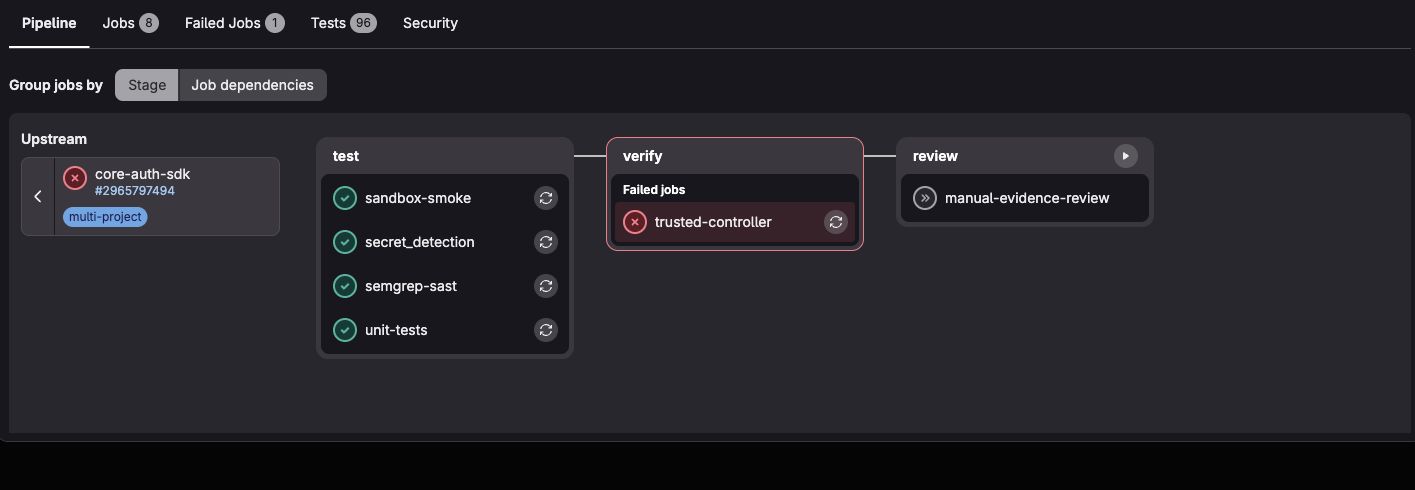
Breaking change blocked
-
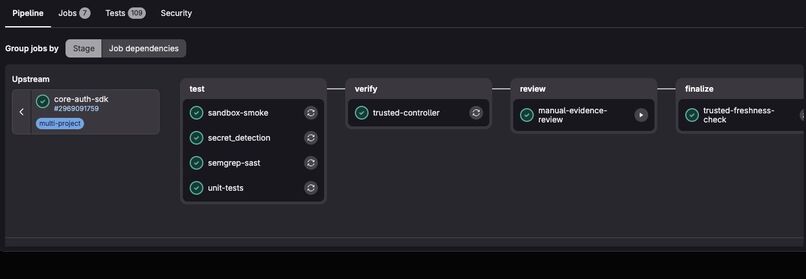
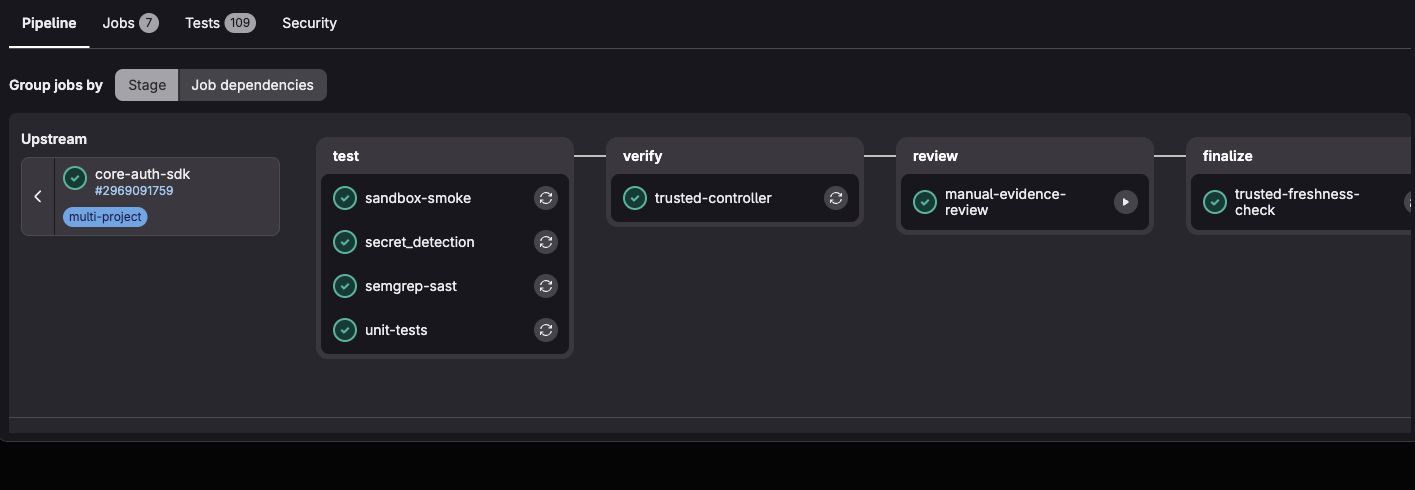
Completed manual review and freshness check
-
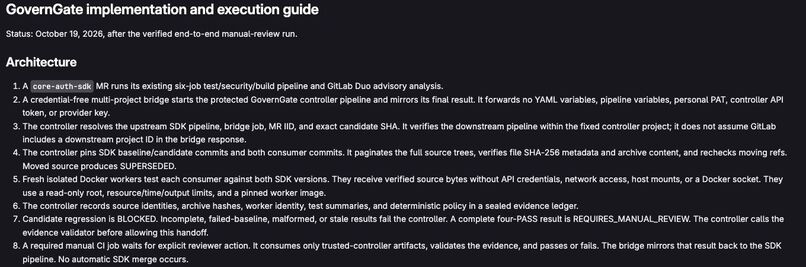
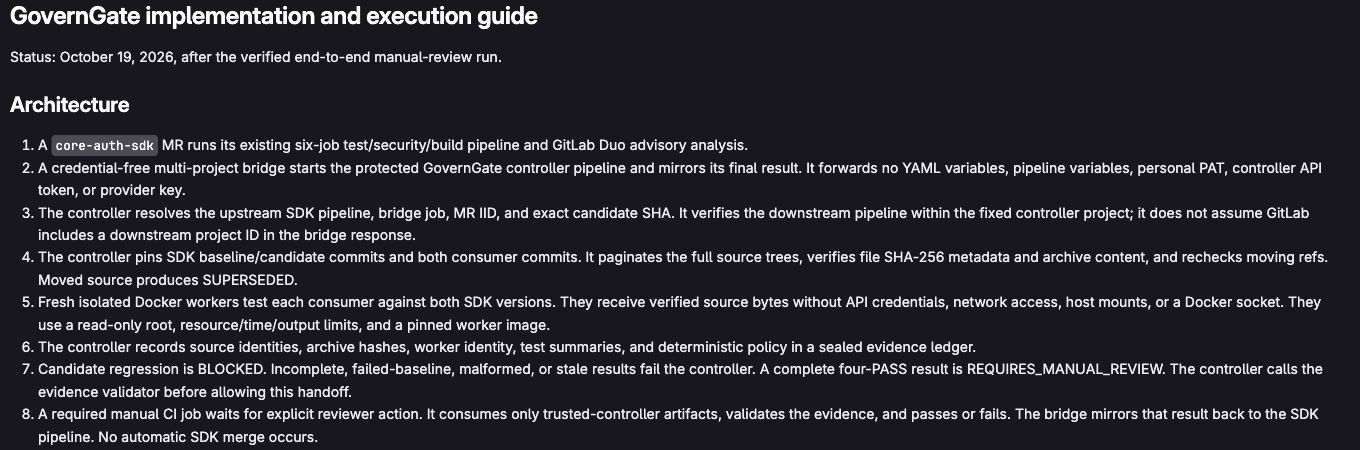
Architecture overview
GovernGate: Autonomous Release Governance
GovernGate checks whether a change to a shared SDK breaks the services that depend on it, then gives a reviewer traceable evidence before release. A green SDK build alone cannot show that downstream consumers still work.
What it does
For each SDK merge request, GitLab Duo provides advisory impact analysis. GitLab CI/CD runs the SDK checks and launches a trusted controller through a credential-free bridge. The controller verifies pipeline and commit identities, pins the SDK and consumer revisions, and runs Billing and Notification against both the baseline and candidate SDK in isolated workers. A deterministic policy blocks regressions or missing evidence. Passing evidence still requires explicit manual review; GovernGate never merges code automatically.
Architecture and security
The operational implementation spans four GitLab projects: governgate, core-auth-sdk, billing-service, and notification-service. The protected controller validates the upstream merge request, commit, pipeline, and downstream job identities. Workers use verified source bytes and run without network access, API credentials, host mounts, signing keys, or a Docker socket, with resource and output limits. The evidence ledger records source hashes and test summaries. Its SHA-256 digest is unkeyed, so it checks consistency rather than independently proving authorship; candidate tests can forge their own reports. That limitation is why passing results remain review-gated.
Verified end-to-end runs
The positive case is SDK MR !6. The SDK pipeline passed, the bridge reached the GovernGate controller, both consumers passed against the pinned candidate, and the manual evidence-review job passed. SDK pipeline · GovernGate pipeline · manual review job.
The negative case is SDK MR !1. Its SDK checks passed, but the bridge/controller blocked release because Billing passed with the baseline and failed with the candidate; Notification passed both runs. SDK pipeline · GovernGate pipeline · trusted-controller job.
Public demo and reproduction
The public MIT-licensed GitLab repository contains source, tests, setup instructions, public CI history, and a demo with captured evidence and policy simulation. That demo does not make live API calls or perform approvals. The operational controller and service projects remain private, so the public repository can reproduce its own checks but cannot rerun the private multi-project workflow without group access. The GitLab run links above show the live operational evidence.
What we learned
A baseline failure must not be confused with a candidate regression, and a candidate’s own test report cannot be treated as independent proof. GovernGate checks both versions, pins identities, fails closed on incomplete evidence, and keeps a human review step. Independent result attestation is future hardening. Nebius/Nemotron, Tavily, and Google Cloud are not part of the verified running flow.

Log in or sign up for Devpost to join the conversation.