Inspiration
Writing code is only one part of software development. Developers still need to review changes, troubleshoot failing pipelines, investigate security findings, validate fixes, and prepare releases. We built GitLab Duo Sentinel to bring these scattered post-coding tasks into one structured workflow.
What it does
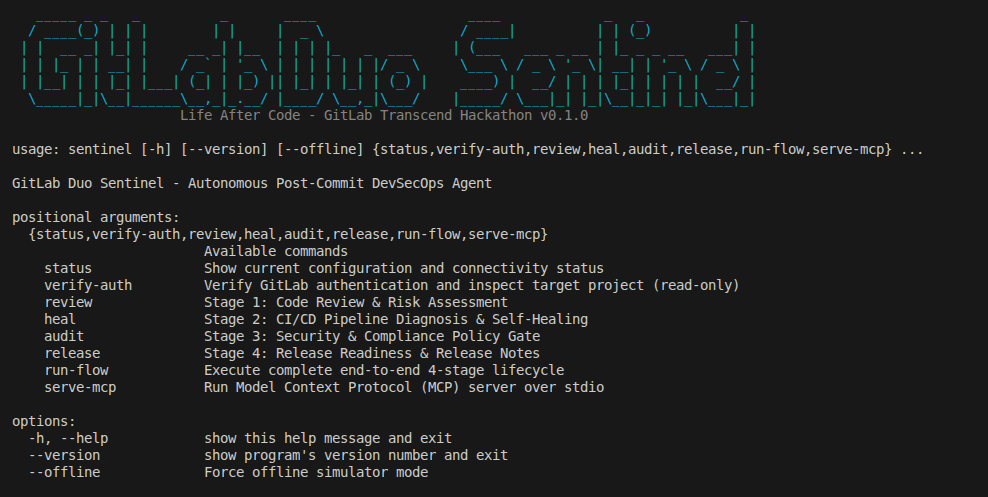
GitLab Duo Sentinel is a Python-based DevSecOps agent that helps developers review code, diagnose CI/CD failures, prepare and validate remediation patches, audit GitLab security reports, and assess release readiness. It provides a CLI, GitLab API integration, and an MCP server, with an emphasis on validation and human oversight.
How we built it
We built Sentinel in Python, integrating GitLab workflows with automated testing and security scanning. Its modular stages handle review, pipeline diagnosis and remediation, security auditing, and release preparation. We added configurable autonomy and safeguards to keep consequential actions controlled. GitLab CI/CD runs automated tests and SAST checks, while an offline demo makes the workflow reproducible.
Challenges we ran into
Integrating multiple DevSecOps stages while keeping the workflow safe and testable was challenging. GitLab CI also exposed packaging issues and a command-injection risk in shell-based test execution. We fixed package discovery and replaced shell-based command execution with argument-based execution. Getting the hosted pipeline green helped validate the configured checks.
Accomplishments that we're proud of
We brought code review, failure diagnosis, remediation validation, security auditing, and release readiness into one tool. Sentinel has automated tests, GitLab CI/CD integration, SAST scanning, and a reproducible demonstration. We're especially proud of addressing a security finding discovered during development rather than ignoring it.
What we learned
We learned that generating a fix is not enough. A useful DevSecOps agent must validate its changes, handle security findings deliberately, make its actions observable, and preserve human control over risky operations. We also learned how packaging, CI configuration, and security scanning fit together in a real delivery workflow.
What's next for GitLab Duo Sentinel
We plan to deepen live GitLab Duo Agent Platform orchestration, expand pipeline recovery scenarios, and improve integrations across the DevSecOps lifecycle. Our long-term goal is to help developers move from written code to tested, secure, release-ready software with less repetitive work.
Built With
- api
- ci/cd
- gitlab
- mcp
- pytest
- python
- rest
- semgrep

Log in or sign up for Devpost to join the conversation.