-
-
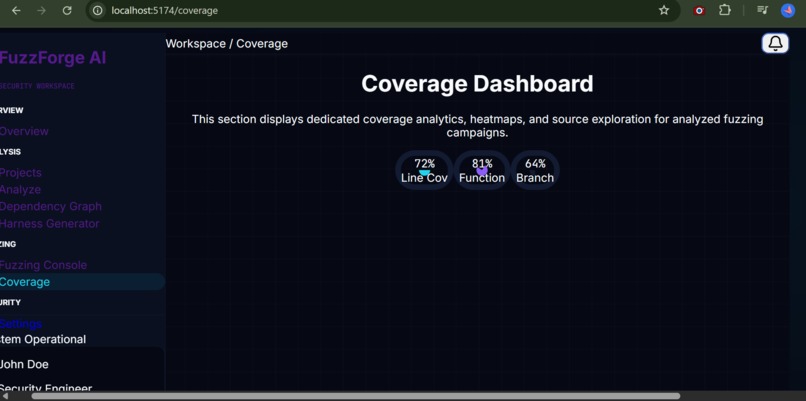
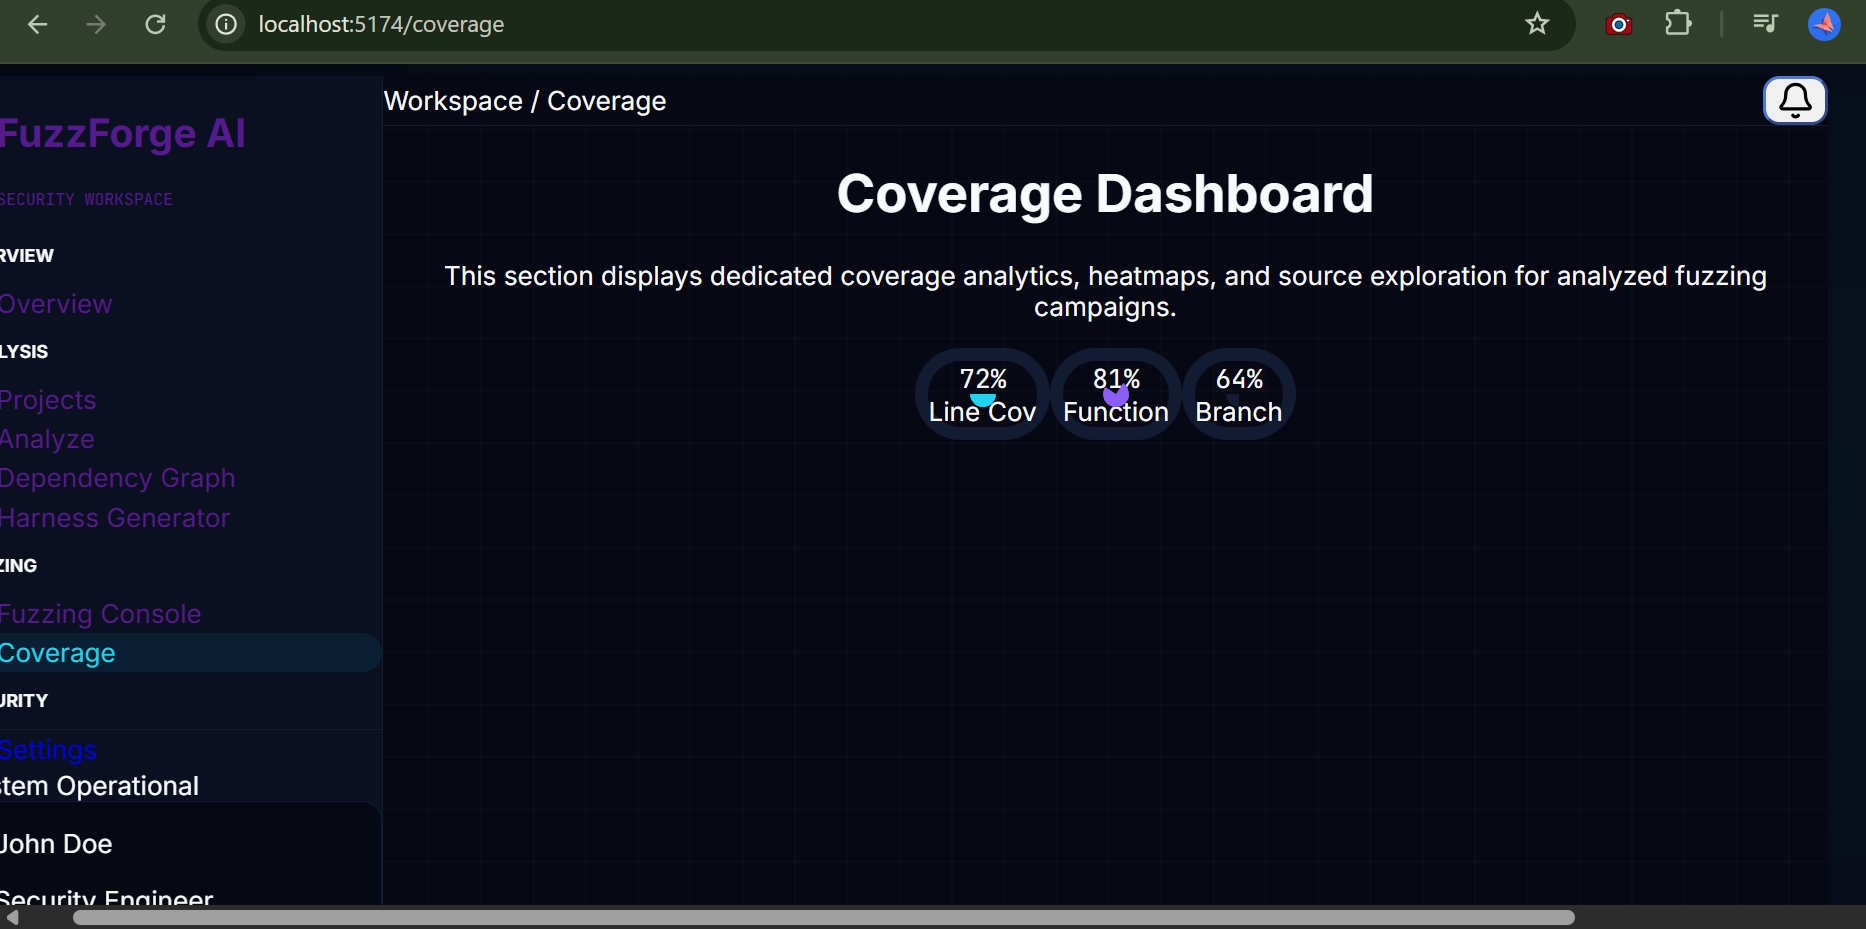
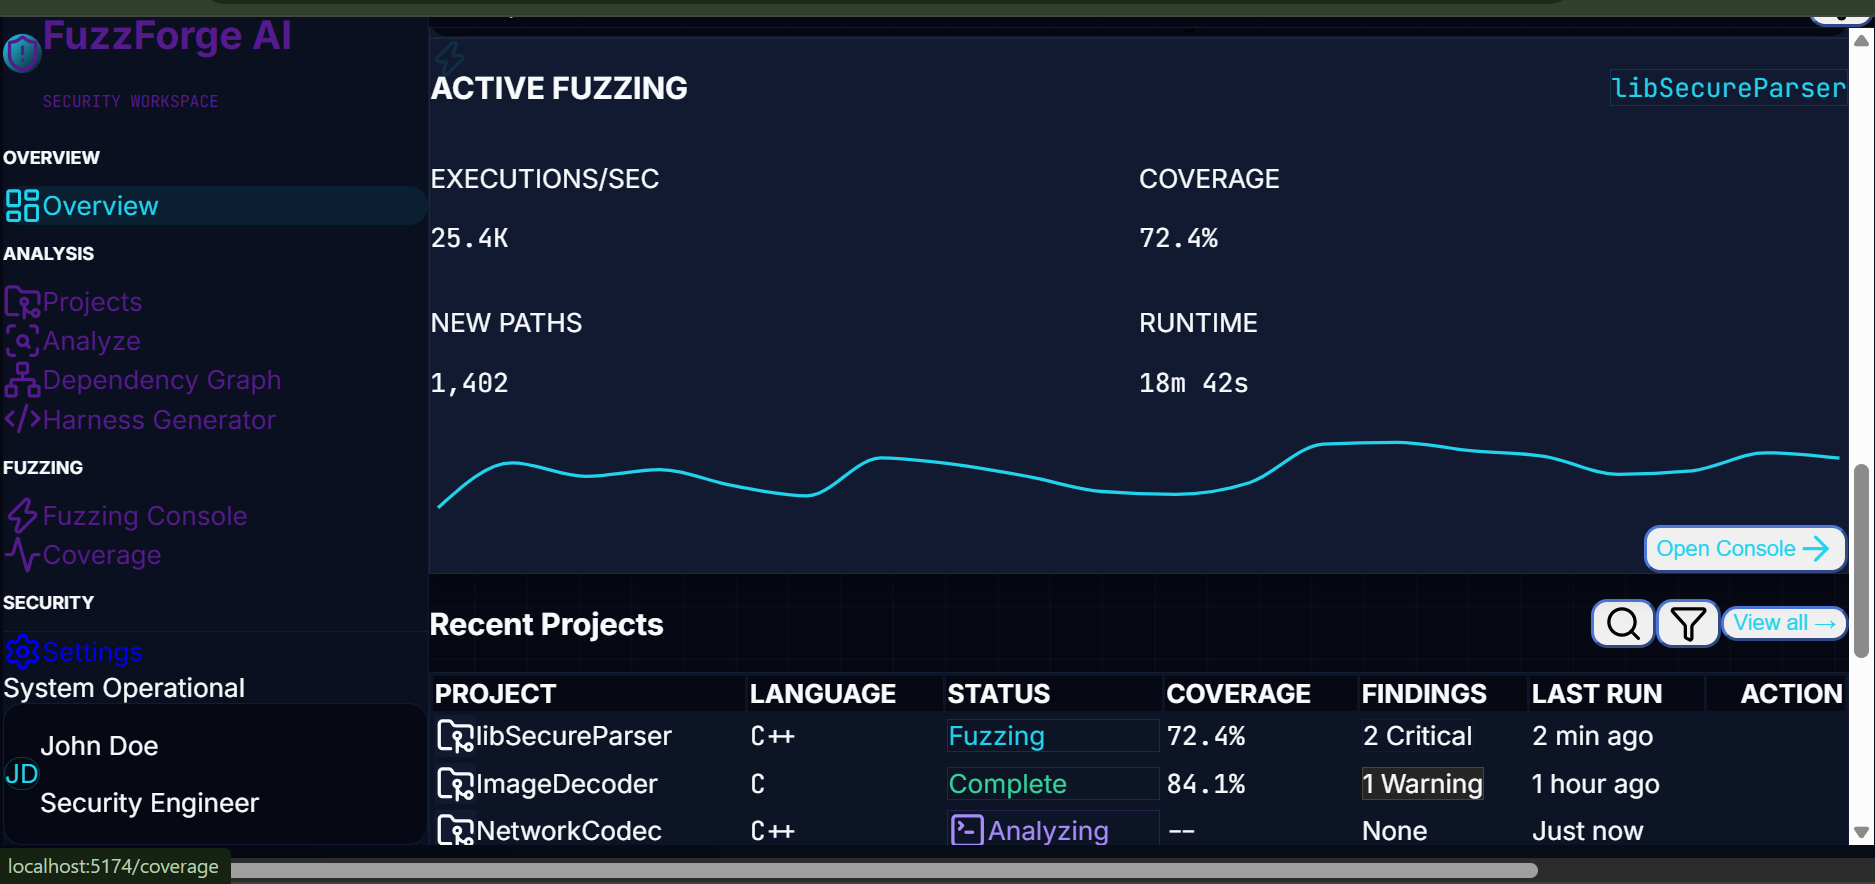
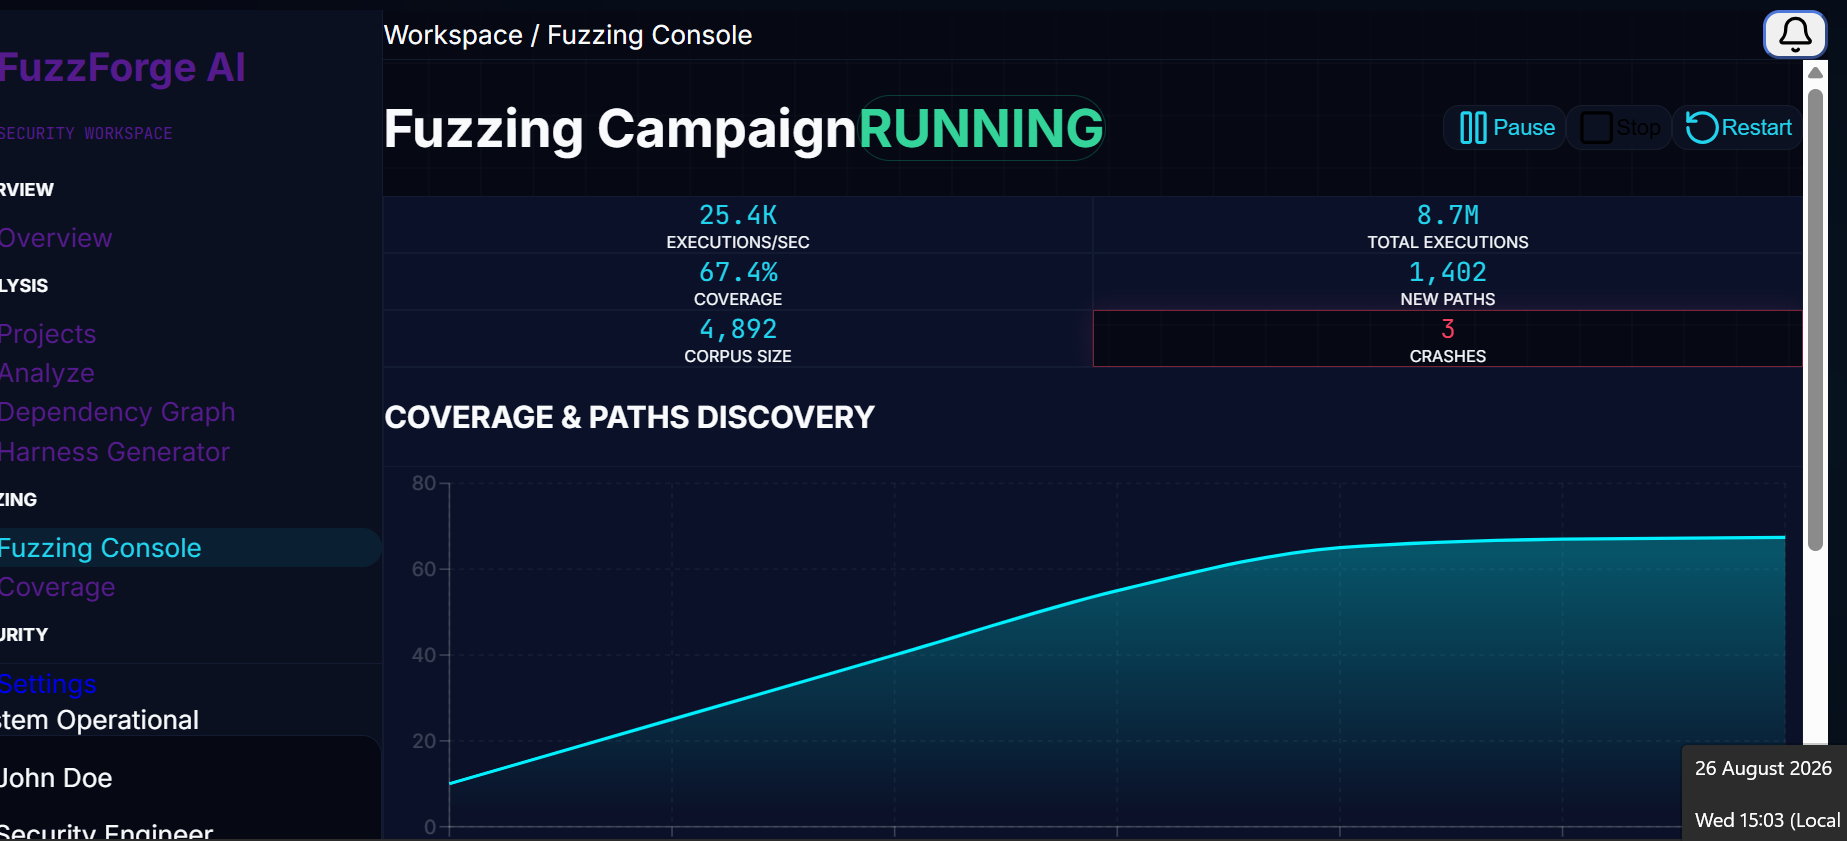
coverage dashboard
-
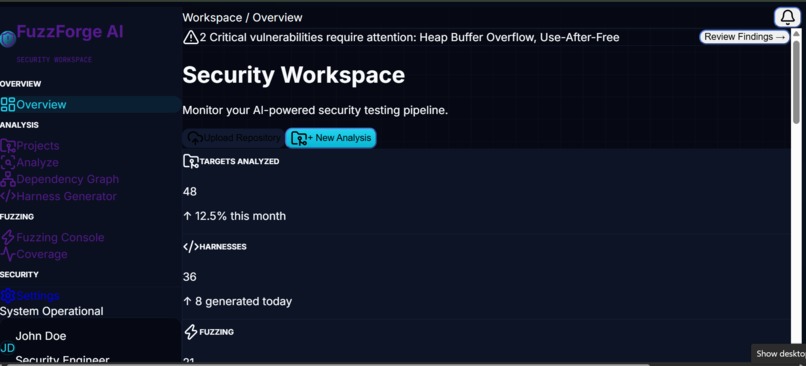
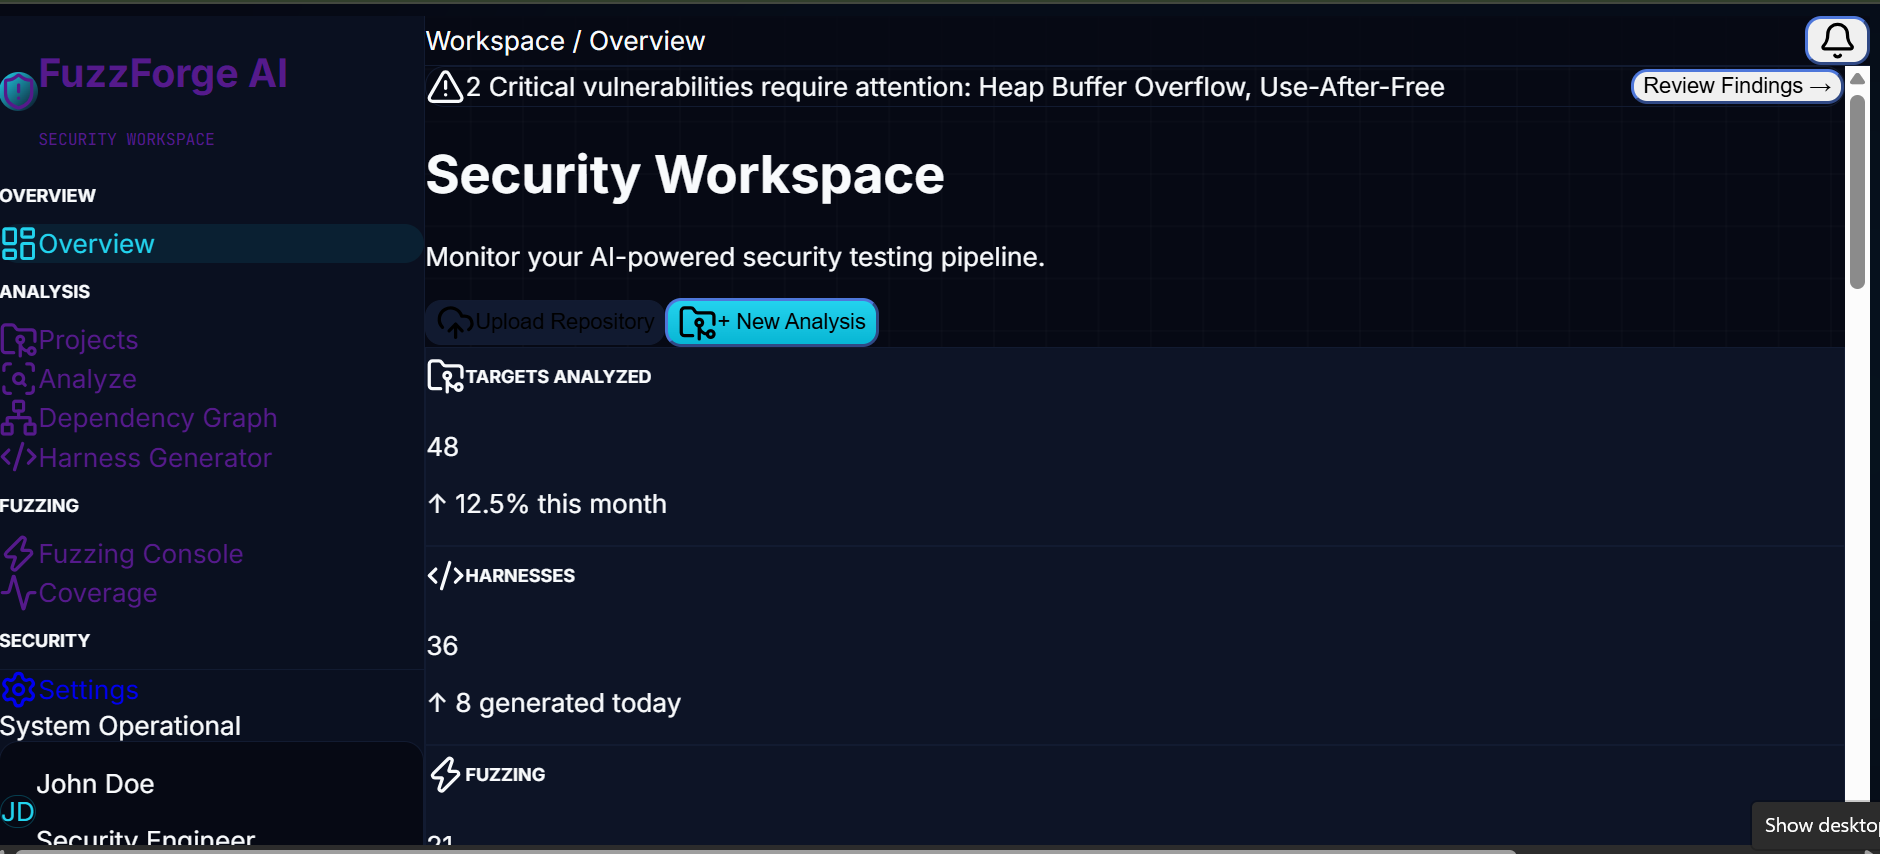
security workspace
-
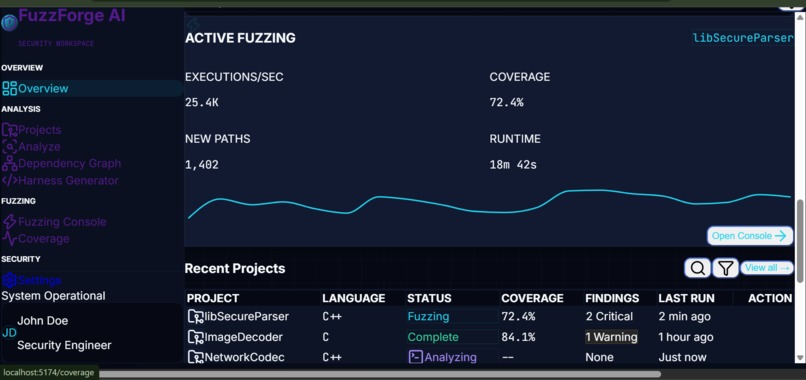
active fuzzing
-
analytics
-
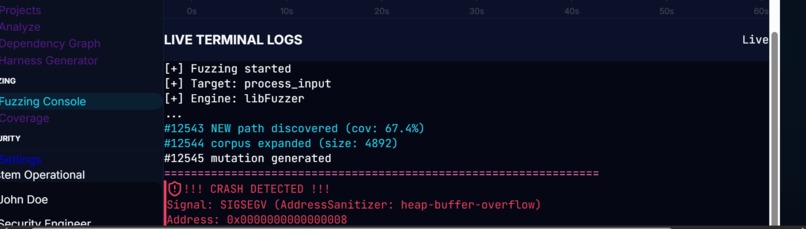
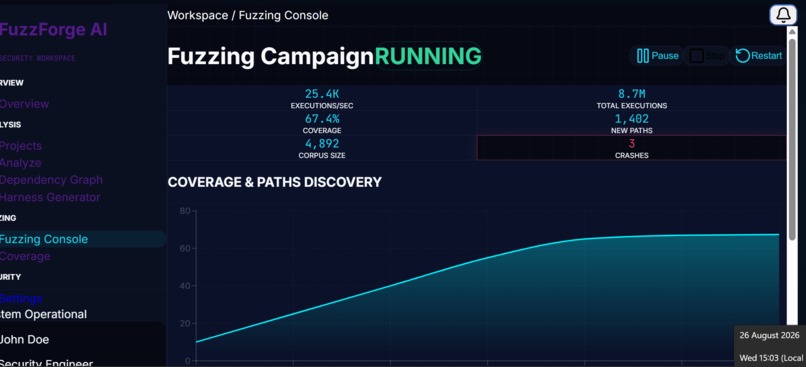
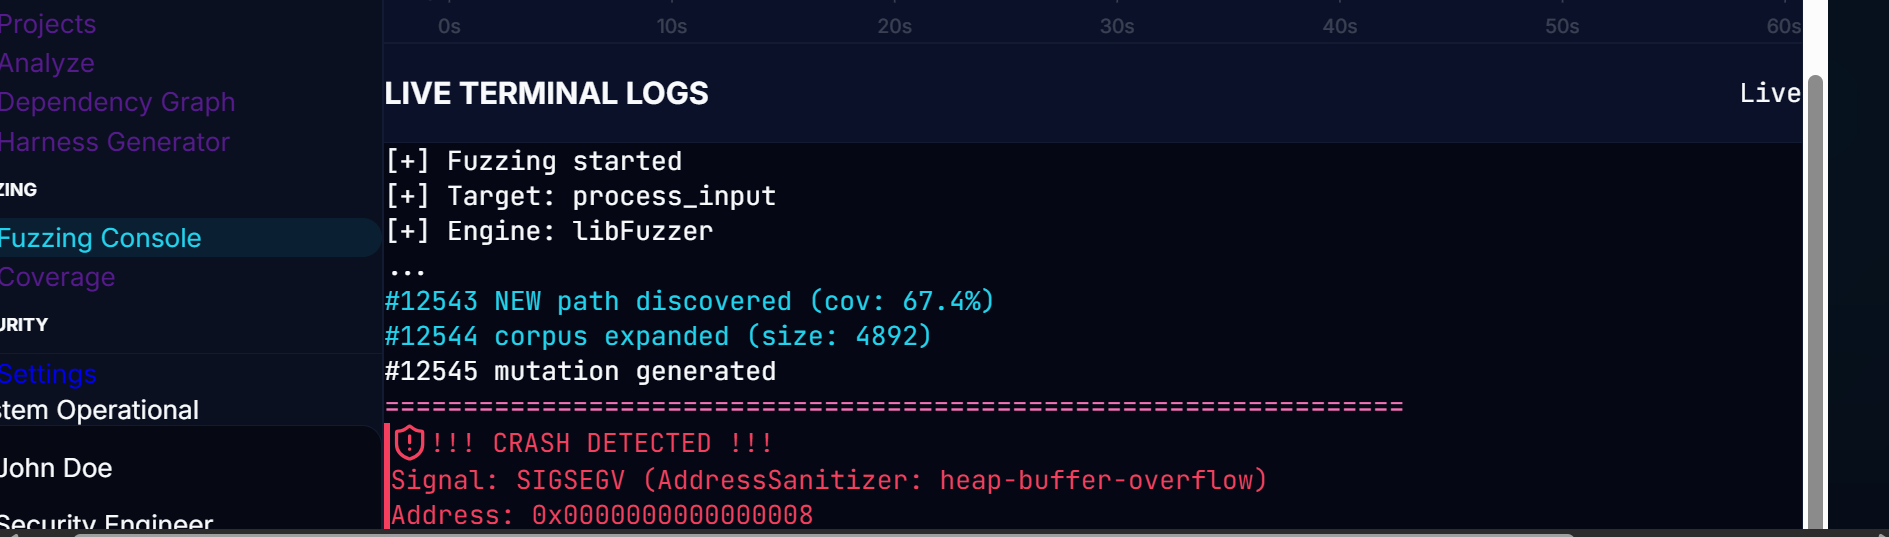
live console
-
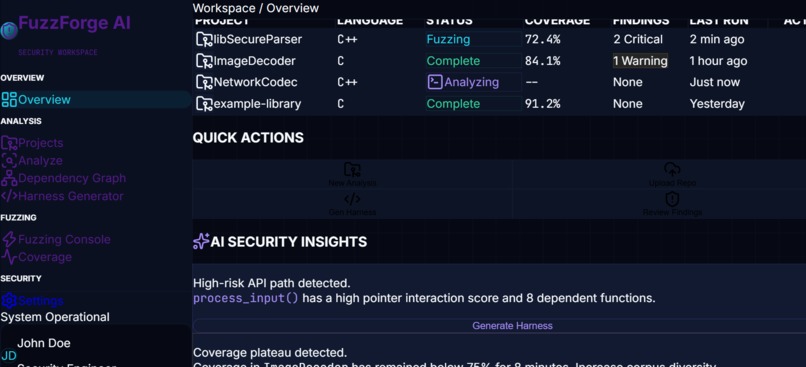
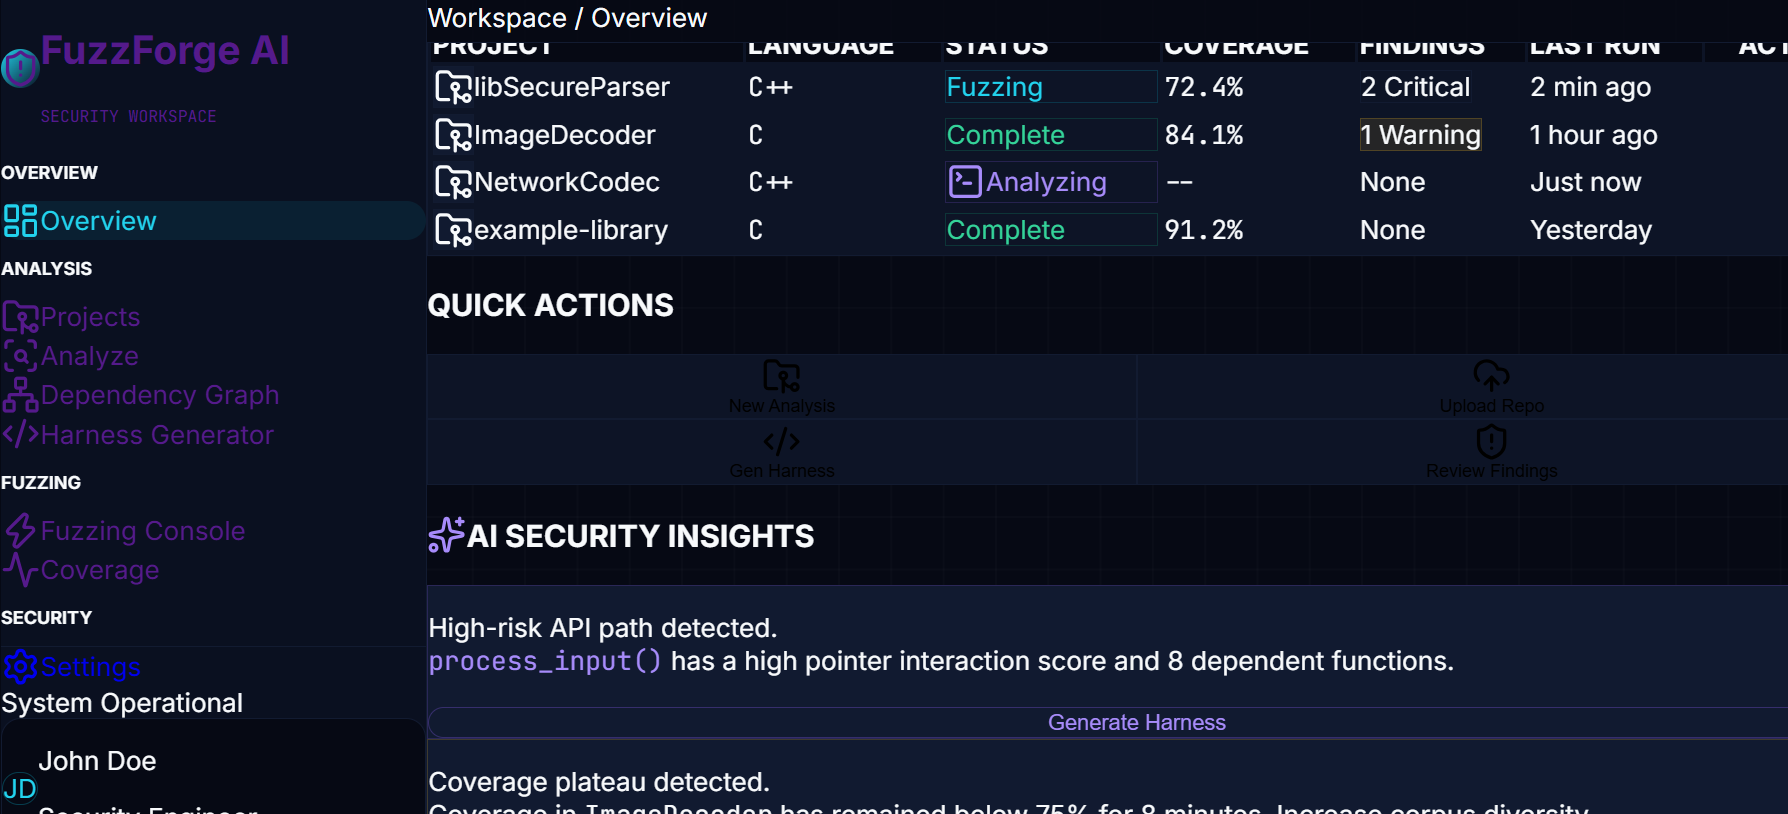
security insights
Inspiration
Security testing C/C++ libraries heavily relies on fuzzing, but writing a fuzz harness manually is often difficult and time-consuming. Developers need to understand APIs, data structures, pointers, valid inputs, and initialization sequences before fuzzing can even begin. We wanted to automate this barrier.
What We Built
FuzzForge AI automatically analyzes an unfamiliar C/C++ library and generates a coverage-guided fuzzing harness.
It uses Clang AST/LibTooling to extract functions, parameters, structures, pointers, return types, and API relationships. It then identifies potential initialization dependencies and builds valid function call sequences.
The generated harness is integrated with libFuzzer and sanitizers such as AddressSanitizer (ASan) and UndefinedBehaviorSanitizer (UBSan). Coverage feedback helps the system identify which generated strategies reach deeper code paths.
How It Works
C/C++ Library
      ↓
Clang AST Analysis
      ↓
API & Type Extraction
      ↓
Dependency Detection
      ↓
Input & Call-Sequence Generation
      ↓
Automatic Fuzz Harness
      ↓
libFuzzer + Sanitizers
      ↓
Coverage & Crash Analysis
What We Learned
We learned how C/C++ APIs can be analyzed using compiler infrastructure and how fuzzing works beyond simply generating random data. We also explored API dependency analysis, code coverage, sanitizers, and automated test generation.
Challenges
The biggest challenge was determining whether an API can be safely called without manually understanding the entire library. Pointer ownership, initialization requirements, structures, and dependencies can make arbitrary C/C++ code difficult to analyze.
Our approach combines static analysis, dependency inference, and coverage feedback to make the generated harness increasingly useful.
Future Scope
We plan to improve support for complex C++ types, improve API sequence prediction using machine learning, support more fuzzing engines, and provide richer vulnerability reports and coverage visualization.
Built With
- address
- cmake
- code
- coverage
- docker
- fuzzing
- libtooling
- llvm
- sanitiser


Log in or sign up for Devpost to join the conversation.