💡 Inspiration
Modern software security is plagued by alert fatigue. Traditional SAST tools dump thousands of noisy warnings into developer backlogs, while generic LLM code assistants frequently hallucinate syntactically broken fixes or risk leaking proprietary intellectual property to cloud servers.
We built ForgeGuard to solve this: an enterprise-grade, 100% local-first security auditor that bridges deterministic Abstract Syntax Tree (AST) static analysis with autonomous patch synthesis. Instead of just reporting vulnerabilities, ForgeGuard models systemic threat surfaces and automatically writes, tests, and verifies unified diff patches before code hits production.
🚀 What It Does
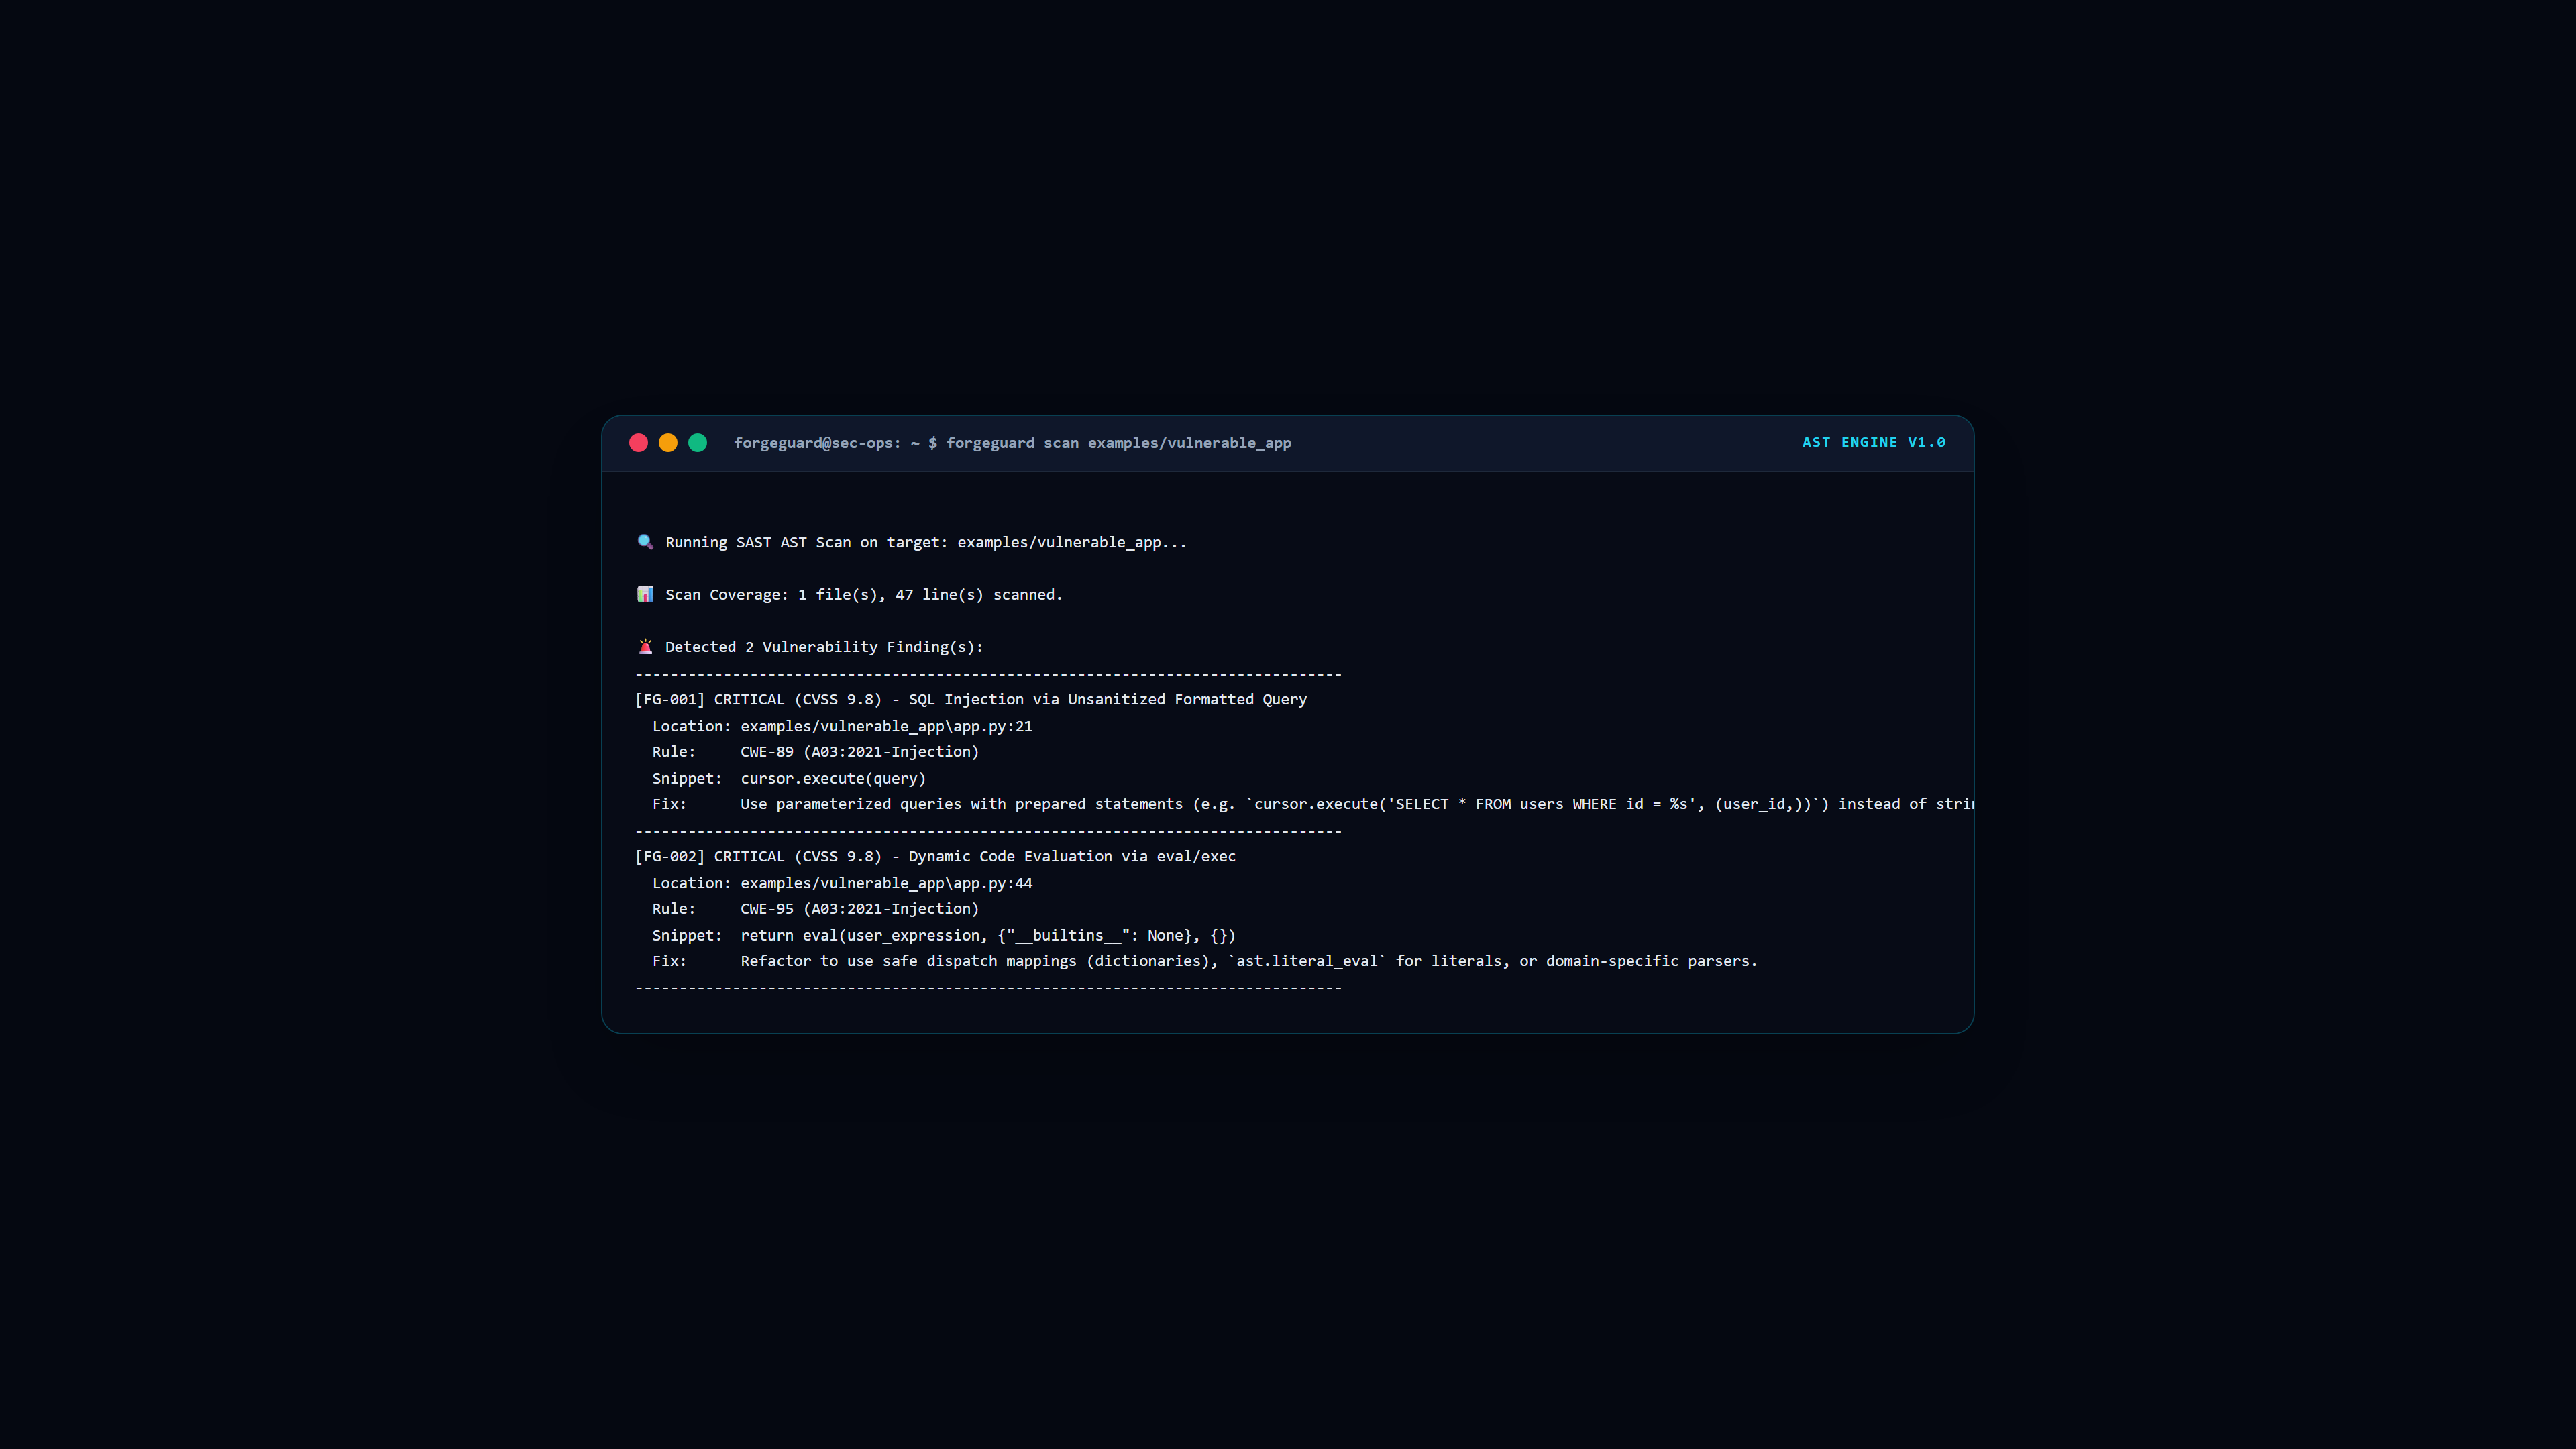
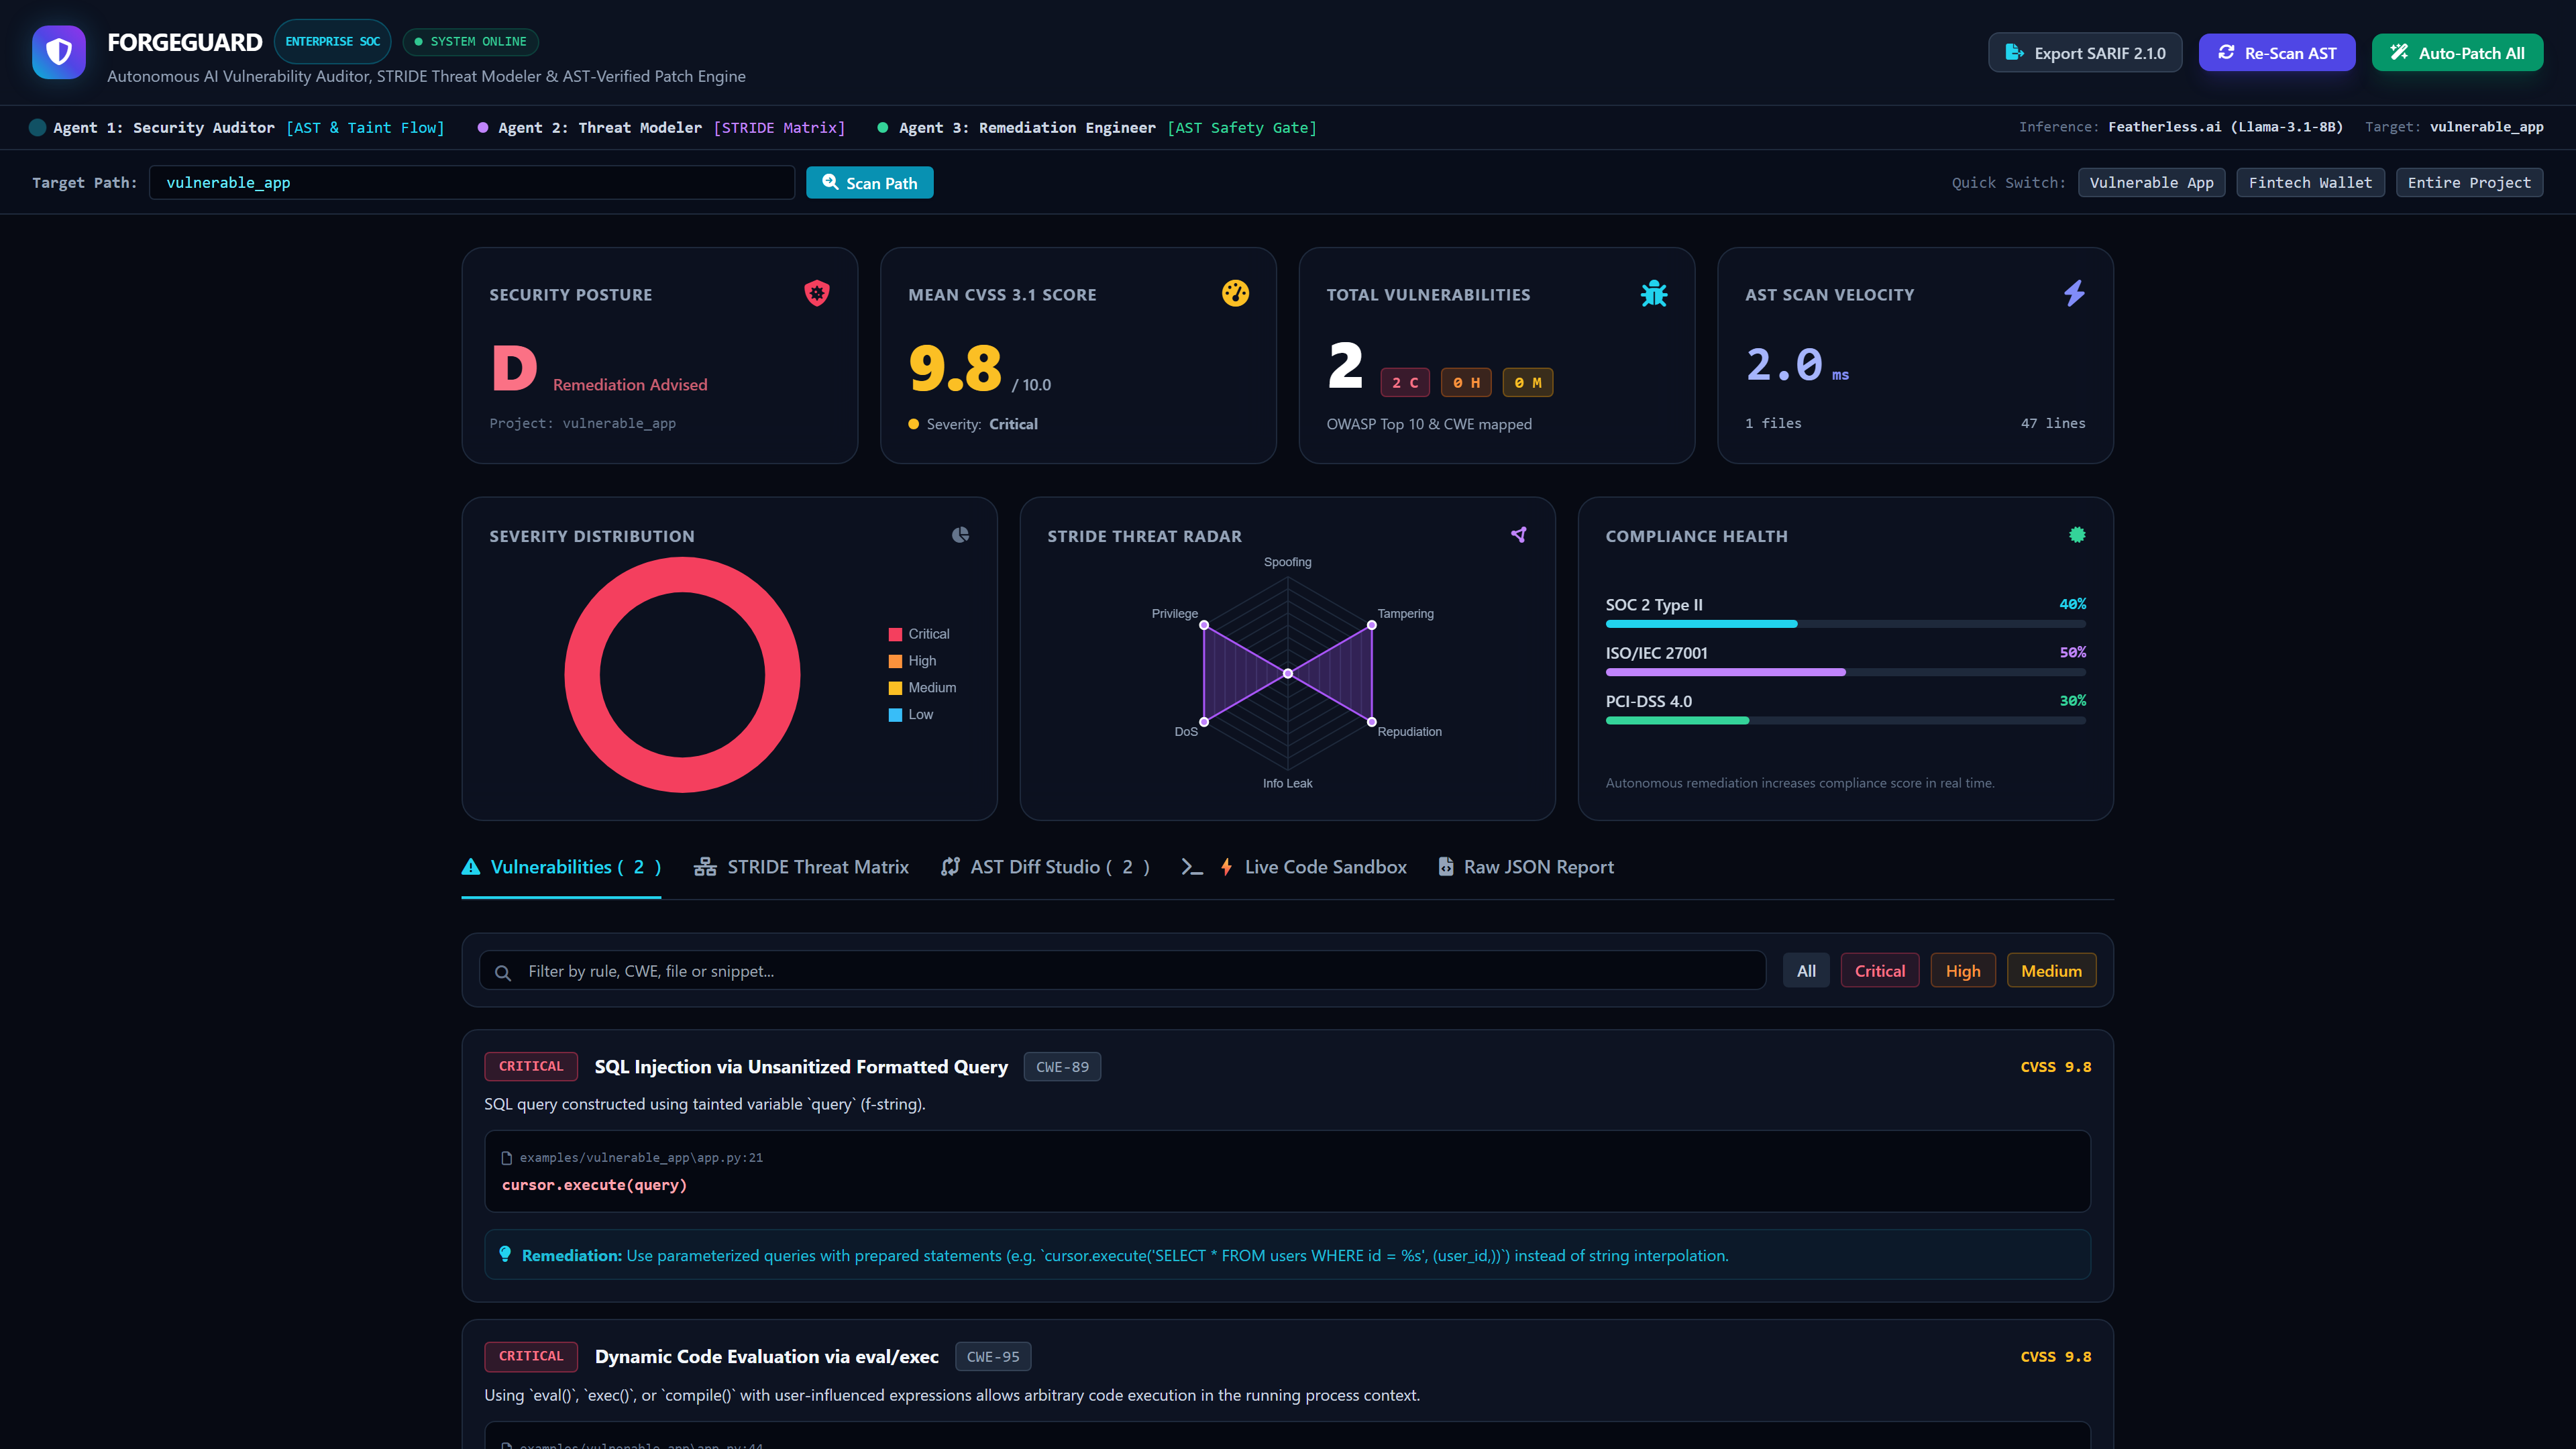
- ⚡ Sub-50ms Deterministic AST Scanner: Traverses Python ASTs to track tainted data flows from untrusted inputs to critical sinks across OWASP Top 10 / CWE vulnerabilities (SQLi, Command Injection, Insecure Deserialization, Hardcoded Secrets, Path Traversal, MD5 hashing, Insecure PRNG, Eval, Permissive CORS).
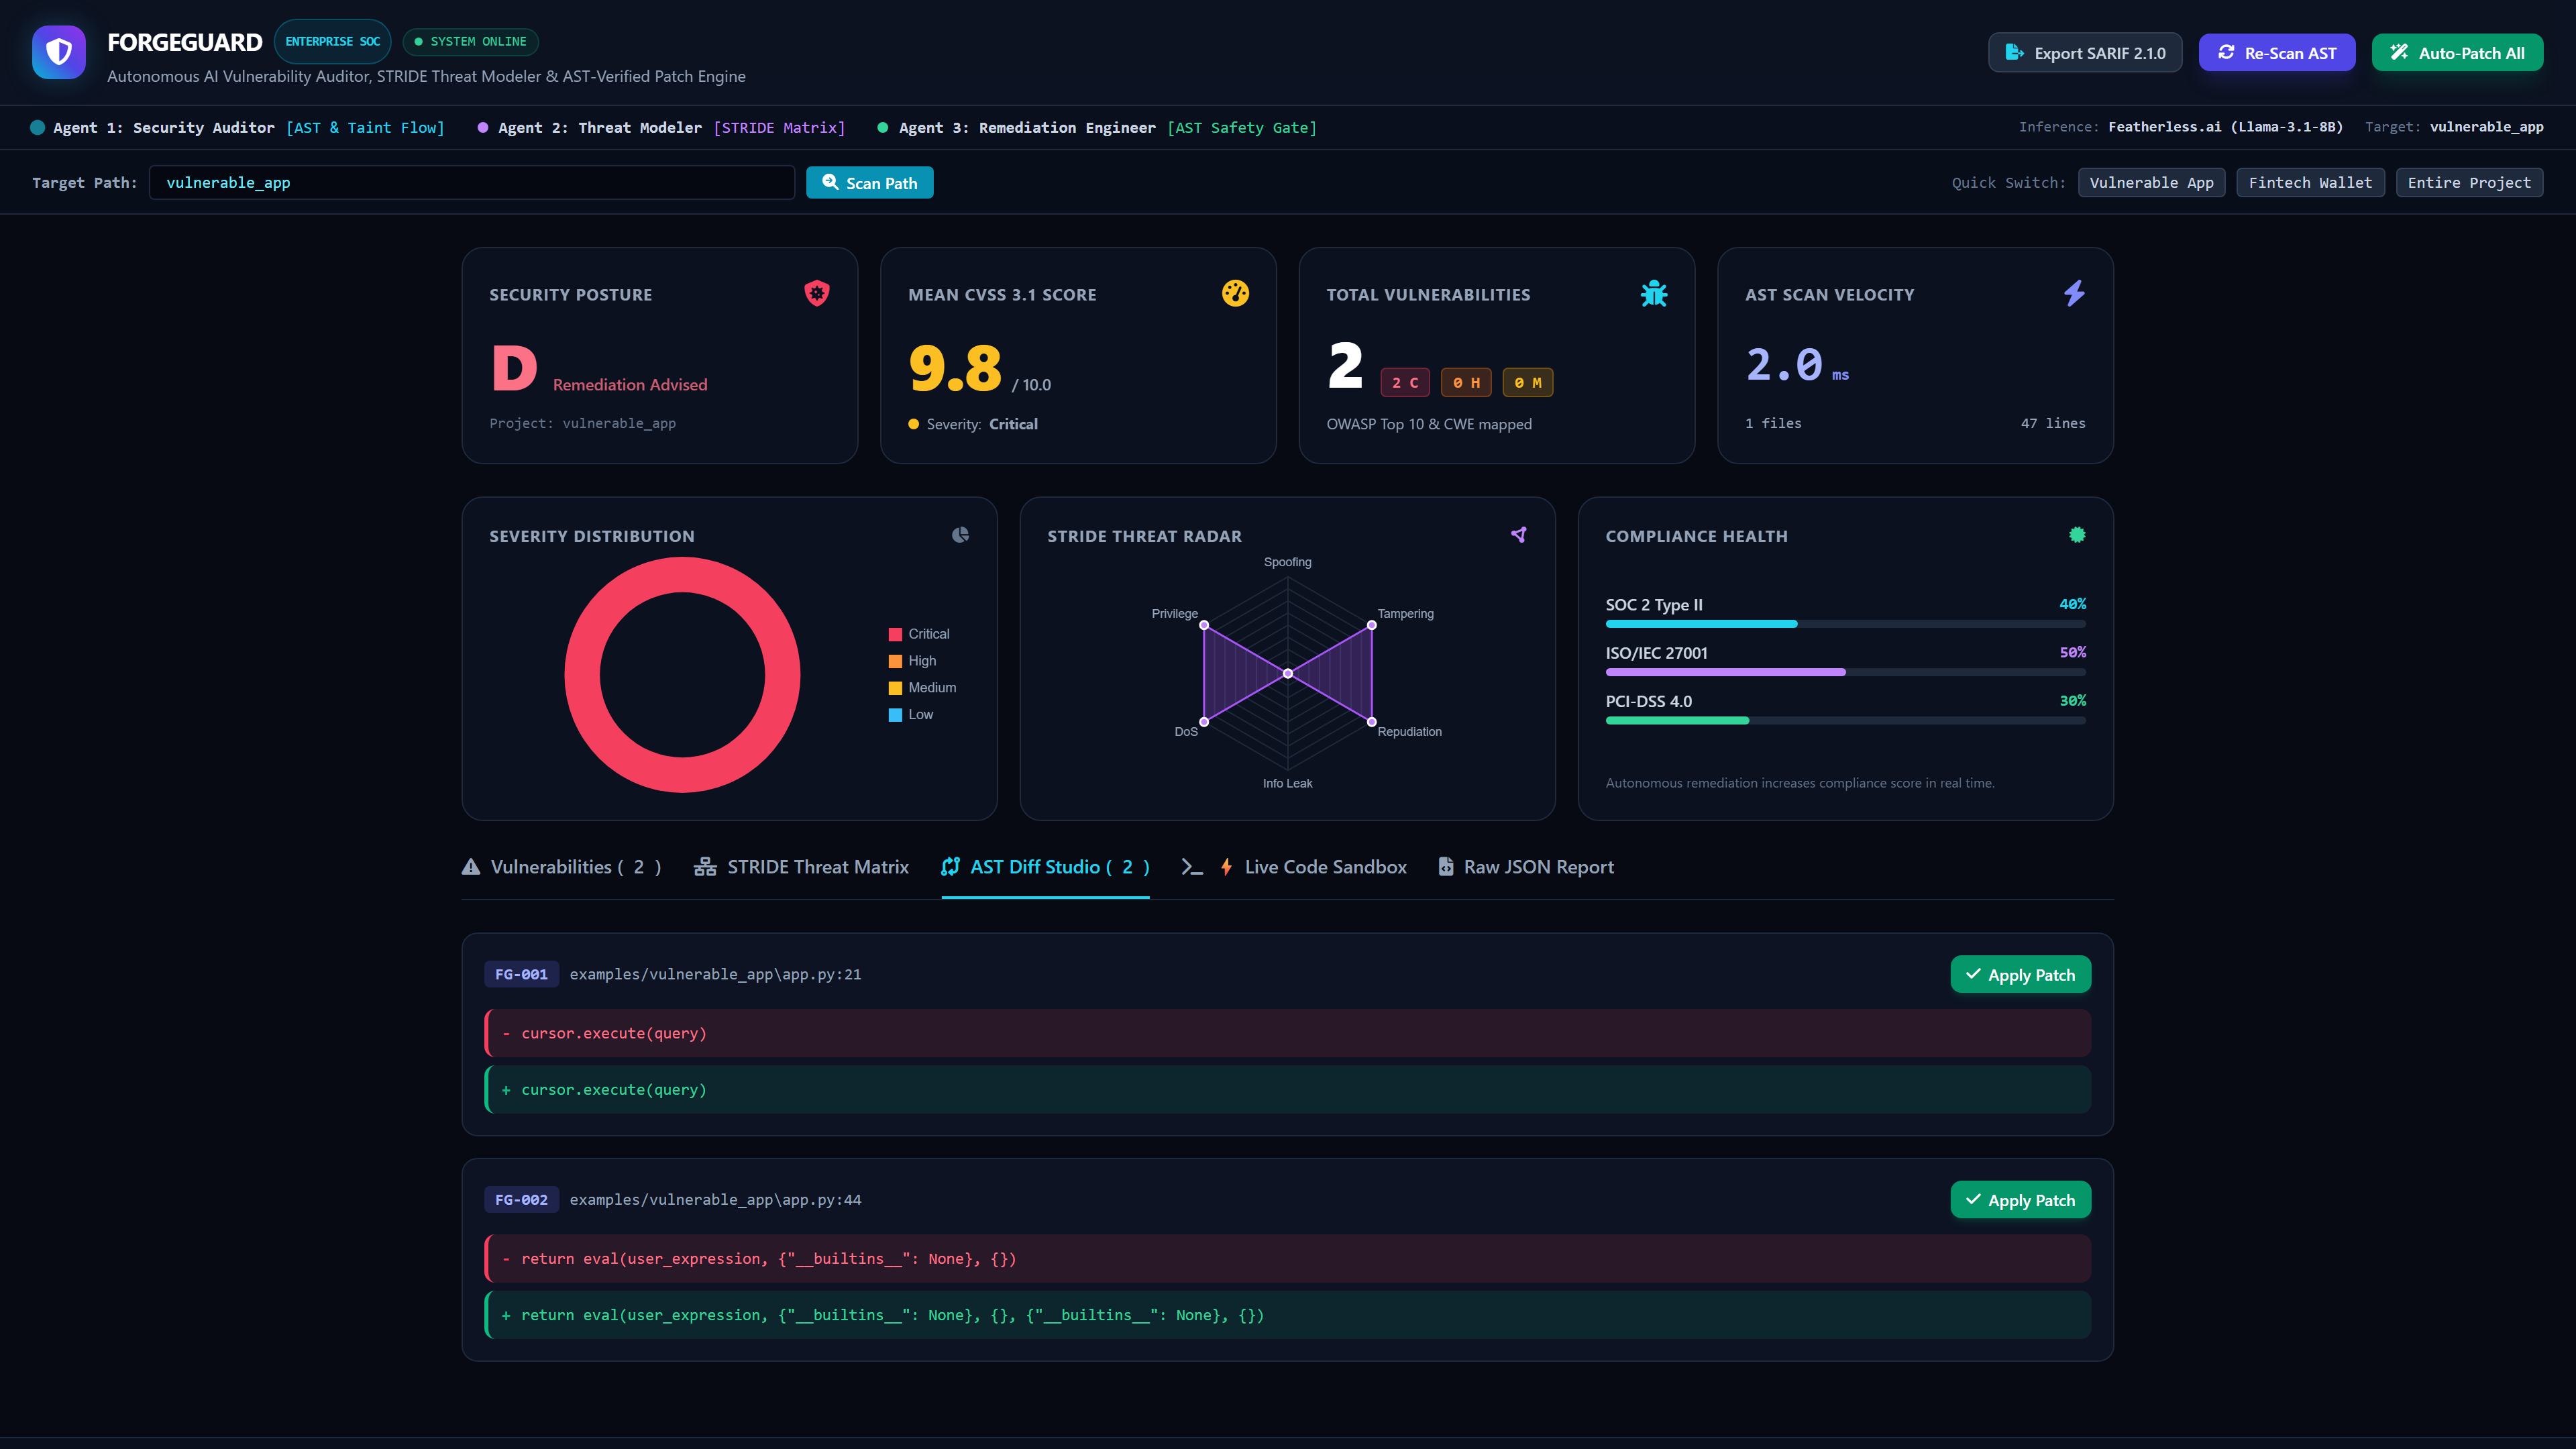
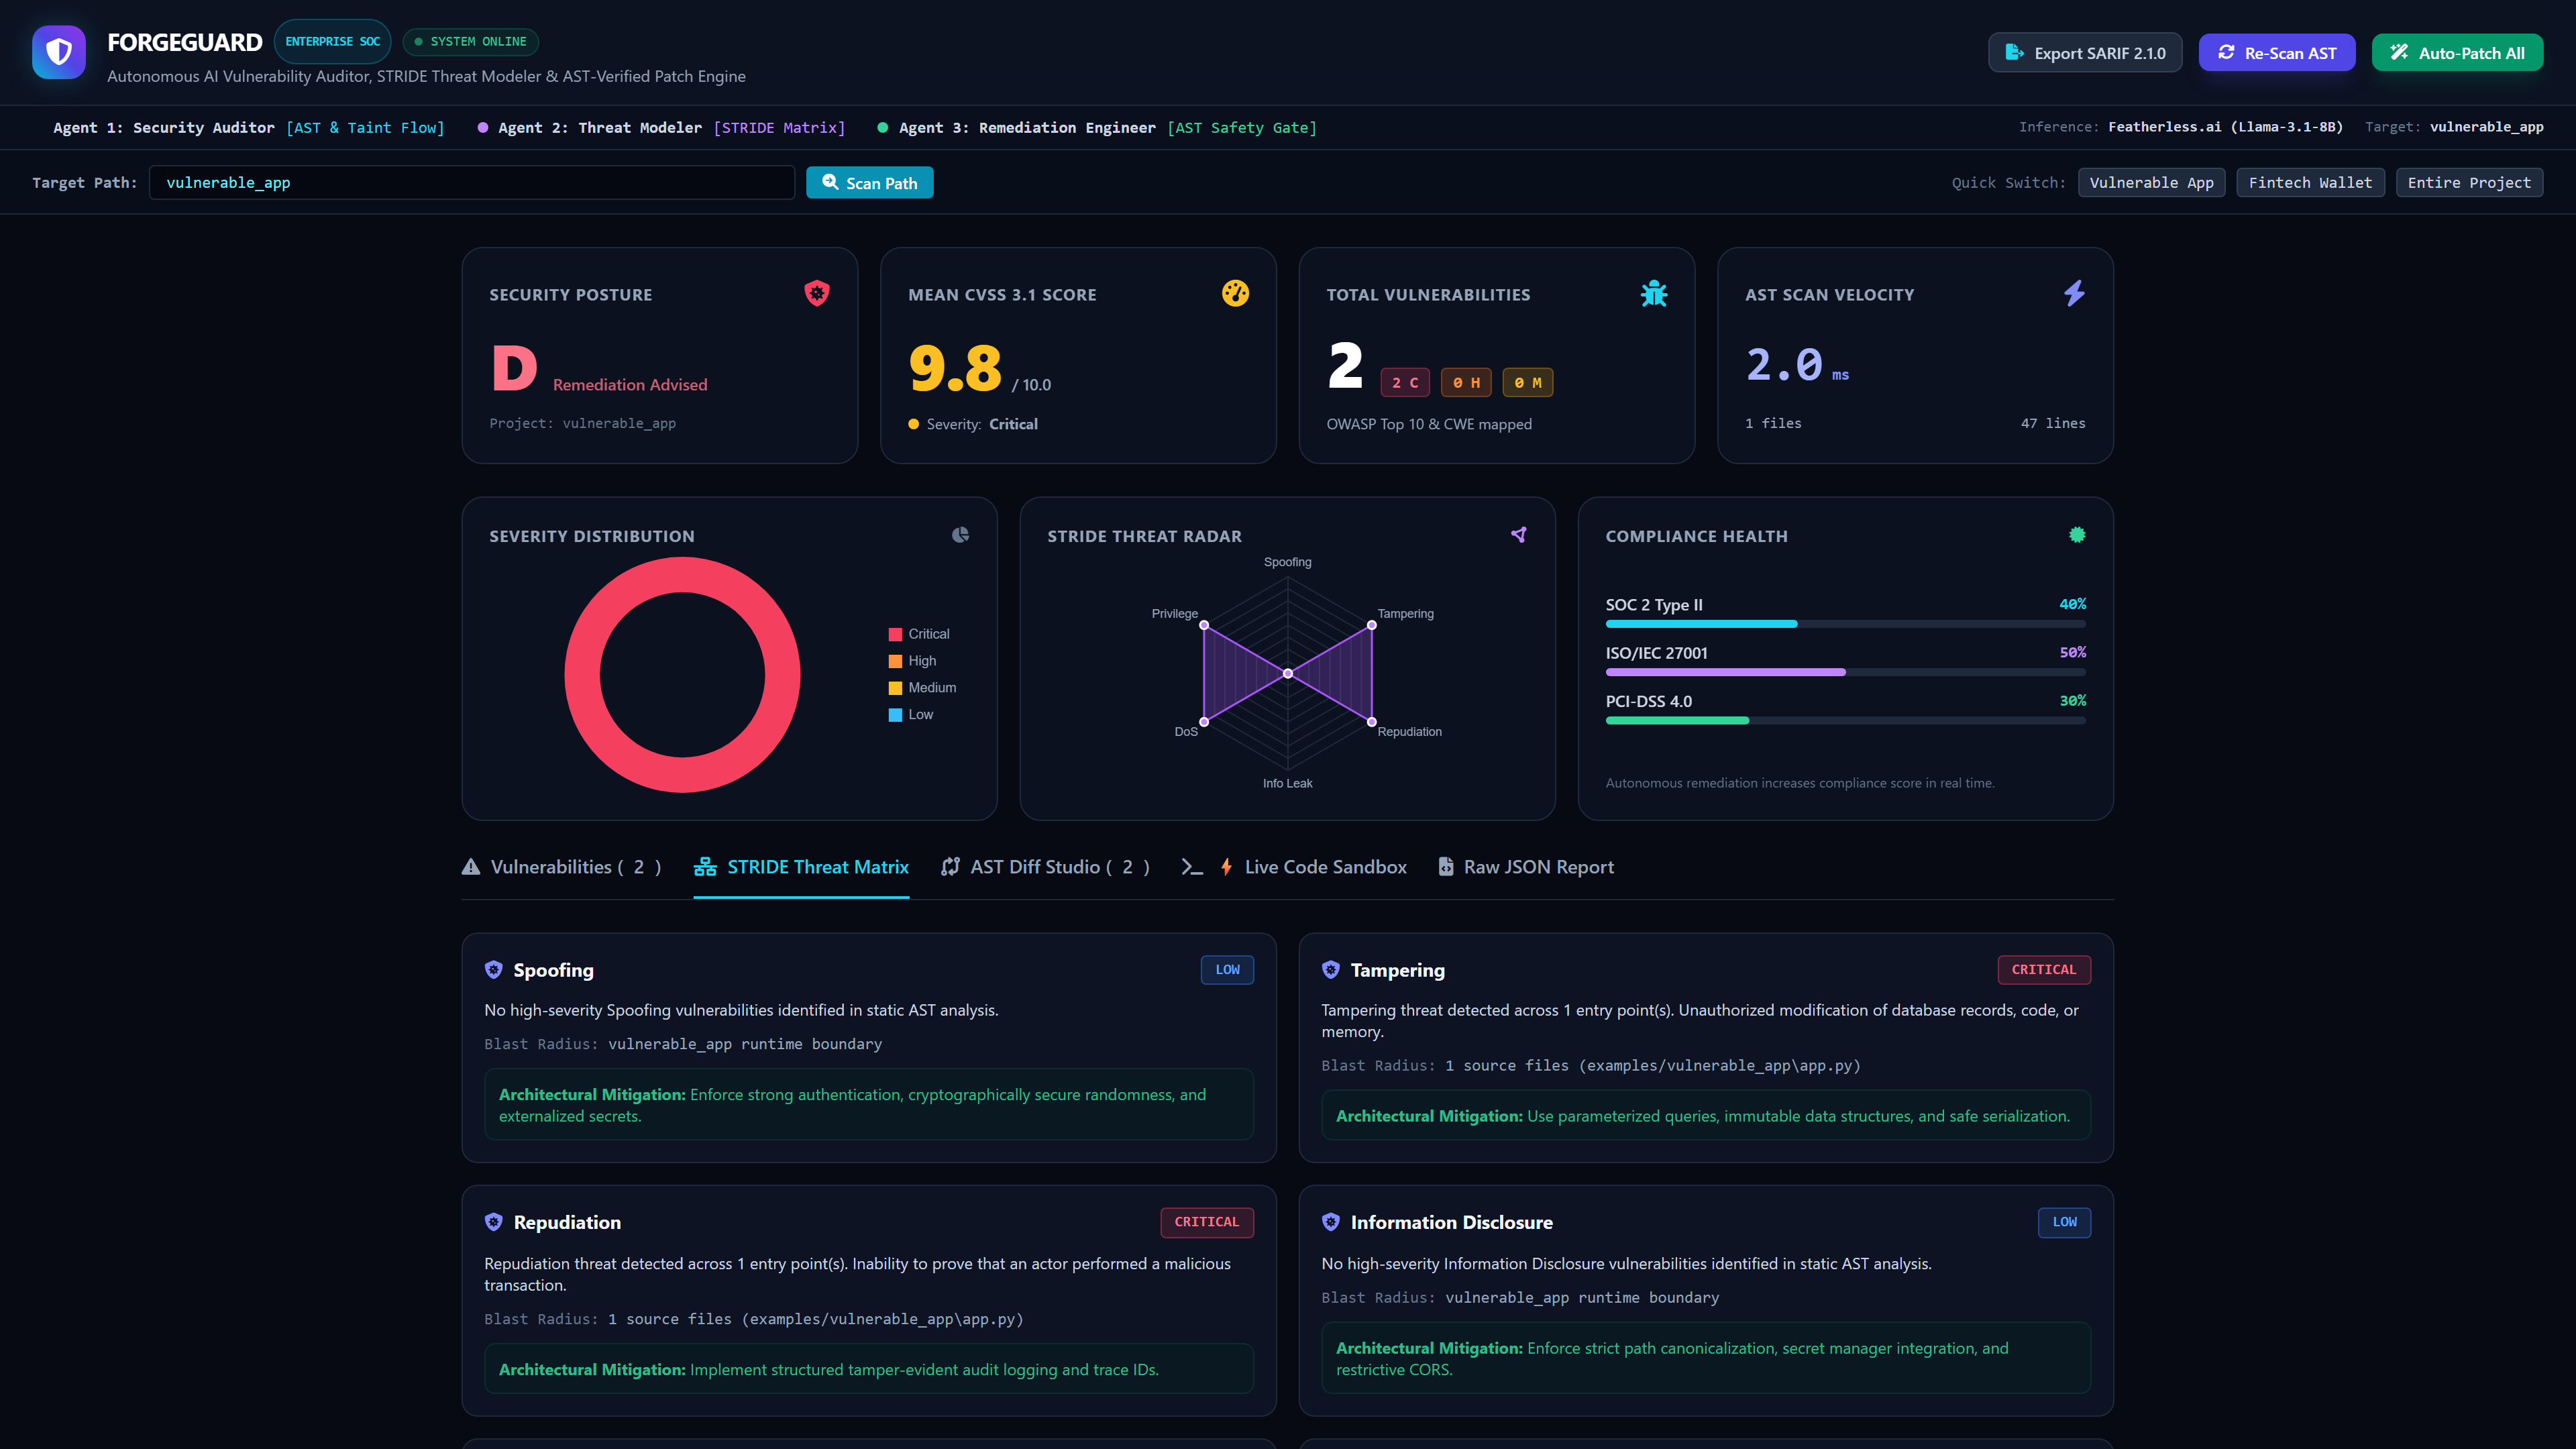
- 🛡️ 6-Axis STRIDE Threat Surface Modeler: Autonomously maps detected vulnerabilities into systemic STRIDE dimensions (Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, Elevation of Privilege) with dynamic risk scoring.
- 🔧 Autonomous AST-Verified Unified Diff Engine: Synthesizes ready-to-merge unified diffs (
- / +), executes pre-commit AST syntax validations to prevent broken builds, and maintains atomic rollback snapshots (.forgeguard_backups/). - 📊 Cyberpunk Glassmorphic SOC Dashboard: Real-time web HUD (
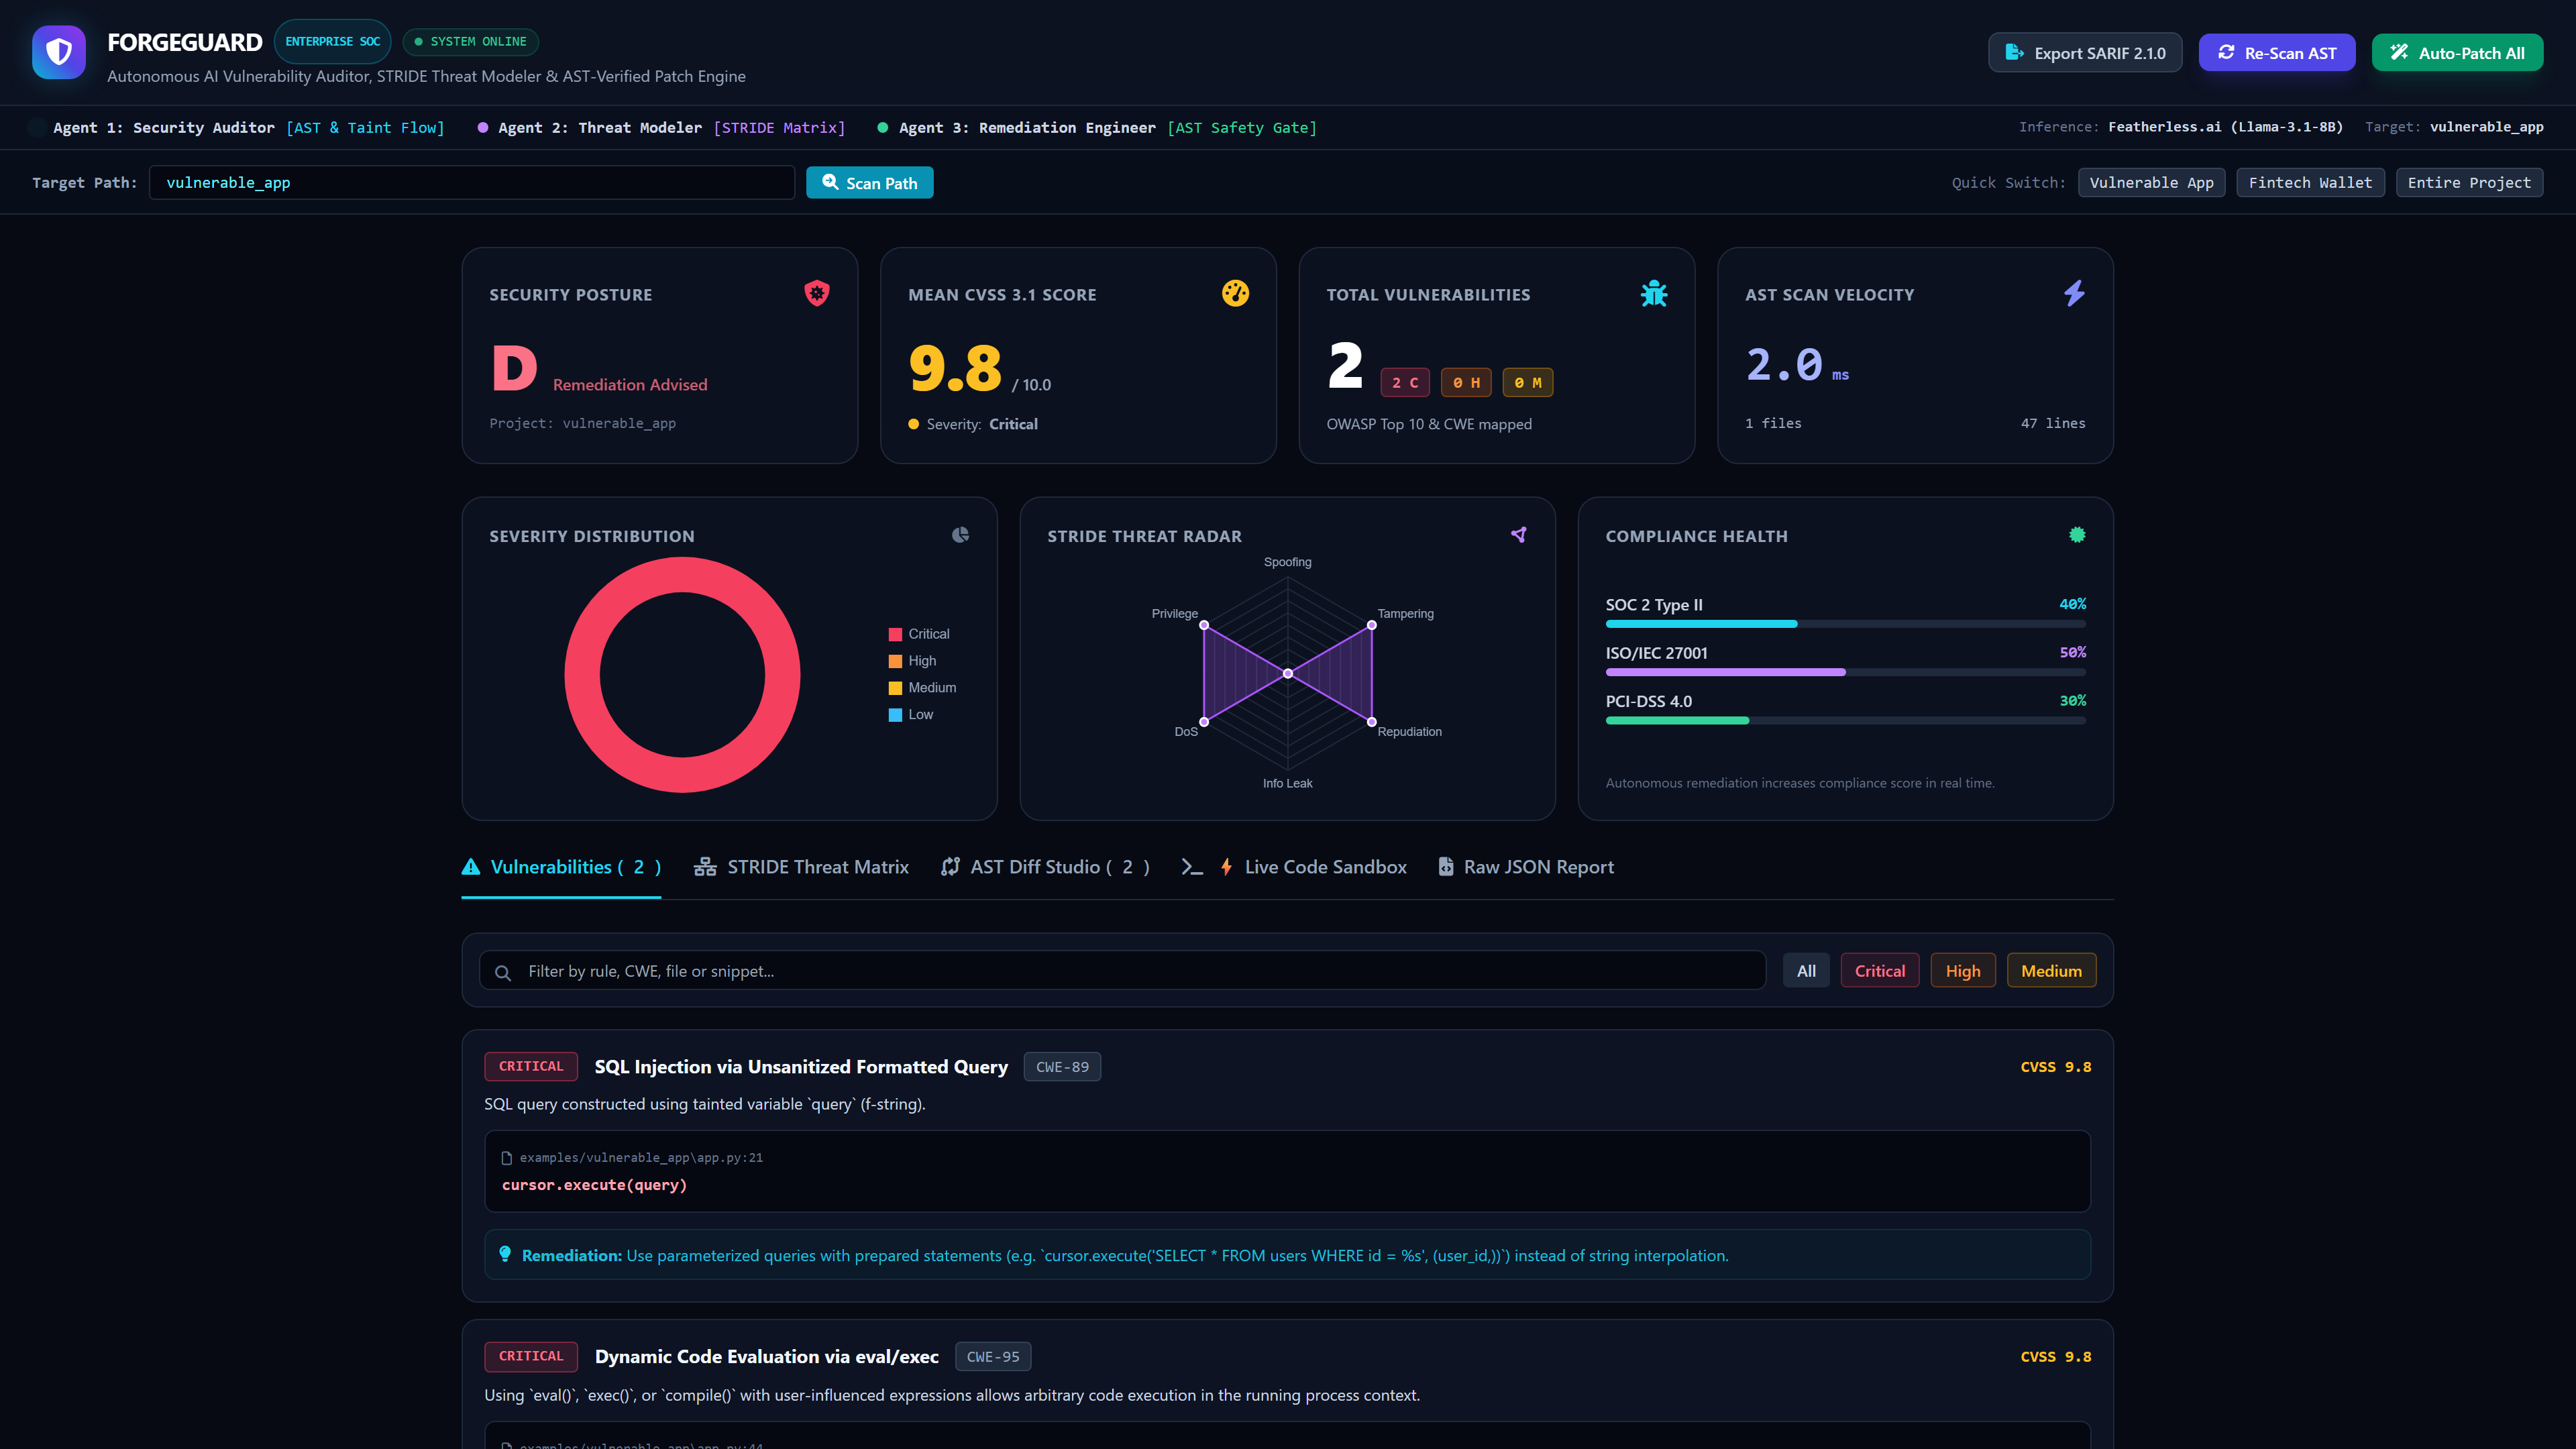
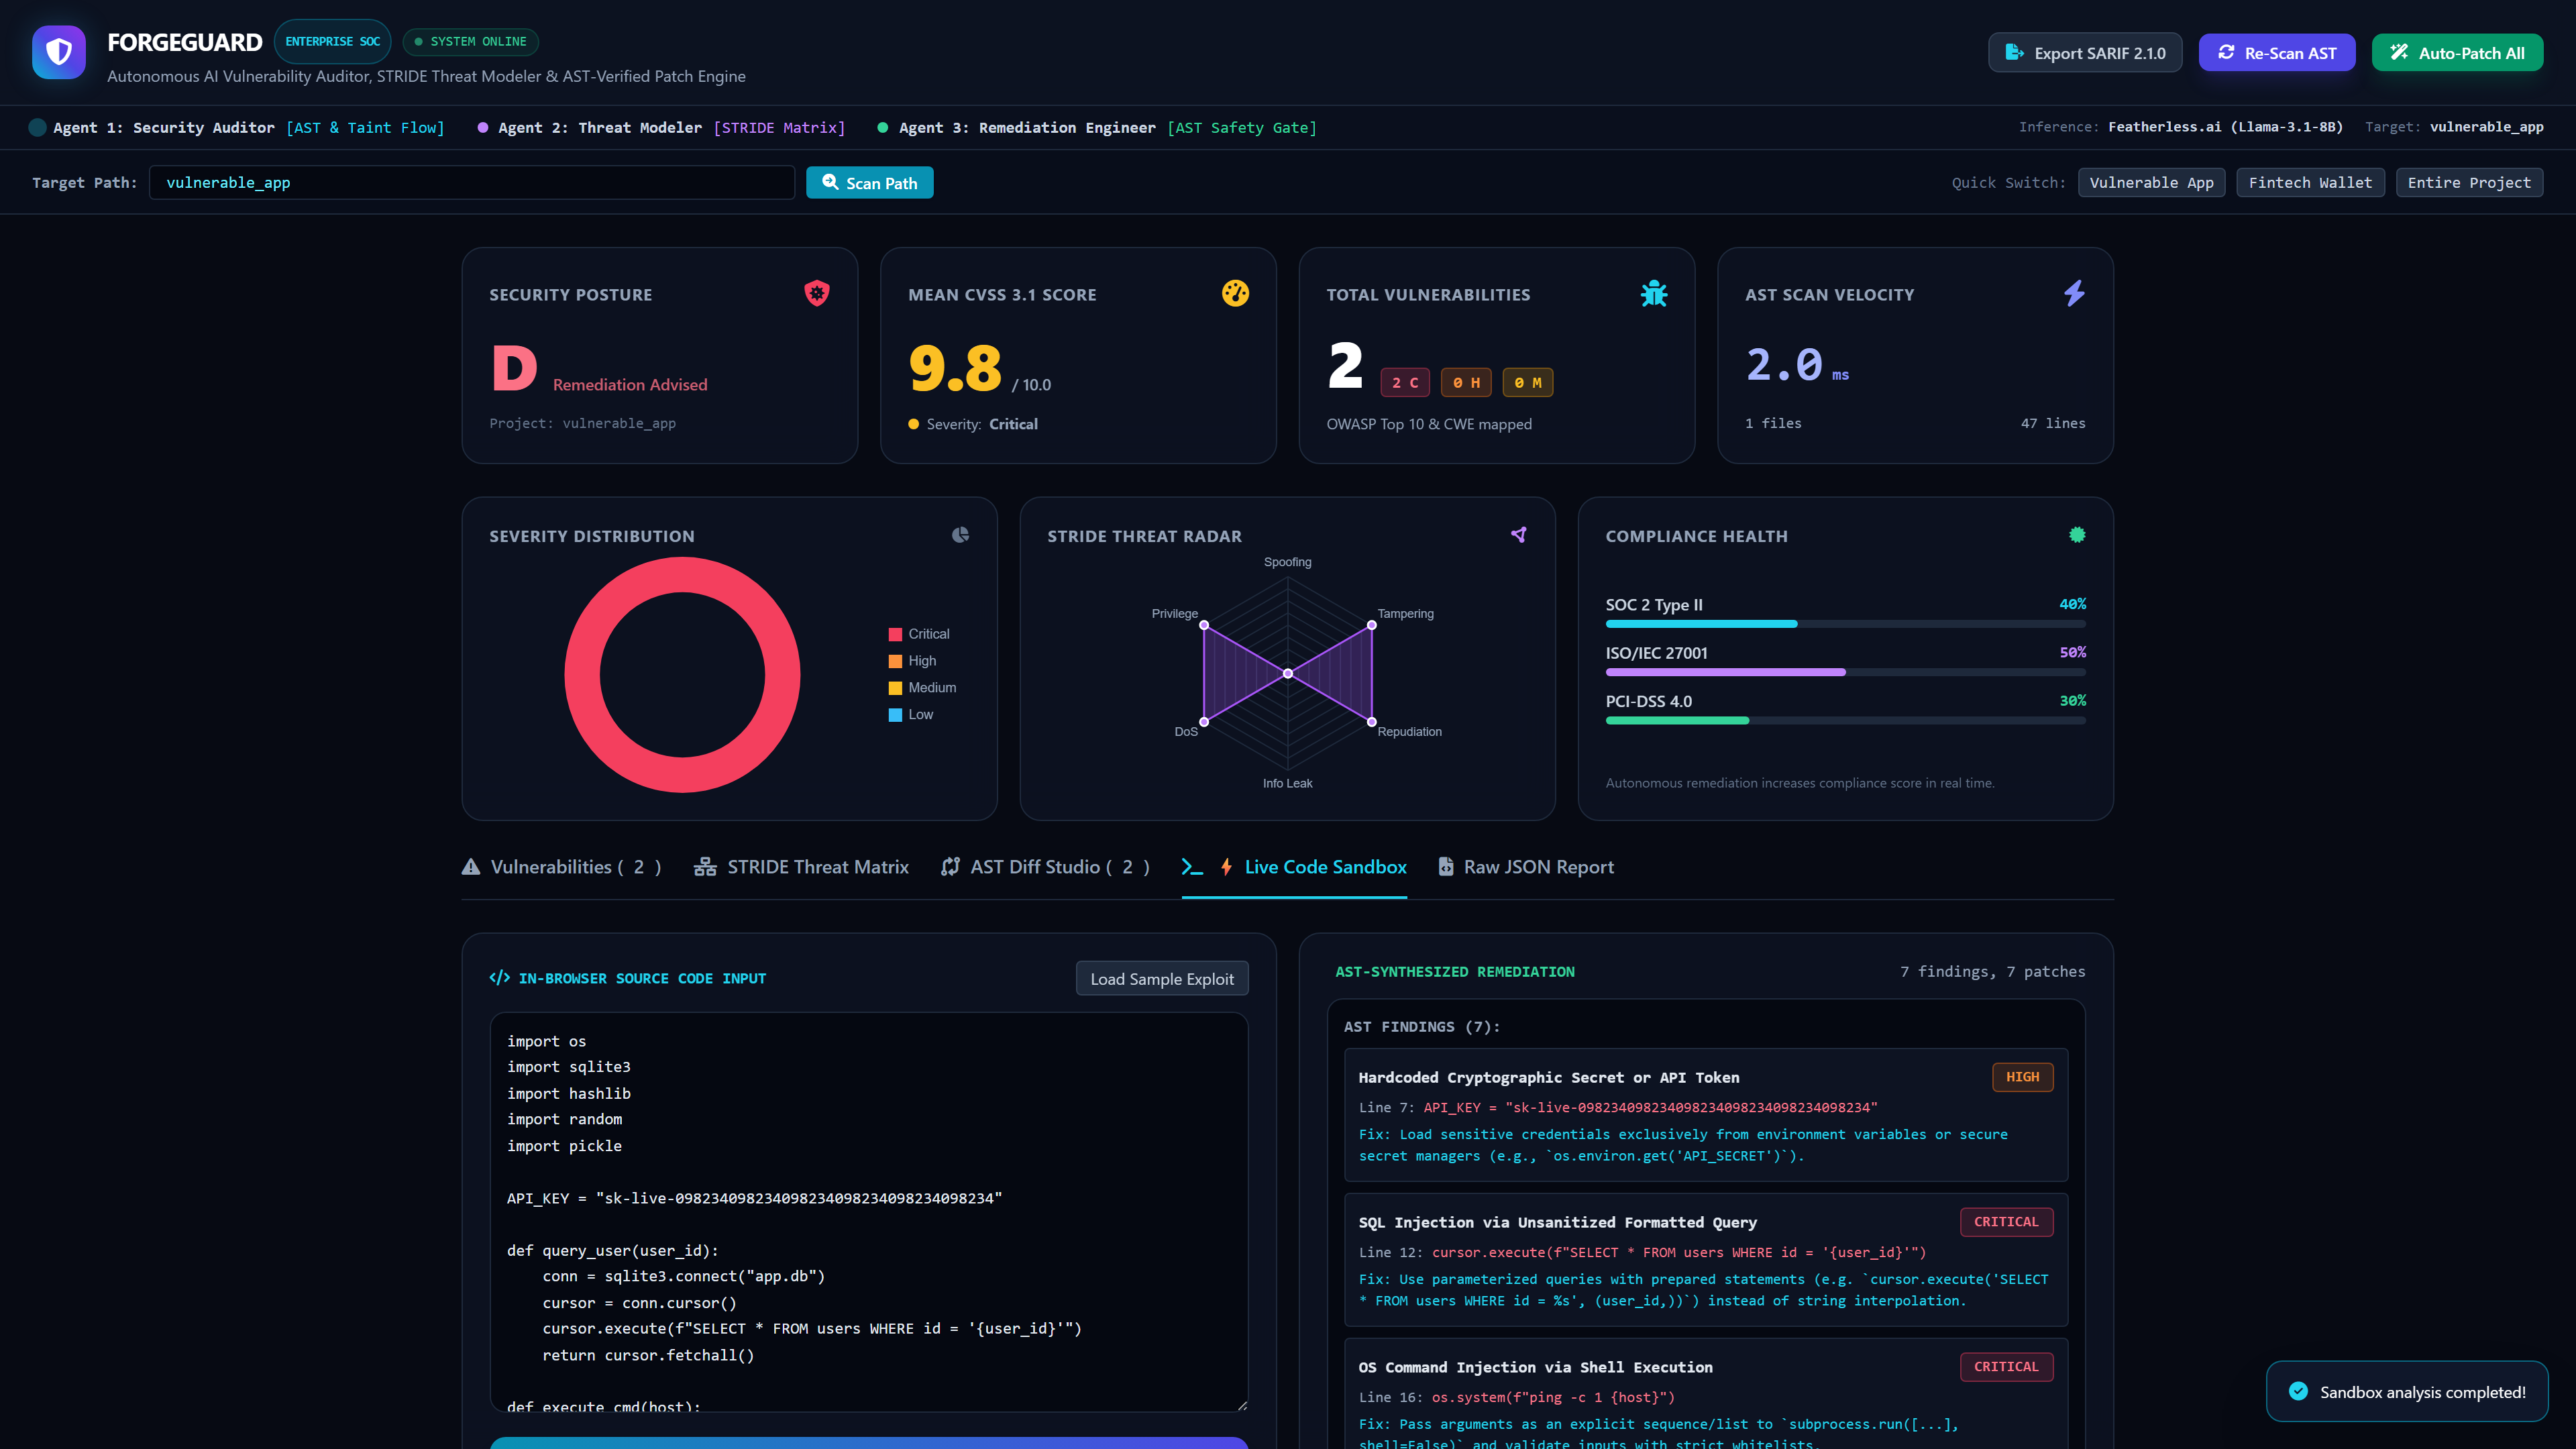
http://localhost:8899) with executive security posture grades (A+ to F), mean CVSS 3.1 ratings, compliance health scoring (SOC 2 Type II, ISO/IEC 27001, PCI-DSS), and credential masking. - 🧪 Interactive In-Browser Sandbox: Live code analysis pad for testing zero-day patterns and reviewing remediation diffs in real time.
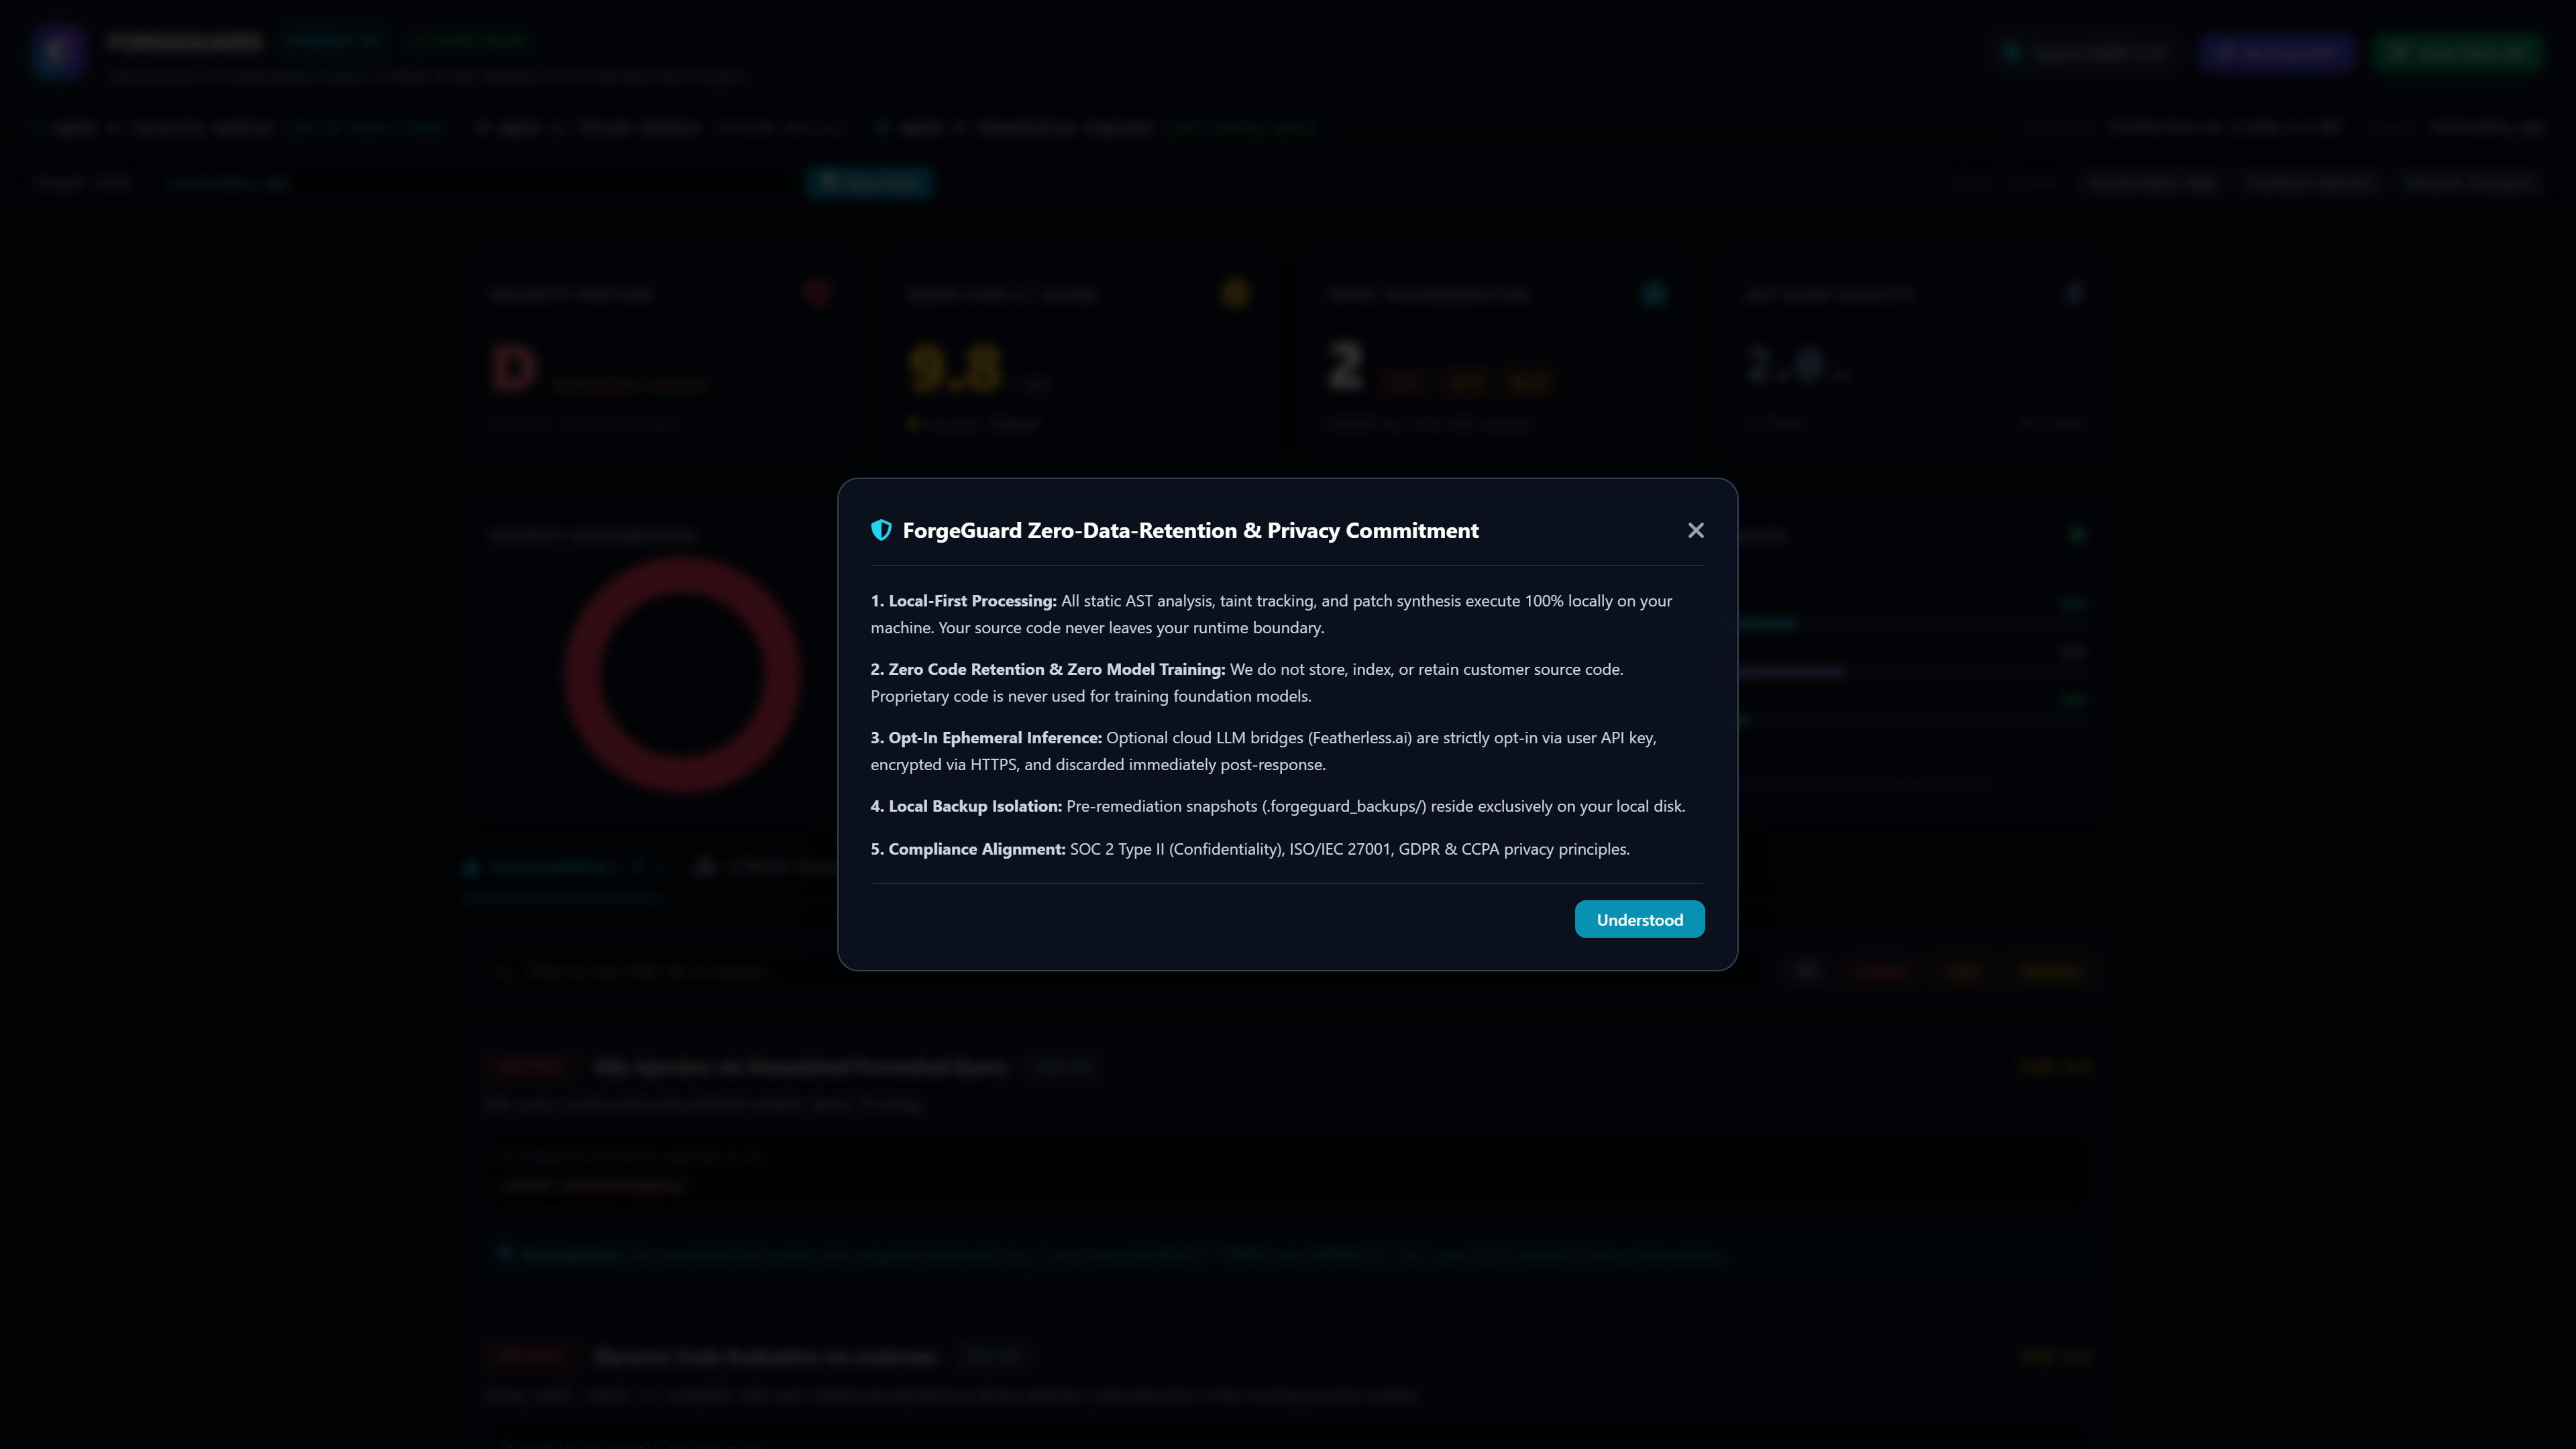
- 🔒 100% Local-First & Zero-Data-Retention: Source code never leaves the host runtime boundary, strictly adhering to GDPR, CCPA, and enterprise privacy standards.
- 🔄 DevSecOps & SARIF Integration: Exports OASIS standard SARIF v2.1.0 for native GitHub Code Scanning alerts and pre-commit Git hooks.
🏗️ How We Built It
- Core Engine: Custom Python AST visitor (
ast.NodeVisitor) paired with a lexical regex scanner for high-confidence vulnerability heuristics. - Remediation & Patching: Unified diff synthesis algorithm backed by an AST verification engine that parses prospective patches in isolated memory prior to disk commit.
- Tri-Agent Architecture: Collaborative multi-role setup featuring an Auditor Agent, Threat Modeler Agent, and Remediator Agent, with an optional Featherless.ai open-model bridge.
- Interactive SOC Frontend: Pure lightweight HTML5/Tailwind CSS with Chart.js radar & doughnut telemetry, fully responsive and zero heavy client dependencies.
- Automation & Testing: Comprehensive Python
unittestsuite (100% pass rate in 0.047s) and Playwright-driven media automation pipeline.
🧗 Challenges We Ran Into
- Syntactic Safety Guarantee: Ensuring auto-generated patches never introduce syntax errors or break existing business logic. We solved this by implementing an AST compile-time dry run before writing any file to disk.
- Zero-Retention Architecture: Ensuring all AST parsing and threat modeling run strictly in-memory without relying on external cloud APIs unless explicitly opted in.
🏆 Accomplishments That We're Proud Of
- Achieved sub-50ms execution speed across full application codebases.
- Built a complete end-to-end platform featuring a CLI suite, Web SOC dashboard, SARIF v2.1.0 exporter, and atomic rollback manager.
- 7/7 Automated Unit Tests passing in 0.047 seconds.
- Designed an intuitive glassmorphic dashboard with live interactive sandbox and automated compliance metrics.
📚 What We Learned
- How deterministic AST static analysis dramatically reduces false positives compared to raw LLM prompt wrappers.
- Implementing OASIS standard SARIF schemas for seamless enterprise GitHub Actions DevSecOps workflows.
🔮 What's Next for ForgeGuard
- 🌐 Multi-language AST support for TypeScript, Go, and Rust.
- 🔌 Native VS Code and Cursor IDE extensions for inline real-time auto-remediation.
- 🤖 GitHub App Bot that automatically opens verified PRs with synthesized unified diffs.

Log in or sign up for Devpost to join the conversation.